
OWASP App Sec BeijingAsia 2011 The OWASP Foundation
OWASP App. Sec Beijing/Asia 2011 The OWASP Foundation http: //www. owasp. org Crypto weakness in popular Web Applications Hanqin Wu Aliyun. com axis@ph 4 nt 0 m. org Copyright © The OWASP Foundation Permission is granted to copy, distribute and/or modify this document under the terms of the OWASP License.
About Me 2001 Founder of “Ph 4 nt 0 m” 2005 join alibaba corp. 2008 join aliyun. com t. qq. com/aullik 5 Blog:hi. baidu. com/aullik 5 Book: 《完美防线》 2
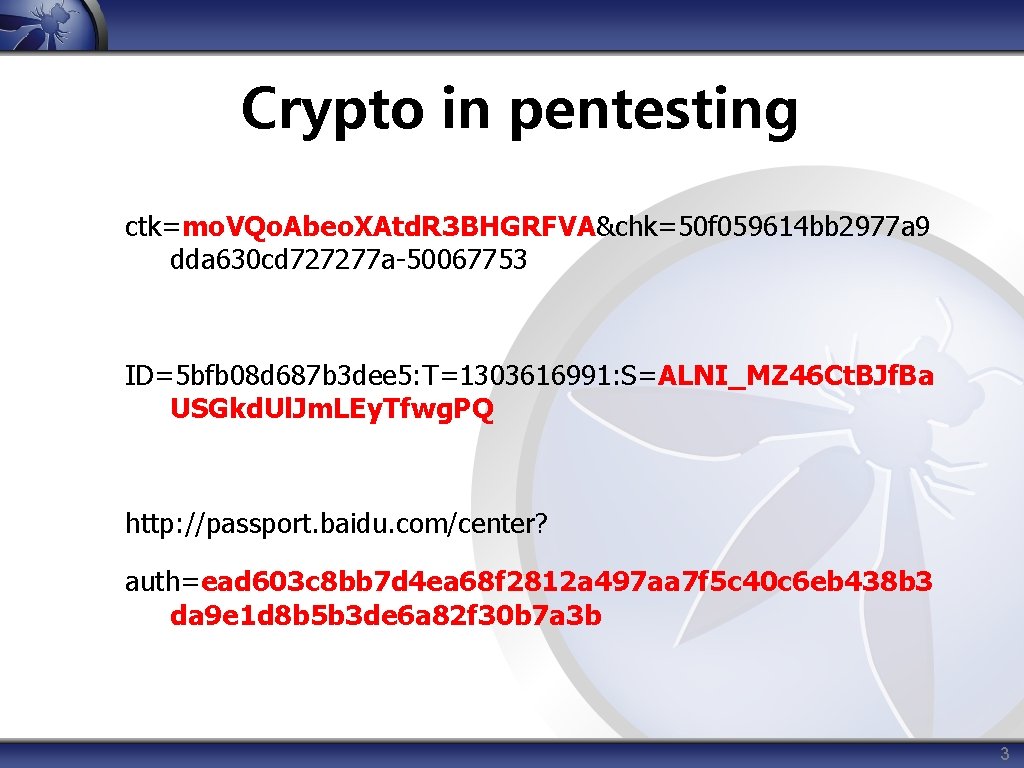
Crypto in pentesting ctk=mo. VQo. Abeo. XAtd. R 3 BHGRFVA&chk=50 f 059614 bb 2977 a 9 dda 630 cd 727277 a-50067753 ID=5 bfb 08 d 687 b 3 dee 5: T=1303616991: S=ALNI_MZ 46 Ct. BJf. Ba USGkd. Ul. Jm. LEy. Tfwg. PQ http: //passport. baidu. com/center? auth=ead 603 c 8 bb 7 d 4 ea 68 f 2812 a 497 aa 7 f 5 c 40 c 6 eb 438 b 3 da 9 e 1 d 8 b 5 b 3 de 6 a 82 f 30 b 7 a 3 b 3
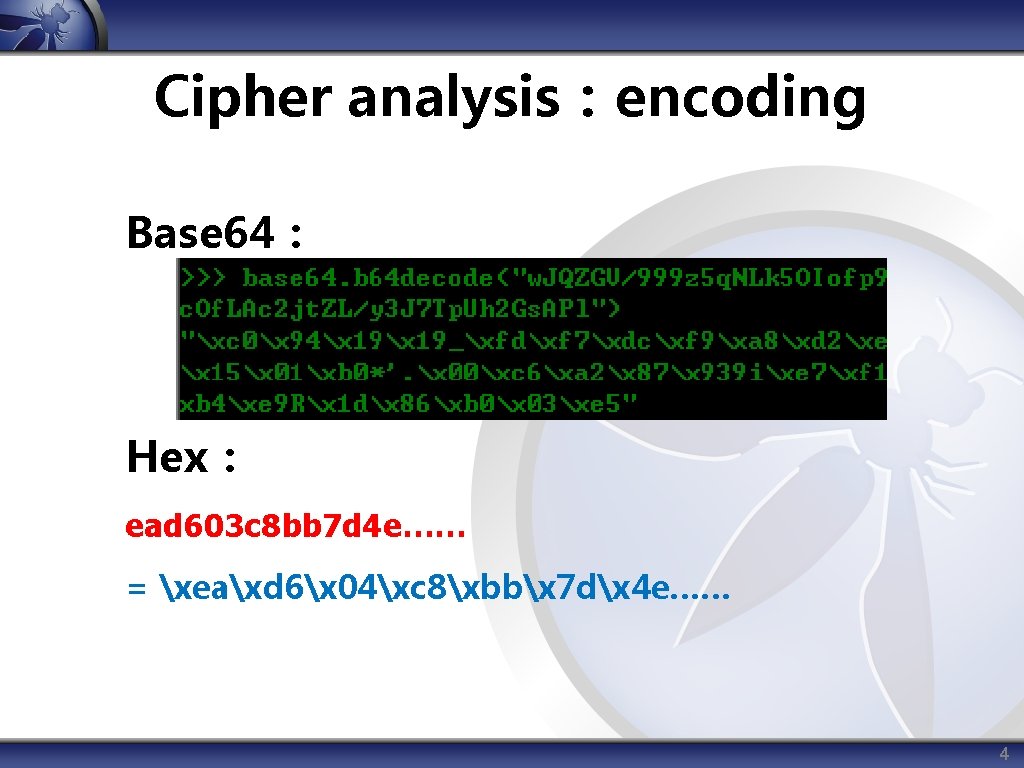
Cipher analysis:encoding Base 64: Hex: ead 603 c 8 bb 7 d 4 e…… = xeaxd 6x 04xc 8xbbx 7 dx 4 e…… 4
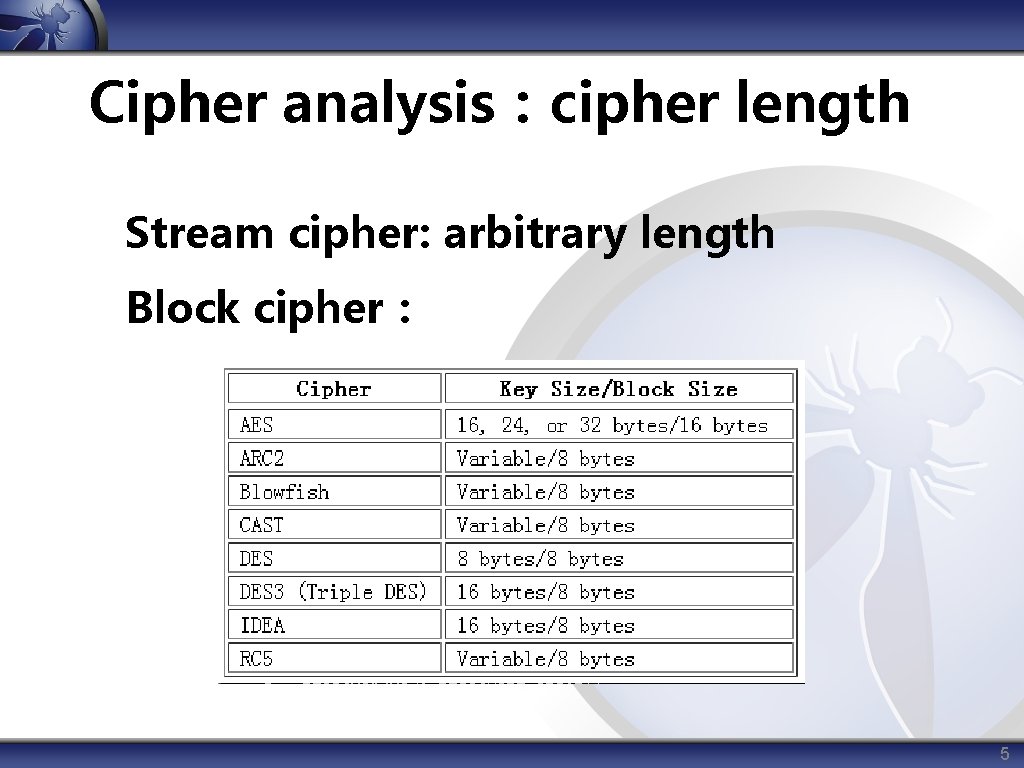
Cipher analysis:cipher length Stream cipher: arbitrary length Block cipher: 5
Cipher analysis:cipher mode ECB-mode: change 1 byte in plaintext 1 block changed in ciphertext CBC-mode: change 1 byte in plaintext whole ciphertext changed 6
In developer’s mind 1. Third-party crypto library 2. performance 3. security – only key length 7
Failures 1. Using hash algorithm instead of crypto 2. No “salts” when using hash algorithm 3. Using “time” instead of random num. 4. Lack of knowledage about crypto 5. …… 8
Crypto introduce Block cipher Stream cipher 9
Basic in crypto IV:init vector mode:ECB、CBC、CFB、OFB、CTR blocksize:Blocksize KEY 10
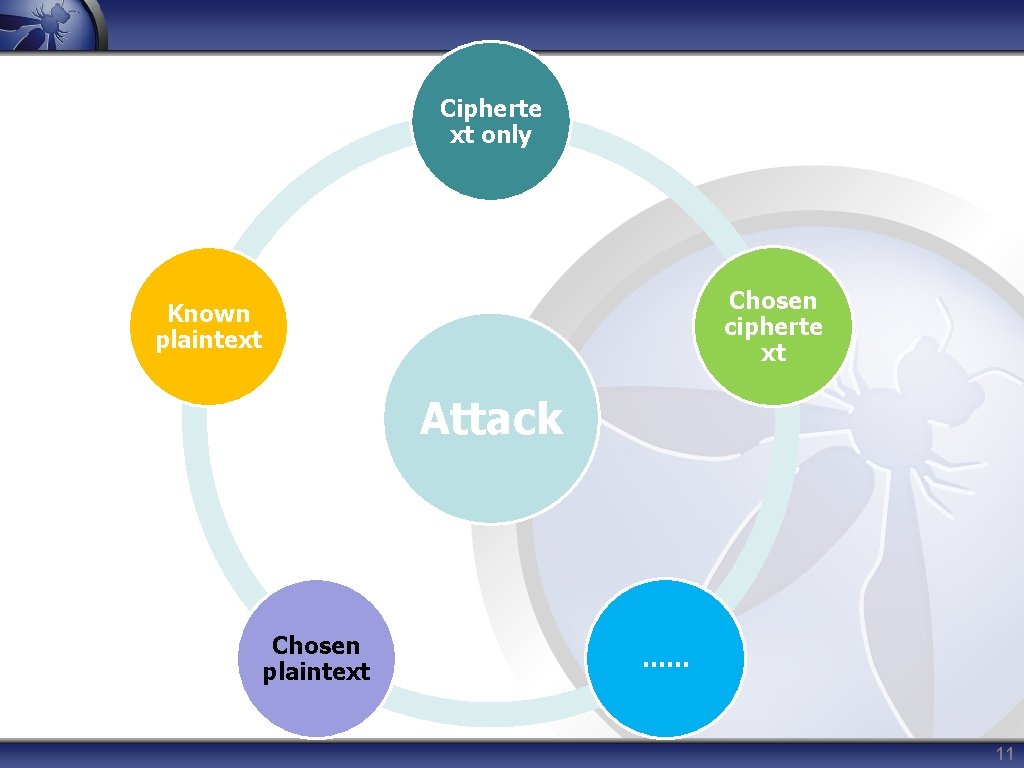
Cipherte xt only Chosen cipherte xt Known plaintext Attack Chosen plaintext …… 11
Attack block cipher 12

ECB mode 13
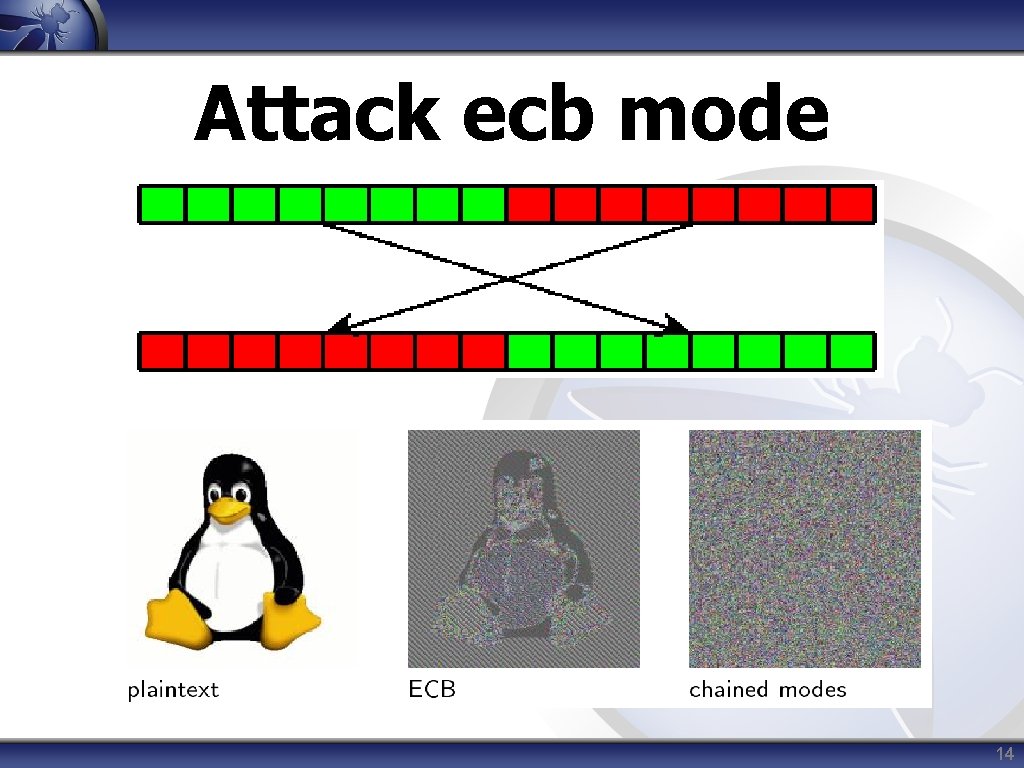
Attack ecb mode 14
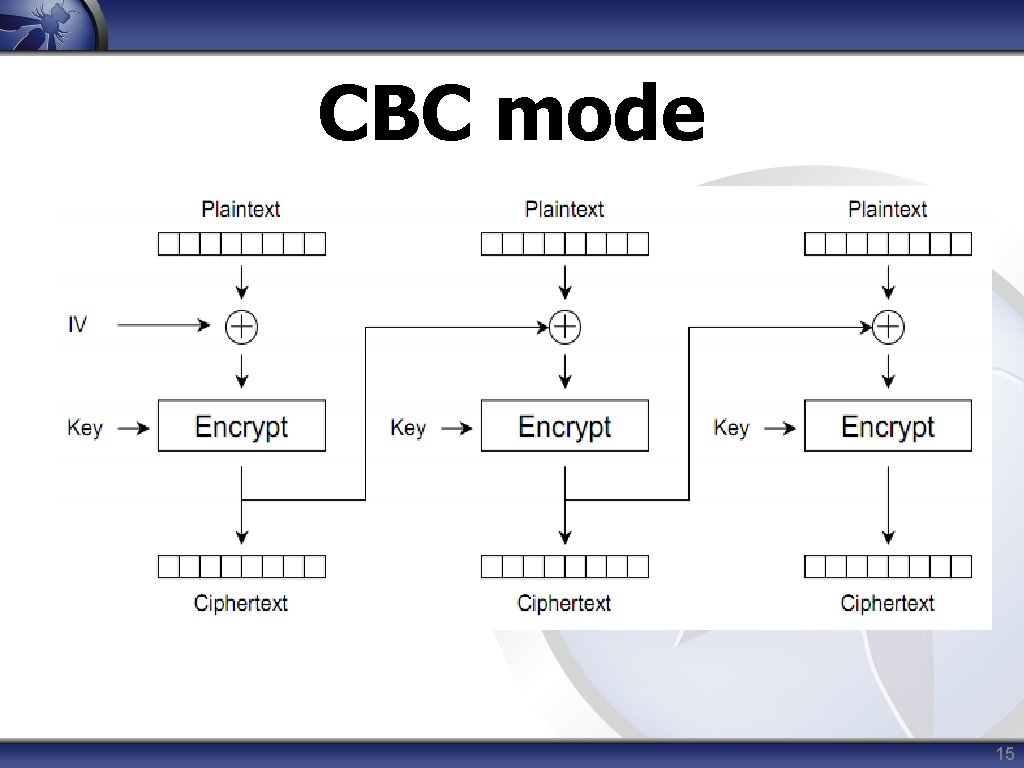
CBC mode 15
Padding Oracle Padding:PKCS#5 Oracle Like “blind injection” “side channel attack” 16
Attack stream cipher 17
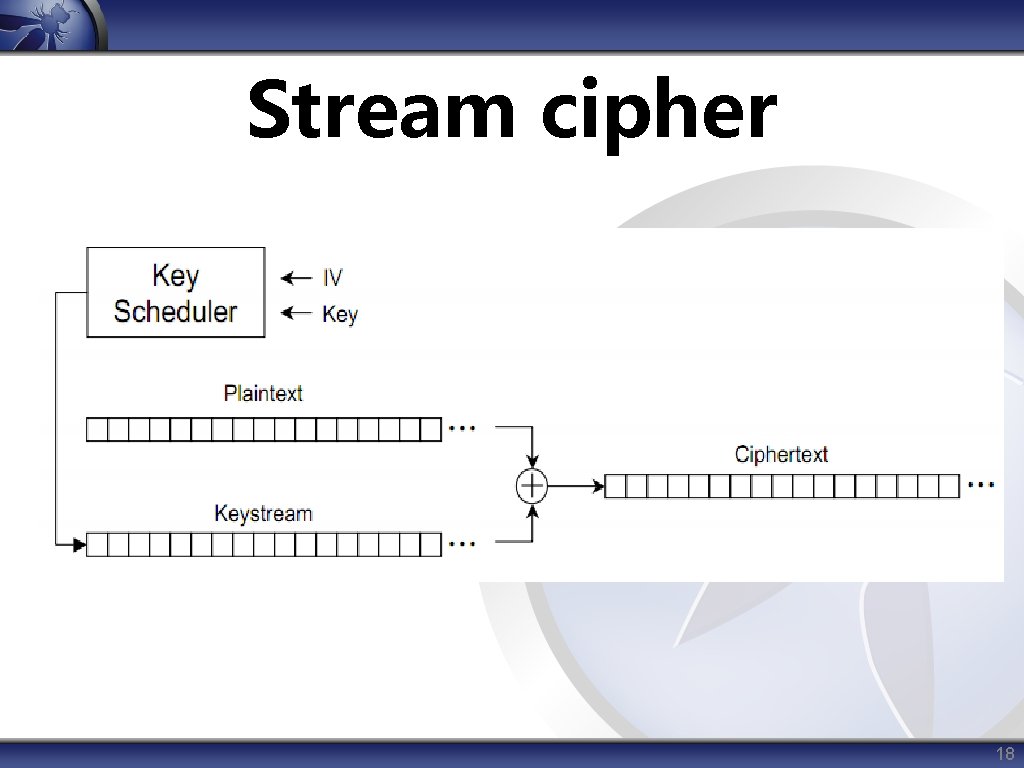
Stream cipher 18
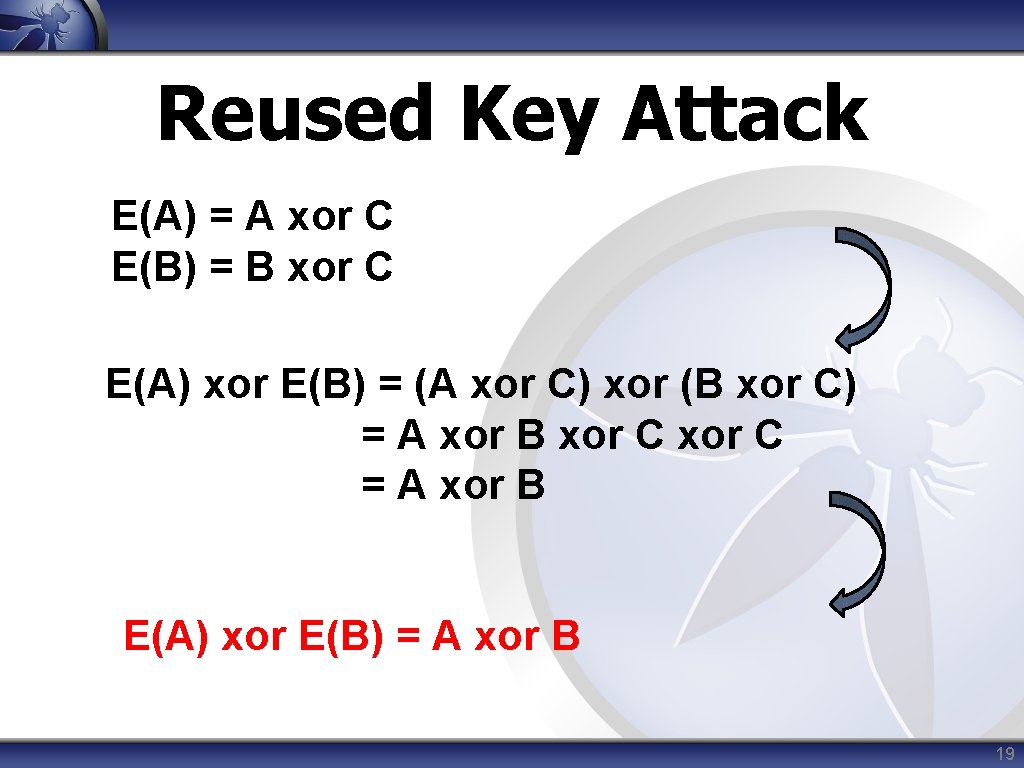
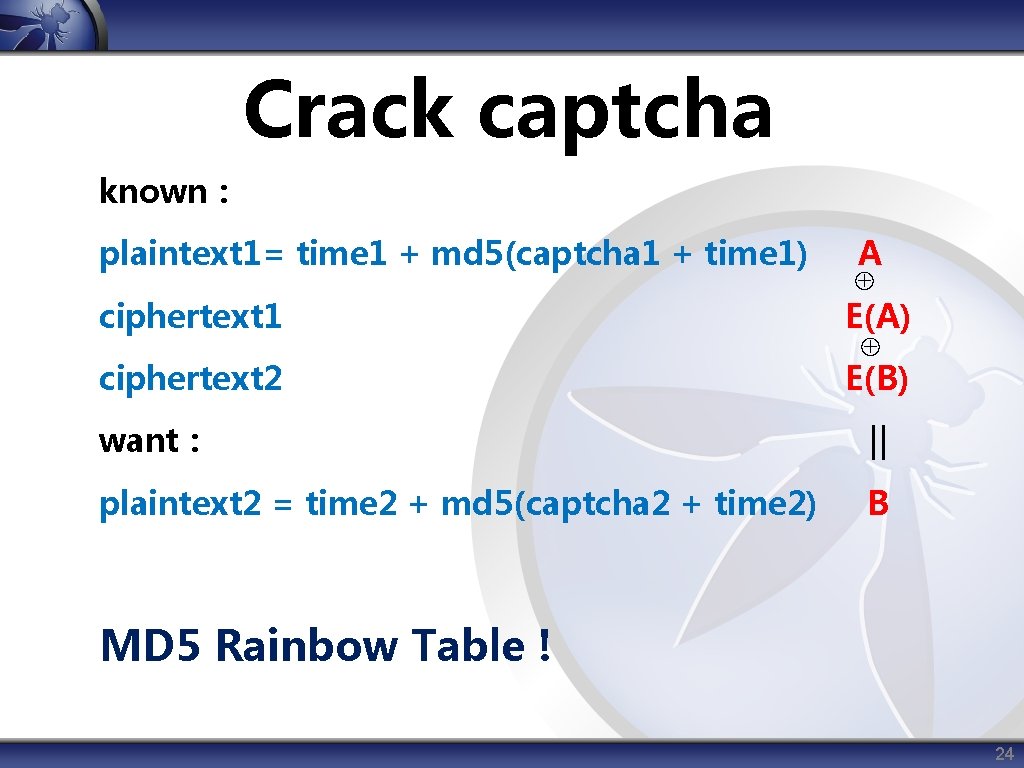
Reused Key Attack E(A) = A xor C E(B) = B xor C E(A) xor E(B) = (A xor C) xor (B xor C) = A xor B xor C = A xor B E(A) xor E(B) = A xor B 19
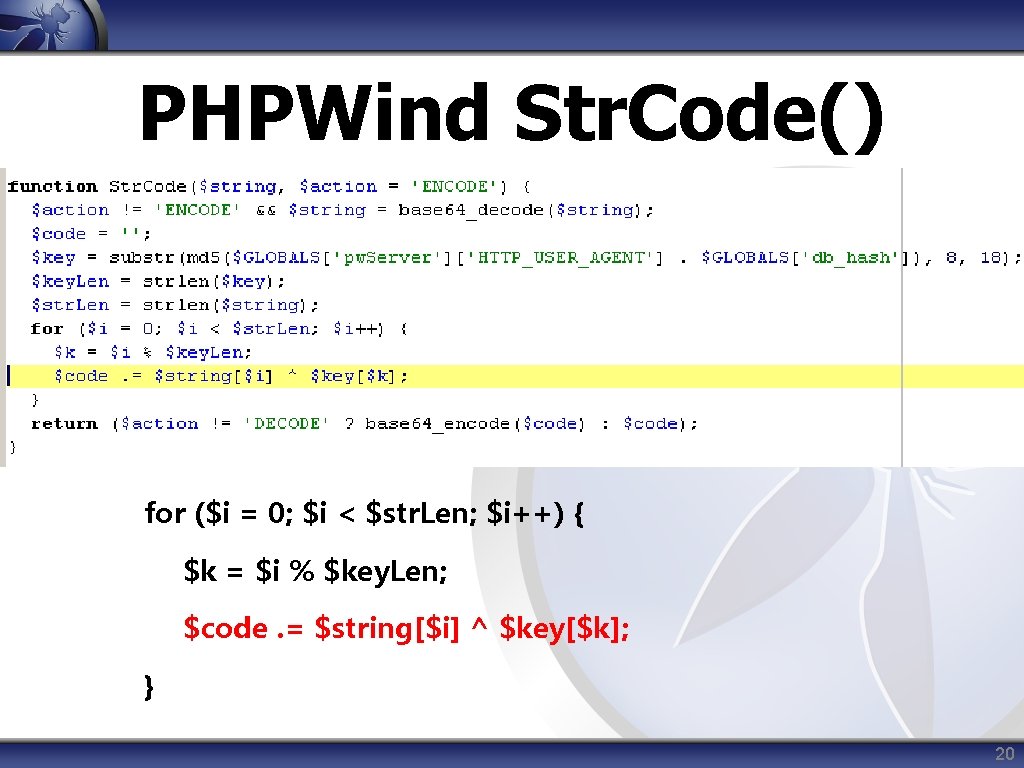
PHPWind Str. Code() for ($i = 0; $i < $str. Len; $i++) { $k = $i % $key. Len; $code. = $string[$i] ^ $key[$k]; } 20
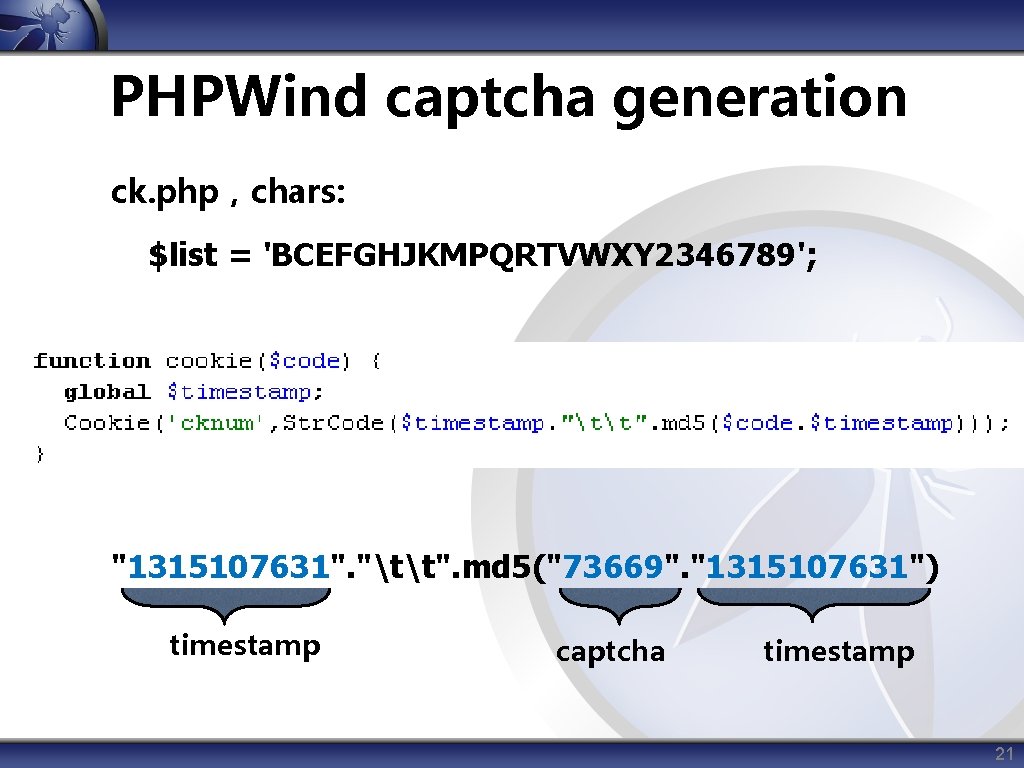
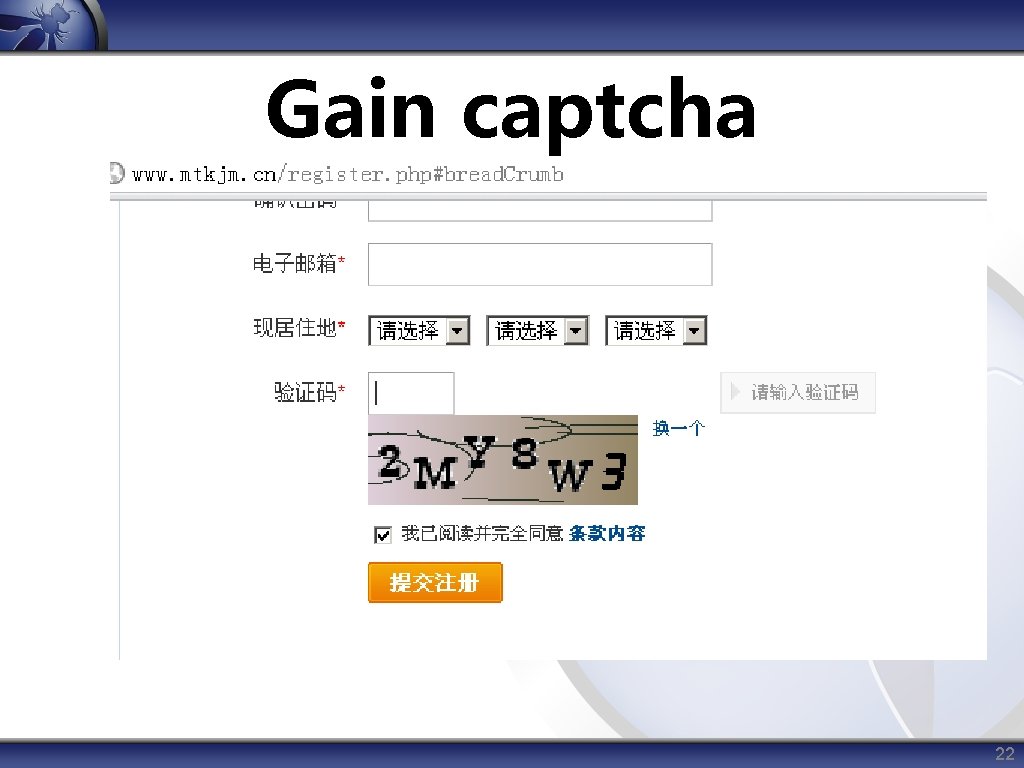
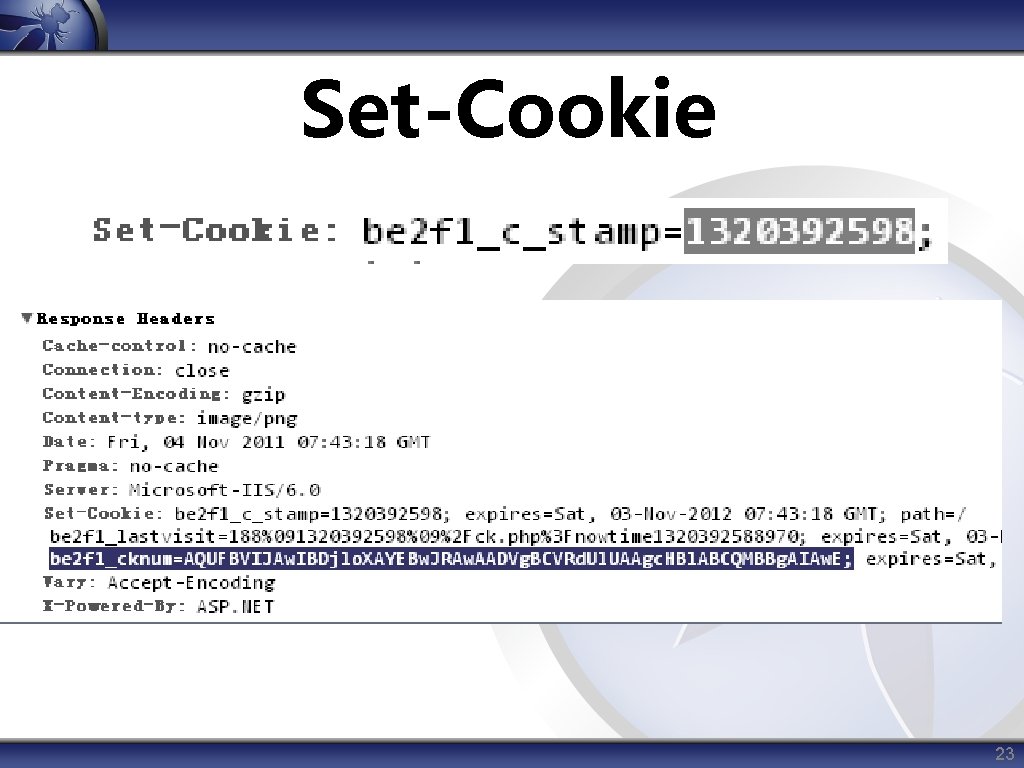
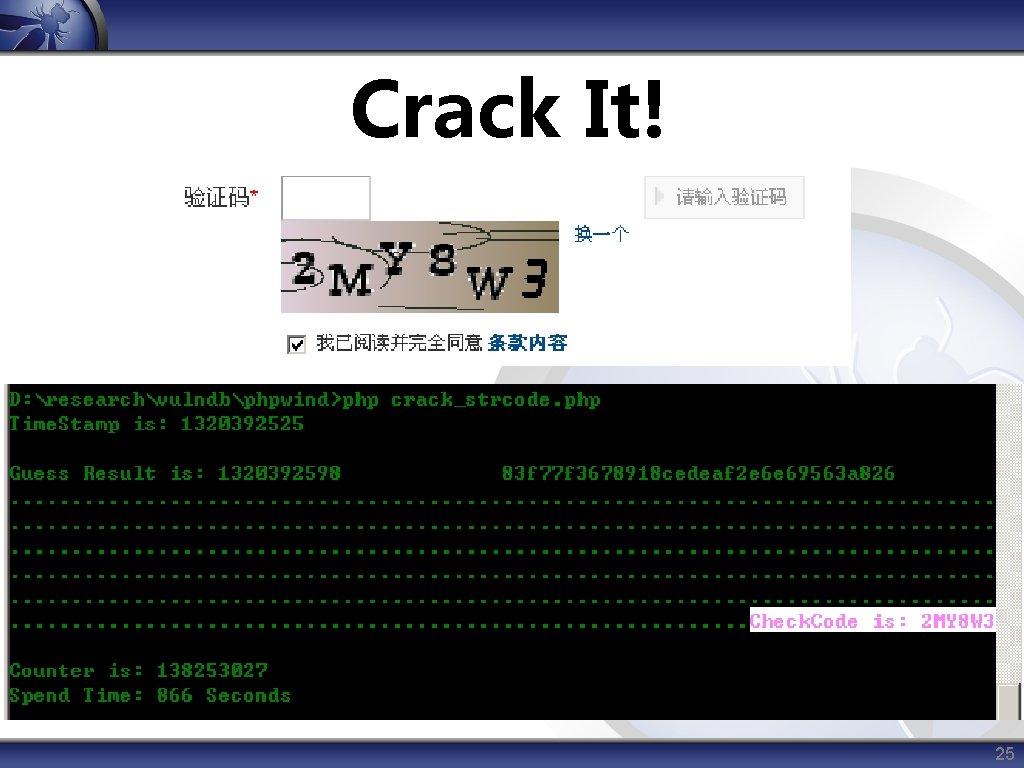
PHPWind captcha generation ck. php,chars: $list = 'BCEFGHJKMPQRTVWXY 2346789'; "1315107631". "tt". md 5("73669". "1315107631") timestamp captcha timestamp 21
Gain captcha 22
Set-Cookie 23
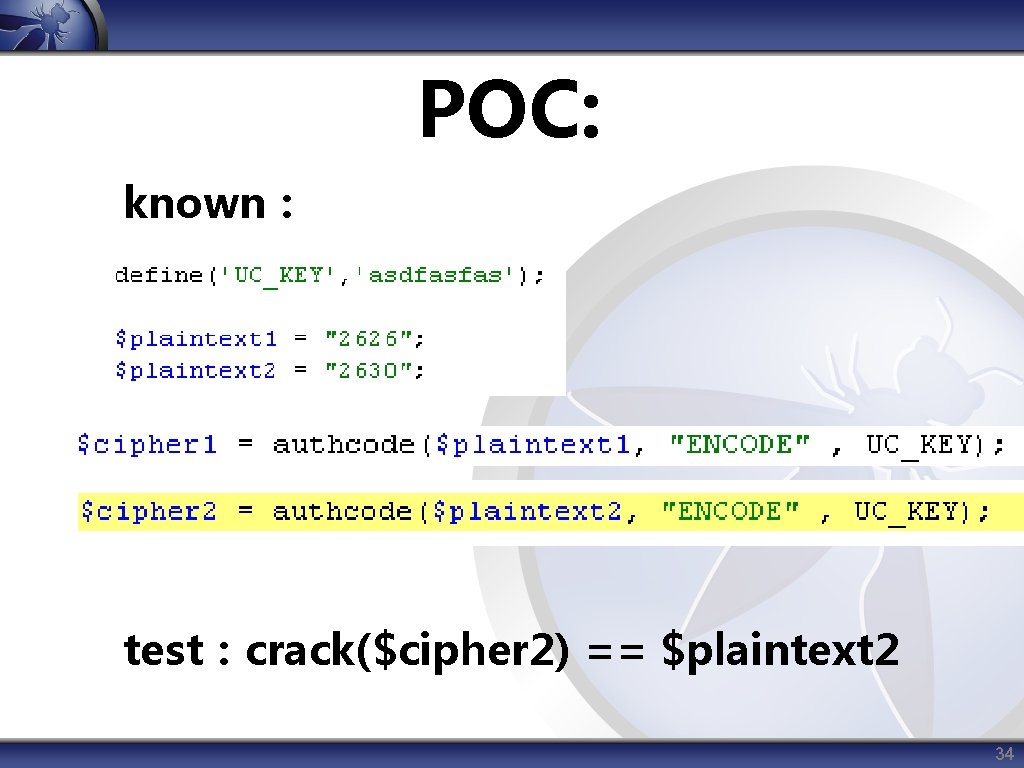
Crack captcha known: plaintext 1= time 1 + md 5(captcha 1 + time 1) A ⊕ ciphertext 1 E(A) ciphertext 2 E(B) ⊕ want: ‖ plaintext 2 = time 2 + md 5(captcha 2 + time 2) B MD 5 Rainbow Table ! 24
Crack It! 25
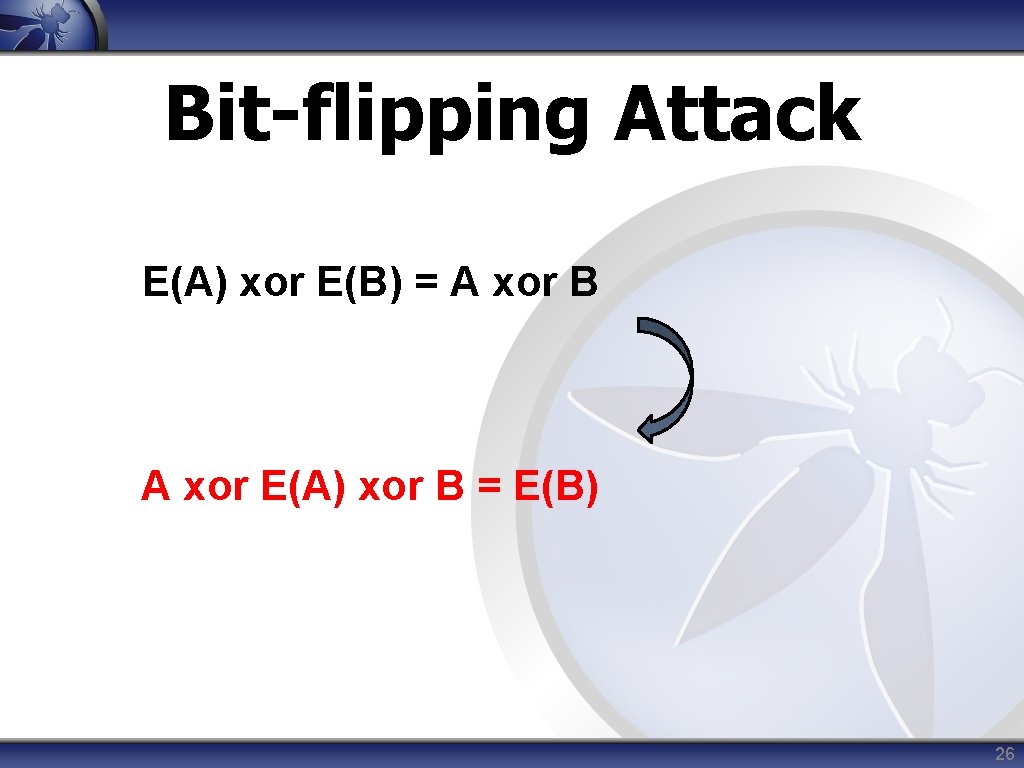
Bit-flipping Attack E(A) xor E(B) = A xor B A xor E(A) xor B = E(B) 26
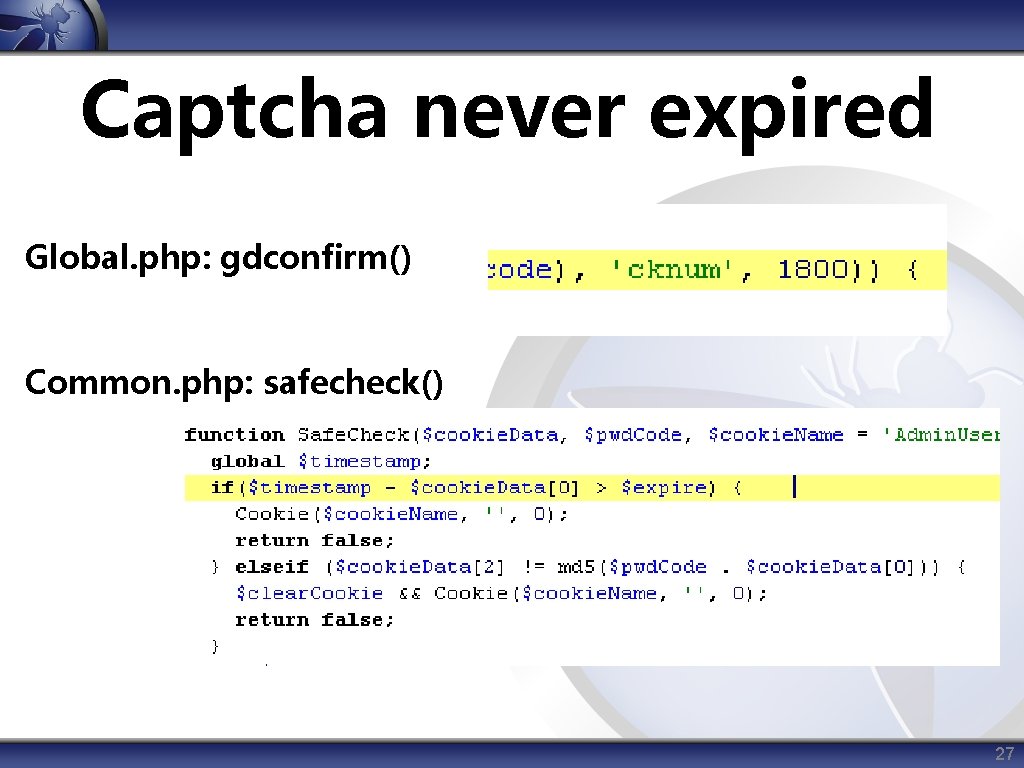
Captcha never expired Global. php: gdconfirm() Common. php: safecheck() 27
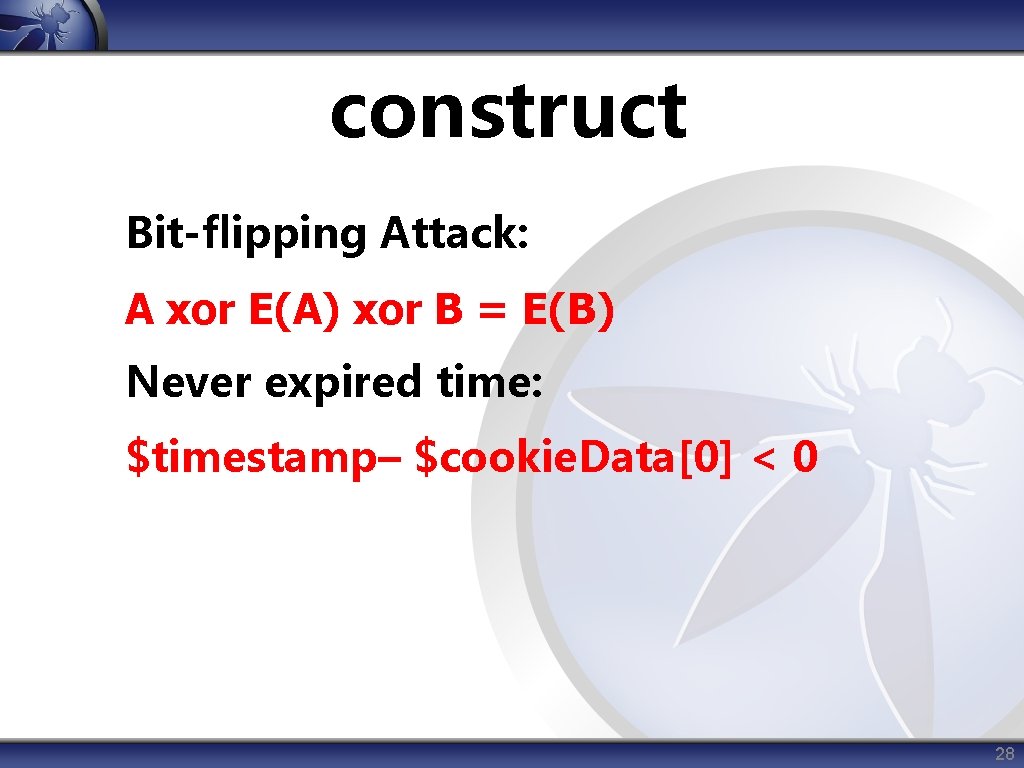
construct Bit-flipping Attack: A xor E(A) xor B = E(B) Never expired time: $timestamp– $cookie. Data[0] < 0 28
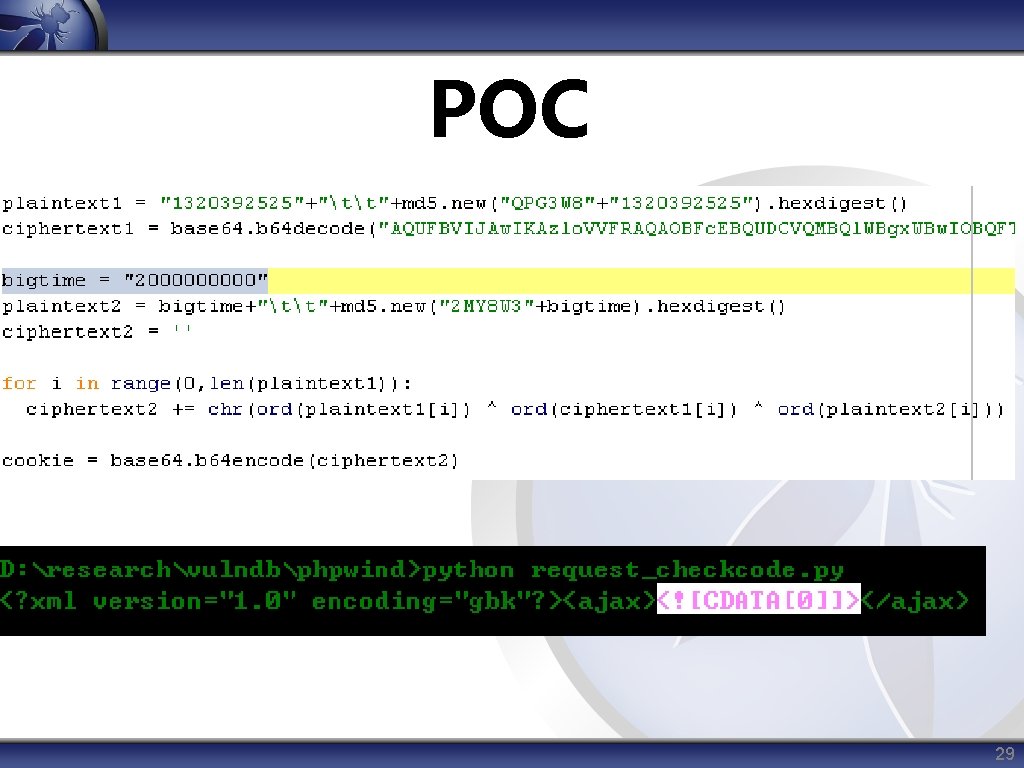
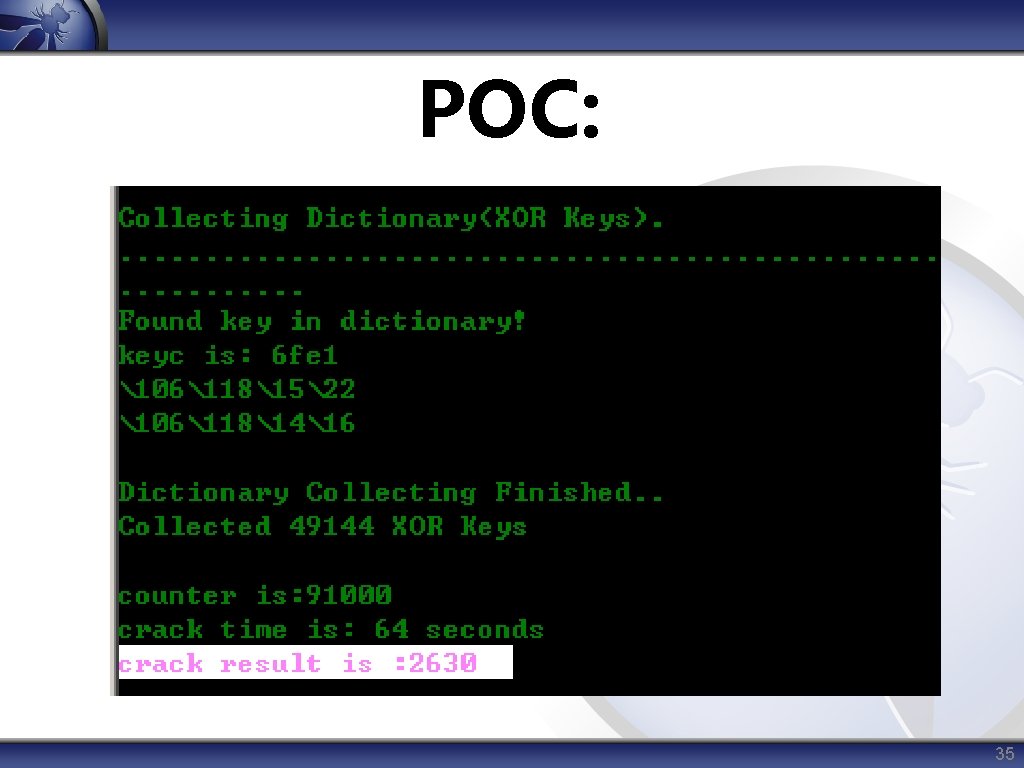
POC 29
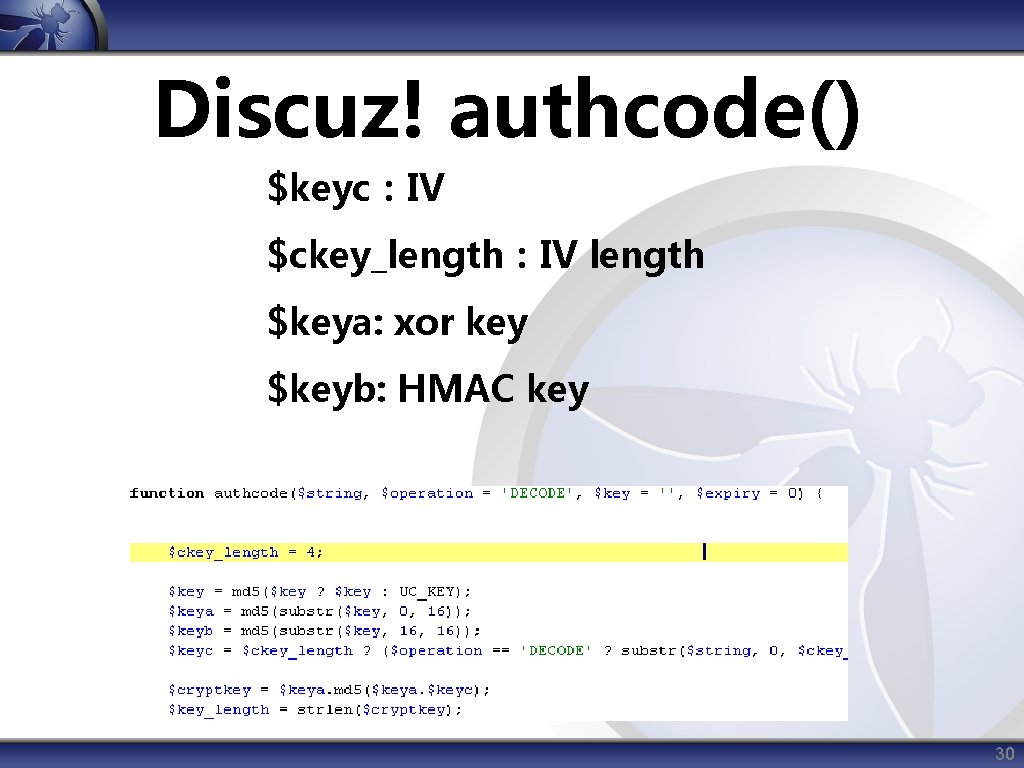
Discuz! authcode() $keyc:IV $ckey_length:IV length $keya: xor key $keyb: HMAC key 30
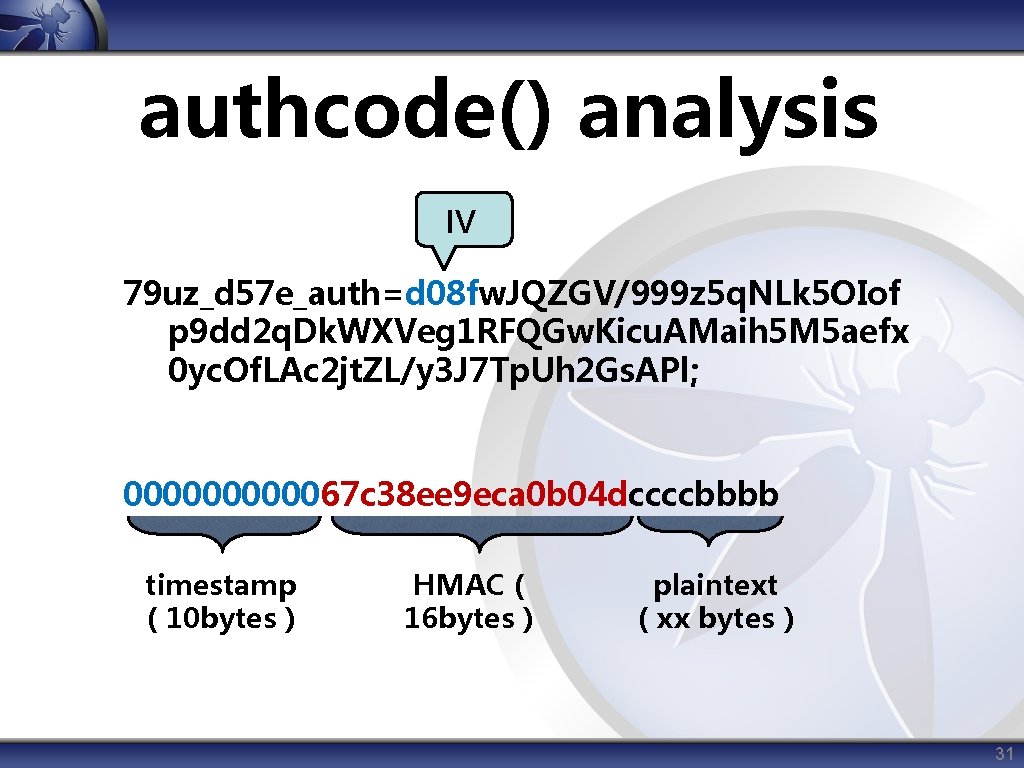
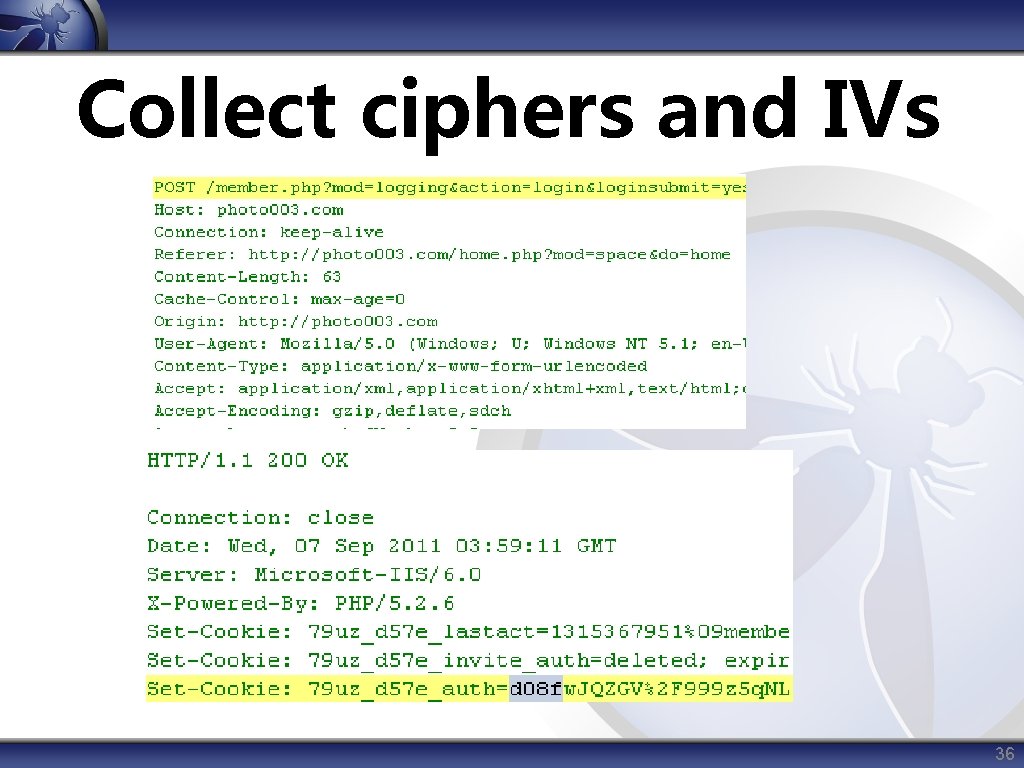
authcode() analysis IV 79 uz_d 57 e_auth=d 08 fw. JQZGV/999 z 5 q. NLk 5 OIof p 9 dd 2 q. Dk. WXVeg 1 RFQGw. Kicu. AMaih 5 M 5 aefx 0 yc. Of. LAc 2 jt. ZL/y 3 J 7 Tp. Uh 2 Gs. APl; 0000067 c 38 ee 9 eca 0 b 04 dccccbbbb timestamp (10 bytes) HMAC( 16 bytes) plaintext (xx bytes) 31
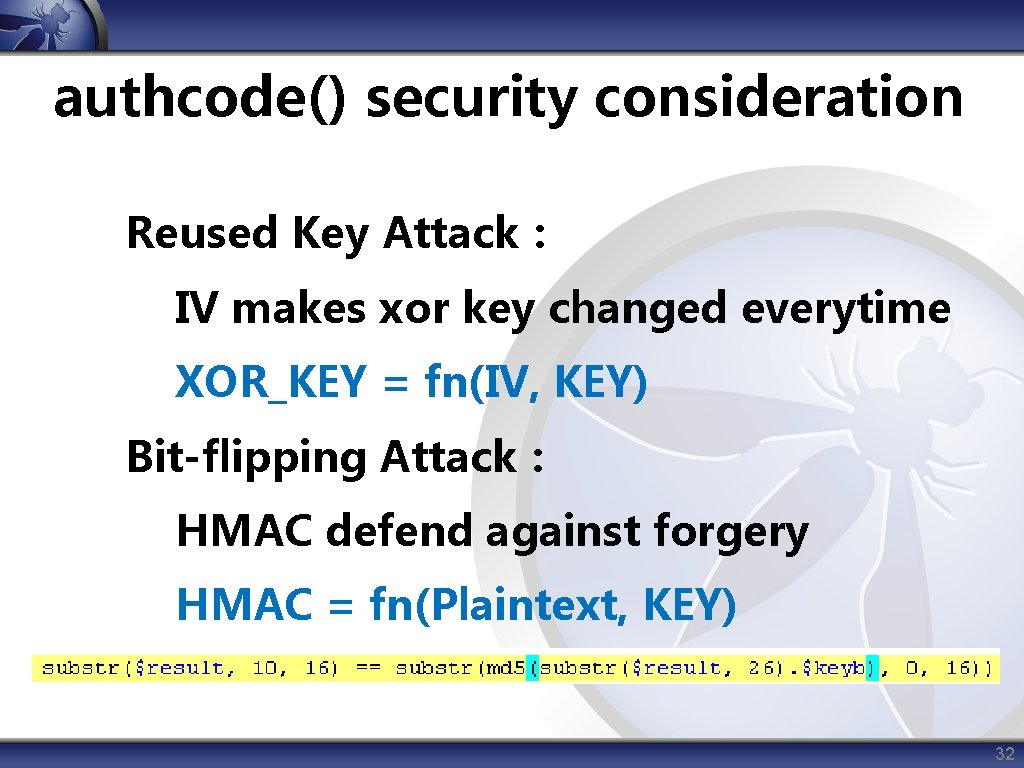
authcode() security consideration Reused Key Attack: IV makes xor key changed everytime XOR_KEY = fn(IV, KEY) Bit-flipping Attack: HMAC defend against forgery HMAC = fn(Plaintext, KEY) 32
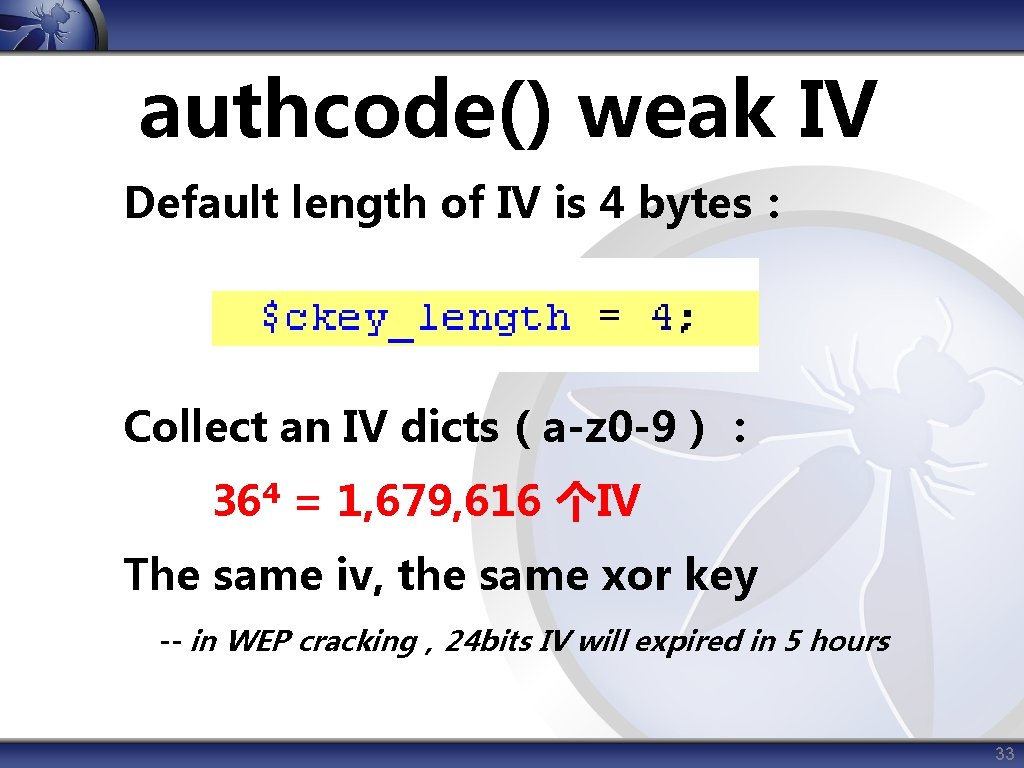
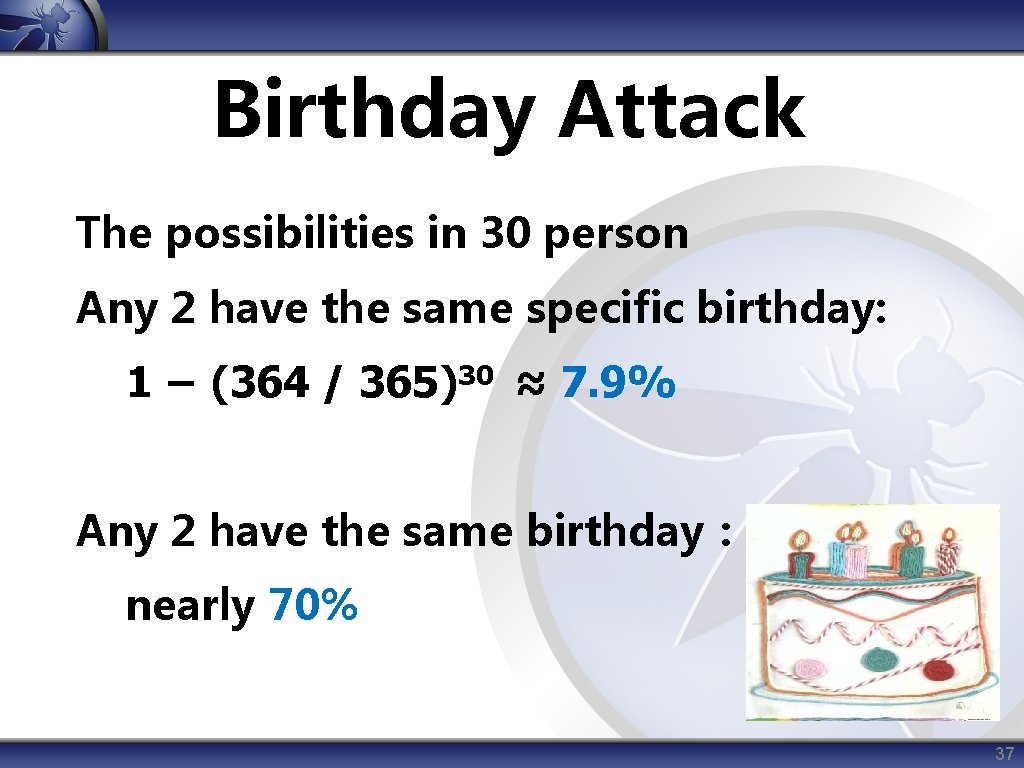
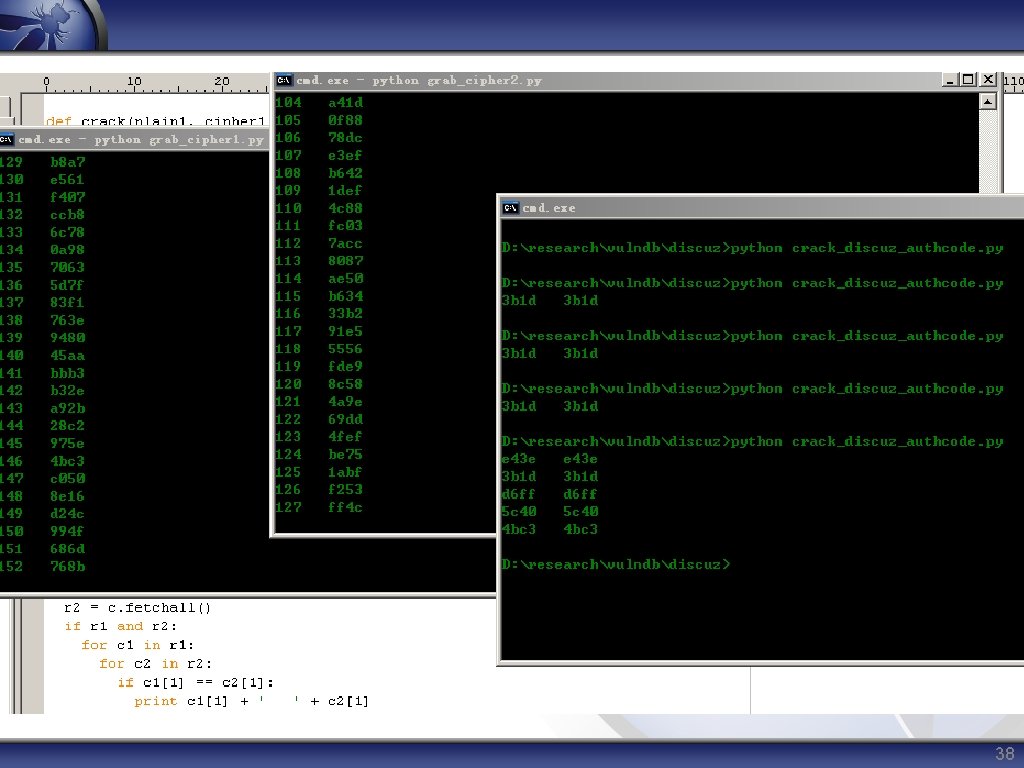
authcode() weak IV Default length of IV is 4 bytes: Collect an IV dicts(a-z 0 -9): 4 36 = 1, 679, 616 个IV The same iv, the same xor key -- in WEP cracking,24 bits IV will expired in 5 hours 33
POC: known: test:crack($cipher 2) == $plaintext 2 34
POC: 35
Collect ciphers and IVs 36
Birthday Attack The possibilities in 30 person Any 2 have the same specific birthday: 1 − (364 / 365)30 ≈ 7. 9% Any 2 have the same birthday: nearly 70% 37
38
Attack authcode()? Reused Key Attack: IV makes xor key changed everytime brutefoce IVs Bit-flipping Attack: HMAC defend against forgery still safe 39
Other attack? Discuz! Getwebshell: http: //www. oldjun. com/blog/index. php/archives/76/ Phpcms cookie sql injection: http: //www. 80 vul. com/phpcms_sys_auth. txt …… 40
Summary & Conclusion
advice Do not use ECB mode Do not use stream cipher Use AES-256 or blowfish in CBC mode Do not use the same key to do different things Use random IV Use HMAC-SHA 512 instead of MD 5 42
Thanks!
- Slides: 43