
MYTHBUSTERS Credit Card Processing Fees PCI Compliance Presented
MYTHBUSTERS! Credit Card Processing Fees & PCI Compliance Presented by Meredith Mitchell Partner Channel Manager, Charge. Logic
Rules and Points MYTH or FACT: Ligers are bred for skills in magic.
MYTH or FACT? Credit card processing is a necessary evil for doing business? FACT! 40% prefer credit 35% prefer debit 11% prefer cash
MYTH or FACT? Credit card processing is a necessary evil for doing business? FACT! • Buy now, pay later • Credit cards are convenient for business & consumers • Benefits like ü Deferred payments ü Points ü Less painful than cash
MYTH or FACT? You have to work through a bank for credit card processing. MYTH! Meow. You’ve got options.
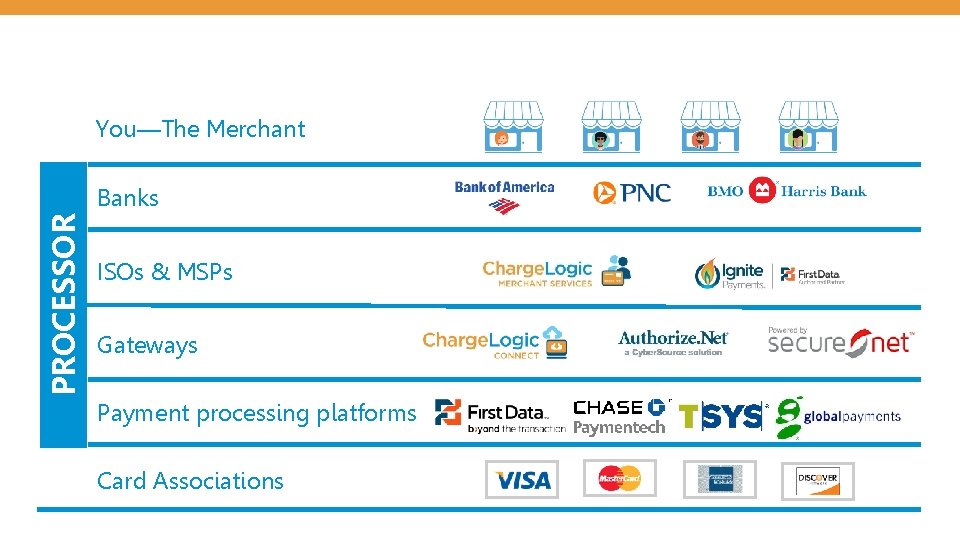
You—The Merchant PROCESSOR Banks ISOs & MSPs Gateways Payment processing platforms Card Associations
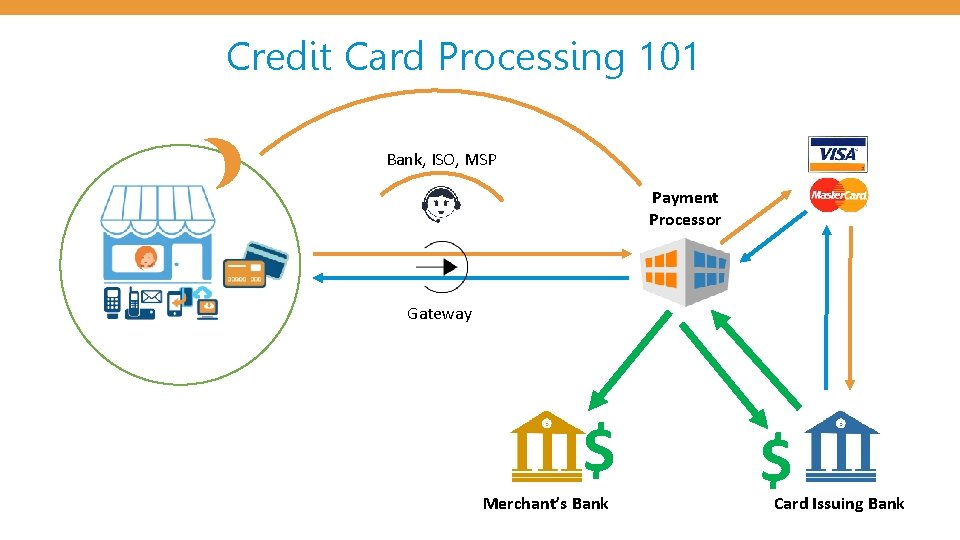
Credit Card Processing 101 Bank, ISO, MSP Payment Processor Gateway $ Merchant’s Bank $ Card Issuing Bank
MYTH or FACT? A gateway and payment processing platform provide the same services/are the same. MYTH! Gateways • • Fee/transaction Necessary for ecommerce • • • Authorize. net Secure. Net Charge. Logic Connect
MYTH or FACT? A gateway and payment processing platform provide the same services/are the same. MYTH! Payment Processing Platforms • Direct connect = lower fees • Level 2 & Level 3 • First Data • Chase Paymentech • Vantiv
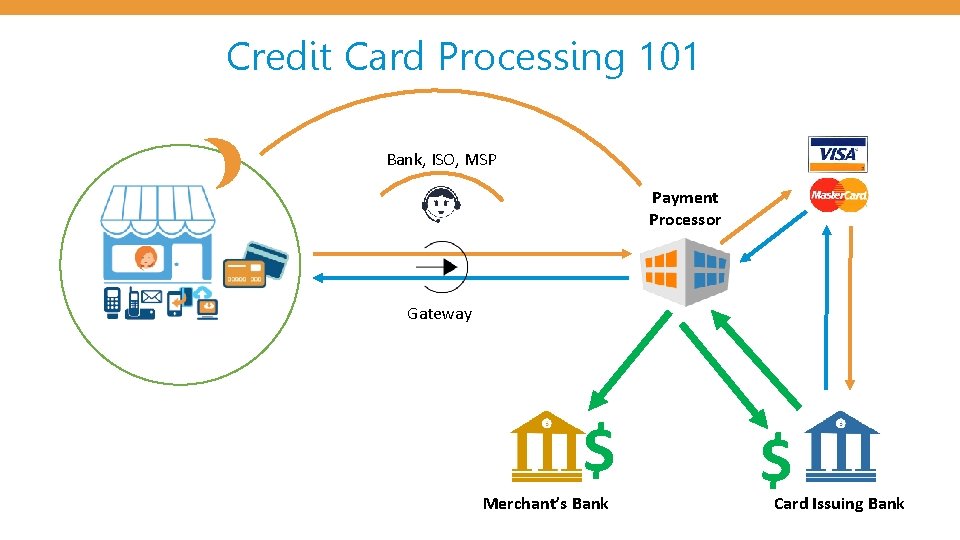
Credit Card Processing 101 Bank, ISO, MSP Payment Processor Gateway $ Merchant’s Bank $ Card Issuing Bank
MYTH or FACT? I only need to be PCI compliant if I’m a large company. MYTH! Any business that process, handles, or stores credit card data must be PCI DSS compliant.
What is PCI Compliance? Adherence to the standards to protect cardholder data as set forth by the Payment Card Industry Standards Council. All businesses that process, transmit, and/or store cardholder data need to be PCI compliant.
MYTH or FACT? Hackers don’t target small business. MYTH! Small business are vulnerable to attacks.
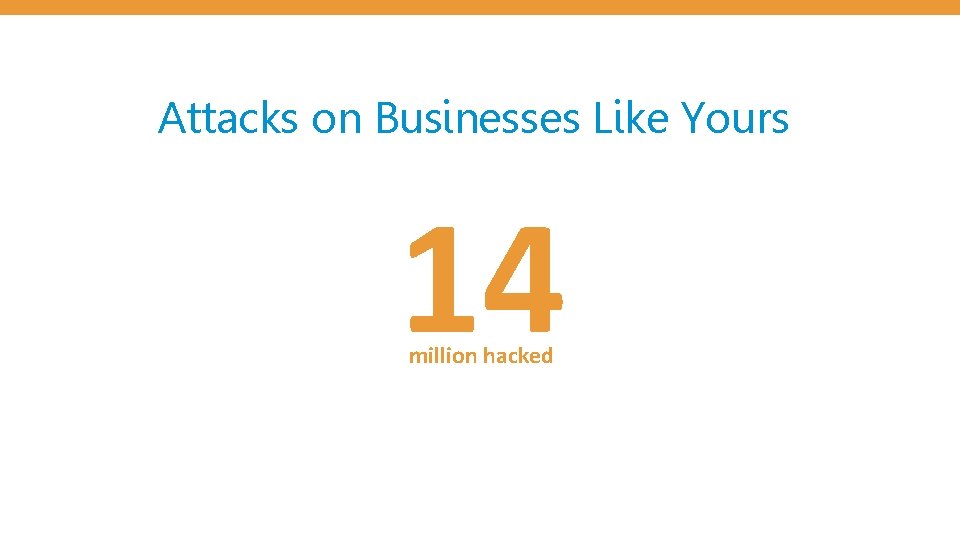
Attacks on Businesses Like Yours 14 million hacked
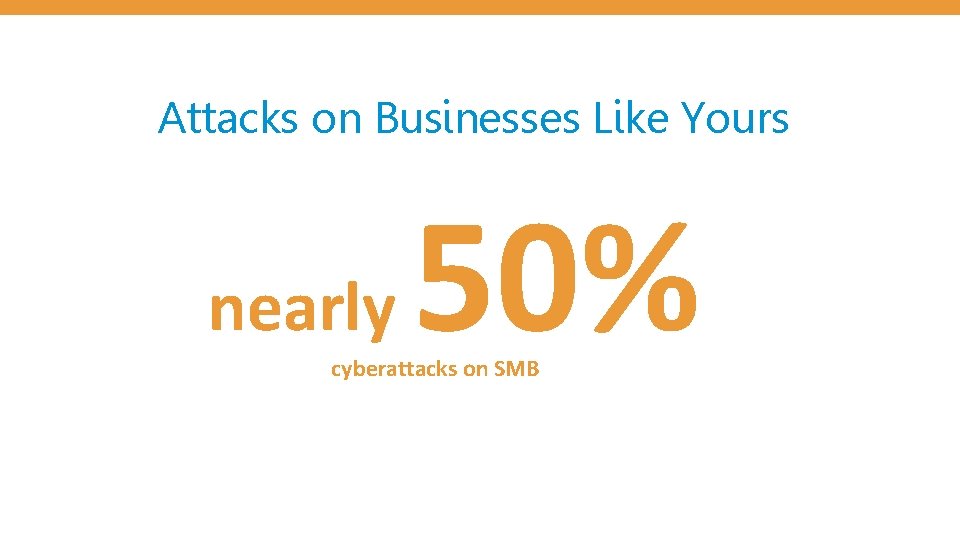
Attacks on Businesses Like Yours nearly 50% cyberattacks on SMB
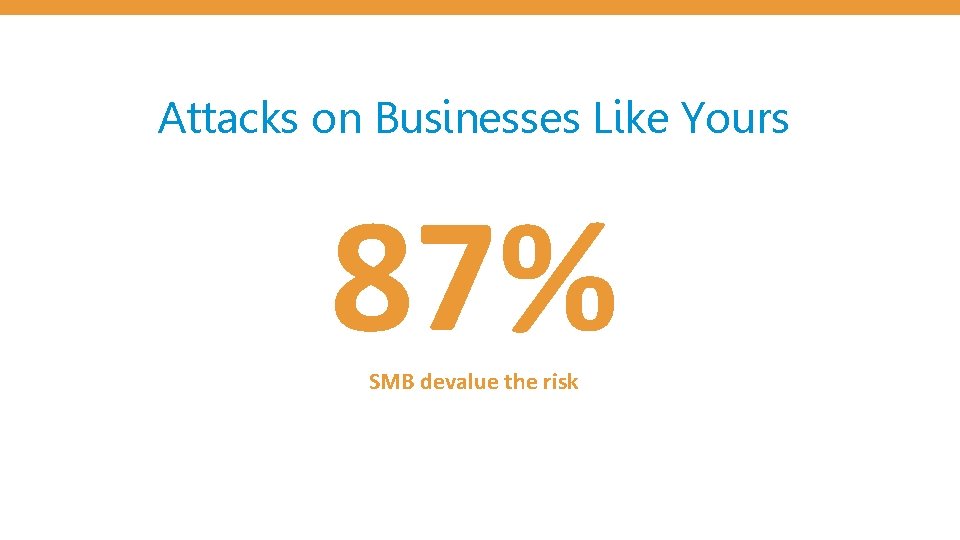
Attacks on Businesses Like Yours 87% SMB devalue the risk
Attacks on Businesses Like Yours $24 mil To criminals deploying ransomware
Attacks on Businesses Like Yours 1 in 3 Lacking protection
The Cost of Noncompliance Fines, penalties, and increased fees Lost revenues, customers, jobs Negative market image Cost of reissuing credit cards Lawsuits, insurance claims Average cost of each stolen card or record = $141* Global average cost of a data breach = $3. 62 million* *2017 Ponemon Cost of Data Breach Study
MYTH or FACT? Using a PA-DSS validated (PCI-validated software) makes my company PCI compliant. MYTH! It’s just one of many steps that help you achieve compliance.
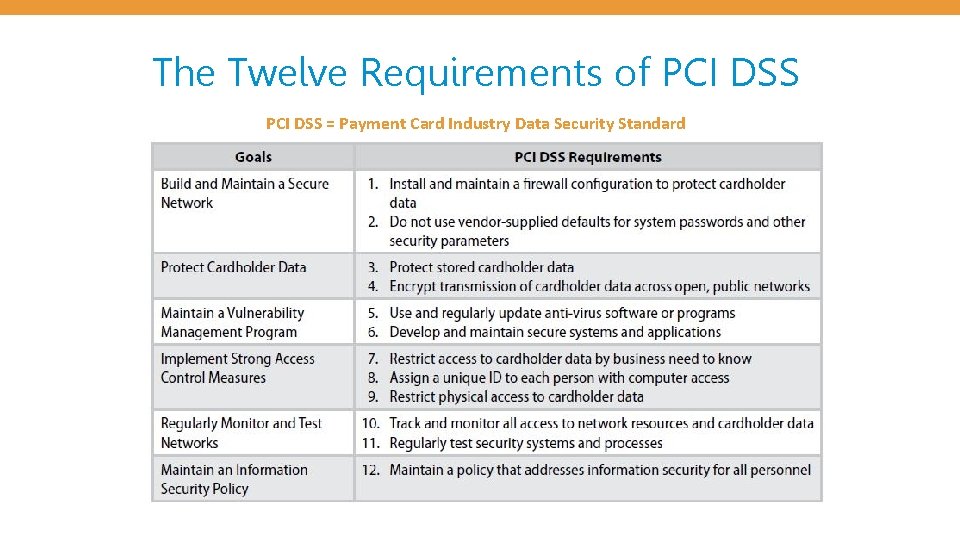
The Twelve Requirements of PCI DSS = Payment Card Industry Data Security Standard
MYTH or FACT? The longer the password the better. FACT! The longer the better!
Build and Maintain a Secure Network Install and maintain a firewall configuration to protect data Do not use vendor-supplied defaults for system passwords and other security requirements
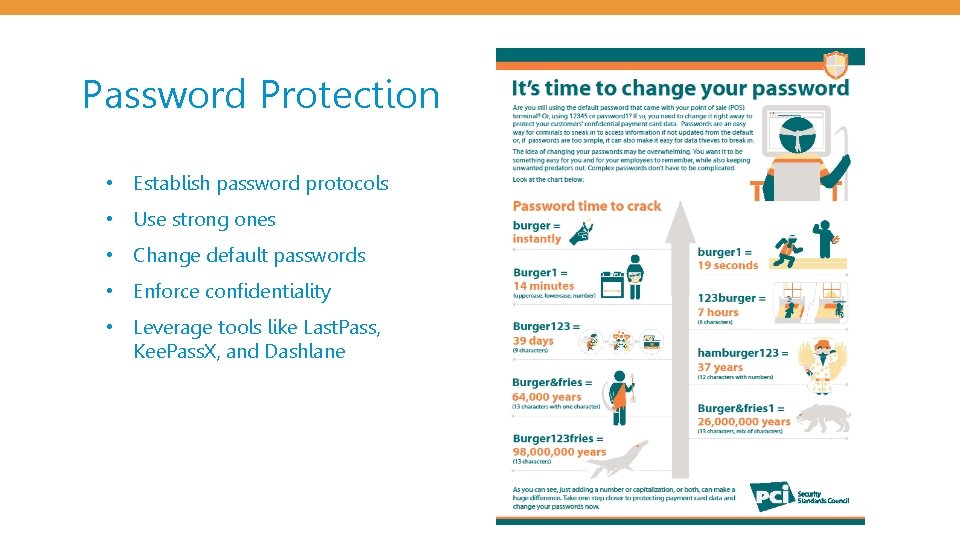
Password Protection • Establish password protocols • Use strong ones • Change default passwords • Enforce confidentiality • Leverage tools like Last. Pass, Kee. Pass. X, and Dashlane
MYTH or FACT? Storing credit card data on my company’s servers is a violation of PCI compliance. MYTH! Stored card holder data must be encrypted.
Protect Cardholder Data Protect stored data Encrypt transmission of cardholder data and sensitive information across public networks
Tokenization and Encryption xxxxx
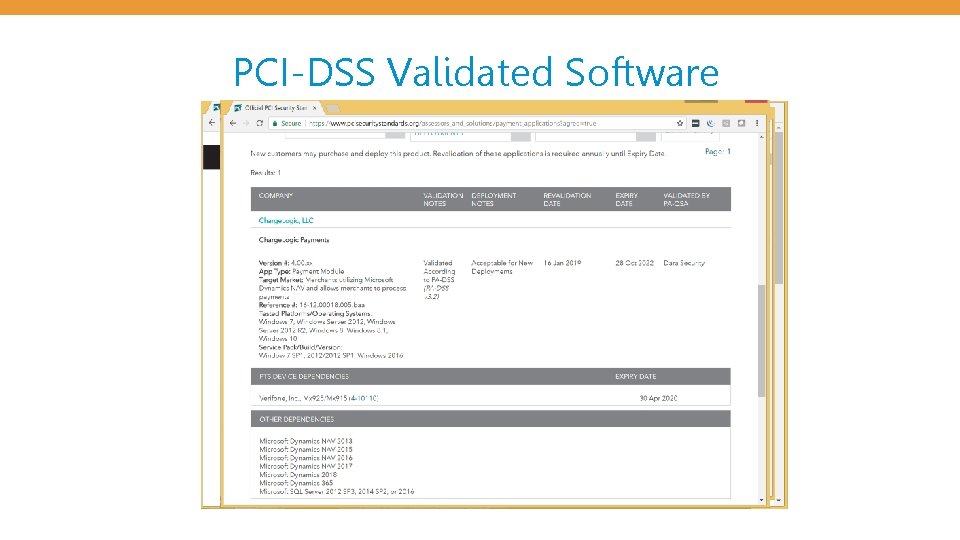
PCI-DSS Validated Software
MYTH or FACT? Applying security patches to software helps protect against malware and viruses. FACT! Keep your systems current!
Maintain a Vulnerability Management Program Protect all systems against malware and regularly update antivirus software or program Develop and maintain secure systems and applications
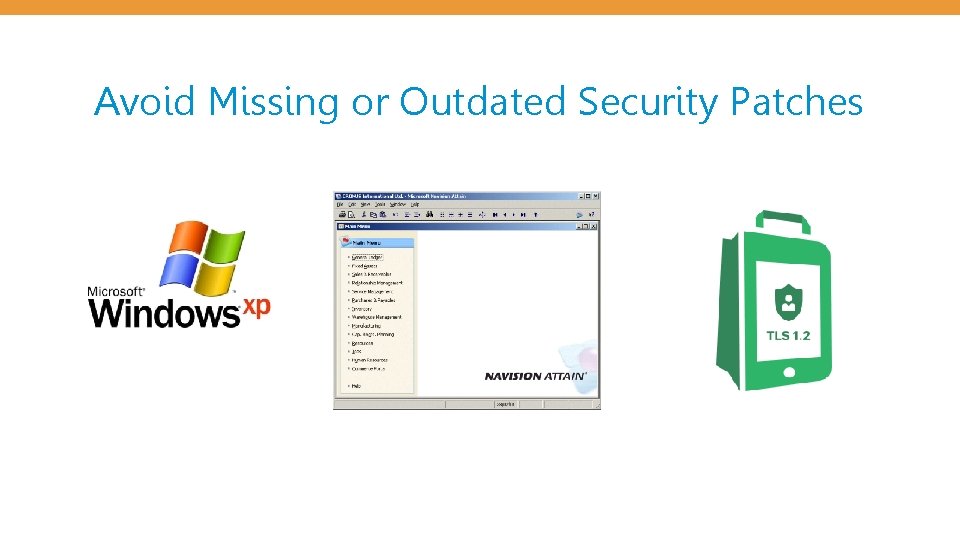
Avoid Missing or Outdated Security Patches
MYTH or FACT? It is PCI compliant to keep written records of credit card numbers and card holder data. FACT, but… It must be stored under lock and key.
Implement Strong Access Control Measures Restrict access to cardholder data by business need to know Assign a unique ID to each person with computer access Restrict physical access to cardholder data
Regularly Monitor and Test Networks Track and monitor all access to network resources and cardholder data Regularly test security systems and processes
MYTH or FACT? You should save customers’ CVV numbers so you don’t have to ask for them each time they make a purchase. MYTH! CVV numbers prove the card holder is in possession of the card.
Maintain an Information Security Policy Maintain a policy that addresses information security for all personnel
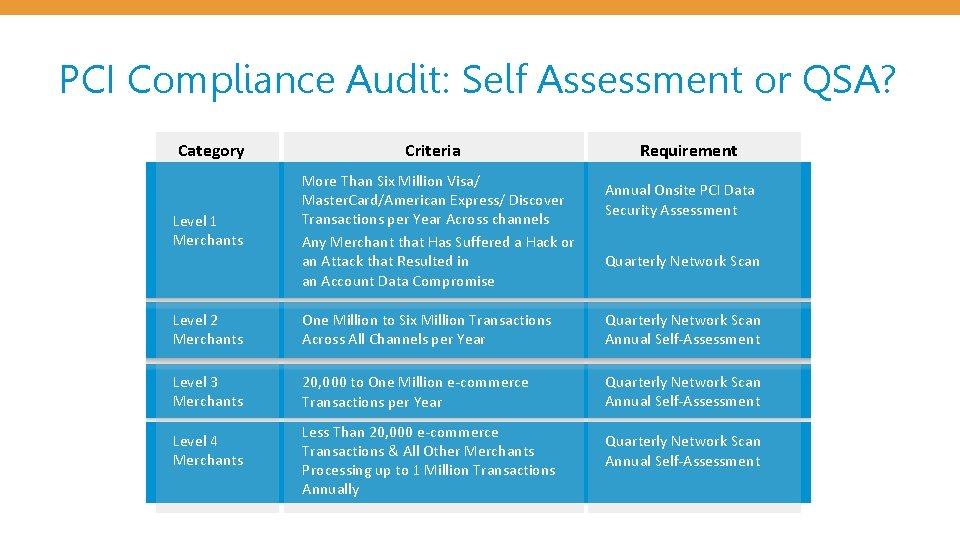
PCI Compliance Audit: Self Assessment or QSA? Category Level 1 Merchants Criteria More Than Six Million Visa/ Master. Card/American Express/ Discover Transactions per Year Across channels Any Merchant that Has Suffered a Hack or an Attack that Resulted in an Account Data Compromise Requirement Annual Onsite PCI Data Security Assessment Quarterly Network Scan Level 2 Merchants One Million to Six Million Transactions Across All Channels per Year Quarterly Network Scan Annual Self-Assessment Level 3 Merchants 20, 000 to One Million e-commerce Transactions per Year Quarterly Network Scan Annual Self-Assessment Level 4 Merchants Less Than 20, 000 e-commerce Transactions & All Other Merchants Processing up to 1 Million Transactions Annually Quarterly Network Scan Annual Self-Assessment
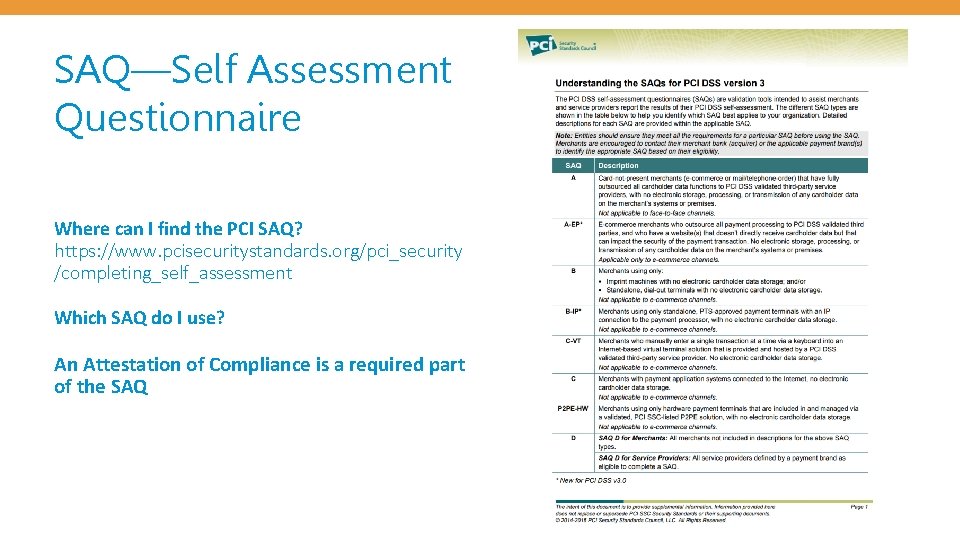
SAQ—Self Assessment Questionnaire Where can I find the PCI SAQ? https: //www. pcisecuritystandards. org/pci_security /completing_self_assessment Which SAQ do I use? An Attestation of Compliance is a required part of the SAQ
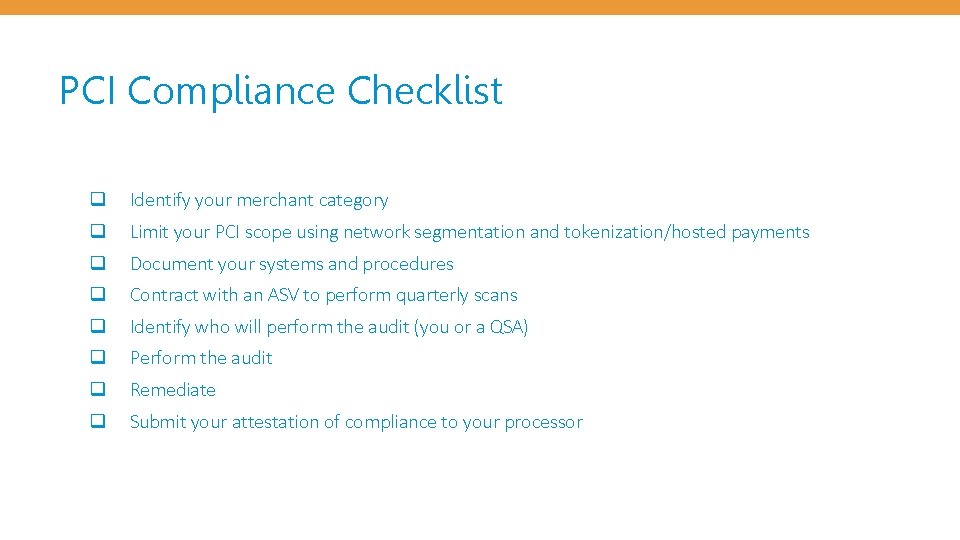
PCI Compliance Checklist q Identify your merchant category q Limit your PCI scope using network segmentation and tokenization/hosted payments q Document your systems and procedures q Contract with an ASV to perform quarterly scans q Identify who will perform the audit (you or a QSA) q Perform the audit q Remediate q Submit your attestation of compliance to your processor
Q&A Meredith Mitchell Partner Channel Manager, Charge. Logic mmitchell@chargelogic. com sales@chargelogic. com
PCI Resources PCI Security Standards Council Website https: //www. pcisecuritystandards. org/ PCI DSS v 3. 2 Requirements and Security Assessment Procedures https: //www. pcisecuritystandards. org/document_library? category=pcidss&document=pci_dss Payment Security Educational Resources https: //www. pcisecuritystandards. org/pci_security/educational_resources Validated Payment Applications https: //www. pcisecuritystandards. org/assessors_and_solutions/payment_applications? agree=true SAQs https: //www. pcisecuritystandards. org/document_library? category=saqs#results PCI Document Library https: //www. pcisecuritystandards. org/document_library TLS Migration https: //blog. pcisecuritystandards. org/are-you-ready-for-30 -june-2018 -sayin-goodbye-to-ssl-early-tls
- Slides: 41