
Microsoft Virtual Academy Free online technical courses Take
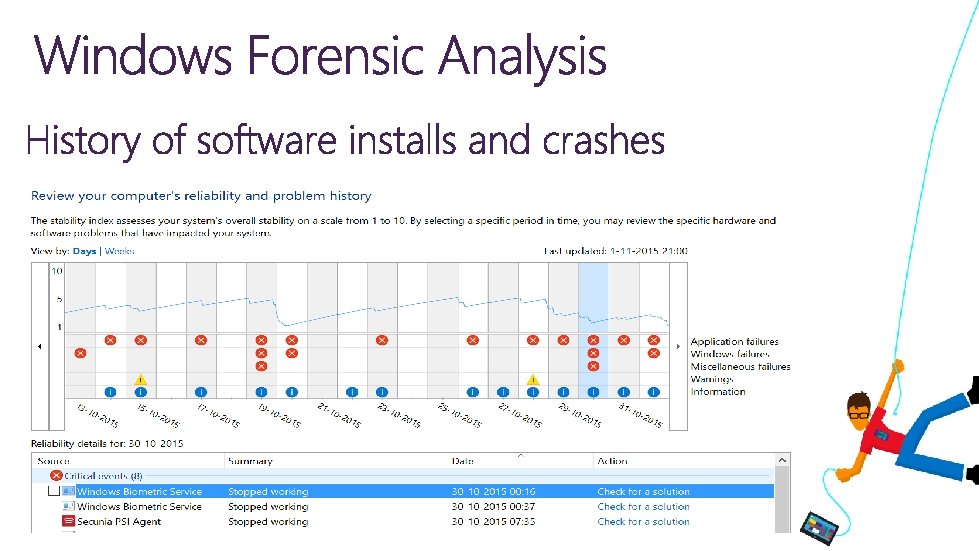
- Slides: 61
Microsoft Virtual Academy Free, online, technical courses Take a free online course. http: //www. microsoftvirtualacademy. com
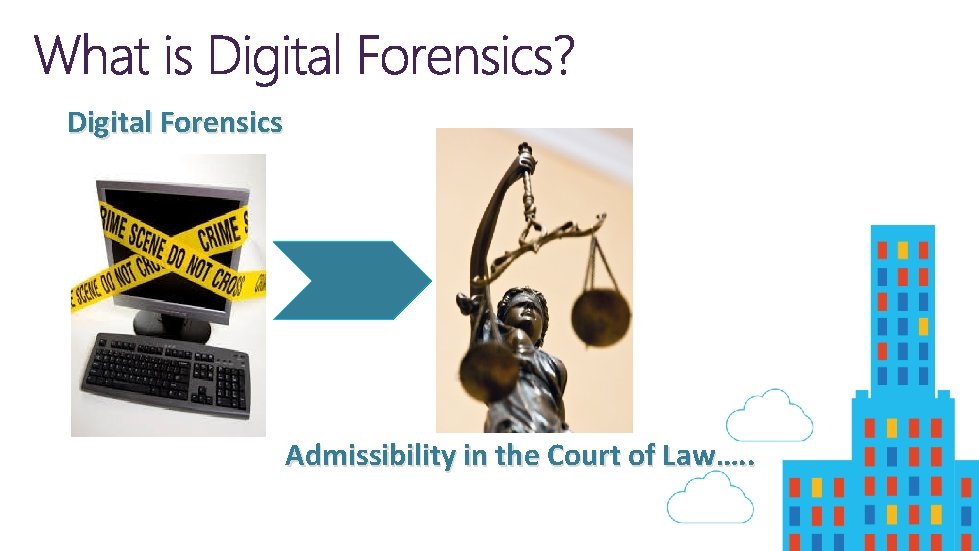
Digital Forensics Admissibility in the Court of Law…. .
§ Intrusion Analysis § Damage Assement § Suspect Examination § Tool Analysis § Log File Analysis § Evidence Search Data as seen by Forensic Investigators using his sophisticated toolkit. May include deleted data, hidden data, unauthorized information and records of illegal activity!
§ Who gained entry? § What did they do? § When did this happen? § Where did they go? § Why the chosen network? § How did they do this? Data as seen by Forensic Investigators using his sophisticated toolkit. May include deleted data, hidden data, unauthorized information and records of illegal activity!
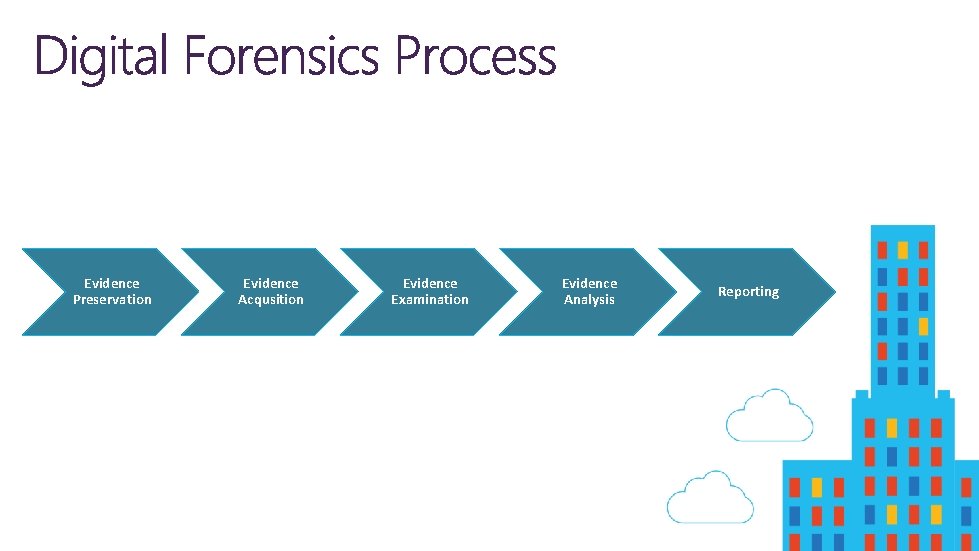
Evidence Preservation Evidence Acqusition Evidence Examination Evidence Analysis Reporting
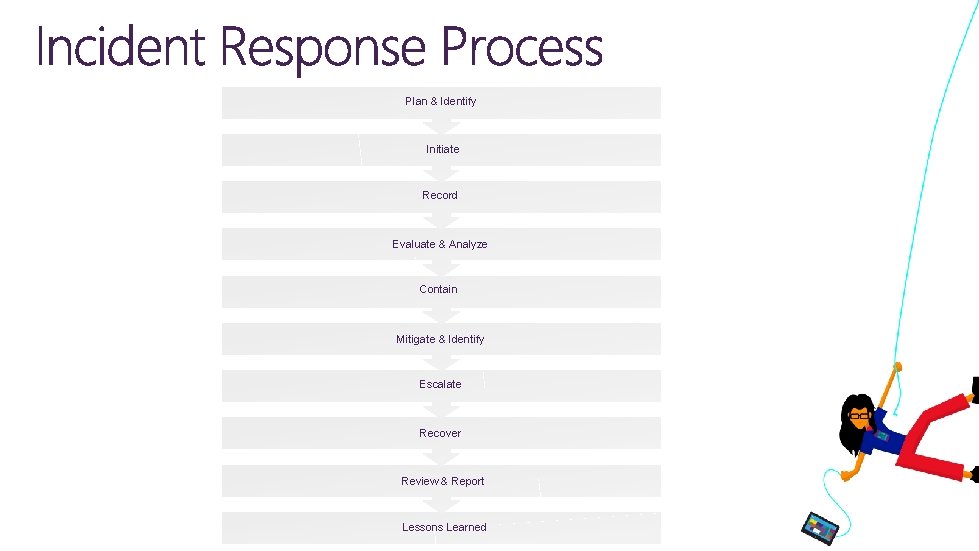
Plan & Identify Initiate Record Evaluate & Analyze Contain Mitigate & Identify Escalate Recover Review & Report Lessons Learned
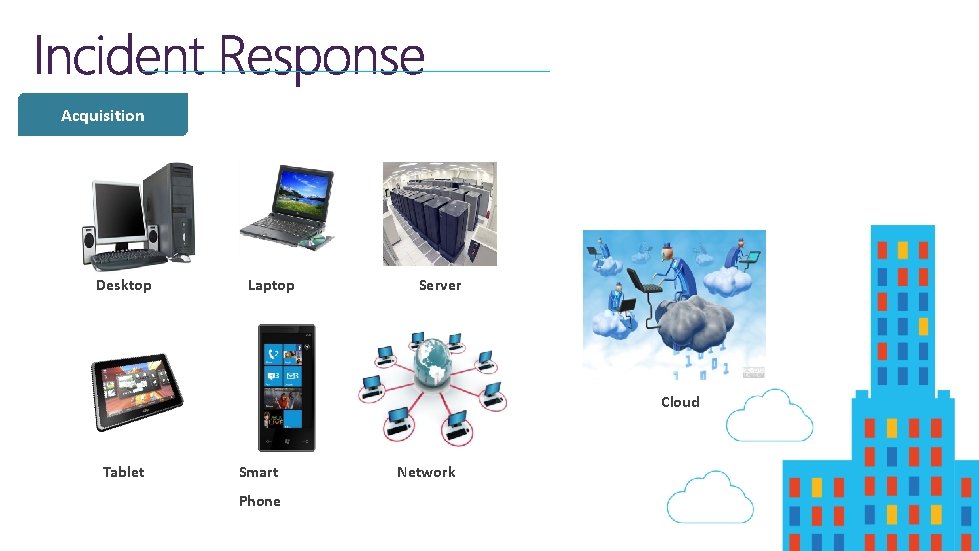
Acquisition Desktop Laptop Server Cloud Tablet Smart Phone Network
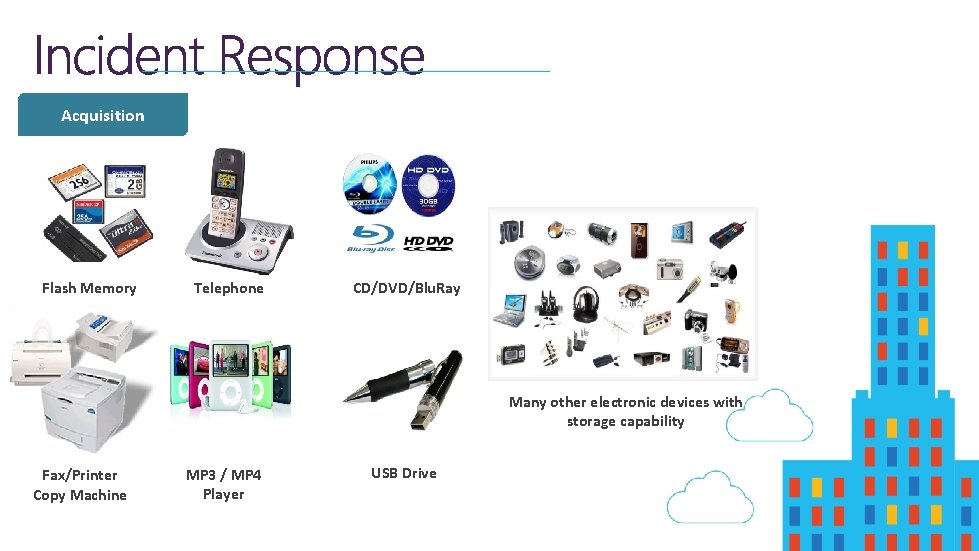
Acquisition Flash Memory Telephone CD/DVD/Blu. Ray Many other electronic devices with storage capability Fax/Printer Copy Machine MP 3 / MP 4 Player USB Drive
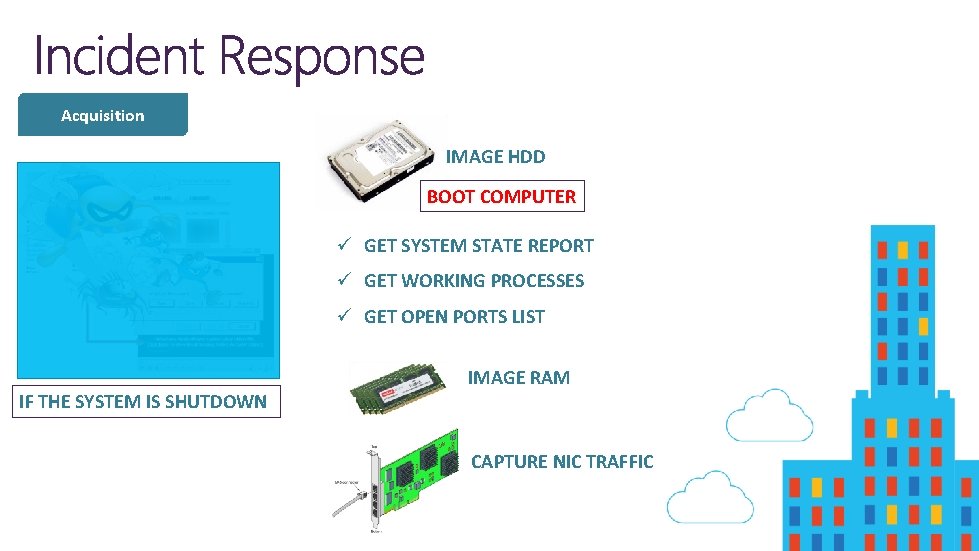
Acquisition IMAGE HDD BOOT COMPUTER ü GET SYSTEM STATE REPORT ü GET WORKING PROCESSES ü GET OPEN PORTS LIST IF THE SYSTEM IS SHUTDOWN IMAGE RAM CAPTURE NIC TRAFFIC
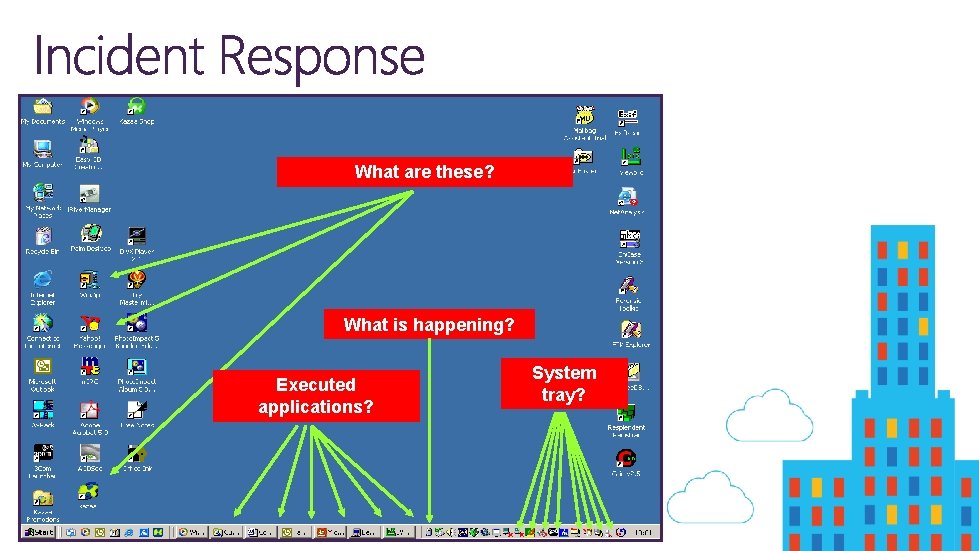
What are these? What is happening? Executed applications? System tray?
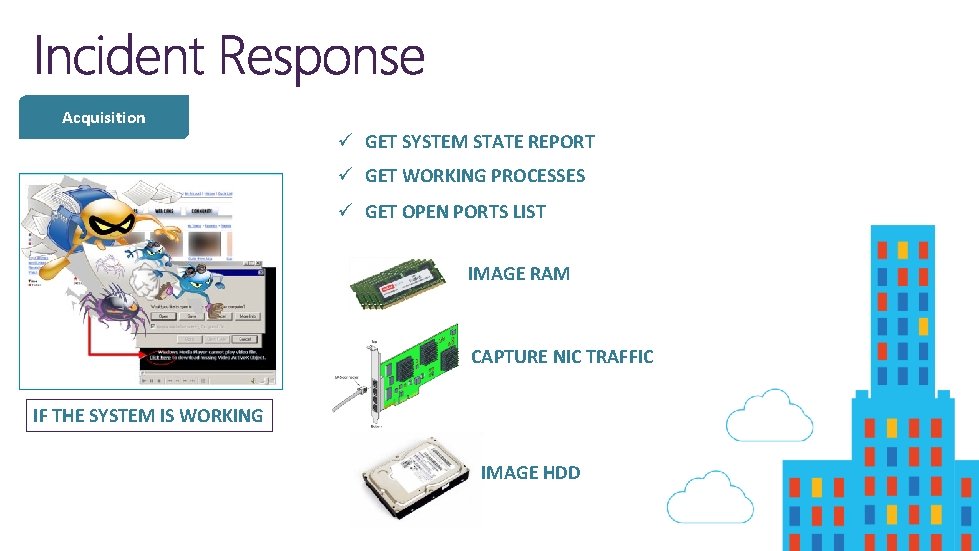
Acquisition ü GET SYSTEM STATE REPORT ü GET WORKING PROCESSES ü GET OPEN PORTS LIST IMAGE RAM CAPTURE NIC TRAFFIC IF THE SYSTEM IS WORKING IMAGE HDD
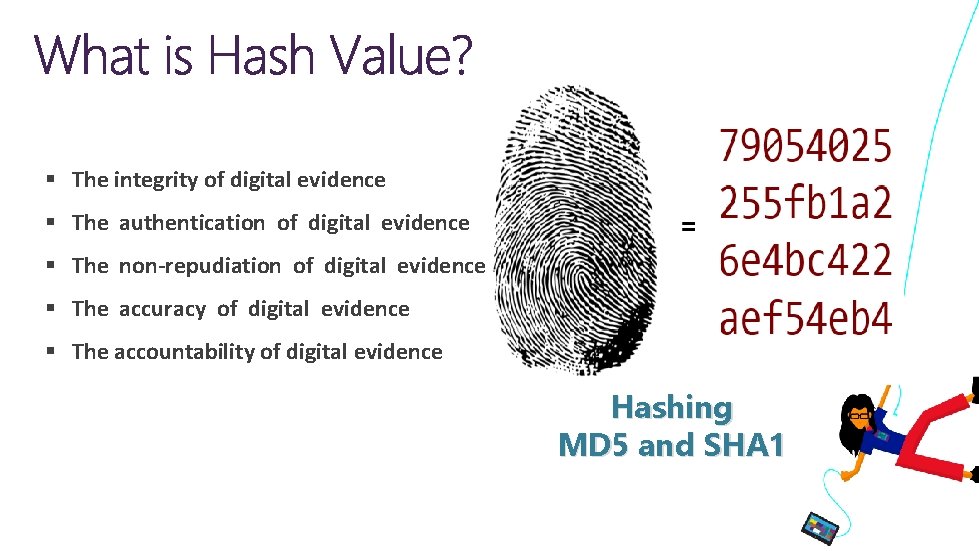
§ The integrity of digital evidence § The authentication of digital evidence § The non-repudiation of digital evidence § The accuracy of digital evidence § The accountability of digital evidence Hashing MD 5 and SHA 1
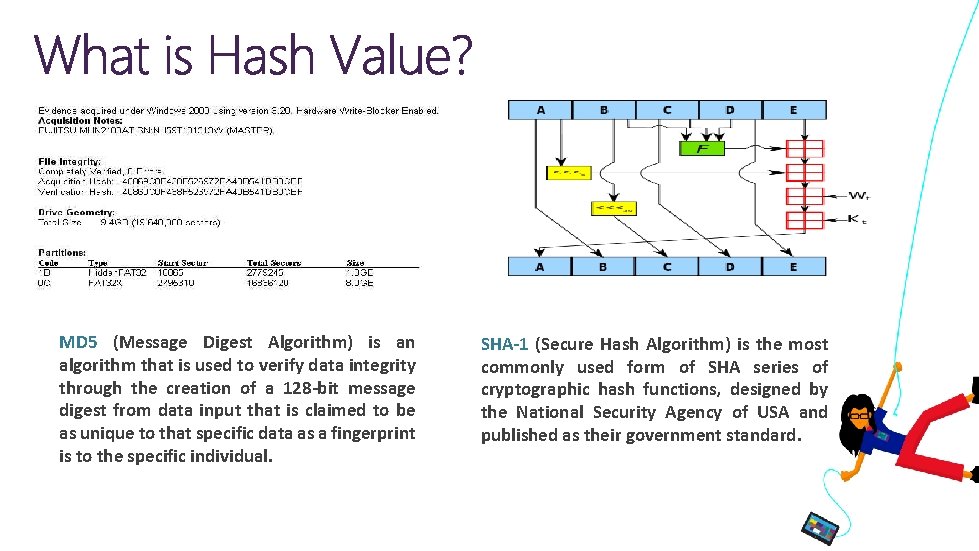
MD 5 (Message Digest Algorithm) is an algorithm that is used to verify data integrity through the creation of a 128 -bit message digest from data input that is claimed to be as unique to that specific data as a fingerprint is to the specific individual. SHA-1 (Secure Hash Algorithm) is the most commonly used form of SHA series of cryptographic hash functions, designed by the National Security Agency of USA and published as their government standard.
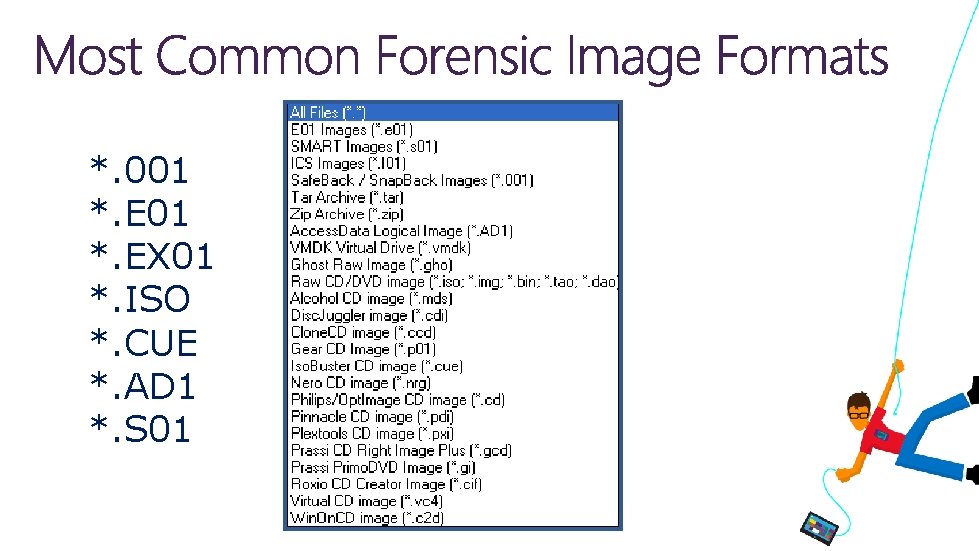
*. 001 *. EX 01 *. ISO *. CUE *. AD 1 *. S 01
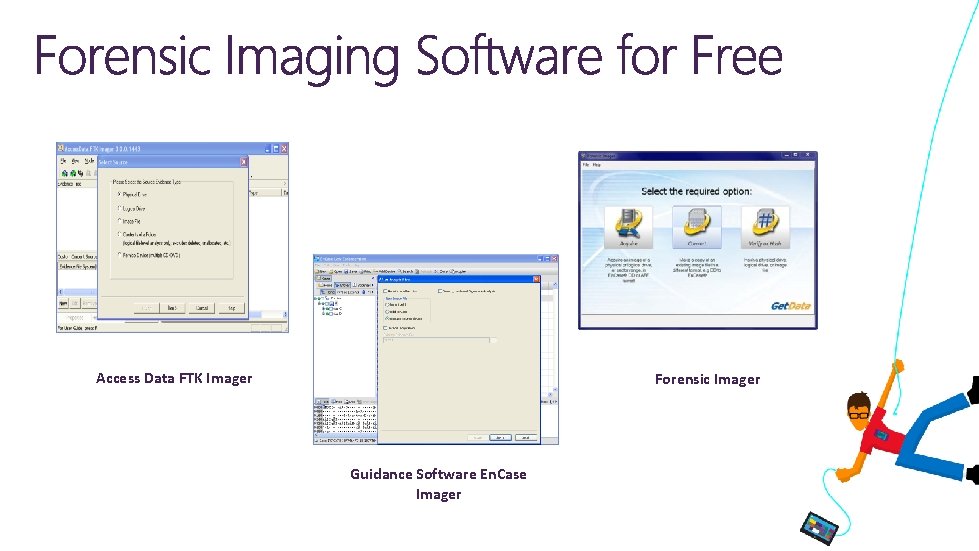
Access Data FTK Imager Forensic Imager Guidance Software En. Case Imager
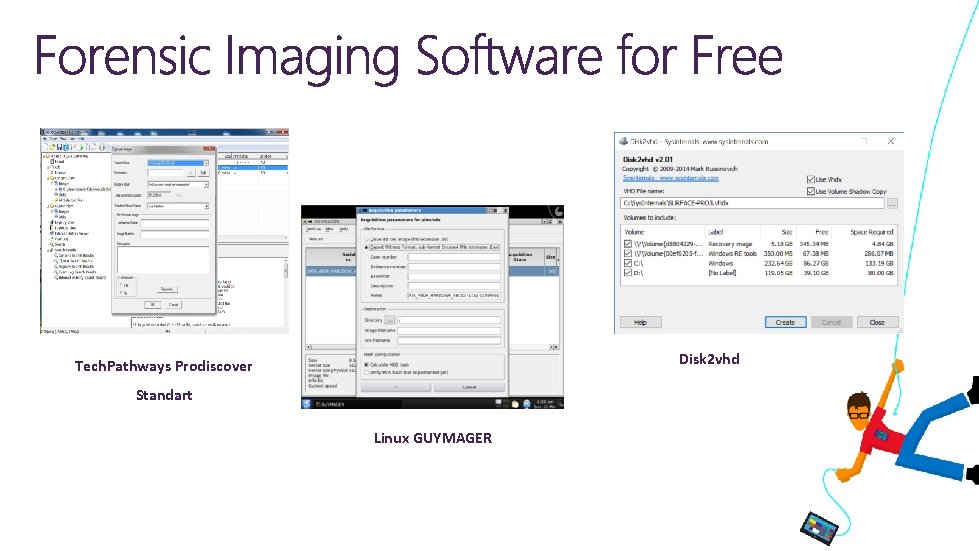
Disk 2 vhd Tech. Pathways Prodiscover Standart Linux GUYMAGER
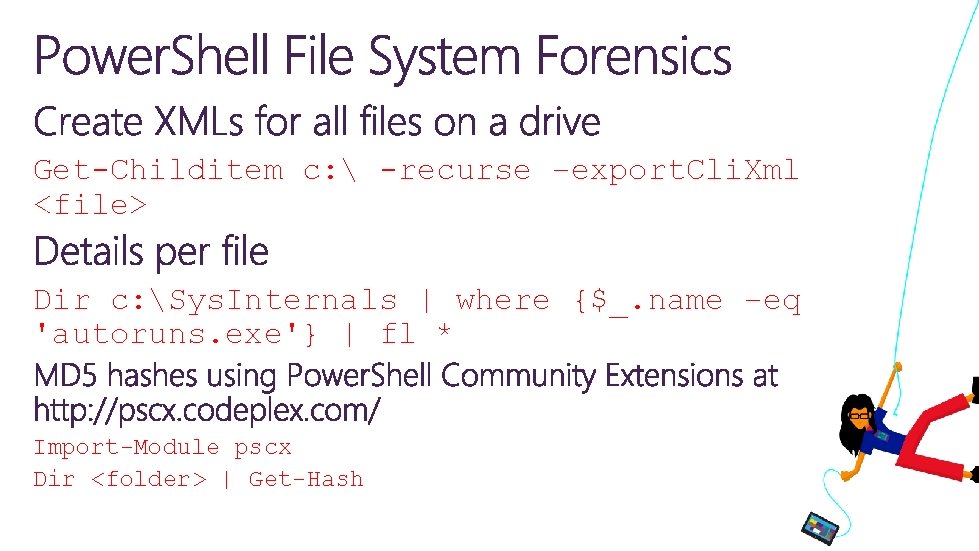
Get-Childitem c: -recurse –export. Cli. Xml <file> Dir c: Sys. Internals | where {$_. name –eq 'autoruns. exe'} | fl * Import-Module pscx Dir <folder> | Get-Hash
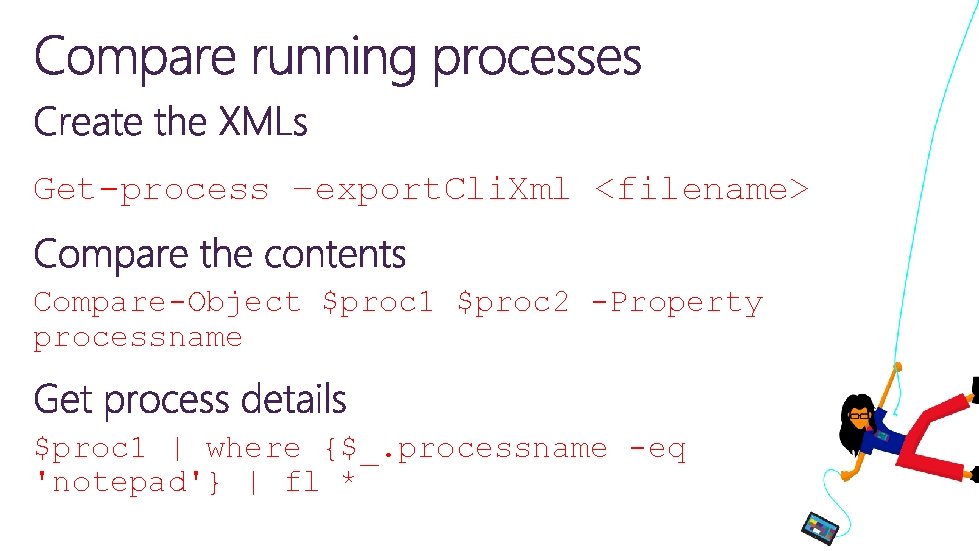
Get-process –export. Cli. Xml <filename> Compare-Object $proc 1 $proc 2 -Property processname $proc 1 | where {$_. processname -eq 'notepad'} | fl *
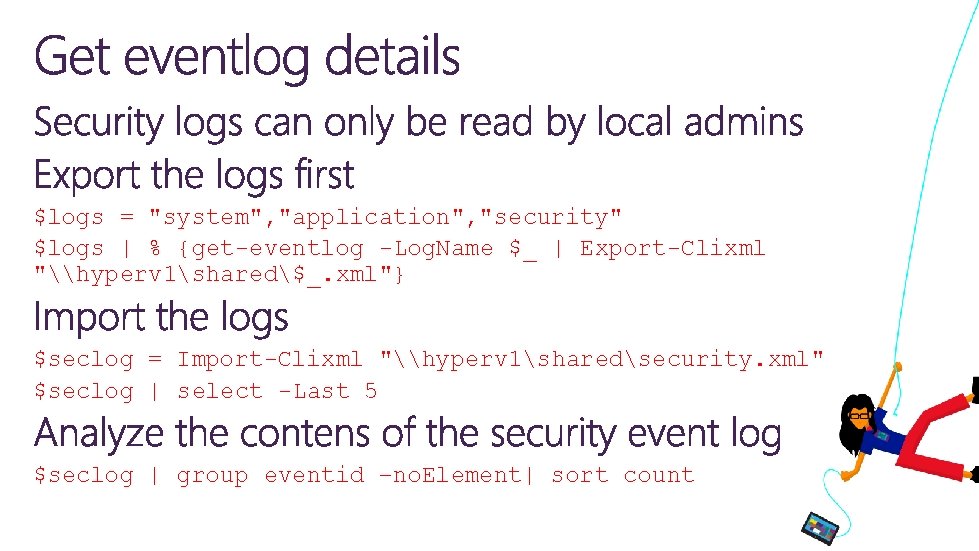
$logs = "system", "application", "security" $logs | % {get-eventlog -Log. Name $_ | Export-Clixml "\hyperv 1shared$_. xml"} $seclog = Import-Clixml "\hyperv 1sharedsecurity. xml" $seclog | select -Last 5 $seclog | group eventid –no. Element| sort count
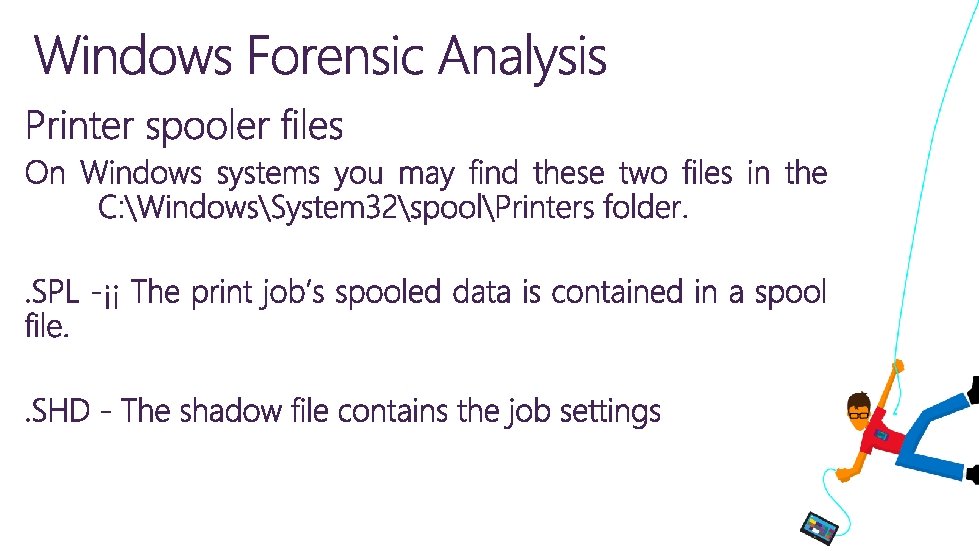
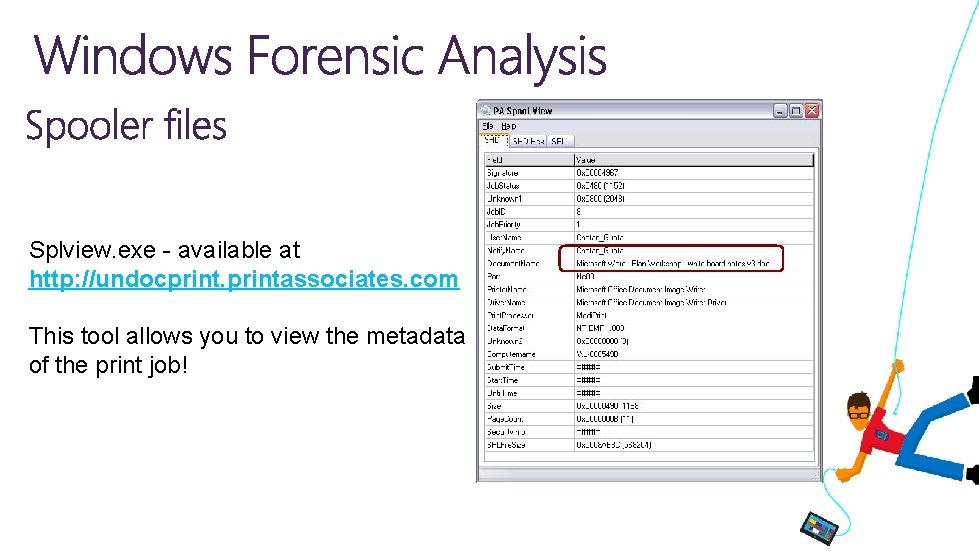
Splview. exe - available at http: //undocprintassociates. com This tool allows you to view the metadata of the print job!
ü Unauthorized access to SQL database server, admin password deleted and all user permissions are cleared. ü Information is retrieved. ü To protect the privacy of case, administration is informed. ü Digital Forensic Tools are prepared. ü During imaging of SQL server RAM and HDD’s, SQL server log files and event logs are deleted. And also other servers log files deleted too? ? ? INSIDER SUSPECT
ü 20 computers were imaged ü Totally 20 PC’s and 1 server and 1 RAM image files had to be whose owners were analyzed! working at IT department. How and where to start? Which methods do we have to use?
Edmond Locard’s Exchange Principle Core Principles A crime cannot occur without leaving a trace With contact between two items, there will be an exchange Every contact leaves a trace Evidence Dynamics…
Is there any one who deleted Windows event logs? ONLY ONE PERSON DELETED DEEP DIGITAL FORENSICS INVESTIGATION
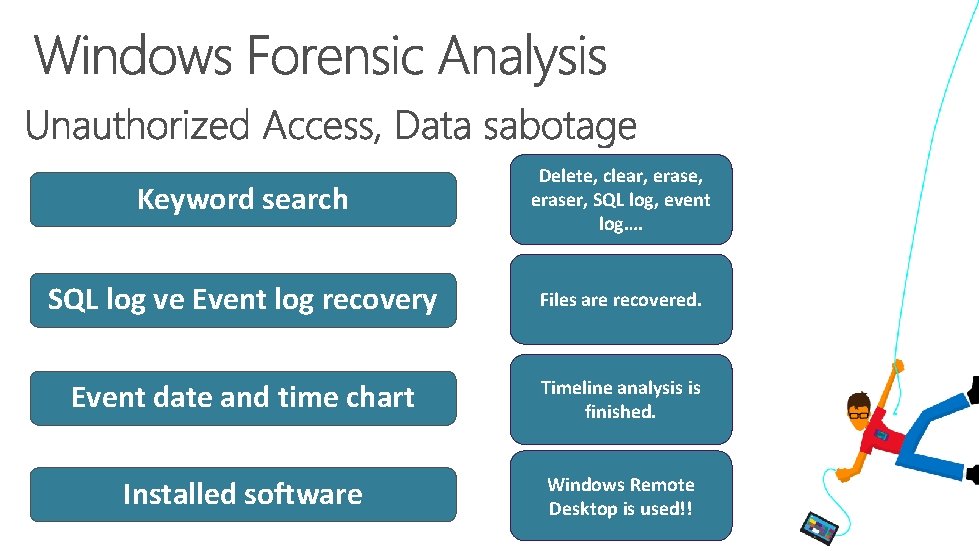
Keyword search Delete, clear, eraser, SQL log, event log…. SQL log ve Event log recovery Files are recovered. Event date and time chart Timeline analysis is finished. Installed software Windows Remote Desktop is used!!
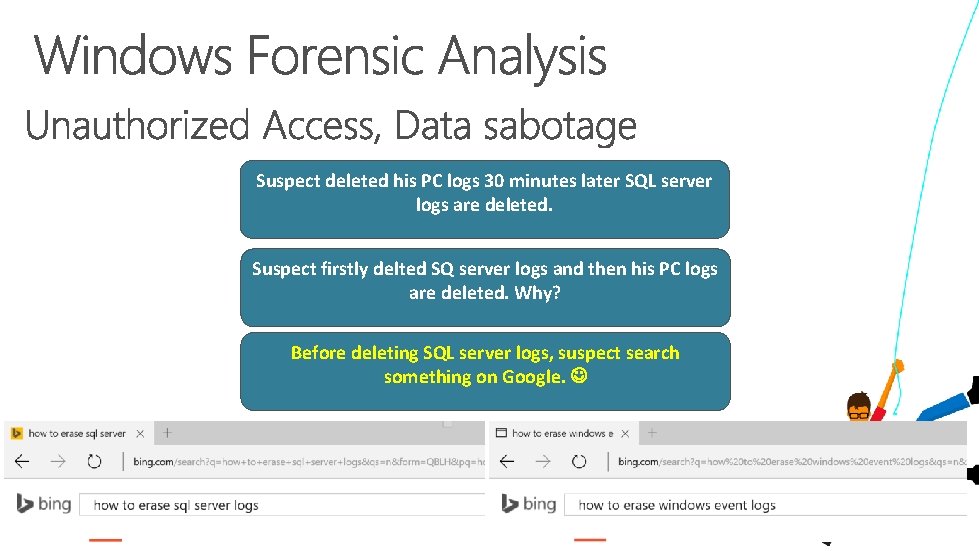
Suspect deleted his PC logs 30 minutes later SQL server logs are deleted. Suspect firstly delted SQ server logs and then his PC logs are deleted. Why? Before deleting SQL server logs, suspect search something on Google.
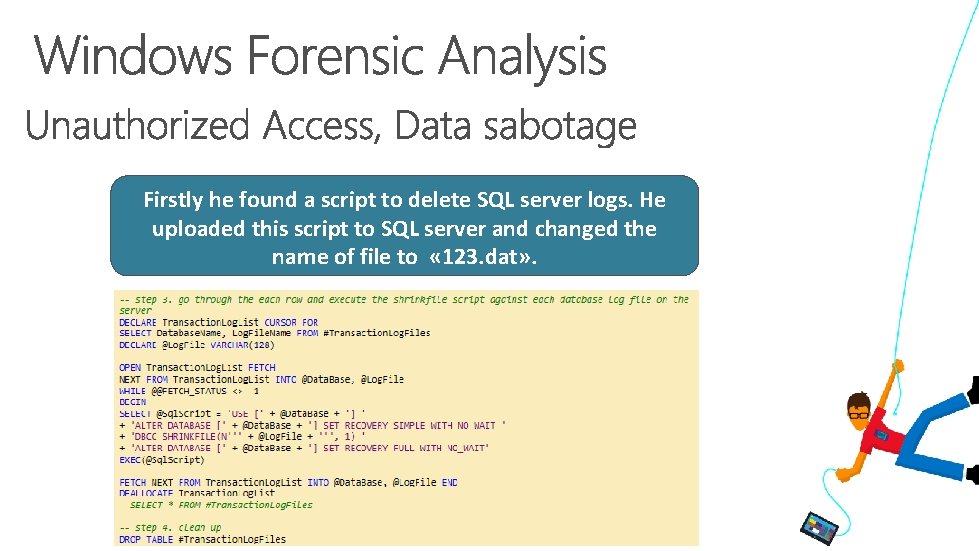
Firstly he found a script to delete SQL server logs. He uploaded this script to SQL server and changed the name of file to « 123. dat» .
SQL server logs are analyzed and there is an error belonging to a Canon mx 340 printer. The same error was occured the same date and time at suspect’s PC.
Named «Book 1. xls» MS Excel file is closed before saving at SQL server, and it made an error at the logs. The same error also occured at the same time at suspect’s PC?
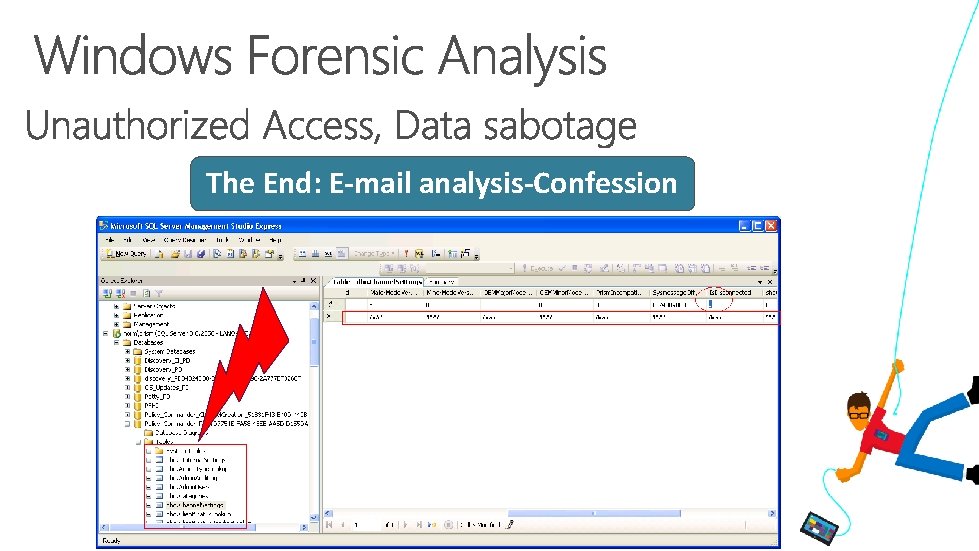
The End: E-mail analysis-Confession
Tech. Net Virtual Labs Deep technical content and free product evaluations Hands-on deep technical labs Free, online, technical courses Download Microsoftware trials today. Find Hand On Labs. Take a free online course. Technet. microsoft. com/evalcenter Technet. microsoft. com/virtuallabs microsoftvirtualacademy. com