
Marriott Breach Learn From One of the Largest
Marriott Breach – Learn From One of the Largest Breaches in History A brief research note for Info-Tech’s members. Info-Tech Research Group Inc. is a global leader in providing IT research and advice. Info-Tech’s products and services combine actionable insight and relevant advice with ready-to-use tools and templates that cover the full spectrum of IT concerns. © 1997 -2019 Info-Tech Research Group Inc. Info-Tech Research Group 1
FUTURE PERSPECTIVE The future of US privacy regulations? Until companies like Marriott feel the threat of multi-billion dollar fines, and jail-time for their senior executives, these companies won’t take privacy seriously. …It’s time for Congress to pass comprehensive consumer privacy and data security legislation that requires companies to adhere to strong data security standards, directs them to only collect the data they actually need to service their customer, and creates penalties for companies that fail to meet them. Ron Wyden, US Senator, Oregon Info-Tech Research Group 2

Timeline of Marriott/Starwood breach(s) The 2018 Marriott breach may be linked to a 2014 vulnerability in Starwood’s environment, disclosed shortly after acquisition was announced. 2014 Nov 2014 2016 2015 May 2015 Earliest date of Date that Starwood breach #1 #1 was assumed to have been remediated Nov 2015 Announcement of Marriott’s acquisition of Starwoods Sept 2016 Marriott’s acquisition of Starwood was finalized Disclosure of Starwoods breach #1 assumed to have ended in May 2015 2017 2018 Sept 8 Marriott was alerted that a database was trying to be accessed Nov 2018 Investigation determined that unauthorized access to the database had occurred Sept 10 Information used to make reservations on or before this date may be compromised Source: Krebs Security Info-Tech Research Group 3

What we know about the breach Despite a lack of intel, there are four main things we’ve learned about the Marriott breach: 01 Three private investigators have indicated that clues in the breach link it to a nation-state attack from somewhere in Asia. However, these sources have not been verified by Marriott or the US government. 02 Attackers accessed the data via a database containing guest information. They’ve been inside the Marriott network since 2014. 03 Marriott has NOT disclosed how the attackers gained access to its network. Experts have hypothesized it was via a phishing attempt. 04 To avoid data loss prevention tools, the attackers encrypted and exfiltrated the data (including credit card numbers). It is likely they also had access to the encryption keys. Info-Tech Research Group 4

Who was impacted? Anyone who previously made a reservation at a Starwood hotel on or before September 10, 2018. (as far back as 2014) 500 MILLION PEOPLE 170 million Basic information was lost: • Name • Mailing address • Phone number • Email address Source: Marriott, Wired 327 million Valuable information was lost: • Name • Passport number • Encrypted credit card information • Date of birth • Gender • Mailing address • Phone number • Email address • Arrival and departure information • Reservation date(s) • Communication preferences • Starwood Preferred Guest (SPG) account information What hotel brands are included? Aloft Hotels Element Hotels Four Points by Sheraton Le Méridien Hotels & Resorts Sheraton Hotels & Resorts St. Regis The Luxury Collection Tribute Portfolio W Hotels Westin Hotels & Resorts Design Hotels (that participate in the SPG program) Other Starwood-branded timeshare properties: • Sheraton Vacation Club • St. Regis Residence Club • The Luxury Collection Residence Club • Vistana • Westin Vacation Club Info-Tech Research Group 5
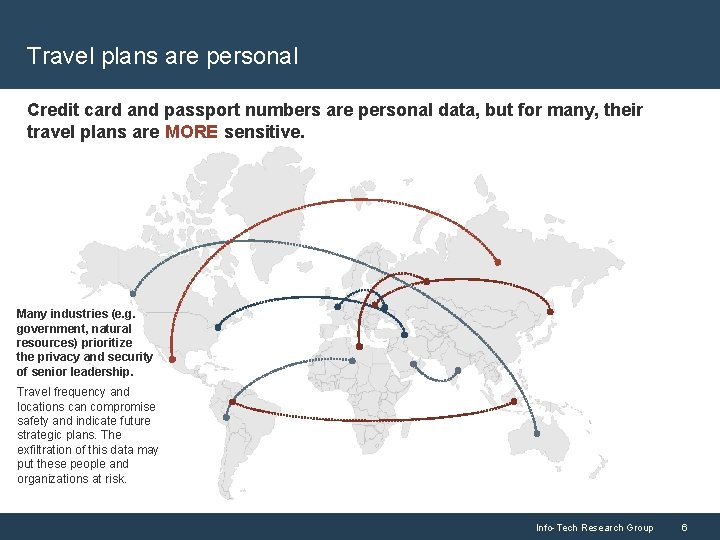
Travel plans are personal Credit card and passport numbers are personal data, but for many, their travel plans are MORE sensitive. Many industries (e. g. government, natural resources) prioritize the privacy and security of senior leadership. Travel frequency and locations can compromise safety and indicate future strategic plans. The exfiltration of this data may put these people and organizations at risk. Info-Tech Research Group 6

Specific Marriott breach considerations Has your organization experienced an M&A within the last five years? What is the likelihood that your organization is a target for international attackers and nation states? Has your organization considered (and complied with) your regulatory requirements? Marriott’s acquisition of Starwood Hotels was a strategic venture that has continually proven to be a cause of information security and IT issues. Marriott may not appear to be a standard target for an attack. However, with a global presence, millions of records, and sensitive travel plans – its data provides value for attackers. Marriott’s incident response indicates it is striving for GDPR compliance. This regulation may have been the catalyst for the timely disclosure. All data breaches can help re-educate and re-affirm the importance of information security. Move to the next slide to learn more about the critical elements required to prepare for a breach. Info-Tech Research Group 7

The Marriott breach is unique in size, but consistent in security program essentials The following are staple requirements for preparing for a data breach. Formal incident response Effective monitoring & detection Example documentation includes the following: Have the right-sized capabilities to detect and respond to any event. Understand what events must be escalated to incidents based on criteria (e. g. access levels, data type, log patterns). • Incident type playbooks • Escalation protocol for non-IT stakeholders • Policy documentation • Tabletop exercises Leadership training for metrics reporting Implement leadership training for critical stakeholders to understand security terminology, and thus, risks. Information security educated boards will better interpret metrics. Data backups Implement and test backups frequently to ensure minimal downtime. Validate that retention schedules meet regulatory requirements and align to executed backups. Sound understanding of all regulatory requirements Including: • State requirements • International regulations (GDPR) • Industry frameworks A superior M&A process A robust due diligence process (including integrated security testing) with a known go/no-go point, segregation of environments, and an integration plan. Info-Tech Research Group 8
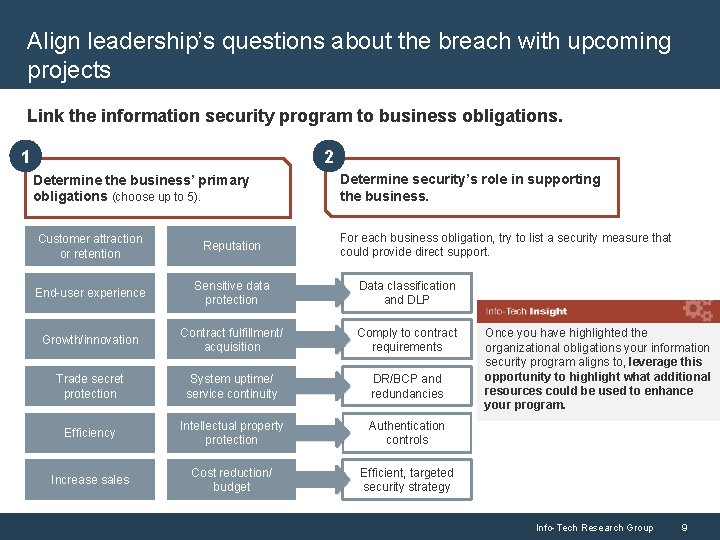
Align leadership’s questions about the breach with upcoming projects Link the information security program to business obligations. 1 2 Determine the business’ primary obligations (choose up to 5). Determine security’s role in supporting the business. For each business obligation, try to list a security measure that could provide direct support. Customer attraction or retention Reputation End-user experience Sensitive data protection Data classification and DLP Growth/innovation Contract fulfillment/ acquisition Comply to contract requirements Trade secret protection System uptime/ service continuity DR/BCP and redundancies Efficiency Intellectual property protection Authentication controls Increase sales Cost reduction/ budget Efficient, targeted security strategy Once you have highlighted the organizational obligations your information security program aligns to, leverage this opportunity to highlight what additional resources could be used to enhance your program. Info-Tech Research Group 9
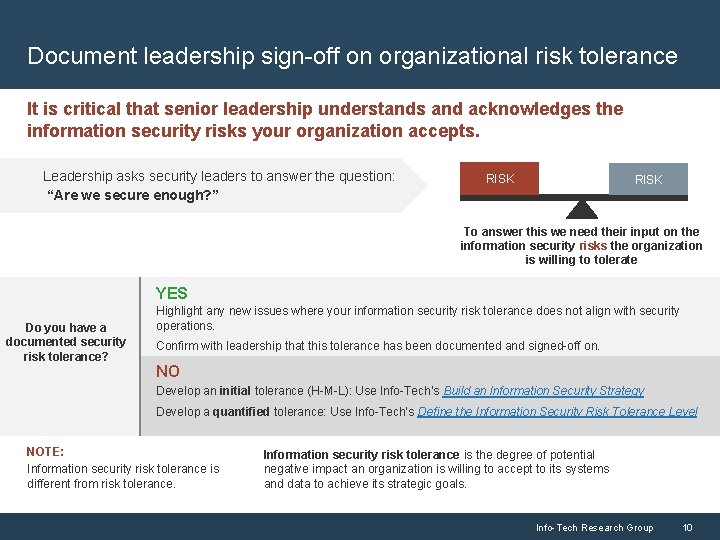
Document leadership sign-off on organizational risk tolerance It is critical that senior leadership understands and acknowledges the information security risks your organization accepts. Leadership asks security leaders to answer the question: “Are we secure enough? ” RISK To answer this we need their input on the information security risks the organization is willing to tolerate YES Do you have a documented security risk tolerance? Highlight any new issues where your information security risk tolerance does not align with security operations. Confirm with leadership that this tolerance has been documented and signed-off on. NO Develop an initial tolerance (H-M-L): Use Info-Tech’s Build an Information Security Strategy Develop a quantified tolerance: Use Info-Tech’s Define the Information Security Risk Tolerance Level NOTE: Information security risk tolerance is different from risk tolerance. Information security risk tolerance is the degree of potential negative impact an organization is willing to accept to its systems and data to achieve its strategic goals. Info-Tech Research Group 10

What to do if you may have been impacted Assume that credit card information has been accessed. Booking information, including encrypted credit numbers have been exfiltrated. Marriott has not reported on encryption keys exfiltration. However, the extent and length of breach suggests that attackers likely accessed these keys. Credit card information: 1 Review your credit card statement. Check your accounts for fraudulent activity that may have been missed. 2 Alert your credit card company. Notify your credit card company and request a new credit card number. 3 Establish credit monitoring. Example services: Equifax’s Trusted. ID and Credit. Karma. 4 Freeze your credit. If you are particularly concerned, consider requesting a credit freeze to prevent any new credit from being established without your consent. Other information: 1 Continually visit Starwood’s information site. Marriott International has established an information website and call center to help answer guest questions. 2 Establish identity monitoring. Marriott is offering guests a free one-year subscription to Web. Watcher, which monitors websites and alerts guests when their information is detected. 3 Monitor non-financial accounts. Your information may be used for other purposes such as targeted phishing attempts. Remember to monitor your Starwood Preferred Guest membership for any suspicious activity, such as reward points being used. Alert Marriott immediately if you see this occurring. Info-Tech Research Group 11
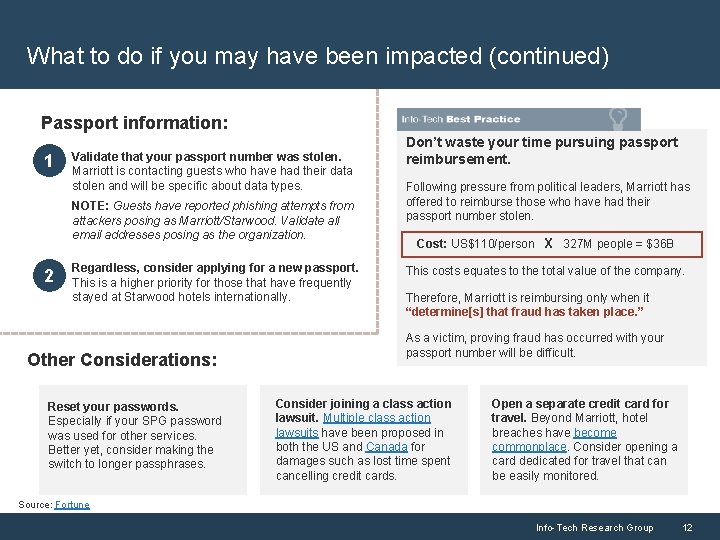
What to do if you may have been impacted (continued) Passport information: 1 Validate that your passport number was stolen. Marriott is contacting guests who have had their data stolen and will be specific about data types. NOTE: Guests have reported phishing attempts from attackers posing as Marriott/Starwood. Validate all email addresses posing as the organization. 2 Regardless, consider applying for a new passport. This is a higher priority for those that have frequently stayed at Starwood hotels internationally. Other Considerations: Reset your passwords. Especially if your SPG password was used for other services. Better yet, consider making the switch to longer passphrases. Don’t waste your time pursuing passport reimbursement. Following pressure from political leaders, Marriott has offered to reimburse those who have had their passport number stolen. Cost: US$110/person X 327 M people = $36 B This costs equates to the total value of the company. Therefore, Marriott is reimbursing only when it “determine[s] that fraud has taken place. ” As a victim, proving fraud has occurred with your passport number will be difficult. Consider joining a class action lawsuit. Multiple class action lawsuits have been proposed in both the US and Canada for damages such as lost time spent cancelling credit cards. Open a separate credit card for travel. Beyond Marriott, hotel breaches have become commonplace. Consider opening a card dedicated for travel that can be easily monitored. Source: Fortune Info-Tech Research Group 12

Use this opportunity to conduct a security program evaluation Leverage Info-Tech’s various security blueprints: Develop and Implement a Security Incident Management Program Master Your Security Incident Response Communications Program Fast Track Your GDPR Compliance Efforts Integrate Threat Intelligence Into Your Security Operations Humanize the Security Awareness & Training Program Effective information security management will help you: Enhance your organizational security posture • Reduced risk • Enhanced compliance management • Improved organizational situational awareness Create and clarify accountability and responsibility • Formalized role and process responsibility • Enhanced internal and external communication Control security costs • Reduced incidents • Streamlined security operations processes • Aligned strategy Identify opportunities for improvement • Defined measurement programs • Defined opportunities for continuous improvement Improve threat protection • Built intelligence-driven security operations process • Optimized patch management program • Improved effectiveness of internal controls • Standardized operational use cases Info-Tech Research Group 13
- Slides: 13