
Managing Cyber Risk by applying AI to automate
Managing Cyber Risk by applying AI to automate threat hunting DARREN GALE, SENIOR DIRECTOR, HIGH GROWTH MARKETS © Vectra | vectra. ai
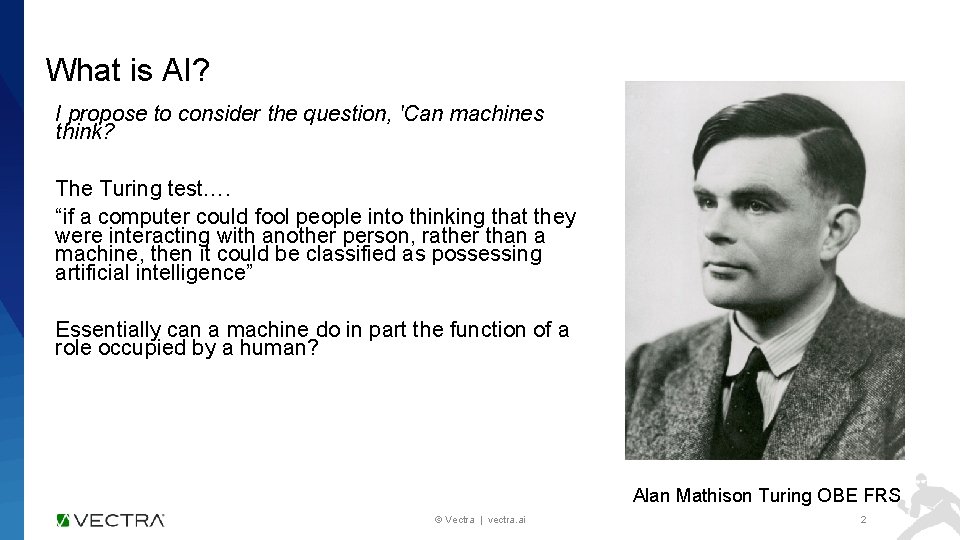
What is AI? I propose to consider the question, 'Can machines think? The Turing test…. “if a computer could fool people into thinking that they were interacting with another person, rather than a machine, then it could be classified as possessing artificial intelligence” Essentially can a machine do in part the function of a role occupied by a human? Alan Mathison Turing OBE FRS © Vectra | vectra. ai 2
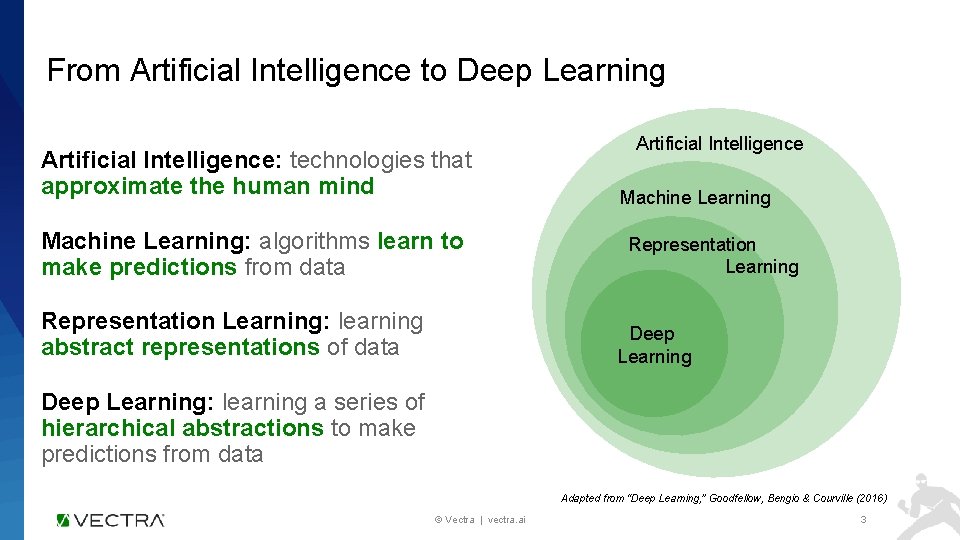
From Artificial Intelligence to Deep Learning Artificial Intelligence: technologies that approximate the human mind Machine Learning: algorithms learn to make predictions from data Representation Learning: learning abstract representations of data Artificial Intelligence Machine Learning Representation Learning Deep Learning: learning a series of hierarchical abstractions to make predictions from data Adapted from “Deep Learning, ” Goodfellow, Bengio & Courville (2016) © Vectra | vectra. ai 3
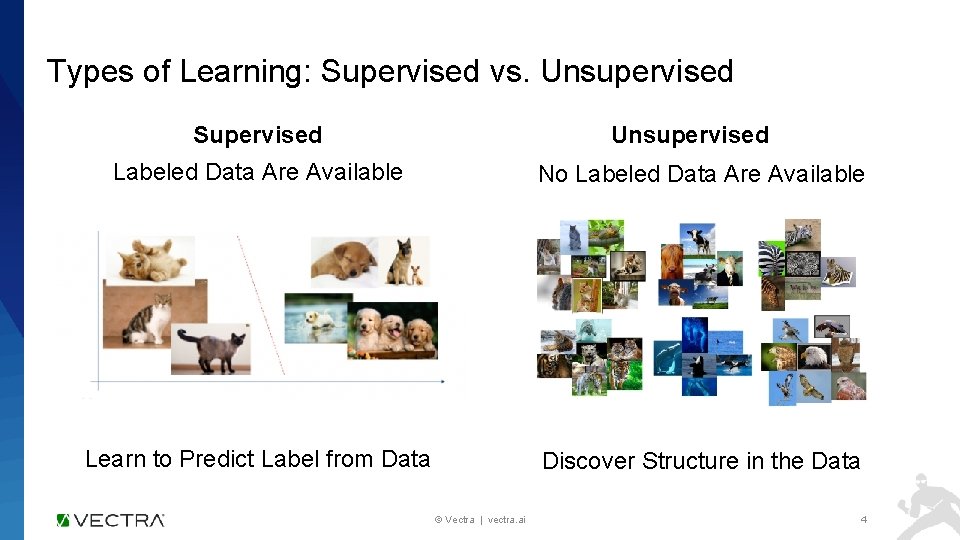
Types of Learning: Supervised vs. Unsupervised Supervised Labeled Data Are Available No Labeled Data Are Available Learn to Predict Label from Data Discover Structure in the Data © Vectra | vectra. ai 4
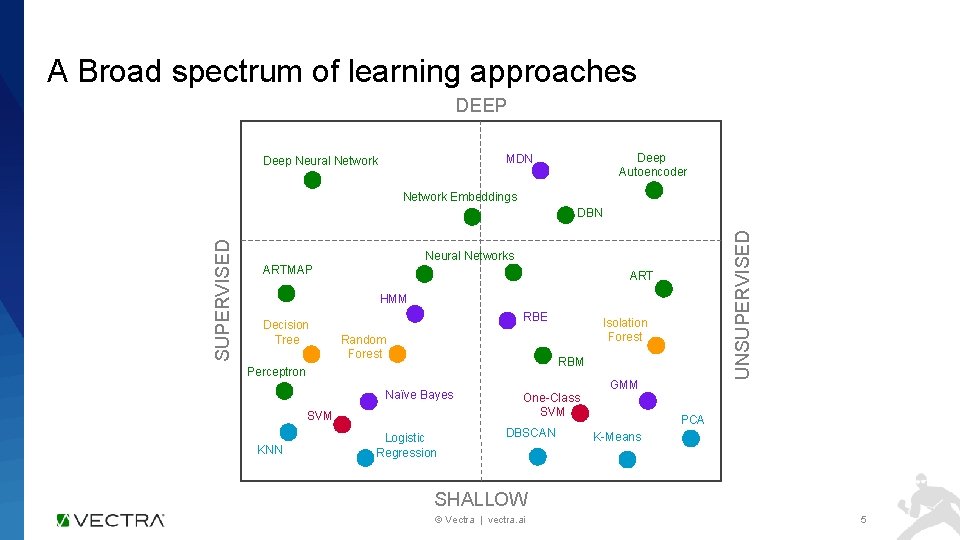
A Broad spectrum of learning approaches DEEP Deep Autoencoder MDN Deep Neural Network Embeddings UNSUPERVISED DBN Neural Networks ARTMAP ART HMM Decision Tree RBE Random Forest RBM Perceptron Naïve Bayes SVM KNN Isolation Forest Logistic Regression One-Class SVM DBSCAN GMM PCA K-Means SHALLOW © Vectra | vectra. ai 5
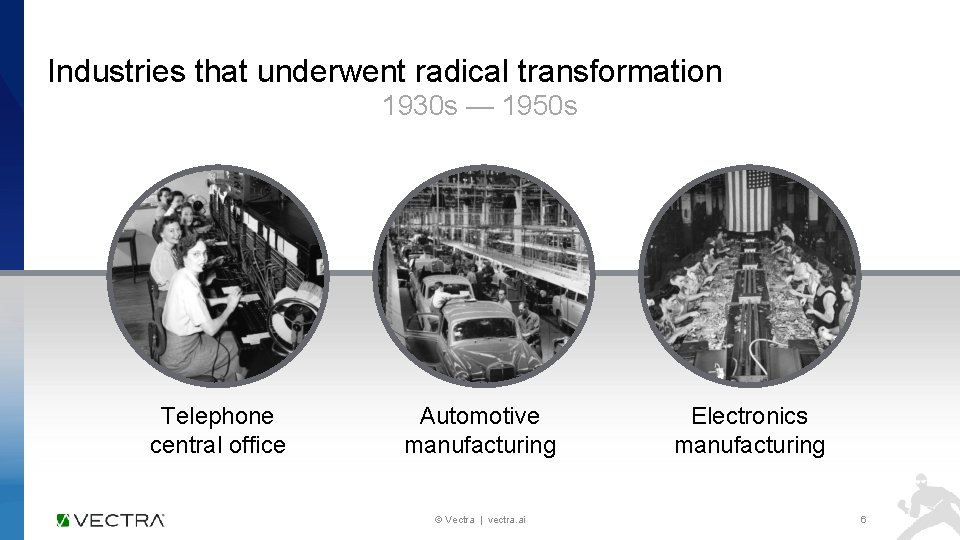
Industries that underwent radical transformation 1930 s — 1950 s Telephone central office Automotive manufacturing © Vectra | vectra. ai Electronics manufacturing 6
Would this have felt like AI? Telephone central office Automotive manufacturing © Vectra | vectra. ai Electronics manufacturing 7
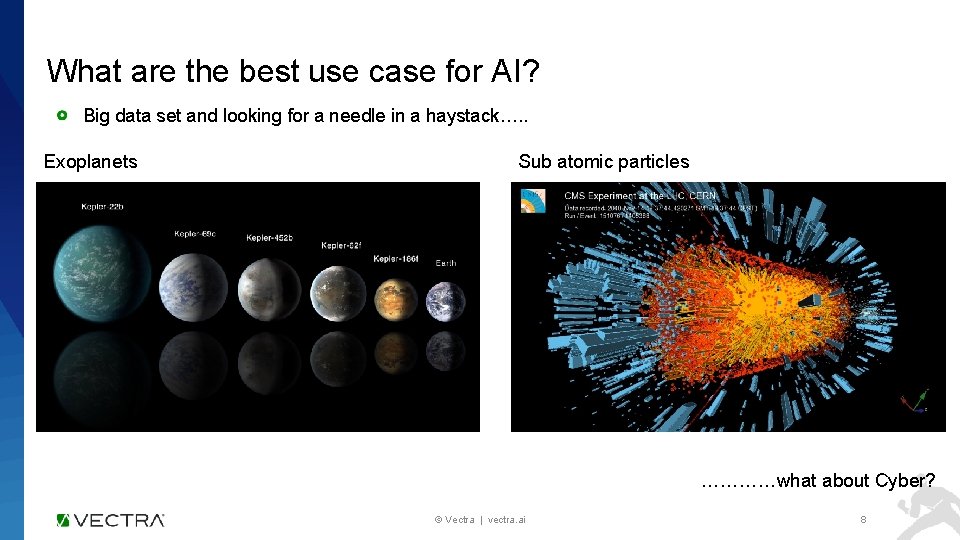
What are the best use case for AI? Big data set and looking for a needle in a haystack…. . Exoplanets Sub atomic particles …………what about Cyber? © Vectra | vectra. ai 8
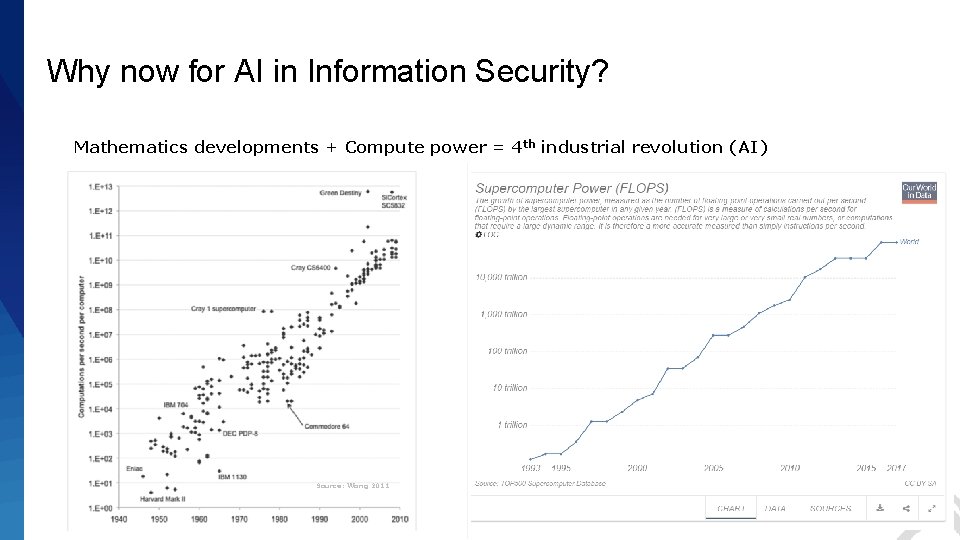
Why now for AI in Information Security? Mathematics developments + Compute power = 4 th industrial revolution (AI) Naive Bayes has been studied extensively since the 1950 s. Lloyd, S. P. (1957). "Least square quantization in PCM" Quadratic Classifier – 1965 Paper by TM Cover 1986 “Induction of Decision trees” – regression tree development, Quinlan, J. R Richard Sutton (1988). "Learning to predict by the methods of temporal differences” Deep learning - Gradient-based learning applied to document recognition 1988 The first algorithm for random decision forests by Tin Kam Ho 1995 Frey & Dueck (2007). "Clustering by passing messages between data points" Source: Wong 2011 © Vectra | vectra. ai 9

1 2 Signatures cannot detect skilled adversaries. Cybersecurity skill gap → Manual hunting alone won’t work. >350, 000 unfilled European cybersecurity jobs than candidates by 2022* © Vectra | vectra. ai 10
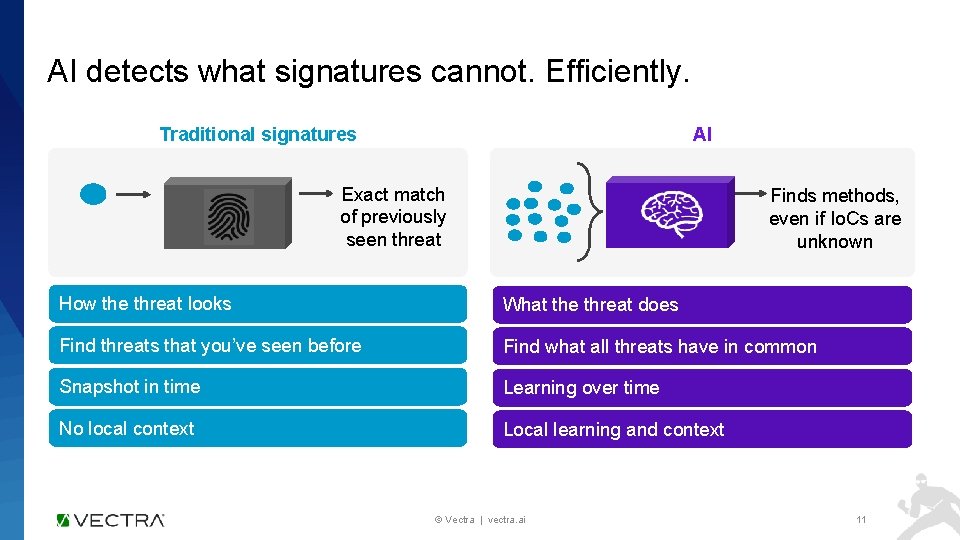
AI detects what signatures cannot. Efficiently. Traditional signatures AI Exact match of previously seen threat Finds methods, even if Io. Cs are unknown How the threat looks What the threat does Find threats that you’ve seen before Find what all threats have in common Snapshot in time Learning over time No local context Local learning and context © Vectra | vectra. ai 11
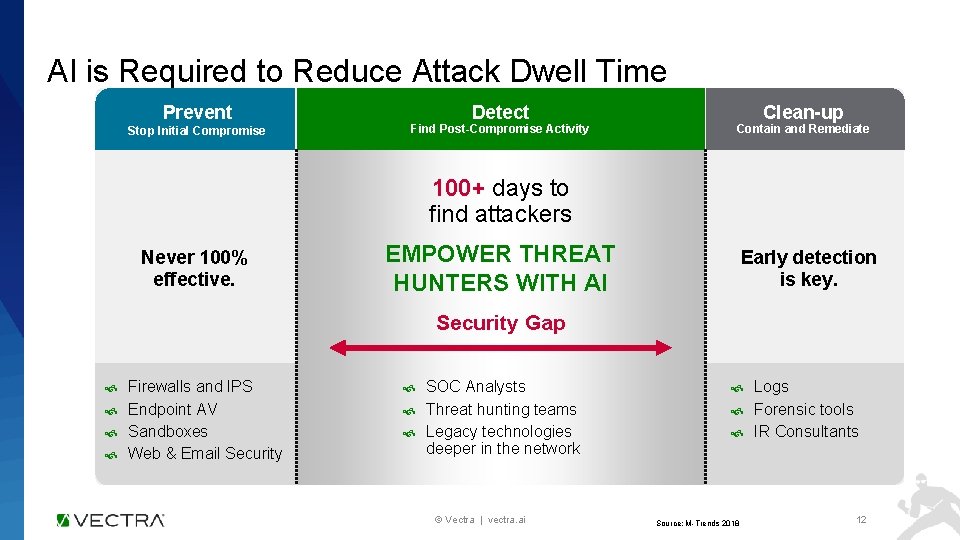
AI is Required to Reduce Attack Dwell Time Prevent Stop Initial Compromise Detect Find Post-Compromise Activity Clean-up Contain and Remediate 100+ days to find attackers Never 100% effective. EMPOWER THREAT HUNTERS WITH AI Early detection is key. Security Gap Firewalls and IPS Endpoint AV Sandboxes Web & Email Security SOC Analysts Threat hunting teams Legacy technologies deeper in the network © Vectra | vectra. ai Logs Forensic tools IR Consultants Source: M-Trends 2018 12
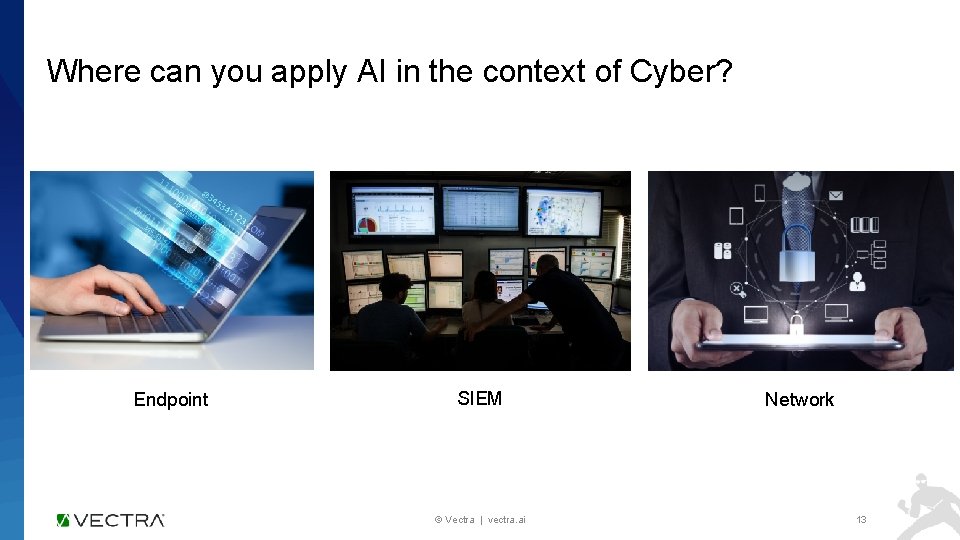
Where can you apply AI in the context of Cyber? Endpoint SIEM © Vectra | vectra. ai Network 13
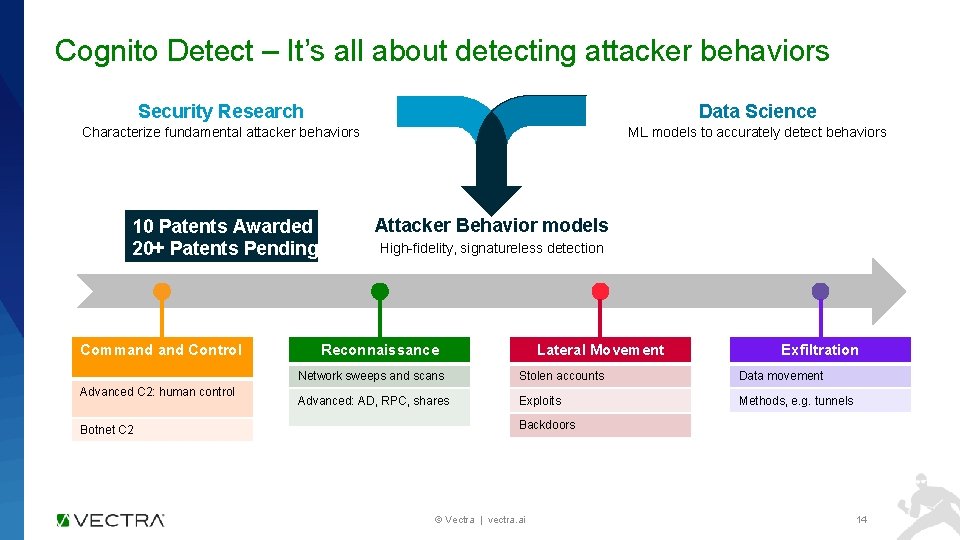
Cognito Detect – It’s all about detecting attacker behaviors Security Research Data Science Characterize fundamental attacker behaviors ML models to accurately detect behaviors 10 Patents Awarded 20+ Patents Pending Command Control Advanced C 2: human control Botnet C 2 Attacker Behavior models High-fidelity, signatureless detection Reconnaissance Lateral Movement Exfiltration Network sweeps and scans Stolen accounts Data movement Advanced: AD, RPC, shares Exploits Methods, e. g. tunnels Backdoors © Vectra | vectra. ai 14
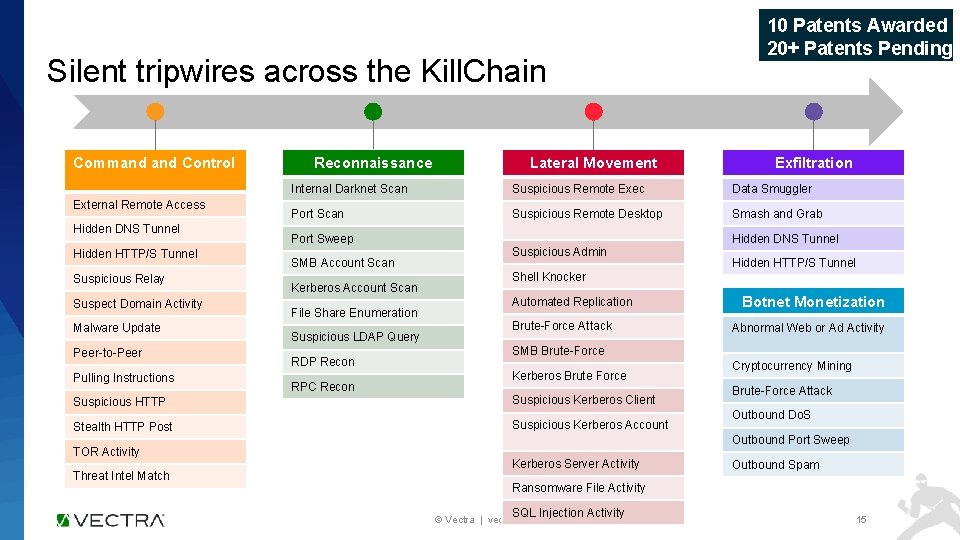
Silent tripwires across the Kill. Chain Command Control External Remote Access Hidden DNS Tunnel Hidden HTTP/S Tunnel Suspicious Relay Suspect Domain Activity Malware Update Peer-to-Peer Pulling Instructions Reconnaissance Lateral Movement Suspicious Remote Exec Data Smuggler Port Scan Suspicious Remote Desktop Smash and Grab Port Sweep SMB Account Scan Kerberos Account Scan File Share Enumeration Suspicious LDAP Query RDP Recon RPC Recon Hidden DNS Tunnel Suspicious Admin Hidden HTTP/S Tunnel Shell Knocker Automated Replication Brute-Force Attack Botnet Monetization Abnormal Web or Ad Activity SMB Brute-Force Kerberos Brute Force Suspicious Kerberos Client Stealth HTTP Post Suspicious Kerberos Account Threat Intel Match Exfiltration Internal Darknet Scan Suspicious HTTP TOR Activity 10 Patents Awarded 20+ Patents Pending Cryptocurrency Mining Brute-Force Attack Outbound Do. S Outbound Port Sweep Kerberos Server Activity Outbound Spam Ransomware File Activity SQL Injection Activity © Vectra | vectra. ai 15
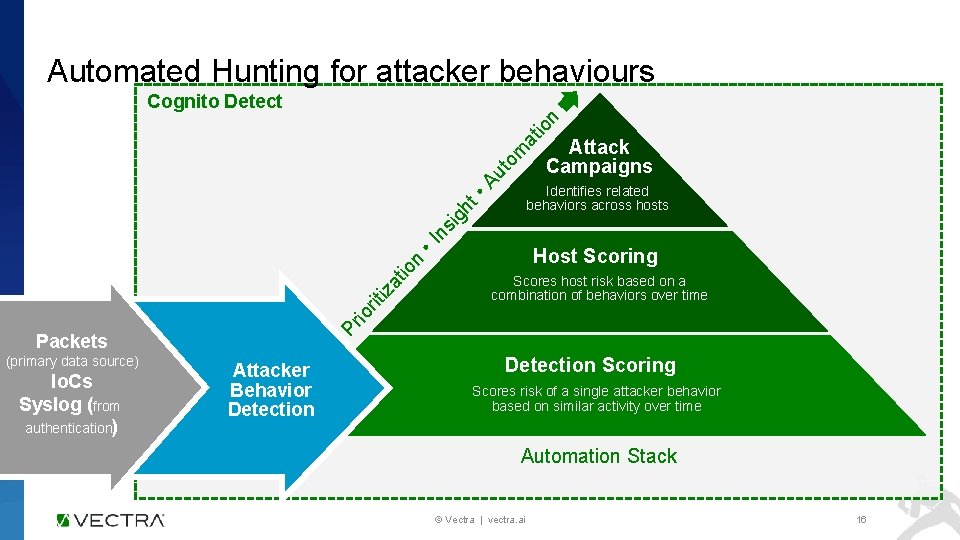
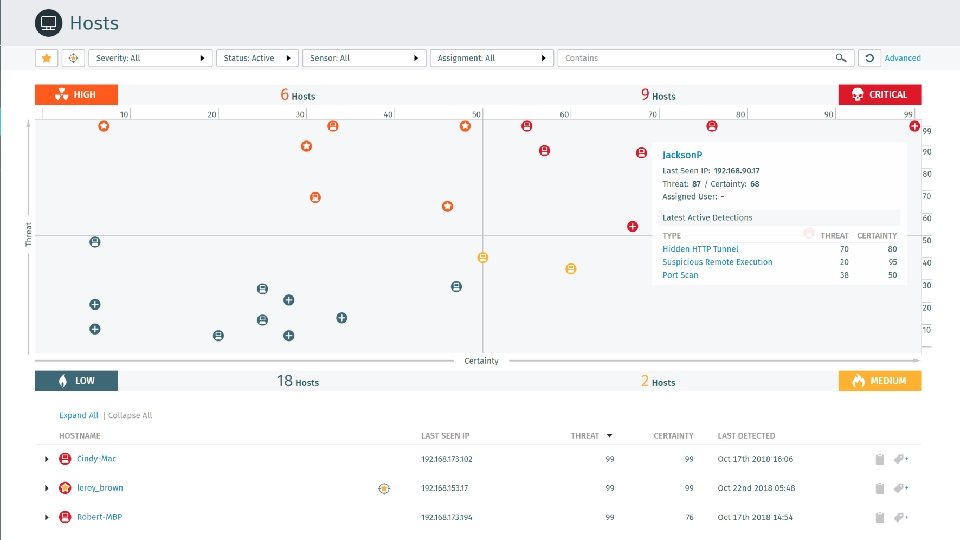
Automated Hunting for attacker behaviours Au to m at io n Cognito Detect Attack Campaigns Host Scoring Scores host risk based on a combination of behaviors over time Pr io rit iza tio n • I n sig ht • Identifies related behaviors across hosts Packets (primary data source) Io. Cs Syslog (from authentication) Attacker Behavior Detection Scoring Scores risk of a single attacker behavior based on similar activity over time Automation Stack © Vectra | vectra. ai 16
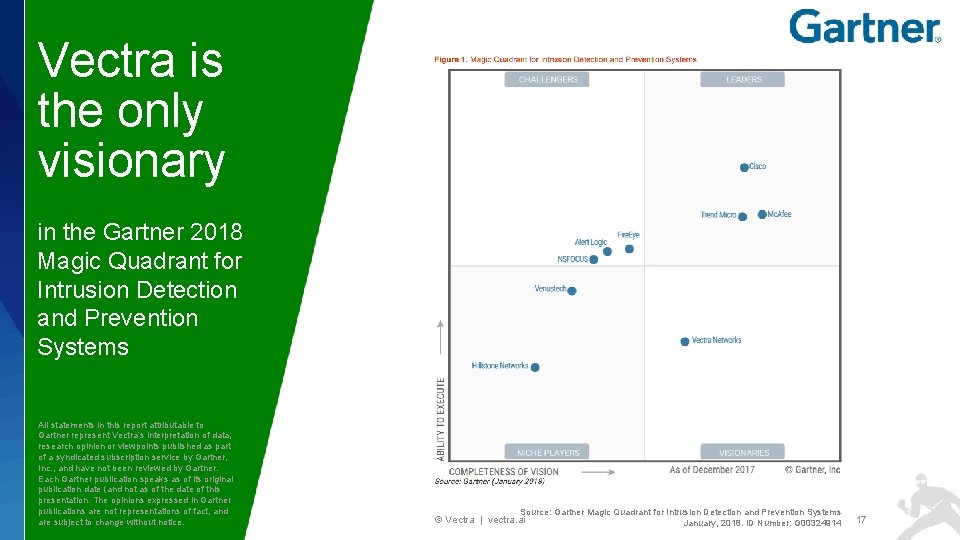
Vectra is the only visionary in the Gartner 2018 Magic Quadrant for Intrusion Detection and Prevention Systems All statements in this report attributable to Gartner represent Vectra’s interpretation of data, research opinion or viewpoints published as part of a syndicated subscription service by Gartner, Inc. , and have not been reviewed by Gartner. Each Gartner publication speaks as of its original publication date (and not as of the date of this presentation. The opinions expressed in Gartner publications are not representations of fact, and are subject to change without notice. Source: Gartner Magic Quadrant for Intrusion Detection and Prevention Systems January, 2018. ID Number: G 00324914 © Vectra | vectra. ai 17
We chose Vectra as the winner because it prioritizes threats and reduces attacker dwell time with a lightweight solution. – Tim Wilson Editor in Chief, Dark Reading, 2016 © Vectra | vectra. ai 18
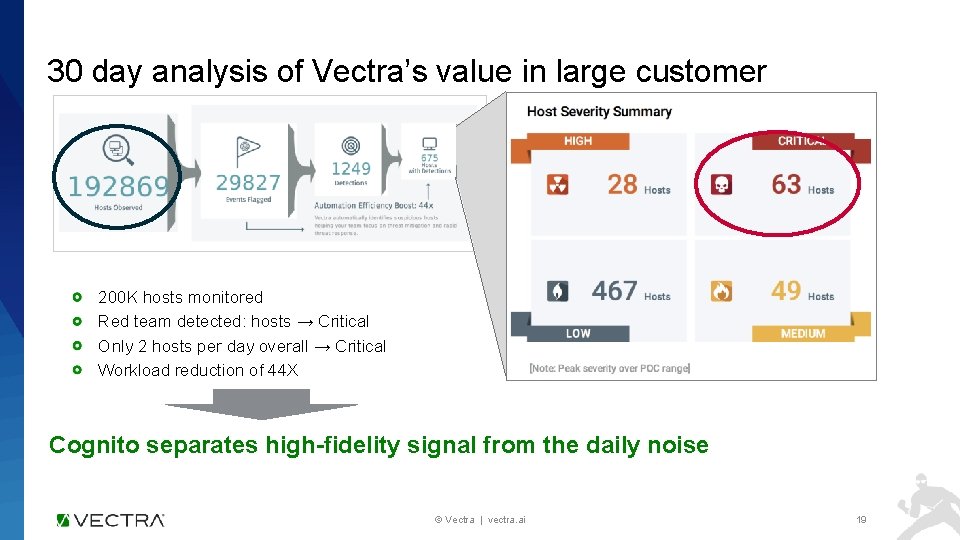
30 day analysis of Vectra’s value in large customer 200 K hosts monitored Red team detected: hosts → Critical Only 2 hosts per day overall → Critical Workload reduction of 44 X Cognito separates high-fidelity signal from the daily noise © Vectra | vectra. ai 19
© Vectra | vectra. ai 20
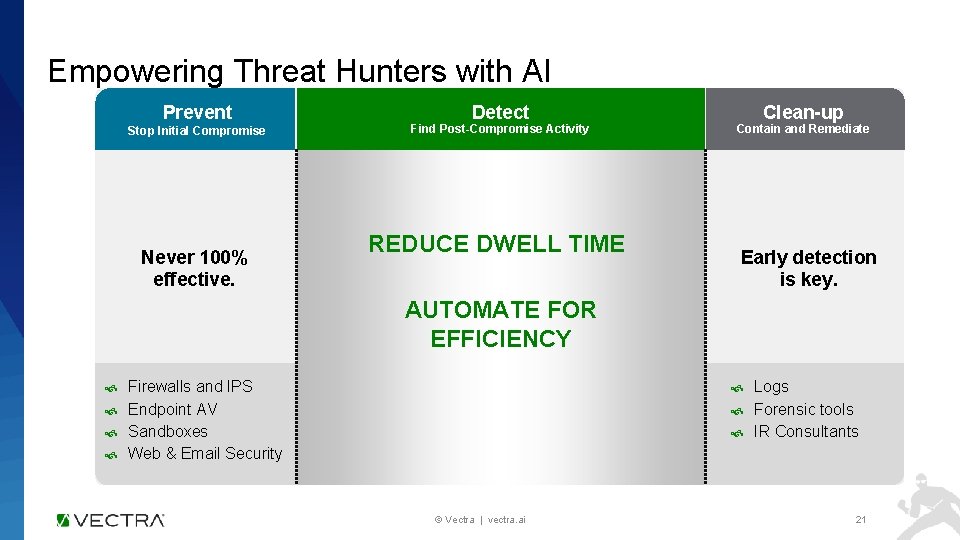
Empowering Threat Hunters with AI Prevent Stop Initial Compromise Never 100% effective. Detect Find Post-Compromise Activity REDUCE DWELL TIME Clean-up Contain and Remediate Early detection is key. AUTOMATE FOR EFFICIENCY Firewalls and IPS Endpoint AV Sandboxes Web & Email Security Logs Forensic tools IR Consultants © Vectra | vectra. ai 21

© Vectra | vectra. ai 22
- Slides: 22