
Major Pain Points for Organizations of all Types
- Slides: 31
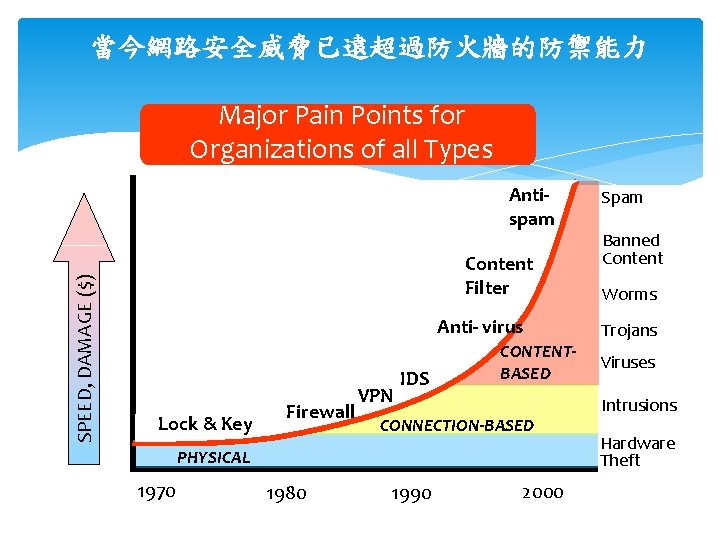
當今網路安全威脅已遠超過防火牆的防禦能力 Major Pain Points for Organizations of all Types SPEED, DAMAGE ($) Antispam Content Filter Anti- virus Lock & Key Firewall VPN IDS CONTENTBASED CONNECTION-BASED PHYSICAL 1970 1980 1990 2000 Spam Banned Content Worms Trojans Viruses Intrusions Hardware Theft
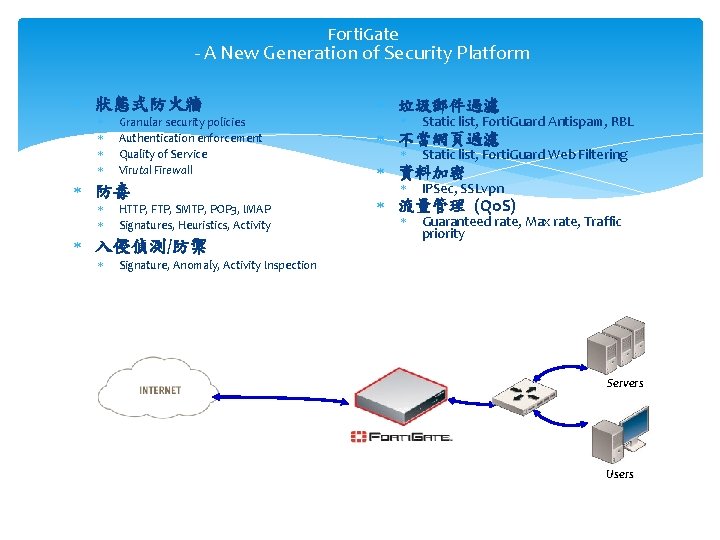
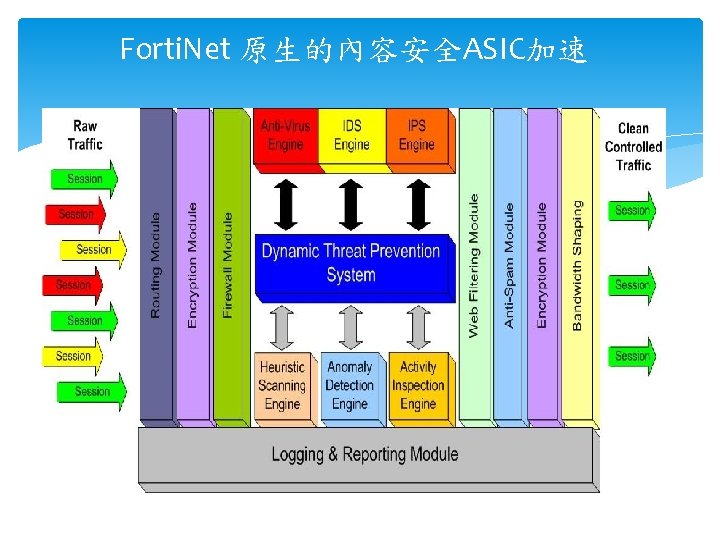
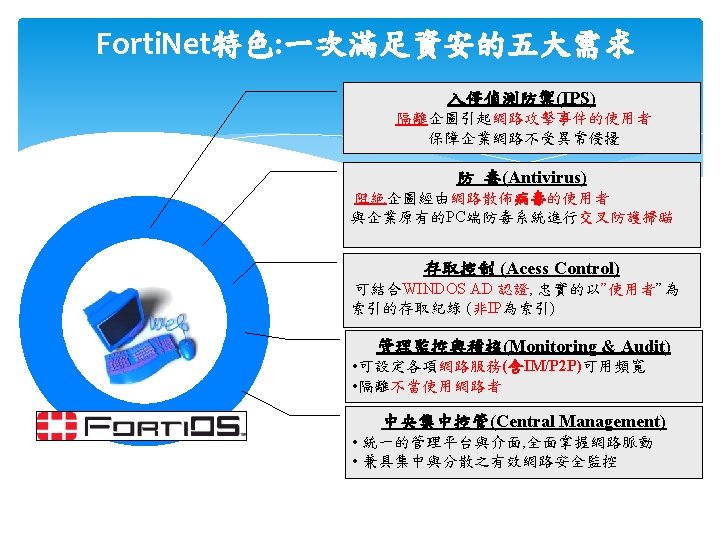
Forti. Gate - A New Generation of Security Platform 狀態式防火牆 Granular security policies Authentication enforcement Quality of Service Virutal Firewall 防毒 HTTP, FTP, SMTP, POP 3, IMAP Signatures, Heuristics, Activity 入侵偵測/防禦 垃圾郵件過濾 Static list, Forti. Guard Antispam, RBL 不當網頁過濾 Static list, Forti. Guard Web Filtering 資料加密 IPSec, SSLvpn 流量管理 (Qo. S) Guaranteed rate, Max rate, Traffic priority Signature, Anomaly, Activity Inspection Servers Users
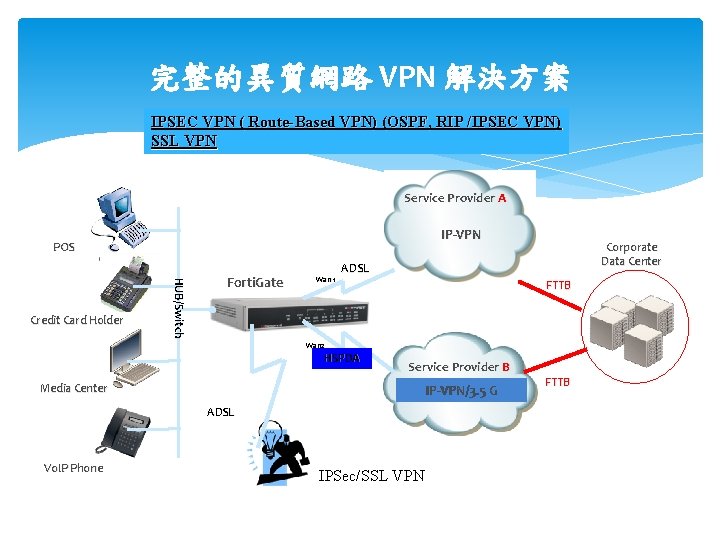
完整的異質網路 VPN 解決方案 IPSEC VPN ( Route-Based VPN) (OSPF, RIP /IPSEC VPN) SSL VPN Service Provider A IP-VPN POS HUB/Switch Credit Card Holder Forti. Gate Wan 1 Corporate Data Center ADSL FTTB Wan 2 HSPDA ADSL Service Provider B IP-VPN G IP-VPN/3. 5 Media Center ADSL Vo. IP Phone IPSec/SSL VPN FTTB
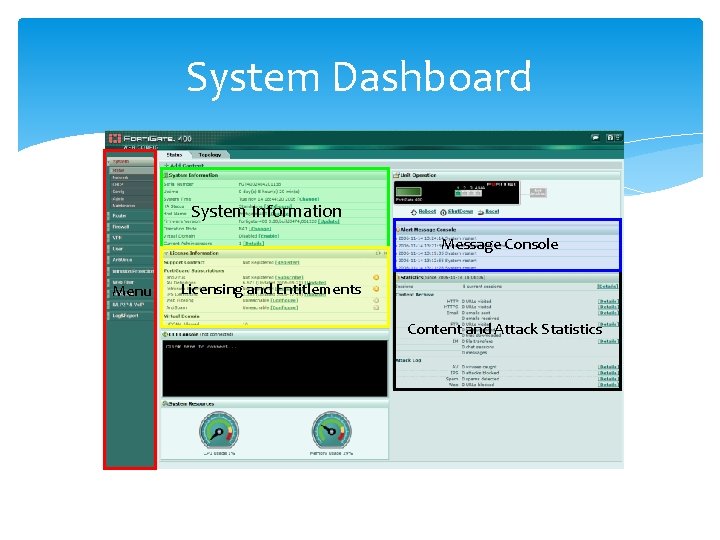
System Dashboard System Information Message Console Menu Licensing and Entitlements Content and Attack Statistics
DHCP Server A DHCP server may be configured on any interface with a static IP address Multiple DHCP servers on a single interface Relay a DHCP request to a remote DHCP server
CLI
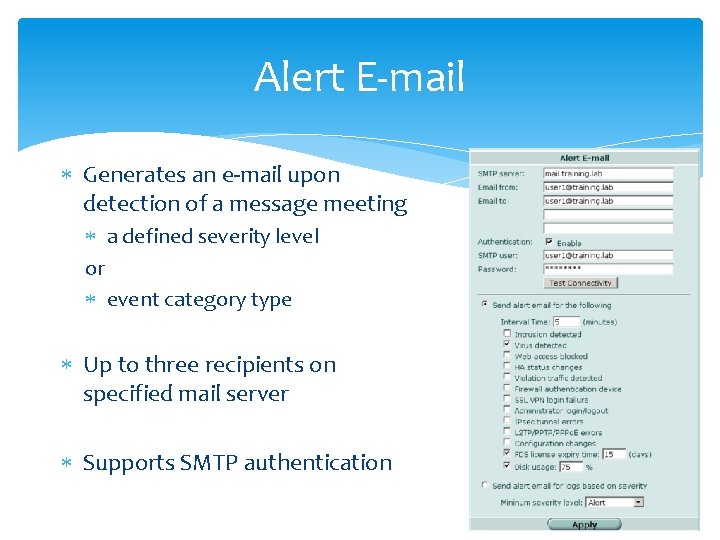
Alert E-mail Generates an e-mail upon detection of a message meeting a defined severity level or event category type Up to three recipients on specified mail server Supports SMTP authentication
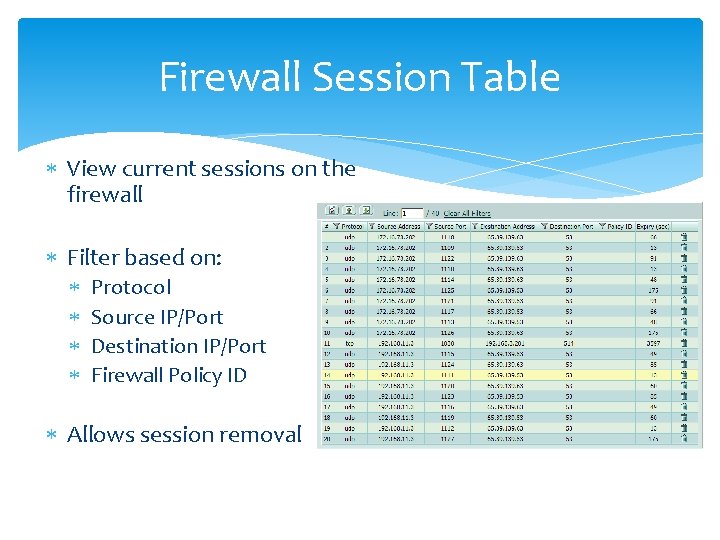
Firewall Session Table View current sessions on the firewall Filter based on: Protocol Source IP/Port Destination IP/Port Firewall Policy ID Allows session removal
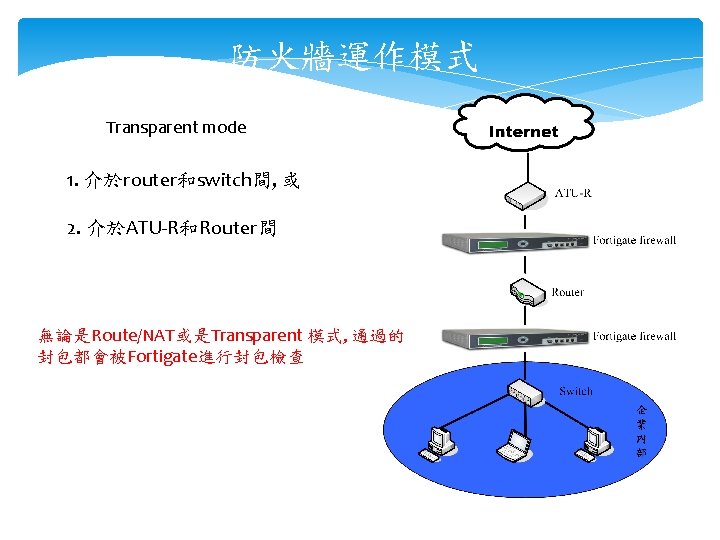
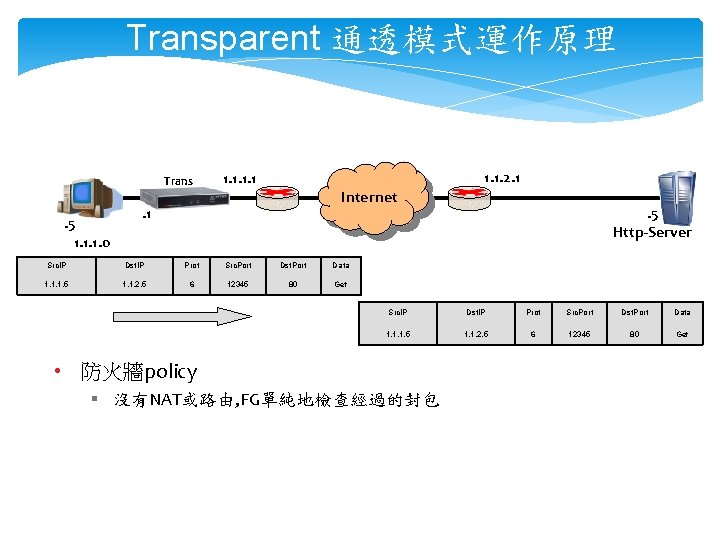
防火牆運作模式 Transparent mode 1. 介於router和switch間, 或 2. 介於ATU-R和Router間 無論是Route/NAT或是Transparent 模式, 通過的 封包都會被Fortigate進行封包檢查
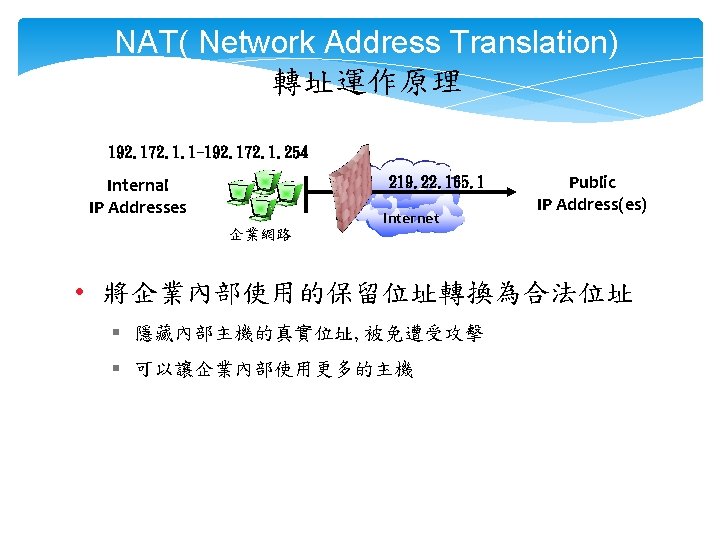
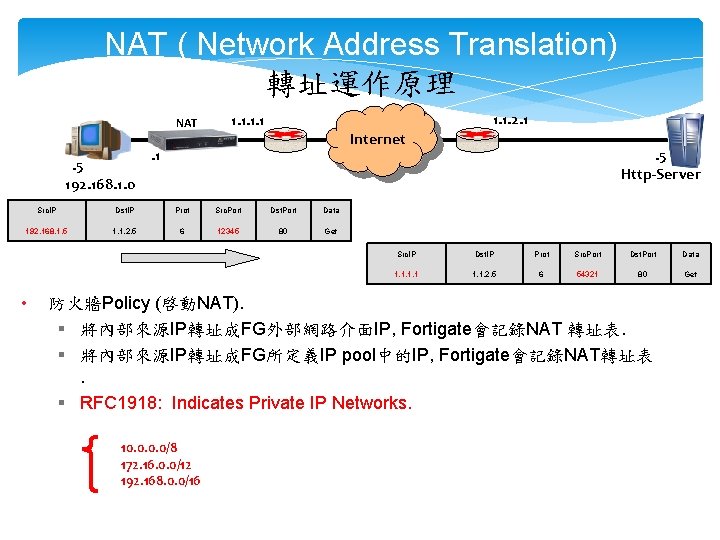
NAT ( Network Address Translation) 轉址運作原理 NAT . 5 192. 168. 1. 0 1. 1. 2. 1 1. 1 Internet . 1 Src. IP Dst. IP Prot Src. Port Dst. Port Data 192. 168. 1. 5 1. 1. 2. 5 6 12345 80 Get • . 5 Http-Server Src. IP Dst. IP Prot Src. Port Dst. Port Data 1. 1. 2. 5 6 54321 80 Get 防火牆Policy (啓動NAT). § 將內部來源IP轉址成FG外部網路介面IP, Fortigate會記錄NAT 轉址表. § 將內部來源IP轉址成FG所定義IP pool中的IP, Fortigate會記錄NAT轉址表. § RFC 1918: Indicates Private IP Networks. 10. 0/8 172. 16. 0. 0/12 192. 168. 0. 0/16
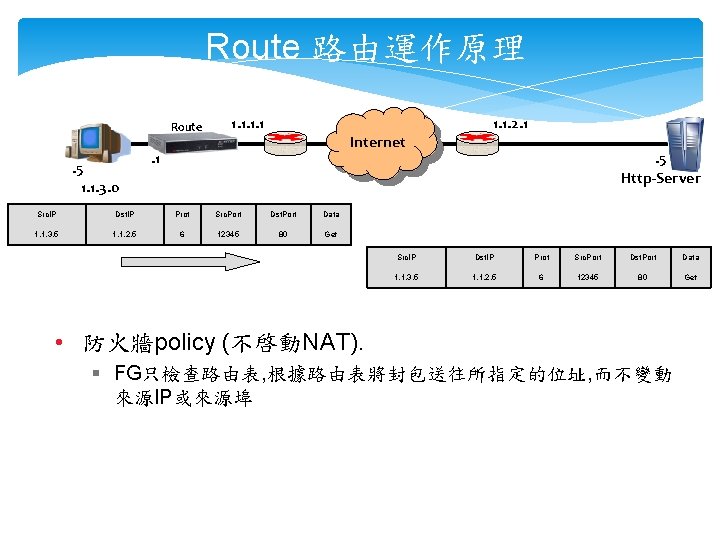
Route 路由運作原理 Route . 5 1. 1. 3. 0 1. 1. 2. 1 1. 1 Internet . 1 Src. IP Dst. IP Prot Src. Port Dst. Port Data 1. 1. 3. 5 1. 1. 2. 5 6 12345 80 Get . 5 Http-Server Src. IP Dst. IP Prot Src. Port Dst. Port Data 1. 1. 3. 5 1. 1. 2. 5 6 12345 80 Get • 防火牆policy (不啓動NAT). § FG只檢查路由表, 根據路由表將封包送往所指定的位址, 而不變動 來源IP或來源埠
Transparent 通透模式運作原理 Trans . 5 1. 1. 1. 0 1. 1. 2. 1 1. 1 Internet . 1 Src. IP Dst. IP Prot Src. Port Dst. Port Data 1. 1. 1. 5 1. 1. 2. 5 6 12345 80 Get . 5 Http-Server Src. IP Dst. IP Prot Src. Port Dst. Port Data 1. 1. 1. 5 1. 1. 2. 5 6 12345 80 Get • 防火牆policy § 沒有NAT或路由, FG單純地檢查經過的封包
Authentication A User object is a instance of an authentication method A User Group object is a container for User objects Identifies group members Protection Profile and Type provides authorization attributes for members Forti. Gate units control access to resources based on group membership The combination of User Group and Firewall Policy defines the authorization for a particular user Firewall Policy: VPN (SSL/IPSec/PPTP/L 2 TP), FWUA (firewall user authentication)
Authentication – User/Server Types Local password file Username and password prompt RADIUS Username and password prompt LDAP / AD Username and password prompt FSAE / NTLM (AD) Single Sign On based on earlier authentication event PKI Certificate based authentication
Authentication – Services Firewall Policies (Firewall User Authentication) SSL VPN IPSec VPN PPTP and L 2 TP Admin login Forti. Guard Web Filtering Override
Firewall Policies User Groups linked to Accept Firewall Policies On successful authentication a temporary rule is created If no traffic present rule remove after the ‘authtimeout’ Local, RADIUS, LDAP authentication presents user with a login page On successful authentication the user is redirected to requested site Windows AD (FSAE and NTLM) Authentication based on AD Group membership PKI user authenticated on presentation of a valid certificate HTTPS (and HTTP with redirect to HTTPS)
SSL VPN User Groups are linked to SSL VPN policies Allows users access to the SSL VPN portal Creates temporary rules based on SSL VPN firewall policies linked to the User Group Local, RADIUS, LDAP present user with a login page On successful authentication user is connected to SSL VPN portal PKI allows a user to be authenticated on presentation of a valid certificate Users directly connected to portal, no username or password is required
IPSec VPN Phase 1 objects authenticate remote gateways using a Peer ID, and a pre-share key or certificate Dynamic IP remote gateways (dial up) configure a Local ID which will be sent in the clear when using aggressive mode Xauth is used with Dial Up remote gateways to identify the user using a username and password Xauth links to a User Group object type firewall
PPTP and L 2 TP Forti. OS terminates the PPTP/L 2 TP connection and assigns authenticated users an address out of the configured address pool On successful authentication a temporary rule matching the configured address pool is created Local, RADIUS and LDAP used to authenticate connecting users
Admin login Admin account link to a profile defining the users role and VDOM membership Local and RADIUS If both are configured the RADIUS object is attempted first and then if no response the Local password is used RADIUS Accounting packets sent for Admin users PKI allows a user to be authenticated on presentation of a valid certificate Users directly connected to the Web. UI, no username or password is required
RADIUS Forti. Gate acts as a network access server (NAS) User information passed to the RADIUS server User authenticated based on the RADIUS servers response Object identifies the IP address and shared secret of up to two RADIUS servers RADIUS object can be used for all services supporting authentication Radius Accounting for Admin users
LDAP Forti. Gate configured as LDAP client for LDAP server or Active Directory Supports LDAP protocol functionality defined in RFC 2251 for looking up and validating user names and passwords Forti. OS v 3. 00 supports three LDAP Auth Types: Simple: provides simple password authentication without search capabilities (default). Anonymous: binds to the server as an Anonymous user. It then performs the LDAP search and the secondary bind. Regular: binds (logs on) to the LDAP server with a userspecified username and password. It then performs the LDAP search and secondary bind.
Types of SSL VPN Web Application mode Secured access to a portal interface Available via any browser supporting SSL version 2 or 3 Tunnel mode Virtual IP assignment (Similar to PPP) Uses Active. X and Java controls Host security is based only on firewall policies
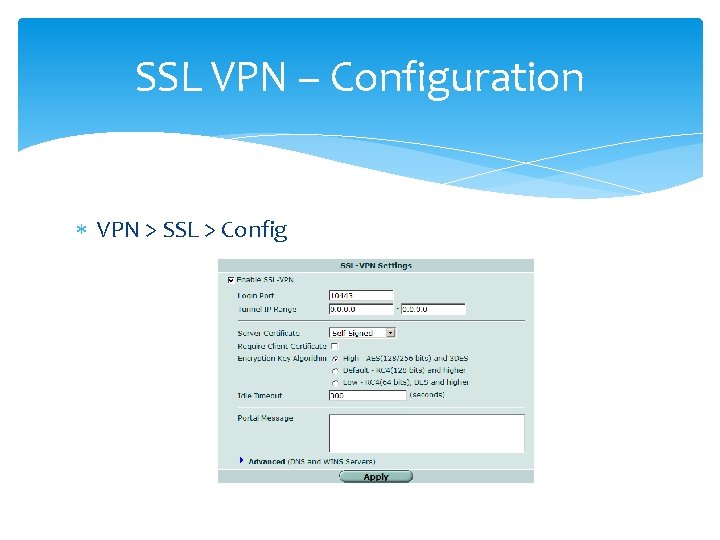
SSL VPN – Configuration VPN > SSL > Config
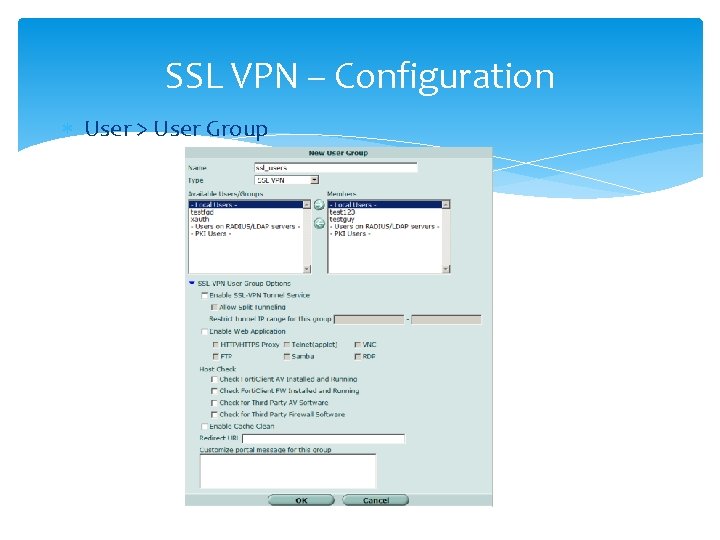
SSL VPN – Configuration User > User Group
Thanks