
LINUX Foundation LF EDGE Secure Device Onboard FIDO
LINUX Foundation – LF EDGE Secure Device Onboard / FIDO IOT Overview Making Device Plugs & Play - Enables Any Device to any Cloud Password replacement and automated device activation
How long does it take to manually onboard 1 10, 000 Gateways, Devices, Sensors? Answer: Over 2 man years 2 1. Assumes out-of-box to securely streaming data to an Io. T Platform 2. Kaiser Associates Research and Analysis, Io. T study, August 2017
Worldwide Trends around “Passwords” ü US (Ca) Sep’ 18 - Bans Default Passwords in Connected Devices https: //leginfo. legislature. ca. gov/faces/bill. Text. Client. xhtml? bill_id=201720180 SB 327 ü Japan Apr’ 20 - New Ordinance “No Default Password” http: //www. soumu. go. jp/main_content/000611859. pdf Multiple world wide government initiatives to legislate against default passwords
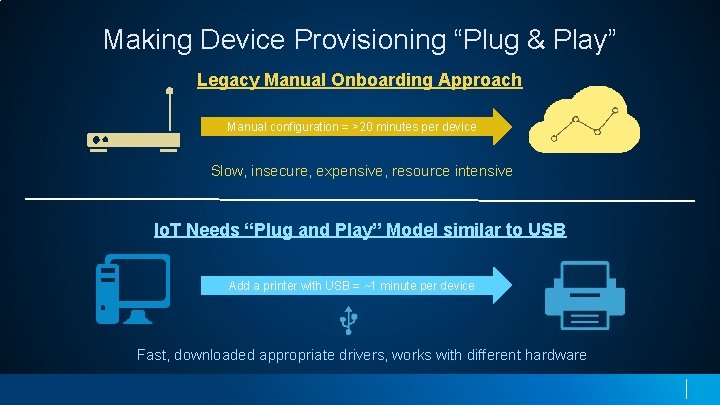
Making Device Provisioning “Plug & Play” Legacy Manual Onboarding Approach Manual configuration = >20 minutes per device Slow, insecure, expensive, resource intensive Io. T Needs “Plug and Play” Model similar to USB Add a printer with USB = ~1 minute per device Fast, downloaded appropriate drivers, works with different hardware
The onboarding challenge • • • Wide variety of equipment – hardware and Operating Systems Most devices headless (i. e. don’t have displays) Different connectivity – wired / wireless Manual installation adds cost and time to IOT deployments, impacting program ROI Requires trusted and skilled staff
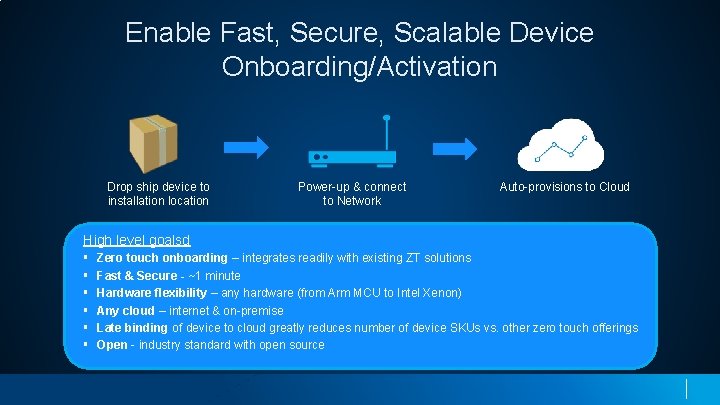
Enable Fast, Secure, Scalable Device Onboarding/Activation Drop ship device to installation location Power-up & connect to Network Auto-provisions to Cloud High level goalsd § § § Zero touch onboarding – integrates readily with existing ZT solutions Fast & Secure - ~1 minute Hardware flexibility – any hardware (from Arm MCU to Intel Xenon) Any cloud – internet & on-premise Late binding of device to cloud greatly reduces number of device SKUs vs. other zero touch offerings Open - industry standard with open source
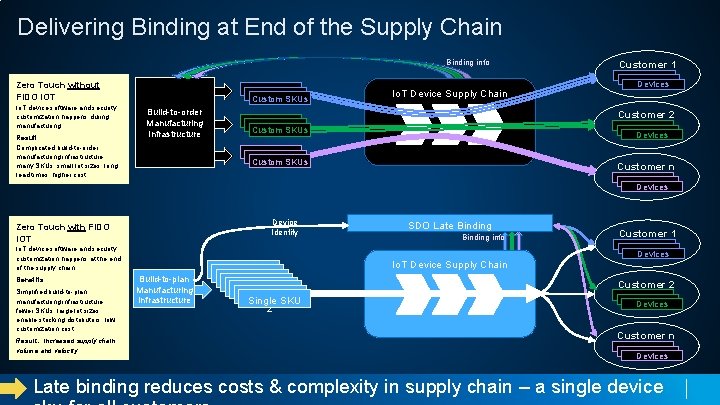
Delivering Binding at End of the Supply Chain Binding info Zero Touch without FIDO IOT Io. T device software and security customization happens during manufacturing Result: Complicated build-to-order manufacturing infrastructure, many SKUs, small lot sizes, long lead times, higher cost Custom SKUs Build-to-order Manufacturing Infrastructure Io. T Device Supply Chain Customer 1 Devices Customer 2 Custom SKUs Devices Custom SKUs Customer n Devices Device Identity Zero Touch with FIDO IOT Io. T device software and security customization happens at the end of the supply chain Benefits: Simplified build-to-plan manufacturing infrastructure, fewer SKUs, large lot sizes, enable stocking distributors, low customization cost Result: Increased supply chain volume and velocity Build-to-plan Manufacturing Infrastructure Device SKU 2 Device SKU 2 Device 22 SKU Single 22 SKU SDO Late Binding info Io. T Device Supply Chain Customer 1 Devices Customer 2 Devices Customer n Devices Late binding reduces costs & complexity in supply chain – a single device
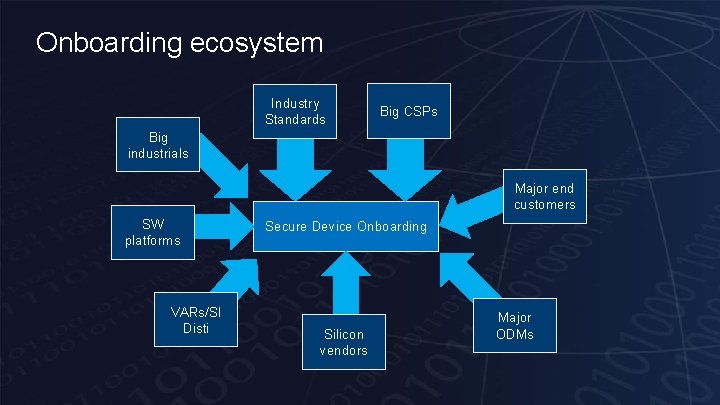
Onboarding ecosystem Industry Standards Big CSPs Big industrials Major end customers SW platforms VARs/SI Disti Secure Device Onboarding Silicon vendors Major ODMs
FIDO Alliance IOT WG Meeting FIDO IOT Charter: “The Io. T TWG has been established to develop use cases, target architectures, and specifications covering the following topics: Io. T Device Attestation/Authentication profiles to enable interoperability between relying parties and Io. T devices, automated onboarding, and binding of applications and/or users to Io. T devices , Io. T device authentication and provisioning via smart routers and Io. T hubs, and gap analysis and extensions/modifications (where necessary) of existing FIDO specifications related to Io. T authentication, platforms and protocols” First F 2 F meeting: July 2019 Attendees o Google o Microsoft o RSA o Qualcomm o Alibaba O Arm o Intel o o o o AWS Infineon Phoenix Technologies Lenovo NXP e. WBM Device Authority
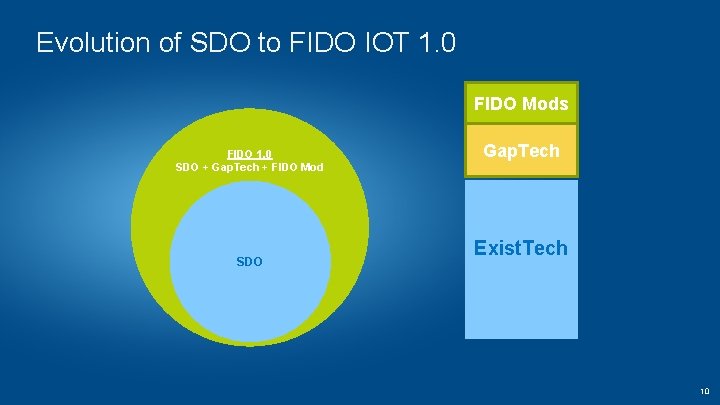
Evolution of SDO to FIDO IOT 1. 0 FIDO Mods FIDO 1. 0 SDO + Gap. Tech + FIDO Mod SDO Gap. Tech Exist. Tech 10
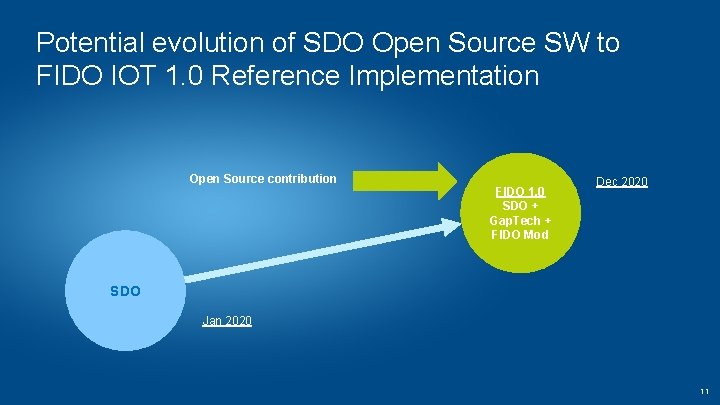
Potential evolution of SDO Open Source SW to FIDO IOT 1. 0 Reference Implementation Open Source contribution FIDO 1. 0 SDO + Gap. Tech + FIDO Mod Dec 2020 SDO Jan 2020 11
Summary • Objectives: • Create open source implementation of FIDO IOT onboarding spec as a reference/gold implementation for the industry • Create vibrant LFEdge ecosystem that will innovate on top of SDO/FIDO baseline (eg. IBM Open Horizon) • Encourage key partners (ARM, Microsoft, Google) to actively engage and contribute to LFEdge/FIDO program • Key Strategies: • Place SDO in Open Source (Github) – Complete. • Kick off LFEdge program to leverage SDO/FIDO Open Source as spring board to develop FIDO IOT code • FIDO will provide early access to spec drafts to allow Open Source to remain in lock step with FIDO spec 12
Back-up
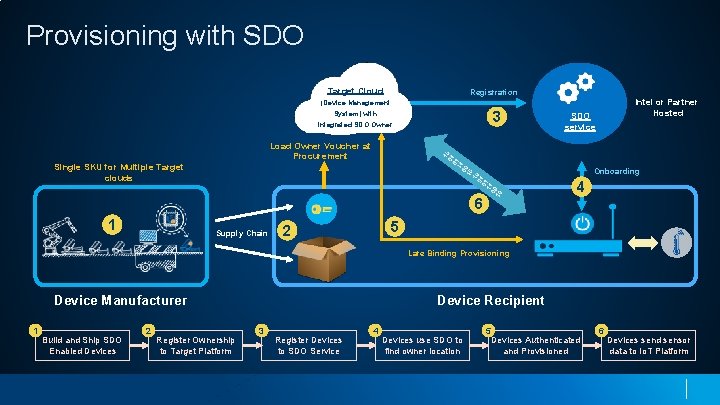
Provisioning with SDO Target Cloud Registration Intel or Partner Hosted (Device Management 3 System) with integrated SDO Owner SDO service Load Owner Voucher at Procurement Single SKU for Multiple Target clouds Onboarding 4 6 1 Supply Chain 5 2 Late Binding Provisioning Device Manufacturer 1 Build and Ship SDO Enabled Devices 2 Register Ownership to Target Platform Device Recipient 3 Register Devices to SDO Service 4 Devices use SDO to find owner location 5 Devices Authenticated and Provisioned 6 Devices send sensor data to Io. T Platform
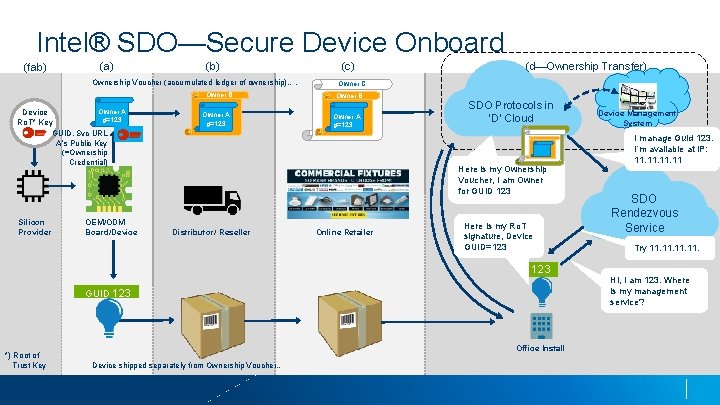
Intel® SDO—Secure Device Onboard (fab) (a) (b) Ownership Voucher (accumulated ledger of ownership)…. Owner B Owner A Device g=123 Ro. T* Key GUID, Svc URL A’s Public Key (=Ownership Credential) Silicon Provider OEM/ODM Board/Device Owner A g=123 (c) (d—Ownership Transfer) Owner C Owner B Owner A g=123 SDO Protocols in ‘D’ Cloud Here is my Ownership Voucher, I am Owner for GUID 123 Distributor/ Reseller Online Retailer Here is my Ro. T signature, Device GUID=123 GUID 123 *) Root of Trust Key Office Install Device shipped separately from Ownership Voucher… Device Management System “d” cloud I manage Guid 123. I’m available at IP: 11. 11. 11 SDO Rendezvous Service Try 11. 11. Hi, I am 123. Where is my management service?
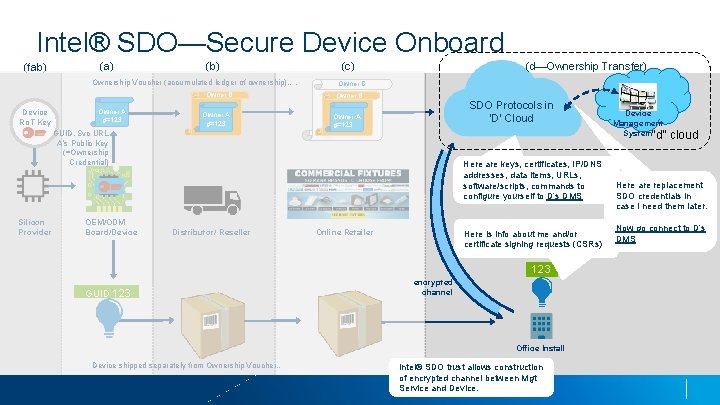
Intel® SDO—Secure Device Onboard (fab) (a) (b) Ownership Voucher (accumulated ledger of ownership)…. Owner B Device Ro. T Key Owner A g=123 (c) (d—Ownership Transfer) Owner C Owner B SDO Protocols in ‘D’ Cloud Owner A g=123 GUID, Svc URL A’s Public Key (=Ownership Credential) Silicon Provider OEM/ODM Board/Device Here are keys, certificates, IP/DNS addresses, data items, URLs, software/scripts, commands to configure yourself to D’s DMS Distributor/ Reseller Online Retailer Here is info about me and/or certificate signing requests (CSRs) 123 GUID 123 encrypted channel Office Install Device shipped separately from Ownership Voucher… Intel® SDO trust allows construction of encrypted channel between Mgt Service and Device Management System“d” cloud Here are replacement SDO credentials in case I need them later. Now go connect to D’s DMS
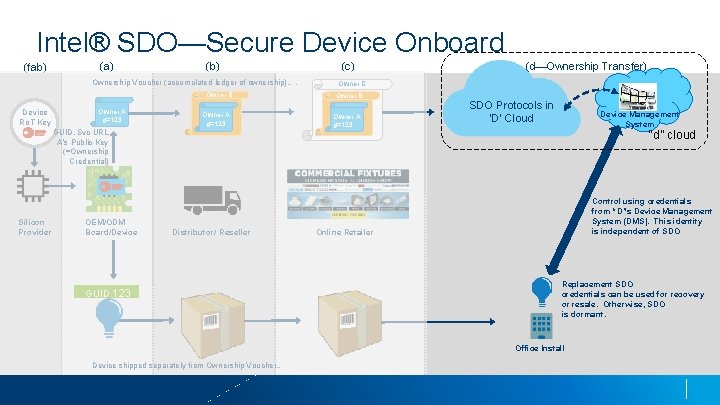
Intel® SDO—Secure Device Onboard (fab) (a) (b) Ownership Voucher (accumulated ledger of ownership)…. Owner B Device Ro. T Key Owner A g=123 GUID, Svc URL A’s Public Key (=Ownership Credential) Silicon Provider OEM/ODM Board/Device Distributor/ Reseller GUID 123 (c) (d—Ownership Transfer) Owner C Owner B Owner A g=123 SDO Protocols in ‘D’ Cloud Device Management System “d” cloud Control using credentials from “D”s Device Management System (DMS). This identity is independent of SDO Online Retailer Replacement SDO credentials can be used for recovery or resale. Otherwise, SDO is dormant. Office Install Device shipped separately from Ownership Voucher…
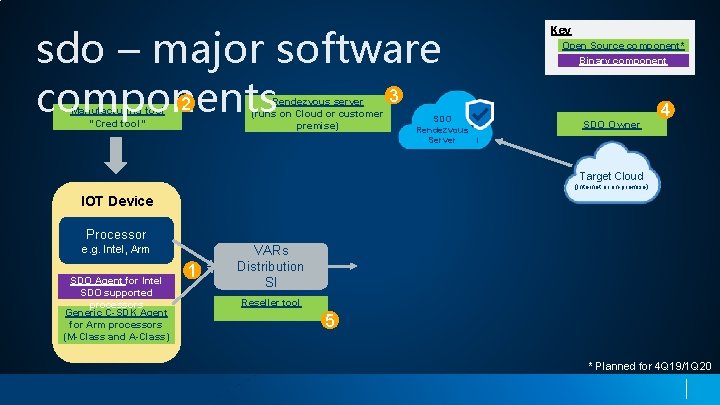
sdo – major software 3 2 components Rendezvous server (runs on Cloud or customer premise) Manufacturing tool “Cred tool” SDO Rendezvous Server Key Open Source component* Binary component SDO Owner 4 Target Cloud (Internet or on-premise) IOT Device Processor e. g. Intel, Arm SDO Agent for Intel SDO supported processors Generic C-SDK Agent for Arm processors (M-Class and A-Class) 1 VARs Distribution SI Reseller tool 5 * Planned for 4 Q 19/1 Q 20
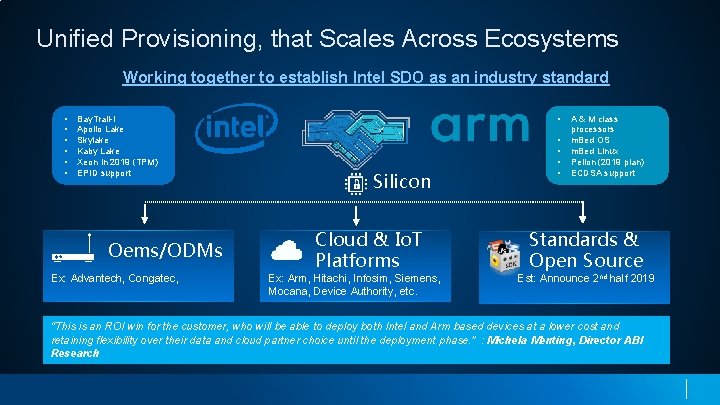
Unified Provisioning, that Scales Across Ecosystems Working together to establish Intel SDO as an industry standard • • • Bay. Trail-I Apollo Lake Skylake Kaby Lake Xeon in 2019 (TPM) EPID support Oems/ODMs Ex: Advantech, Congatec, • Silicon Cloud & Io. T Platforms Ex: Arm, Hitachi, Infosim, Siemens, Mocana, Device Authority, etc. • • A & M class processors m. Bed OS m. Bed Linux Pelion (2019 plan) ECDSA support Standards & Open Source Est: Announce 2 nd half 2019 “This is an ROI win for the customer, who will be able to deploy both Intel and Arm based devices at a lower cost and retaining flexibility over their data and cloud partner choice until the deployment phase. ” : Michela Menting, Director ABI Research
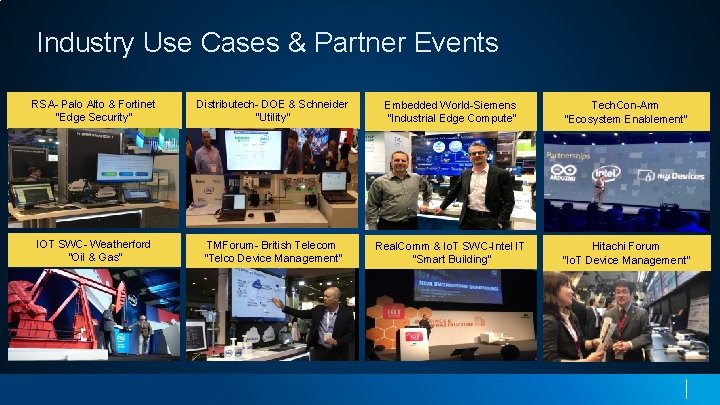
Industry Use Cases & Partner Events RSA- Palo Alto & Fortinet “Edge Security” Distributech- DOE & Schneider “Utility” Embedded World-Siemens “Industrial Edge Compute” Tech. Con-Arm “Ecosystem Enablement” IOT SWC- Weatherford “Oil & Gas” TMForum- British Telecom “Telco Device Management” Real. Comm & Io. T SWC-Intel IT “Smart Building” Hitachi Forum “Io. T Device Management”
Industry recognition for SDO Io. T Solution World Congress 2018 Test. Bed Winner Mo Zoualfaghari & Gary Bruce BT @ TM Forum, May 2019 1# Evaluation Rank 21
Learn More CALL TO ACTION Collateral, Videos & Animations Spec Sheet 1. See SDO in action: § Arm Demo Video § Overview Collateral 2. Request access to SDO documentation and software. § iotonboarding@intel. com 3. Access Developer docs and software: § Register an IDZ account § Access SDKs
Late Binding – Unique to Intel SDO ü Most zero touch solutions require unique silicon & SW embedded into device at manufacture § § This means ODMs must manufacture device SKUs for each customer/cloud combination SDO removes this need with Open Late Binding ü SDO- Open Late Binding § § § Open – service & cloud independent Late – allows users to choose their target cloud (or on premise server) late in the supply chain – typically at first power on. Services can also be downloaded at this time. Open Late Binding - Works with existing cloud services, it does not replace them. Io. T Solution World Congress 2018 Test. Bed Winner ü Increased supply chain volume & velocity § SDO allows the manufacture and distribution of identical devices in large lots which are bound to the target ecosystem at installation time 1# Evaluation Rank 23
FIDO Alliance to address IOT • The FIDO Alliance has chosen to enter the IOT space (announced 26 th June 2019) • IOT WG members include Intel, Arm, major CSPs and others. • The FIDO Alliance has for several years been addressing password replacement in internet applications. • These challenges are very similar to those seen in the IOT space. • FIDO IOT Charter: “The Io. T TWG has been established to develop use cases, target architectures, and specifications covering the following topics: Io. T Device Attestation/Authentication profiles to enable interoperability between relying parties and Io. T devices, automated onboarding, and binding of applications and/or users to Io. T devices, Io. T device authentication and provisioning via smart routers and Io. T hubs, and gap analysis and extensions/modifications (where necessary) of existing FIDO specifications related to Io. T authentication, platforms and protocols” • Intel plans to contribute SDO specification to the FIDO Alliance • Intel plans to Open Source SDO later in 2019
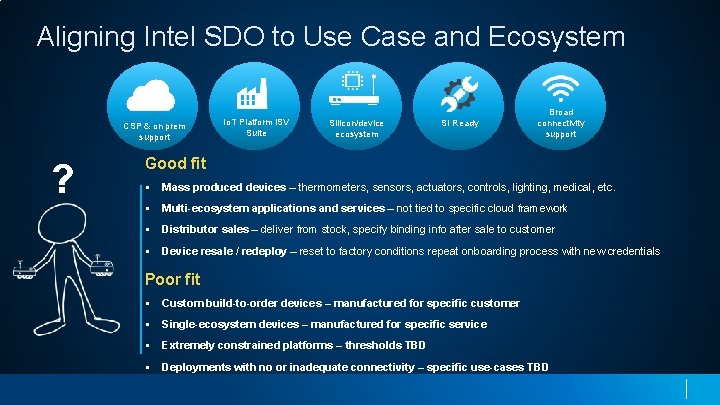
Aligning Intel SDO to Use Case and Ecosystem CSP & on prem support ? Io. T Platform ISV Suite Silicon/device ecosystem SI Ready Broad connectivity support Good fit § Mass produced devices – thermometers, sensors, actuators, controls, lighting, medical, etc. § Multi-ecosystem applications and services – not tied to specific cloud framework § Distributor sales – deliver from stock, specify binding info after sale to customer § Device resale / redeploy – reset to factory conditions repeat onboarding process with new credentials Poor fit § Custom build-to-order devices – manufactured for specific customer § Single-ecosystem devices – manufactured for specific service § Extremely constrained platforms – thresholds TBD § Deployments with no or inadequate connectivity – specific use-cases TBD
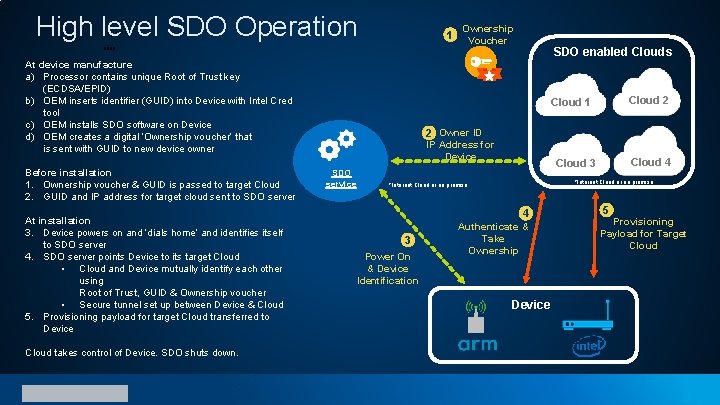
High level SDO Operation At device manufacture a) Processor contains unique Root of Trust key (ECDSA/EPID) b) OEM inserts identifier (GUID) into Device with Intel Cred tool c) OEM installs SDO software on Device d) OEM creates a digital ‘Ownership voucher’ that is sent with GUID to new device owner Before installation 1. Ownership voucher & GUID is passed to target Cloud 2. GUID and IP address for target cloud sent to SDO server At installation 3. Device powers on and ‘dials home’ and identifies itself to SDO server 4. SDO server points Device to its target Cloud • Cloud and Device mutually identify each other using Root of Trust, GUID & Ownership voucher • Secure tunnel set up between Device & Cloud 5. Provisioning payload for target Cloud transferred to Device Cloud takes control of Device. SDO shuts down. 1 Ownership Voucher SDO enabled Clouds Cloud 2 Cloud 1 2 Owner ID IP Address for Device SDO Rendezvous Server SDO service *Internet Cloud or on premise 4 3 Power On & Device Identification Cloud 4 Cloud 3 Authenticate & Take Ownership Device 5 Provisioning Payload for Target Cloud
- Slides: 26