
Leveraging Threat Intelligence in the Enterprise USING HBGARYS
Leveraging Threat Intelligence in the Enterprise USING HBGARY’S ACTIVE DEFENSE
HBGary • Enterprise software product company • 7 years old • Experts on malicious software threats Products: Active Defense Digital DNA™ (patent pending) Responder Recon Fast. Dump Integrations: En. Case Enterprise Mc. Afee e. PO
Evolving Risk • Most intellectual property and valuable data is stored online digitally within the Enterprise • Attackers are motivated and well funded • Cyber-weapons work, existing security solutions don’t, end of story.
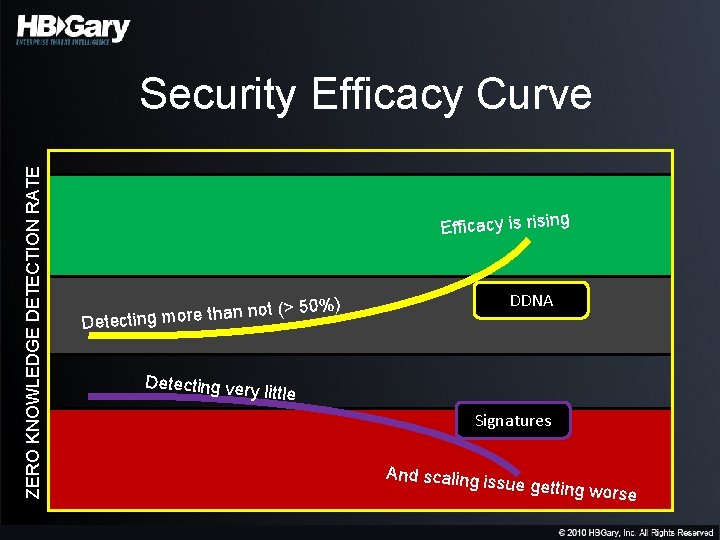
ZERO KNOWLEDGE DETECTION RATE Security Efficacy Curve Efficacy is rising DDNA ) t (> 50% o n n a th re o m Detecting ver y little Signatures And scaling is sue getting w orse
HBGary’s Approach • Focus on malicious behavior, not signatures – There are only so many ways to do something bad on a Windows machine • Bad guys don’t write 50, 000 new malware every morning – Their techniques, algorithms, and protocols stay the same, day in day out • Once executing in physical memory, the software is just software – Physmem is the best information source available
The Big Picture • Detect bad guys using a smallish genome of behaviors – and this means zero-day and APT – no signatures required • Follow up with strong incident response technology, enterprise scalable • Back this with very low level & sophisticated deep-dive capability for attribution and forensics work
Active Defense • Detect Advanced Malware & Persistent Threat – No prior knowledge of the threat required – Powered by Digital DNA™ • Obtain actionable intelligence – Registry keys & files – URL’s used for communication Actionable = make your existing investment more effective - Detect & block at the network perimeter IDS signatures, egress firewalls - Clean machines of infection Ideal: No re-image costs
The Power of Action Using Responder + REcon, HBGary was able to trace Aurora malware and obtain actionable intel in about 5 minutes. This intel was then used to create an inoculation shot, downloaded over 10, 000 times over a few days time. To automatically attempt a clean operation: ********************** Inoculate. Aurora. exe -range 192. 168. 0. 1 192. 168. 0. 254 -clean
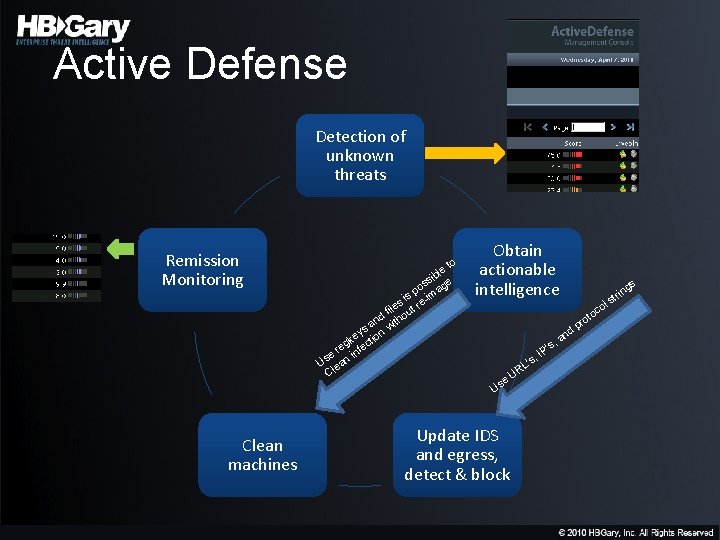
Active Defense Detection of unknown threats Remission Monitoring Clean machines to le sib e s o ag s p -im i s re file out d an with s ey on gk ecti e r inf e Us ean Cl Obtain actionable intelligence s, L’s e Us Update IDS and egress, detect & block UR P’ , I d an pr l co o ot in str gs
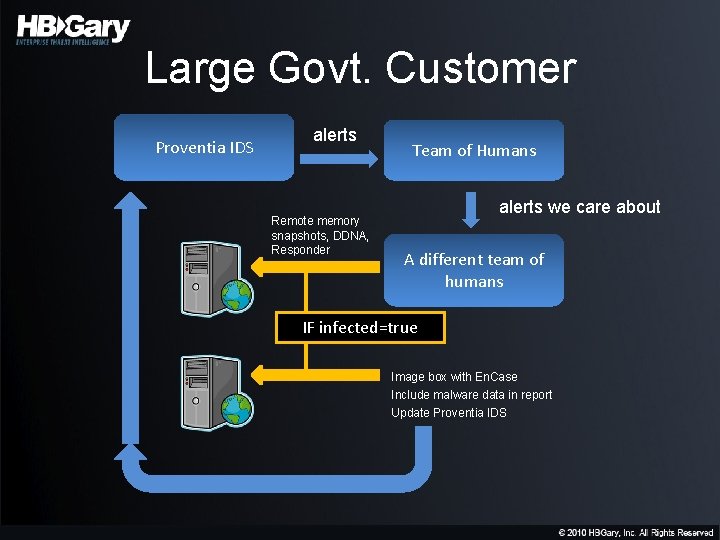
Large Govt. Customer Proventia IDS alerts Remote memory snapshots, DDNA, Responder Team of Humans alerts we care about A different team of humans IF infected=true Image box with En. Case Include malware data in report Update Proventia IDS
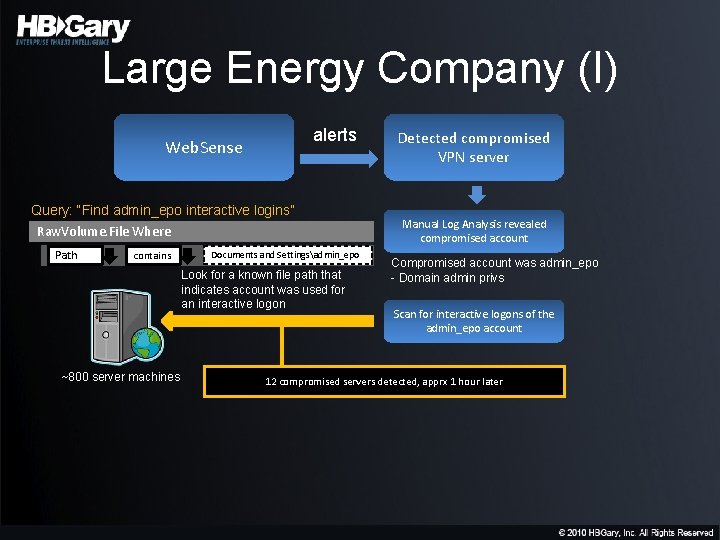
Large Energy Company (I) alerts Web. Sense Query: “Find admin_epo interactive logins” Raw. Volume. File Where Path contains Documents and Settingsadmin_epo Look for a known file path that indicates account was used for an interactive logon ~800 server machines Detected compromised VPN server Manual Log Analysis revealed compromised account Compromised account was admin_epo - Domain admin privs Scan for interactive logons of the admin_epo account 12 compromised servers detected, apprx 1 hour later
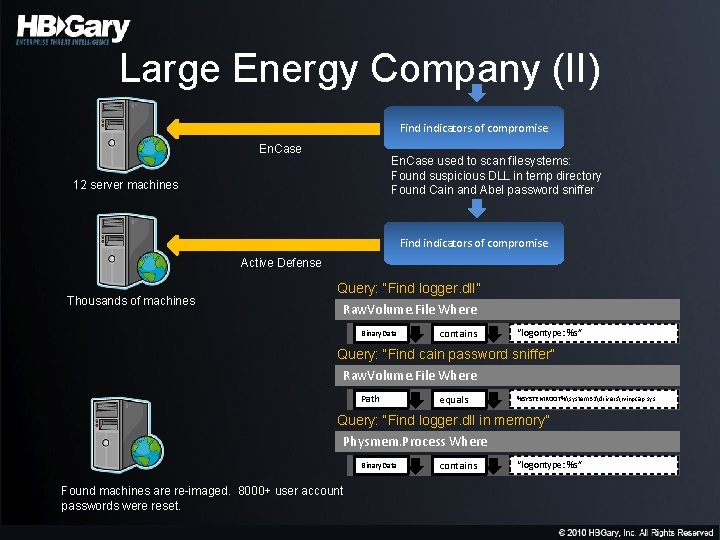
Large Energy Company (II) Find indicators of compromise En. Case used to scan filesystems: Found suspicious DLL in temp directory Found Cain and Abel password sniffer 12 server machines Find indicators of compromise Active Defense Thousands of machines Query: “Find logger. dll” Raw. Volume. File Where Binary. Data contains “logontype: %s” Query: “Find cain password sniffer” Raw. Volume. File Where Path equals %SYSTEMROOT%system 32driverswinpcap. sys Query: “Find logger. dll in memory” Physmem. Process Where Binary. Data Found machines are re-imaged. 8000+ user account passwords were reset. contains “logontype: %s”
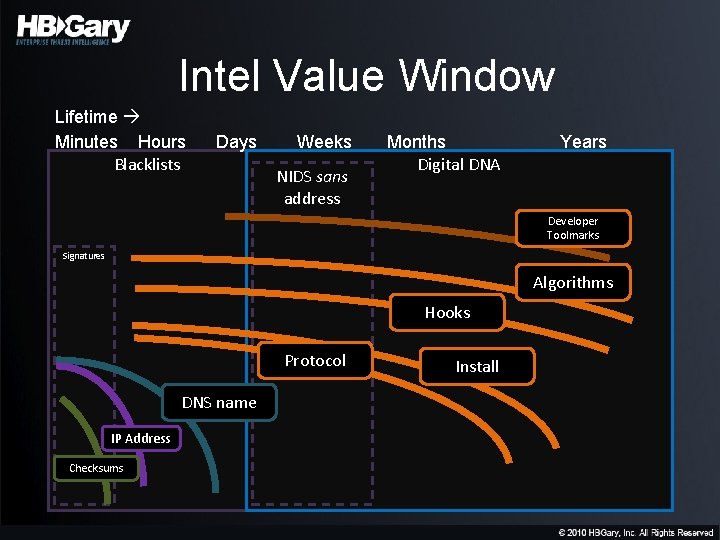
Intel Value Window Lifetime Minutes Hours Blacklists Days Weeks NIDS sans address Months Digital DNA Years Developer Toolmarks Signatures Algorithms Hooks Protocol DNS name IP Address Checksums Install
Active Defense Technical Discussion
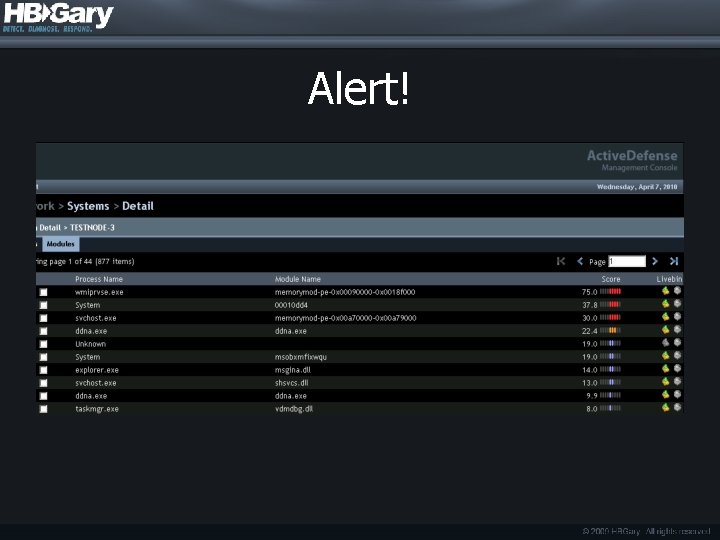
Alert!
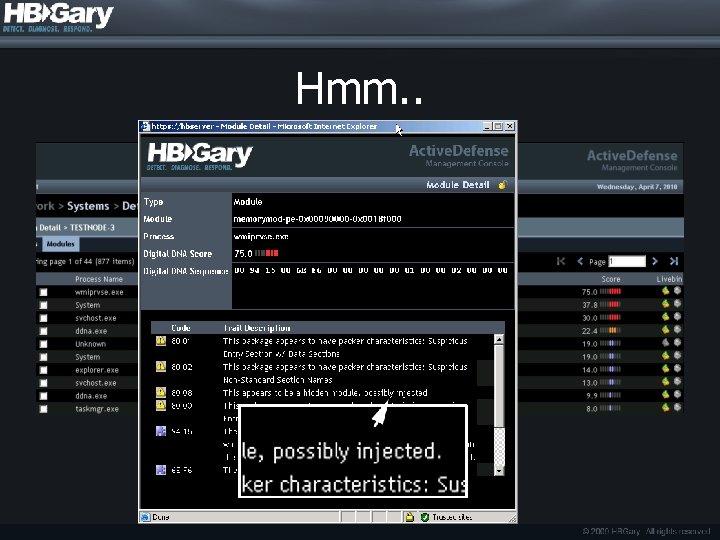
Hmm. .
Active Defense Queries • What happened? • What is being stolen? • How did it happen? • Who is behind it? • How do I bolster network defenses?
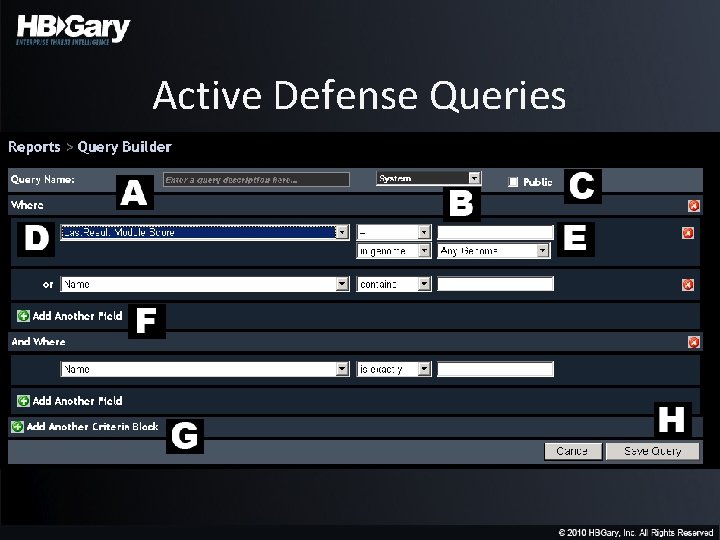
Active Defense Queries
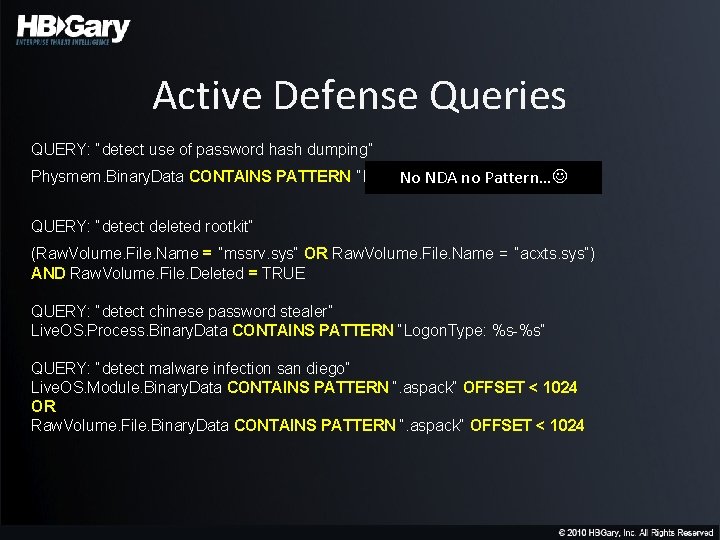
Active Defense Queries QUERY: “detect use of password hash dumping” Physmem. Binary. Data CONTAINS PATTERN “B[a-f. A-F 0 -9]{32}: B[a-f. A-F 0 -9]{32}“ No NDA no Pattern… QUERY: “detect deleted rootkit” (Raw. Volume. File. Name = “mssrv. sys“ OR Raw. Volume. File. Name = “acxts. sys“) AND Raw. Volume. File. Deleted = TRUE QUERY: “detect chinese password stealer” Live. OS. Process. Binary. Data CONTAINS PATTERN “Logon. Type: %s-%s“ QUERY: “detect malware infection san diego” Live. OS. Module. Binary. Data CONTAINS PATTERN “. aspack“ OFFSET < 1024 OR Raw. Volume. File. Binary. Data CONTAINS PATTERN “. aspack“ OFFSET < 1024
Enterprise Systems • Digital DNA for Mc. Afee e. PO • Digital DNA for HBGary Active Defense • Digital DNA for Guidance En. Case Enterprise • Digital DNA for Verdasys Digital Guardian
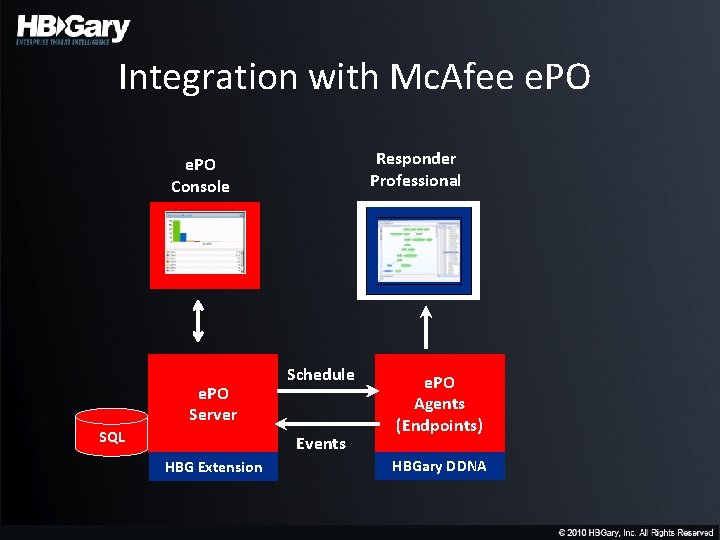
Integration with Mc. Afee e. PO Responder Professional e. PO Console e. PO Server SQL Schedule Events HBG Extension e. PO Agents (Endpoints) HBGary DDNA
Fuzzy Search
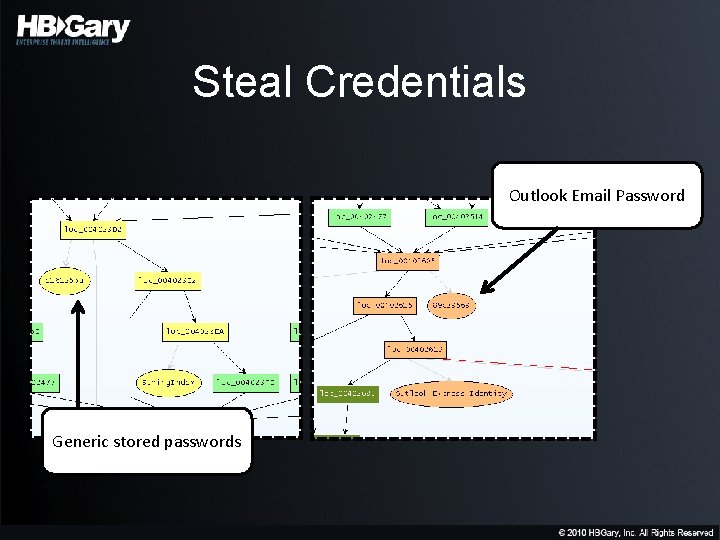
Steal Credentials Outlook Email Password Generic stored passwords
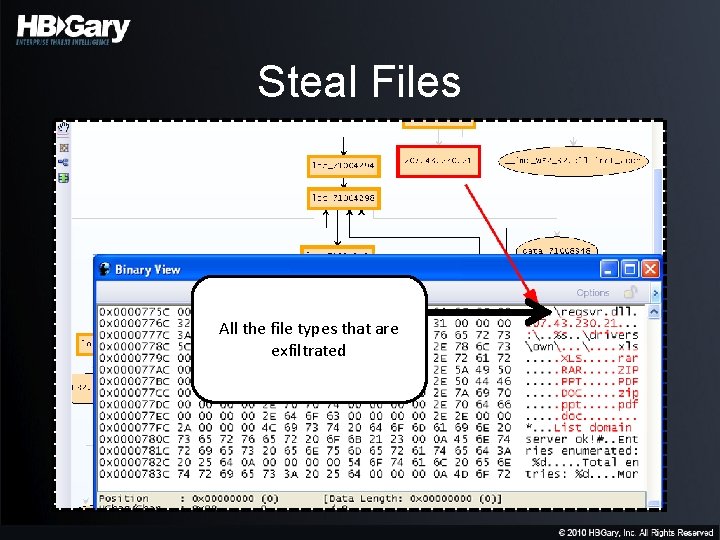
Steal Files All the file types that are exfiltrated
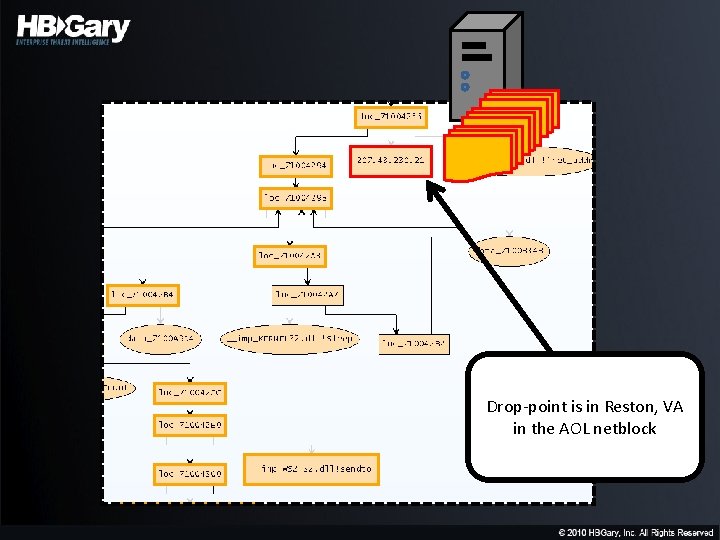
Drop-point is in Reston, VA in the AOL netblock
Digital DNA™ Technical Discussion
Digital DNA™ Performance • 4 gigs per minute, thousands of patterns in parallel, NTFS raw disk, end node • 2 gig memory, 5 minute scan, end node • Hi/Med/Low throttle • = 10, 000 machine scan completes in < 1 hour
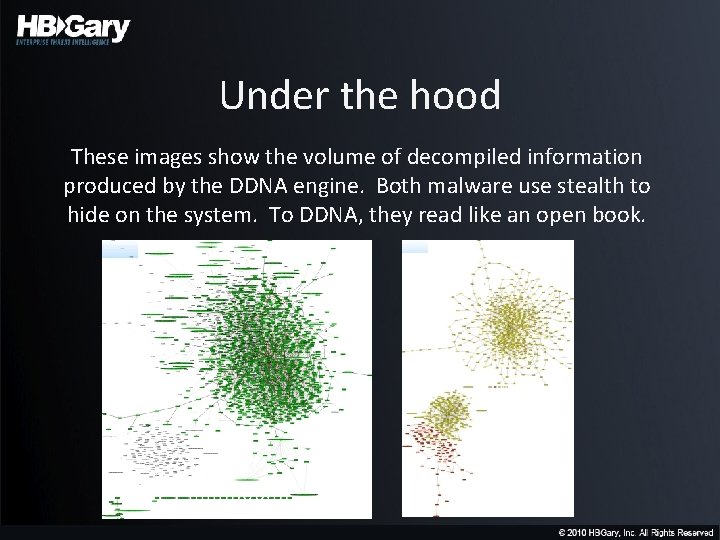
Under the hood These images show the volume of decompiled information produced by the DDNA engine. Both malware use stealth to hide on the system. To DDNA, they read like an open book.
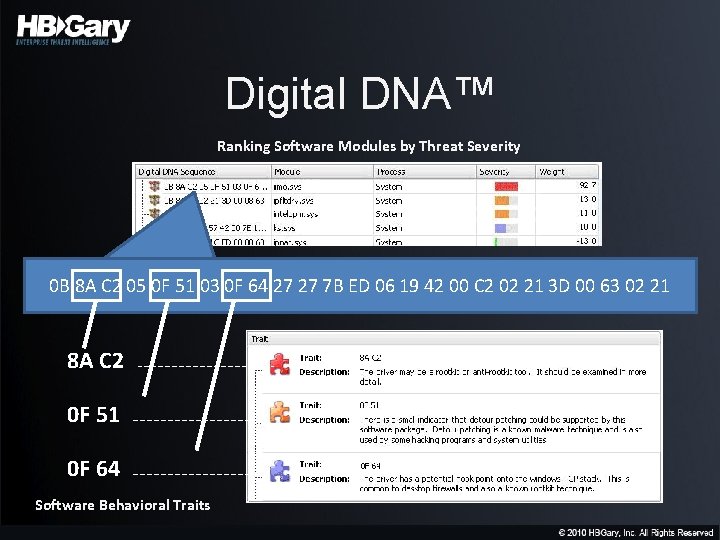
Digital DNA™ Ranking Software Modules by Threat Severity 0 B 8 A C 2 05 0 F 51 03 0 F 64 27 27 7 B ED 06 19 42 00 C 2 02 21 3 D 00 63 02 21 8 A C 2 0 F 51 0 F 64 Software Behavioral Traits
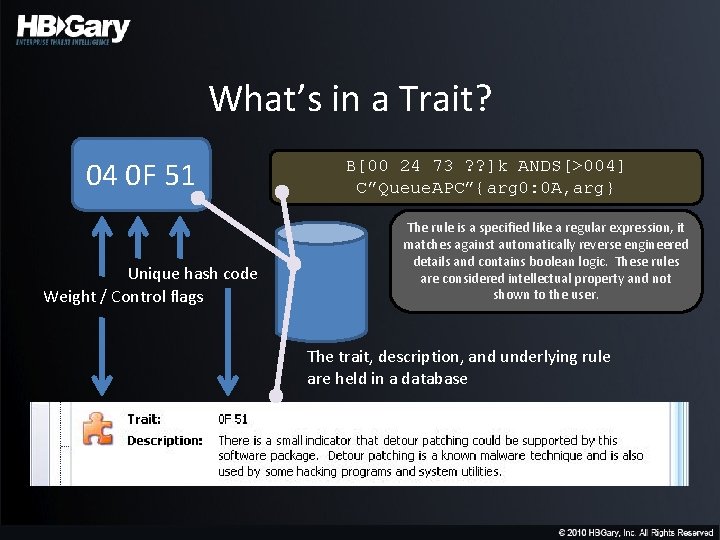
What’s in a Trait? 04 0 F 51 Unique hash code Weight / Control flags B[00 24 73 ? ? ]k ANDS[>004] C”Queue. APC”{arg 0: 0 A, arg} The rule is a specified like a regular expression, it matches against automatically reverse engineered details and contains boolean logic. These rules are considered intellectual property and not shown to the user. The trait, description, and underlying rule are held in a database
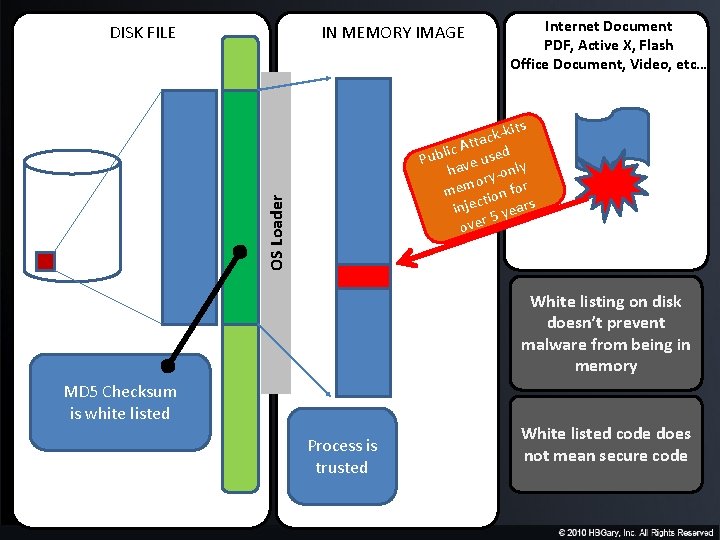
IN MEMORY IMAGE Internet Document PDF, Active X, Flash Office Document, Video, etc… kits k c Atta d c i l b use y Pu e v l ha y-on r o mem tion for injec 5 years over OS Loader DISK FILE White listing on disk doesn’t prevent malware from being in memory MD 5 Checksum is white listed Process is trusted White listed code does not mean secure code
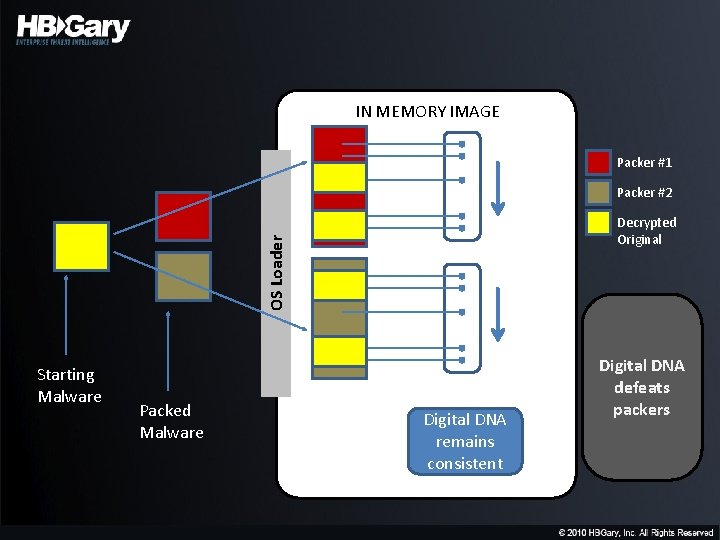
IN MEMORY IMAGE Packer #1 Packer #2 OS Loader Decrypted Original Starting Malware Packed Malware Digital DNA remains consistent Digital DNA defeats packers
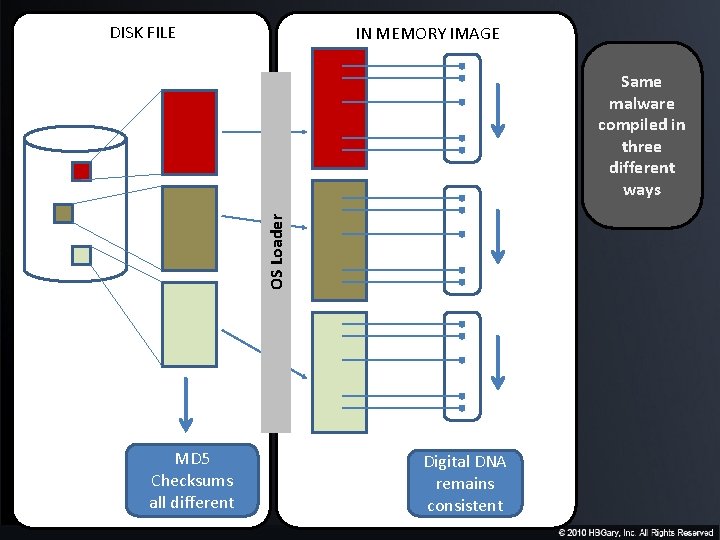
DISK FILE IN MEMORY IMAGE OS Loader Same malware compiled in three different ways MD 5 Checksums all different Digital DNA remains consistent
The Future Vision Technical Discussion
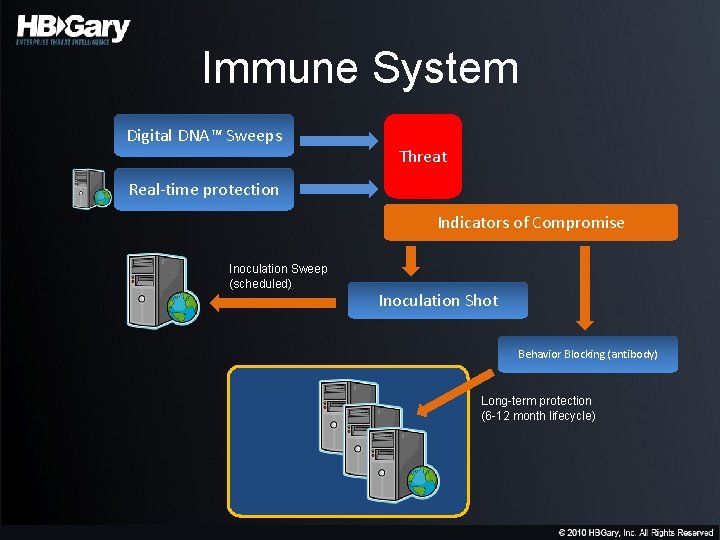
Immune System Digital DNA™ Sweeps Threat Real-time protection Indicators of Compromise Inoculation Sweep (scheduled) Inoculation Shot Behavior Blocking (antibody) Long-term protection (6 -12 month lifecycle)
- Slides: 36