
Leveraging the HECVAT for Cloud Vendor Assessments Introductions
- Slides: 35
Leveraging the HECVAT for Cloud Vendor Assessments
Introductions
What the HECVAT • Project is two years old • Goal to simplify, expedite and get higher quality assessments • A win for the schools and the vendors
HECVAT Phase 2 • Updated HECVAT • Crosswalk • Cloud Broker Index (CBI)
Crosswalk • • • CIS Critical Controls HIPAA ISO: 27002: 2013 NIST Cybersecurity Framework NIST 800 -171 r 1 NIST 800 -53 r 4
HECVAT & the CBI • CBI = Cloud Broker Index • Balance accessibility with privacy • https: //www. renisac. net/hecvat/cbi. html
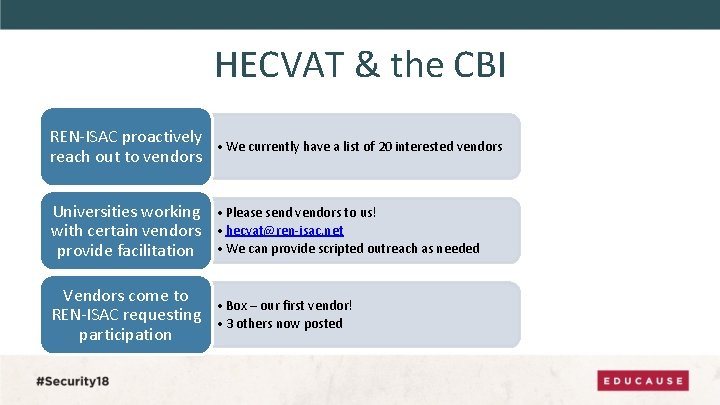
HECVAT & the CBI REN-ISAC proactively • We currently have a list of 20 interested vendors reach out to vendors Universities working • Please send vendors to us! with certain vendors • hecvat@ren-isac. net provide facilitation • We can provide scripted outreach as needed Vendors come to • Box – our first vendor! REN-ISAC requesting • 3 others now posted participation
CBI • www. ren-isac. net/hecvat/cbi. html
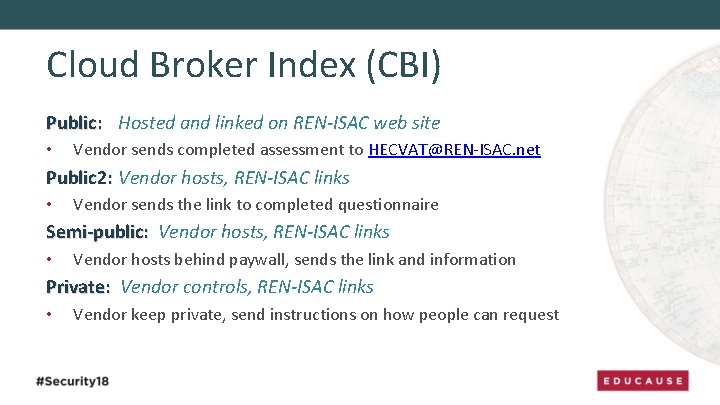
Cloud Broker Index (CBI) Public: Hosted and linked on REN-ISAC web site • Vendor sends completed assessment to HECVAT@REN-ISAC. net Public 2: Vendor hosts, REN-ISAC links • Vendor sends the link to completed questionnaire Semi-public: Vendor hosts, REN-ISAC links Semi-public: • Vendor hosts behind paywall, sends the link and information Private: Vendor controls, REN-ISAC links Private: • Vendor keep private, send instructions on how people can request
HECVAT & the CBI
West Virginia University’s Case Study
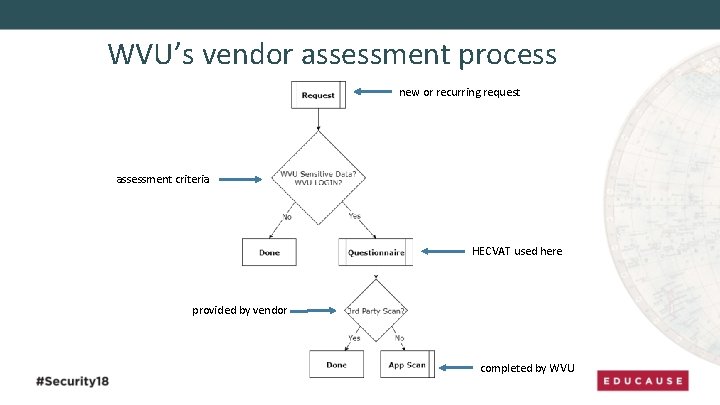
WVU’s vendor assessment process new or recurring request assessment criteria HECVAT used here provided by vendor completed by WVU
Questionnaire • On-line form • Uses HECVAT questions • Vendor results compiled for analysis
What’s Next • Current process has limits • Purchasing a Governance Risk and Compliance system • HECVAT to be used in the vendor assessment module
Indiana University Case Study
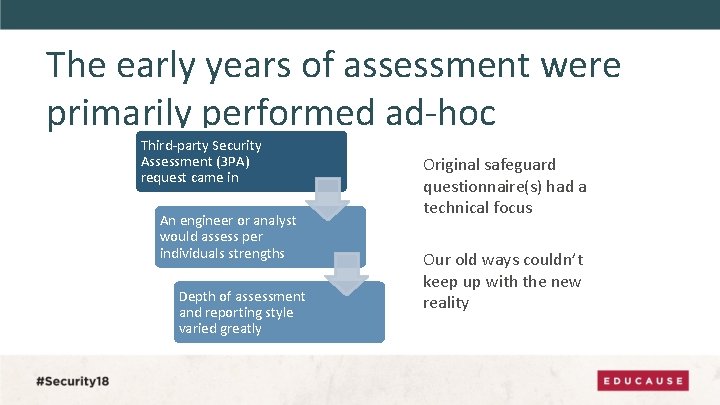
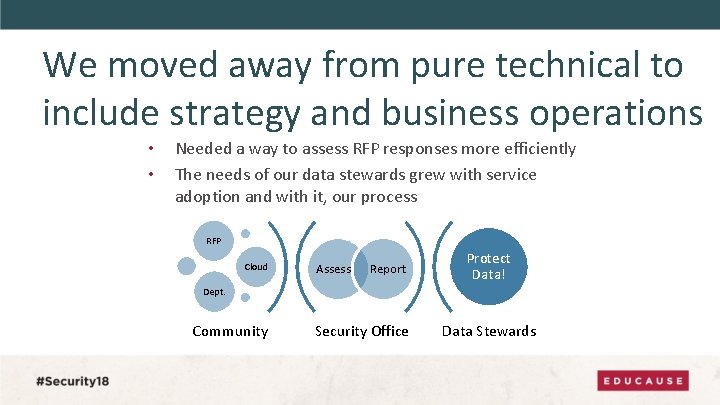
The early years of assessment were primarily performed ad-hoc Third-party Security Assessment (3 PA) request came in An engineer or analyst would assess per individuals strengths Depth of assessment and reporting style varied greatly Original safeguard questionnaire(s) had a technical focus Our old ways couldn’t keep up with the new reality
We moved away from pure technical to include strategy and business operations • • Needed a way to assess RFP responses more efficiently The needs of our data stewards grew with service adoption and with it, our process RFP Cloud Assess Report Protect Data! Dept. Community Security Office Data Stewards
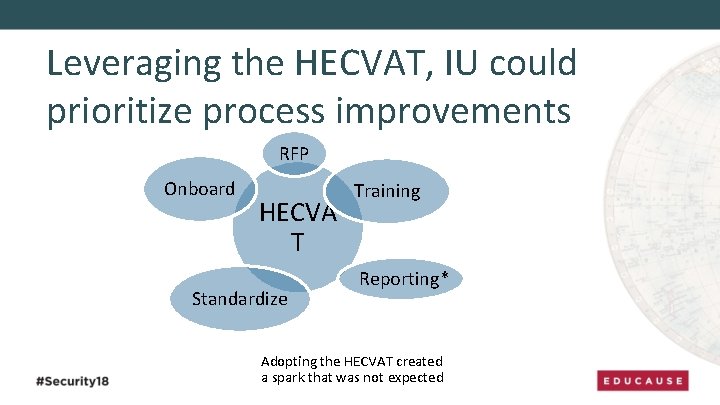
Leveraging the HECVAT, IU could prioritize process improvements RFP Onboard HECVA T Standardize Training Reporting* Adopting the HECVAT created a spark that was not expected
University of Toronto Case Study
I have a HECVAT – now what? Case study • The Good • The Arrogant • The New
Documented Info. Sec policy? • Good – Yes; reviewed, updated, and approved by management at least annually. • Arrogant - Proprietary and Confidential • New – Yes; document attached
Scan for vulnerabilities < new release • Good - manual and automated built in; Weekly web application vulnerability scans • Arrogant – Provide documentation that a scan was performed. • New - Scan prior to deployment; actively developing ability to provide results.
Data input validation The good • must validate all inputs against acceptable values for the context. • performs daily web application scanning to validate Input Validation and Sanitization techniques.
Data input validation • The arrogant – and wrong answer • This is for LMS integration. Authentication and authorization data will result from School administrator configured tools and the LMS. Direct authentication is not in scope and not available for this integration
Data input validation • The New • examples of validation error messages are given in the User Guide. • follows OWASP recommendations for data validation best practices.
Log security/Authz changes? • Good – Available; integrates with SIEM • Arrogant - Proprietary and confidential; Screen shot could be provided • New – basically everything logged; No Customer view mentioned
Cloud Security • • New Data Streams: New Disclosures, New Uses Unauthorized Processing/Secondary Purposes Covert Surveillance Breach Detection, Remediation and Reporting Data Permanence Loss of Access Jurisdiction • https: //www. ipc. on. ca/wp-content/uploads/2016/08/Thinking-About-Clouds-1. pdf
Cloud Vendor contracts • Define access to data for incident analysis • • Will they inform you of a breach? How do you carry out an incident analysis? Will your access to the data cost money? Who informs your users?
Cloud Vendor Contracts cont • Continued Security audits • Retention of data • Jurisdiction concerns
Cloud Vendor Contracts cont • Vendor Lock in • Define data format; exit terms • Vendor third parties • The Vendor is your agent – what about the vendor’s third parties?
Call to Community • • Commit to HECVAT Allow referencing Educate Vendors Give feedback
Phase 3 • Engage vendors • For HECVAT awareness • CBI participation • Automated triage
Educause Webinar • For Educause vendor partners to learn about the HECVAT • July 30 th 1: 30 ET
Tools to Triage • Automate scoring of HECVAT • Highlight areas of possible deficiency • May not cover the full HECVAT question list
Feedback and Questions