
Leveraging HITRUST as Part of Your Risk Management
- Slides: 33
Leveraging HITRUST as Part of Your Risk Management Program 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 1 © 2018 HITRUST Alliance
Introduction to the HITRUST team Michael Parisi has led over 500 controls-related engagements primarily in the healthcare and financial services industries. He has extensive experience with third-party assurance reporting including HITRUST readiness, HITRUST certification, SOC 1, SOC 2, SOC 3, Agreed Upon Procedure and customized AT-101 engagements. He also has several years’ experience implementing large Oracle ERP systems specializing in the General Ledger and Governance Risk and Compliance modules. He has extensive knowledge of financial reporting and regulatory standards through his external audit and consulting experience, including Sarbanes Oxley, HIPAA, NIST, CMS and state specific standards. He holds a Bachelor of Science in Accounting, a Bachelor of Science in Computer Information Systems and an MBA from Quinnipiac University and is an active member of ISACA. Michael Parisi Vice President, Assurance Strategy & Community Development Michael. Parisi@Hitrustalliance. net 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 2 © 2018 HITRUST Alliance
Objectives By the end of this presentation, you will have learned 1. How to leverage the HITRUST Assurance Program in support of an overall enterprise risk management function 2. How third-party risk management under an enterprise risk management program can be streamlined and designed to be more effective by using TPA reporting 3. How organizations across multiple industries are leveraging HITRUST programs 4. How organizations are leveraging HITRUST programs and reporting as a market differentiator in the sales cycle 5. Clarification around common questions and misconceptions related to HITRUST programs (facts and myths) 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 3 © 2018 HITRUST Alliance
Section 1 ABOUT HITRUST 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 4 © 2018 HITRUST Alliance
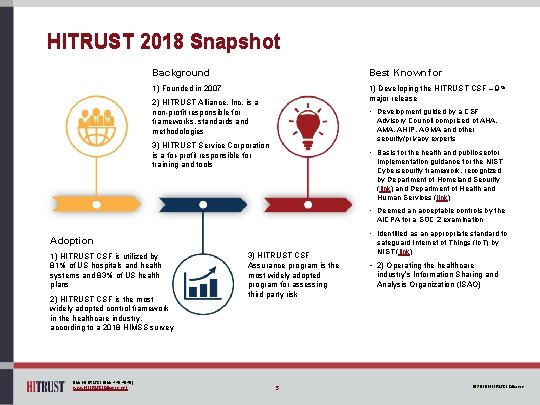
HITRUST 2018 Snapshot Background Best Known for 1) Founded in 2007 1) Developing the HITRUST CSF – 9 th major release 2) HITRUST Alliance, Inc. is a non-profit responsible for frameworks, standards and methodologies • Development guided by a CSF Advisory Council comprised of AHA, AMA, AHIP, AGMA and other security/privacy experts 3) HITRUST Service Corporation is a for-profit responsible for training and tools • Basis for the health and public sector implementation guidance for the NIST Cybersecurity framework, recognized by Department of Homeland Security (link) and Department of Health and Human Services (link) • Deemed an acceptable controls by the AICPA for a SOC 2 examination • Identified as an appropriate standard to Adoption 1) HITRUST CSF is utilized by 81% of US hospitals and health systems and 83% of US health plans 2) HITRUST CSF is the most widely adopted control framework in the healthcare industry, according to a 2018 HIMSS survey 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 3) HITRUST CSF Assurance program is the most widely adopted program for assessing third party risk 5 safeguard Internet of Things (Io. T) by NIST (link) • 2) Operating the healthcare industry’s Information Sharing and Analysis Organization (ISAO) © 2018 HITRUST Alliance
Section 2 RISK MANAGEMENT 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 6 © 2018 HITRUST Alliance
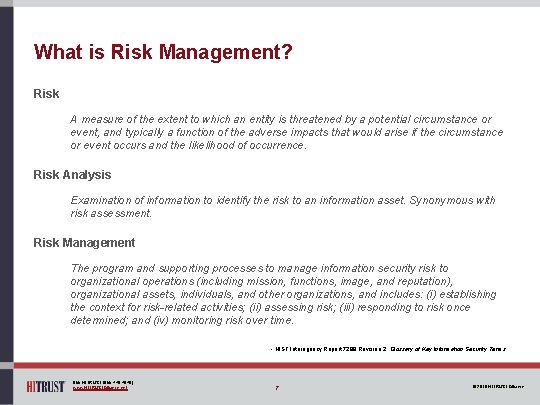
What is Risk Management? Risk A measure of the extent to which an entity is threatened by a potential circumstance or event, and typically a function of the adverse impacts that would arise if the circumstance or event occurs and the likelihood of occurrence. Risk Analysis Examination of information to identify the risk to an information asset. Synonymous with risk assessment. Risk Management The program and supporting processes to manage information security risk to organizational operations (including mission, functions, image, and reputation), organizational assets, individuals, and other organizations, and includes: (i) establishing the context for risk-related activities; (ii) assessing risk; (iii) responding to risk once determined; and (iv) monitoring risk over time. - NIST Interagency Report 7298 Revision 2, Glossary of Key Information Security Terms 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 7 © 2018 HITRUST Alliance
Polling Question #1 Is your organization a? a. Covered Entity b. Business Associate c. Vendor d. Other 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 8 © 2018 HITRUST Alliance
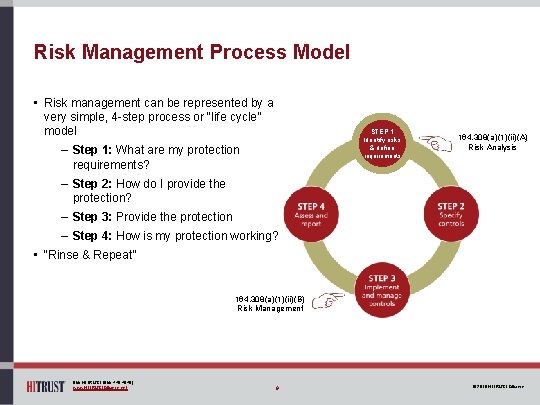
Risk Management Process Model • Risk management can be represented by a very simple, 4 -step process or “life cycle” model – Step 1: What are my protection requirements? STEP 1 Identify risks & define 164. 308(a)(1)(ii)(A) Risk Analysis requirements – Step 2: How do I provide the protection? – Step 3: Provide the protection – Step 4: How is my protection working? • “Rinse & Repeat” 164. 308(a)(1)(ii)(B) Risk Management 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 9 © 2018 HITRUST Alliance
Section 3 RISK MANAGEMENT FRAMEWORKS 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 10 © 2018 HITRUST Alliance
Risk Management Frameworks • A risk management framework (RMF) provides an overall approach to managing information security risk throughout the information and information system life cycle and typically includes: – Lexicon (vocabulary) and taxonomy (classification/structure) for information security risk management – Methodology for evaluating and treating information security risk • A control-based risk management framework (RMF) provides an overall approach to managing information security risk via the design, implementation, monitoring/assessment, review and improvement of security controls throughout the information and information system lifecycle and typically includes: – Lexicon (vocabulary) and taxonomy (classification/structure) for information security risk management – Methodology for evaluating and treating information security risk – Set of security controls from which to choose/implement – Methodology for the selection and implementation of security controls – Methodology for the evaluation, review and improvement of security controls When referring to RMFs throughout the rest of the presentation, we refer specifically to control-based RMFs 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 11 © 2018 HITRUST Alliance
Common Risk Management Frameworks Examples include but are not limited to: • The HITRUST CSF and supporting publications: used extensively by commercial entities in the healthcare industry and increasingly by nonhealthcare organizations • National Institute of Standards & Technology (NIST) – Framework for Improving Critical Infrastructure Cybersecurity, more commonly known as the NIST Cybersecurity Framework: intended to be an overarching framework for understanding and communicating information (cyber) security in the public and private sectors – NIST SP 800 -series publications: typically used by U. S. federal agencies to support FISMA-compliance, but also used by other governments and commercial entities • Organization for International Standards (ISO) 27000 -series publications: used by some governments and commercial entities, mostly non-U. S. 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 12 © 2018 HITRUST Alliance
Polling Question #2 Are you currently leveraging any HITRUST programs or have you ever? a. Yes b. No 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 13 © 2018 HITRUST Alliance
Attributes of a Good Risk Management Framework • The framework should provide comprehensive coverage of general security requirements and provide prescriptive controls (safeguards), i. e. , the control requirements should be detailed support implementation in the intended environment and adequately address the threat(s) • The framework’s controls should be practical for an organization to implement and maintain, and scalable based on the size and type of organization or information system being protected • The controls and implementation, assessment and reporting methodologies should be vetted by organizations and industry experts such as leading professional services firms via an open and transparent development and update process • The controls specified in the framework should be supported by detailed audit or assessment guidance that helps ensure consistency and accuracy in evaluation and reporting regardless of the specific assessor used • The framework should be efficient and allow an organization to assess once and report many, i. e. , an assessment must address multiple compliance and best practice requirements and support the reporting of assurances tailored to each requirement • Evaluation of the framework’s implementation should be reliable, i. e. , organizations should be able to rely on the assurances provided by internal and external assessments 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 14 © 2018 HITRUST Alliance
Section 4 THE HITRUST RISK MANAGEMENT FRAMEWORK 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 15 © 2018 HITRUST Alliance
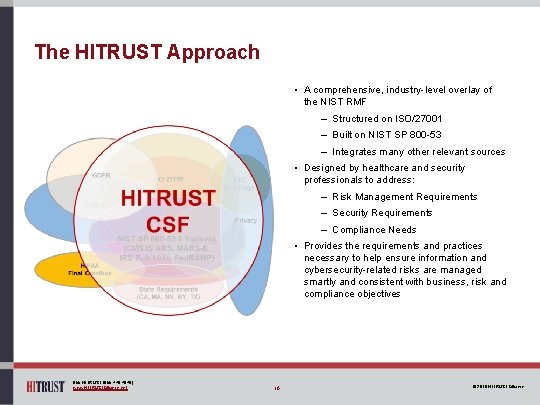
The HITRUST Approach • A comprehensive, industry-level overlay of the NIST RMF – Structured on ISO/27001 – Built on NIST SP 800 -53 – Integrates many other relevant sources • Designed by healthcare and security professionals to address: – Risk Management Requirements – Security Requirements – Compliance Needs • Provides the requirements and practices necessary to help ensure information and cybersecurity-related risks are managed smartly and consistent with business, risk and compliance objectives 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 16 © 2018 HITRUST Alliance
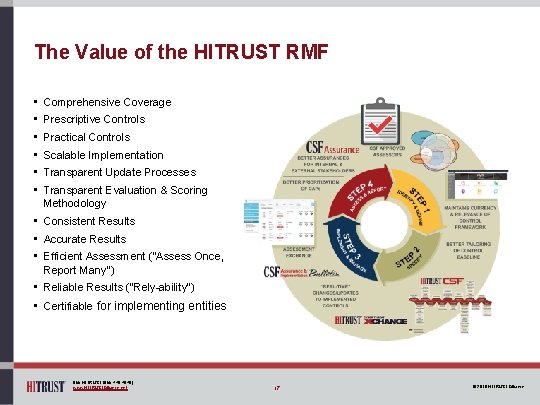
The Value of the HITRUST RMF • Comprehensive Coverage • Prescriptive Controls • Practical Controls • Scalable Implementation • Transparent Update Processes • Transparent Evaluation & Scoring Methodology • Consistent Results • Accurate Results • Efficient Assessment (“Assess Once, Report Many”) • Reliable Results (“Rely-ability”) • Certifiable for implementing entities 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 17 © 2018 HITRUST Alliance
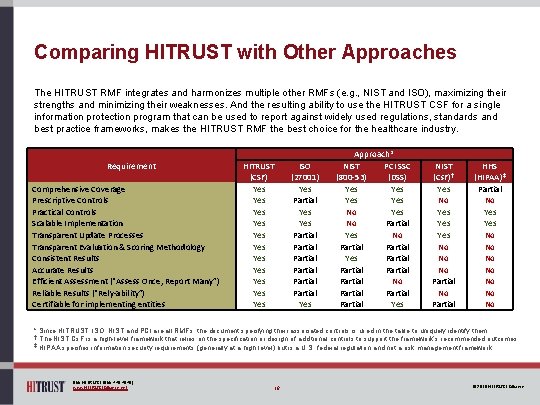
Comparing HITRUST with Other Approaches The HITRUST RMF integrates and harmonizes multiple other RMFs (e. g. , NIST and ISO), maximizing their strengths and minimizing their weaknesses. And the resulting ability to use the HITRUST CSF for a single information protection program that can be used to report against widely used regulations, standards and best practice frameworks, makes the HITRUST RMF the best choice for the healthcare industry. Requirement Comprehensive Coverage Prescriptive Controls Practical Controls Scalable Implementation Transparent Update Processes Transparent Evaluation & Scoring Methodology Consistent Results Accurate Results Efficient Assessment (“Assess Once, Report Many”) Reliable Results (“Rely-ability”) Certifiable for implementing entities HITRUST (CSF) Yes Yes Yes ISO (27001) Yes Partial Partial Yes Approach* NIST PCI SSC (800 -53) (DSS) Yes Yes No Partial Yes Partial No Partial Yes NIST (Cs. F)† Yes No Yes Yes No No No Partial HHS (HIPAA)‡ Partial No Yes No No * Since HITRUST, ISO, NIST and PCI are all RMFs, the document specifying their associated controls is used in the table to uniquely identify them † The NIST Cs. F is a high-level framework that relies on the specification or design of additional controls to support the framework’s recommended outcomes ‡ HIPAA specifies information security requirements (generally at a high level) but is a U. S. federal regulation and not a risk management framework 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 18 © 2018 HITRUST Alliance
Section 5 HITRUST CSF Third Party Assurance Program 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 19 © 2018 HITRUST Alliance
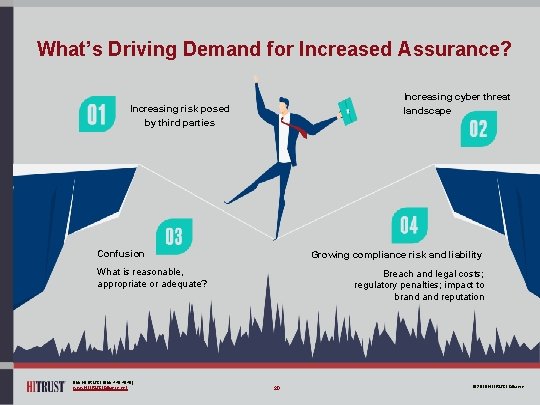
What’s Driving Demand for Increased Assurance? Section 2 Increasing cyber threat landscape Increasing risk posed by third parties Confusion Growing compliance risk and liability What is reasonable, appropriate or adequate? 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net Breach and legal costs; regulatory penalties; impact to brand reputation 20 © 2018 HITRUST Alliance
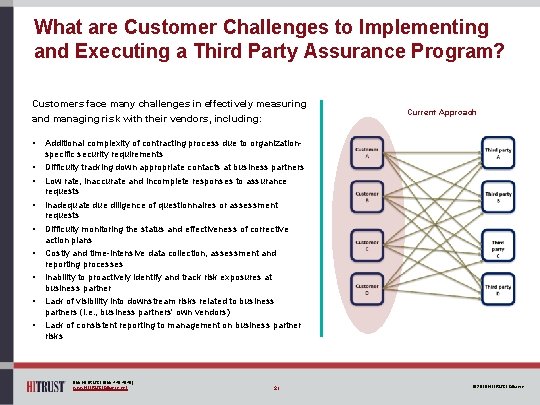
What are Customer Challenges to Implementing and Executing a Third Party Assurance Program? Customers face many challenges in effectively measuring and managing risk with their vendors, including: • • • Current Approach Additional complexity of contracting process due to organizationspecific security requirements Difficulty tracking down appropriate contacts at business partners Low rate, inaccurate and incomplete responses to assurance requests Inadequate due diligence of questionnaires or assessment requests Difficulty monitoring the status and effectiveness of corrective action plans Costly and time-intensive data collection, assessment and reporting processes Inability to proactively identify and track risk exposures at business partner Lack of visibility into downstream risks related to business partners (i. e. , business partners' own vendors) Lack of consistent reporting to management on business partner risks 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 21 © 2018 HITRUST Alliance
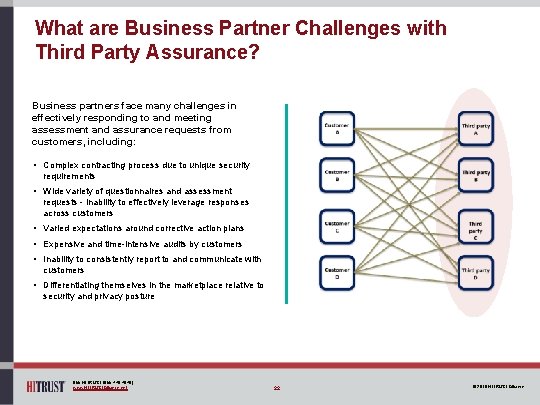
What are Business Partner Challenges with Third Party Assurance? Business partners face many challenges in effectively responding to and meeting assessment and assurance requests from customers, including: • Complex contracting process due to unique security requirements • Wide variety of questionnaires and assessment requests - inability to effectively leverage responses across customers • Varied expectations around corrective action plans • Expensive and time-intensive audits by customers • Inability to consistently report to and communicate with customers • Differentiating themselves in the marketplace relative to security and privacy posture 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 22 © 2018 HITRUST Alliance
Universal Agreement that the Current Model for Third Party Assurance is Broken There are no scenarios where performing 15, 50 or 250 or more unique assessments makes sense for a vendor to communicate their information privacy and security posture (relating to the same scope of services) Nor does it make sense to maintain and support organization-specific assessment methodologies and multiple assessments for each organization HITRUST has been working with customers and business partners to identify a practical and implementable approach 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 23 © 2018 HITRUST Alliance
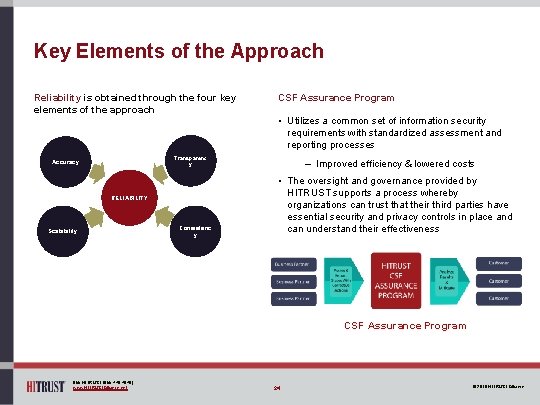
Key Elements of the Approach Reliability is obtained through the four key elements of the approach CSF Assurance Program • Utilizes a common set of information security requirements with standardized assessment and reporting processes Transparenc y Accuracy RELIABILITY Scalability Consistenc y – Improved efficiency & lowered costs • The oversight and governance provided by HITRUST supports a process whereby organizations can trust that their third parties have essential security and privacy controls in place and can understand their effectiveness CSF Assurance Program 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 24 © 2018 HITRUST Alliance
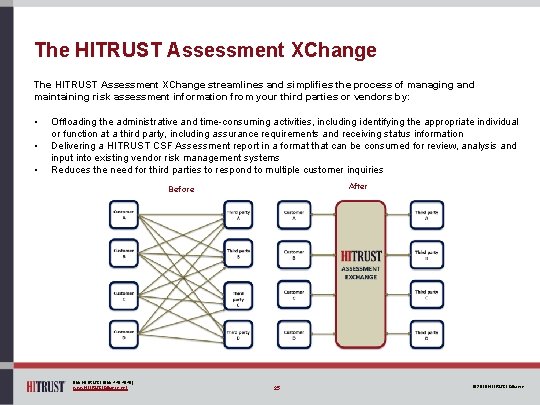
The HITRUST Assessment XChange streamlines and simplifies the process of managing and maintaining risk assessment information from your third parties or vendors by: • • • Offloading the administrative and time-consuming activities, including identifying the appropriate individual or function at a third party, including assurance requirements and receiving status information Delivering a HITRUST CSF Assessment report in a format that can be consumed for review, analysis and input into existing vendor risk management systems Reduces the need for third parties to respond to multiple customer inquiries After Before 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 25 © 2018 HITRUST Alliance
How does the Assessment XChange help? Third party outreach • Contacts third parties, and identifies points of contact • Coordinates third-party assessment management and tracking ensures efficient outreach and emphasizes importance…coordinated outreach on behalf of multiple organizations Third Party Education Experienced HITRUST personnel to explain and answer questions on the assessment & assurance processes Third party assessment expectations • Ensuring that the assessment information obtained from third parties is inline with customer contractual obligations Visibility into status of third parties/third party assurance • Provides status updates during the process to support progress tracking • More granular information about a third party’s security posture including CAPs and GAPS by providing the full report Provides the ability to electronically receive or export results in a format that is easy to consume into GRC or VRM solutions • Open API integration to existing vendor risk management and governance risk and compliance tools • Create and report on security metrics across a third party population 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 26 © 2018 HITRUST Alliance
Common Questions • I thought the HITRUST CSF was for healthcare? • Does this mean I have to redo my security program? • How does HITRUST relate to SOC 2 reporting? • Does it comply with HIPAA’s risk analysis requirements? • Why can’t I just use the NIST Cybersecurity Framework? • How can smaller organizations leverage the HITRUST programs? • What are the costs to implement HITRUST and go through an assessment process? 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 27 © 2018 HITRUST Alliance
HITRUST Facts and Myths • You don’t have to choose between HITRUST, NIST or ISO as your risk management framework (fact) • Adopting and complying with the HITRUST CSF is more complicated compared to other frameworks (myth) • The HISTRUST CSF is a risk-based framework (fact) • You can adopt the NIST Cybersecurity Framework by itself (myth) • NIST doesn't provide a certification against the NIST Cybersecurity Framework (fact) • Getting assessed against the HITRUST CSF is more expensive than other assessments (myth) 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 28 © 2018 HITRUST Alliance
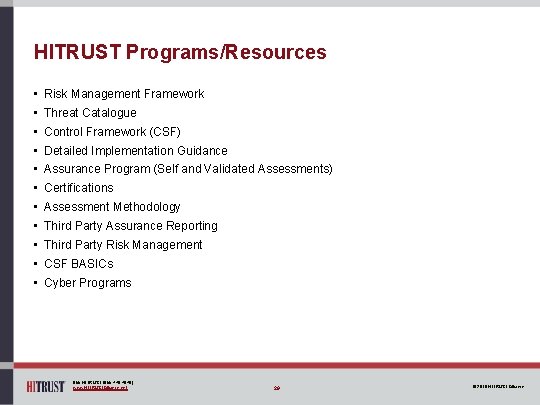
HITRUST Programs/Resources • Risk Management Framework • Threat Catalogue • Control Framework (CSF) • Detailed Implementation Guidance • Assurance Program (Self and Validated Assessments) • Certifications • Assessment Methodology • Third Party Assurance Reporting • Third Party Risk Management • CSF BASICs • Cyber Programs 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 29 © 2018 HITRUST Alliance
Upcoming Webinars from HITRUST • Right Start Program – November 13 th, 2018 • Threat Catalogue – November 29 th, 2018 • Provider Third Party Risk Management Council – December 2018 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 30 © 2018 HITRUST Alliance
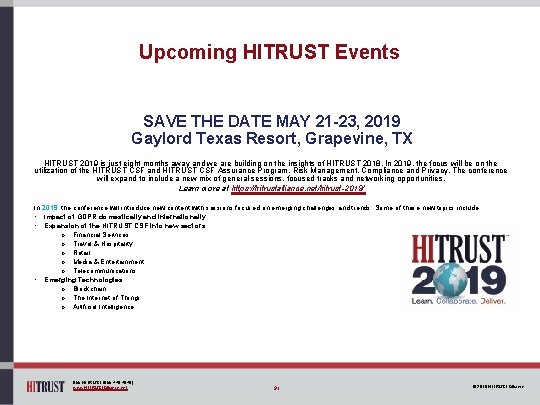
Upcoming HITRUST Events SAVE THE DATE MAY 21 -23, 2019 Gaylord Texas Resort, Grapevine, TX HITRUST 2019 is just eight months away and we are building on the insights of HITRUST 2018. In 2019, the focus will be on the utilization of the HITRUST CSF and HITRUST CSF Assurance Program, Risk Management, Compliance and Privacy. The conference will expand to include a new mix of general sessions, focused tracks and networking opportunities. Learn more at https: //hitrustalliance. net/hitrust-2019/ In 2019, the conference will introduce new content with sessions focused on emerging challenges and trends. Some of these new topics include: • Impact of GDPR domestically and internationally • Expansion of the HITRUST CSF into new sectors o Financial Services o Travel & Hospitality o Retail o Media & Entertainment o Telecommunications • Emerging Technologies o Blockchain o The Internet of Things o Artificial Intelligence 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 31 © 2018 HITRUST Alliance
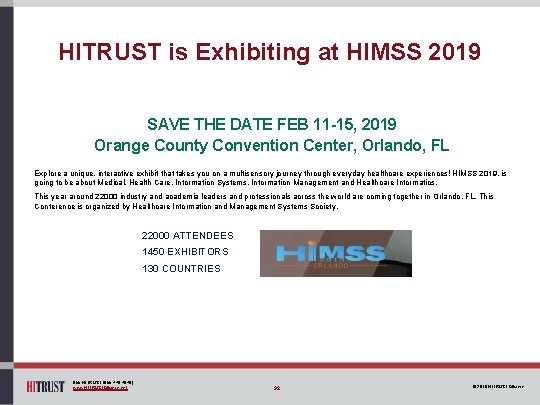
HITRUST is Exhibiting at HIMSS 2019 SAVE THE DATE FEB 11 -15, 2019 Orange County Convention Center, Orlando, FL Explore a unique, interactive exhibit that takes you on a multisensory journey through everyday healthcare experiences! HIMSS 2019, is going to be about Medical, Health Care, Information Systems, Information Management and Healthcare Informatics. This year around 22000 industry and academia leaders and professionals across the world are coming together in Orlando, FL. This Conference is organized by Healthcare Information and Management Systems Society. 22000 ATTENDEES 1450 EXHIBITORS 130 COUNTRIES 855. HITRUST (855. 448. 7878) www. HITRUSTAlliance. net 32 © 2018 HITRUST Alliance
For more information on HITRUST visit www. HITRUSTAlliance. net To view our latest documents, visit the Content Spotlight