
Kaspersky Threat Intelligence Services pro vae organizace Vladimr
- Slides: 25
Kaspersky Threat Intelligence Services pro vaše organizace Vladimír Váňa, Territory Channel Manager, Kaspersky
Facts about us > 22 years of history > 4, 000 highly qualified specialists > 400, 000 users worldwide are protected by our technologies > 270, 000 corporate clients worldwide
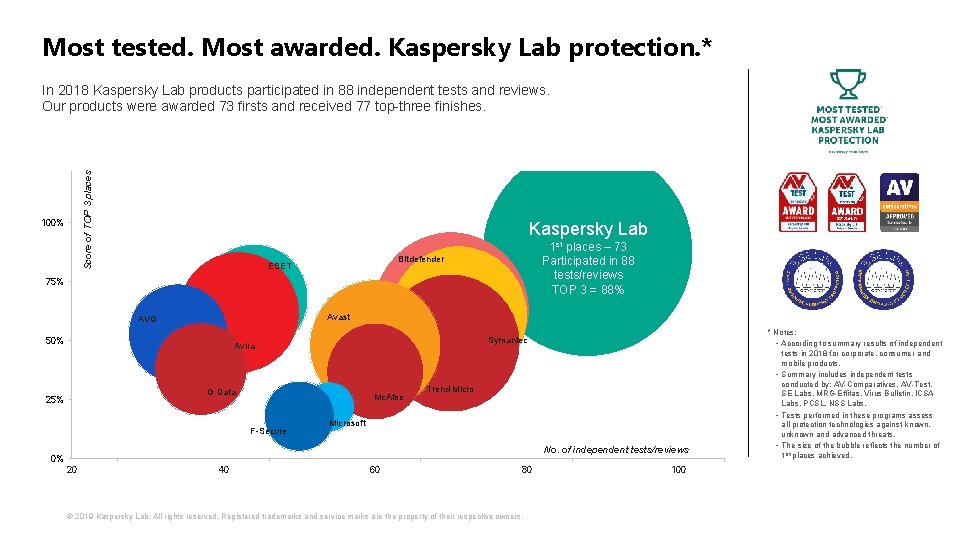
Most tested. Most awarded. Kaspersky Lab protection. * Score of TOP 3 places In 2018 Kaspersky Lab products participated in 88 independent tests and reviews. Our products were awarded 73 firsts and received 77 top-three finishes. 100% Kaspersky Lab 1 st places – 73 Participated in 88 tests/reviews TOP 3 = 88% Bitdefender ESET 75% Avast AVG 50% Symantec Avira G Data 25% Mc. Afee F-Secure Trend Microsoft No. of independent tests/reviews 0% 20 40 60 80 © 2019 Kaspersky Lab. All rights reserved. Registered trademarks and service marks are the property of their respective owners. 100 * Notes: • According to summary results of independent tests in 2018 for corporate, consumer and mobile products. • Summary includes independent tests conducted by: AV-Comparatives, AV-Test, SE Labs, MRG-Effitas, Virus Bulletin, ICSA Labs, PCSL, NSS Labs. • Tests performed in these programs assess all protection technologies against known, unknown and advanced threats. • The size of the bubble reflects the number of 1 st places achieved.
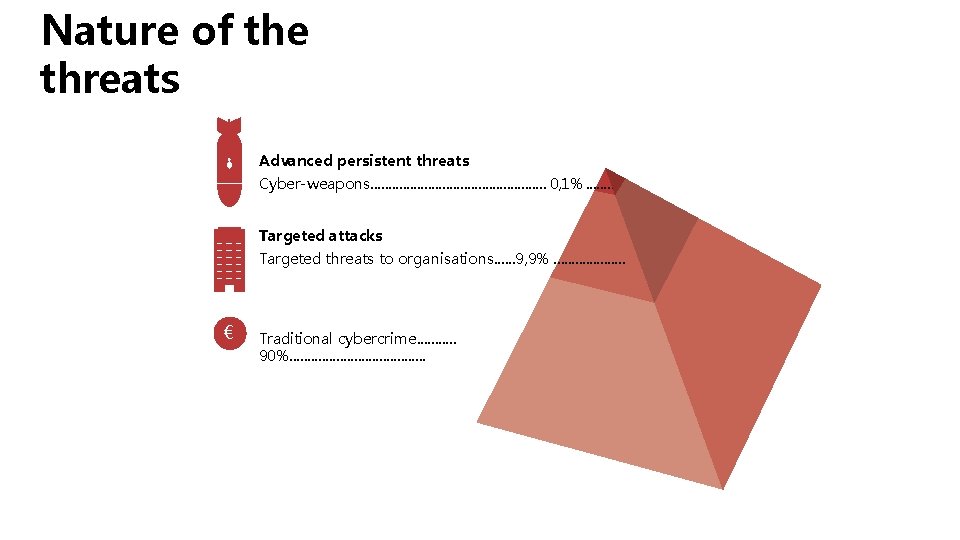
Nature of the threats Advanced persistent threats Cyber-weapons. . . 0, 1%. . Targeted attacks Targeted threats to organisations. . . 9, 9%. . . . . € Traditional cybercrime. . . 90%. . . . . 1 0
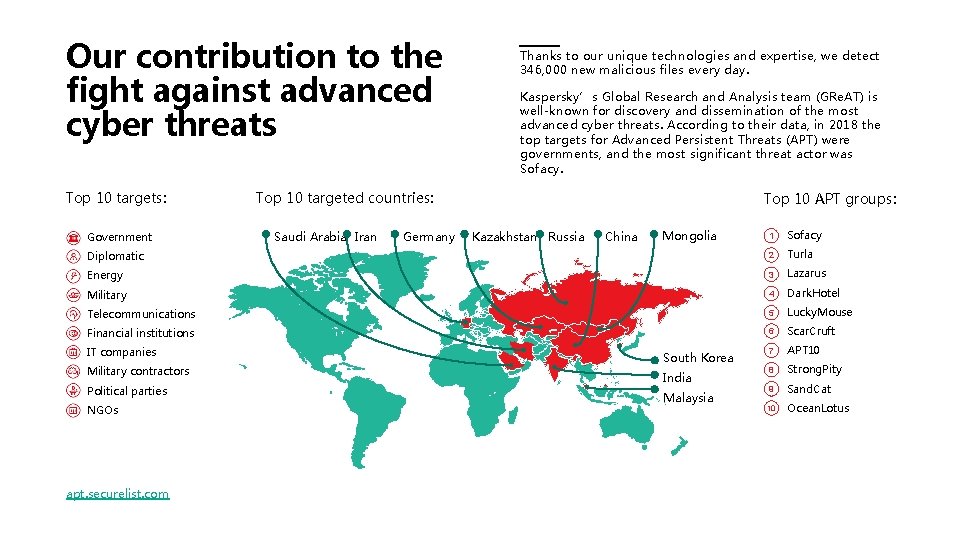
Our contribution to the fight against advanced cyber threats Top 10 targets: Thanks to our unique technologies and expertise, we detect 346, 000 new malicious files every day. Kaspersky’s Global Research and Analysis team (GRe. AT) is well-known for discovery and dissemination of the most advanced cyber threats. According to their data, in 2018 the top targets for Advanced Persistent Threats (APT) were governments, and the most significant threat actor was Sofacy. Top 10 targeted countries: Top 10 APT groups: Mongolia 1 Sofacy Diplomatic 2 Turla Energy 3 Lazarus Military 4 Dark. Hotel Telecommunications 5 Lucky. Mouse Financial institutions 6 Scar. Cruft 7 APT 10 8 Strong. Pity 9 Sand. Cat 10 Ocean. Lotus Government IT companies Military contractors Political parties NGOs apt. securelist. com Saudi Arabia Iran Germany Kazakhstan Russia China South Korea India Malaysia
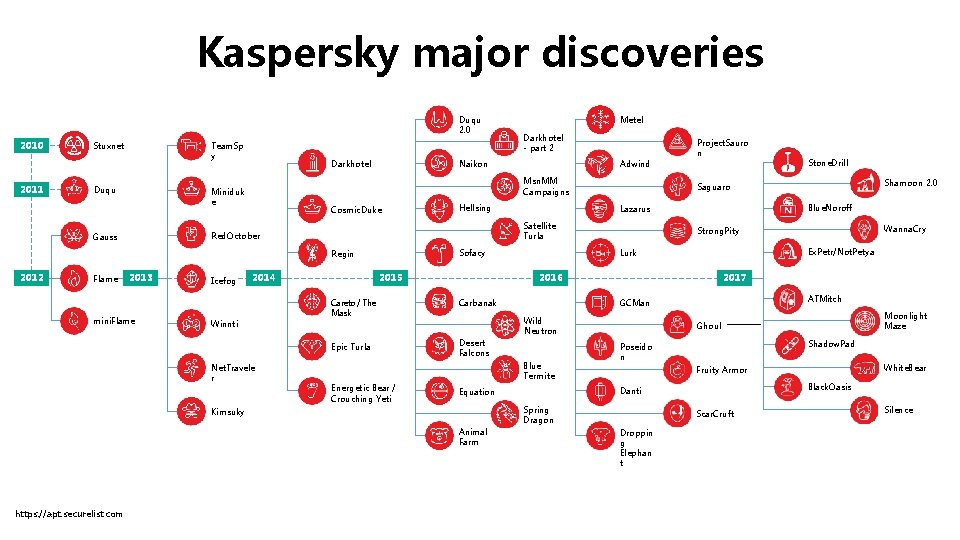
Kaspersky major discoveries Duqu 2. 0 2011 Team. Sp y Stuxnet Duqu Flame Cosmic. Duke Hellsing mini. Flame Icefog 2014 Winnti Careto / The Mask Epic Turla Net. Travele r Energetic Bear / Crouching Yeti Wild Neutron Animal Farm ATMitch Moonlight Maze Ghoul Shadow. Pad Poseido n White. Bear Fruity Armor Black. Oasis Danti Equation Kimsuky https: //apt. securelist. com 2017 GCMan Blue Termite Wanna. Cry Ex. Petr/Not. Petya 2016 Desert Falcons Shamoon 2. 0 Strong. Pity Lurk Carbanak Stone. Drill Blue. Noroff Lazarus Sofacy 2015 Project. Sauro n Saguaro Satellite Turla Red. October 2013 Adwind Msn. MM Campaigns Regin 2012 Darkhotel - part 2 Naikon Darkhotel Miniduk e Gauss Metel Spring Dragon Scar. Cruft Droppin g Elephan t Silence
? Security Operations Center
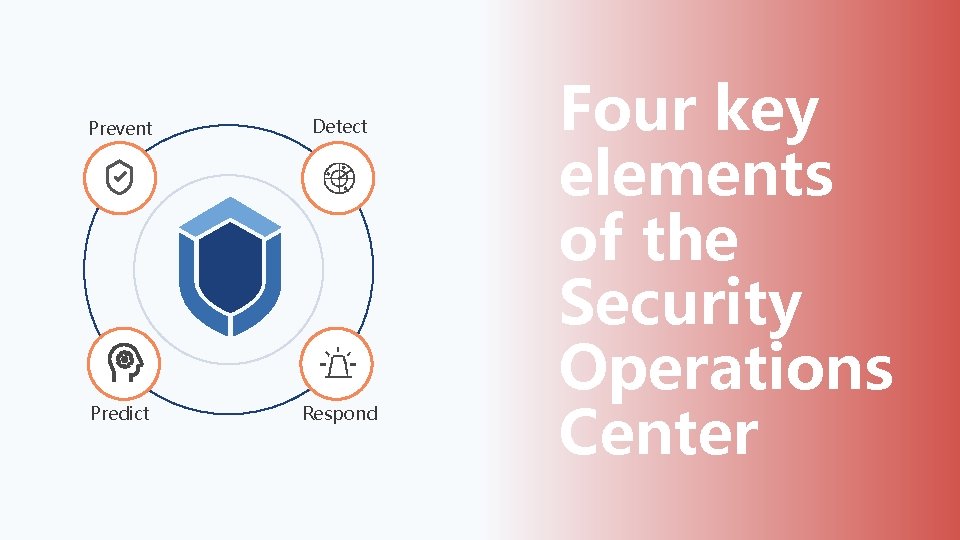
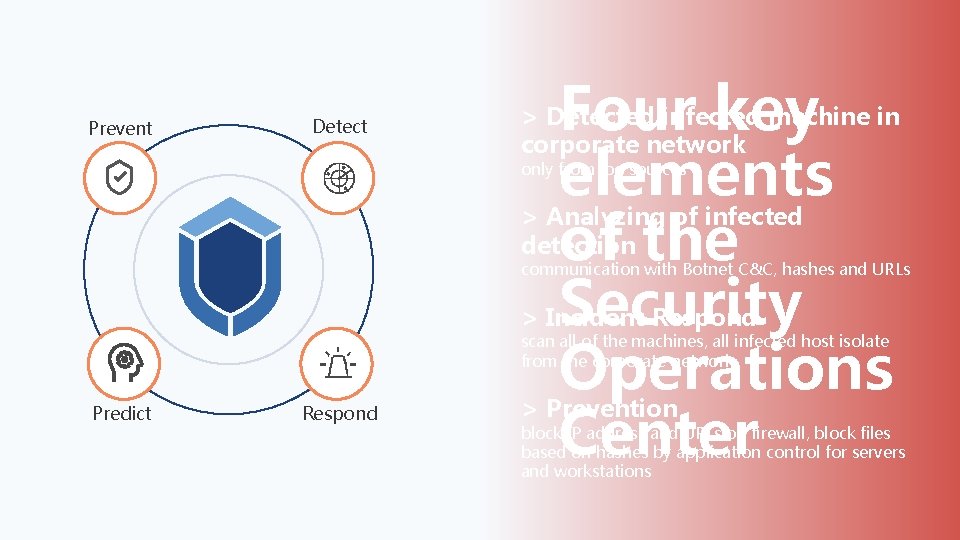
Prevent Detect Predict Respond Four key elements of the Security Operations Center
Kaspersky Threat Data Feeds
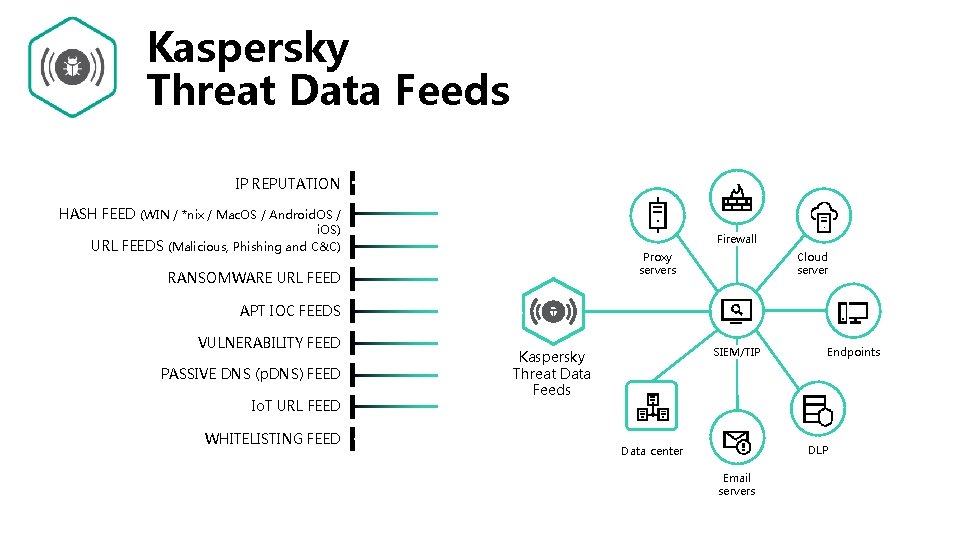
Kaspersky Threat Data Feeds IP REPUTATION HASH FEED (WIN / *nix / Mac. OS / Android. OS / i. OS) URL FEEDS (Malicious, Phishing and C&C) Firewall Proxy servers RANSOMWARE URL FEED Cloud server APT IOC FEEDS VULNERABILITY FEED PASSIVE DNS (p. DNS) FEED Io. T URL FEED WHITELISTING FEED SIEM/TIP Kaspersky Threat Data Feeds Endpoints DLP Data center Email servers
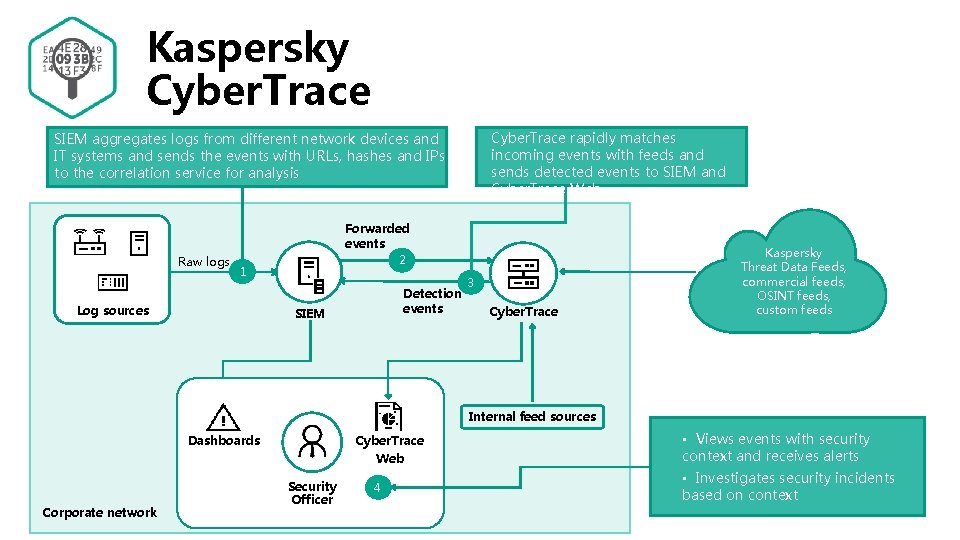
Kaspersky Cyber. Trace rapidly matches incoming events with feeds and sends detected events to SIEM and Cyber. Trace Web SIEM aggregates logs from different network devices and IT systems and sends the events with URLs, hashes and IPs to the correlation service for analysis Raw logs Forwarded events 2 1 Log sources Detection events SIEM 3 Cyber. Trace Kaspersky Threat Data Feeds, commercial feeds, OSINT feeds, custom feeds Internal feed sources Dashboards Corporate network Cyber. Trace Web Security Officer 4 • Views events with security context and receives alerts • Investigates security incidents based on context
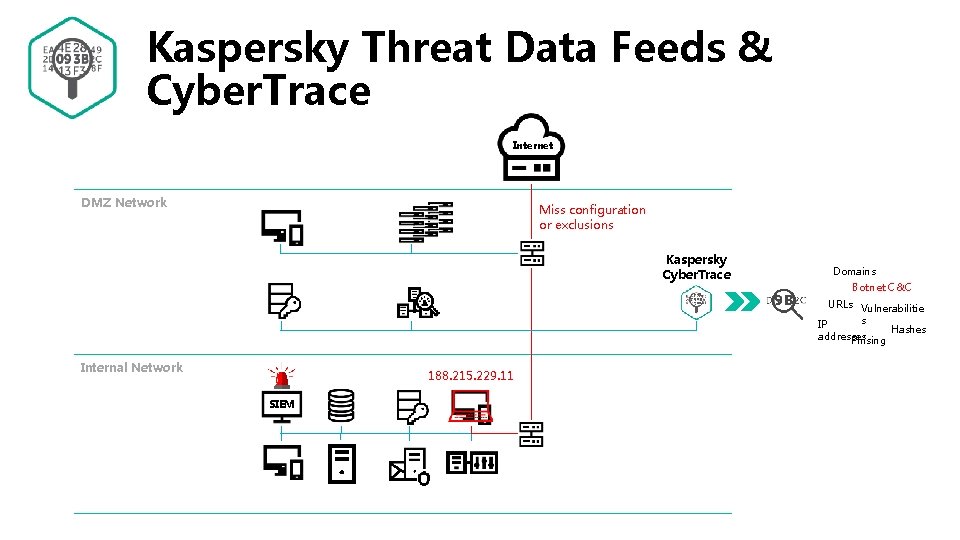
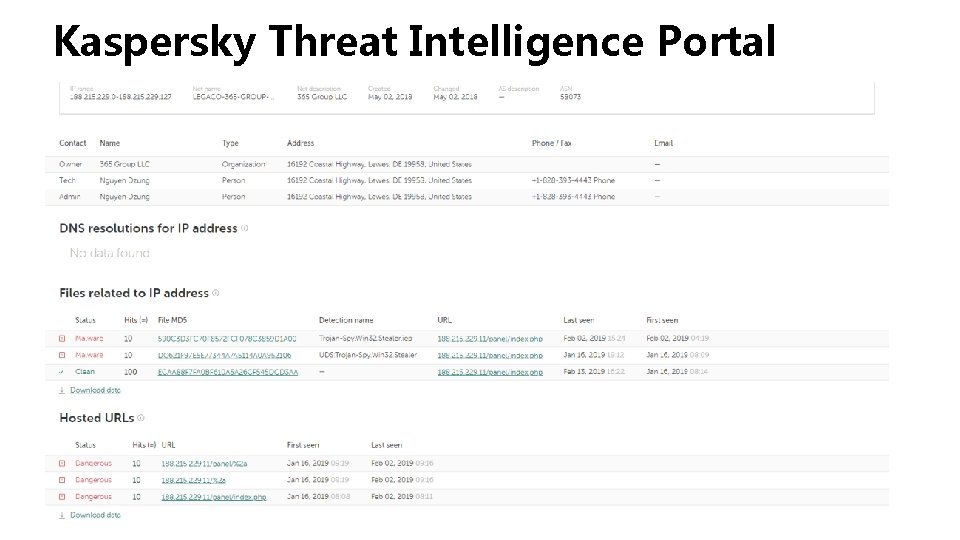
Kaspersky Threat Data Feeds & Cyber. Trace Internet DMZ Network Miss configuration or exclusions Kaspersky Cyber. Trace Domains Botnet C&C URLs Vulnerabilitie s IP Hashes addresses Phising Internal Network 188. 215. 229. 11 SIEM
? 188. 215. 229. 11
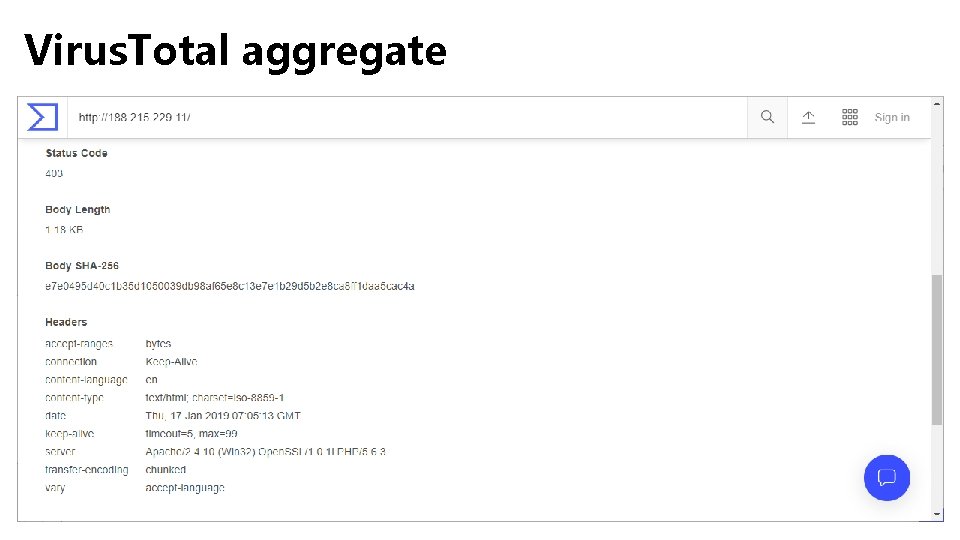
Virus. Total aggregate
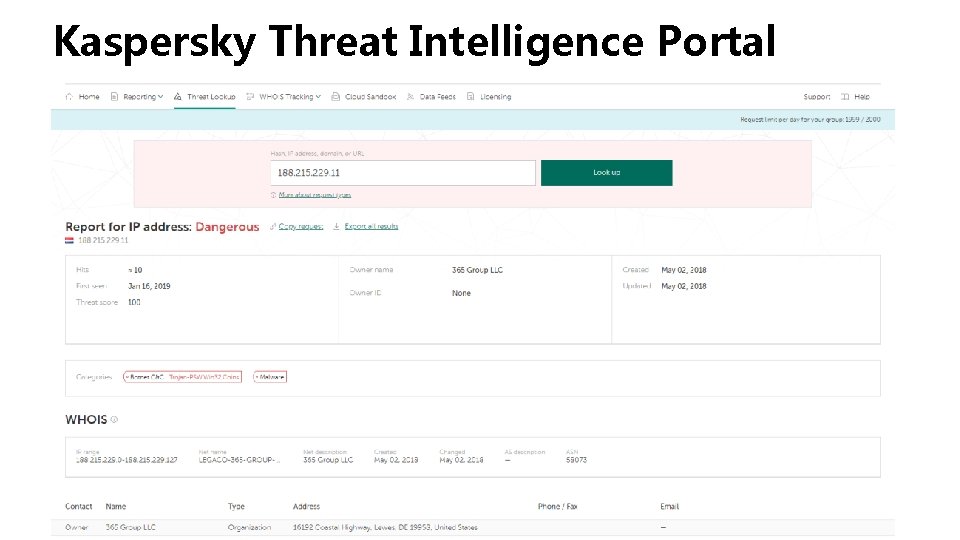
Kaspersky Threat Intelligence Portal
Kaspersky Threat Intelligence Portal
Kaspersky Threat Intelligence Portal
Kaspersky Threat Intelligence Portal
Kaspersky Threat Intelligence Portal
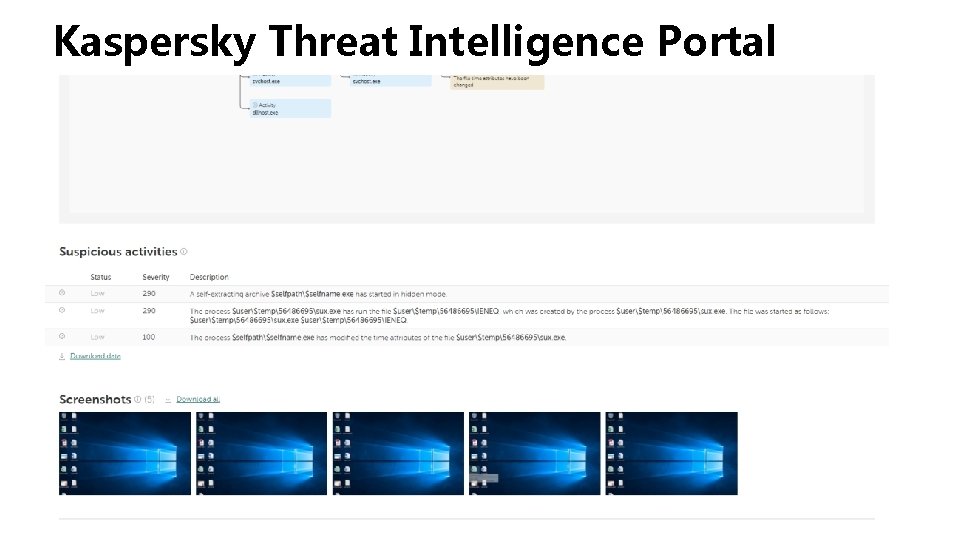
Kaspersky Threat Intelligence Portal
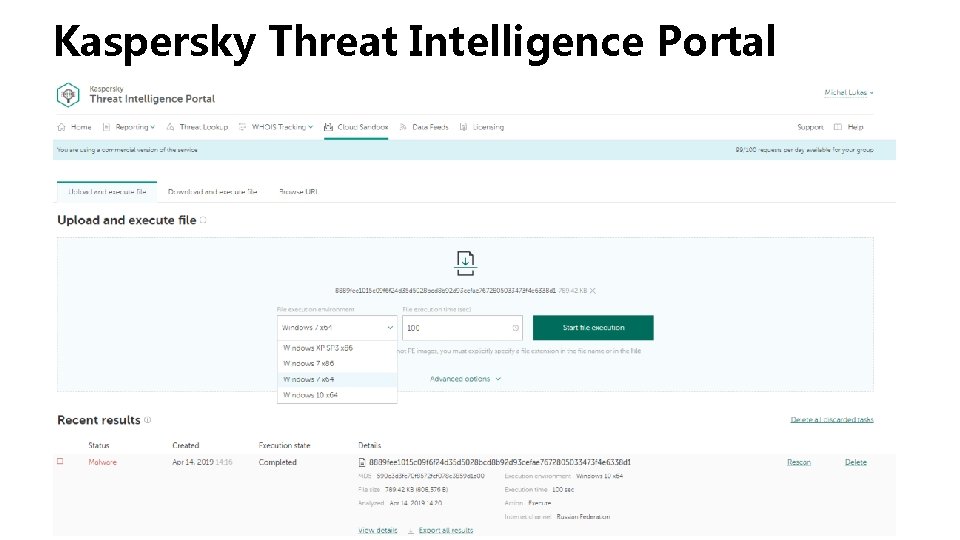
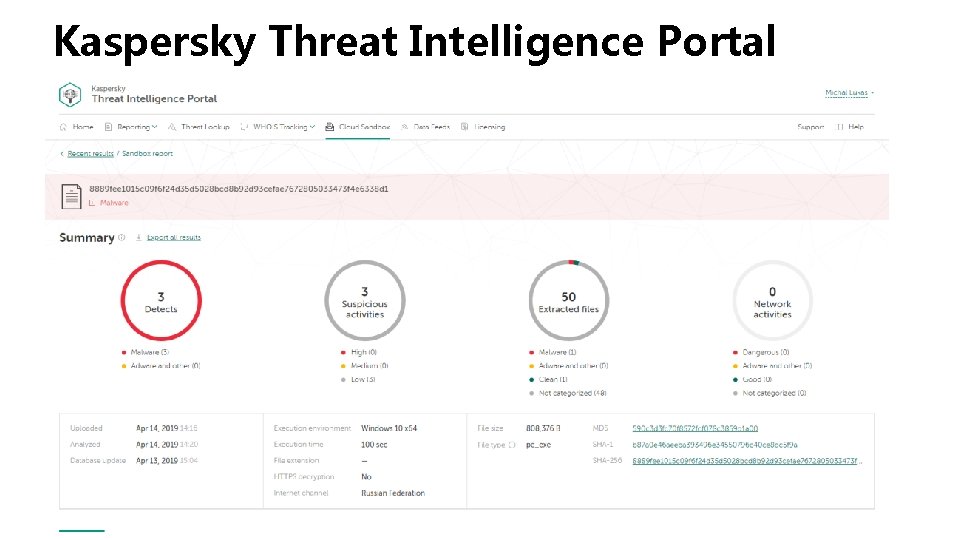
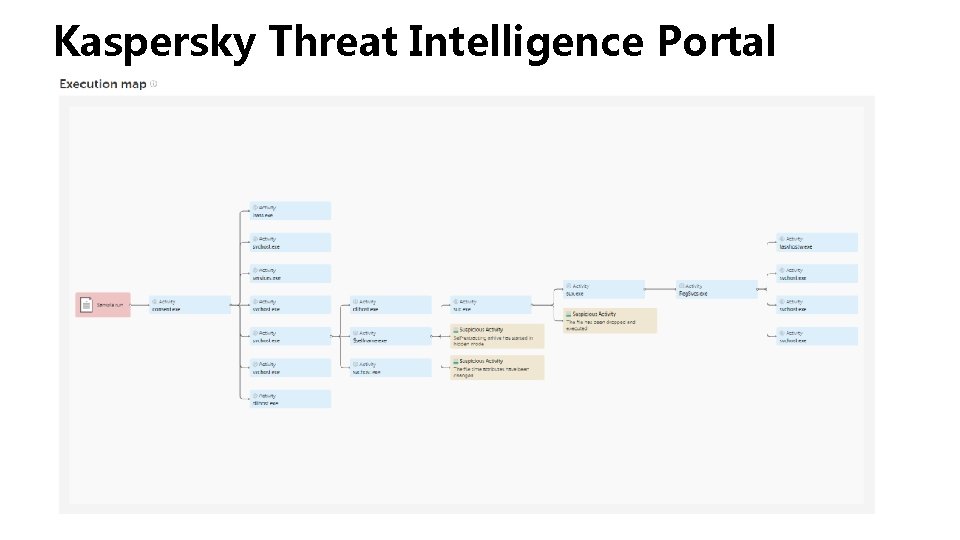
Summary > Detected infected machine in corporate network only from log sources > Analyzing of infected detection communication with Botnet C&C, hashes and URLs > Incident Respond scan all of the machines, all infected host isolate from the corporate network > Prevention block IP address and URLs on firewall, block files based on hashes by application control for servers and workstations
Prevent Detect Four key elements of the Security Operations Center > Detected infected machine in corporate network only from log sources > Analyzing of infected detection communication with Botnet C&C, hashes and URLs > Incident Respond scan all of the machines, all infected host isolate from the corporate network Predict Respond > Prevention block IP address and URLs on firewall, block files based on hashes by application control for servers and workstations
Thank you! Vladimír Váňa, Territory Channel Manager, Kaspersky