
ISO 27001 Information Security Staff Awareness All Rights
- Slides: 39
ISO 27001 Information Security – Staff Awareness All Rights Reserved a Teleste Company
Agenda § What is information? § What is information security? § What is risk? § Introduction to the ISO standards § Managing information security § Your security responsibilities Passion Expertise Innovation
Information is an asset which, like other important business assets, has value to an organisation and consequently needs to be suitably protected Passion Expertise Innovation
Information Types Information exists in many forms: § Printed or written on paper § Stored electronically § Transmitted by post or electronic means § Visual e. g. videos, diagrams § Published on the Web § Verbal/aural e. g. conversations, phone calls § Intangible e. g. knowledge, experience, expertise, ideas ‘Whatever form the information takes, or means by which it is shared or stored, it should always be appropriately protected’ Passion Expertise Innovation
Information Lifecycle Information can be … § Created § Owned (it is an asset) § Stored § Processed § Transmitted/communicated § Used (for proper or improper purposes) § Modified or corrupted § Shared or disclosed (whether appropriately or not) § Destroyed or lost § Stolen § Controlled, secured and protected throughout its existence Passion Expertise Innovation
Key Term What is information security? § Information security is what keeps valuable information ‘free of danger’ (protected, safe from harm) § It is not something you buy, it is something you do o It’s a process not a product § It is achieved using a combination of suitable strategies and approaches: o Determining the risks to information and treating them accordingly (proactive risk management) o Protecting CIA (Confidentiality, Integrity and Availability) o Avoiding, preventing, detecting and recovering from incidents o Securing people, processes and technology … not just IT! Passion Expertise Innovation
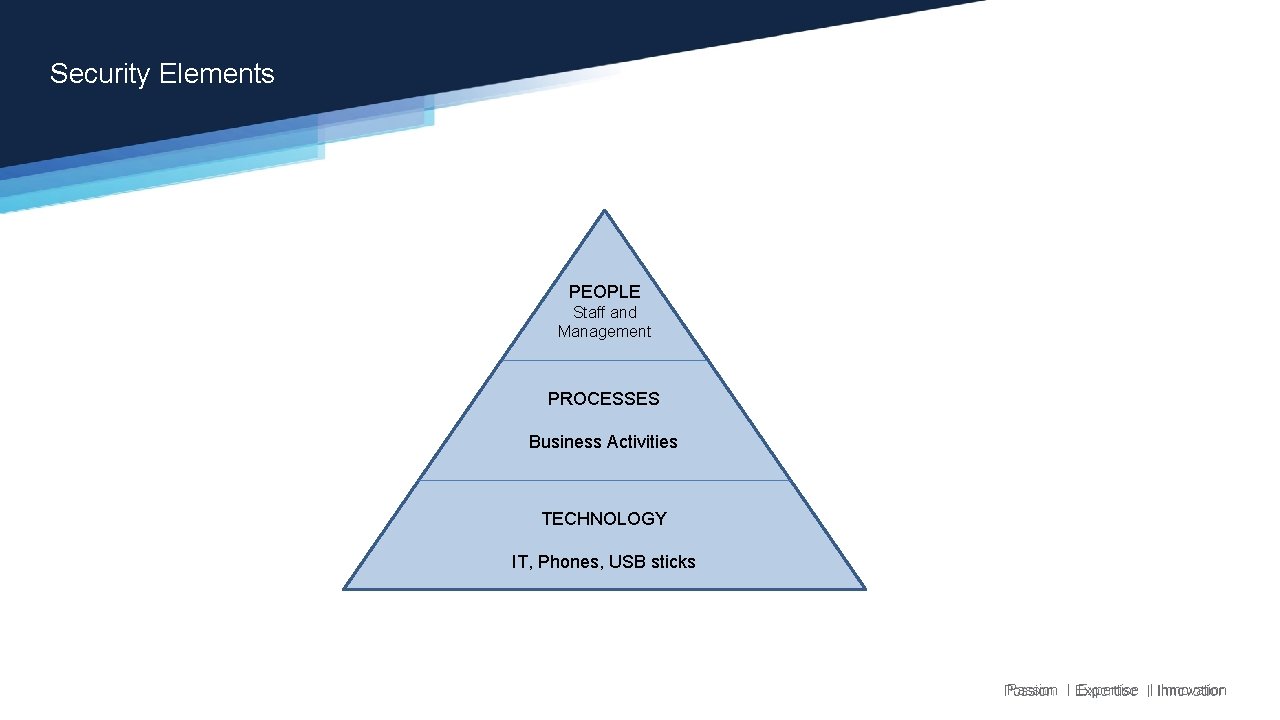
Security Elements PEOPLE Staff and Management PROCESSES Business Activities TECHNOLOGY IT, Phones, USB sticks Passion Expertise Innovation
People who use or have an interest in our information security include: Shareholders / owners Management & staff Customers / clients, suppliers & business partners Service providers, contractors, consultants & advisors Authorities, regulators & judges Our biggest threats arise from people (social engineers, unethical competitors, hackers, fraudsters, careless workers, bugs, flaws …), yet our biggest asset is our people (e. g. security-aware employees who spot trouble early) Passion Expertise Innovation
Processes are work practices or workflows, the steps or activities needed to accomplish business objectives. • Processes are described in procedures. • Virtually all business processes involve and/or depend on information making information a critical business asset. Information security policies and procedures define how we secure information appropriately and repeatedly. Passion Expertise Innovation
Technology Information technologies Cabling, data/voice networks and equipment Telecommunications services (PABX, Vo. IP, ISDN, videoconferencing) Phones, cellphones, PDAs Computer servers, desktops and associated data storage devices (disks, tapes) Operating system and application software Paperwork, files Pens, ink Security technologies Locks, barriers, card-access systems, CCTV Passion Expertise Innovation
Value Information security is valuable because it … • Protects information against various threats • Ensures business continuity • Minimizes financial losses and other impacts • Optimizes return on investments • Creates opportunities to do business safely • Maintains privacy and compliance We all depend on information security Passion Expertise Innovation
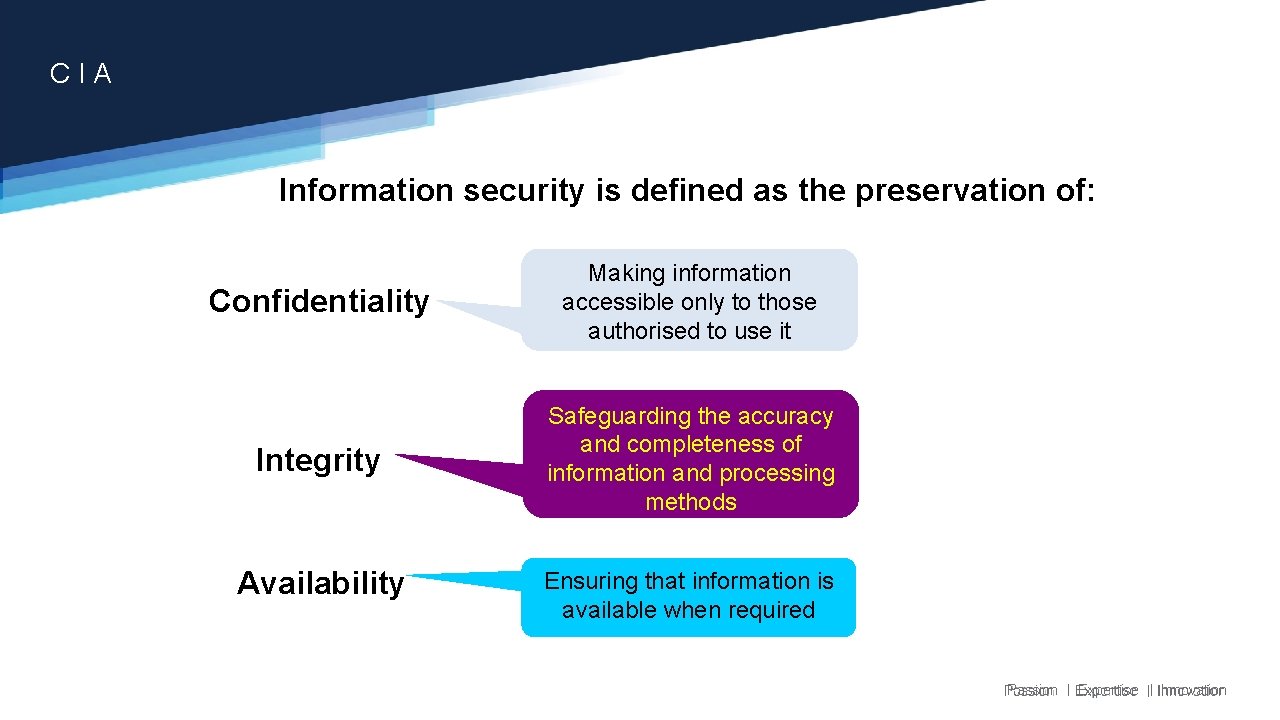
C I A Information security is defined as the preservation of: Confidentiality Making information accessible only to those authorised to use it Integrity Safeguarding the accuracy and completeness of information and processing methods Availability Ensuring that information is available when required Passion Expertise Innovation
Impacts Security Incidents Cause…. • IT downtime, business interruption • Financial losses and costs • Devaluation of intellectual property • Breaking laws and regulations, leading to prosecutions, fines and penalties • Reputation and brand damage leading to loss of customer, market, business partner or owners’ confidence and lost business • Fear, uncertainty and doubt Passion Expertise Innovation
Key Term What is Risk? Risk is the possibility that a threat exploits a vulnerability in an information asset, leading to an adverse impact on the organisation Threat: something that might cause harm Vulnerability: a weakness that might be exploited Impact: financial damage etc. Passion Expertise Innovation
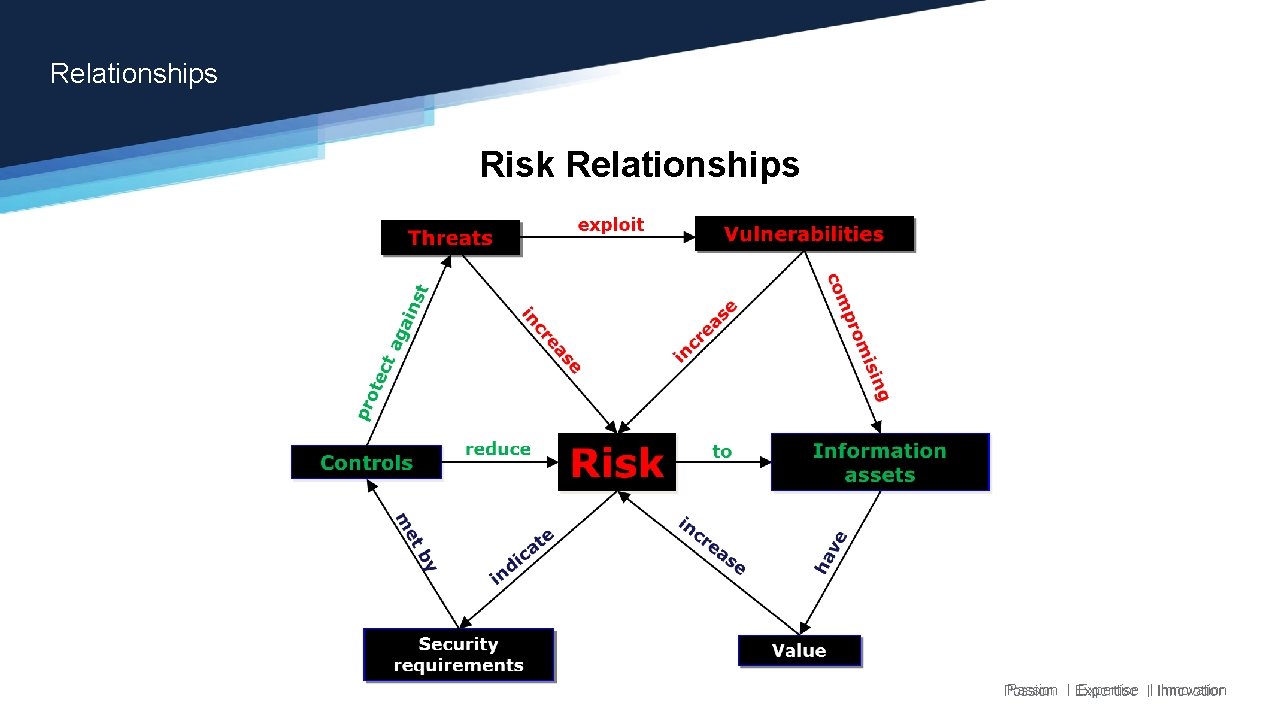
Relationships Risk Relationships Passion Expertise Innovation
Threat Agent The ‘actor’ that represents, carries out or catalyses the threat • Human • Machine • Nature Passion Expertise Innovation
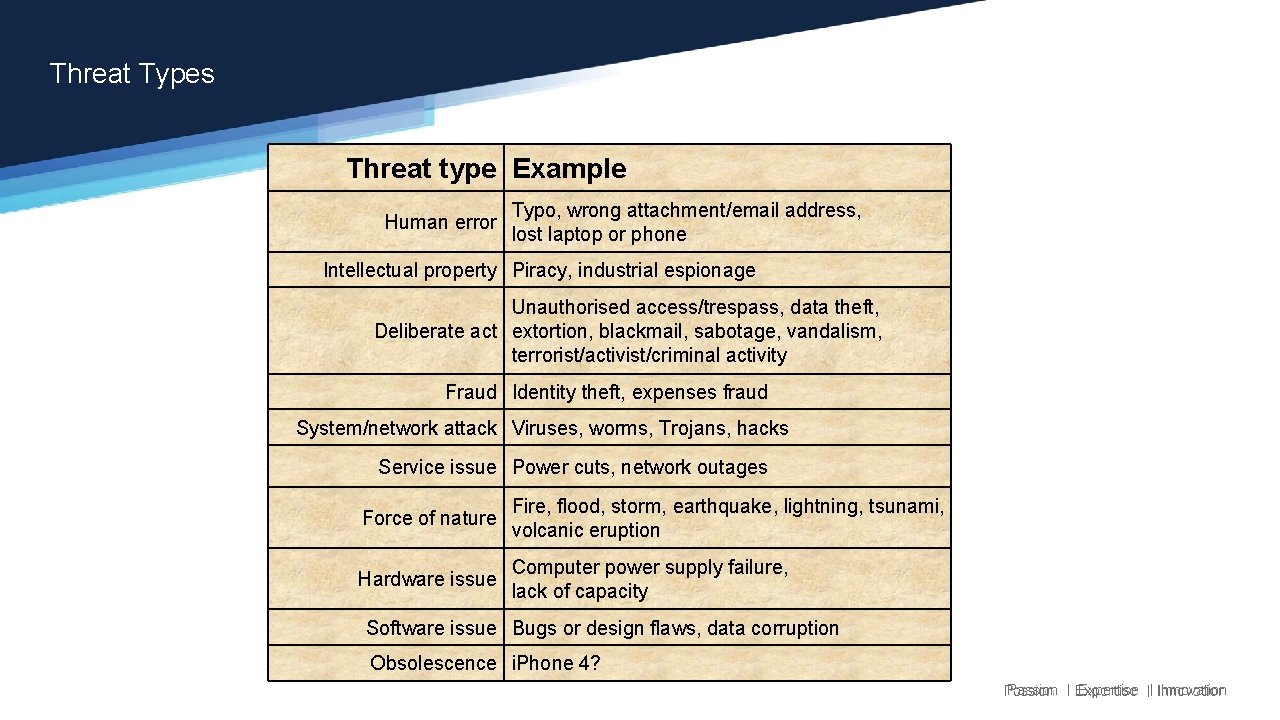
Threat Types Threat type Example Human error Typo, wrong attachment/email address, lost laptop or phone Intellectual property Piracy, industrial espionage Unauthorised access/trespass, data theft, Deliberate act extortion, blackmail, sabotage, vandalism, terrorist/activist/criminal activity Fraud Identity theft, expenses fraud System/network attack Viruses, worms, Trojans, hacks Service issue Power cuts, network outages Force of nature Fire, flood, storm, earthquake, lightning, tsunami, volcanic eruption Hardware issue Computer power supply failure, lack of capacity Software issue Bugs or design flaws, data corruption Obsolescence i. Phone 4? Passion Expertise Innovation
So how do we secure our information assets? Passion Expertise Innovation
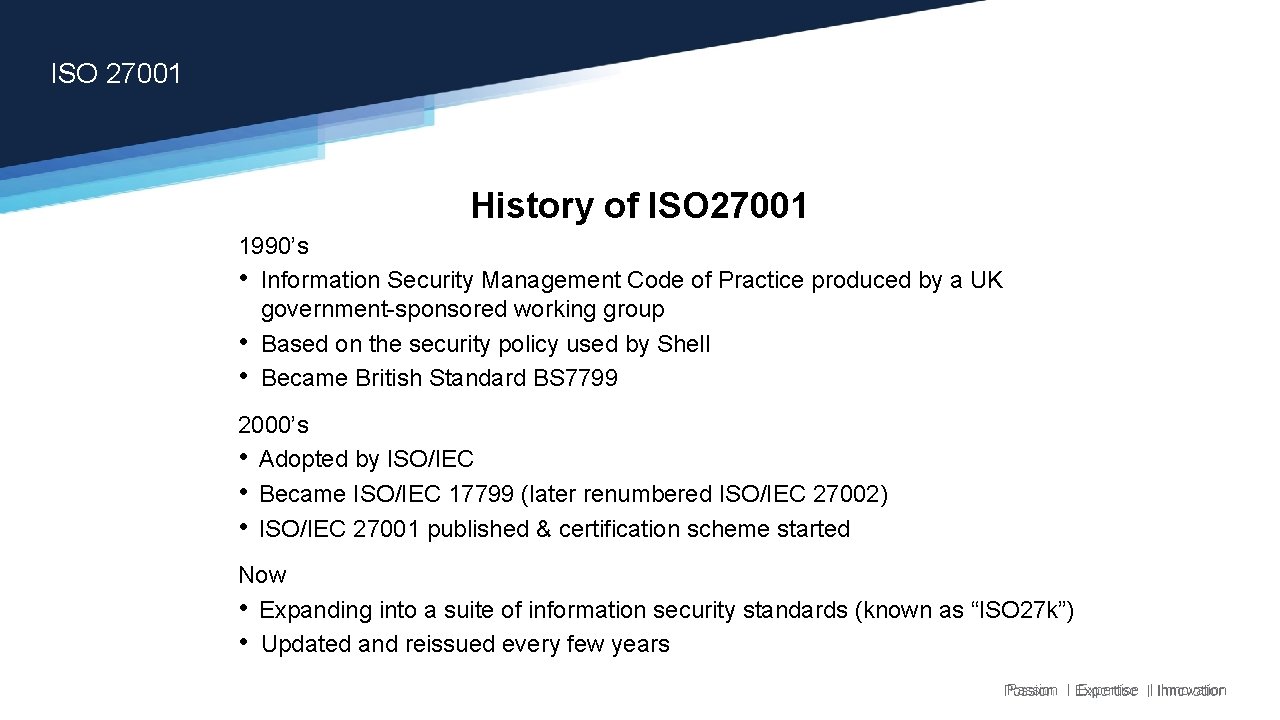
ISO 27001 History of ISO 27001 1990’s • Information Security Management Code of Practice produced by a UK government-sponsored working group • Based on the security policy used by Shell • Became British Standard BS 7799 2000’s • Adopted by ISO/IEC • Became ISO/IEC 17799 (later renumbered ISO/IEC 27002) • ISO/IEC 27001 published & certification scheme started Now • Expanding into a suite of information security standards (known as “ISO 27 k”) • Updated and reissued every few years Passion Expertise Innovation
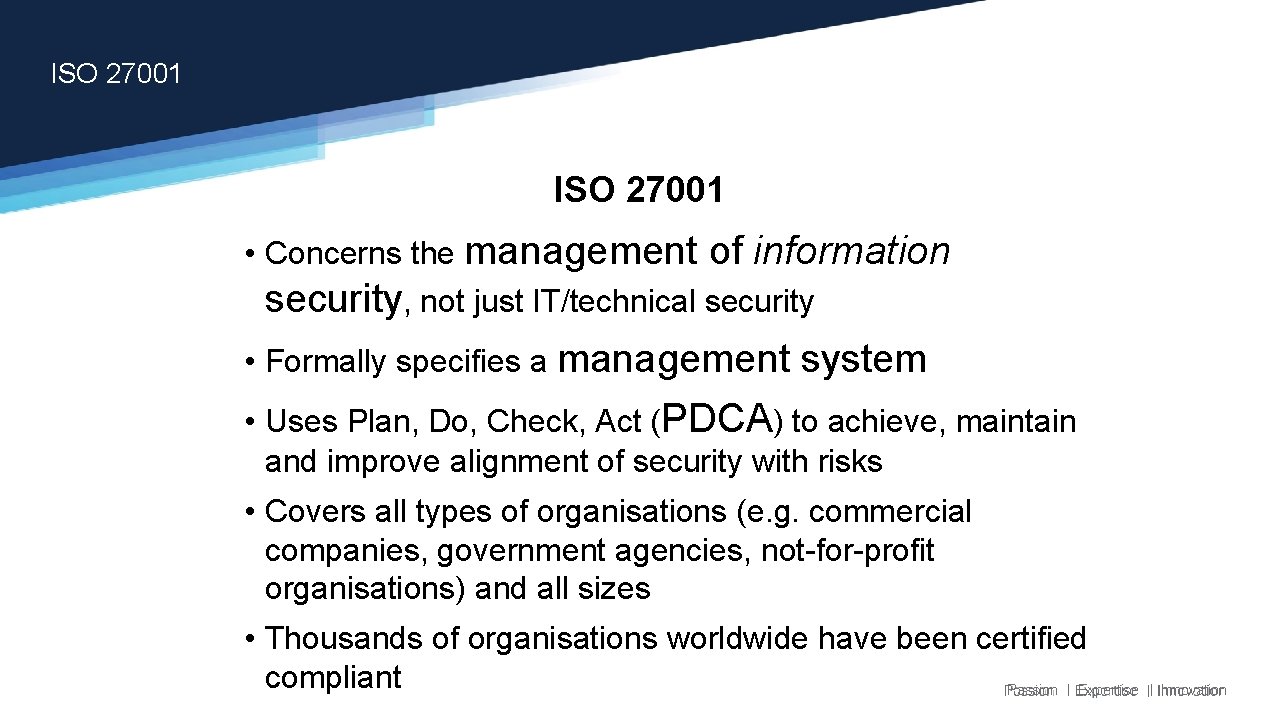
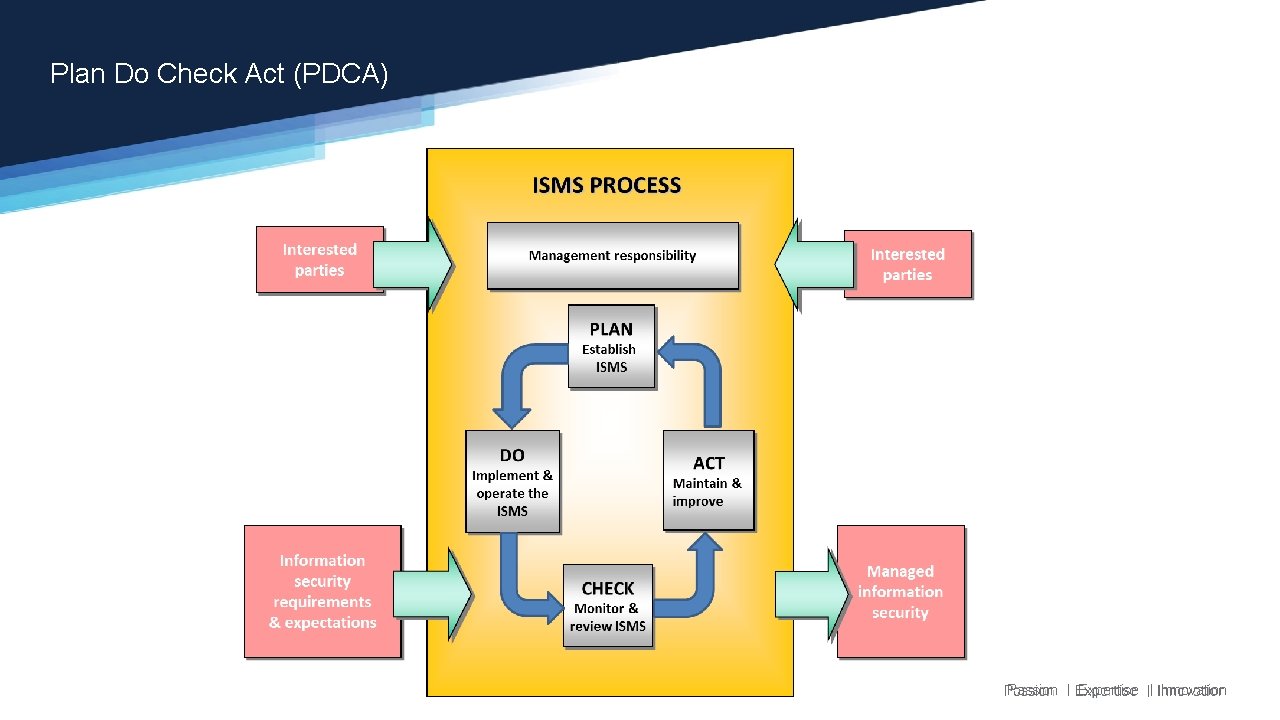
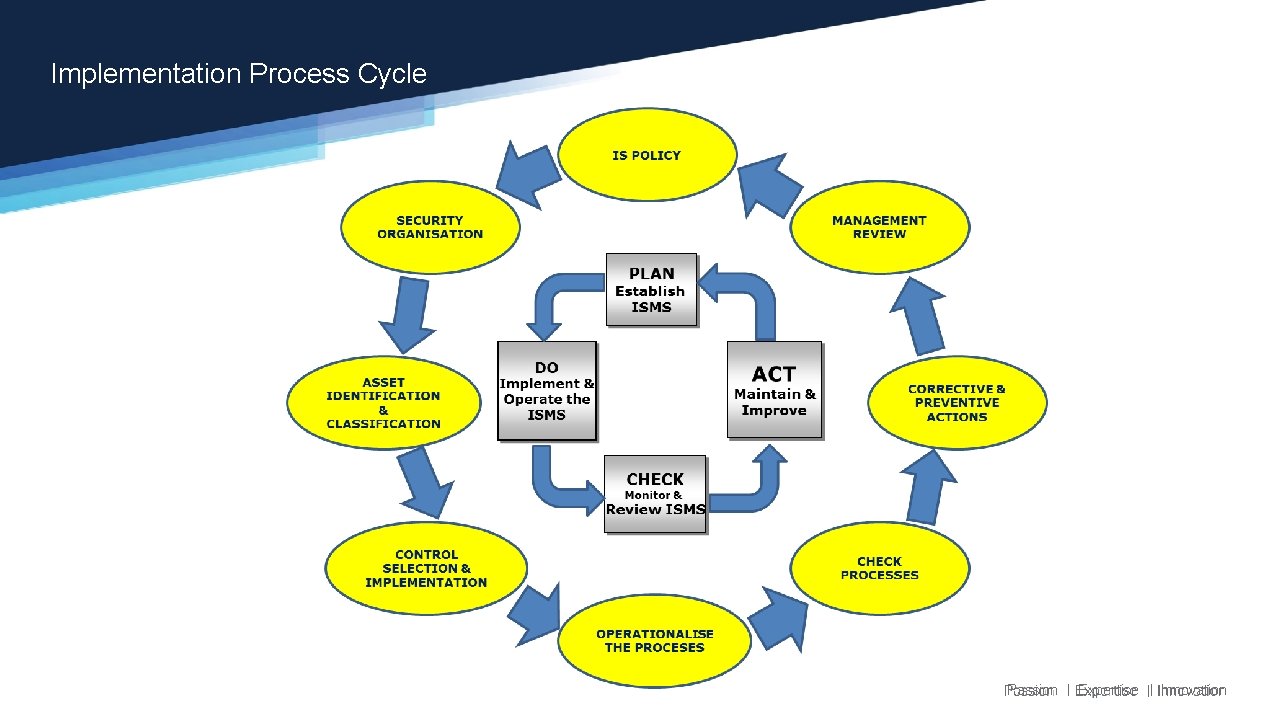
ISO 27001 • Concerns the management of information security, not just IT/technical security • Formally specifies a management system • Uses Plan, Do, Check, Act (PDCA) to achieve, maintain and improve alignment of security with risks • Covers all types of organisations (e. g. commercial companies, government agencies, not-for-profit organisations) and all sizes • Thousands of organisations worldwide have been certified compliant Passion Expertise Innovation
Plan Do Check Act (PDCA) Passion Expertise Innovation
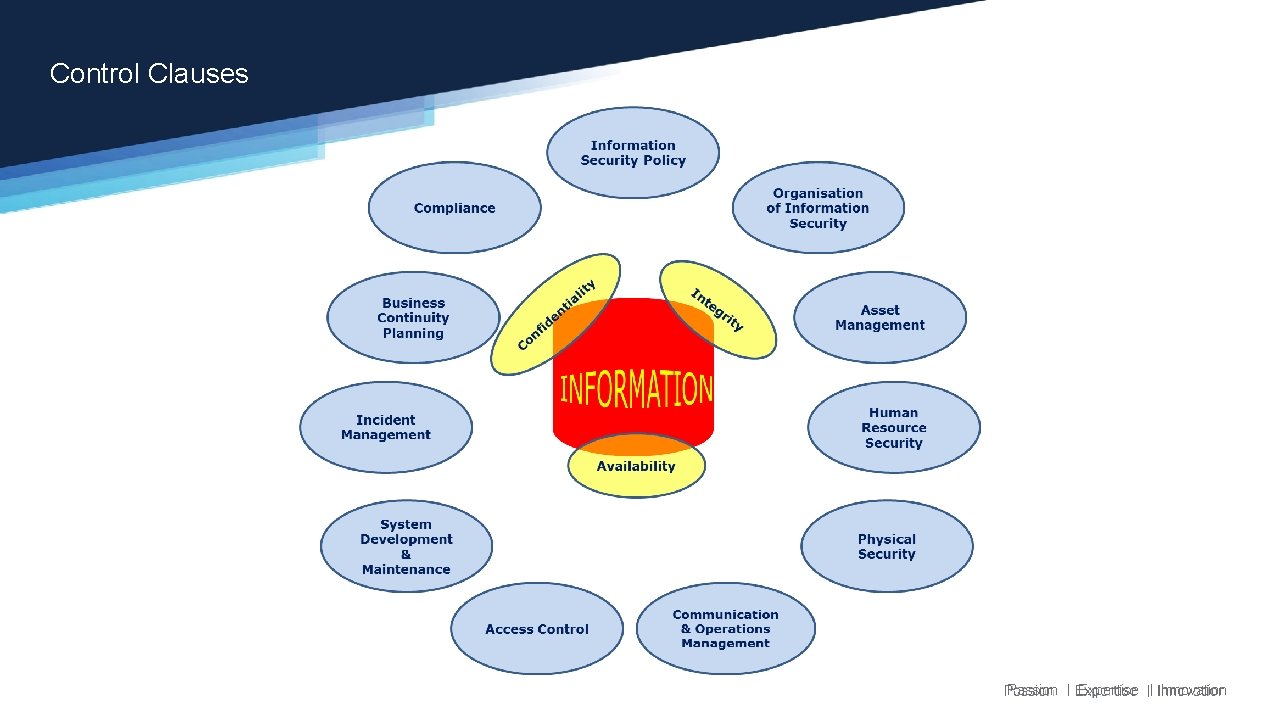
Control Clauses Passion Expertise Innovation
Control Clauses • Information security policy - management direction • Organisation of information security - management framework for implementation • Asset management – assessment, classification and protection of valuable information assets • HR security – security for joiners, movers and leavers • Physical & environmental security - prevents unauthorised access, theft, compromise, damage to information and computing facilities, power cuts Passion Expertise Innovation
Control Clauses • Communications & operations management - ensures the correct and secure operation of IT • Access control – restrict unauthorised access to information assets • Information systems acquisition, development & maintenance – build security into systems • Information security incident management – deal sensibly with security incidents that arise • Business continuity management – maintain essential business processes and restore any that fail • Compliance - avoid breaching laws, regulations, policies and other security obligations Passion Expertise Innovation
Implementation Process Cycle Passion Expertise Innovation
Benefits • • • Demonstrable commitment to security by the organisation Legal and regulatory compliance Better risk management Commercial credibility, confidence, and assurance Reduced costs Clear employee direction and improved awareness Passion Expertise Innovation
Scope Flomatik office areas at the following 2 locations: • Unit 3, Kingsbury Business Park, Kingsbury Road, Minworth, Birmingham, West Midlands, B 76 9 DL • 1, Gloster Court, Whittle Avenue, Segensworth West, Fareham, PO 15 5 SH Providing the following services to all Flomatik users and clients: • Sales • Resource Management • Service Development & Programme Delivery • Product Planning & Design • Manufacture, Materials Procurement & Logistics • Field Engineering • Business Operations All information assets throughout the organisation Passion Expertise Innovation
Key Documents • High level corporate security policy • Supporting policies e. g. physical & environmental, email, HR, incident management, compliance etc. • Standards e. g. Windows Security Standard • Procedures and guidelines • Records e. g. security logs, security review reports, corrective actions Passion Expertise Innovation
Security Vision/Mission Vision The organisation is acknowledged as forward thinking in the implementation and maintenance of information security Mission To design, implement, operate, manage and maintain an Information Security Management System that complies with international standards, incorporating generallyaccepted good security practices Passion Expertise Innovation
Motive Responsiblities • Information Security Management Committee • Information Security Manager/CISO and Department • Incident Response Team • Business Continuity Team • IT, Legal/Compliance, HR, Risk and other departments • Audit Committee • Last but not least, you! Information security is everyone’s responsibility Passion Expertise Innovation
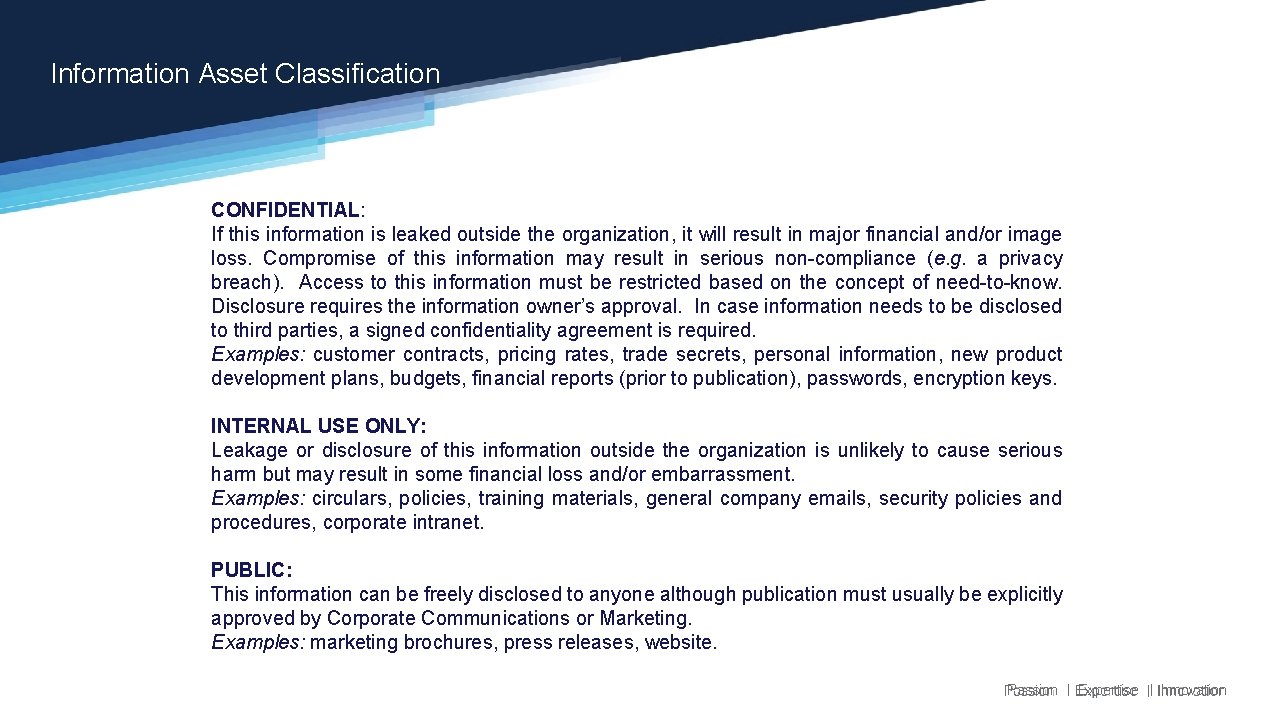
Information Asset Classification CONFIDENTIAL: If this information is leaked outside the organization, it will result in major financial and/or image loss. Compromise of this information may result in serious non-compliance (e. g. a privacy breach). Access to this information must be restricted based on the concept of need-to-know. Disclosure requires the information owner’s approval. In case information needs to be disclosed to third parties, a signed confidentiality agreement is required. Examples: customer contracts, pricing rates, trade secrets, personal information, new product development plans, budgets, financial reports (prior to publication), passwords, encryption keys. INTERNAL USE ONLY: Leakage or disclosure of this information outside the organization is unlikely to cause serious harm but may result in some financial loss and/or embarrassment. Examples: circulars, policies, training materials, general company emails, security policies and procedures, corporate intranet. PUBLIC: This information can be freely disclosed to anyone although publication must usually be explicitly approved by Corporate Communications or Marketing. Examples: marketing brochures, press releases, website. Passion Expertise Innovation
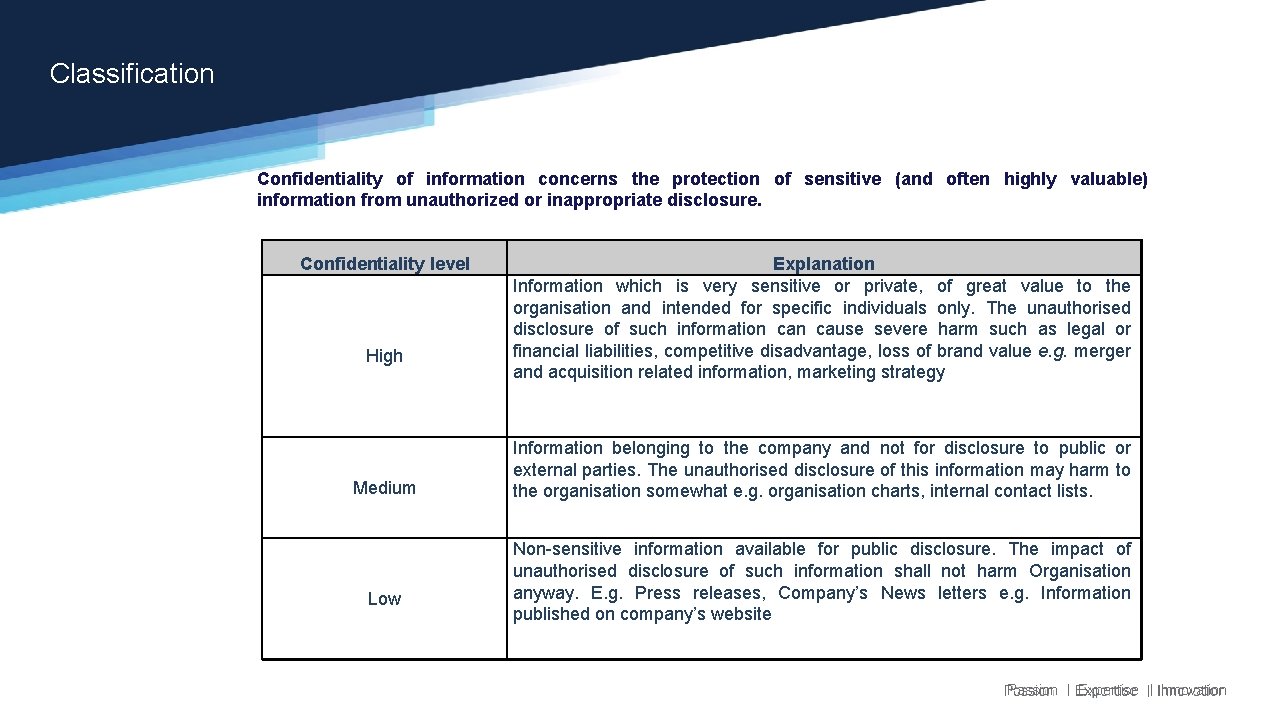
Classification Confidentiality of information concerns the protection of sensitive (and often highly valuable) information from unauthorized or inappropriate disclosure. Confidentiality level High Medium Low Explanation Information which is very sensitive or private, of great value to the organisation and intended for specific individuals only. The unauthorised disclosure of such information cause severe harm such as legal or financial liabilities, competitive disadvantage, loss of brand value e. g. merger and acquisition related information, marketing strategy Information belonging to the company and not for disclosure to public or external parties. The unauthorised disclosure of this information may harm to the organisation somewhat e. g. organisation charts, internal contact lists. Non-sensitive information available for public disclosure. The impact of unauthorised disclosure of such information shall not harm Organisation anyway. E. g. Press releases, Company’s News letters e. g. Information published on company’s website Passion Expertise Innovation
User Responsibilities Physical Security Do • • Read and follow security policies and procedures Display identity cards while on the premises Challenge or report anyone without an ID card Visit the intranet Security Zone or call IT Help/Service Desk for advice on most information security matters Do Not • Allow unauthorised visitors onto the premises • Bring weapons, hazardous/combustible materials, recording devices etc. , especially in secure areas • Use personal IT devices for work purposes, unless explicitly authorised by management Passion Expertise Innovation
User Responsibilities Password Guidelines Ø Use long, complicated passwords - whole sentences if you can Ø Reserve your strongest passwords for high security systems (don’t re-use the same passphrase everywhere) Ø Use famous quotes, lines from your favorite songs, poems etc. to make them memorable Ø Use short or easily-guessed passwords Ø Write down passwords or store them in plain text Ø Share passwords over phone or email Passion Expertise Innovation
User Responsibilites Internet Usage Ø Use the corporate Internet facilities only for legitimate and authorized business purposes Ø Avoid websites that would be classed as obscene, racist, offensive or illegal – anything that would be embarrassing Ø Do not access online auction or shopping sites, except where authorised by your manager Ø Don’t hack! Ø Do not download or upload commercial software or other copyrighted material without the correct license and permission from your manager Warning: Internet usage is routinely logged and monitored. Be careful which websites you visit and what you disclose. Passion Expertise Innovation
User Responsibilities E-mail Usage Ø Use corporate email for business purposes only Ø Follow the email storage guidelines Ø If you receive spam email, simply delete it. If it is offensive or you receive a lot, call the IT Help/Service Desk Ø Do not use your corporate email address for personal email Ø Do not circulate chain letters, hoaxes, inappropriate jokes, videos etc. Ø Do not send emails outside the organization unless you are authorized to do so Ø Be very wary of email attachments and links, especially in unsolicited emails (most are virus-infected) Passion Expertise Innovation
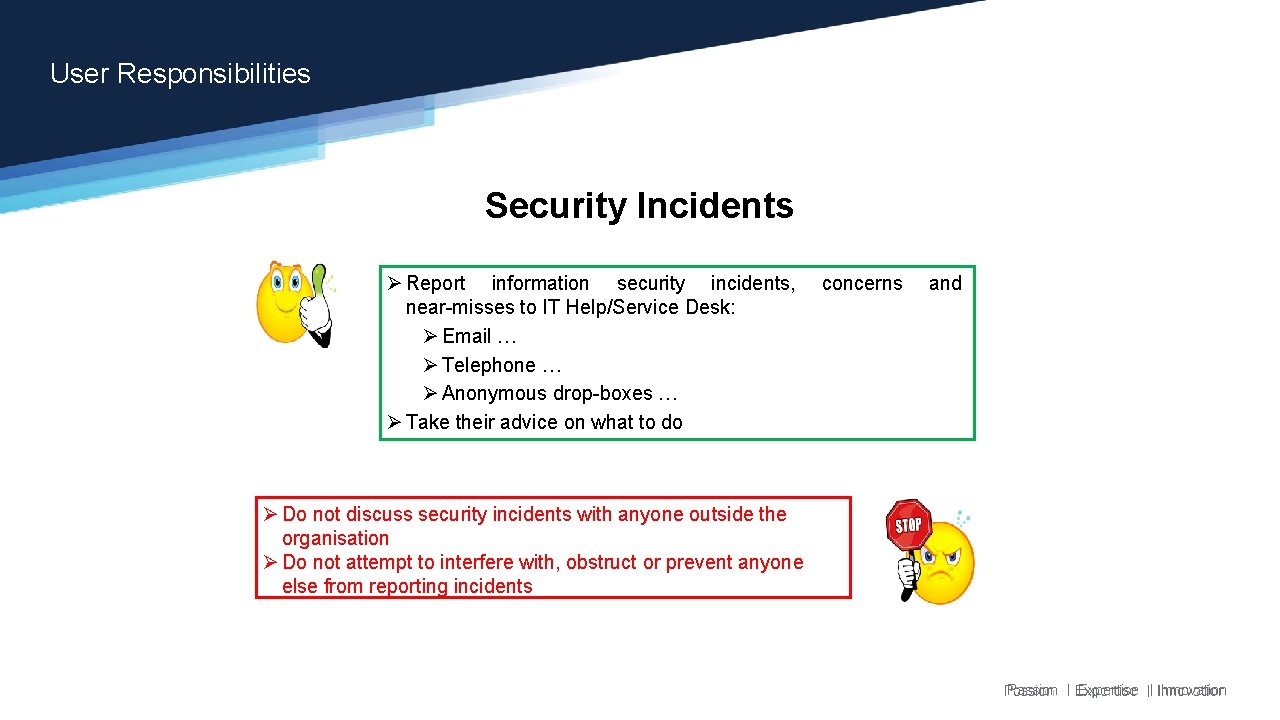
User Responsibilities Security Incidents Ø Report information security incidents, concerns and near-misses to IT Help/Service Desk: Ø Email … Ø Telephone … Ø Anonymous drop-boxes … Ø Take their advice on what to do Ø Do not discuss security incidents with anyone outside the organisation Ø Do not attempt to interfere with, obstruct or prevent anyone else from reporting incidents Passion Expertise Innovation
User Responsibilities ü Ensure your PC is getting antivirus updates and patches ü Lock your keyboard (Windows L) before leaving your PC unattended, and log-off at the end of the day ü Store laptops and valuable information (paperwork as well as CDs, USB sticks etc. ) securely under lock and key ü Keep your wits about you while traveling: § Keep your voice down on the cellphone § Be discreet about your IT equipment ü Take regular information back ups ü Fulfill your security obligations: § Comply with security and privacy laws, copyright and licenses, NDA (Non Disclosure Agreements) and contracts § Comply with corporate policies and procedures ü Stay up to date on information security: § Review the Information Security policies in the staff section of the Flomatik website Passion Expertise Innovation
Questions Passion Expertise Innovation