
IP Spoofing Sometimes on the internet a girl
- Slides: 32
IP Spoofing Sometimes on the internet, a girl named Alice is really a man named Yves
Sources o General Information: n n n o Mitnick Attack Sequence: n o http: //tarpit. rmc. ca/knight/EEE 466 Lectures/DA 14/14%20%20 Security%20 I. ppt Do. S and DDo. S attacks: n n o http: //www. gulker. com/ra/hack/tsattack. html Session Hijack Sequence: n o http: //en. wikipedia. org/wiki/Ip_spoofing http: //www. securityfocus. com/infocus/1674 http: //tarpit. rmc. ca/knight/EE 579 index. htm (See ppts on subject) http: //tarpit. rmc. ca/knight/EEE 466 Lectures/DA 14/14%20%20 Security%20 I. ppt Conversation with Todd ‘Hot Toddy’ Jackson Phrack Article: n http: //www. phrack. org/issues. html? issue=64&id=15#article
Overview o o TCP/IP – in brief IP Spoofing n n o o o Basic overview Examples o Mitnick Attack o Session Hijack o Do. S/DDo. S Attack Defending Against the Threat Continuous Evolution Conclusion
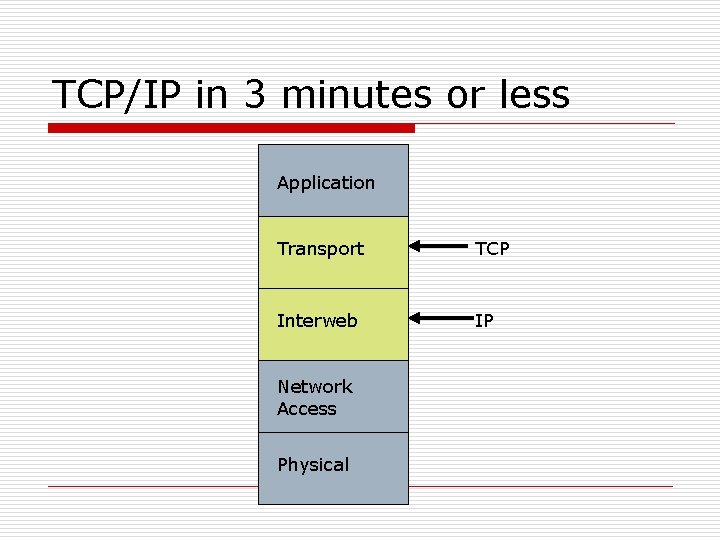
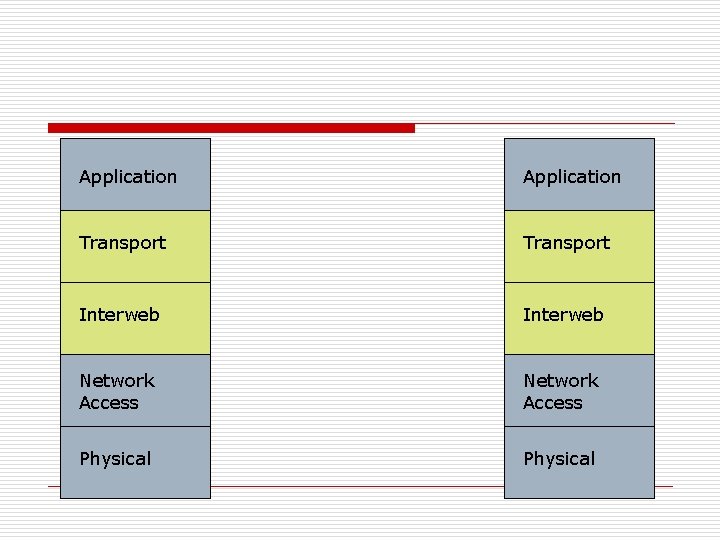
TCP/IP in 3 minute or less o o General use of term describes the Architecture upon which the Interweb is built. TCP/IP are specific protocols within that architecture.
TCP/IP in 3 minutes or less Application Transport TCP Interweb IP Network Access Physical
TCP/IP in 3 minute or less o o IP is the internet layer protocol. Does not guarantee delivery or ordering, only does its best to move packets from a source address to a destination address. IP addresses are used to express the source and destination. IP assumes that each address is unique within the network.
TCP/IP in 3 minutes or less o o TCP is the transport layer protocol. It guarantees delivery and ordering, but relies upon IP to move packets to proper destination. Port numbers are used to express source and destination. Destination Port is assumed to be awaiting packets of data.
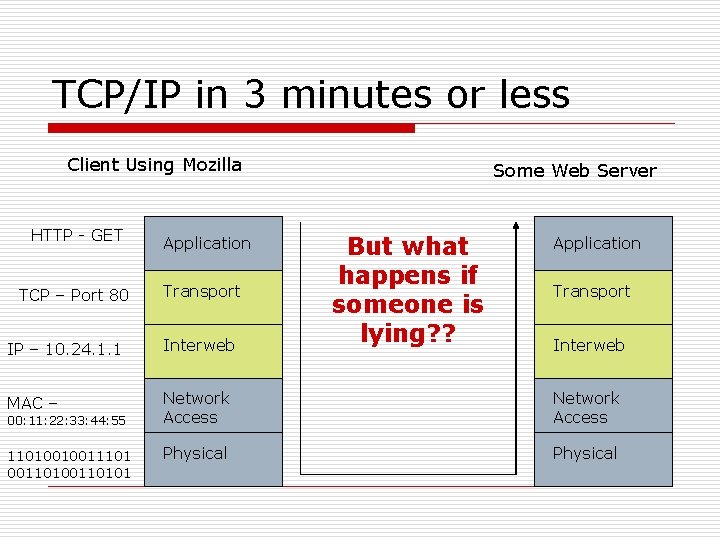
TCP/IP in 3 minutes or less Client Using Mozilla HTTP - GET TCP – Port 80 Application Transport Some Web Server But what happens if someone is lying? ? Application Transport IP – 10. 24. 1. 1 Interweb MAC – Network Access 11010010011101 00110101 Physical 00: 11: 22: 33: 44: 55 Interweb
IP Spoofing – Basic Overview o o o Basically, IP spoofing is lying about an IP address. Normally, the source address is incorrect. Lying about the source address lets an attacker assume a new identity.
IP Spoofing – Basic Overview o o o Because the source address is not the same as the attacker’s address, any replies generated by the destination will not be sent to the attacker. Attacker must have an alternate way to spy on traffic/predict responses. To maintain a connection, Attacker must adhere to protocol requirements
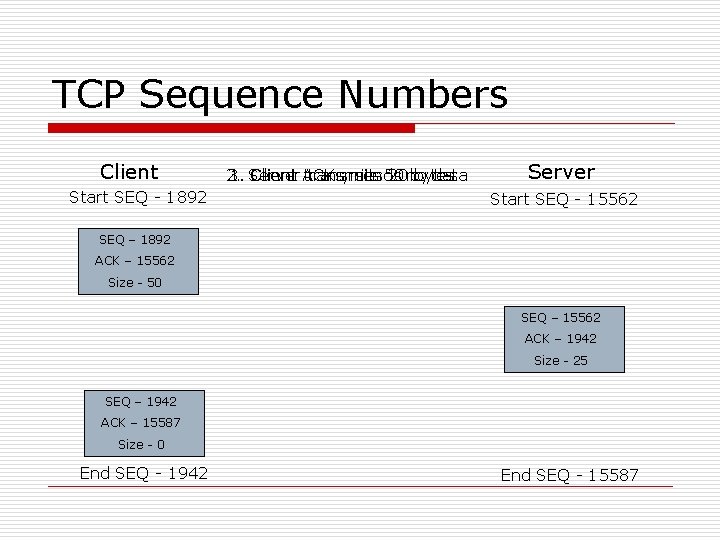
IP Spoofing – Basic Overview o Difficulties for attacker: n n n TCP sequence numbers One way communication Adherence to protocols for other layers
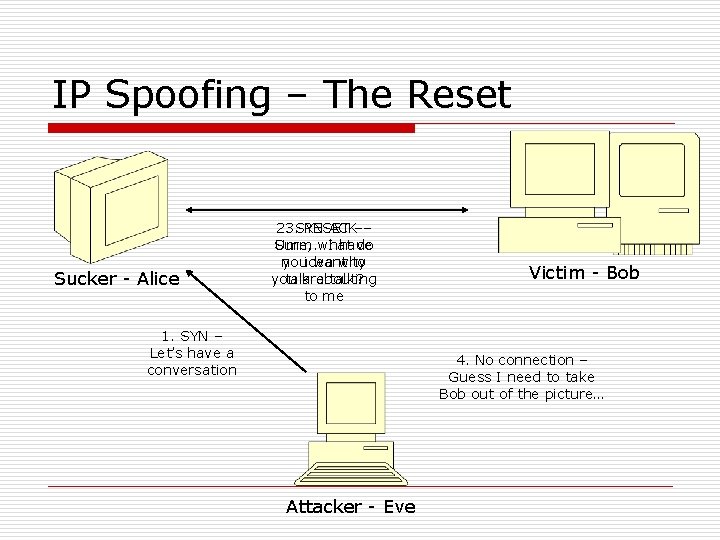
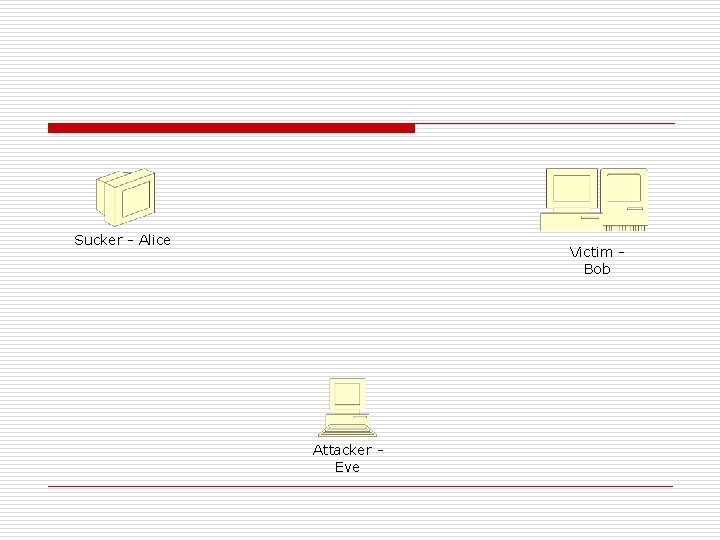
IP Spoofing – The Reset Sucker - Alice 2. 3. SYN RESET ACK–– Sure, Umm. . what I have do no youidea want why to you talk are about? talking to me 1. SYN – Let’s have a conversation Victim - Bob 4. No connection – Guess I need to take Bob out of the picture… Attacker - Eve
IP Spoofing – Mitnick Attack o o o Merry X-mas! Mitnick hacks a Diskless Workstation on December 25 th, 1994 The victim – Tsutomu Shinomura The attack – IP spoofing and abuse of trust relationships between a diskless terminal and login server.
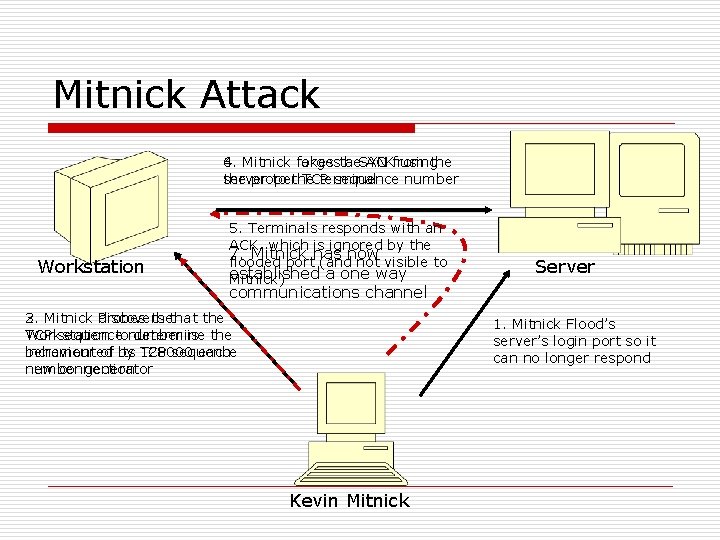
Mitnick Attack 6. Mitnick fakes 4. forgesthe a SYN ACKfrom using the server the proper to the TCP terminal sequence number Workstation 5. Terminals responds with an ACK, which is ignored by the 7. Mitnick has now flooded port (and not visible to established a one way Mitnick) Server communications channel 3. Mitnick discovers 2. Probes thethat the Workstation TCP sequence tonumber determine is the behaviour of by incremented its 128000 TCP sequence each number new connection generator 1. Mitnick Flood’s server’s login port so it can no longer respond Kevin Mitnick
Mitnick Attack – Why it worked o o Mitnick abused the trust relationship between the server and workstation He flooded the server to prevent communication between it and the workstation Used math skillz to determine the TCP sequence number algorithm (ie add 128000) This allowed Mitnick to open a connection without seeing the workstations outgoing sequence numbers and without the server interrupting his attack
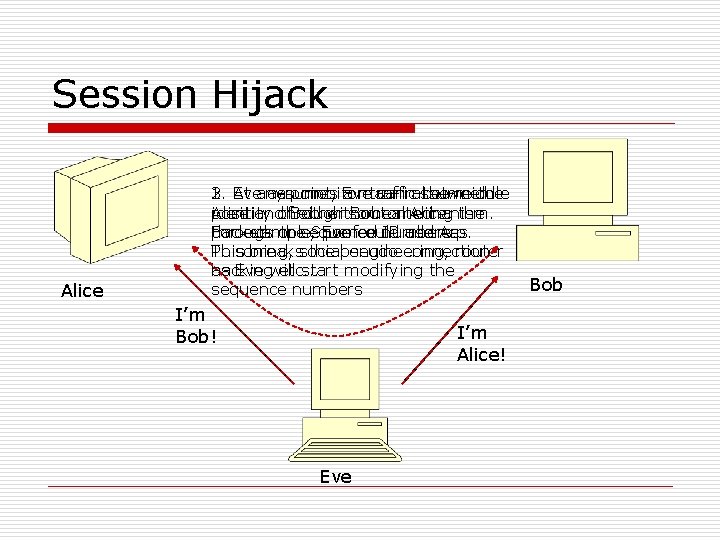
IP Spoofing - Session Hijack o o o IP spoofing used to eavesdrop/take control of a session. Attacker normally within a LAN/on the communication path between server and client. Not blind, since the attacker can see traffic from both server and client.
Session Hijack Alice 3. At 1. 2. Eveany assumes can point, monitor Eve a man-in-the-middle traffic can assume between the position Alice identity andof through Bob either without some Bob or altering mechanism. Alice the For example, packets through or thesequence Spoofed Eve could numbers. IP address. use Arp Poisoning, This breakssocial the pseudo engineering, connection router hacking as Eve will etc. . . start modifying the sequence numbers I’m Bob! I’m Alice! Eve Bob
IP Spoofing – Do. S/DDo. S o o Denial of Service (Do. S) and Distributed Denial of Service (DDo. S) are attacks aimed at preventing clients from accessing a service. IP Spoofing can be used to create Do. S attacks
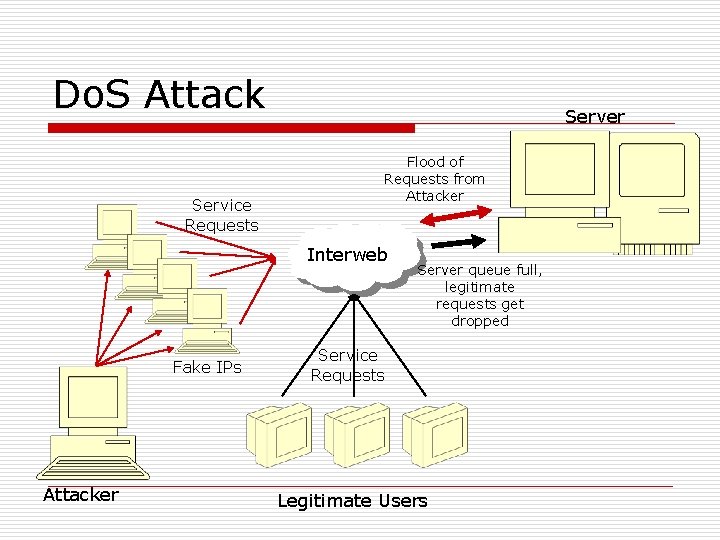
Do. S Attack Service Requests Server Flood of Requests from Attacker Interweb Fake IPs Attacker Server queue full, legitimate requests get dropped Service Requests Legitimate Users
Do. S Attack o o The attacker spoofs a large number of requests from various IP addresses to fill a Services queue. With the services queue filled, legitimate user’s cannot use the service.
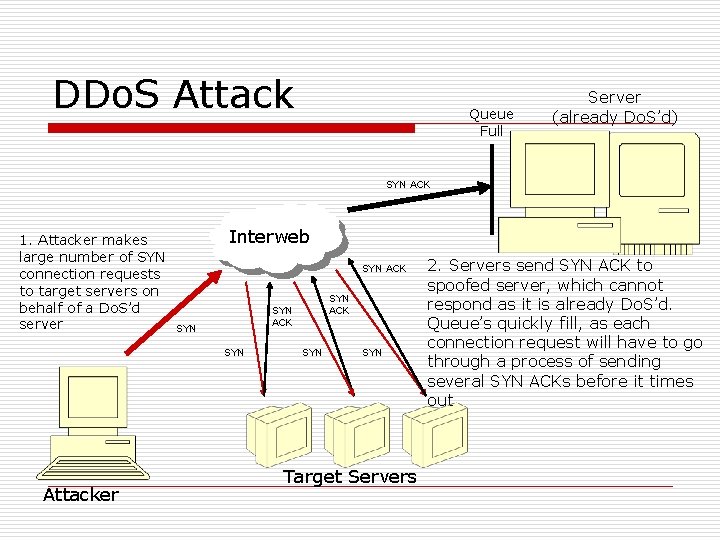
DDo. S Attack Queue Full Server (already Do. S’d) SYN ACK 1. Attacker makes large number of SYN connection requests to target servers on behalf of a Do. S’d server Interweb SYN ACK SYN Attacker SYN ACK SYN Target Servers 2. Servers send SYN ACK to spoofed server, which cannot respond as it is already Do. S’d. Queue’s quickly fill, as each connection request will have to go through a process of sending several SYN ACKs before it times out
DDo. S Attack o o Many other types of DDo. S are possible. Do. S becomes more dangerous if spread to multiple computers.
IP Spoofing – Defending o IP spoofing can be defended against in a number of ways: n As mentioned, other protocols in the Architectural model may reveal spoofing. o o o n n TCP sequence numbers are often used in this manner New generators for sequence numbers are a lot more complicated than ‘add 128000’ Makes it difficult to guess proper sequence numbers if the attacker is blind “Smart” routers can detect IP addresses that are outside its domain. “Smart” servers can block IP ranges that appear to be conducting a Do. S.
IP Spoofing continues to evolve o o o IP spoofing is still possible today, but has to evolve in the face of growing security. New issue of Phrack includes a method of using IP spoofing to perform remote scans and determine TCP sequence numbers This allows a session Hijack attack even if the Attacker is blind
Conclusion o o o IP Spoofing is an old school Hacker trick that continues to evolve. Can be used for a wide variety of purposes. Will continue to represent a threat as long as each layer continues to trust each other and people are willing to subvert that trust.
Questions?
Application Transport Interweb Network Access Physical
Sucker - Alice Victim Bob Attacker Eve
Sucker - Alice Interweb Victim Bob Attacker Eve
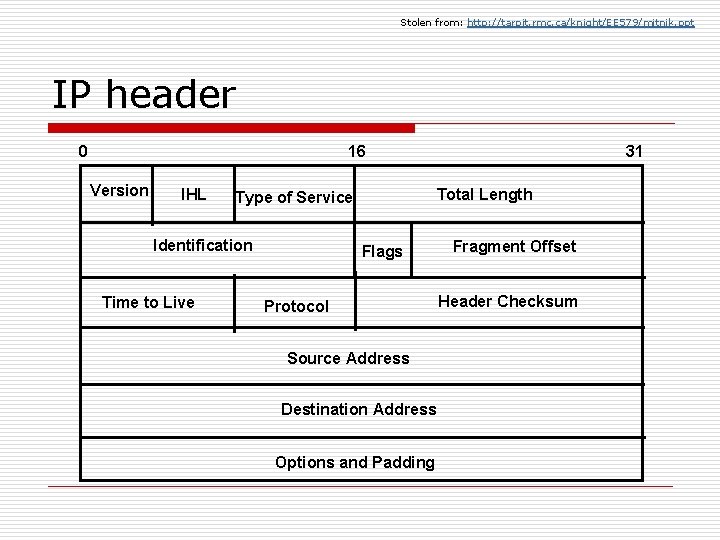
Stolen from: http: //tarpit. rmc. ca/knight/EE 579/mitnik. ppt IP header 0 16 Version IHL Time to Live Total Length Type of Service Identification 31 Flags Protocol Source Address Destination Address Options and Padding Fragment Offset Header Checksum
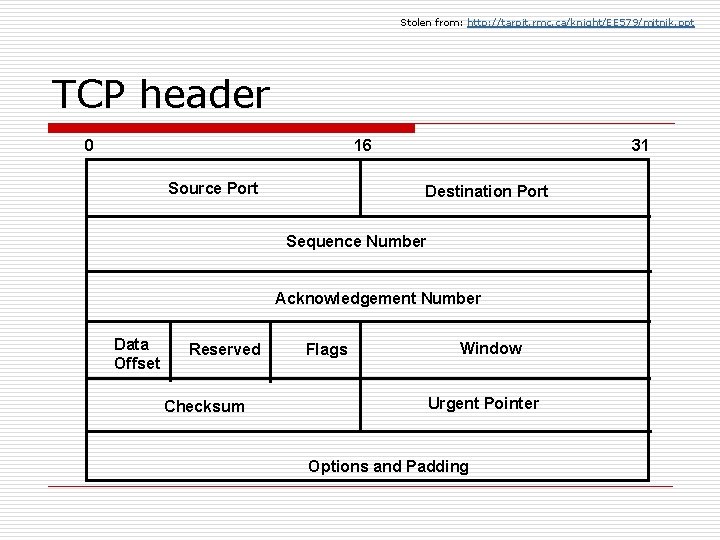
Stolen from: http: //tarpit. rmc. ca/knight/EE 579/mitnik. ppt TCP header 0 16 Source Port 31 Destination Port Sequence Number Acknowledgement Number Data Offset Reserved Checksum Flags Window Urgent Pointer Options and Padding
TCP Sequence Numbers Client Start SEQ - 1892 2. 3. 1. Server Client ACKs, transmits sends 50 20 no bytes data Server Start SEQ - 15562 SEQ – 1892 ACK – 15562 Size - 50 SEQ – 15562 ACK – 1942 Size - 25 SEQ – 1942 ACK – 15587 Size - 0 End SEQ - 1942 End SEQ - 15587