
Introduction to DNS and its vulnerabilities Olaf M
Introduction to DNS and its vulnerabilities Olaf M. Kolkman olaf@nlnetlabs. nl © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
d n a DNS a n i C E S S DN ll e h s t Nu 2 source: http: //upload. wikimedia. org/wikipedia/commons/b/b 7/Korean. Pine. Seeds. jpg

y l h g i h s i S Rec N D e urs Th N e v i ive a t m u b i Rec eser distr ver urs e Aut hor s over nam itat ese ive rs 3 s e i r e u q e c i Dev e v i s r u Rec r e v r e s e m a N DN imp S is l e t ch ca h e me ar ts ul Res rou ed n t g e h d tho 1 usa 00 s ma nds of chi o nes f

Authoritative Nameservers ROOT www. nlnetlabs. nl A Stub Resolver Recursive Nameservers NL referral: nl NS www. nlnetlabs. nl A 213. 154. 224. 1 www. nlnetlabs. nl A referral: nlnetlabs. nl NS www. nlnetlabs. nl A 213. 154. 224. 1 www. nlnetlabs. nl A Answer: www. nlnetlabs. nl A 213. 154. 224. 1 root. hints: location of the root servers 4 NLnet. Labs. N L
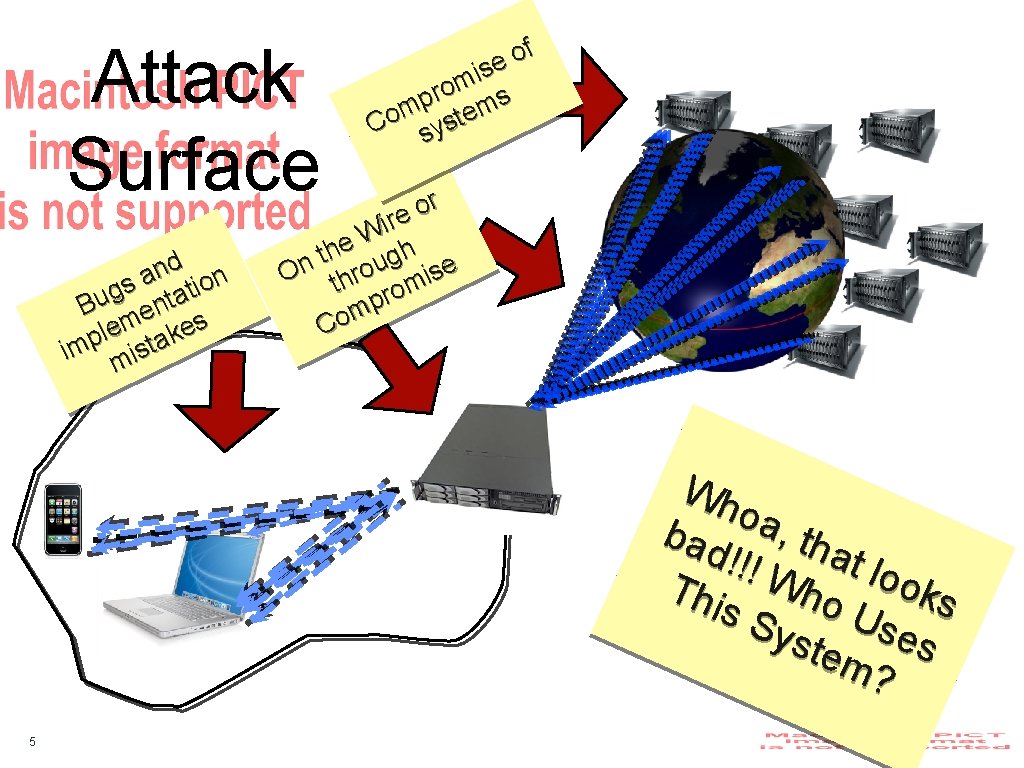
Attack Surface nd n a o s i t g a Bu ent m kes e l p ta m s i i m f o e s i m o r s p m m Co syste r o re i W e h h t g On throu mise ro p m o C Wh o bad a, th at lo !!! Th Who oks is S U yst ses em ? 5
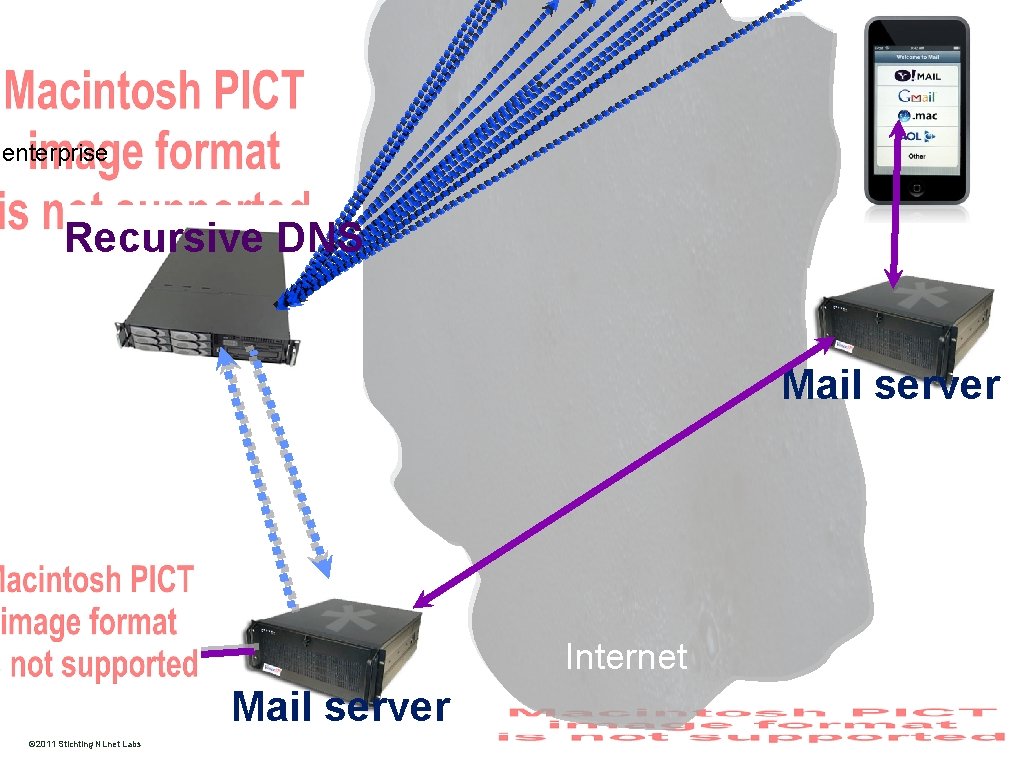
enterprise Recursive DNS Mail server Internet http: //www. nlnetlabs. nl/ © 2011 Stichting NLnet Labs Mail server
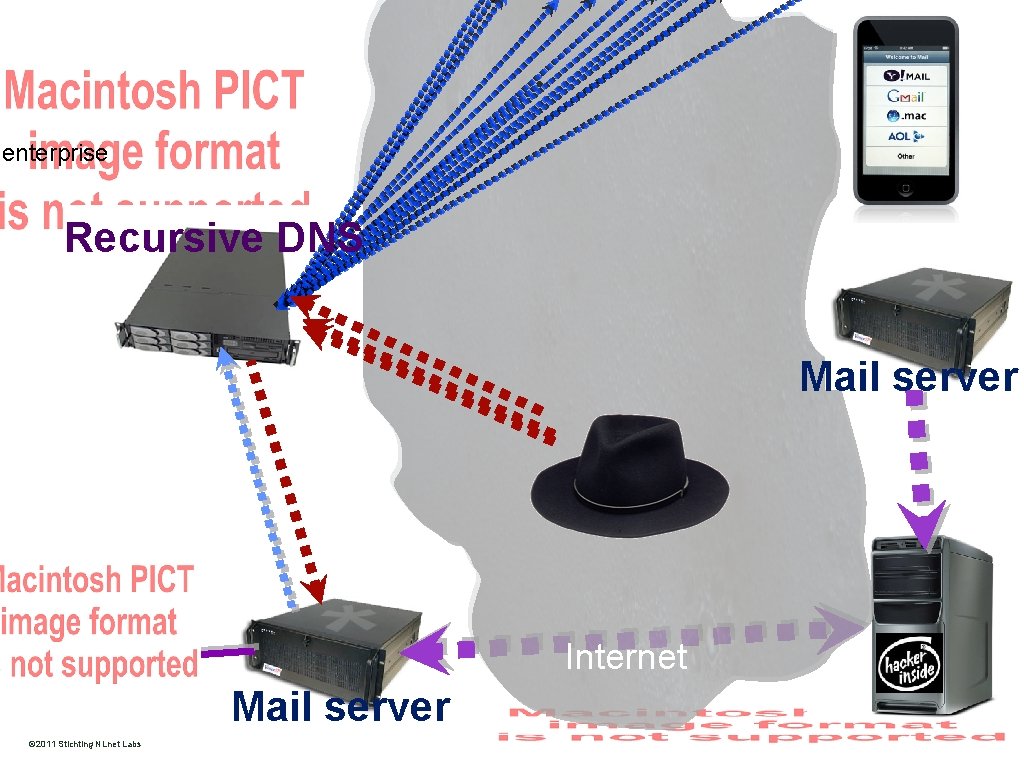
enterprise Recursive DNS Mail server Internet http: //www. nlnetlabs. nl/ © 2011 Stichting NLnet Labs Mail server
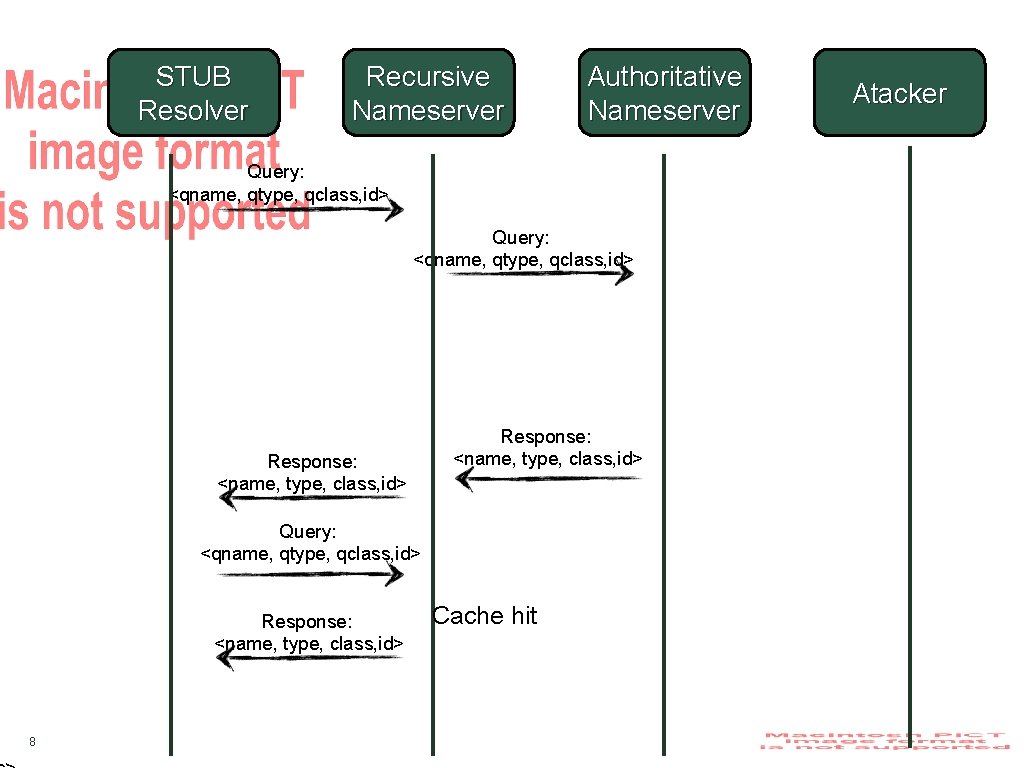
STUB Resolver Recursive Nameserver Authoritative Nameserver Query: <qname, qtype, qclass, id> Response: <name, type, class, id> 8 Cache hit Atacker

STUB Resolver Recursive Nameserver Authoritative Nameserver s u o i r a v n o e h d t t a An h t s Query: e i t r o t e s p <qname, qtype, qclass, id> d o e pr e n r e h c atta h c t a m Response: t r o P D I e c r u o <name, type, class, id> y S r e Qu Response: Atacker Query: <qname, qtype, qclass, id> Response: <name, type, class, id> 0 X 20 Query: <qname, qtype, qclass, id> Response: <name, type, class, id> 9 Cache hit Succ ess d epen on le d s g a c spee y and d of netw ork.
TTL saves you? !? I don’t think so. . Dan Kaminsky’s image from zdnet. com 10 y t i r u c Se r a t s p Po
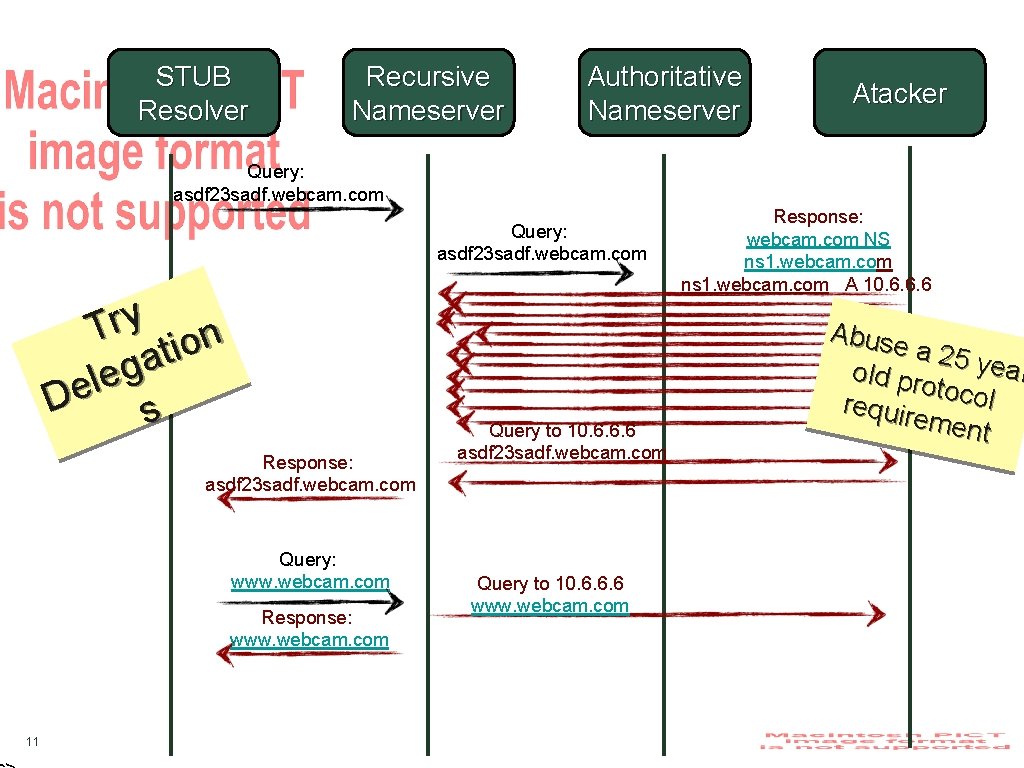
STUB Resolver Recursive Nameserver Authoritative Nameserver Atacker Query: asdf 23 sadf. webcam. com Try ion t a g e l De s Response: asdf 23 sadf. webcam. com Query: www. webcam. com Response: www. webcam. com 11 Query to 10. 6. 6. 6 asdf 23 sadf. webcam. com Query to 10. 6. 6. 6 www. webcam. com Response: webcam. com NS ns 1. webcam. com A 10. 6. 6. 6 Abuse a 25 y ear old pr otoco l requir emen t
Do a ttack happ s en in prac tice? ? e c i t o n u o y d l u Wo ou y d l Wou ll? te 12
Do a ttack happ s en in prac tice? e n o d l u o w ? y S h N W D e h t k c atta Wh ile one doi ng c oth ould er t b hin e gs 13
How t o Prot ect? 14
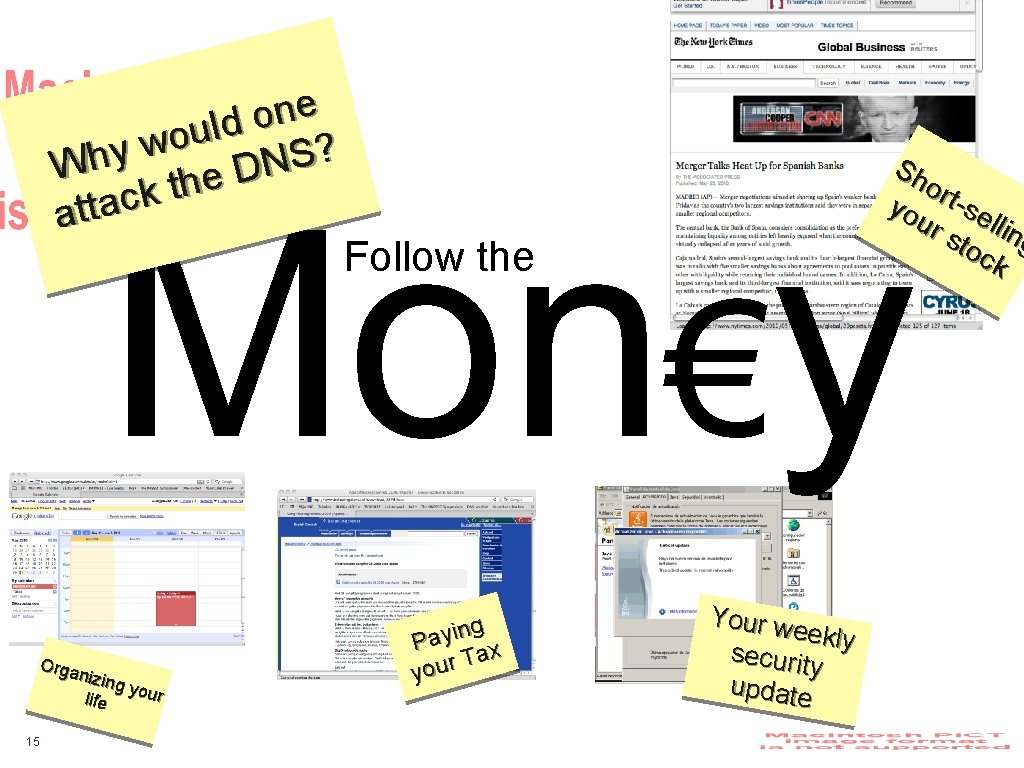
e n o d l u o w ? y S h N W D e h t k c a t t a Sh ort yo -se ur llin sto g ck Mon€y Orga nizin g you r life 15 Follow the ng i y a P x a T r you Your w eekly securit y update
Mon€y e s e h t l l a t ’ e n s o u D s n o i t c a s d tran n a SSL tes? a c i f i t r e C 16
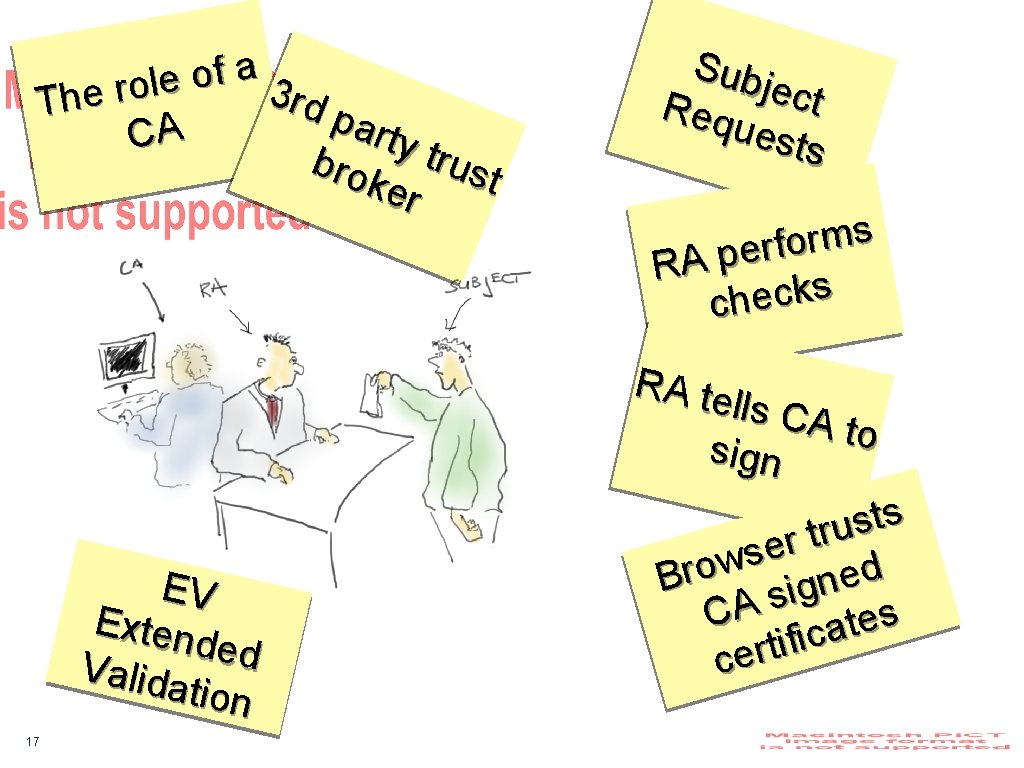
a f o e l o r 3 rd e h T p arty A C bro trust ker Sub j e Req ct uest s s m r o f r e p A R s k c e h c RA te lls CA t o sign EV Exten ded Valida tion 17 s t s u r t r e s w Bro signed s CA e t a c i f i t r ce
Howe ver al little m l thes e en ar eaw bit ex ee pensi ve AUTOMATE THE LOT 18
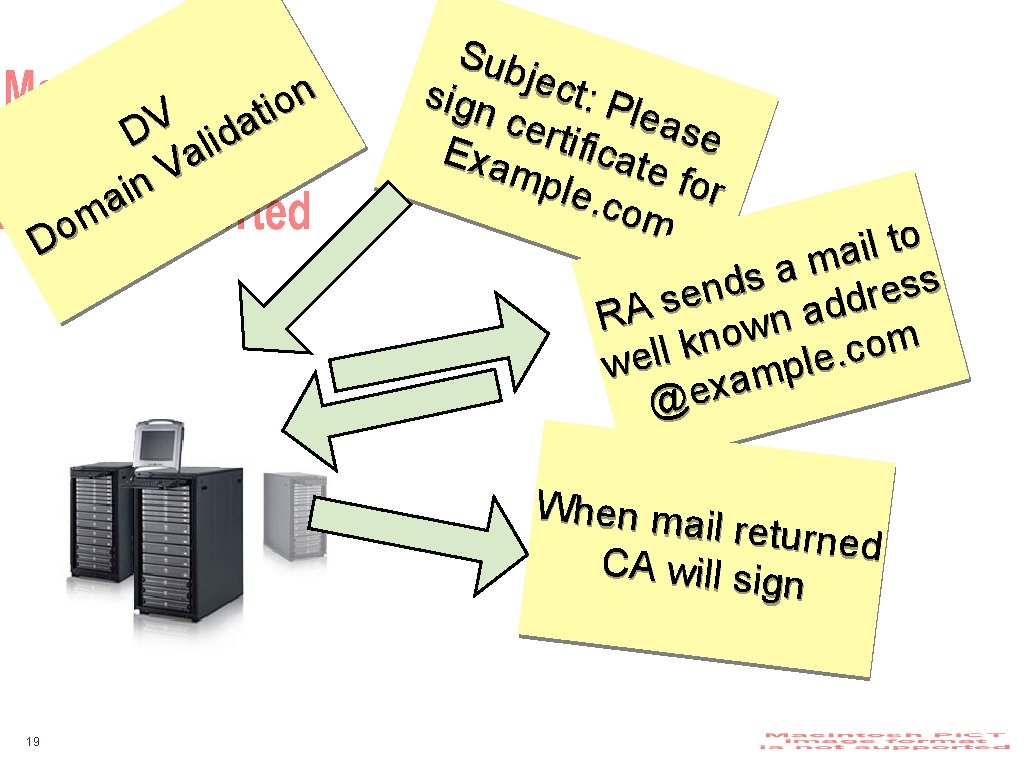
n o i t V D lida a V n i a m o D Sub j e sign ct: Pl eas certi e fi ca Exa te fo mpl r e. co m o t l i a m a s s d s n e r e s d d A a R n w o m n k o l c l. e l we p m a x @e When ma il returned CA will sig n 19
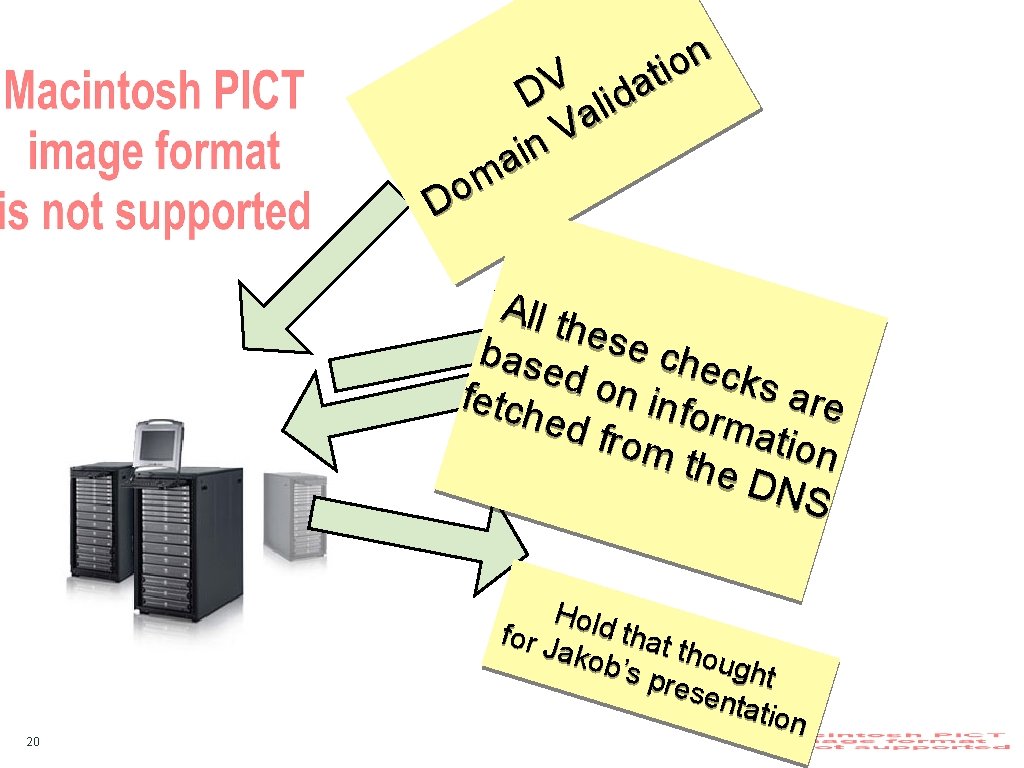
n o i t V D lida a V n i a m o D All th e base se che cks d o n info are fetch ed fr rma tion om t he D NS 20 Hold that for J thou akob ght ’s p rese ntatio n
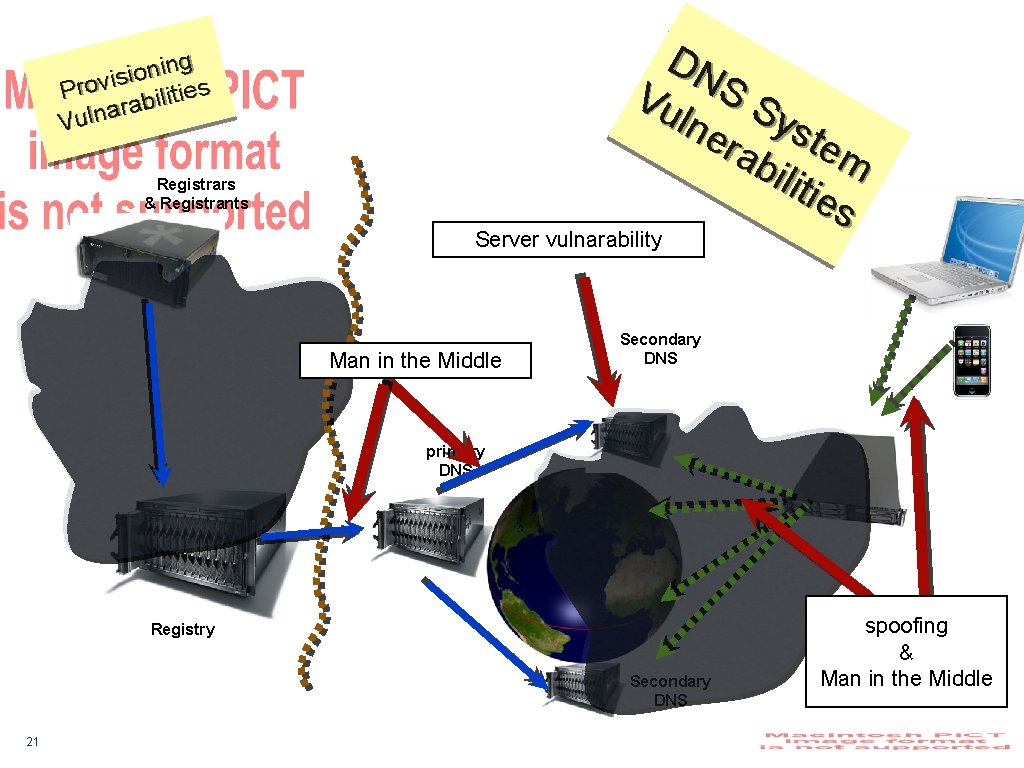
DN Vu S S lne ys rab tem iliti es g n i n o i s i v o r P es i t i l i b ra a n l u V Registrars & Registrants Server vulnarability Man in the Middle Secondary DNS primary DNS Registry Secondary DNS 21 spoofing & Man in the Middle
Wha t can one prot d ect. . o to. (skip ping DNS SEC ) 22
Taking Unbound as example. Othe r mak server s mi e oth g e r cho ht but a ices ny m reso , oder lver n take s sim appr oach ilar es © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Security Choices in Unbound • In general, a modern paranoid resolver • DNSSEC support. • RFC 2181 support completely • Fine grained. Keeps track of where RRSets came from and won't upgrade them into answers. • Does not allow RRSets to be overridden by lower level rrsets © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Filtering • • Scrubber: Only in-bailiwick data is accepted in the answer • • The answer section must contain only answer CNAME, DNAME checked that chain is correct • CNAME cut off and only the first CNAME kept • • • Lookup rest yourself do not trust other server DNAME synthesize CNAME by unbound do not trust other server. Also cut off like above. DNAME from cache only used if DNSSEC-secure. © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Filtering II • No address records in authority, additional section unless relevant – i. e. mentioned in a NS record in the authority section. • Irrelevant data is removed • When the message only had preliminary parsing and has not yet been copied to the working region of memory © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Entropy • • • Randomness protects against spoof • • Arc 4 random() (Open. BSD): crypto strong. May not be perfectly random, but predicting it is a cryptographical breakin. Real entropy from OS as seed Query id – all 16 bits used. Port randomisation – uses all 16 bits there, goes out of its way to make sure every query gets a fresh port number © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Entropy II • Destination address, and ipv 4/ipv 6. RTT band of 400 msec (=everything). • • • Its not the timewindow but the randomness Query aggregation – same queries are not sent out – unless by different threads Qname strict match checked in reply 0 x 20 option Harden-referral-path (my draft) option Can use multiple source interfaces! • 4 outgoing IP address add +2 bits © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Other measures • Not for the wire itself • • Heap function pointer protection (whitelisted) Chroot() by default User privileges are dropped (lots of code!) ACL for recursion No detection of attacks – assume always under attack version. bind hostname. bind can be blocked or configured what to return (version hiding) Disprefer recursion lame servers – they have a cache that can be poisoned © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Arm s Ra ce. . . C E S S N D g n i c u d o r Int © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Metaphor 31
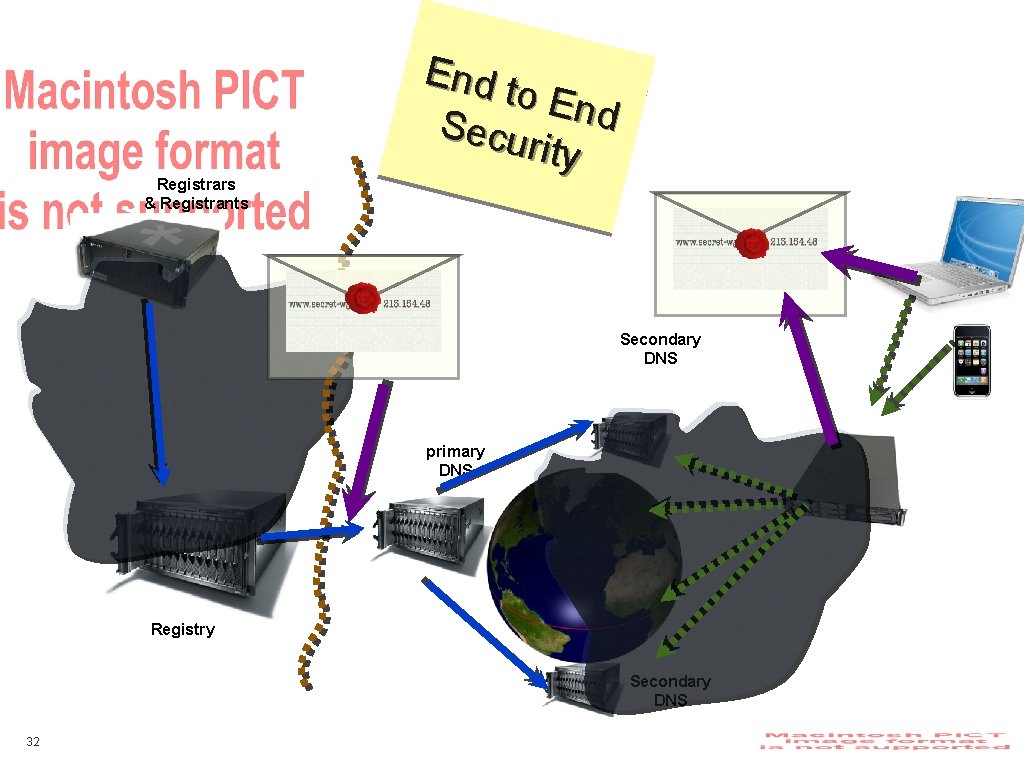
Registrars & Registrants End t o End Secu rity Secondary DNS primary DNS Registry Secondary DNS 32
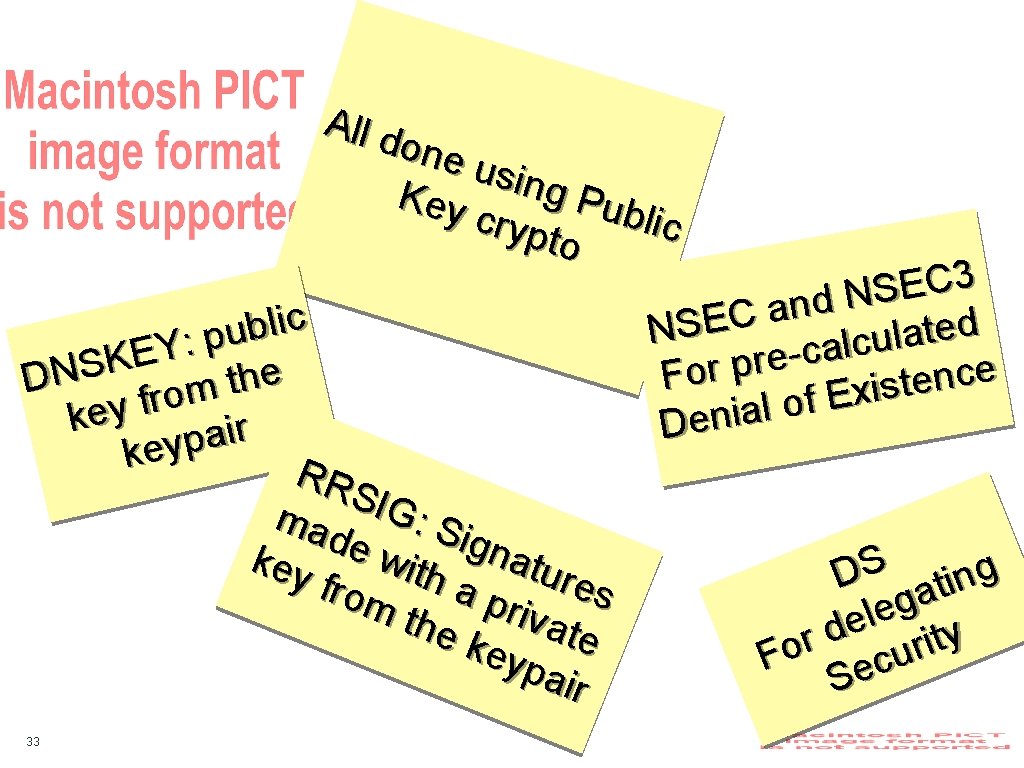
All d one usin g Pu Key blic cryp to c i l b u p : Y E K S N e h D t m o r f key r i a p key RR SIG ma : Sig de with natu key from a p res the rivate key pair 33 3 C E S N d n a C E d e NS t a l u c l a c e r p r e c Fo n e t s i x E f o l a i Den DS ating g e l e d y t r i Fo ecur S
But more on that later Let u ano s ha ve a the r cr DN ypto look a Sp t g r me rotec aphic tion cha nism © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Securing Host Communication © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
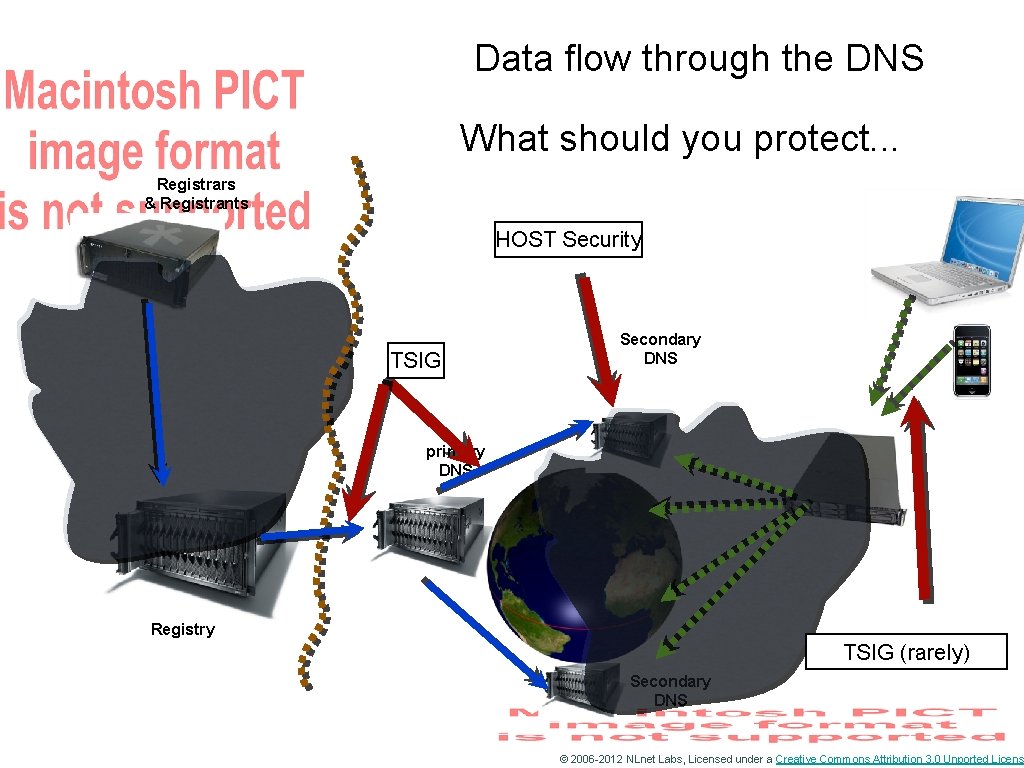
Data flow through the DNS What should you protect. . . Registrars & Registrants HOST Security TSIG Secondary DNS primary DNS Registry TSIG (rarely) Secondary DNS © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Transaction Signature: TSIG • TSIG (RFC 2845) –Authorising dynamic updates and zone transfers –Authentication of caching forwarders –Independent from other features of DNSSEC • One-way hash function –DNS question or answer and timestamp • Traffic signed with “shared secret” key • Used in configuration, NOT in zone file © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
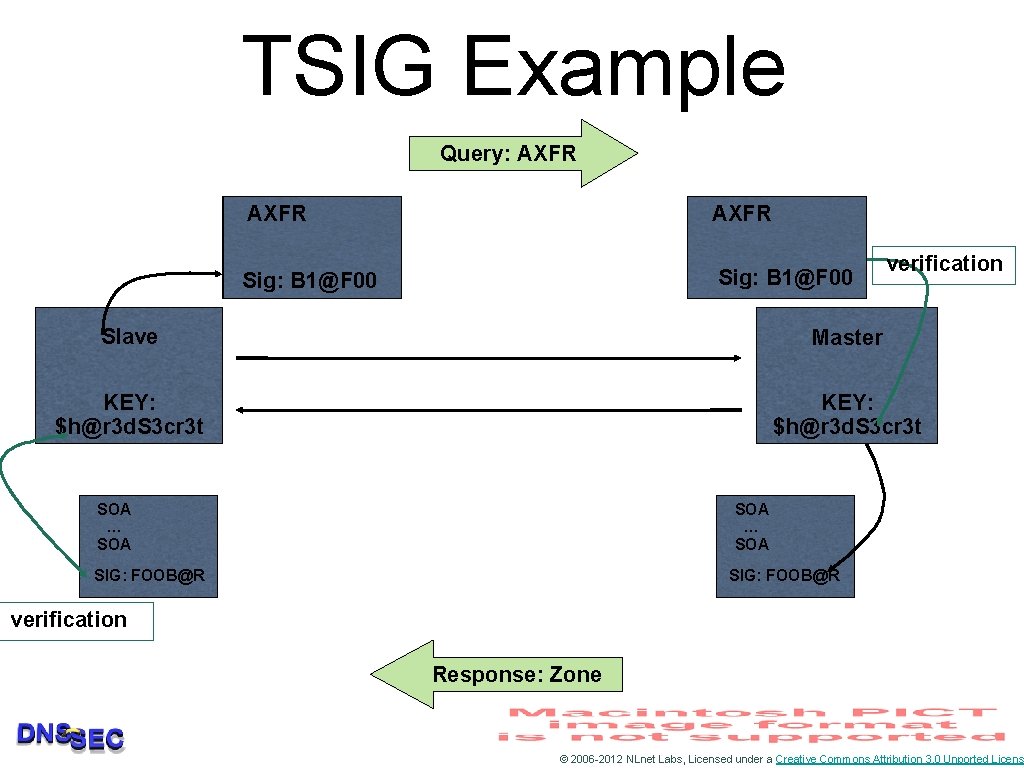
TSIG Example Query: AXFR Sig: B 1@F 00 verification Slave Master KEY: $h@r 3 d. S 3 cr 3 t SOA … SOA SIG: FOOB@R verification Response: Zone © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
TSIG for Zone Transfers 1. Generate secret 2. Communicate secret 3. Configure servers 4. Test © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Importance of the Time Stamp • TSIG/SIG(0) signs a complete DNS request / response with time stamp – To prevent replay attacks – Currently hardcoded at five minutes • Operational problems when comparing times – Make sure your local time zone is properly defined – date -u will give UTC time, easy to compare between the two systems – Use NTP synchronisation! © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Authenticating Servers Using SIG(0) • Alternatively, it is possible to use SIG(0) –Not yet widely used –Works well in dynamic update environment • Public key algorithm –Authentication against a public key published in the DNS • SIG(0) specified in RFC 2931 © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
Cool Application • Use TSIG-ed dynamic updates to configure your laptops name • My laptop is know by the name of aagje. secret-wg. org – http: //ops. ietf. org/dns/dynupd/secure-ddnshowto. html –Mac OS users: there is a bonjour based tool. • www. dns-sd. org © 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
© 2006 -2012 NLnet Labs, Licensed under a Creative Commons Attribution 3. 0 Unported Licens
- Slides: 43