
Information Security Forum From an ISO 17799 Audit
- Slides: 15
Information Security Forum From an ISO 17799 Audit to an Information Security Plan (the 100 day plans - part 2) By Jim Reiner Sacramento County July 31, 2007
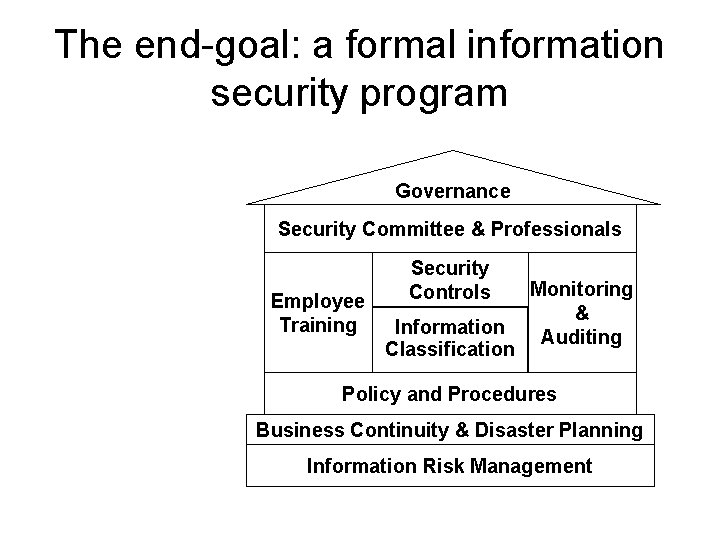
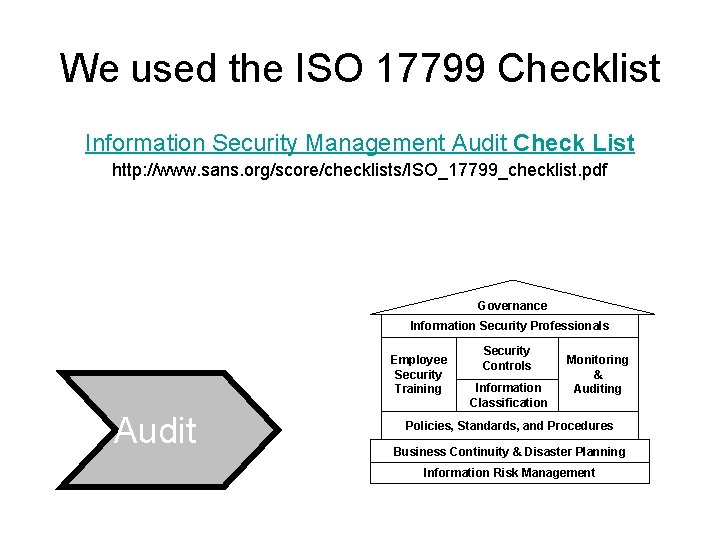
The end-goal: a formal information security program Governance Security Committee & Professionals Employee Training Security Controls Information Classification Monitoring & Auditing Policy and Procedures Business Continuity & Disaster Planning Information Risk Management
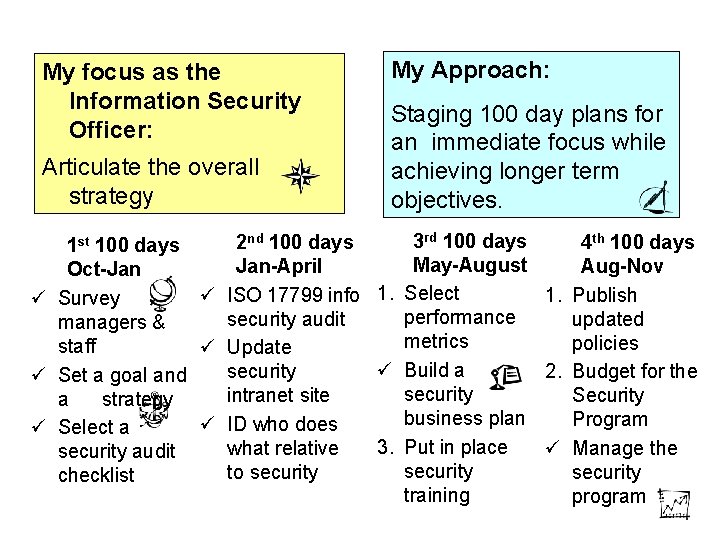
My focus as the Information Security Officer: Articulate the overall strategy My Approach: Staging 100 day plans for an immediate focus while achieving longer term objectives. 3 rd 100 days 2 nd 100 days 4 th 100 days 1 st 100 days May-August Jan-April Aug-Nov Oct-Jan ü ISO 17799 info 1. Select 1. Publish ü Survey performance security audit updated managers & metrics policies staff ü Update ü Build a security 2. Budget for the ü Set a goal and security intranet site Security a strategy business plan Program ü ID who does ü Select a 3. Put in place what relative ü Manage the security audit security to security checklist training program
www. ocit. saccounty. net/Information. Security/index. htm
Audit IS Plan IS Pgm
We used the ISO 17799 Checklist Information Security Management Audit Check List http: //www. sans. org/score/checklists/ISO_17799_checklist. pdf Governance Information Security Professionals Employee Security Training Audit Security Controls Information Classification Monitoring & Auditing Policies, Standards, and Procedures Business Continuity & Disaster Planning Information Risk Management
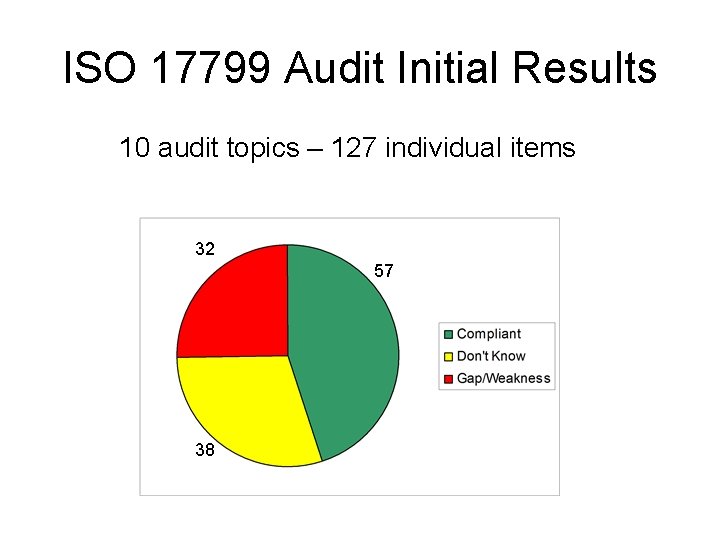
ISO 17799 Audit Initial Results 10 audit topics – 127 individual items 32 57 38
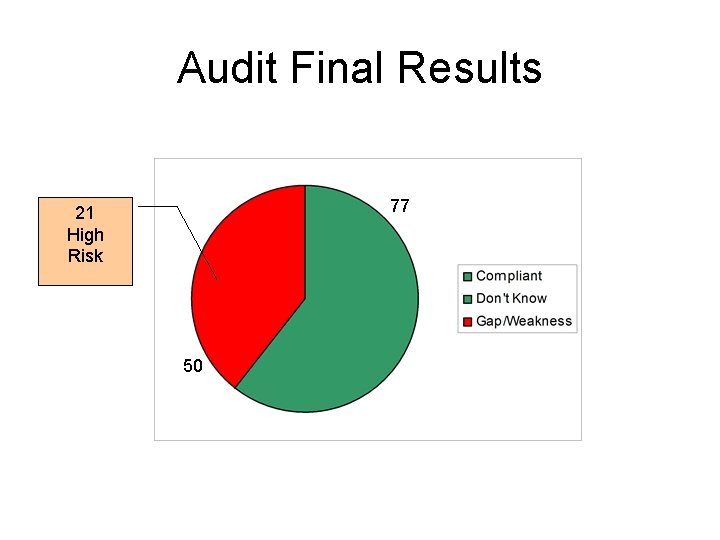
Audit Final Results 77 21 High Risk 50
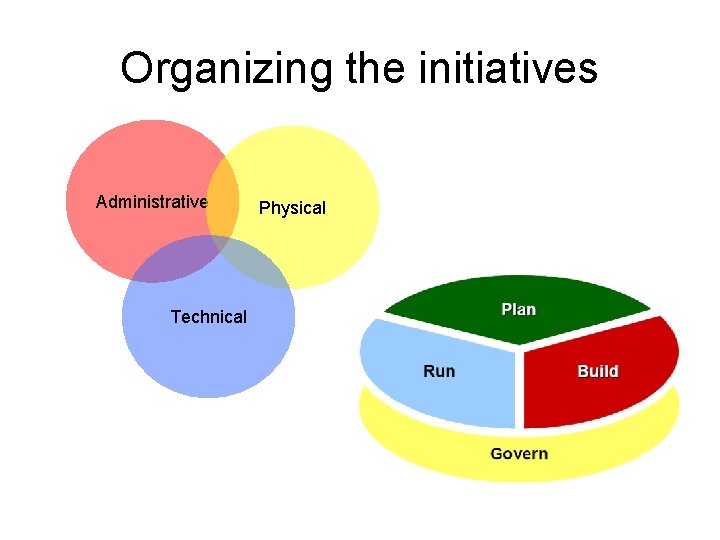
Organizing the initiatives Administrative Technical Physical
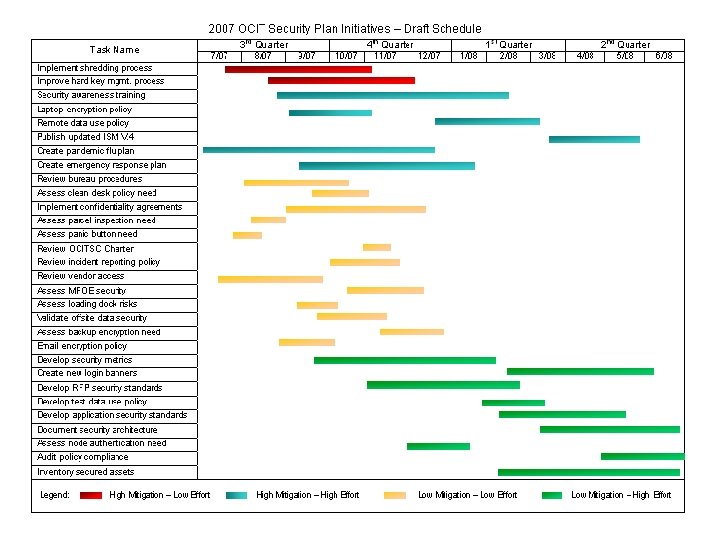
IS Plan 1 of 4
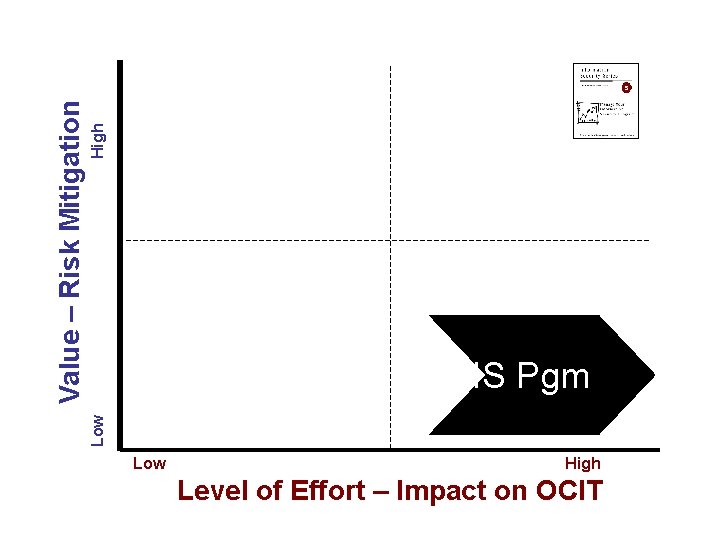
High Low Value – Risk Mitigation IS Pgm Low High Level of Effort – Impact on OCIT
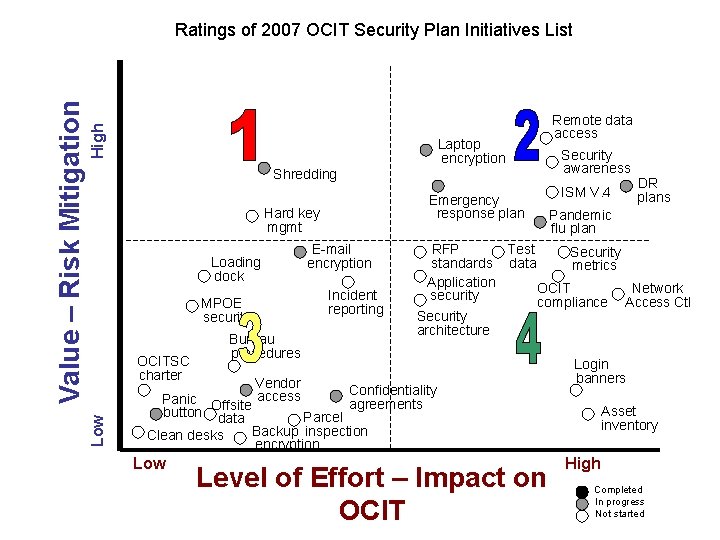
High Laptop encryption Shredding Emergency response plan Hard key mgmt Loading dock OCITSC charter E-mail encryption Incident reporting MPOE security Low Value – Risk Mitigation Ratings of 2007 OCIT Security Plan Initiatives List Bureau procedures Security awareness ISM V. 4 DR plans Pandemic flu plan RFP Test Security standards data metrics Application OCIT Network security compliance Access Ctl Security architecture Vendor access Confidentiality Panic Offsite agreements button data Parcel Backup inspection Clean desks encryption Low Remote data access Level of Effort – Impact on OCIT Login banners Asset inventory High Completed In progress Not started
Network Vulnerability Assessment and Mitigation A CASE STUDY
www. ocit. saccounty. net/Information. Security/index. htm