
Incident Response in case of Advanced Persistent Threat
- Slides: 17
Incident Response in case of Advanced Persistent Threat Actor Dr. Viktor Polic, CISA, CRISC, CISSP Chief Information Security Officer - International Labour Organization Adjunct professor – Webster University Geneva
The views expressed herein are those of the author and do not necessarily reflect the views of the International Labour Organization. Dr. Viktor Polic, CISA, CRISC, CISSP 2
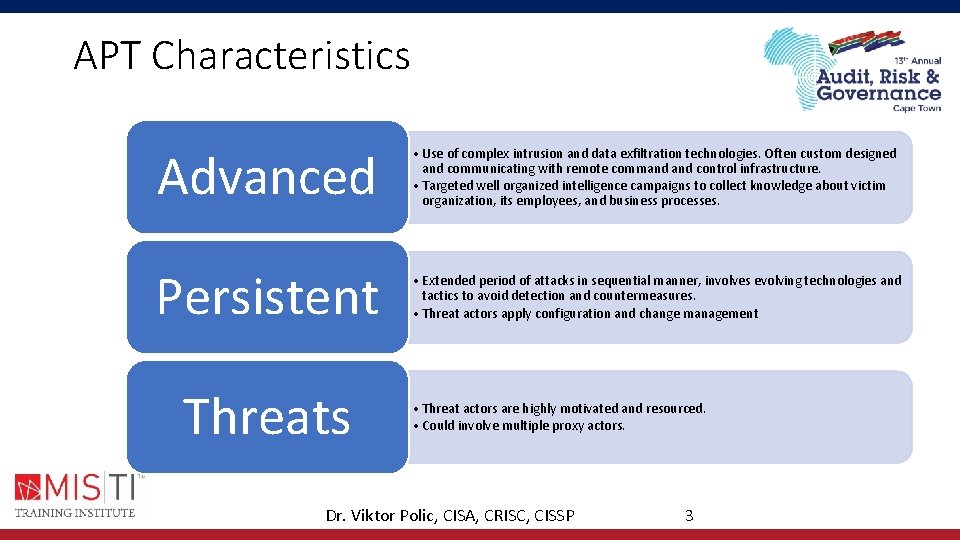
APT Characteristics Advanced • Use of complex intrusion and data exfiltration technologies. Often custom designed and communicating with remote command control infrastructure. • Targeted well organized intelligence campaigns to collect knowledge about victim organization, its employees, and business processes. Persistent • Extended period of attacks in sequential manner, involves evolving technologies and tactics to avoid detection and countermeasures. • Threat actors apply configuration and change management Threats • Threat actors are highly motivated and resourced. • Could involve multiple proxy actors. Dr. Viktor Polic, CISA, CRISC, CISSP 3
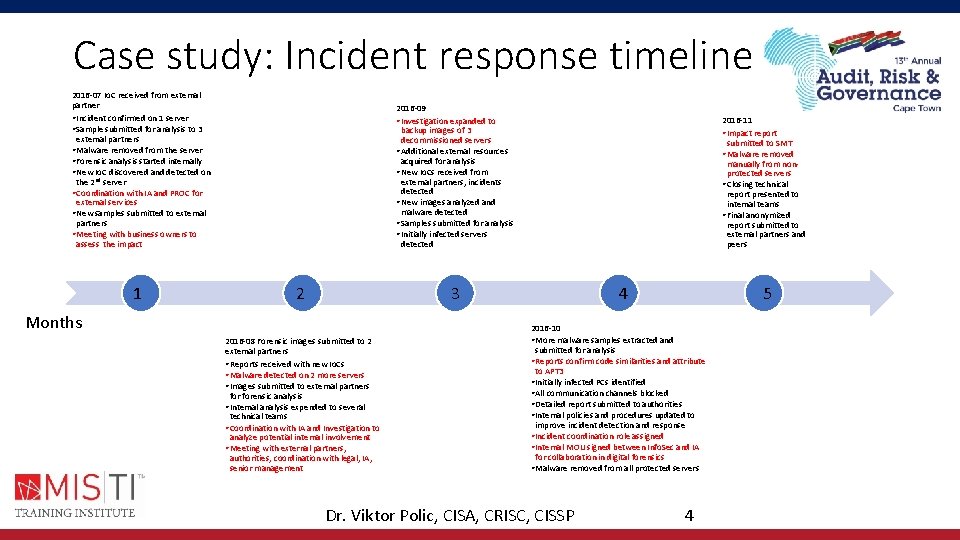
Case study: Incident response timeline 2016 -07 Io. C received from external partner • Incident confirmed on 1 server • Sample submitted for analysis to 3 external partners • Malware removed from the server • Forensic analysis started internally • New Io. C discovered and detected on the 2 nd server • Coordination with IA and PROC for external services • New samples submitted to external partners • Meeting with business owners to assess the impact 1 2016 -09 • Investigation expanded to backup images of 3 decommissioned servers • Additional external resources acquired for analysis • New Io. Cs received from external partners, incidents detected • New images analyzed and malware detected • Samples submitted for analysis • Initially infected servers detected 2 2016 -11 • Impact report submitted to SMT • Malware removed manually from nonprotected servers • Closing technical report presented to internal teams • Final anonymized report submitted to external partners and peers 3 Months 2016 -08 Forensic images submitted to 2 external partners • Reports received with new Io. Cs • Malware detected on 2 more servers • Images submitted to external partners forensic analysis • Internal analysis expended to several technical teams • Coordination with IA and Investigation to analyze potential internal involvement • Meeting with external partners, authorities, coordination with legal, IA, senior management 4 5 2016 -10 • More malware samples extracted and submitted for analysis • Reports confirm code similarities and attribute to APT 3 • Initially infected PCs identified • All communication channels blocked • Detailed report submitted to authorities • Internal policies and procedures updated to improve incident detection and response • Incident coordination role assigned • Internal MOU signed between Info. Sec and IA for collaboration in digital forensics • Malware removed from all protected servers Dr. Viktor Polic, CISA, CRISC, CISSP 4
Case study of APT 3 or “Pirpi” • Cyber-espionage operations against industrial targets, governments, public-sector. • Ability to acquire or develop 0 -day exploits. • Rapid adoption of disclosed vulnerabilities and update deployed malware. • Uses steganography to conceal malware. • Uses custom cryptography to establish communication. • Uses specific command control (C&C) infrastructure for each target. • Reference https: //attack. mitre. org/wiki/Group/G 0022 Dr. Viktor Polic, CISA, CRISC, CISSP 5
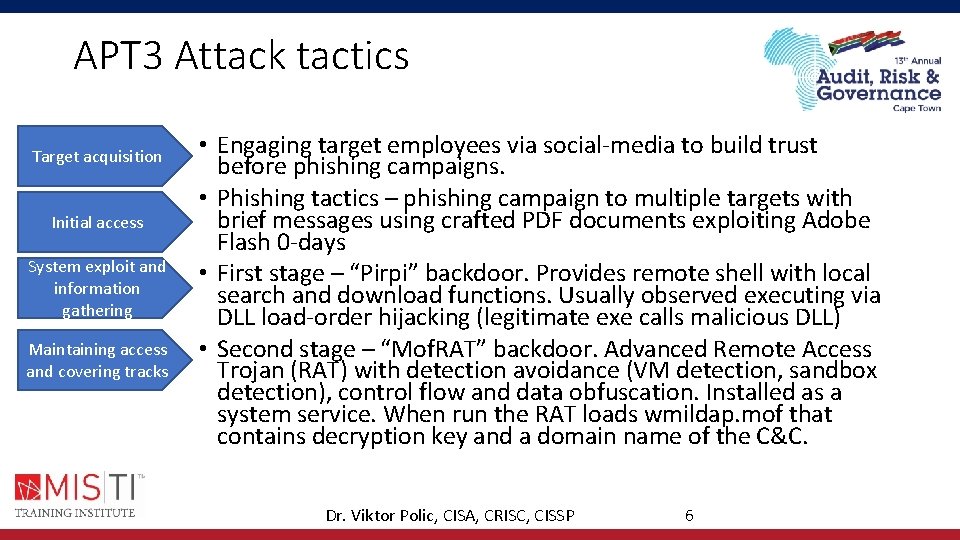
APT 3 Attack tactics Target acquisition Initial access System exploit and information gathering Maintaining access and covering tracks • Engaging target employees via social-media to build trust before phishing campaigns. • Phishing tactics – phishing campaign to multiple targets with brief messages using crafted PDF documents exploiting Adobe Flash 0 -days • First stage – “Pirpi” backdoor. Provides remote shell with local search and download functions. Usually observed executing via DLL load-order hijacking (legitimate exe calls malicious DLL) • Second stage – “Mof. RAT” backdoor. Advanced Remote Access Trojan (RAT) with detection avoidance (VM detection, sandbox detection), control flow and data obfuscation. Installed as a system service. When run the RAT loads wmildap. mof that contains decryption key and a domain name of the C&C. Dr. Viktor Polic, CISA, CRISC, CISSP 6
APT 3 Communication with C&C • The older variant uses Microsoft secure channel API from sspicli. dll on port 443 and MS Crypto. API to create a certificate store. It is able to tunnel through victim’s proxy server. It could also encode and randomize initial beacon to avoid detection. • Newer samples use the Open. SSL library instead of MS secure channel. They are larger because the Open. SSL is statically compiled. • Network traffic is difficult to detect since C&C infrastructure evolves more dynamically than threat intelligence and indicators of compromise (Io. C) Dr. Viktor Polic, CISA, CRISC, CISSP 7
APT 3 Functionality • RAT can fork interactive shell (cmd. exe), download and upload files, update configuration, and alter communication parameters. • Provides interactive remote sessions as well as batch processing. • Recent samples provide anti-forensic functionality • Provides Windows Registry manipulation. • Provides memory manipulation and debugger hooks to prevent reverse engineering. • Contains handles to windows user desktop to interact with end-users. Dr. Viktor Polic, CISA, CRISC, CISSP 8
APT 3 Code analysis of a 0 -day • UPS. EXE matches the common portable executable (PE) format. • It uses Import address table for DLLs: • Open. SSL, Kernel 32. dll, advapi 32. dll, msvcr 90. dll, ws 2_32. dll, shlwapi. dll, user 32. dll • Still detected by 31 out of 55 anti-malware products referenced by Virustotal • Reference: https: //www. virustotal. com/en/file/4 b 0 eef 64 b 378 c 3101551662170 f 3 b 6 ee 577 b 0 d 525 afba 93 e 17 5 b 9 b 06 fd 99 e 199/analysis/ Dr. Viktor Polic, CISA, CRISC, CISSP 9
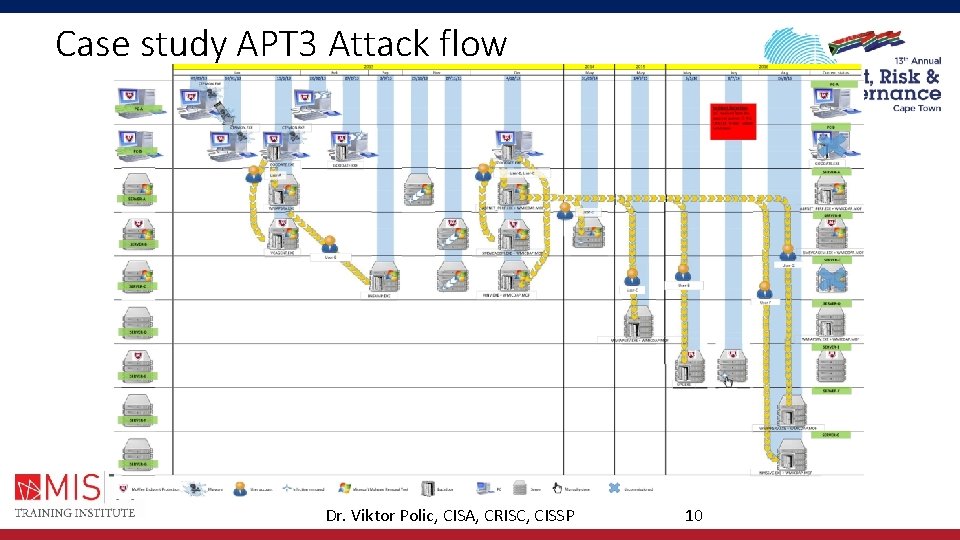
Case study APT 3 Attack flow Dr. Viktor Polic, CISA, CRISC, CISSP 10
Case study: Impact summary • 7 servers and 2 PCs compromised during 3 years long campaign • 3 IT administrator accounts compromised • 3 IT service accounts compromised • 10 “zero-day” malware binaries identified • 3 entry points to C&C infrastructure identified at 3 ISPs (2 countries) • 1 “zero-day” could be sold for 300’ 000 USD Ref: https: //zerodium. com/program. html Dr. Viktor Polic, CISA, CRISC, CISSP 11
APT Countermeasures • Prevention • Policy – Technology use, Incident reporting and response, Identity management • Awareness – End-user education on risk avoidance, Anti-phishing simulations, IT administrators training • Vulnerability mitigation – Computer hardening, Patch management, Configuration management, Access control with segregation of roles, Application whitelisting, Network segregation, Multi-factor authentication • Data Backup Dr. Viktor Polic, CISA, CRISC, CISSP 12
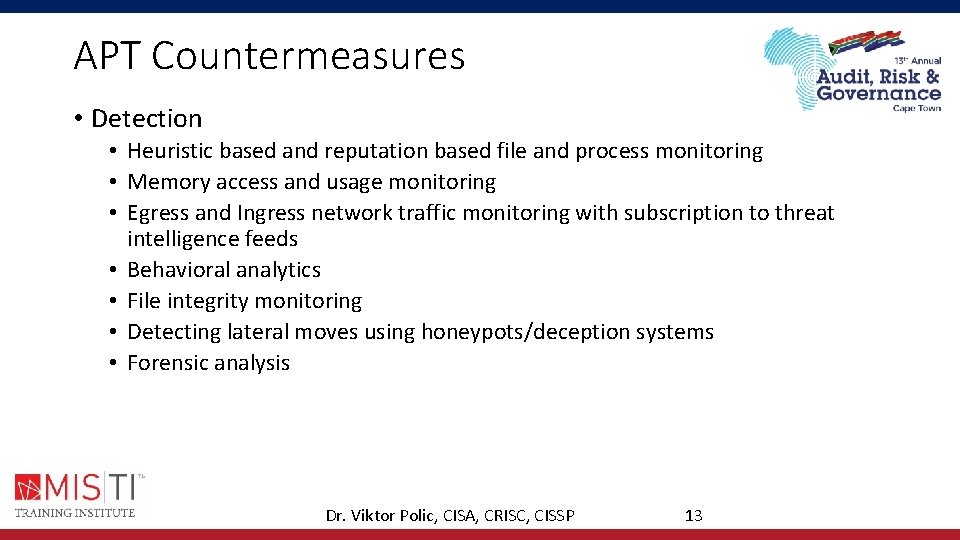
APT Countermeasures • Detection • Heuristic based and reputation based file and process monitoring • Memory access and usage monitoring • Egress and Ingress network traffic monitoring with subscription to threat intelligence feeds • Behavioral analytics • File integrity monitoring • Detecting lateral moves using honeypots/deception systems • Forensic analysis Dr. Viktor Polic, CISA, CRISC, CISSP 13
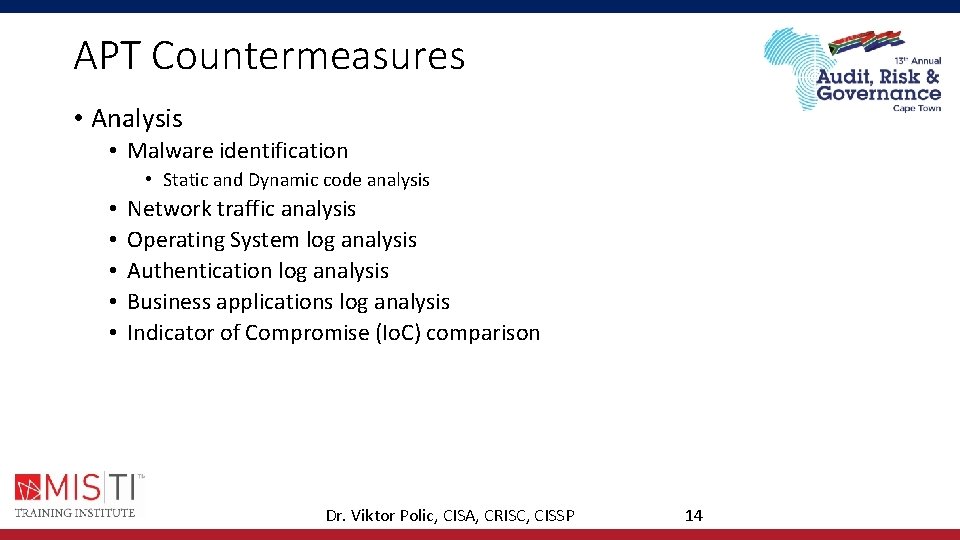
APT Countermeasures • Analysis • Malware identification • Static and Dynamic code analysis • • • Network traffic analysis Operating System log analysis Authentication log analysis Business applications log analysis Indicator of Compromise (Io. C) comparison Dr. Viktor Polic, CISA, CRISC, CISSP 14
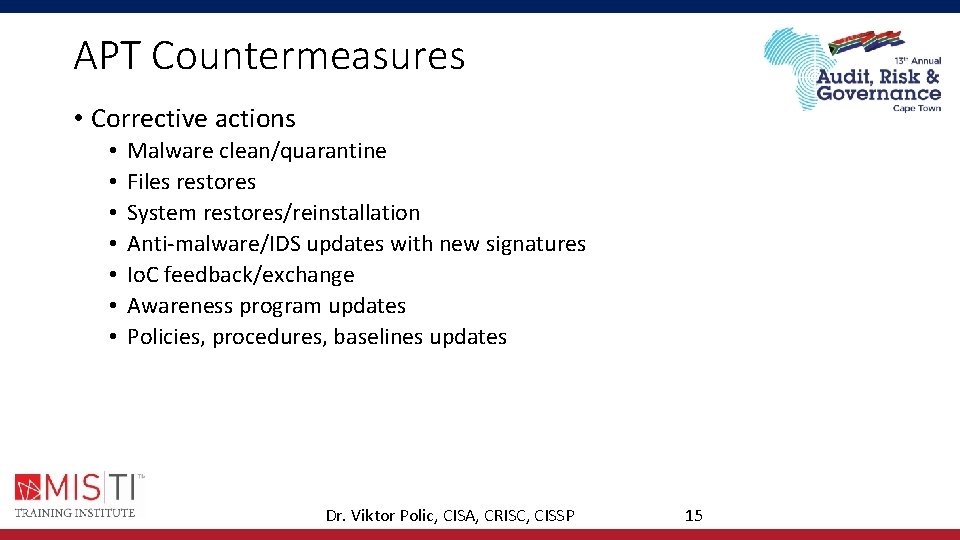
APT Countermeasures • Corrective actions • • Malware clean/quarantine Files restores System restores/reinstallation Anti-malware/IDS updates with new signatures Io. C feedback/exchange Awareness program updates Policies, procedures, baselines updates Dr. Viktor Polic, CISA, CRISC, CISSP 15
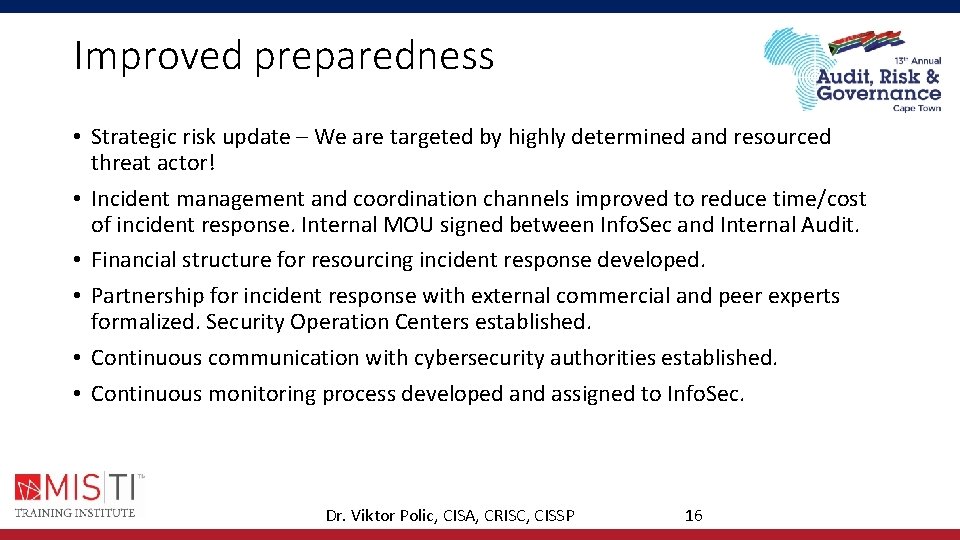
Improved preparedness • Strategic risk update – We are targeted by highly determined and resourced threat actor! • Incident management and coordination channels improved to reduce time/cost of incident response. Internal MOU signed between Info. Sec and Internal Audit. • Financial structure for resourcing incident response developed. • Partnership for incident response with external commercial and peer experts formalized. Security Operation Centers established. • Continuous communication with cybersecurity authorities established. • Continuous monitoring process developed and assigned to Info. Sec. Dr. Viktor Polic, CISA, CRISC, CISSP 16
Q&A https: //cybersymbiosis. com/ vpolic@cybersymbiosis. com https: //ch. linkedin. com/in/viktor-polic-891 a 1 a 145 https: //twitter. com/Viktor. Polic Dr. Viktor Polic, CISA, CRISC, CISSP 17