
http grca nat gov tw http gca nat
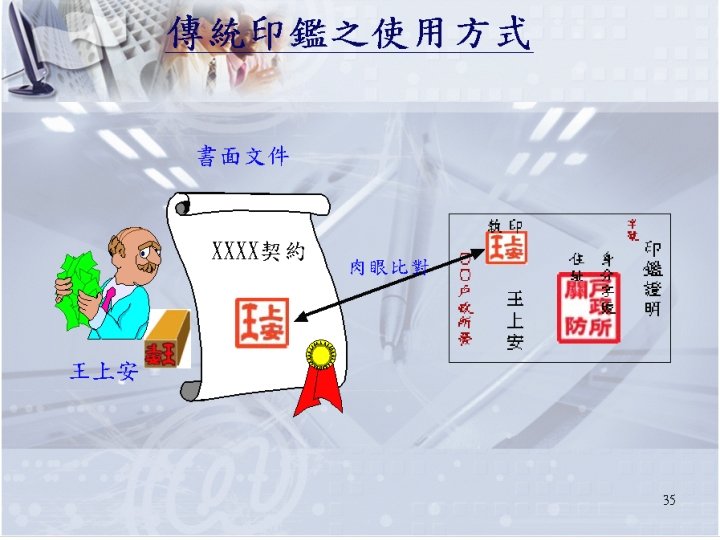
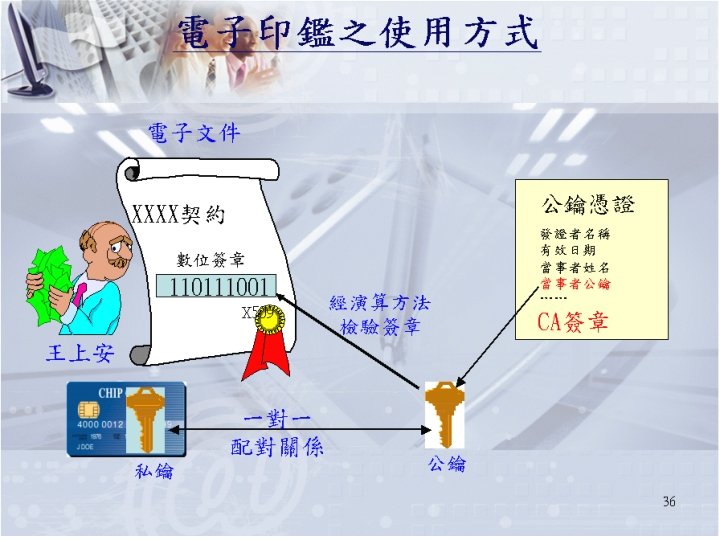
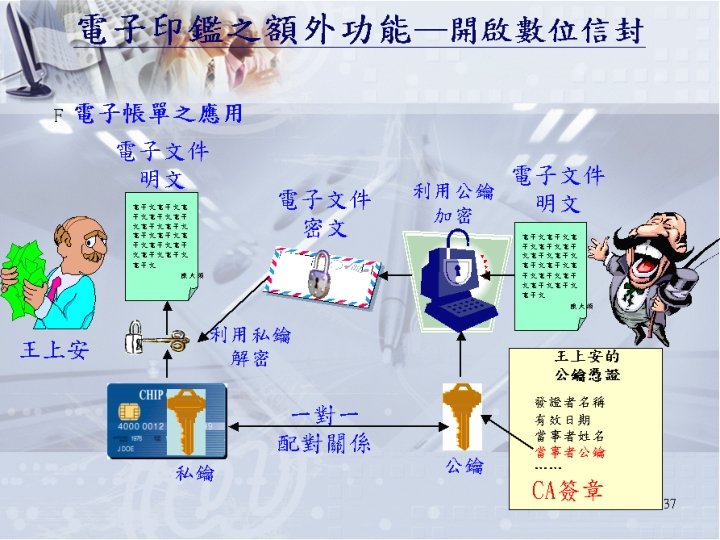
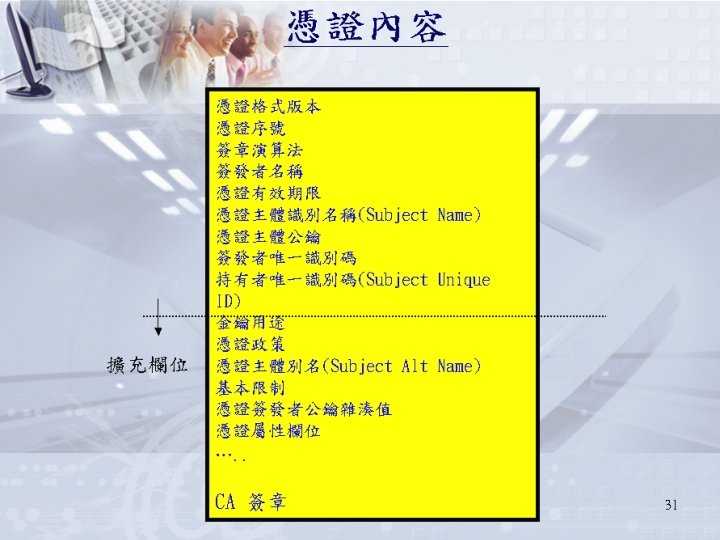
- Slides: 51
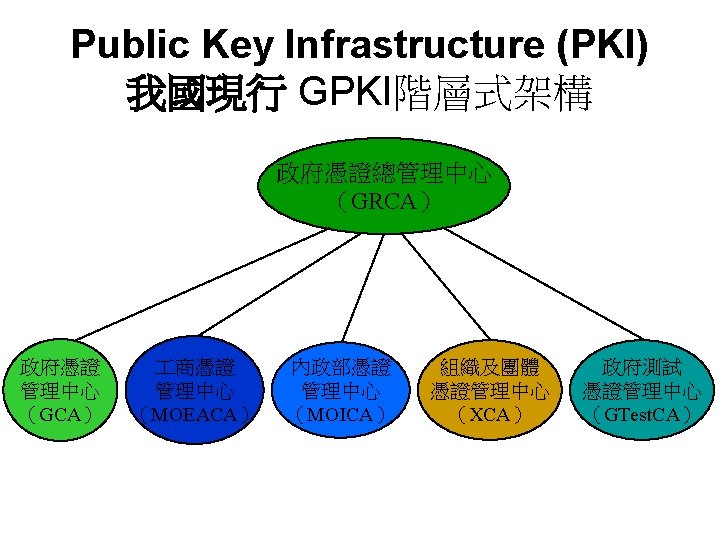
相關網址 • • http: //grca. nat. gov. tw http: //gca. nat. gov. tw http: //xca. nat. gov. tw http: //moica. nat. gov. tw http: //gtestca. nat. gov. tw http: //moeaca. nat. gov. tw 政府OID查詢網站(http: //oid. nat. gov. tw)
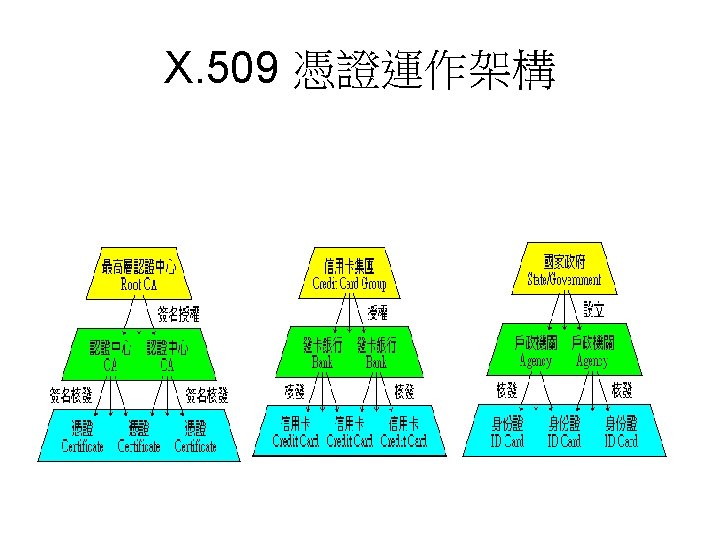
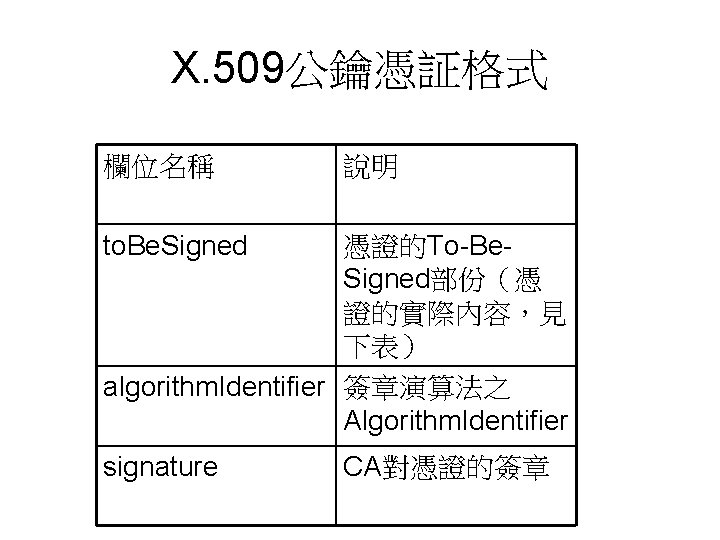
X. 509公鑰憑証格式 欄位名稱 說明 to. Be. Signed 憑證的To-Be. Signed部份(憑 證的實際內容,見 下表) algorithm. Identifier 簽章演算法之 Algorithm. Identifier signature CA對憑證的簽章
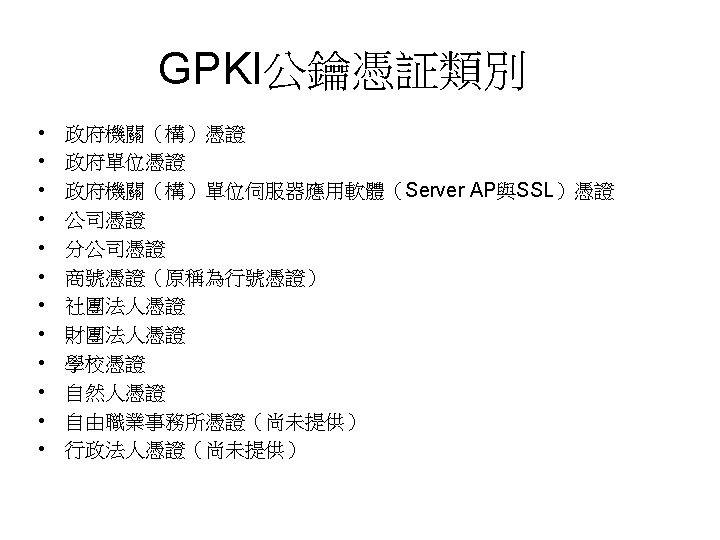
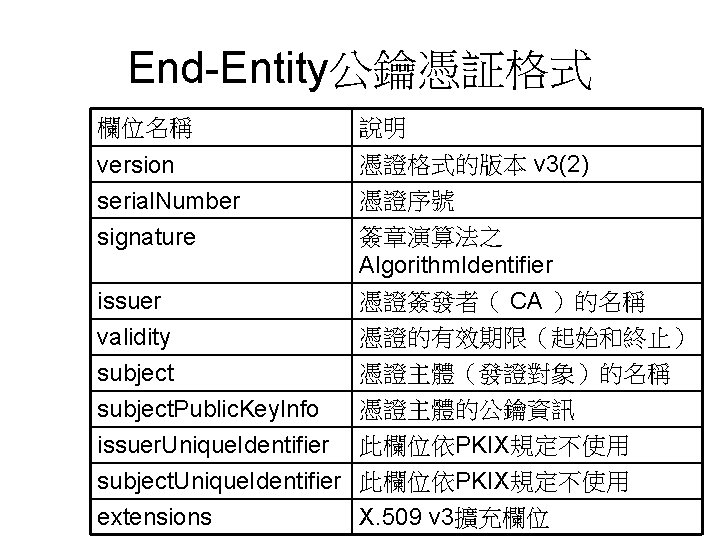
End-Entity公鑰憑証格式 欄位名稱 version serial. Number signature 說明 憑證格式的版本 v 3(2) 憑證序號 簽章演算法之 Algorithm. Identifier 憑證簽發者( CA )的名稱 issuer 憑證的有效期限(起始和終止) validity 憑證主體(發證對象)的名稱 subject 憑證主體的公鑰資訊 subject. Public. Key. Info issuer. Unique. Identifier 此欄位依PKIX規定不使用 subject. Unique. Identifier 此欄位依PKIX規定不使用 X. 509 v 3擴充欄位 extensions
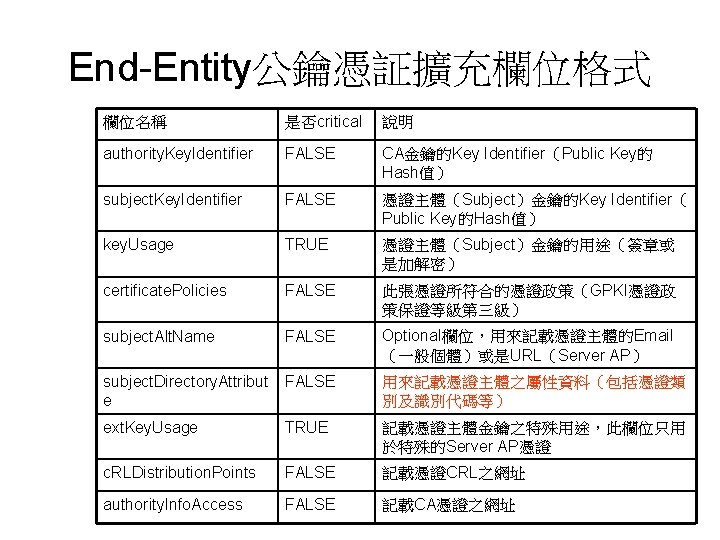
End-Entity公鑰憑証擴充欄位格式 欄位名稱 是否critical 說明 authority. Key. Identifier FALSE CA金鑰的Key Identifier(Public Key的 Hash值) subject. Key. Identifier FALSE 憑證主體(Subject)金鑰的Key Identifier( Public Key的Hash值) key. Usage TRUE 憑證主體(Subject)金鑰的用途(簽章或 是加解密) certificate. Policies FALSE 此張憑證所符合的憑證政策(GPKI憑證政 策保證等級第三級) subject. Alt. Name FALSE Optional欄位,用來記載憑證主體的Email (一般個體)或是URL(Server AP) subject. Directory. Attribut e FALSE 用來記載憑證主體之屬性資料(包括憑證類 別及識別代碼等) ext. Key. Usage TRUE 記載憑證主體金鑰之特殊用途,此欄位只用 於特殊的Server AP憑證 c. RLDistribution. Points FALSE 記載憑證CRL之網址 authority. Info. Access FALSE 記載CA憑證之網址
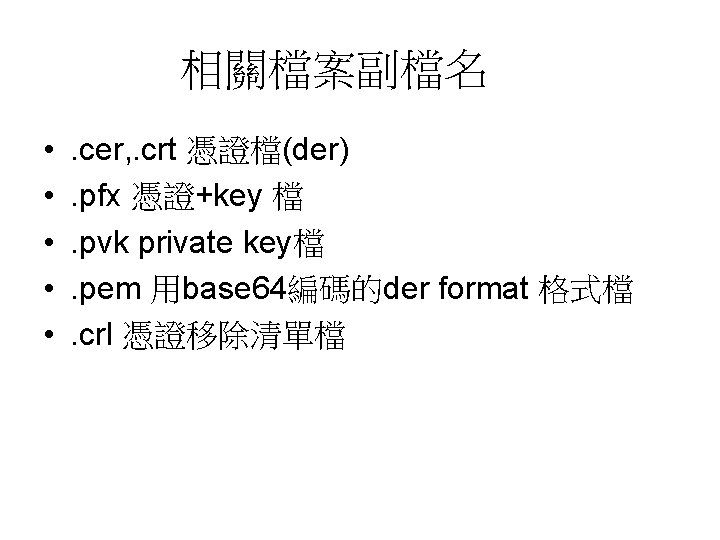
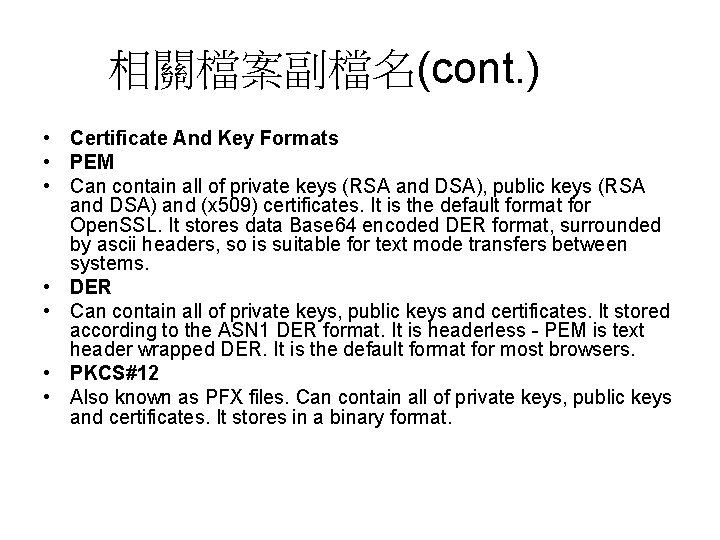
相關檔案副檔名(cont. ) • Certificate And Key Formats • PEM • Can contain all of private keys (RSA and DSA), public keys (RSA and DSA) and (x 509) certificates. It is the default format for Open. SSL. It stores data Base 64 encoded DER format, surrounded by ascii headers, so is suitable for text mode transfers between systems. • DER • Can contain all of private keys, public keys and certificates. It stored according to the ASN 1 DER format. It is headerless - PEM is text header wrapped DER. It is the default format for most browsers. • PKCS#12 • Also known as PFX files. Can contain all of private keys, public keys and certificates. It stores in a binary format.
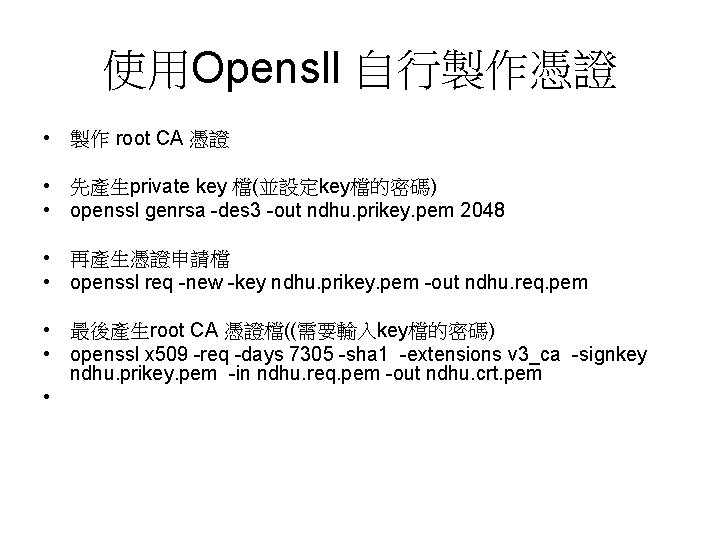
使用Opensll 自行製作憑證 • 製作 root CA 憑證 • 先產生private key 檔(並設定key檔的密碼) • openssl genrsa -des 3 -out ndhu. prikey. pem 2048 • 再產生憑證申請檔 • openssl req -new -key ndhu. prikey. pem -out ndhu. req. pem • 最後產生root CA 憑證檔((需要輸入key檔的密碼) • openssl x 509 -req -days 7305 -sha 1 -extensions v 3_ca -signkey ndhu. prikey. pem -in ndhu. req. pem -out ndhu. crt. pem •
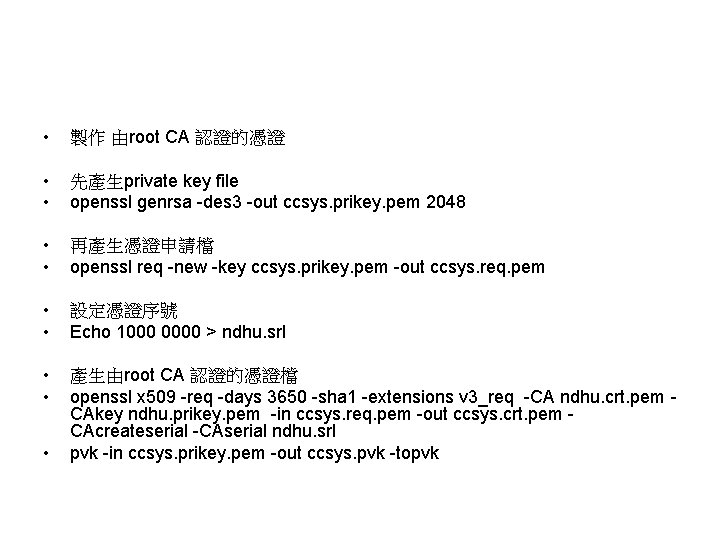
• 製作 由root CA 認證的憑證 • • 先產生private key file openssl genrsa -des 3 -out ccsys. prikey. pem 2048 • • 再產生憑證申請檔 openssl req -new -key ccsys. prikey. pem -out ccsys. req. pem • • 設定憑證序號 Echo 1000 0000 > ndhu. srl • • 產生由root CA 認證的憑證檔 openssl x 509 -req -days 3650 -sha 1 -extensions v 3_req -CA ndhu. crt. pem CAkey ndhu. prikey. pem -in ccsys. req. pem -out ccsys. crt. pem CAcreateserial -CAserial ndhu. srl pvk -in ccsys. prikey. pem -out ccsys. pvk -topvk •
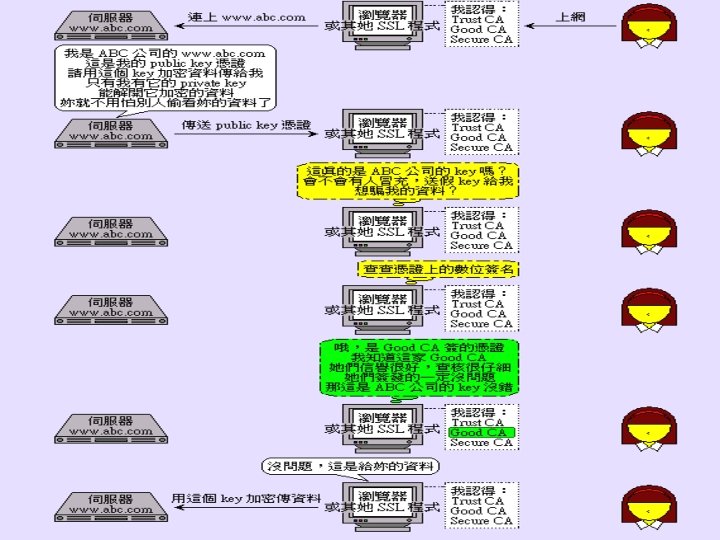
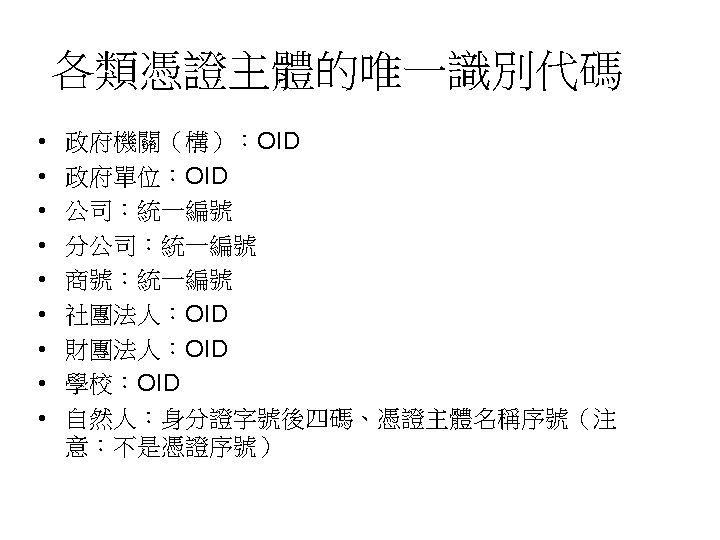
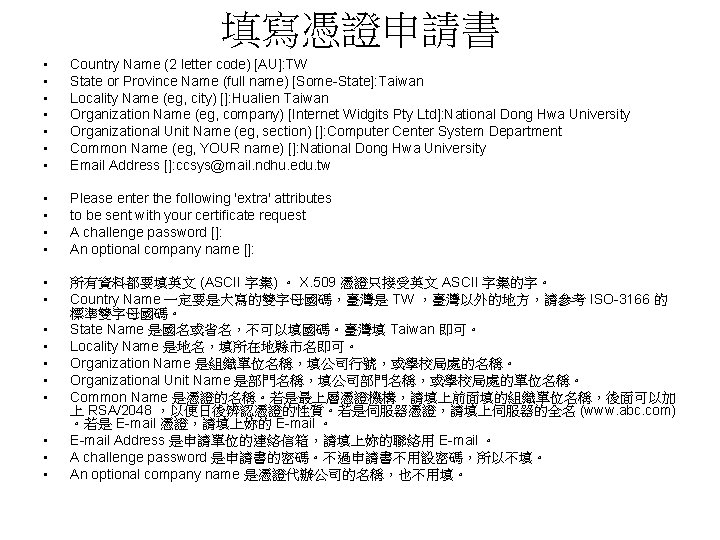
填寫憑證申請書 • • Country Name (2 letter code) [AU]: TW State or Province Name (full name) [Some-State]: Taiwan Locality Name (eg, city) []: Hualien Taiwan Organization Name (eg, company) [Internet Widgits Pty Ltd]: National Dong Hwa University Organizational Unit Name (eg, section) []: Computer Center System Department Common Name (eg, YOUR name) []: National Dong Hwa University Email Address []: ccsys@mail. ndhu. edu. tw • • Please enter the following 'extra' attributes to be sent with your certificate request A challenge password []: An optional company name []: • • 所有資料都要填英文 (ASCII 字集) 。 X. 509 憑證只接受英文 ASCII 字集的字。 Country Name 一定要是大寫的雙字母國碼,臺灣是 TW ,臺灣以外的地方,請參考 ISO-3166 的 標準雙字母國碼。 State Name 是國名或省名,不可以填國碼。臺灣填 Taiwan 即可。 Locality Name 是地名,填所在地縣市名即可。 Organization Name 是組織單位名稱,填公司行號,或學校局處的名稱。 Organizational Unit Name 是部門名稱,填公司部門名稱,或學校局處的單位名稱。 Common Name 是憑證的名稱。若是最上層憑證機構,請填上前面填的組織單位名稱,後面可以加 上 RSA/2048 ,以便日後辨認憑證的性質。若是伺服器憑證,請填上伺服器的全名 (www. abc. com) 。若是 E-mail 憑證,請填上妳的 E-mail 。 E-mail Address 是申請單位的連絡信箱,請填上妳的聯絡用 E-mail 。 A challenge password 是申請書的密碼。不過申請書不用設密碼,所以不填。 An optional company name 是憑證代辦公司的名稱,也不用填。 • •
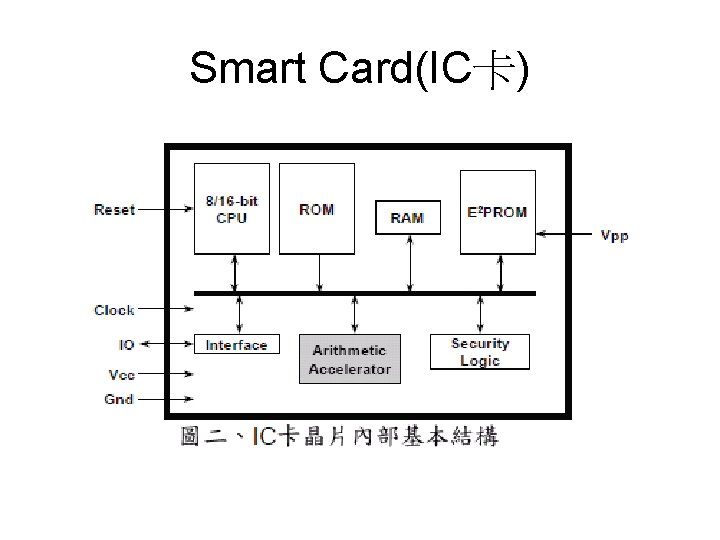
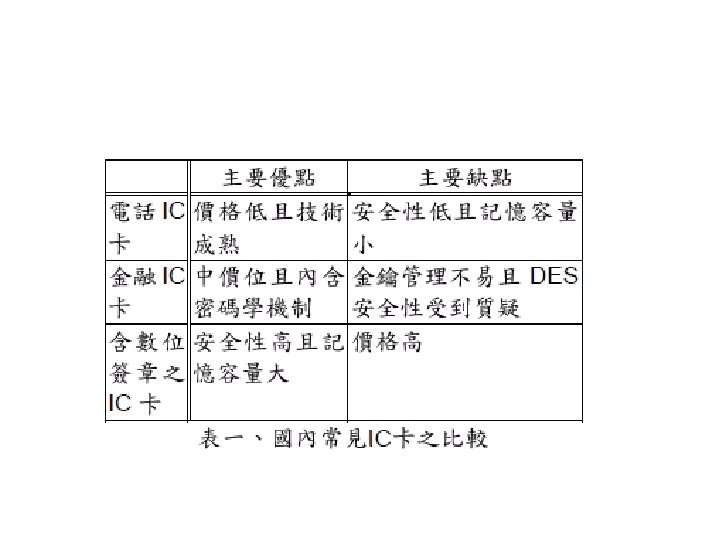
Smart Card(IC卡)
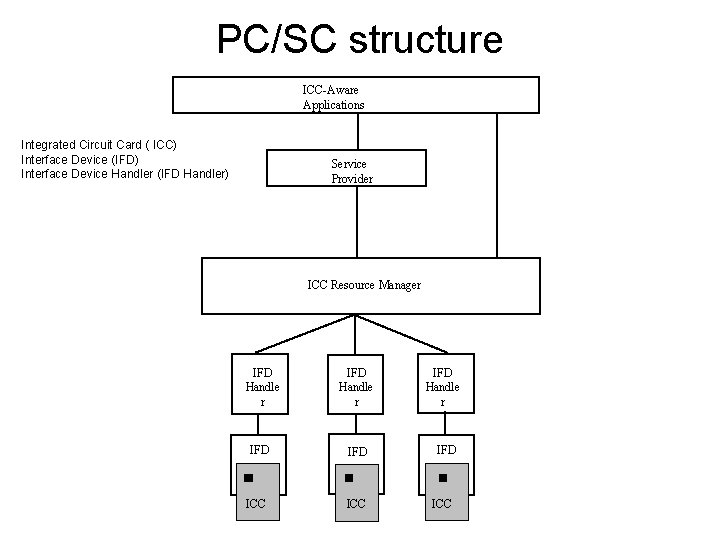
Windows下的使用 • 可用來做為登入電腦的認證 • Winscard. dll 為與IC卡讀卡機動作的函式庫 • 使用 APDU(Application Protocol Data Unit) 指令控制讀卡機運作 • Delphi 下的物件 PCSC component package(http: //www. ppuvas. com. pl)
PC/SC structure ICC-Aware Applications Integrated Circuit Card ( ICC) Interface Device (IFD) Interface Device Handler (IFD Handler) Service Provider ICC Resource Manager IFD Handle r IFD ICC
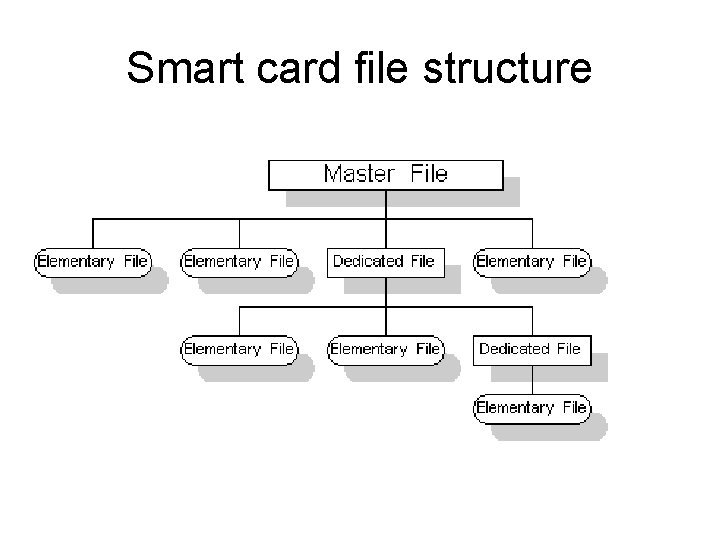
Smart card file structure
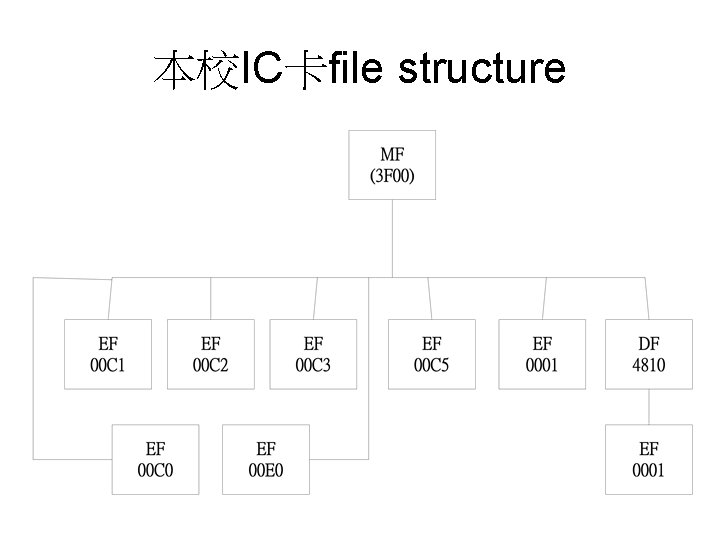
本校IC卡file structure
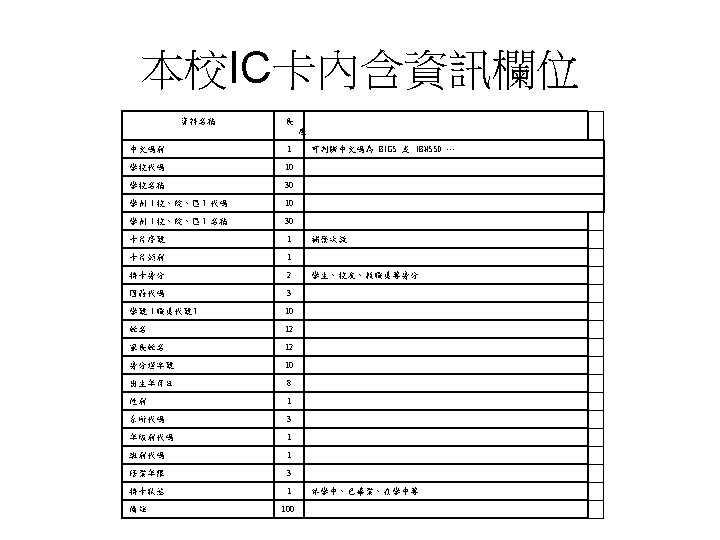
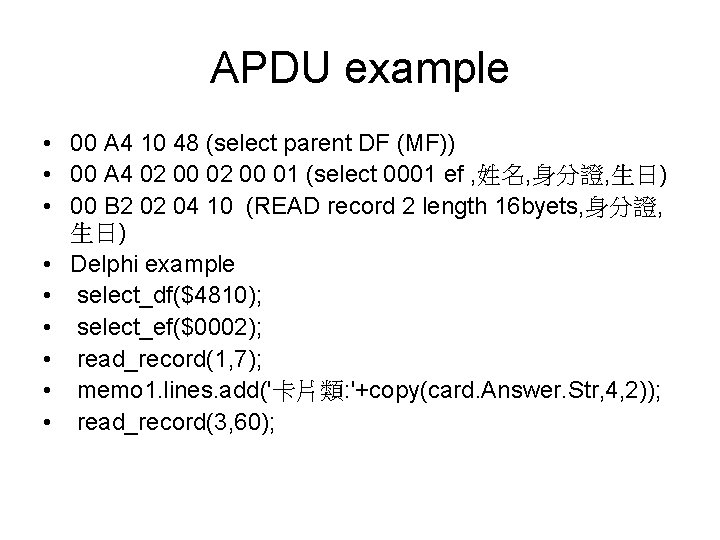
APDU example • 00 A 4 10 48 (select parent DF (MF)) • 00 A 4 02 00 01 (select 0001 ef , 姓名, 身分證, 生日) • 00 B 2 02 04 10 (READ record 2 length 16 byets, 身分證, 生日) • Delphi example • select_df($4810); • select_ef($0002); • read_record(1, 7); • memo 1. lines. add('卡片類: '+copy(card. Answer. Str, 4, 2)); • read_record(3, 60);
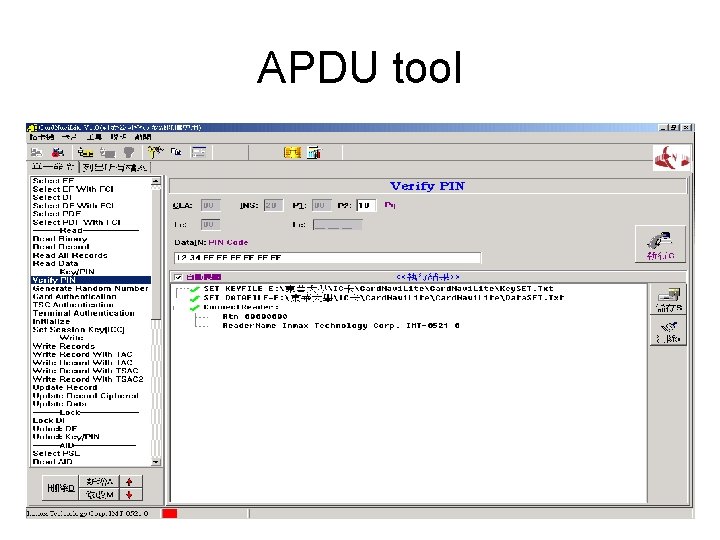
APDU tool