
Environment Application Server Tomcat 4 1 SOAP API
- Slides: 12
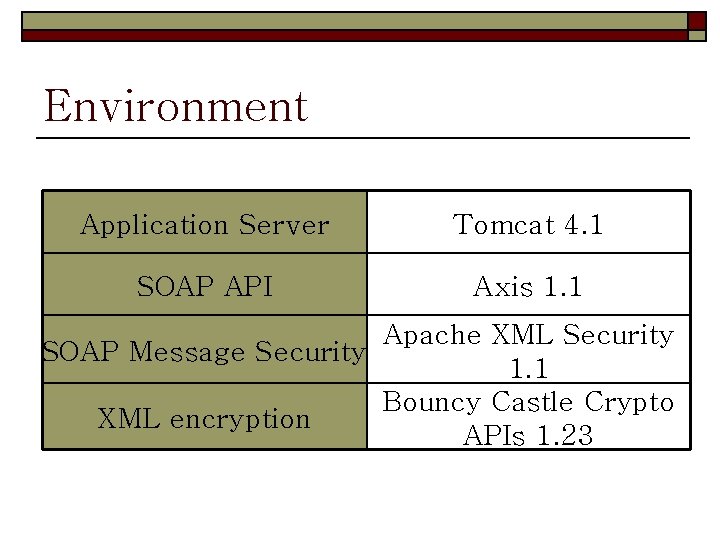
Environment Application Server Tomcat 4. 1 SOAP API Axis 1. 1 Apache XML Security SOAP Message Security 1. 1 Bouncy Castle Crypto XML encryption APIs 1. 23
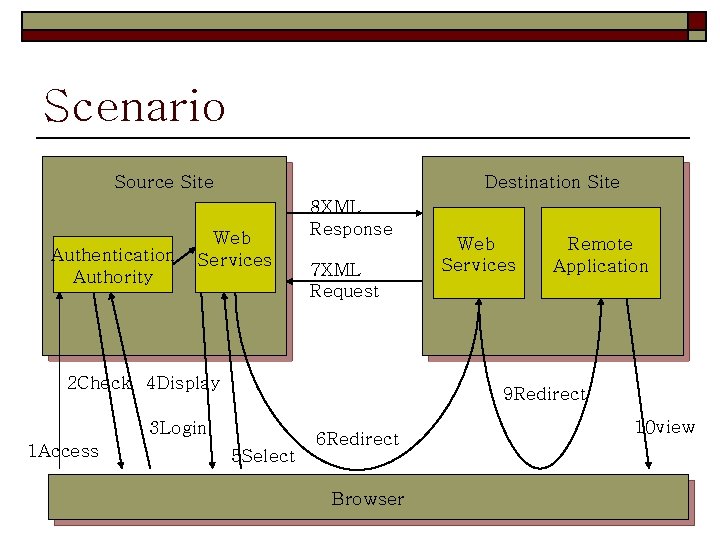
Scenario Destination Site Source Site Authentication Authority Web Services 8 XML Response 7 XML Request 2 Check 4 Display Remote Application 9 Redirect 3 Login 1 Access Web Services 5 Select 6 Redirect Browser 10 view
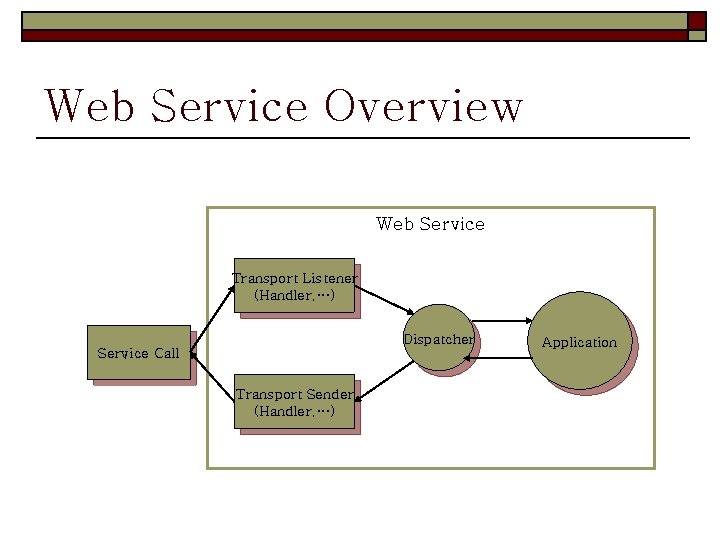
Web Service Overview Web Service Transport Listener (Handler, …) Dispatcher Service Call Transport Sender (Handler, …) Application
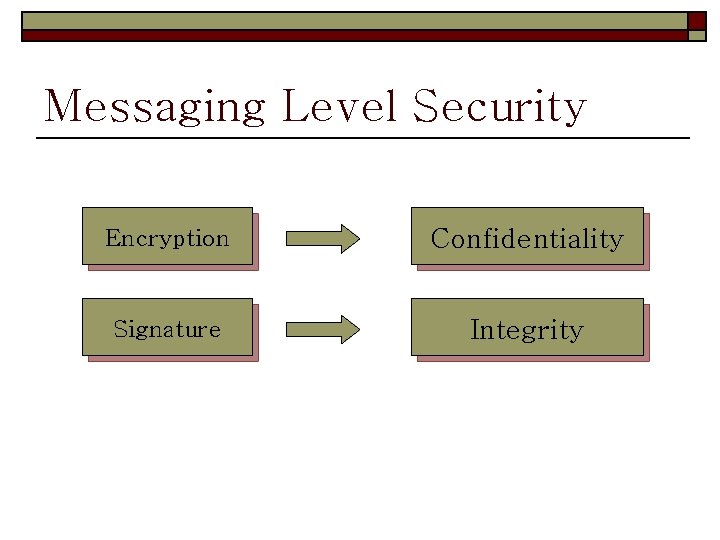
Messaging Level Security Encryption Confidentiality Signature Integrity
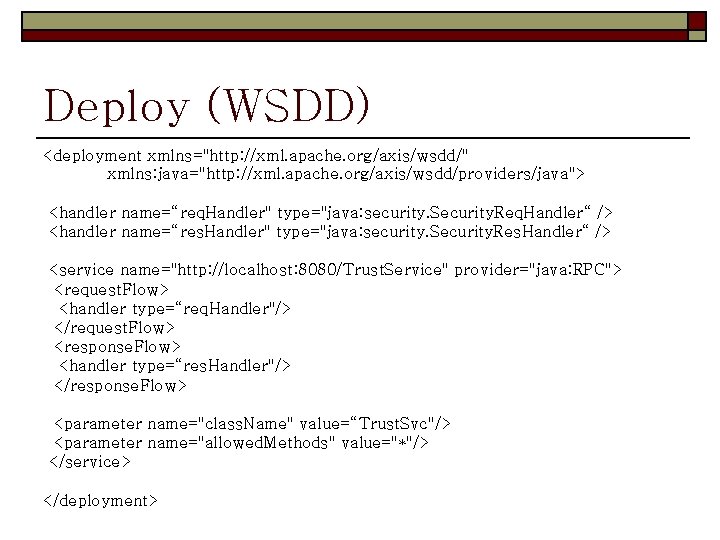
Deploy (WSDD) <deployment xmlns="http: //xml. apache. org/axis/wsdd/" xmlns: java="http: //xml. apache. org/axis/wsdd/providers/java"> <handler name=“req. Handler" type="java: security. Security. Req. Handler“ /> <handler name=“res. Handler" type="java: security. Security. Res. Handler“ /> <service name="http: //localhost: 8080/Trust. Service" provider="java: RPC"> <request. Flow> <handler type=“req. Handler"/> </request. Flow> <response. Flow> <handler type=“res. Handler"/> </response. Flow> <parameter name="class. Name" value=“Trust. Svc"/> <parameter name="allowed. Methods" value="*"/> </service> </deployment>
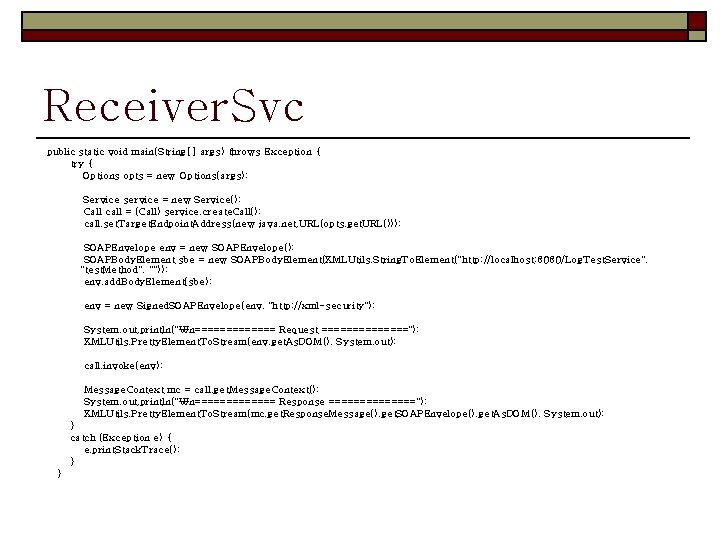
Receiver. Svc public static void main(String[] args) throws Exception { try { Options opts = new Options(args); Service service = new Service(); Call call = (Call) service. create. Call(); call. set. Target. Endpoint. Address(new java. net. URL(opts. get. URL())); SOAPEnvelope env = new SOAPEnvelope(); SOAPBody. Element sbe = new SOAPBody. Element(XMLUtils. String. To. Element("http: //localhost: 8080/Log. Test. Service", "test. Method", "")); env. add. Body. Element(sbe); env = new Signed. SOAPEnvelope(env, "http: //xml-security"); System. out. println("₩n======= Request ======="); XMLUtils. Pretty. Element. To. Stream(env. get. As. DOM(), System. out); call. invoke(env); Message. Context mc = call. get. Message. Context(); System. out. println("₩n======= Response ======="); XMLUtils. Pretty. Element. To. Stream(mc. get. Response. Message(). get. SOAPEnvelope(). get. As. DOM (), System. out); } catch (Exception e) { e. print. Stack. Trace(); } }
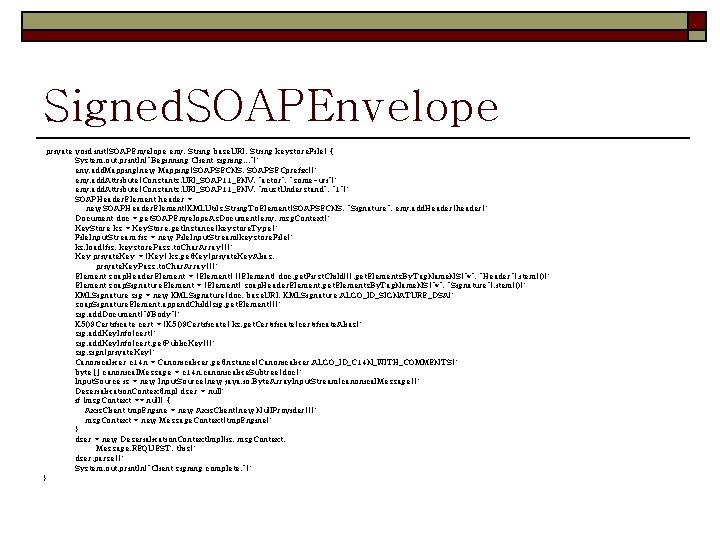
Signed. SOAPEnvelope private void init(SOAPEnvelope env, String base. URI, String keystore. File) { System. out. println("Beginning Client signing. . . "); env. add. Mapping(new Mapping(SOAPSECNS, SOAPSECprefix)); env. add. Attribute(Constants. URI_SOAP 11_ENV, "actor", "some-uri"); env. add. Attribute(Constants. URI_SOAP 11_ENV, "must. Understand", "1"); SOAPHeader. Element header = new SOAPHeader. Element(XMLUtils. String. To. Element(SOAPSECNS, "Signature", env. add. Header(header); Document doc = get. SOAPEnvelope. As. Document(env, msg. Context); Key. Store ks = Key. Store. get. Instance(keystore. Type); File. Input. Stream fis = new File. Input. Stream(keystore. File); ks. load(fis, keystore. Pass. to. Char. Array()); Key private. Key = (Key) ks. get. Key(private. Key. Alias, private. Key. Pass. to. Char. Array()); Element soap. Header. Element = (Element) ((Element) doc. get. First. Child()). get. Elements. By. Tag. Name. NS("*", "Header"). item(0); Element soap. Signature. Element = (Element) soap. Header. Element. get. Elements. By. Tag. Name. NS("*", "Signature"). item(0); XMLSignature sig = new XMLSignature(doc, base. URI, XMLSignature. ALGO_ID_SIGNATURE_DSA); soap. Signature. Element. append. Child(sig. get. Element()); sig. add. Document("#Body"); X 509 Certificate cert = (X 509 Certificate) ks. get. Certificate(certificate. Alias); sig. add. Key. Info(cert. get. Public. Key()); sign(private. Key); Canonicalizer c 14 n = Canonicalizer. get. Instance(Canonicalizer. ALGO_ID_C 14 N_WITH_COMMENTS); byte[] canonical. Message = c 14 n. canonicalize. Subtree(doc); Input. Source is = new Input. Source(new java. io. Byte. Array. Input. Stream(canonical. Message)); Deserialization. Context. Impl dser = null; if (msg. Context == null) { Axis. Client tmp. Engine = new Axis. Client(new Null. Provider()); msg. Context = new Message. Context(tmp. Engine); } dser = new Deserialization. Context. Impl(is, msg. Context, Message. REQUEST, this); dser. parse(); System. out. println("Client signing complete. "); }
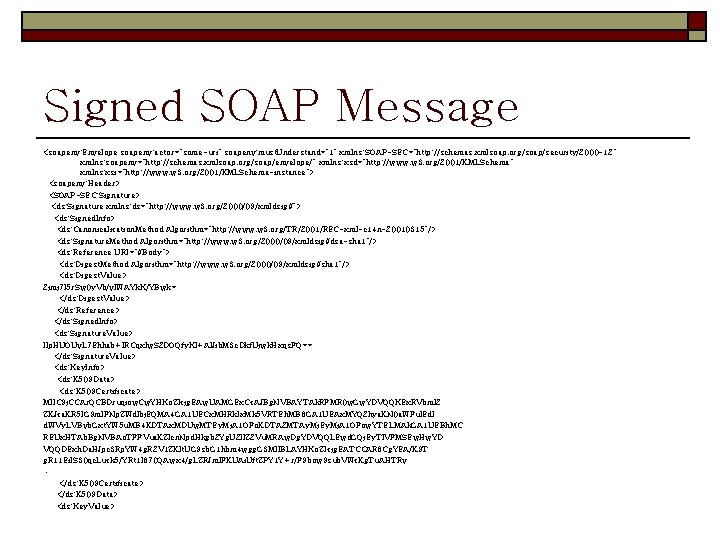
Signed SOAP Message <soapenv: Envelope soapenv: actor="some-uri" soapenv: must. Understand="1" xmlns: SOAP-SEC="http: //schemas. xmlsoap. org/soap/security/2000 -12" xmlns: soapenv="http: //schemas. xmlsoap. org/soap/envelope/" xmlns: xsd="http: //www. w 3. org/2001/XMLSchema" xmlns: xsi="http: //www. w 3. org/2001/XMLSchema-instance"> <soapenv: Header> <SOAP-SEC: Signature> <ds: Signature xmlns: ds="http: //www. w 3. org/2000/09/xmldsig#"> <ds: Signed. Info> <ds: Canonicalization. Method Algorithm="http: //www. w 3. org/TR/2001/REC-xml-c 14 n-20010315"/> <ds: Signature. Method Algorithm="http: //www. w 3. org/2000/09/xmldsig#dsa-sha 1"/> <ds: Reference URI="#Body"> <ds: Digest. Method Algorithm="http: //www. w 3. org/2000/09/xmldsig#sha 1"/> <ds: Digest. Value> 2 jmj 7 l 5 r. Sw 0 y. Vb/vl. WAYk. K/YBwk= </ds: Digest. Value> </ds: Reference> </ds: Signed. Info> <ds: Signature. Value> Ilp. HUOUv. L 7 Ehhab+IRCqxlw. S 2 DOQfy. KI+Al. Jib. M 3 c. Dkf. Ujwk. Hxqs. FQ== </ds: Signature. Value> <ds: Key. Info> <ds: X 509 Data> <ds: X 509 Certificate> MIIC 9 j. CCAr. QCBDruqiow. Cw. YHKo. ZIzjg. EAw. UAMGEx. Cz. AJBg. NVBAYTAk. RFMR 0 w. Gw. YDVQQKEx. RVbml 2 ZXJza. XR 5 IG 9 m. IFNp. ZWdlbj. EQMA 4 GA 1 UECx. MHRk. Ix. Mk 5 VRTEh. MB 8 GA 1 UEAx. MYQ 2 hya. XN 0 a. WFu. IEdl d. WVy. LVBvb. Gxt. YW 5 u. MB 4 XDTAx. MDUw. MTEy. Mj. A 1 OFo. XDTA 2 MTAy. Mj. Ey. Mj. A 1 OFow. YTELMAk. GA 1 UEBh. MC REUx. HTAb. Bg. NVBAo. TFFVua. XZlcn. Npd. Hkgb 2 Yg. U 2 ll. Z 2 Vu. MRAw. Dg. YDVQQLEwd. GQj. Ey. Tl. VFMSEw. Hw. YD VQQDExh. Da. HJpc 3 Rp. YW 4 g. R 2 V 1 ZXIt. UG 9 sb. G 1 hbm 4 wgg. G 3 MIIBLAYHKo. ZIzjg. EATCCAR 8 Cg. YEA/X 9 T g. R 11 Eil. S 30 qc. Luzk 5/YRt 1 I 870 QAwx 4/g. LZRJml. FXUAi. Uft. ZPY 1 Y+r/F 9 bow 9 sub. VWz. Xg. Tu. AHTRv … </ds: X 509 Certificate> </ds: X 509 Data> <ds: Key. Value>
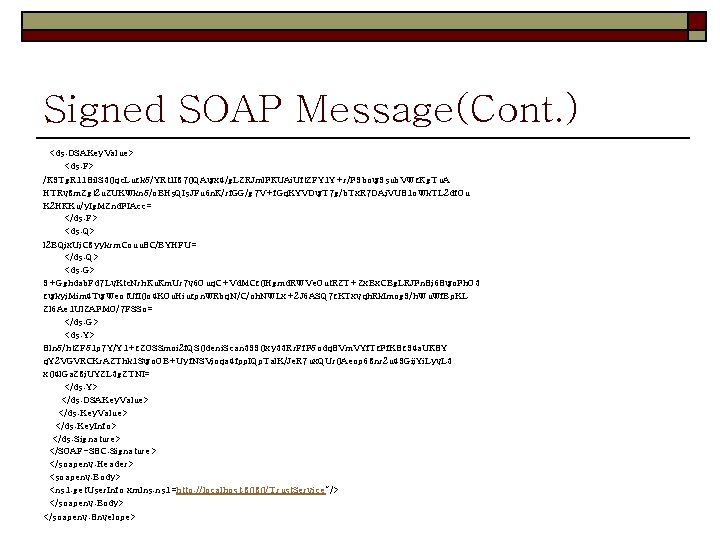
Signed SOAP Message(Cont. ) <ds: DSAKey. Value> <ds: P> /X 9 Tg. R 11 Eil. S 30 qc. Luzk 5/YRt 1 I 870 QAwx 4/g. LZRJml. FXUAi. Uft. ZPY 1 Y+r/F 9 bow 9 sub. VWz. Xg. Tu. A HTRv 8 m. Zgt 2 u. ZUKWkn 5/o. BHs. QIs. JPu 6 n. X/rf. GG/g 7 V+f. Gq. KYVDw. T 7 g/b. Tx. R 7 DAj. VUE 1 o. Wk. TL 2 df. Ou K 2 HXKu/y. Ig. MZnd. FIAcc= </ds: P> <ds: Q> l 2 BQjx. Uj. C 8 yykrm. Couu. EC/BYHPU= </ds: Q> <ds: G> 9+Gghdab. Pd 7 Lv. Ktc. Nrh. Xu. Xm. Ur 7 v 6 Ouq. C+Vd. MCz 0 Hgmd. RWVe. Out. RZT+Zx. Bx. CBg. LRJFn. Ej 6 Ewo. Fh. O 3 zwkyj. Mim 4 Tw. Weot. Uf. I 0 o 4 KOu. Hiuzpn. WRbq. N/C/oh. NWLx+2 J 6 ASQ 7 z. KTxvqh. Rk. Imog 9/h. Wu. Wf. Bp. KL Zl 6 Ae 1 Ul. ZAFMO/7 PSSo= </ds: G> <ds: Y> Eln 5/ht. ZP 51 p 7 Y/Y 1+z. ZOSSmoi 2 f. QS 0 deni. Scan 3990 xy 33 Rr. Pf. F 5 odq. EVm. VYf. Tz. Ff. KEz 94 a. UXEY q. Y 2 VGVRCKr. AZThk 1 Swo. OB+Uyf. NSVjoqa 4 fpp. IQp. Tal. K/Je. R 7 ux. QUr 0 Aeop 68 nr 2 u 49 Gij. Yi. Lyv. L 3 x 04 l. Ga. Z 8 j. UYZL 3 g. ZTNI= </ds: Y> </ds: DSAKey. Value> </ds: Key. Info> </ds: Signature> </SOAP-SEC: Signature> </soapenv: Header> <soapenv: Body> <ns 1: get. User. Info xmlns: ns 1=http: //localhost: 8080/Trust. Service”/> </soapenv: Body> </soapenv: Envelope>
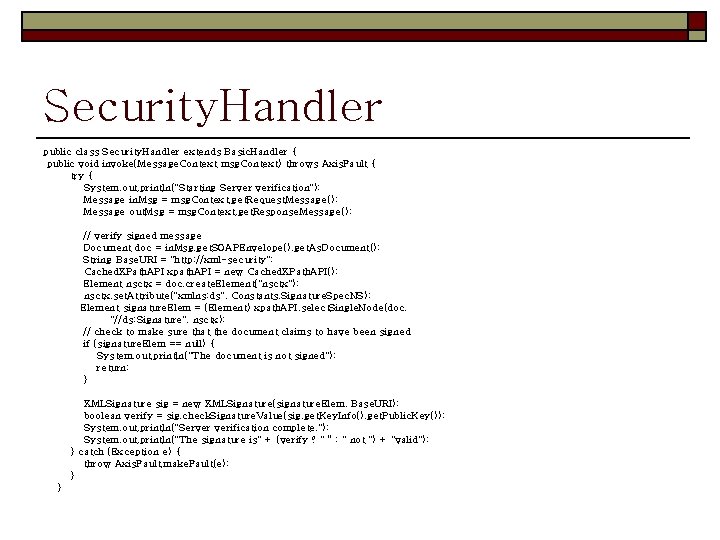
Security. Handler public class Security. Handler extends Basic. Handler { public void invoke(Message. Context msg. Context) throws Axis. Fault { try { System. out. println("Starting Server verification"); Message in. Msg = msg. Context. get. Request. Message(); Message out. Msg = msg. Context. get. Response. Message(); // verify signed message Document doc = in. Msg. get. SOAPEnvelope(). get. As. Document(); String Base. URI = "http: //xml-security"; Cached. XPath. API xpath. API = new Cached. XPath. API(); Element nsctx = doc. create. Element("nsctx"); nsctx. set. Attribute("xmlns: ds", Constants. Signature. Spec. NS); Element signature. Elem = (Element) xpath. API. select. Single. Node(doc, "//ds: Signature", nsctx); // check to make sure that the document claims to have been signed if (signature. Elem == null) { System. out. println("The document is not signed"); return; } XMLSignature sig = new XMLSignature(signature. Elem, Base. URI); boolean verify = sig. check. Signature. Value(sig. get. Key. Info(). get. Public. Key()); System. out. println("Server verification complete. "); System. out. println("The signature is" + (verify ? " “ : " not ") + "valid"); } catch (Exception e) { throw Axis. Fault. make. Fault(e); } }
To do. o o XML Encryption Handler Test JSP, servlet Test & Debug