
ENSDV Enhance Network Scanning for Discovering Vulnerabilities Master
ENSDV Enhance Network Scanning for Discovering Vulnerabilities Master Thesis by Raymond Cordova
Introduction • Emerging Technology • Early-to-market technologies ideal targets for attack • Vulnerabilities with wireless and Internet Protocol • Nessus scanner - de-facto industry scanner • Design and Implementation of an Enhanced Network Scanner • Performance Analysis of ENSDV • Lessons learnt and Future Directions • Conclusion 2/20/2021 ENSDV / Cordova 1
Emerging Technology • NIST 800 -82 Guide to Industrial Control Systems Security (ICS) [11] • Emerging Technology integrates wireless and Internet with ICS infrastructure • Integration introduces all the vulnerabilities and problems of Wireless and the Internet Protocol into ICS [8] [13] • Manual vulnerability discovery impossible 2/20/2021 ENSDV / Cordova 2
Vulnerabilities • Common Vulnerability Exploits (CVE) [2] [12] • Several production meters identified as vulnerable ignored and used in production[7] • $8. 1 billion stimulus to secure the Smart Grid[10] • “everyone rides when the ship comes in” • even TI’s CC 2430 u-controller • Regulation, Management and Guidelines • not too much and not too little 2/20/2021 ENSDV / Cordova 4
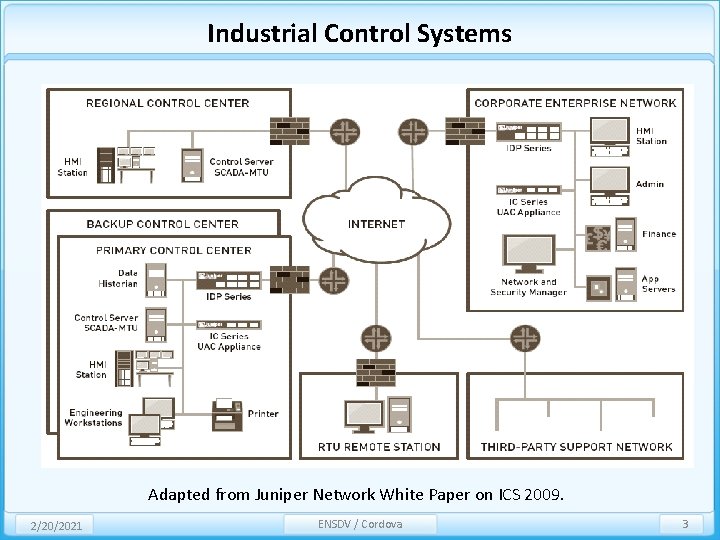
Industrial Control Systems Adapted from Juniper Network White Paper on ICS 2009. 2/20/2021 ENSDV / Cordova 3
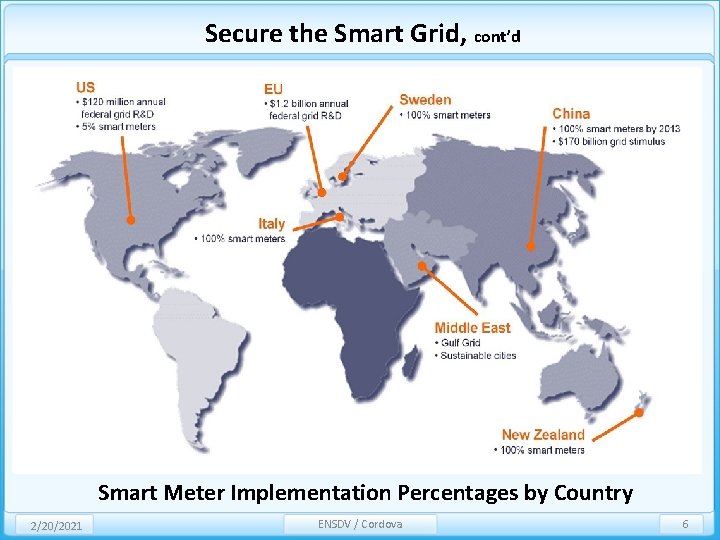
Secure the Smart Grid, cont’d Smart Meter Implementation Percentages by Country 2/20/2021 ENSDV / Cordova 6
Nessus Vulnerability Scanner • Automatic scanning solution approved by NERC CIP for use with SCADA, AMI/AMR [9] • Vulnerability scanning relies on signatures of “known bad things” • Compliance checks compare a system against the “known good” • Flexible, reliable, robust, open source, customizable, automatic, GUI, CLI, option for safe checks/scans and still it is inadequate • Customize plug-ins to enhance operation to resolve inadequacy 2/20/2021 ENSDV / Cordova 7
Prototype – Difficulties Encountered • First attempted to procure meters and collection points • Cost prohibitive, proprietary constraints, minimal support • Inaccessible SCADA systems – focus on Servers/Workstations that control ICS, Smart Grids, LANs, WANs, Enterprise Systems • No Access to Nessus Pro. Feed scanner and SCADA plug-ins • Nessus Attack Script Language (NASL) [3] • new attack language to learn • Full functionality disabled in trial versions of Home. Feed • “buggy” when creating plug-ins 2/20/2021 ENSDV / Cordova 8
Prototype – Difficulties Encountered, cont’d • No Access to Pro. Feed version of the Nessus scanner • SCADA plug-ins • Established correspondence with Renaud Deraison for a full version of Nessus Pro. Feed • some functionality disabled in trial versions of Home. Feed • “buggy” when creating plug-ins • SCADA plug-ins pre-compiled as. nbin binary files • Unreadable unless reverse engineered • Nessus Attack Script Language (NASL) [3] • new attack language to learn • Create VM environment with Fedora 12, and XP un-patched • Create custom 0 -day vulnerability plug-in and audit scripts [6] [7] 2/20/2021 ENSDV / Cordova 9
Nessus Scanner • Centralized automatic scanning tool for a variety of Operating Systems • Vulnerability scanning and Compliance checking • local or remote • Server/Client with GUI or CLI • Knowledgebase • designed with the idea to use results of scripts in other scans • Script Methodology -> write custom script • execute only if necessary • use other script results by use of dependencies • share by saving to KB, upload report results, plug-ins • Plug-in written for and scans for only one vulnerability at a time 2/20/2021 ENSDV / Cordova 10
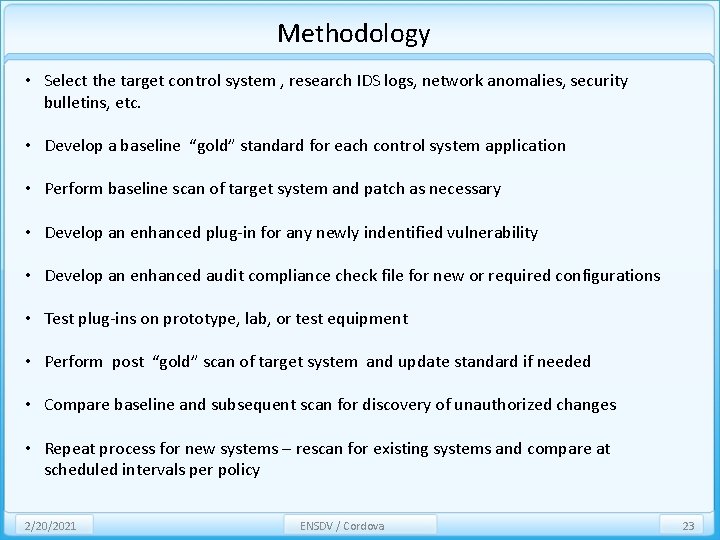
Methodology • Select the target control system , research IDS logs, network anomalies, security bulletins, etc. • Develop a baseline “gold” standard for each control system application • Perform baseline scan of target system and patch as necessary • Develop an enhanced plug-in for any newly indentified vulnerability • Develop an enhanced audit compliance check file for new or required configurations • Test plug-ins on prototype, lab, or test equipment • Perform post “gold” scan of target system and update standard if needed • Compare baseline and subsequent scan for discovery of unauthorized changes • Repeat process for new systems – rescan for existing systems and compare at scheduled intervals per policy 2/20/2021 ENSDV / Cordova 23
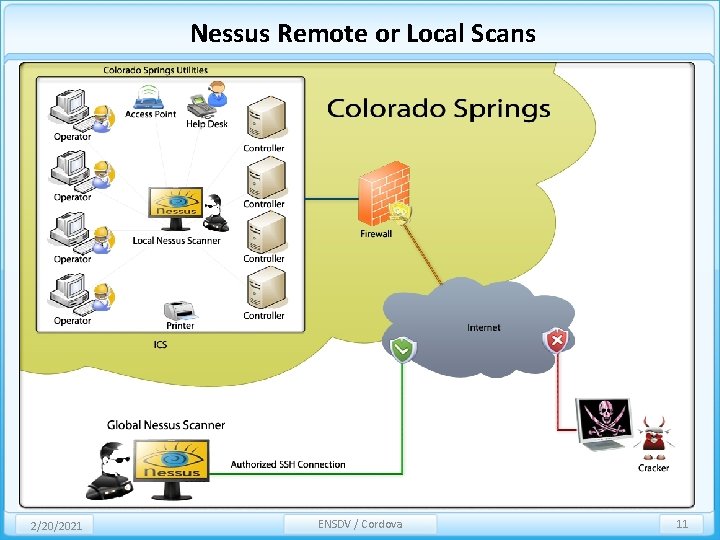
Nessus Remote or Local Scans 2/20/2021 ENSDV / Cordova 11
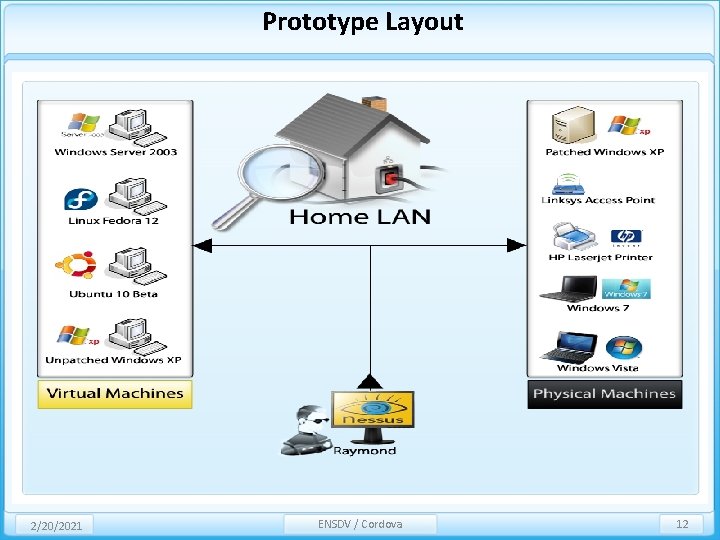
Prototype Layout 2/20/2021 ENSDV / Cordova 12
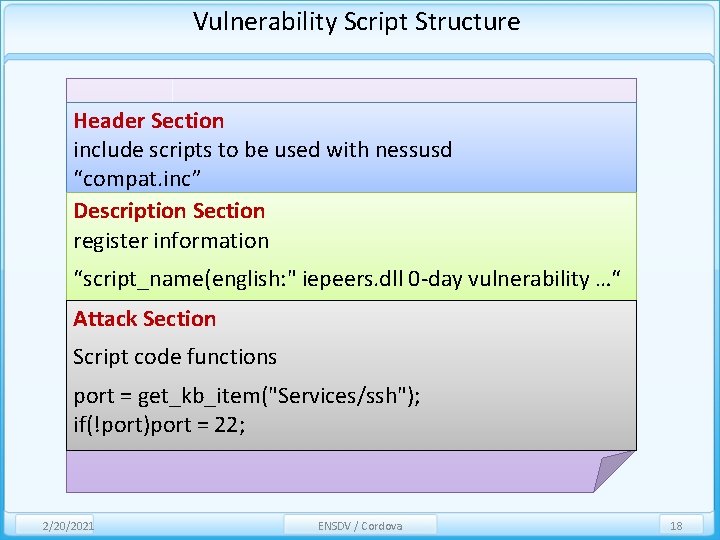
Vulnerability Script Structure Header Section include scripts to be used with nessusd “compat. inc” Description Section register information “script_name(english: " iepeers. dll 0 -day vulnerability …“ Attack Section Script code functions port = get_kb_item("Services/ssh"); if(!port)port = 22; 2/20/2021 ENSDV / Cordova 18
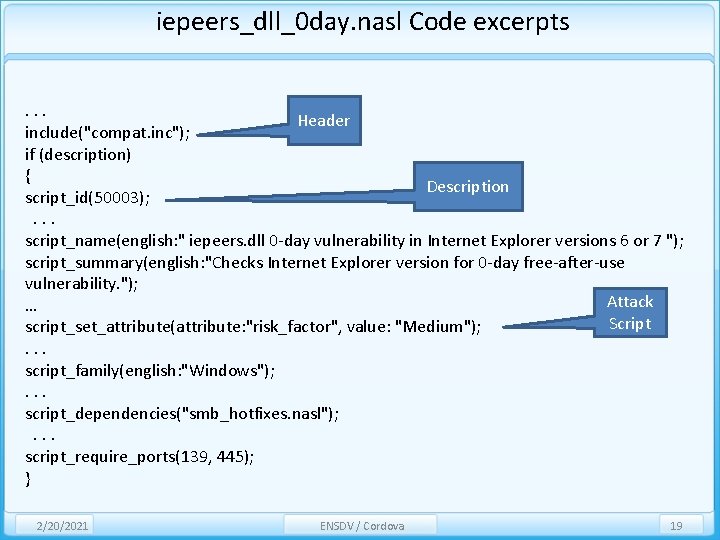
iepeers_dll_0 day. nasl Code excerpts. . . Header include("compat. inc"); if (description) { Description script_id(50003); . . . script_name(english: " iepeers. dll 0 -day vulnerability in Internet Explorer versions 6 or 7 "); script_summary(english: "Checks Internet Explorer version for 0 -day free-after-use vulnerability. "); Attack … Script script_set_attribute(attribute: "risk_factor", value: "Medium"); . . . script_family(english: "Windows"); . . . script_dependencies("smb_hotfixes. nasl"); . . . script_require_ports(139, 445); } 2/20/2021 ENSDV / Cordova 19
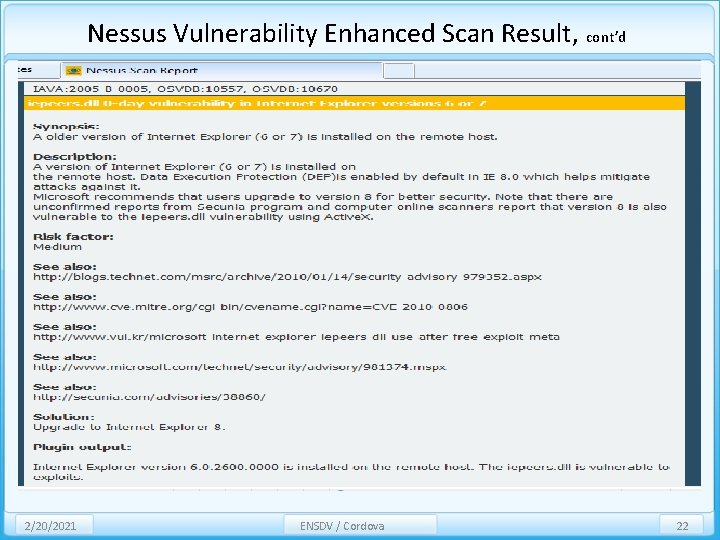
Nessus Vulnerability Enhanced Scan Result, cont’d 2/20/2021 ENSDV / Cordova 22
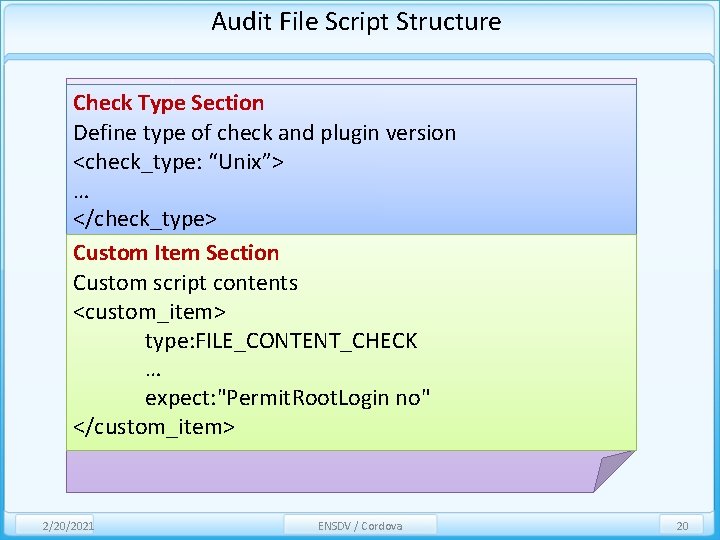
Audit File Script Structure Check Type Section Define type of check and plugin version <check_type: “Unix”> … </check_type> Custom Item Section Custom script contents <custom_item> type: FILE_CONTENT_CHECK … expect: "Permit. Root. Login no" </custom_item> 2/20/2021 ENSDV / Cordova 20
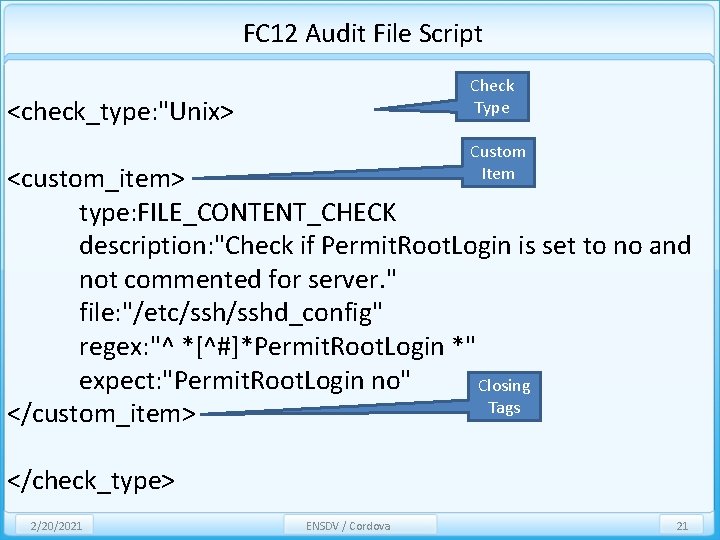
FC 12 Audit File Script Check Type <check_type: "Unix> Custom Item <custom_item> type: FILE_CONTENT_CHECK description: "Check if Permit. Root. Login is set to no and not commented for server. " file: "/etc/sshd_config" regex: "^ *[^#]*Permit. Root. Login *" expect: "Permit. Root. Login no" Closing Tags </custom_item> </check_type> 2/20/2021 ENSDV / Cordova 21
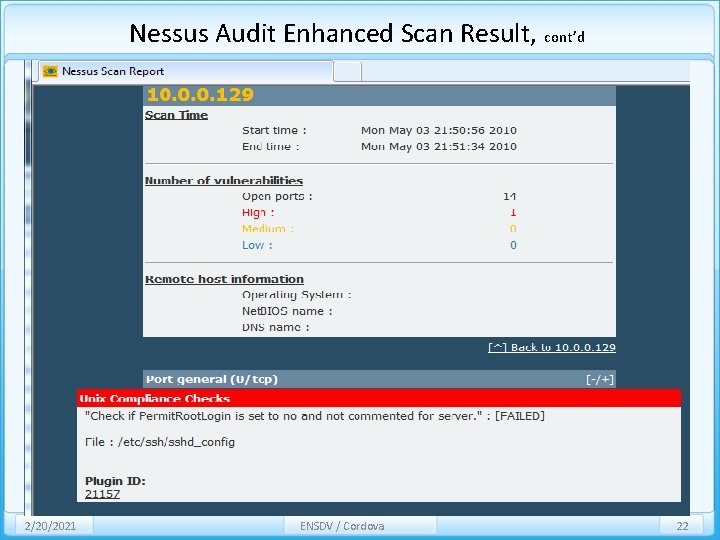
Nessus Audit Enhanced Scan Result, cont’d 2/20/2021 ENSDV / Cordova 22
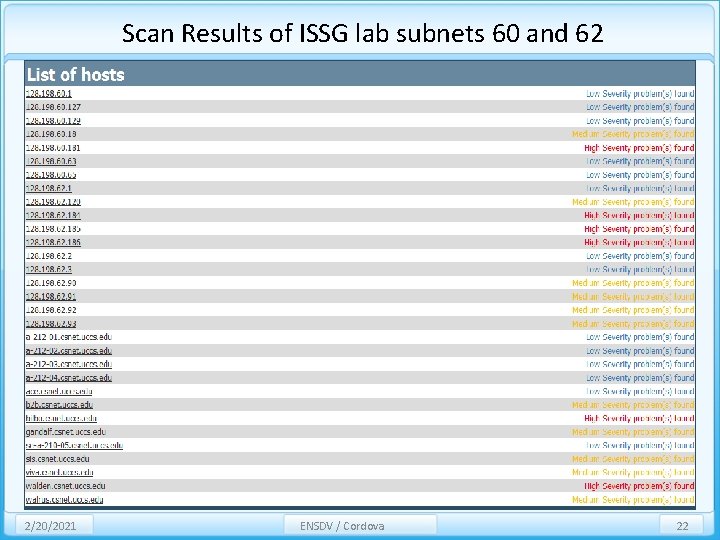
Scan Results of ISSG lab subnets 60 and 62 2/20/2021 ENSDV / Cordova 22
Future Work • Continue meaningful research in the lab setup of MPS 2530 controllers with Nessus • Research compiler and interpreter for. nbin script development for Smart Grid applications • Possible creation of custom plug-ins to check the Zig. Bee stack version for Pseudo Random Number Generator (PRNG) vulnerability • versions 3 and later do not exhibit this vulnerability 2/20/2021 ENSDV / Cordova 25
Conclusion • Emerging Technology presents many opportunities, both good and bad • Methodology to enhance network scanning used to discover vulnerabilities • Nessus Profeed an excellent candidate for an automated enhanced vulnerability and compliance scanning tool solution • NASL language used to “attack” the systems with a scan • Many difficulties encountered, mostly a problem with no access to SCADA systems 2/20/2021 ENSDV / Cordova 24
References [1] Chow, Edward Dr. , Graphic use granted by permission of Dr. Edward Chow at UCCS website http: //cs. uccs. edu/~cs 691/ [2] Common Vulnerabilities and Exposures (CVE) http: //www-arc. com/sara/cve. html [3] Deraison, Renaud, Reference Manual for Nessus Attack Scripting Language, Version 1. 4. 0, Manual at website at http: //www. virtualblueness. net/nasl. html [4] Digital Bond research project with example audit files. http: //www. digitalbond. com/wiki/index. php/Bandolier#Compliance_Check_Examples [5] Guide to Industrial Control Systems (ICS) Security, Supervisory Control and Data Acquisition (SCADA) systems, Distributed Control Systems (DCS), and other control system configurations such as Programmable Logic Controllers (PLC) http: //csrc. nist. gov/publications/drafts/80082/draft_sp 800 -82 -fpd. pdf [6] Information on 0 -day vulnerability discovered in the wild March 2010. http: //www. cve. mitre. org/cgi-bin/cvename. cgi? name=CVE-2010 -0806 [[7] Information on 0 -day vulnerability discovered in the wild March 2010. http: //secunia. com/advisories/cve_reference/CVE-2010 -0806/ [8] Journal of Energy Security, Making a Secure Smart Grid a Reality, Sub-paragraph, Weaknesses in the Smart Grid, p. 3 -7, October 2009. http: //www. ensec. org/index. php? option= com_content&view=article&id= 218: making-a-secure-smart-grid-areality&catid=100: issuecontent&Itemid=352 [9] NERC approval of Nessus Scanner http: //www. nessus. org/solutions/index. php? view=nerc [10]Smart Grid Stimulus Funding Revealed!, p. 3, October 2009. http: //earth 2 tech. com/2009/10/27/smart-grid-stimulus-funding-revealed/ [11] Stouffer, Keith and Falco, Joe and Scarfone, Karen Final Public Draft, Special Publication 800 -82, Recommendations of the National Institute of Standards and Technology, Guide to Industrial Control Systems (ICS) Security http: //csrc. nist. gov/publications/drafts/80082/draft_sp 800 -82 -fpd. pdf [12] Weiss, Joseph, “Current Status of Cyber Security of Control Systems”, Testimony of Joseph M. Weiss Control Systems Cyber Security Expert before the Committee on Commerce, Science, and Transportation U. S. Senate March 19, 2009. 2/20/2021 ENSDV / Cordova 26
Questions ? ? 2/20/2021 ENSDV / Cordova 27
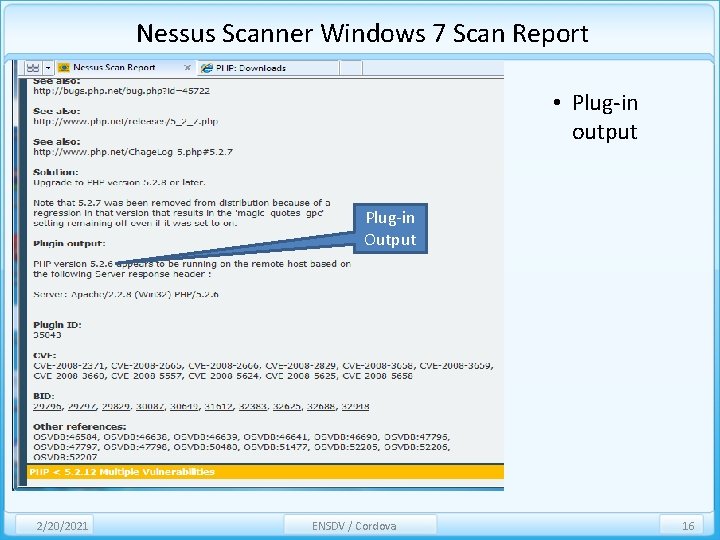
Nessus Scanner Windows 7 Scan Report • Plug-in output Plug-in Output 2/20/2021 ENSDV / Cordova 16
- Slides: 25