
Cybersecurity Threat Systems Management Office TSMO Briefer Mr
Cybersecurity Threat Systems Management Office (TSMO) Briefer: Mr. Brad Thomason Title: Acting Director Date: 25 Jul 2018 E-mail/Phone: bradley. o. thomason. civ@mail. mil/256 -8700 UNCLASSIFIED//FOUO 1
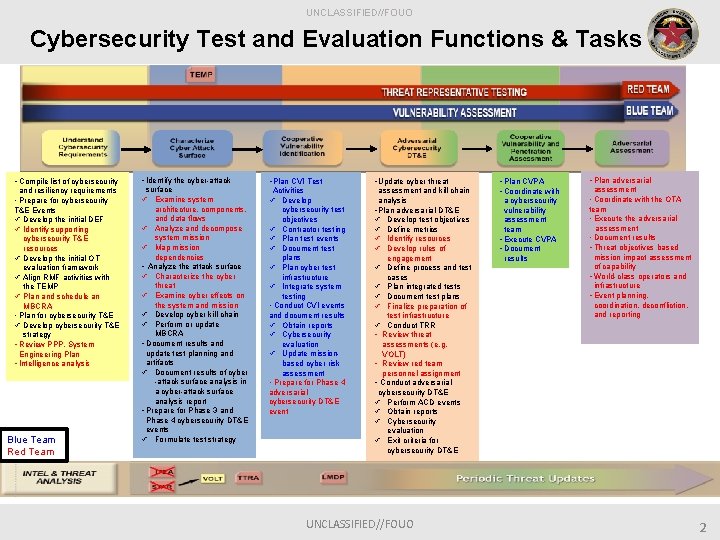
UNCLASSIFIED//FOUO Cybersecurity Test and Evaluation Functions & Tasks • Compile list of cybersecurity and resiliency requirements • Prepare for cybersecurity T&E Events ü Develop the initial DEF ü Identify supporting cybersecurity T&E resources ü Develop the initial OT evaluation framework ü Align RMF activities with the TEMP ü Plan and schedule an MBCRA • Plan for cybersecurity T&E ü Develop cybersecurity T&E strategy • Review PPP, System Engineering Plan • Intelligence analysis Blue Team Red Team • Identify the cyber-attack surface ü Examine system architecture, components, and data flows ü Analyze and decompose system mission ü Map mission dependencies • Analyze the attack surface ü Characterize the cyber threat ü Examine cyber effects on the system and mission ü Develop cyber kill chain ü Perform or update MBCRA • Document results and update test planning and artifacts ü Document results of cyber -attack surface analysis in a cyber-attack surface analysis report • Prepare for Phase 3 and Phase 4 cybersecurity DT&E events ü Formulate test strategy • Plan CVI Test • Update cyber threat Activities ü Develop cybersecurity test objectives ü Contractor testing ü Plan test events ü Document test plans ü Plan cyber test infrastructure ü Integrate system testing • Conduct CVI events and document results ü Obtain reports ü Cybersecurity evaluation ü Update missionbased cyber risk assessment • Prepare for Phase 4 adversarial cybersecurity DT&E event assessment and kill chain analysis • Plan adversarial DT&E ü Develop test objectives ü Define metrics ü Identify resources ü Develop rules of engagement ü Define process and test cases ü Plan integrated tests ü Document test plans ü Finalize preparation of test infrastructure ü Conduct TRR • Review threat assessments (e. g. VOLT) • Review red team personnel assignment • Conduct adversarial cybersecurity DT&E ü Perform ACD events ü Obtain reports ü Cybersecurity evaluation ü Exit criteria for cybersecurity DT&E UNCLASSIFIED//FOUO • Plan CVPA • Coordinate with a cybersecurity vulnerability assessment team • Execute CVPA • Document results • Plan adversarial assessment • Coordinate with the OTA team • Execute the adversarial assessment • Document results • Threat objectives based mission impact assessment of capability • World-class operators and infrastructure • Event planning, coordination, deconfliction, and reporting 2
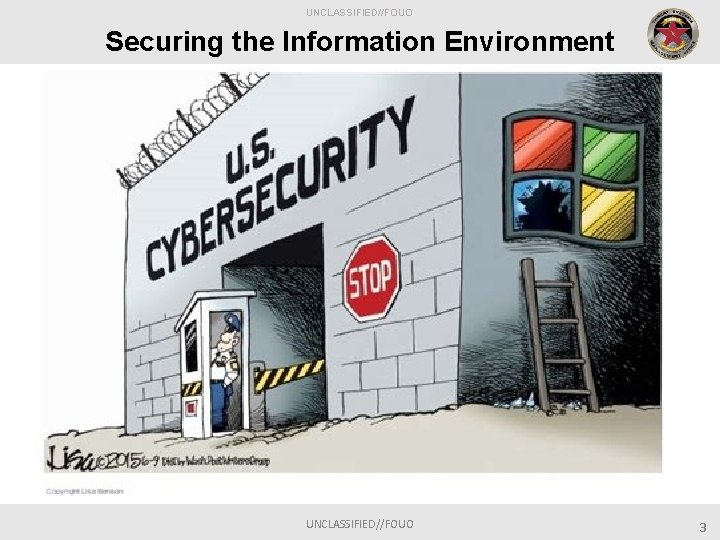
UNCLASSIFIED//FOUO Securing the Information Environment UNCLASSIFIED//FOUO 3
UNCLASSIFIED//FOUO Thoughts on Way Ahead • Expand test philosophy to evaluate information pathways • Compromise of Mission vs Compromise of System − NDAA Section 1647 − Up Front Analysis of Mission • CVPA on Operational Networks • Persistent Red Team UNCLASSIFIED//FOUO 4
UNCLASSIFIED//FOUO Questions UNCLASSIFIED//FOUO 5
- Slides: 5