
CTF Rules Wi Fi SSID Hack In The
- Slides: 4
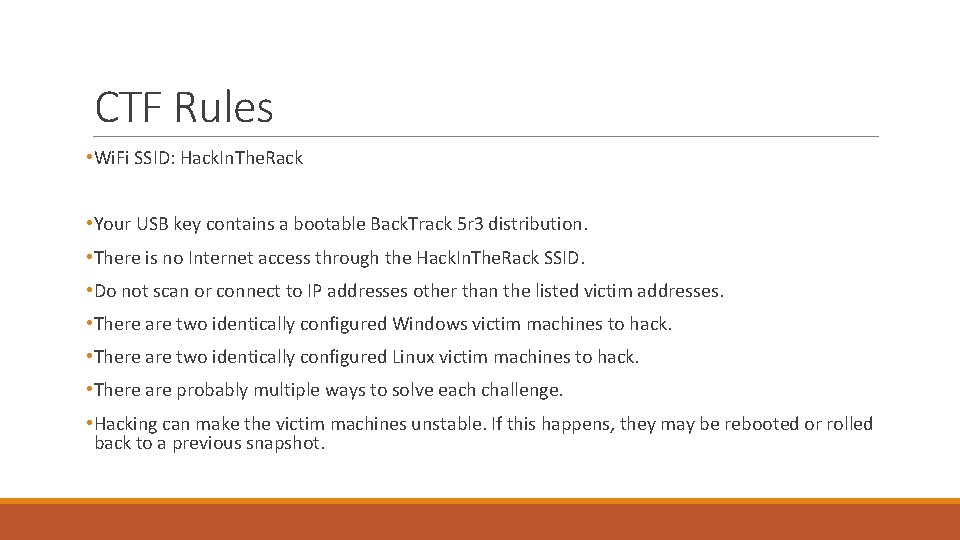
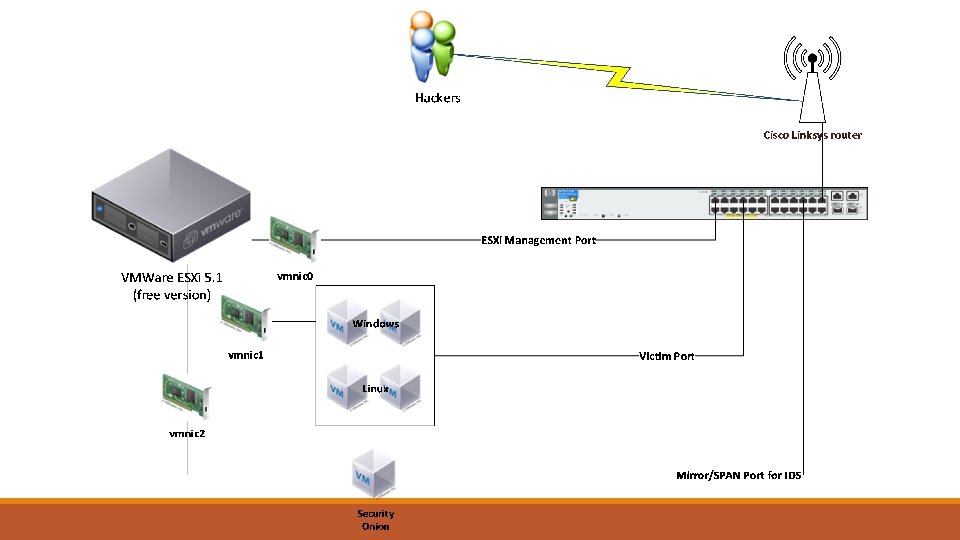
CTF Rules • Wi. Fi SSID: Hack. In. The. Rack • Your USB key contains a bootable Back. Track 5 r 3 distribution. • There is no Internet access through the Hack. In. The. Rack SSID. • Do not scan or connect to IP addresses other than the listed victim addresses. • There are two identically configured Windows victim machines to hack. • There are two identically configured Linux victim machines to hack. • There are probably multiple ways to solve each challenge. • Hacking can make the victim machines unstable. If this happens, they may be rebooted or rolled back to a previous snapshot.
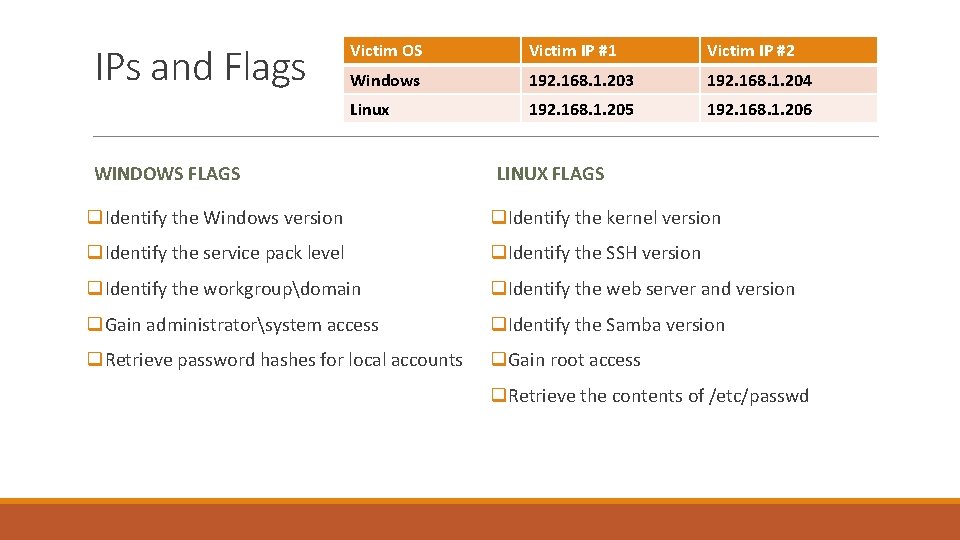
IPs and Flags Victim OS Victim IP #1 Victim IP #2 Windows 192. 168. 1. 203 192. 168. 1. 204 Linux 192. 168. 1. 205 192. 168. 1. 206 WINDOWS FLAGS LINUX FLAGS q. Identify the Windows version q. Identify the kernel version q. Identify the service pack level q. Identify the SSH version q. Identify the workgroupdomain q. Identify the web server and version q. Gain administratorsystem access q. Identify the Samba version q. Retrieve password hashes for local accounts q. Gain root access q. Retrieve the contents of /etc/passwd
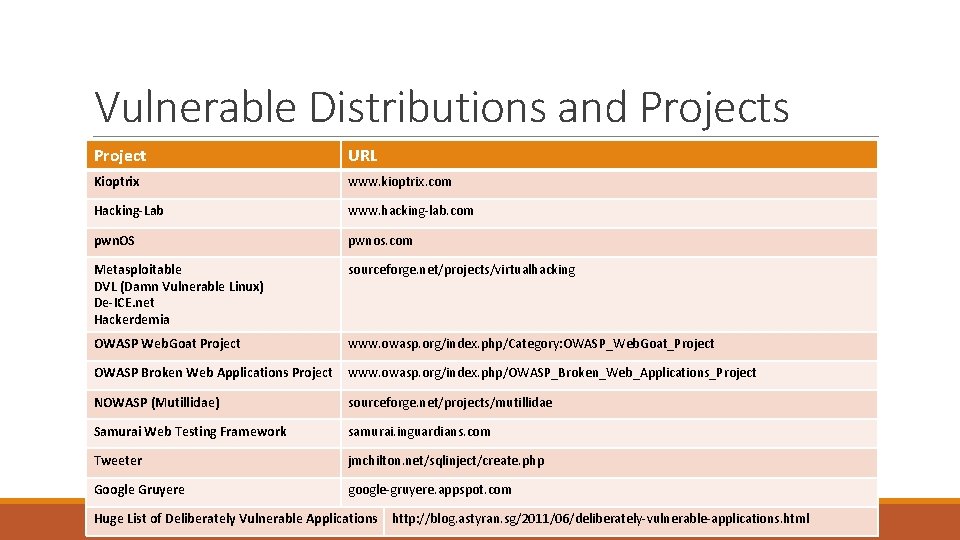
Vulnerable Distributions and Projects Project URL Kioptrix www. kioptrix. com Hacking-Lab www. hacking-lab. com pwn. OS pwnos. com Metasploitable DVL (Damn Vulnerable Linux) De-ICE. net Hackerdemia sourceforge. net/projects/virtualhacking OWASP Web. Goat Project www. owasp. org/index. php/Category: OWASP_Web. Goat_Project OWASP Broken Web Applications Project www. owasp. org/index. php/OWASP_Broken_Web_Applications_Project NOWASP (Mutillidae) sourceforge. net/projects/mutillidae Samurai Web Testing Framework samurai. inguardians. com Tweeter jmchilton. net/sqlinject/create. php Google Gruyere google-gruyere. appspot. com Huge List of Deliberately Vulnerable Applications http: //blog. astyran. sg/2011/06/deliberately-vulnerable-applications. html