
Covering Tracks and Hiding 1 In This Chapter
- Slides: 50
Covering Tracks and Hiding 1
In This Chapter… q Hiding evidence o Altering log files o Hidden files q Practical covert channels Covering Tracks and Hiding 2
Intro q Attacks happen o See zone-h. com q Some attackers want attention q Recently, more stealthy attacks o “Silent” attacks (botnets) o Attacker must hide tracks Covering Tracks and Hiding 3
Altering Event Logs q Even rootkits leave traces in log files q With admin privilege o Attacker could delete log files o Probably a bad idea… q. A better idea: selectively edit logs q How? Covering Tracks and Hiding 4
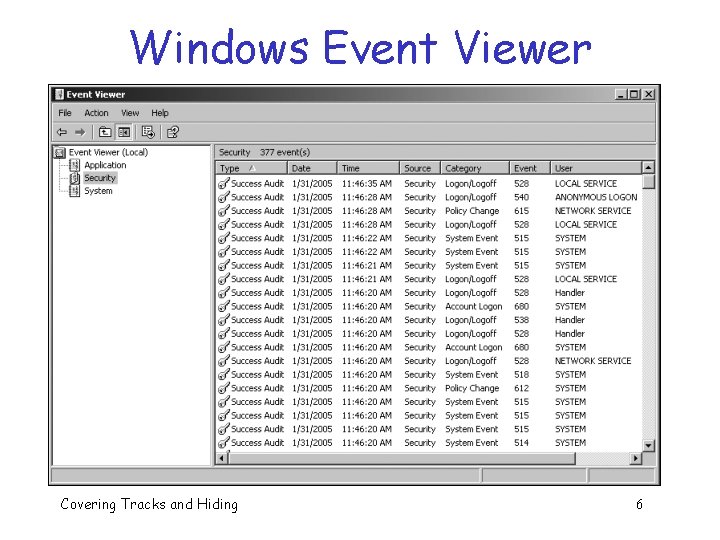
Logs in Windows q Event. Log is logging service o Files ending with. LOG o E. g. , SECURITY, SYSTEM, APPLICATION q This info moved to main event logs o SECEVENT. EVT, SYSEVENT. EVT, … o The. EVT files read by admin using Windows Event Viewer Covering Tracks and Hiding 5
Windows Event Viewer Covering Tracks and Hiding 6
Windows Logs q SECEVENT. EVT o Failed logins, policy changes, attempts to access files without permission, etc. q SYSEVENT. EVT o E. g. , details of driver failure q APPEVENT. EVT o Application-related issues Covering Tracks and Hiding 7
Windows Logs q Altering event logs o At minimum, must change SECEVENTs q EVT files “locked” and binary format o Cannot open/edit with usual tools q With physical access… o …boot to Linux and edit logs o Not practical in most cases Covering Tracks and Hiding 8
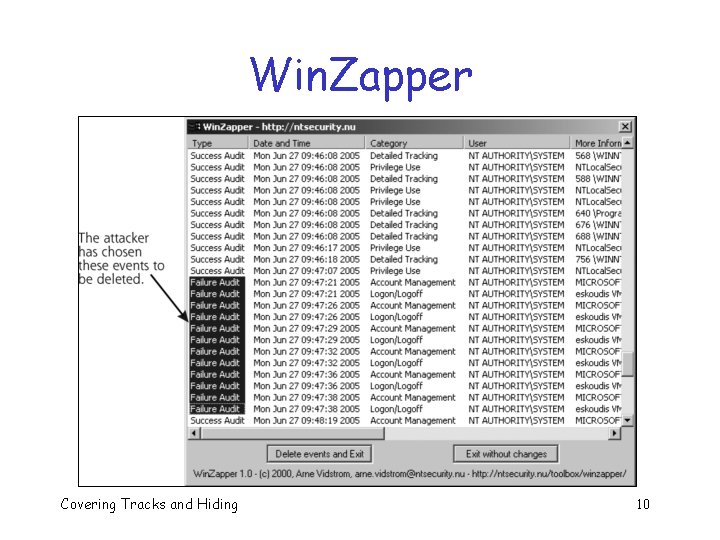
Windows Logs q Event editing tools o None for XP (as of writing) o Do exist for NT/2000 q Win. Zapper o Attacker can selectively edit EVT files o But, must reboot machine to restart Event. Log service Covering Tracks and Hiding 9
Win. Zapper Covering Tracks and Hiding 10
UNIX Logging Log files usually in ASCII text q With privilege, easy to edit q Config file tells where log files located q Attacker can locate files, and edit q Also “accounting files” q o utmp, wtmp, lastlog o Binary files, so harder to edit Covering Tracks and Hiding 11
UNIX Logging q Tools to edit accounting files o Many at www. packetstormsecurity. org o Simple Nomad effect on many versions o Others similar tools: wtemped, marry, cloak, logwedit, wzap, zapper q Accounting file editing tool is standard part of most rootkits Covering Tracks and Hiding 12
Shell History Files List of command line commands issued q Attacker would like to edit this q Files are in ASCII, easy to edit q o Can insert lines too o Why might this be useful? q Edit to shell file written to shell history o When shell is exited gracefully o How to get around this? Covering Tracks and Hiding 13
Defenses q Activate logging o Log according to some specified policy Periodically audit logging q Allow plenty of space for logs q Restrictive permissions on log files q Use separate server for logging q o Logs redirected to logging server o Not everything can be redirected Covering Tracks and Hiding 14
Defenses q Encrypt log files q Make log files append-only o Little more than a “speed bump” q Store logs on unalterable media o E. g. , non-rewritable CD/DVD Covering Tracks and Hiding 15
Hidden Files q Why would attacker use hidden files? o Store attack tools o Save sniffed passwords, etc. q What does “hidden” mean? o Maybe just hard to find o Or easily overlooked Covering Tracks and Hiding 16
Hidden Files q In UNIX, prepend “. ” to filename q Use “. ” followed by space(s) o What the … ? q Other ideas? Covering Tracks and Hiding 17
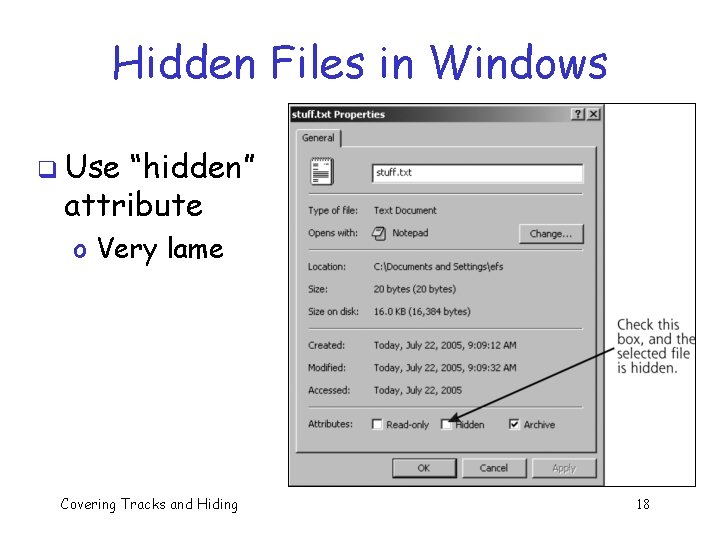
Hidden Files in Windows q Use “hidden” attribute o Very lame Covering Tracks and Hiding 18
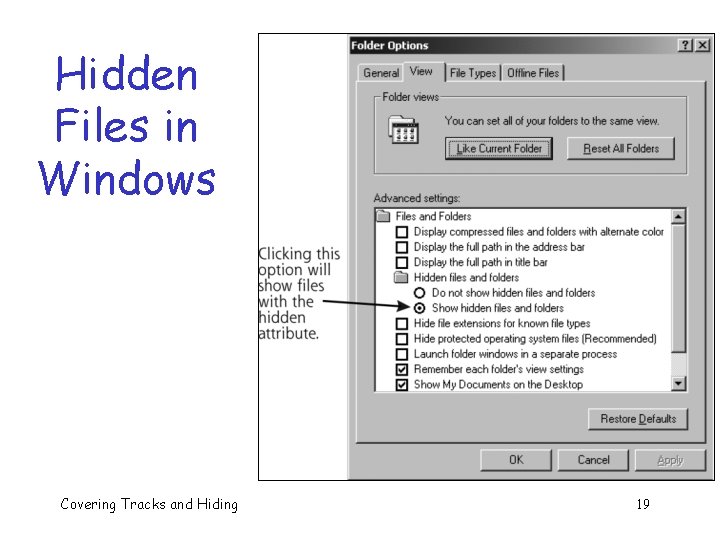
Hidden Files in Windows Covering Tracks and Hiding 19
Hidden Files in Windows q Alternate Data Streams (ADS) o Available in NTFS o Multiple streams of data can be associated with a single file o These streams can store any info o “Usual” view is just one such stream o Fairly effective means of hiding files Covering Tracks and Hiding 20
Defenses q File integrity checking q Host-based IDS q In Windows, use ADS-aware tools o Crucial. ADS, LADS, for example Covering Tracks and Hiding 21
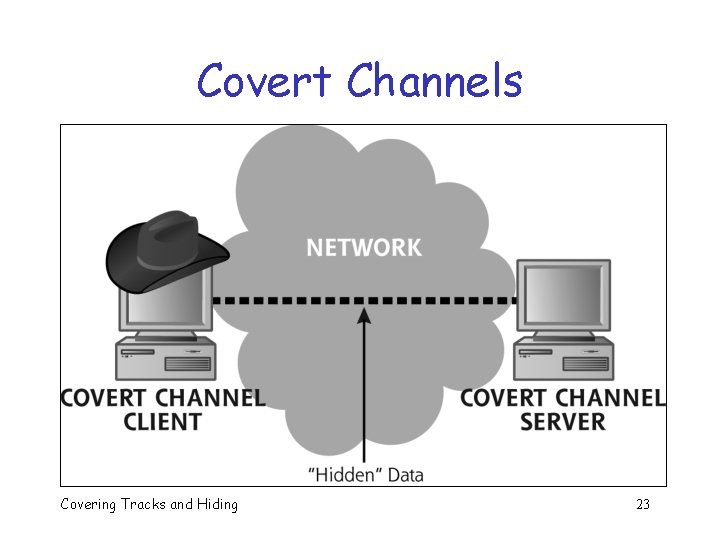
Covert Channels q Suppose attacker has… o Gotten access o Installed evil code/tools o Covered their tracks, etc. q Attacker still needs to communicate o How to do this without detection? q Covert channel o “communication path not intended as such by system’s designers” Covering Tracks and Hiding 22
Covert Channels Covering Tracks and Hiding 23
Covert Channels q In networked systems… o Covert channels are everywhere! q When does a covert channel exist? 1. Sender and receiver have a shared resource 2. Sender able to vary property of resource that receiver can observe 3. Communication between sender and receiver can be synchronized Covering Tracks and Hiding 24
Covert Channels Examples of covert channels? q How to eliminate covert channels? q o Easy: eliminate all communication and shared resources o Do. D gave up on eliminating covert channels o Instead, try to reduce the capacity o Does this solve the problem? o Does it help? Covering Tracks and Hiding 25
Tunneling q Q: What is tunneling? q A: One protocol carries another o E. g. , SSH used to carry Telnet o E. g. , TCP/CP (RFC 1149 and RFC 2549) q Tunneling used for covert channel o We look at Loki, Reverse WWW Shell Covering Tracks and Hiding 26
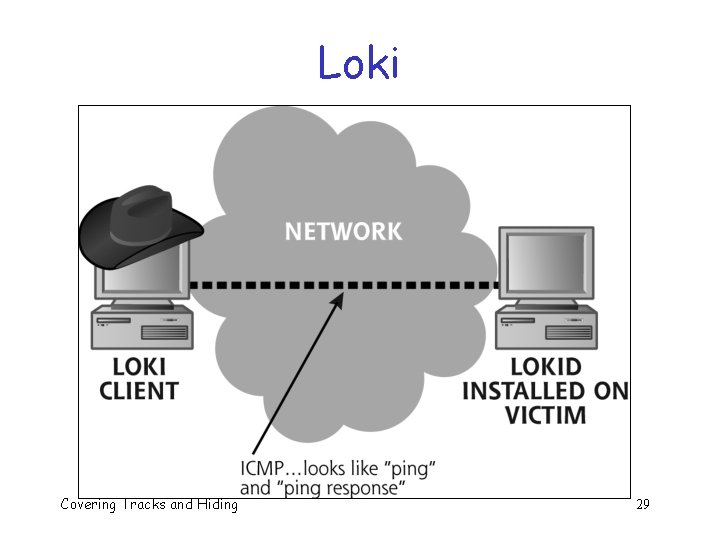
Loki q Suppose o Attacker 0 wns server o Server network allows incoming ICMP (ping/traceroute) q Loki pronounced “low key” o Provides shell access over ICMP o “Better” than TCP/UDP backdoors Covering Tracks and Hiding 27
Loki q Trudy installs Loki server on server o Lokid (“low key dee”) o Must run as root o Grabs incoming ICMP packets from kernel q Trudy installs Loki client on her machine o Data sent to Lokid using ICMP o Under radar of most backdoor detection (Why? ) o ICMP has no concept of a port Covering Tracks and Hiding 28
Loki Covering Tracks and Hiding 29
Loki q Optionally, uses UDP port 53 o Switch between ICMP/UDP on the fly q Supports encryption o Using Blowfish encryption o Diffie-Hellman key exchange q Other similar tools o CCTT and MSNShell Covering Tracks and Hiding 30
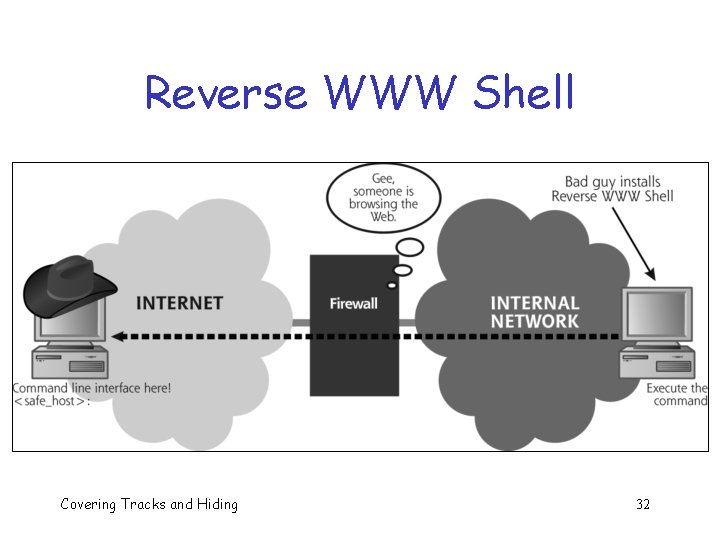
Reverse WWW Shell q Covert channel using HTTP q Reverse WWW Shell installed on machine on network o o Every 60 seconds, it “phones home” I. e, . contacts external master server The “reverse” part: it pulls in commands Looks like normal Web traffic Covering Tracks and Hiding 31
Reverse WWW Shell Covering Tracks and Hiding 32
Reverse WWW Shell q Sometimes username/pwd required to access Web o If known, Reverse WWW Shell can automate Note that other protocols could be used q Reverse WWW Shell idea used by some legitimate software q o E. g. , remote GUI access to machine o See Go. To. My. PC. com Covering Tracks and Hiding 33
Covert Channels and Malware q Consider spyware to steal passwords q How to exfiltrate passwords? o Piggyback on legitimate outbound traffic o In Windows, IE is a natural choice o HTTP/HTTPS q Malware often designed as a Browser Helper Object (BHO) for IE Covering Tracks and Hiding 34
Headers as Covert Channels q Lots of room for covert channels o E. g. , unused bits o But possible to be more clever q Tools o Covert_TCP o Nushu Covering Tracks and Hiding 35
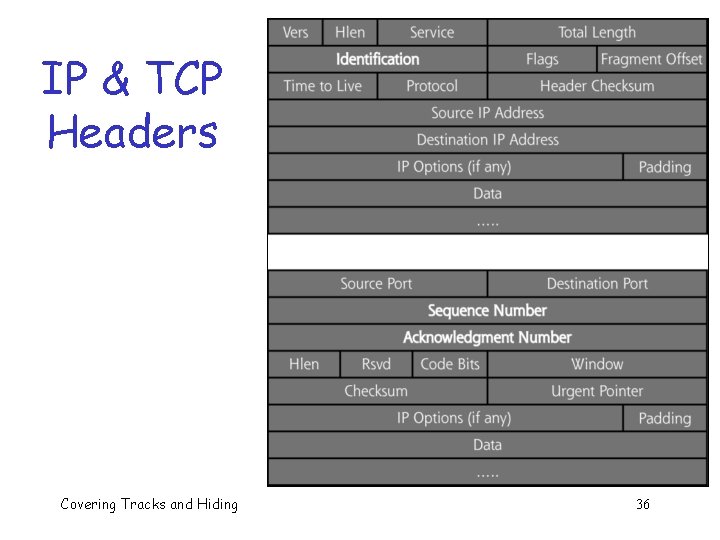
IP & TCP Headers Covering Tracks and Hiding 36
Covert_TCP q Covert_TCP can make use of o IP identification o TCP sequence number o TCP ACK number q Lots of other possible covert channels o Only 3 above used by Covert_TCP q NAT or proxy will cause problems o But IP ID may still work thru NAT Covering Tracks and Hiding 37
Covert_TCP q IP identification o Insert one ASCII character o Read it at other end q TCP sequence number o Send SYN with ASCII character as initial sequence number o Reply with RESET o Ironically, RESET acts as ACK Covering Tracks and Hiding 38
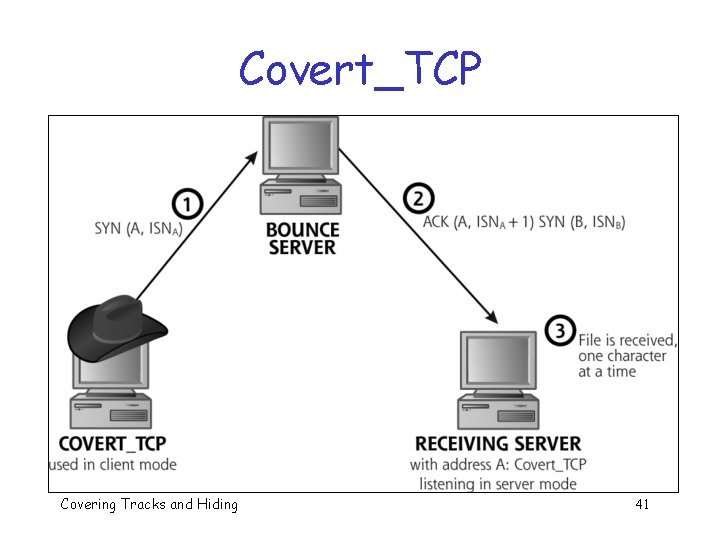
Covert_TCP q TCP ACK number o Most sophisticated option o Involves server (sender), client (receiver), and unwitting “bounce server” o Data “bounces” off bounce server Covering Tracks and Hiding 39
Covert_TCP ACK number q Client send SYN packet to bounce server q o Source address spoofed to client’s address o ISN is one less than desired ASCII character q Bounce server responds to client o Either SYN ACK or RESET o Either way, ISN incremented by 1 q Server recovers ASCII character (ISN) Covering Tracks and Hiding 40
Covert_TCP Covering Tracks and Hiding 41
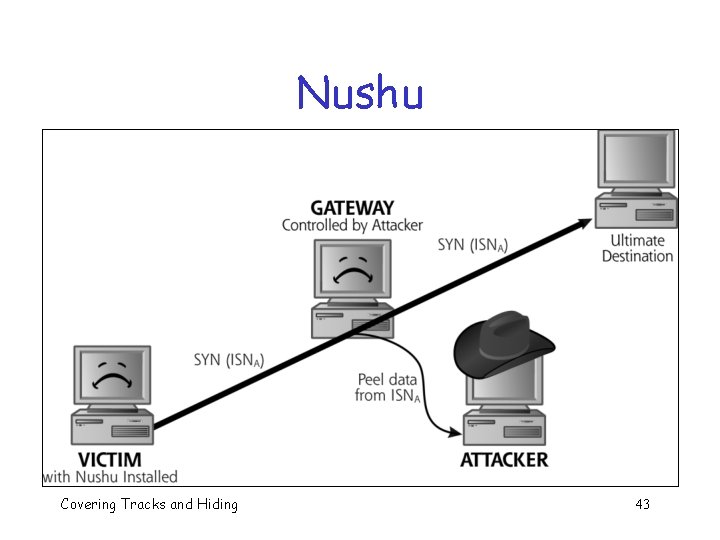
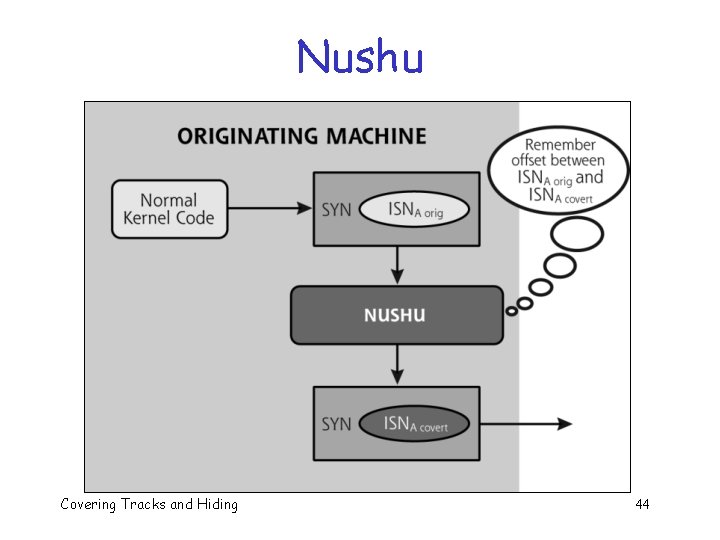
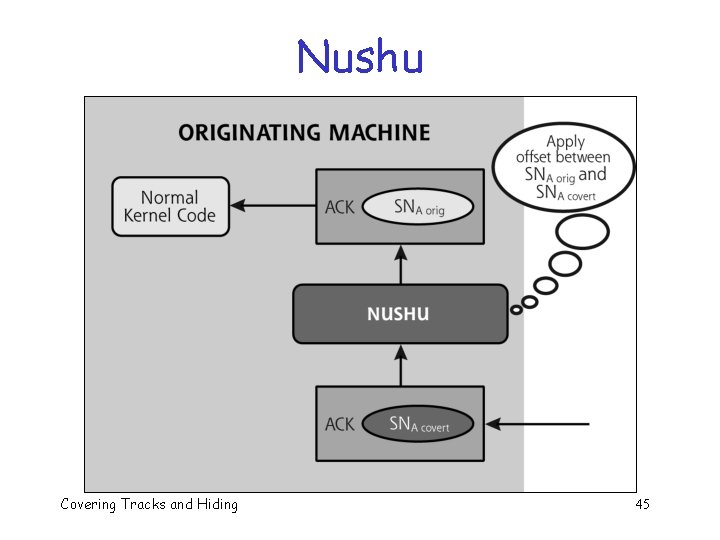
Nushu q Uses a “passive” covert channel o Data sent from host to gateway Embeds info in other (real) packets q Alters ISN to contain data q Assumes attacker also controls gateway q o At gateway, read data from ISN and forward it q How much data can be transferred? Covering Tracks and Hiding 42
Nushu Covering Tracks and Hiding 43
Nushu Covering Tracks and Hiding 44
Nushu Covering Tracks and Hiding 45
Nushu q Implemented as Linux kernel module q Creates “issue” with seq numbers q Spse the good guys o …sniff packets on host o …and same packets elsewhere on LAN o What anomaly will they see? Covering Tracks and Hiding 46
Defenses q No effective defense against covert channels once attacker has access q So, keep attackers out o o Secure configuration Apply patches Antivirus Monitor for BHOs in IE Covering Tracks and Hiding 47
Defenses q Know what is normal o Good luck! q Network-based IDS o Commercial: Sourcefire Intrusion Sensors, ISS Real. Secure, Cisco Secure IDS, Network Flight Recorder o Freeware: Snort Covering Tracks and Hiding 48
Conclusions Covering Tracks and Hiding 49
Summary Covering Tracks and Hiding 50