
CDMA 20001 x EVDO RADIUS Overview Module Objetives
CDMA 2000/1 x. EVDO RADIUS Overview
Module Objetives · Understand the architecture for CDMA 2000 EVDO · Understand the RADIUS protocol to support CDMA 2000 EVDO 2 All Rights Reserved © Alcatel-Lucent 2007
CDMA 2000/1 x. EVDO · It is the packet data access used for CDMA 2000 and 1 x. EVDO § The standards are proposed by 3 GPP 2 · Two main access types: § Simple IP service – to connect to the visited network (when roaming) and Internet, either with IPv 4 or IPv 6 and NO mobility beyond base stations (RN) belonging to the same Provider Network § Mobile IP service A Mobile IP tunnel will be established between the serving PDSN (FA) and the Home Agent (HA) The user appears to be connected to his/her visited network/intranet Only IPv 4 is allowed Mobility can be achieved even between different PDSN belonging to different Providers Network – The user maintains his/her IP address, assigned by the Home network 3 All Rights Reserved © Alcatel-Lucent 2007
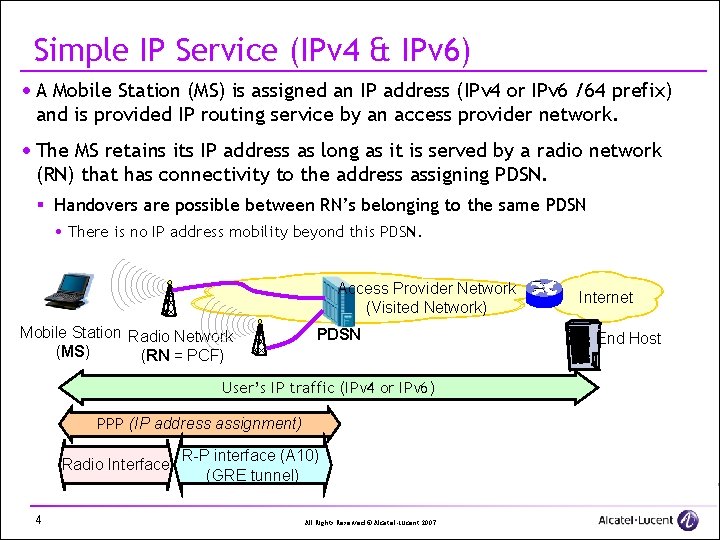
Simple IP Service (IPv 4 & IPv 6) · A Mobile Station (MS) is assigned an IP address (IPv 4 or IPv 6 /64 prefix) and is provided IP routing service by an access provider network. · The MS retains its IP address as long as it is served by a radio network (RN) that has connectivity to the address assigning PDSN. § Handovers are possible between RN’s belonging to the same PDSN There is no IP address mobility beyond this PDSN. Access Provider Network (Visited Network) Mobile Station Radio Network (MS) (RN = PCF) PDSN User’s IP traffic (IPv 4 or IPv 6) PPP (IP address assignment) Radio Interface 4 R-P interface (A 10) (GRE tunnel) All Rights Reserved © Alcatel-Lucent 2007 Internet End Host
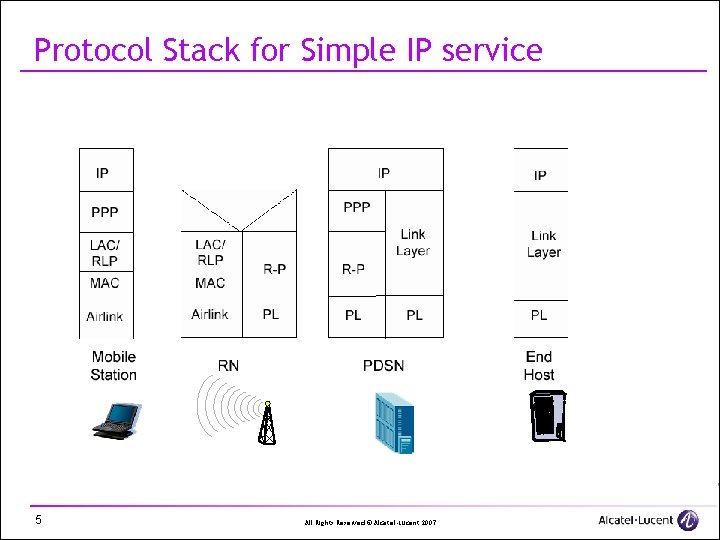
Protocol Stack for Simple IP service 5 All Rights Reserved © Alcatel-Lucent 2007
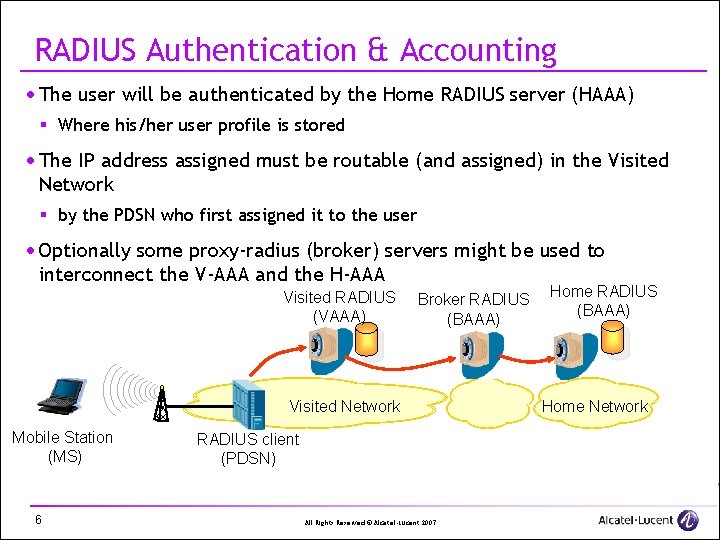
RADIUS Authentication & Accounting · The user will be authenticated by the Home RADIUS server (HAAA) § Where his/her user profile is stored · The IP address assigned must be routable (and assigned) in the Visited Network § by the PDSN who first assigned it to the user · Optionally some proxy-radius (broker) servers might be used to interconnect the V-AAA and the H-AAA Visited RADIUS (VAAA) Broker RADIUS (BAAA) Visited Network Mobile Station (MS) 6 RADIUS client (PDSN) All Rights Reserved © Alcatel-Lucent 2007 Home RADIUS (BAAA) Home Network
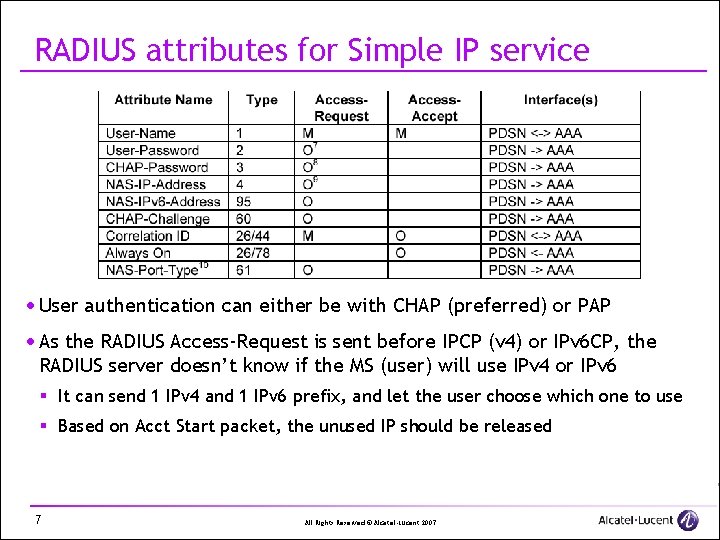
RADIUS attributes for Simple IP service · User authentication can either be with CHAP (preferred) or PAP · As the RADIUS Access-Request is sent before IPCP (v 4) or IPv 6 CP, the RADIUS server doesn’t know if the MS (user) will use IPv 4 or IPv 6 § It can send 1 IPv 4 and 1 IPv 6 prefix, and let the user choose which one to use § Based on Acct Start packet, the unused IP should be released 7 All Rights Reserved © Alcatel-Lucent 2007
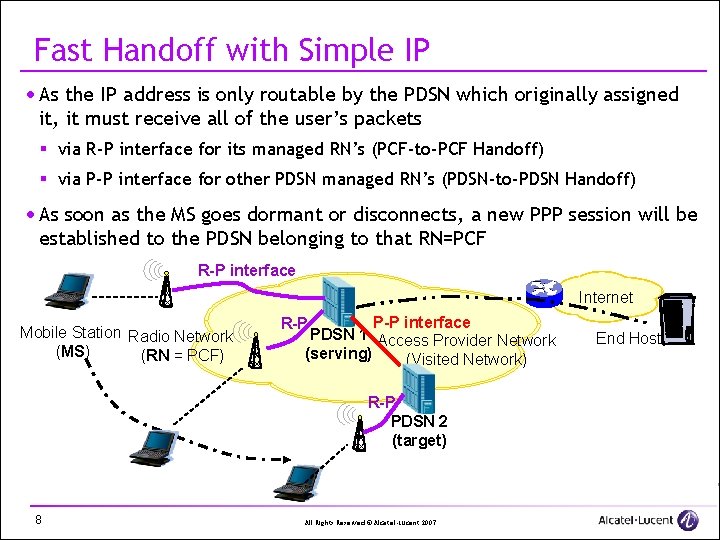
Fast Handoff with Simple IP · As the IP address is only routable by the PDSN which originally assigned it, it must receive all of the user’s packets § via R-P interface for its managed RN’s (PCF-to-PCF Handoff) § via P-P interface for other PDSN managed RN’s (PDSN-to-PDSN Handoff) · As soon as the MS goes dormant or disconnects, a new PPP session will be established to the PDSN belonging to that RN=PCF R-P interface Internet Mobile Station Radio Network (MS) (RN = PCF) P-P interface PDSN 1 Access Provider Network (serving) (Visited Network) R-P PDSN 2 (target) 8 All Rights Reserved © Alcatel-Lucent 2007 End Host
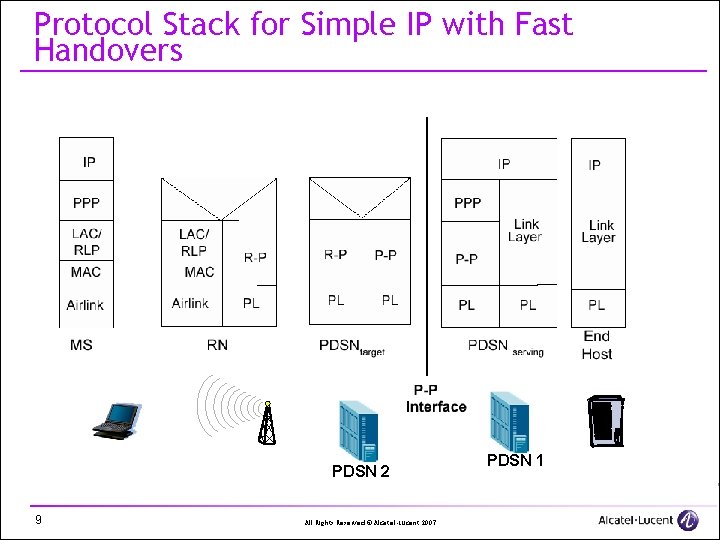
Protocol Stack for Simple IP with Fast Handovers PDSN 2 9 All Rights Reserved © Alcatel-Lucent 2007 PDSN 1
Mobile IP · With Mobile IP the user is able to maintain a persistent IP address even when handing off between RNs connected to different PDSNs. · Mobile IPv 4 provides the user IP routing service to: § a public IP network and/or § a private network securing the traffic · Mobile IP is based on tunnels between a PDSNs (Foreign Agent=FA) and a Home Agent (HA) § The PDSN is always located in the Visited Network (=Serving Network) § The HA can be located in a remote Home Network (when roaming) 10 All Rights Reserved © Alcatel-Lucent 2007
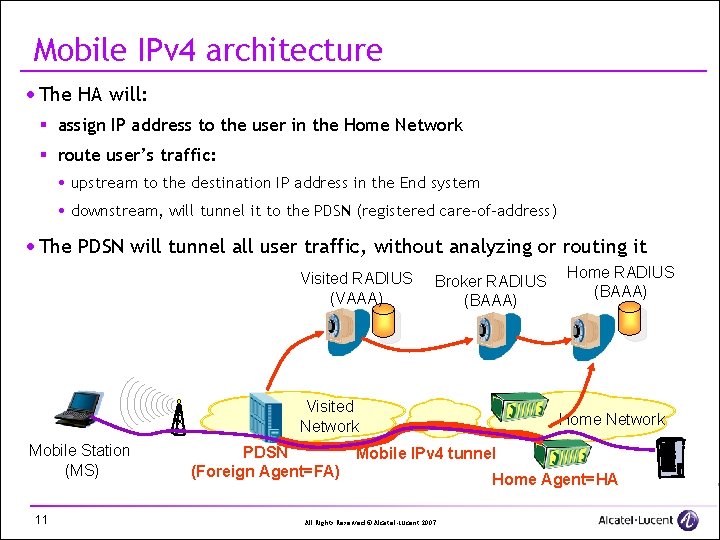
Mobile IPv 4 architecture · The HA will: § assign IP address to the user in the Home Network § route user’s traffic: upstream to the destination IP address in the End system downstream, will tunnel it to the PDSN (registered care-of-address) · The PDSN will tunnel all user traffic, without analyzing or routing it Visited RADIUS (VAAA) Broker RADIUS (BAAA) Visited Network Mobile Station (MS) 11 Home RADIUS (BAAA) Home Network PDSN Mobile IPv 4 tunnel (Foreign Agent=FA) Home Agent=HA All Rights Reserved © Alcatel-Lucent 2007
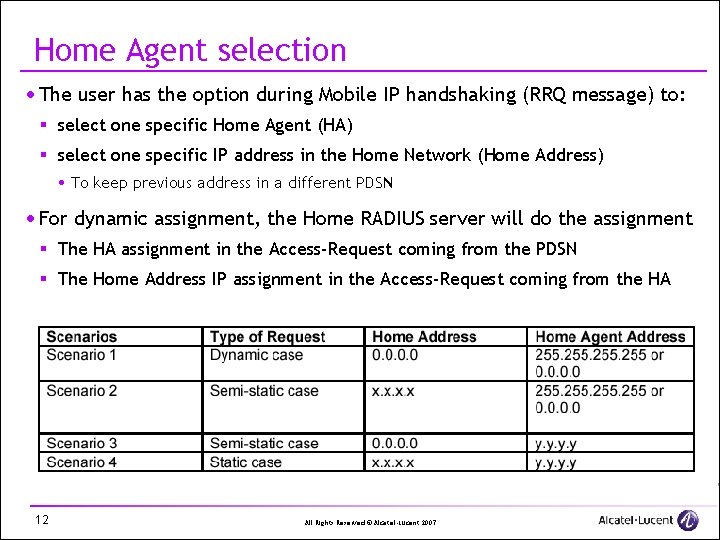
Home Agent selection · The user has the option during Mobile IP handshaking (RRQ message) to: § select one specific Home Agent (HA) § select one specific IP address in the Home Network (Home Address) To keep previous address in a different PDSN · For dynamic assignment, the Home RADIUS server will do the assignment § The HA assignment in the Access-Request coming from the PDSN § The Home Address IP assignment in the Access-Request coming from the HA 12 All Rights Reserved © Alcatel-Lucent 2007
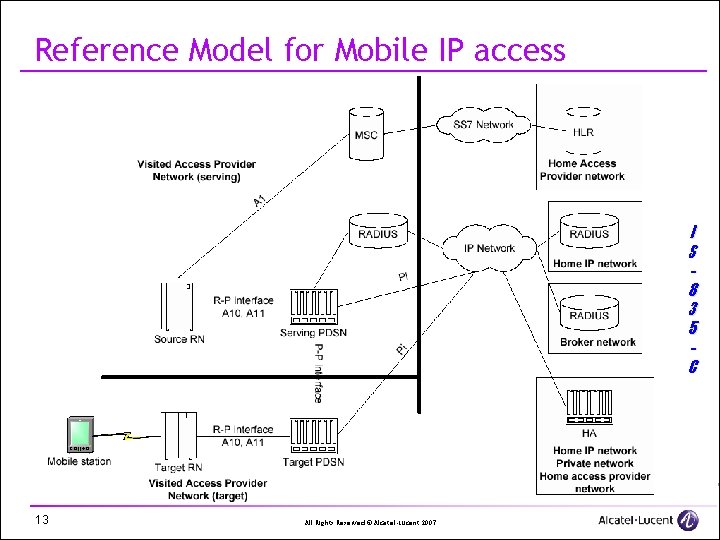
Reference Model for Mobile IP access I S 8 3 5 C 13 All Rights Reserved © Alcatel-Lucent 2007
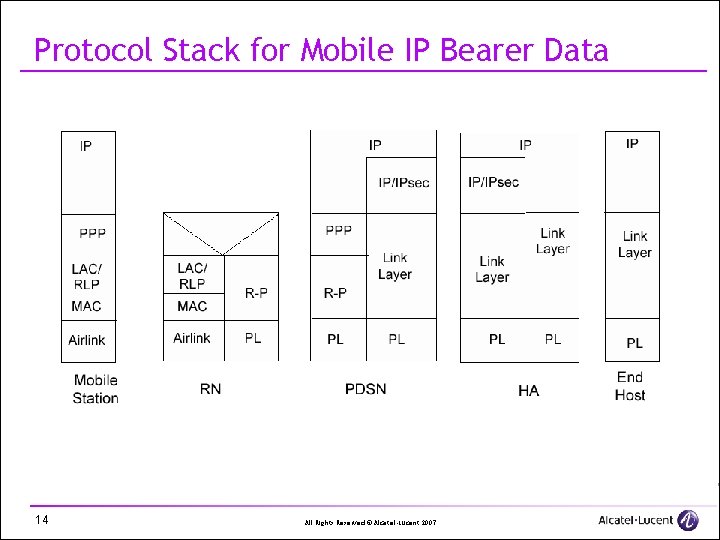
Protocol Stack for Mobile IP Bearer Data 14 All Rights Reserved © Alcatel-Lucent 2007
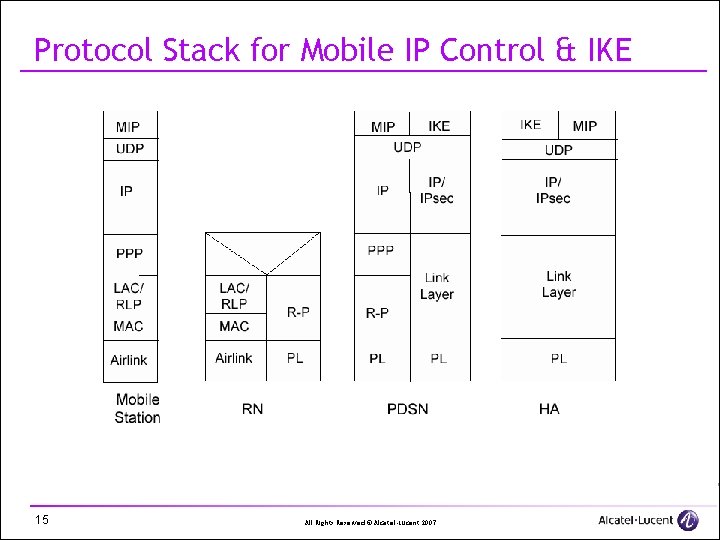
Protocol Stack for Mobile IP Control & IKE 15 All Rights Reserved © Alcatel-Lucent 2007
General User Authentication · The user authentication is done with Mobile IP AAA extensions § MN-NAI = Used to identify the User with a Network Address Identifier (=User. Name) § MN-FA, MN-AAA or MN-HA extension, which has 2 fields (SPI & authenticator): SPI (Security Prefix Index)- It is an identifier to a security association (key) used between the user (MN) and the AAA (or HA), to “sign” the message – There is a special value of CHAP_SPI(=2), meaning there is only 1 key shared between the MN and the HA or AAA Authenticator field: “signature” of the message (MD 5) using the secret key specified in SPI · General PPP authentication (PAP or CHAP) is not recommended with Mobile IP, as it represents double authentication § with twice the amount of RADIUS packets and extra delays 16 All Rights Reserved © Alcatel-Lucent 2007
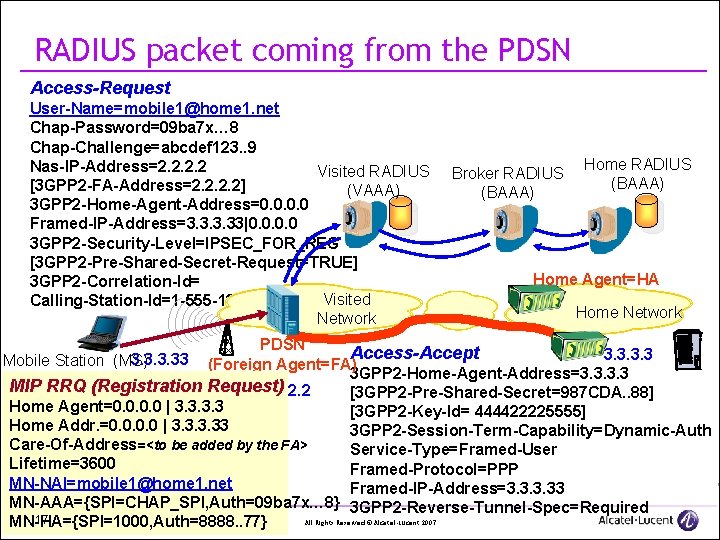
RADIUS packet coming from the PDSN Access-Request User-Name=mobile 1@home 1. net Chap-Password=09 ba 7 x… 8 Chap-Challenge=abcdef 123. . 9 Nas-IP-Address=2. 2 Visited RADIUS [3 GPP 2 -FA-Address=2. 2] (VAAA) 3 GPP 2 -Home-Agent-Address=0. 0 Framed-IP-Address=3. 33|0. 0 3 GPP 2 -Security-Level=IPSEC_FOR_REG [3 GPP 2 -Pre-Shared-Secret-Request=TRUE] 3 GPP 2 -Correlation-Id= Visited Calling-Station-Id=1 -555 -123456 Network Broker RADIUS (BAAA) Home Agent=HA Home Network PDSN 3. 33 (Foreign Agent=FA)Access-Accept Mobile Station (MS) 3 GPP 2 -Home-Agent-Address=3. 3 MIP RRQ (Registration Request) 2. 2 [3 GPP 2 -Pre-Shared-Secret=987 CDA. . 88] Home Agent=0. 0 | 3. 3 [3 GPP 2 -Key-Id= 444422225555] Home Addr. =0. 0 | 3. 33 3 GPP 2 -Session-Term-Capability=Dynamic-Auth Care-Of-Address=<to be added by the FA> Service-Type=Framed-User Lifetime=3600 Framed-Protocol=PPP MN-NAI=mobile 1@home 1. net Framed-IP-Address=3. 33 MN-AAA={SPI=CHAP_SPI, Auth=09 ba 7 x… 8} 3 GPP 2 -Reverse-Tunnel-Spec=Required 17 All Rights Reserved © Alcatel-Lucent 2007 MN-HA={SPI=1000, Auth=8888. . 77}
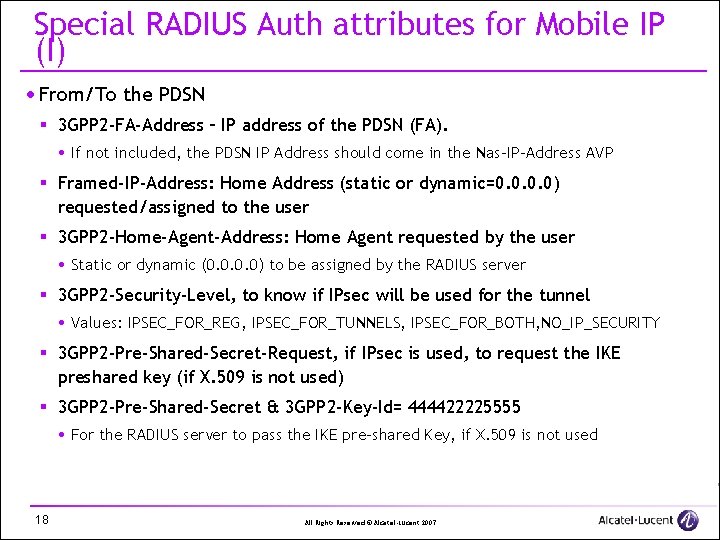
Special RADIUS Auth attributes for Mobile IP (I) · From/To the PDSN § 3 GPP 2 -FA-Address – IP address of the PDSN (FA). If not included, the PDSN IP Address should come in the Nas-IP-Address AVP § Framed-IP-Address: Home Address (static or dynamic=0. 0) requested/assigned to the user § 3 GPP 2 -Home-Agent-Address: Home Agent requested by the user Static or dynamic (0. 0) to be assigned by the RADIUS server § 3 GPP 2 -Security-Level, to know if IPsec will be used for the tunnel Values: IPSEC_FOR_REG, IPSEC_FOR_TUNNELS, IPSEC_FOR_BOTH, NO_IP_SECURITY § 3 GPP 2 -Pre-Shared-Secret-Request, if IPsec is used, to request the IKE preshared key (if X. 509 is not used) § 3 GPP 2 -Pre-Shared-Secret & 3 GPP 2 -Key-Id= 444422225555 For the RADIUS server to pass the IKE pre-shared Key, if X. 509 is not used 18 All Rights Reserved © Alcatel-Lucent 2007
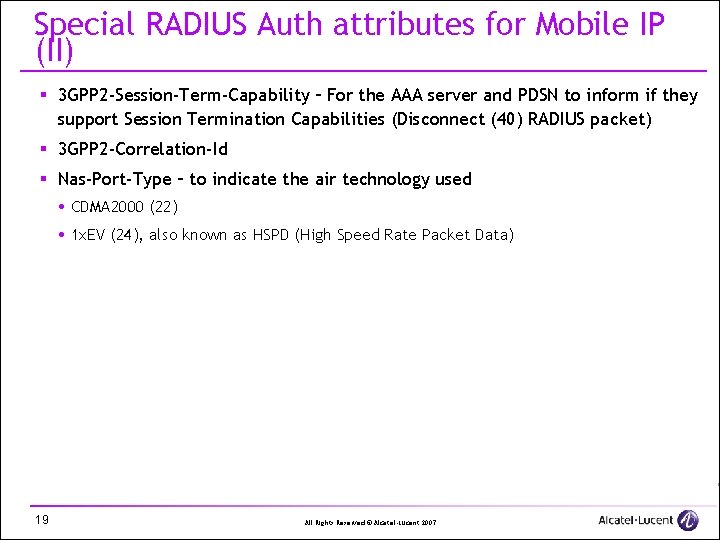
Special RADIUS Auth attributes for Mobile IP (II) § 3 GPP 2 -Session-Term-Capability – For the AAA server and PDSN to inform if they support Session Termination Capabilities (Disconnect (40) RADIUS packet) § 3 GPP 2 -Correlation-Id § Nas-Port-Type – to indicate the air technology used CDMA 2000 (22) 1 x. EV (24), also known as HSPD (High Speed Rate Packet Data) 19 All Rights Reserved © Alcatel-Lucent 2007
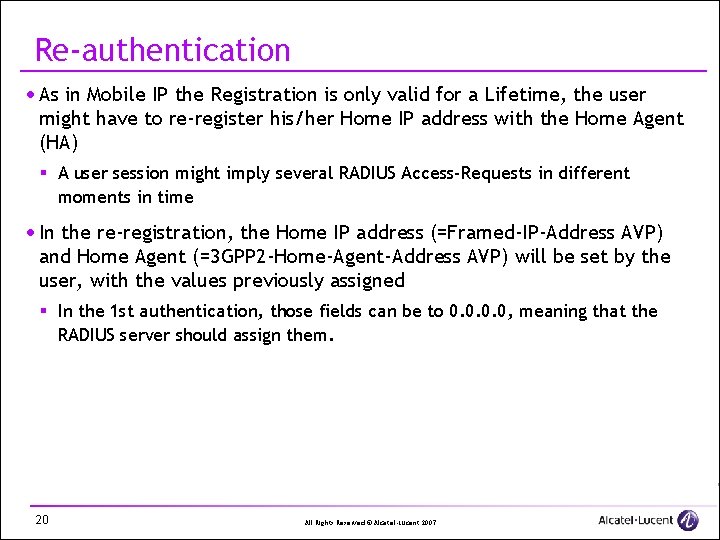
Re-authentication · As in Mobile IP the Registration is only valid for a Lifetime, the user might have to re-register his/her Home IP address with the Home Agent (HA) § A user session might imply several RADIUS Access-Requests in different moments in time · In the re-registration, the Home IP address (=Framed-IP-Address AVP) and Home Agent (=3 GPP 2 -Home-Agent-Address AVP) will be set by the user, with the values previously assigned § In the 1 st authentication, those fields can be to 0. 0, meaning that the RADIUS server should assign them. 20 All Rights Reserved © Alcatel-Lucent 2007
IPsec for the tunnel between PDSN and HA · For extra security, the data in the tunnel can be encrypted and/or authenticated. · In IPsec, the tunnel End. Points must be authenticated, by: § X. 509 digital certificates § Dynamic pre-shared IKE secret distributed by the Home RADIUS Server § Statically configured IKE pre-shared secret. · Many users’ traffic can be transported over the same tunnel 21 All Rights Reserved © Alcatel-Lucent 2007
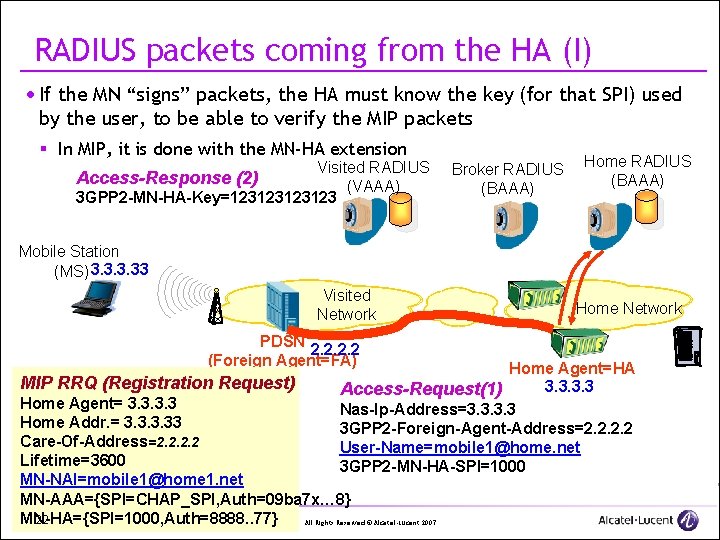
RADIUS packets coming from the HA (I) · If the MN “signs” packets, the HA must know the key (for that SPI) used by the user, to be able to verify the MIP packets § In MIP, it is done with the MN-HA extension Visited RADIUS Access-Response (2) (VAAA) 3 GPP 2 -MN-HA-Key=123123 Broker RADIUS (BAAA) Home RADIUS (BAAA) Mobile Station (MS) 3. 33 Visited Network PDSN 2. 2 (Foreign Agent=FA) MIP RRQ (Registration Request) Home Network Home Agent=HA 3. 3 Access-Request(1) Nas-Ip-Address=3. 3 3 GPP 2 -Foreign-Agent-Address=2. 2 User-Name=mobile 1@home. net 3 GPP 2 -MN-HA-SPI=1000 Home Agent= 3. 3 Home Addr. = 3. 33 Care-Of-Address=2. 2 Lifetime=3600 MN-NAI=mobile 1@home 1. net MN-AAA={SPI=CHAP_SPI, Auth=09 ba 7 x… 8} MN-HA={SPI=1000, Auth=8888. . 77} 22 All Rights Reserved © Alcatel-Lucent 2007
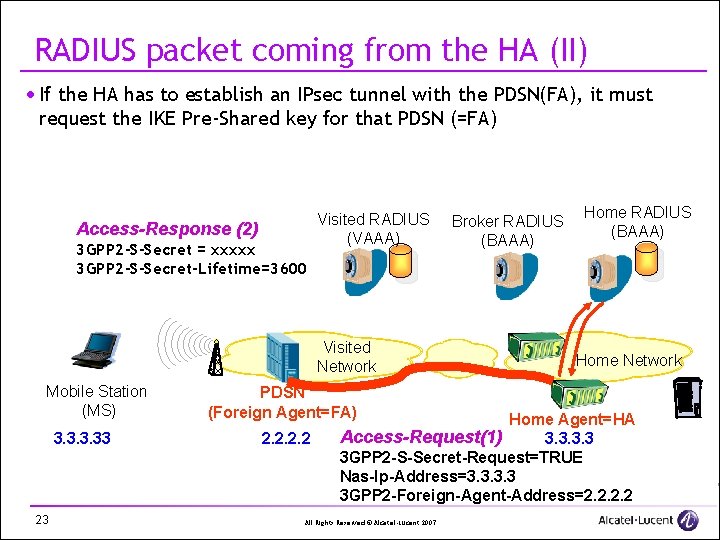
RADIUS packet coming from the HA (II) · If the HA has to establish an IPsec tunnel with the PDSN(FA), it must request the IKE Pre-Shared key for that PDSN (=FA) Access-Response (2) 3 GPP 2 -S-Secret = xxxxx 3 GPP 2 -S-Secret-Lifetime=3600 Visited RADIUS (VAAA) Visited Network Mobile Station (MS) 3. 33 23 PDSN (Foreign Agent=FA) 2. 2 Broker RADIUS (BAAA) Home Network Home Agent=HA Access-Request(1) 3. 3 3 GPP 2 -S-Secret-Request=TRUE Nas-Ip-Address=3. 3 3 GPP 2 -Foreign-Agent-Address=2. 2 All Rights Reserved © Alcatel-Lucent 2007
Accounting · The accounting information is generated by the PDSN, and forwarded to the visited, broker and home RADIUS server. · The accounting information is also called Usage Data Record (UDR) · The PDSN closes a UDR when any of the following events occur: § An existing R-P or P-P connection is closed. Handovers between PCF’s, or between PDSN’s, etc § The PDSN determines the packet data session associated with the correlation ID has ended. 24 All Rights Reserved © Alcatel-Lucent 2007
Special RADIUS Acct attributes · Acct-Session-ID § Unique accounting ID created by the Serving PDSN that allows start and stop RADIUS records from a single R-P connection or P-P connection to be matched · 3 GPP 2 -Correlation-ID § Unique accounting ID created by the Serving PDSN for each packet data session that allows multiple accounting events for each associated R-P connection or P -P connection to be correlated. · 3 GPP 2 -Session-Continue (in Acct STOP) § When set to ‘true’ means it is not the end of a Session. § An Accounting Stop is immediately followed by an Account Start Record from the same PDSN or a different one The new Acct Start will have the same 3 GPP 2 -Correlation-ID, but different Acct-Session -Id · 3 GPP 2 -Beginning-Session (in Acct START) § When set to ‘true’ means new packet data session is established 25 All Rights Reserved © Alcatel-Lucent 2007
Hand-overs (I) · For Radio Networks (Base Stations) belonging to the same PDSN § No special procedure is needed, as the tunnel is still valid (between the same PDSN and HA) A different R-P tunnel will be used (GRE) A RADIUS Acct Stop and an Acct Start will be generated with different Acct-Session-Id AVP’s and different 3 GPP 2 -R-P-Connection-ID, but same 3 GPP 2 -Correlation-Id § Valid for Simple IP service and Mobile IP service · For Radio Networks (Base Stations) belonging to the different PDSN’s § The RADIUS server must know the user was previously attached to another PDSN, and must sent a RADIUS Disconnect (40) packet to the former PDSN to remove his/her context § The ‘former’ PDSN will send an Acct STOP, and the “new” PDSN will send an Acct START, with the same 3 GPP 2 -Correlation-Id 26 All Rights Reserved © Alcatel-Lucent 2007
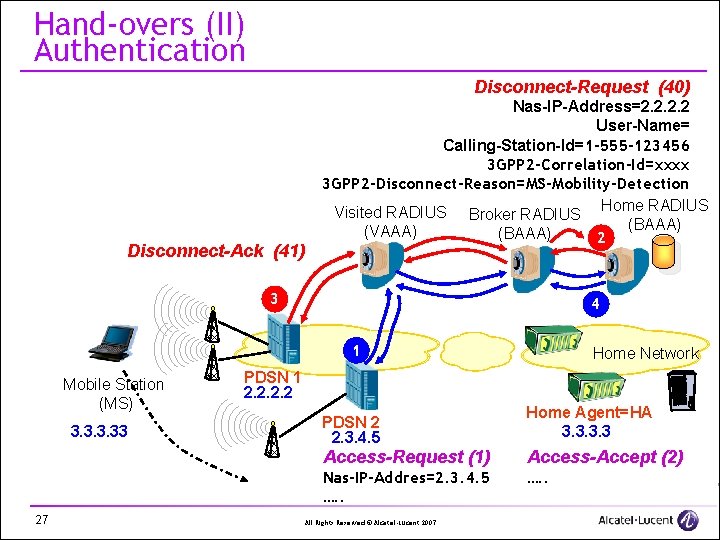
Hand-overs (II) Authentication Disconnect-Request (40) Disconnect-Ack (41) Nas-IP-Address=2. 2 User-Name= Calling-Station-Id=1 -555 -123456 3 GPP 2 -Correlation-Id=xxxx 3 GPP 2 -Disconnect-Reason=MS-Mobility-Detection Visited RADIUS Broker RADIUS Home RADIUS (BAAA) (VAAA) (BAAA) 2 3 4 1 Mobile Station (MS) 3. 33 27 Home Network PDSN 1 2. 2 PDSN 2 2. 3. 4. 5 Home Agent=HA 3. 3 Access-Request (1) Access-Accept (2) Nas-IP-Addres=2. 3. 4. 5 …. . All Rights Reserved © Alcatel-Lucent 2007
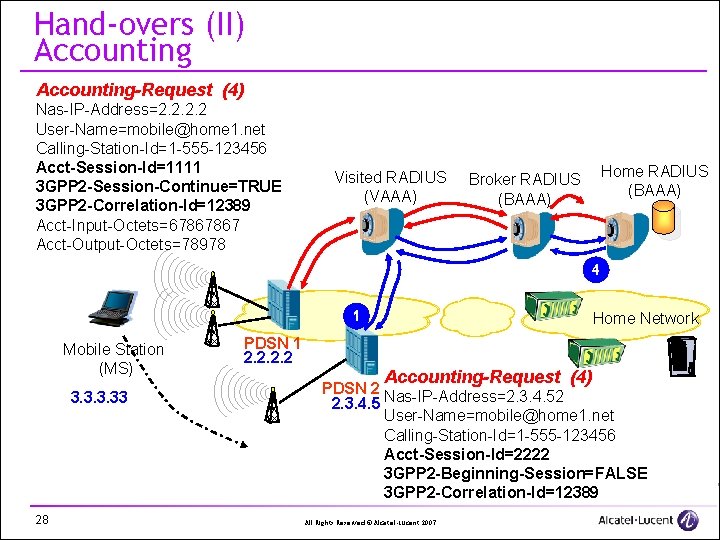
Hand-overs (II) Accounting-Request (4) Nas-IP-Address=2. 2 User-Name=mobile@home 1. net Calling-Station-Id=1 -555 -123456 Acct-Session-Id=1111 3 GPP 2 -Session-Continue=TRUE 3 GPP 2 -Correlation-Id=12389 Acct-Input-Octets=67867867 Acct-Output-Octets=78978 Visited RADIUS (VAAA) Home RADIUS (BAAA) Broker RADIUS (BAAA) 4 1 Mobile Station (MS) 3. 33 28 PDSN 1 2. 2 Home Network Accounting-Request (4) PDSN 2 2. 3. 4. 5 Nas-IP-Address=2. 3. 4. 52 User-Name=mobile@home 1. net Calling-Station-Id=1 -555 -123456 Acct-Session-Id=2222 3 GPP 2 -Beginning-Session=FALSE 3 GPP 2 -Correlation-Id=12389 All Rights Reserved © Alcatel-Lucent 2007
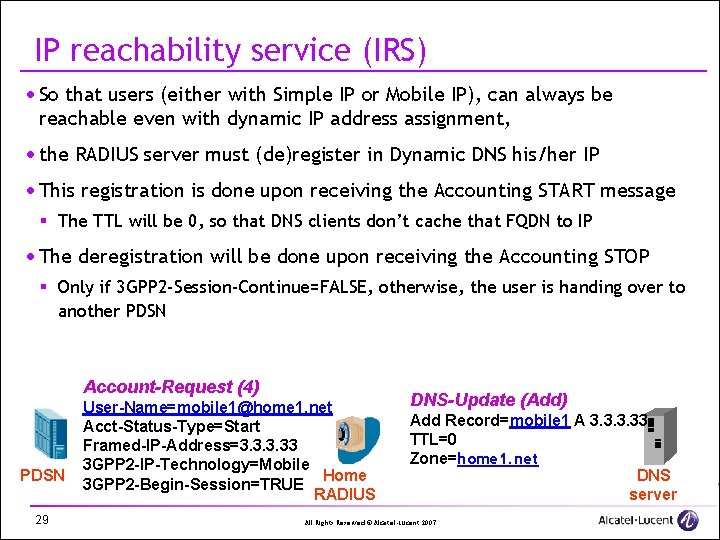
IP reachability service (IRS) · So that users (either with Simple IP or Mobile IP), can always be reachable even with dynamic IP address assignment, · the RADIUS server must (de)register in Dynamic DNS his/her IP · This registration is done upon receiving the Accounting START message § The TTL will be 0, so that DNS clients don’t cache that FQDN to IP · The deregistration will be done upon receiving the Accounting STOP § Only if 3 GPP 2 -Session-Continue=FALSE, otherwise, the user is handing over to another PDSN Account-Request (4) PDSN 29 User-Name=mobile 1@home 1. net Acct-Status-Type=Start Framed-IP-Address=3. 33 3 GPP 2 -IP-Technology=Mobile Home 3 GPP 2 -Begin-Session=TRUE RADIUS DNS-Update (Add) Add Record=mobile 1 A 3. 33 TTL=0 Zone=home 1. net DNS server All Rights Reserved © Alcatel-Lucent 2007
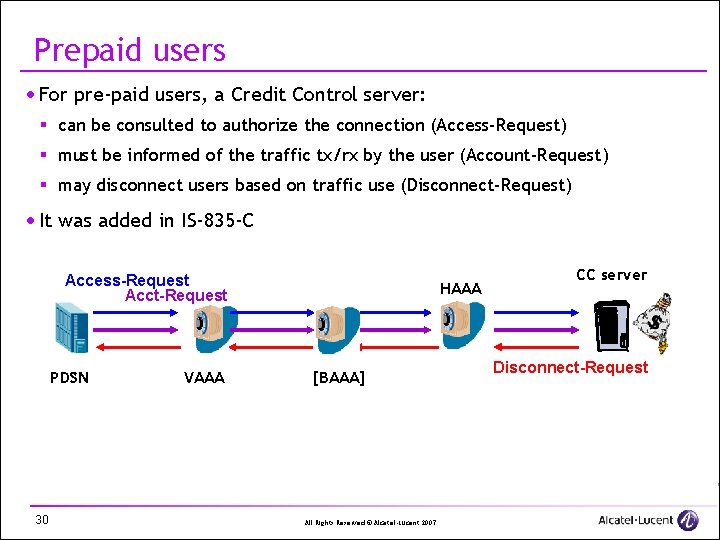
Prepaid users · For pre-paid users, a Credit Control server: § can be consulted to authorize the connection (Access-Request) § must be informed of the traffic tx/rx by the user (Account-Request) § may disconnect users based on traffic use (Disconnect-Request) · It was added in IS-835 -C Access-Request Acct-Request PDSN 30 VAAA HAAA [BAAA] All Rights Reserved © Alcatel-Lucent 2007 CC server Disconnect-Request
Qo. S profiles · In 1 x. EV, rev A, it was added the possibility to define Qo. S profiles for the users · This is done with new AVPs returned by the HAAA in the Access-Accept packet: § 3 GPP 2 -Max-Bandwidth-For-Best-Effort-Traffic § 3 GPP 2 -Authorized-Qo. S-Profile-Ids § 3 GPP 2 -Granted-Qo. S-Parameters § Traffic-Class – Unknown, Conversational, Streaming, Interactive, Background" 31 All Rights Reserved © Alcatel-Lucent 2007
Vital. AAA support for IS -835 -C
Sample IS-835 -C PF · There is a sample PF that can handle all type of RADIUS requests · Vital. AAA can behave as: § Visited AAA (VAAA) & Broker AAA (BAAA) To proxy Auth/Acct requests to BAAA or HAAA, based on realm – Proxy Disconnect-Requests to PDSN coming from HAAA or BAAA, based on Nas-IPAddress Additionally for Acct, it also writes to disk the acct data § Home AAA (HAAA), receiving requests both from the HA & PDSN 33 All Rights Reserved © Alcatel-Lucent 2007
Auth Sample PF for Acct · PDSN Overview: § write accounting record to a detail file § if start record and begin session request DHCP if IPv 4 address from allocated range add DNS records § if stop record and not continue release DHCP if IPv 4 address from allocated range delete DNS records § update DHCP if address from allocated range · HA Overview: § write accounting record to a detail file · Dynamic Auth Overview: § Get routes from cache § Forward request to next hop 34 All Rights Reserved © Alcatel-Lucent 2007
Auth Sample PF for Auth (I) PDSN overview (I) · if Service-Type is Authorize-Only § if 3 GPP 2 -Pre. Paid-Acct-Quota is present proxy request to Pre. Paid Server § else discard · else § read user from file ignoring information for Home Agent § authenticate user and process check items § if 3 GPP 2 -Pre. Paid-Acct-Capability is present proxy request to Pre. Paid Server query USS to see if sessions for different PDSNs exist for each old session – send disconnect message if new PDSN supports disconnect messages – add record for new session to USS 35 All Rights Reserved © Alcatel-Lucent 2007
Auth Sample PF for Auth (II) PDSN overview (II) § if HA address was sent in request copy address to reply § else dynamically assign HA address § if Mn. Address was sent in request if dynamically to be assigned – request one in DHCP server § else discard § if PDSN requests pre-shared secret for IKE if user is authorized for IKE – generate keys 36 All Rights Reserved © Alcatel-Lucent 2007
Auth Sample PF for Auth (III) PDSN overview (III) § query USS to see if sessions for different PDSNs exist § for each old session send disconnect message § if new PDSN supports disconnect messages add record for new session to USS 37 All Rights Reserved © Alcatel-Lucent 2007
Auth Sample PF for Auth (III): HA overview · If asking for S-Secret § return S-Secret and S-Secret-Lifetime · else § if CHAP credentials sent if MN-HA-SPI sent – check SPI and CHAP else – check CHAP § else if MN-HA-SPI sent – check SPI else – drop request 38 All Rights Reserved © Alcatel-Lucent 2007
Vital. AAA plug-in support for IS-835 -C (I) · To proxy requests (RADIUS plug-in): § Auth&Acct - Pre-paid server for credit control (HAAA) § Auth&Acct – regular requests from PDSN to HAAA (VAAA & BAAA) § Dyn. Auth – to proxy Disconnect-Requests towards the PDSN (HAAA, VAAA&BAAA) · To assign dynamic IP addresses to users: § IPv 4: DHCP, ADDRESS or STATESERVER (IPAMv 2) § IPv 6: DHCPv 6 or STATESERVER (IPAMv 2) · To generate pre-shared key for IKE in PDSN, according to the formula: § K = HMAC-MD 5 (Home RADIUS IP address | FA IP address | timestamp, ‘S’) § Read. Key. Cache & Hmac plug-ins 39 All Rights Reserved © Alcatel-Lucent 2007
Vital. AAA plug-in support for IS-835 -C (II) · To know if a user was connected in a different PDSN, to be able to send a Disconnect-Request to the “old” PDSN § State. Server & Query. Uss plug-in, with an USS index based on the User-Name · To send/proxy Disconnect-Requests to the PDSN § A cache mechanism in the engine that stores the proxy server (VAAA or BAAA) that forwarded a request from a specific PDSN § Read. Cache plug-in to be able to read that cache, and know which BAAA is able to proxy a packet towards a specific PDSN § Read. Client, to be able to read the secret of the proxy-radius server or PDSN § Radius plug-in, to proxy or generate the Disconnect packet 40 All Rights Reserved © Alcatel-Lucent 2007
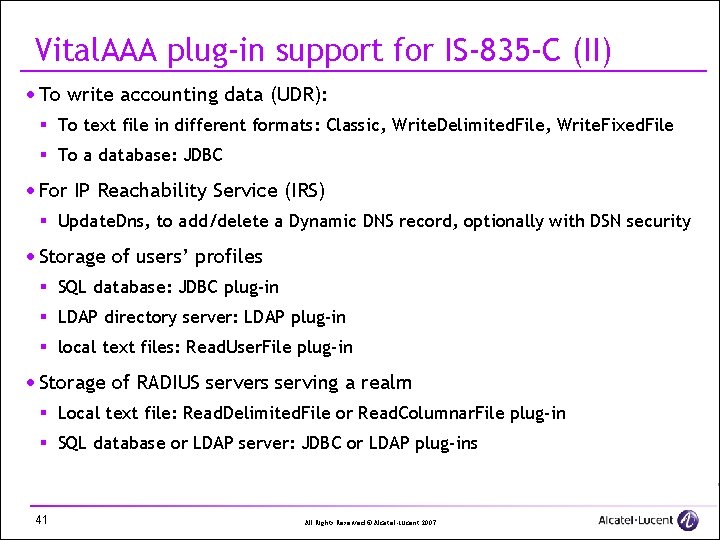
Vital. AAA plug-in support for IS-835 -C (II) · To write accounting data (UDR): § To text file in different formats: Classic, Write. Delimited. File, Write. Fixed. File § To a database: JDBC · For IP Reachability Service (IRS) § Update. Dns, to add/delete a Dynamic DNS record, optionally with DSN security · Storage of users’ profiles § SQL database: JDBC plug-in § LDAP directory server: LDAP plug-in § local text files: Read. User. File plug-in · Storage of RADIUS servers serving a realm § Local text file: Read. Delimited. File or Read. Columnar. File plug-in § SQL database or LDAP server: JDBC or LDAP plug-ins 41 All Rights Reserved © Alcatel-Lucent 2007
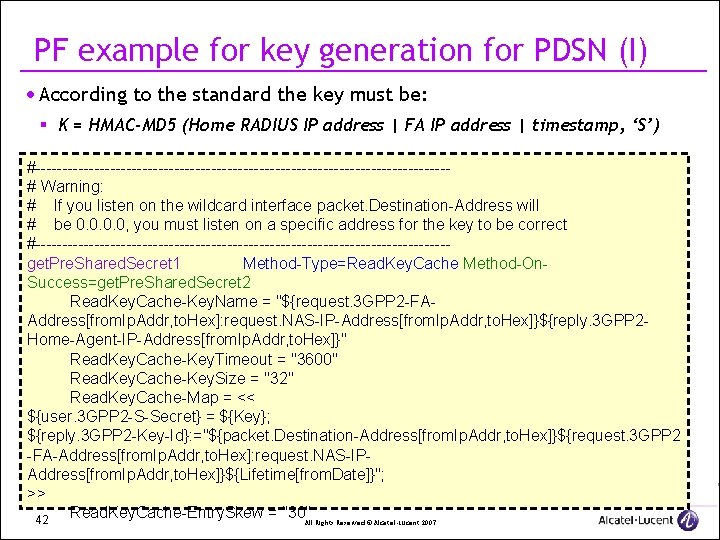
PF example for key generation for PDSN (I) · According to the standard the key must be: § K = HMAC-MD 5 (Home RADIUS IP address | FA IP address | timestamp, ‘S’) #---------------------------------------# Warning: # If you listen on the wildcard interface packet. Destination-Address will # be 0. 0, you must listen on a specific address for the key to be correct #---------------------------------------get. Pre. Shared. Secret 1 Method-Type=Read. Key. Cache Method-On. Success=get. Pre. Shared. Secret 2 Read. Key. Cache-Key. Name = "${request. 3 GPP 2 -FAAddress[from. Ip. Addr, to. Hex]: request. NAS-IP-Address[from. Ip. Addr, to. Hex]}${reply. 3 GPP 2 Home-Agent-IP-Address[from. Ip. Addr, to. Hex]}" Read. Key. Cache-Key. Timeout = "3600" Read. Key. Cache-Key. Size = "32" Read. Key. Cache-Map = << ${user. 3 GPP 2 -S-Secret} = ${Key}; ${reply. 3 GPP 2 -Key-Id}: ="${packet. Destination-Address[from. Ip. Addr, to. Hex]}${request. 3 GPP 2 -FA-Address[from. Ip. Addr, to. Hex]: request. NAS-IPAddress[from. Ip. Addr, to. Hex]}${Lifetime[from. Date]}"; >> Read. Key. Cache-Entry. Skew = "30"All Rights Reserved © Alcatel-Lucent 2007 42
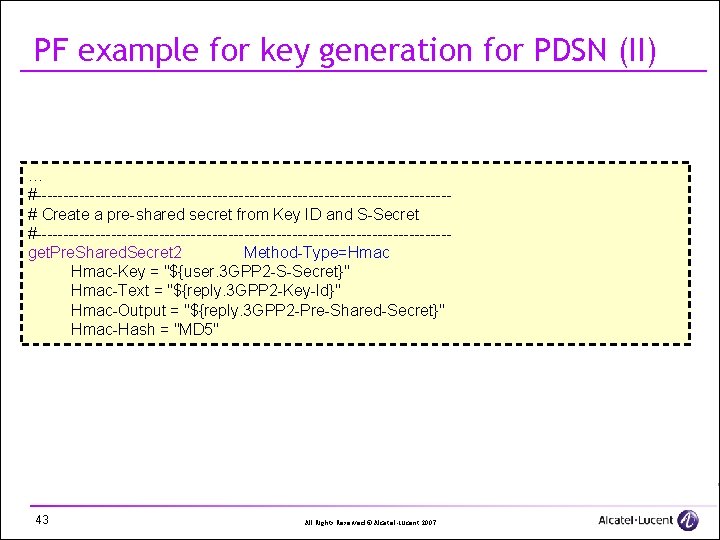
PF example for key generation for PDSN (II) … #---------------------------------------# Create a pre-shared secret from Key ID and S-Secret #---------------------------------------get. Pre. Shared. Secret 2 Method-Type=Hmac-Key = "${user. 3 GPP 2 -S-Secret}" Hmac-Text = "${reply. 3 GPP 2 -Key-Id}" Hmac-Output = "${reply. 3 GPP 2 -Pre-Shared-Secret}" Hmac-Hash = "MD 5" 43 All Rights Reserved © Alcatel-Lucent 2007
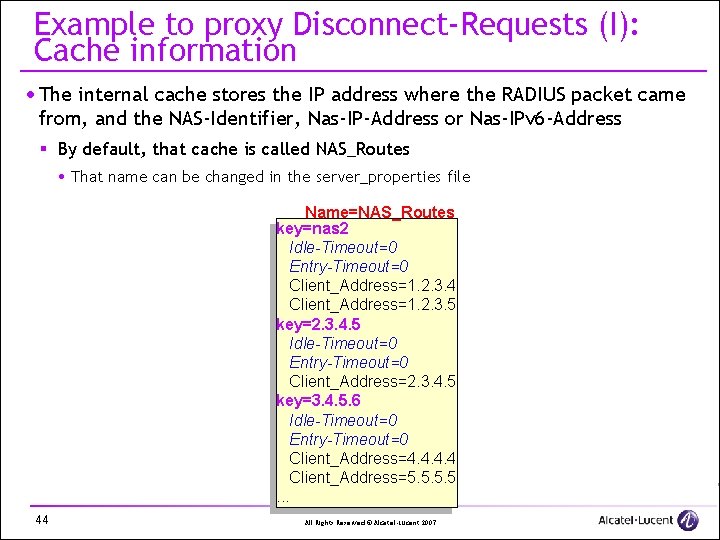
Example to proxy Disconnect-Requests (I): Cache information · The internal cache stores the IP address where the RADIUS packet came from, and the NAS-Identifier, Nas-IP-Address or Nas-IPv 6 -Address § By default, that cache is called NAS_Routes That name can be changed in the server_properties file Name=NAS_Routes key=nas 2 Idle-Timeout=0 Entry-Timeout=0 Client_Address=1. 2. 3. 4 Client_Address=1. 2. 3. 5 key=2. 3. 4. 5 Idle-Timeout=0 Entry-Timeout=0 Client_Address=2. 3. 4. 5 key=3. 4. 5. 6 Idle-Timeout=0 Entry-Timeout=0 Client_Address=4. 4 Client_Address=5. 5. . . 44 All Rights Reserved © Alcatel-Lucent 2007
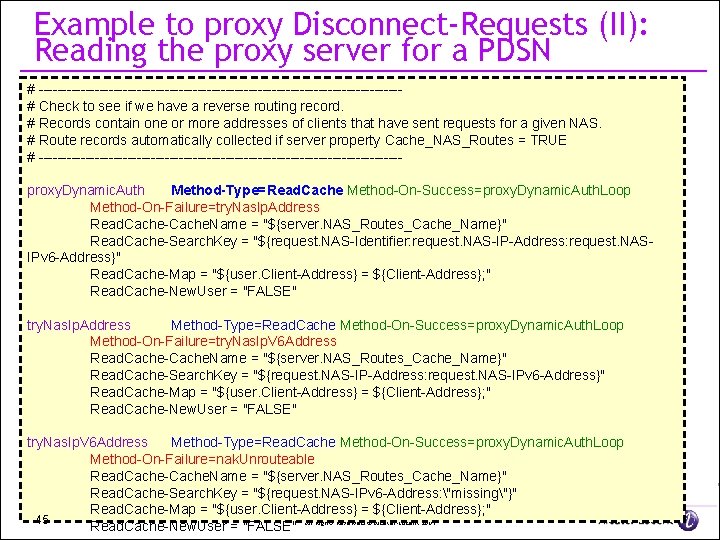
Example to proxy Disconnect-Requests (II): Reading the proxy server for a PDSN # ---------------------------------------# Check to see if we have a reverse routing record. # Records contain one or more addresses of clients that have sent requests for a given NAS. # Route records automatically collected if server property Cache_NAS_Routes = TRUE # ---------------------------------------proxy. Dynamic. Auth Method-Type=Read. Cache Method-On-Success=proxy. Dynamic. Auth. Loop Method-On-Failure=try. Nas. Ip. Address Read. Cache-Cache. Name = "${server. NAS_Routes_Cache_Name}" Read. Cache-Search. Key = "${request. NAS-Identifier: request. NAS-IP-Address: request. NASIPv 6 -Address}" Read. Cache-Map = "${user. Client-Address} = ${Client-Address}; " Read. Cache-New. User = "FALSE" try. Nas. Ip. Address Method-Type=Read. Cache Method-On-Success=proxy. Dynamic. Auth. Loop Method-On-Failure=try. Nas. Ip. V 6 Address Read. Cache-Cache. Name = "${server. NAS_Routes_Cache_Name}" Read. Cache-Search. Key = "${request. NAS-IP-Address: request. NAS-IPv 6 -Address}" Read. Cache-Map = "${user. Client-Address} = ${Client-Address}; " Read. Cache-New. User = "FALSE" try. Nas. Ip. V 6 Address Method-Type=Read. Cache Method-On-Success=proxy. Dynamic. Auth. Loop Method-On-Failure=nak. Unrouteable Read. Cache-Cache. Name = "${server. NAS_Routes_Cache_Name}" Read. Cache-Search. Key = "${request. NAS-IPv 6 -Address: "missing"}" Read. Cache-Map = "${user. Client-Address} = ${Client-Address}; " 45 Read. Cache-New. User = "FALSE" All Rights Reserved © Alcatel-Lucent 2007
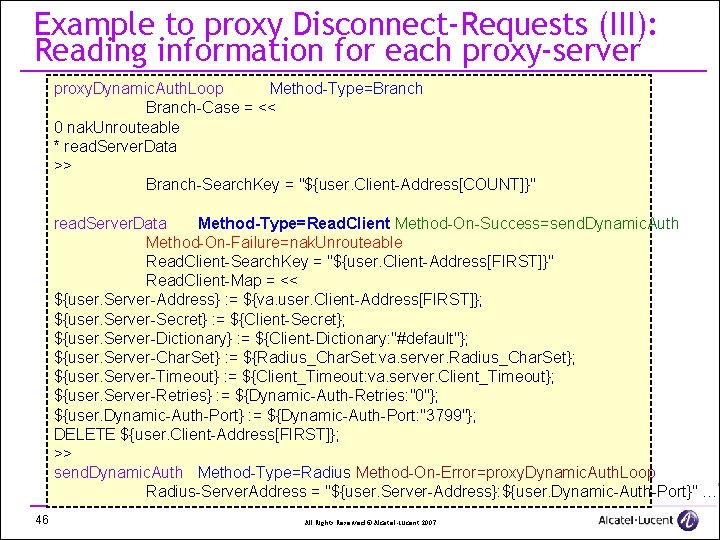
Example to proxy Disconnect-Requests (III): Reading information for each proxy-server proxy. Dynamic. Auth. Loop Method-Type=Branch-Case = << 0 nak. Unrouteable * read. Server. Data >> Branch-Search. Key = "${user. Client-Address[COUNT]}" read. Server. Data Method-Type=Read. Client Method-On-Success=send. Dynamic. Auth Method-On-Failure=nak. Unrouteable Read. Client-Search. Key = "${user. Client-Address[FIRST]}" Read. Client-Map = << ${user. Server-Address} : = ${va. user. Client-Address[FIRST]}; ${user. Server-Secret} : = ${Client-Secret}; ${user. Server-Dictionary} : = ${Client-Dictionary: "#default"}; ${user. Server-Char. Set} : = ${Radius_Char. Set: va. server. Radius_Char. Set}; ${user. Server-Timeout} : = ${Client_Timeout: va. server. Client_Timeout}; ${user. Server-Retries} : = ${Dynamic-Auth-Retries: "0"}; ${user. Dynamic-Auth-Port} : = ${Dynamic-Auth-Port: "3799"}; DELETE ${user. Client-Address[FIRST]}; >> send. Dynamic. Auth Method-Type=Radius Method-On-Error=proxy. Dynamic. Auth. Loop Radius-Server. Address = "${user. Server-Address}: ${user. Dynamic-Auth-Port}" … 46 All Rights Reserved © Alcatel-Lucent 2007
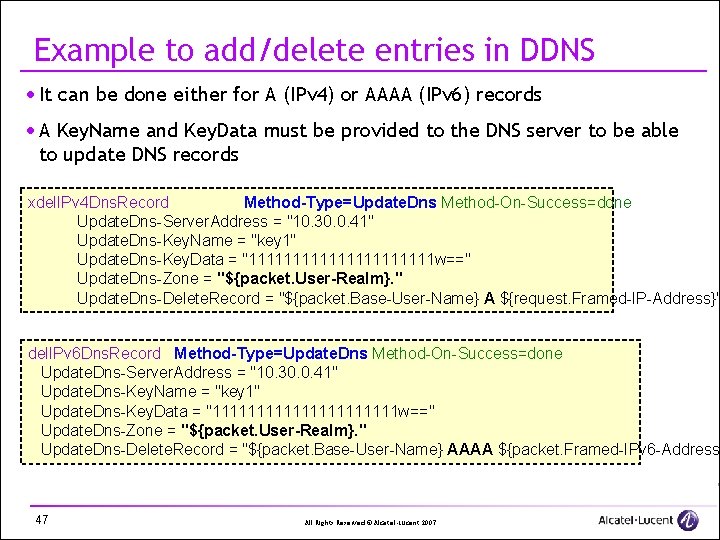
Example to add/delete entries in DDNS · It can be done either for A (IPv 4) or AAAA (IPv 6) records · A Key. Name and Key. Data must be provided to the DNS server to be able to update DNS records xdel. IPv 4 Dns. Record Method-Type=Update. Dns Method-On-Success=done Update. Dns-Server. Address = "10. 30. 0. 41" Update. Dns-Key. Name = "key 1" Update. Dns-Key. Data = "11111111111 w==" Update. Dns-Zone = "${packet. User-Realm}. " Update. Dns-Delete. Record = "${packet. Base-User-Name} A ${request. Framed-IP-Address}" del. IPv 6 Dns. Record Method-Type=Update. Dns Method-On-Success=done Update. Dns-Server. Address = "10. 30. 0. 41" Update. Dns-Key. Name = "key 1" Update. Dns-Key. Data = "11111111111 w==" Update. Dns-Zone = "${packet. User-Realm}. " Update. Dns-Delete. Record = "${packet. Base-User-Name} AAAA ${packet. Framed-IPv 6 -Address 47 All Rights Reserved © Alcatel-Lucent 2007
- Slides: 47