
BGP FlowspecRFC 5575 Case study and Discussion Shishio
BGP Flowspec(RFC 5575) Case study and Discussion Shishio Tsuchiya shtsuchi@cisco. com
Agenda • BGP Flowspec Overview • BGP Flowspec case study • JANOG 35 Q&A 2 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
DDOS Traffic are always changing… http: //www. digitalattackmap. com/ 3 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
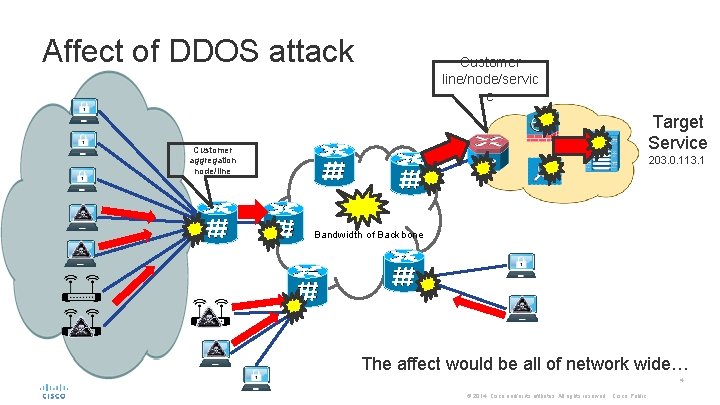
Affect of DDOS attack Customer line/node/servic e Target Service Customer aggregation node/line 203. 0. 113. 1 Bandwidth of Backbone The affect would be all of network wide… 4 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
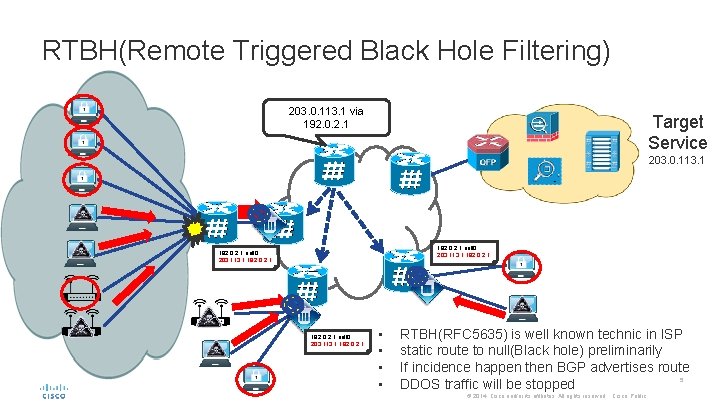
RTBH(Remote Triggered Black Hole Filtering) 203. 0. 113. 1 via 192. 0. 2. 1 Target Service 203. 0. 113. 1 192. 0. 2. 1 null 0 203. 113. 1 192. 0. 2. 1 • • RTBH(RFC 5635) is well known technic in ISP static route to null(Black hole) preliminarily If incidence happen then BGP advertises route 5 DDOS traffic will be stopped © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
Why BGP Flow Specification will be needed § Non DDOS user also would be stopped. § It is difficult to discover/ attempt rule against DDOS attack which rapidly change and increasing Netflow+BGP Attribute 6 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
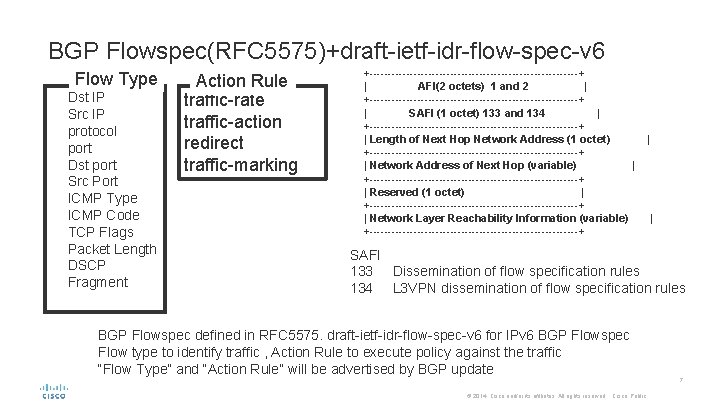
BGP Flowspec(RFC 5575)+draft-ietf-idr-flow-spec-v 6 Flow Type Dst IP Src IP protocol port Dst port Src Port ICMP Type ICMP Code TCP Flags Packet Length DSCP Fragment Action Rule traffic-rate traffic-action redirect traffic-marking +-----------------------------+ | AFI(2 octets) 1 and 2 | +-----------------------------+ | SAFI (1 octet) 133 and 134 | +-----------------------------+ | Length of Next Hop Network Address (1 octet) +-----------------------------+ | Network Address of Next Hop (variable) | +-----------------------------+ | Reserved (1 octet) | +-----------------------------+ | Network Layer Reachability Information (variable) +-----------------------------+ | | SAFI 133 Dissemination of flow specification rules 134 L 3 VPN dissemination of flow specification rules BGP Flowspec defined in RFC 5575. draft-ietf-idr-flow-spec-v 6 for IPv 6 BGP Flowspec Flow type to identify traffic , Action Rule to execute policy against the traffic “Flow Type” and “Action Rule” will be advertised by BGP update © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public 7
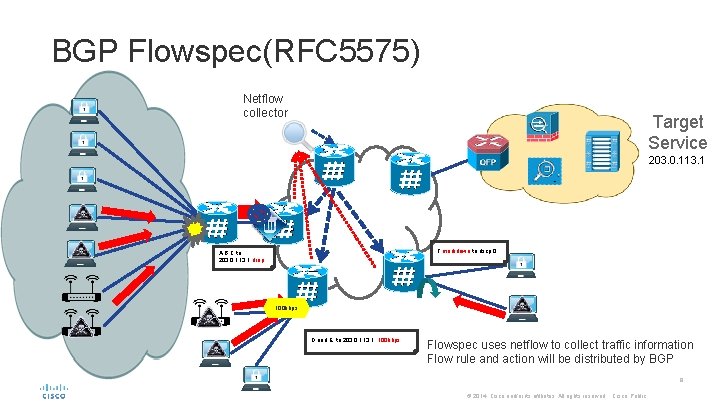
BGP Flowspec(RFC 5575) Netflow collector Target Service 203. 0. 113. 1 F markdown to dscp 0 A, B, C to 203. 0. 113. 1 drop 100 kbps D and E to 203. 0. 113. 1 100 kbps Flowspec uses netflow to collect traffic information Flow rule and action will be distributed by BGP 8 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
Agenda • BGP Flowspec Overview • BGP Flowspec case study • JANOG 35 Q&A 9 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
Flowspec Use case 1 world wide Time Warner Telecom (TWTC) NANOG 38 2006 Deployment Experience With BGP Flow Specification https: //www. nanog. org/meetings/nanog 38/presentations/labovitz-bgp-flowsp • • DDOS Problem • Affect Large/Often to end user • Not only end user but also Infrastructure Risk • OPEX increase DDo. S Analysis • Large DDOS attack by botnet armies/Script Kiddies • TCP Syn Flood greater than 1 Mpps • UDP fragment • Most of Attack source APNIC(Chinese) IP source , difficult to track due to national NAT • Deployed Flowspec for Peer & Transit router from RR • Mitigation from egress point to cleaning vrf • What was missing ? • Multi vendor support (deployed Juniper and Arbor) • Inter-Carrier • Matching DSCP 10 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
Flowspec Use case 2 world wide Neo Telecoms FRNOG 18 2011 Flowspec http: //media. frnog. org/FRn. OG_18 -6. pdf • Compare RTBH/PBR and Flowspec • RTBH(Remote Triggered Black Hole) Website can protect from DDOS attack, but no more traffic on website • PBR(Policy Based Routing) Can control traffic precisely by hardware But need contact to service provide operator to run/remove policy when ddos detect • Flowspec Makes static PBR to dyanmic/Propagate PBR rules/do no need additional communication channel • Deployed Flowspec on transit router Would like to use on e. BGP as architecture but can not trust customer/don’t like to use flow for ebgp session for stability reason • What’s Next • IPv 6 and VPNv 6 support • Traffic Monitoring • More vendors(only Juniper and Alcatel support at that time) 11 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
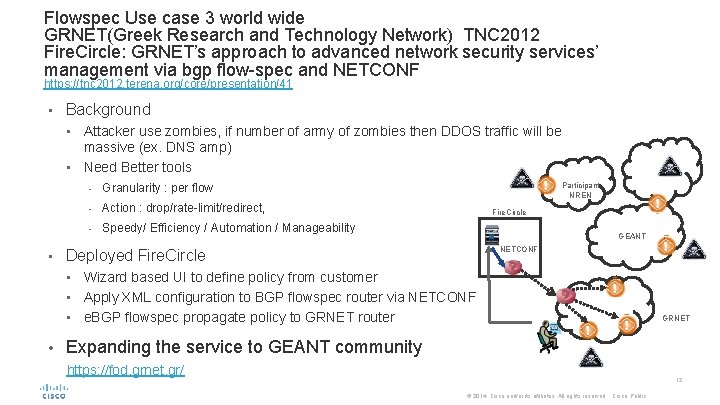
Flowspec Use case 3 world wide GRNET(Greek Research and Technology Network) TNC 2012 Fire. Circle: GRNET’s approach to advanced network security services’ management via bgp flow-spec and NETCONF https: //tnc 2012. terena. org/core/presentation/41 • Background Attacker use zombies, if number of army of zombies then DDOS traffic will be massive (ex. DNS amp) • Need Better tools • • - Granularity : per flow - Action : drop/rate-limit/redirect, - Speedy/ Efficiency / Automation / Manageability Participant NREN Fire. Circle GEANT NETCONF Deployed Fire. Circle Wizard based UI to define policy from customer • Apply XML configuration to BGP flowspec router via NETCONF • e. BGP flowspec propagate policy to GRNET router • • GRNET Expanding the service to GEANT community https: //fod. grnet. gr/ 12 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
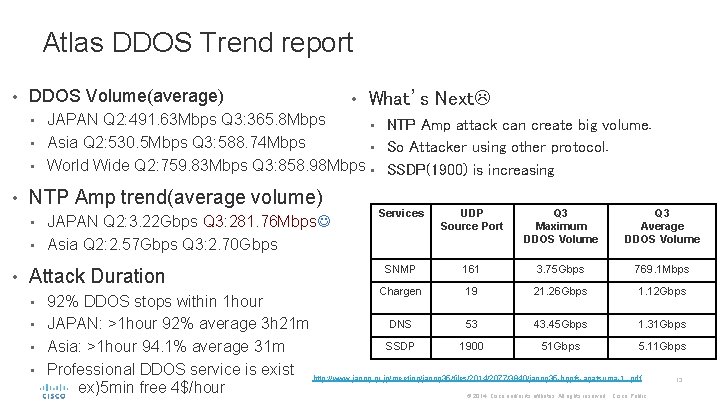
Atlas DDOS Trend report • DDOS Volume(average) • What’s Next JAPAN Q 2: 491. 63 Mbps Q 3: 365. 8 Mbps • NTP Amp attack can create big volume. • Asia Q 2: 530. 5 Mbps Q 3: 588. 74 Mbps • So Attacker using other protocol. • World Wide Q 2: 759. 83 Mbps Q 3: 858. 98 Mbps • SSDP(1900) is increasing • • NTP Amp trend(average volume) JAPAN Q 2: 3. 22 Gbps Q 3: 281. 76 Mbps • Asia Q 2: 2. 57 Gbps Q 3: 2. 70 Gbps • • Attack Duration Services UDP Source Port Q 3 Maximum DDOS Volume Q 3 Average DDOS Volume SNMP 161 3. 75 Gbps 769. 1 Mbps Chargen 19 21. 26 Gbps 1. 12 Gbps 92% DDOS stops within 1 hour DNS 53 43. 45 Gbps 1. 31 Gbps • JAPAN: >1 hour 92% average 3 h 21 m SSDP 1900 51 Gbps 5. 11 Gbps • Asia: >1 hour 94. 1% average 31 m • Professional DDOS service is exist http: //www. janog. gr. jp/meeting/janog 35/files/2014/2077/3840/janog 35 -bgpfs-agatsuma-1. pdf ex)5 min free 4$/hour • 13 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
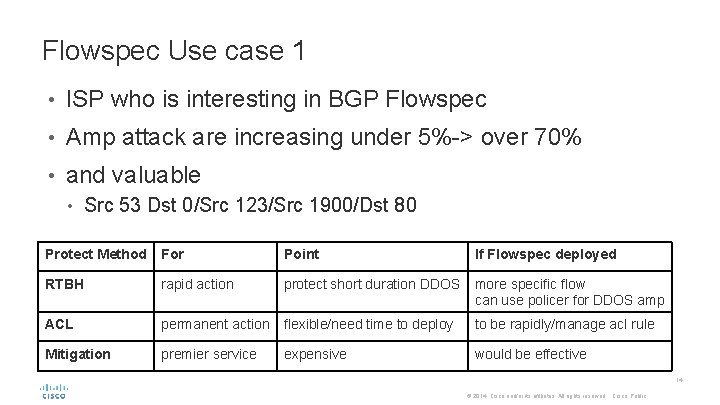
Flowspec Use case 1 • ISP who is interesting in BGP Flowspec • Amp attack are increasing under 5%-> over 70% • and valuable • Src 53 Dst 0/Src 123/Src 1900/Dst 80 Protect Method For Point If Flowspec deployed RTBH rapid action protect short duration DDOS more specific flow can use policer for DDOS amp ACL permanent action flexible/need time to deploy to be rapidly/manage acl rule Mitigation premier service expensive would be effective 14 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
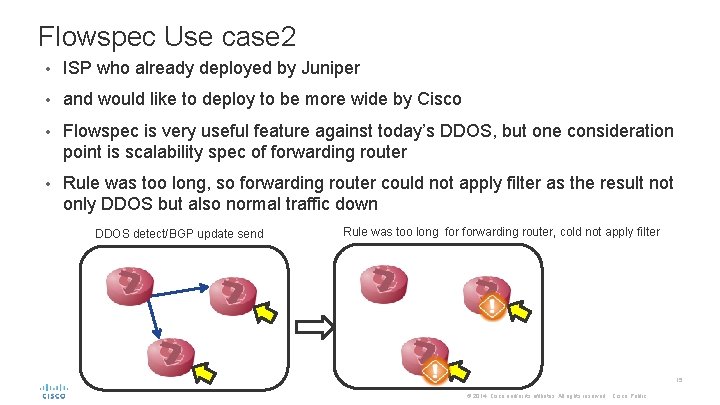
Flowspec Use case 2 • ISP who already deployed by Juniper • and would like to deploy to be more wide by Cisco • Flowspec is very useful feature against today’s DDOS, but one consideration point is scalability spec of forwarding router • Rule was too long, so forwarding router could not apply filter as the result not only DDOS but also normal traffic down DDOS detect/BGP update send Rule was too long forwarding router, cold not apply filter 15 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
Agenda • BGP Flowspec Overview • BGP Flowspec case study • JANOG 35 Q&A 16 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
Discussion summary • JANOG had a session of BGP Flowspec in JANOG 35 Shishio Tsuchiya Shojiro Hirasawa Satoshi Agatsuma Cisco Systems G. K. BIGLOBE Inc. TOYO Corporation http: //www. janog. gr. jp/en/index. php? JANOG 35_Meeting%2 FJANOG 35_Program_Contents%2 FBGPFS http: //www. janog. gr. jp/meeting/janog 35/program/bgpfs/ • Share question/discussion on JANOG 35 meeting 17 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
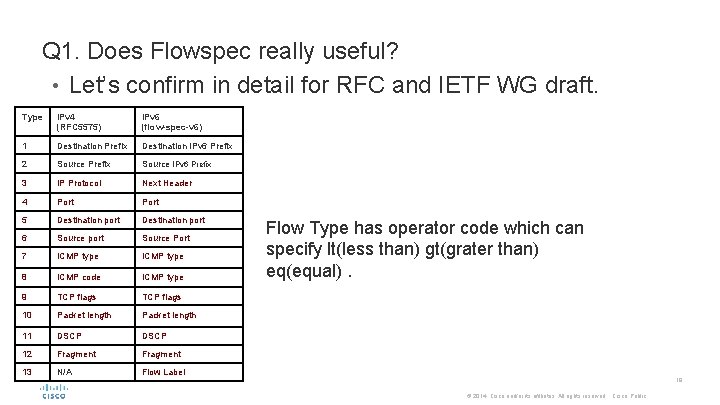
Q 1. Does Flowspec really useful? • Let’s confirm in detail for RFC and IETF WG draft. Type IPv 4 (RFC 5575) IPv 6 (flow-spec-v 6) 1 Destination Prefix Destination IPv 6 Prefix 2 Source Prefix Source IPv 6 Prefix 3 IP Protocol Next Header 4 Port 5 Destination port 6 Source port Source Port 7 ICMP type 8 ICMP code ICMP type 9 TCP flags 10 Packet length 11 DSCP 12 Fragment 13 N/A Flow Label Flow Type has operator code which can specify lt(less than) gt(grater than) eq(equal). 18 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
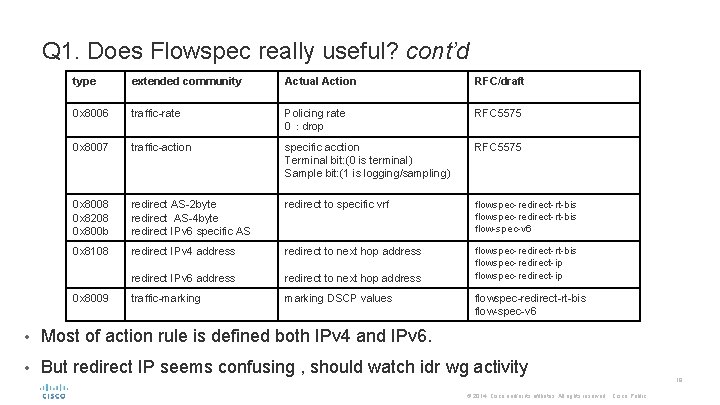
Q 1. Does Flowspec really useful? cont’d type extended community Actual Action RFC/draft 0 x 8006 traffic-rate Policing rate 0:drop RFC 5575 0 x 8007 traffic-action specific acction Terminal bit: (0 is terminal) Sample bit: (1 is logging/sampling) RFC 5575 0 x 8008 0 x 8208 0 x 800 b redirect AS-2 byte redirect AS-4 byte redirect IPv 6 specific AS redirect to specific vrf flowspec-redirect-rt-bis flow-spec-v 6 0 x 8108 redirect IPv 4 address redirect to next hop address redirect IPv 6 address redirect to next hop address flowspec-redirect-rt-bis flowspec-redirect-ip traffic-marking DSCP values 0 x 8009 flowspec-redirect-rt-bis flow-spec-v 6 • Most of action rule is defined both IPv 4 and IPv 6. • But redirect IP seems confusing , should watch idr wg activity © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public 19
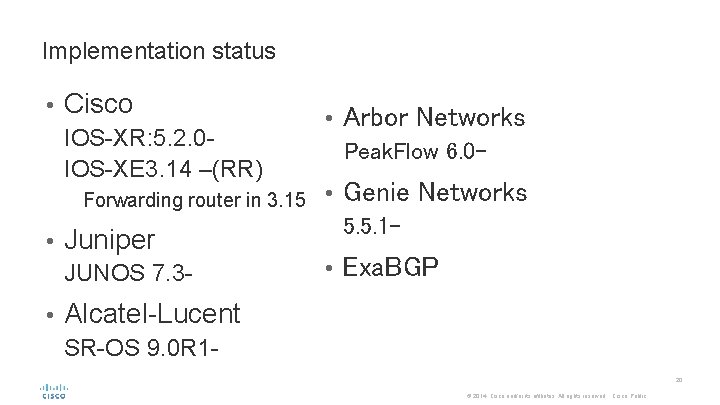
Implementation status • Cisco IOS-XR: 5. 2. 0 IOS-XE 3. 14 –(RR) • Peak. Flow 6. 0 - Forwarding router in 3. 15 • • • Genie Networks 5. 5. 1 - Juniper JUNOS 7. 3 - Arbor Networks • Exa. BGP Alcatel-Lucent SR-OS 9. 0 R 120 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
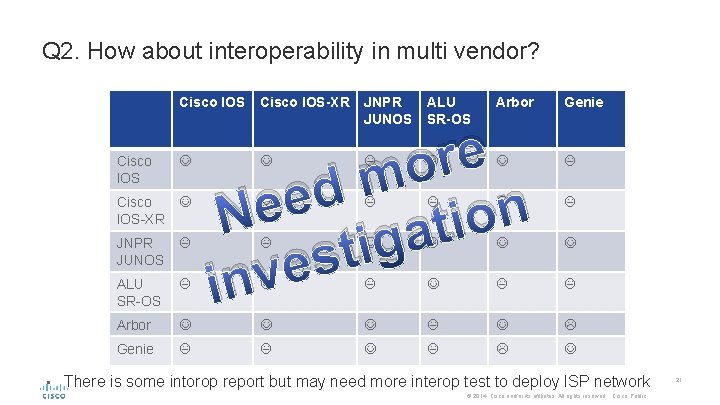
Q 2. How about interoperability in multi vendor? Cisco IOS • Cisco IOS-XR JNPR JUNOS ALU SR-OS Arbor e r o m d e e n N o i t a g i t s e inv Genie Cisco IOS-XR JNPR JUNOS ALU SR-OS Arbor Genie There is some intorop report but may need more interop test to deploy ISP network © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public 21
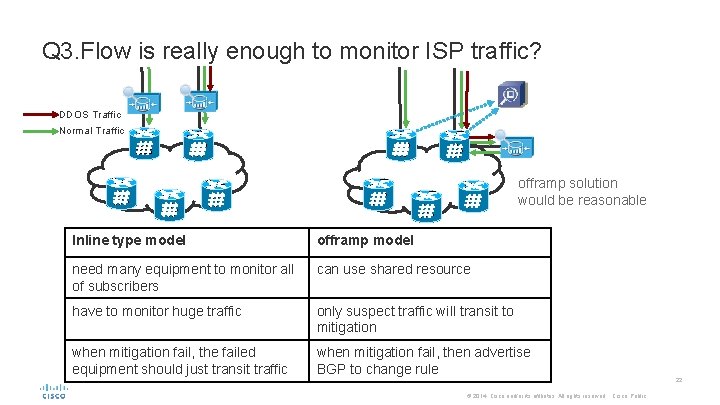
Q 3. Flow is really enough to monitor ISP traffic? DDOS Traffic Normal Traffic offramp solution would be reasonable Inline type model offramp model need many equipment to monitor all of subscribers can use shared resource have to monitor huge traffic only suspect traffic will transit to mitigation when mitigation fail, the failed equipment should just transit traffic when mitigation fail, then advertise BGP to change rule © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public 22
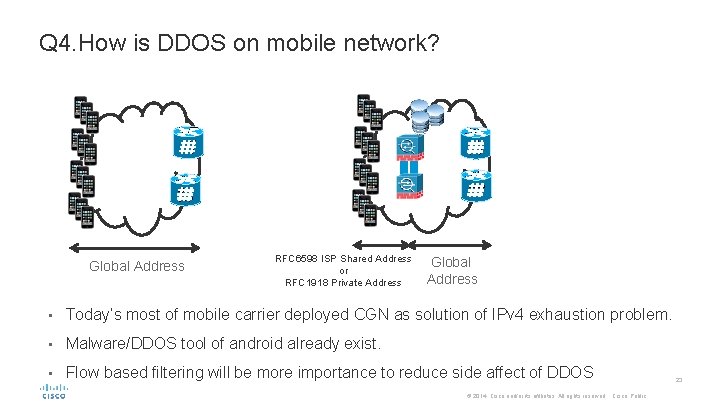
Q 4. How is DDOS on mobile network? Global Address RFC 6598 ISP Shared Address or RFC 1918 Private Address Global Address • Today’s most of mobile carrier deployed CGN as solution of IPv 4 exhaustion problem. • Malware/DDOS tool of android already exist. • Flow based filtering will be more importance to reduce side affect of DDOS © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public 23
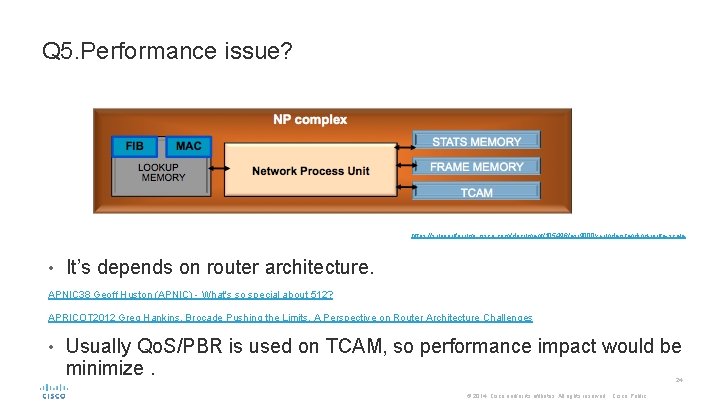
Q 5. Performance issue? https: //supportforums. cisco. com/document/105496/asr 9000 xr-understanding-route-scale • It’s depends on router architecture. APNIC 38 Geoff Huston (APNIC) - What's so special about 512? APRICOT 2012 Greg Hankins, Brocade Pushing the Limits, A Perspective on Router Architecture Challenges • Usually Qo. S/PBR is used on TCAM, so performance impact would be minimize. 24 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
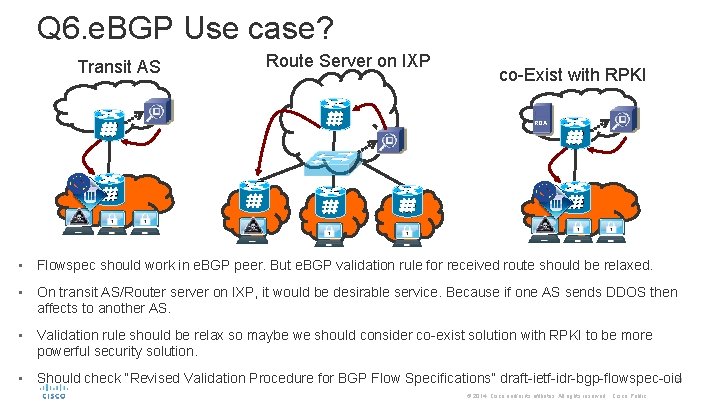
Q 6. e. BGP Use case? Transit AS Route Server on IXP co-Exist with RPKI ROA • Flowspec should work in e. BGP peer. But e. BGP validation rule for received route should be relaxed. • On transit AS/Router server on IXP, it would be desirable service. Because if one AS sends DDOS then affects to another AS. • Validation rule should be relax so maybe we should consider co-exist solution with RPKI to be more powerful security solution. • Should check “Revised Validation Procedure for BGP Flow Specifications” draft-ietf-idr-bgp-flowspec-oid 25 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
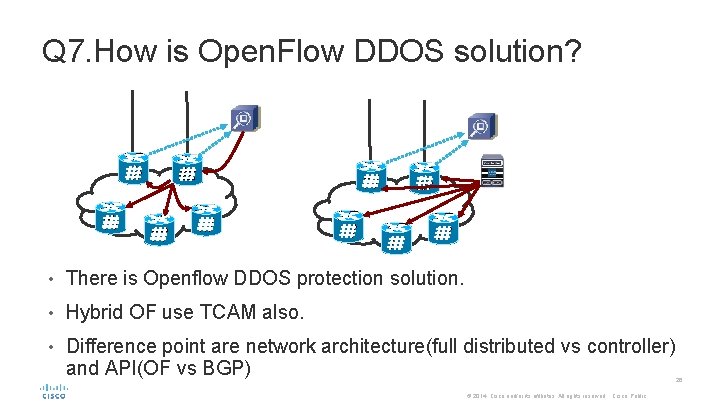
Q 7. How is Open. Flow DDOS solution? • There is Openflow DDOS protection solution. • Hybrid OF use TCAM also. • Difference point are network architecture(full distributed vs controller) and API(OF vs BGP) © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public 26
Summary • Current DDOS are high volume/short duration/amp attack variable and increasing • BGP Flowspec is useful solution against today’s DDOS attack • BGP Flowspec is almost ready to deploy in ISP network. • Need detail implementation information of each of vendors(scalability/nexthop address/IPv 6) and interoperability test result. • e. BGP should work and customer may desire on-demand Firewall/PBR services like a Fire. Circle. 27 © 2014 Cisco and/or its affiliates. All rights reserved. Cisco Public
- Slides: 28