
Authorization workflow 0 User VOMS vomsproxyinit Submission site
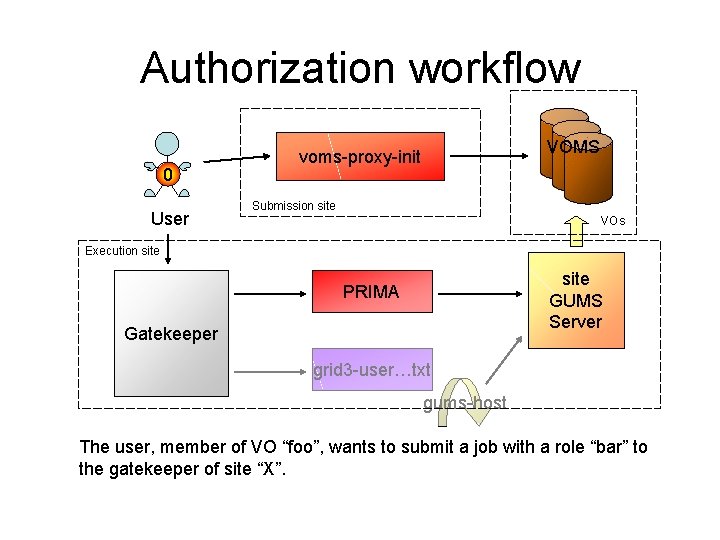
Authorization workflow 0 User VOMS voms-proxy-init Submission site VOs Execution site GUMS Server PRIMA Gatekeeper grid 3 -user…txt gums-host The user, member of VO “foo”, wants to submit a job with a role “bar” to the gatekeeper of site “X”.
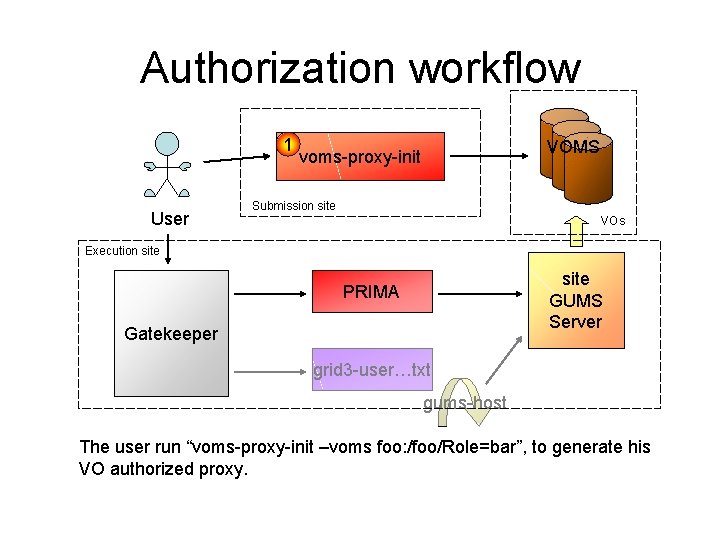
Authorization workflow 1 User VOMS voms-proxy-init Submission site VOs Execution site GUMS Server PRIMA Gatekeeper grid 3 -user…txt gums-host The user run “voms-proxy-init –voms foo: /foo/Role=bar”, to generate his VO authorized proxy.
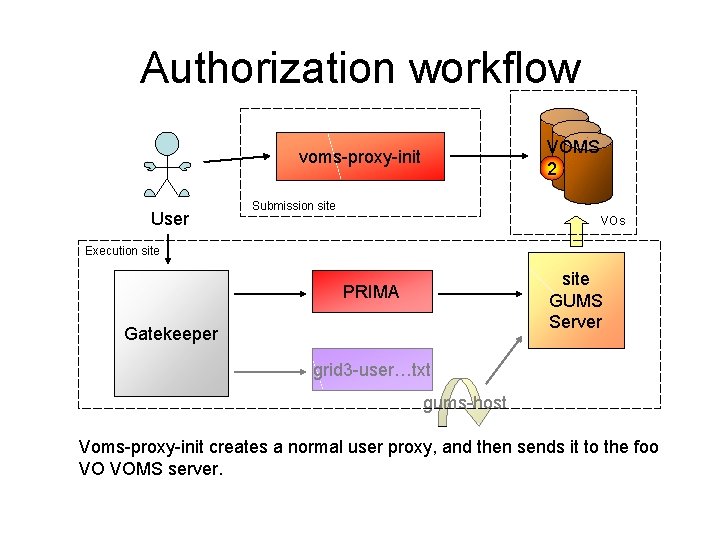
Authorization workflow VOMS 2 voms-proxy-init User Submission site VOs Execution site GUMS Server PRIMA Gatekeeper grid 3 -user…txt gums-host Voms-proxy-init creates a normal user proxy, and then sends it to the foo VO VOMS server.
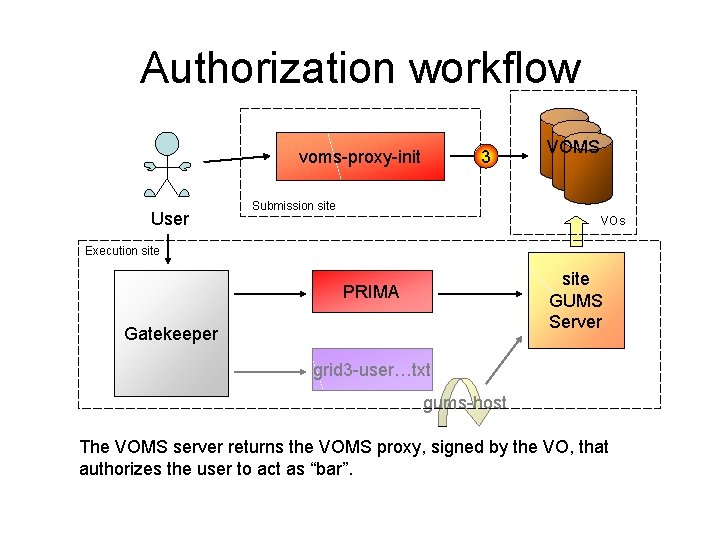
Authorization workflow 3 voms-proxy-init User VOMS Submission site VOs Execution site GUMS Server PRIMA Gatekeeper grid 3 -user…txt gums-host The VOMS server returns the VOMS proxy, signed by the VO, that authorizes the user to act as “bar”.
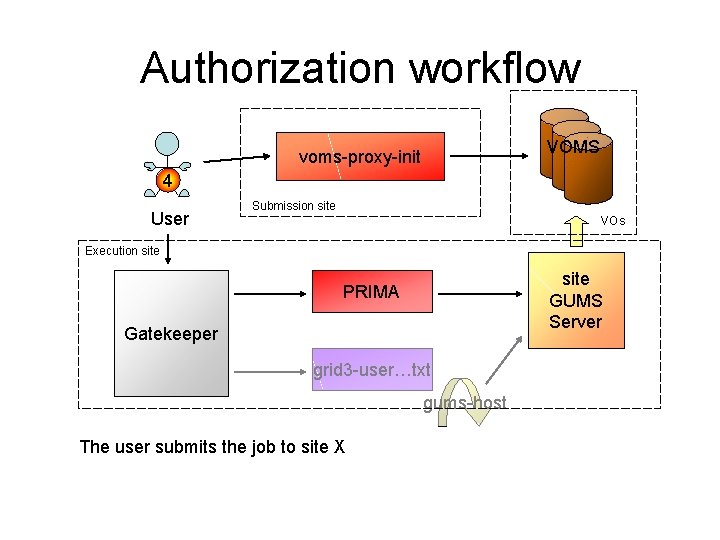
Authorization workflow VOMS voms-proxy-init 4 User Submission site VOs Execution site GUMS Server PRIMA Gatekeeper grid 3 -user…txt gums-host The user submits the job to site X
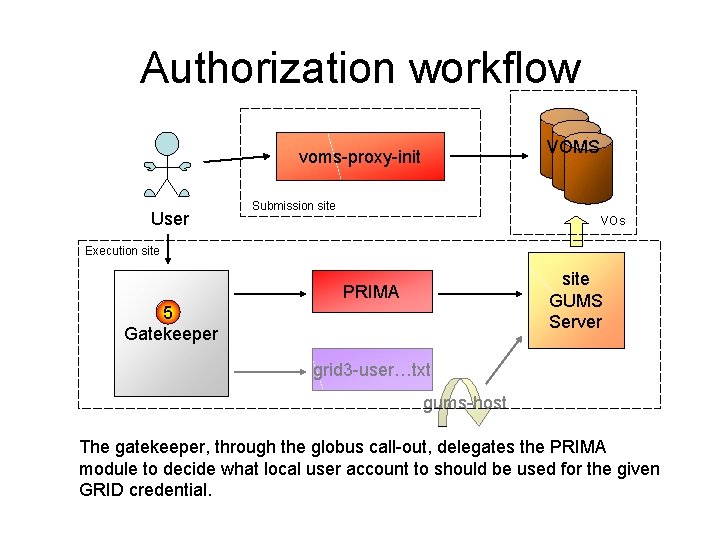
Authorization workflow VOMS voms-proxy-init User Submission site VOs Execution site GUMS Server PRIMA 5 Gatekeeper grid 3 -user…txt gums-host The gatekeeper, through the globus call-out, delegates the PRIMA module to decide what local user account to should be used for the given GRID credential.
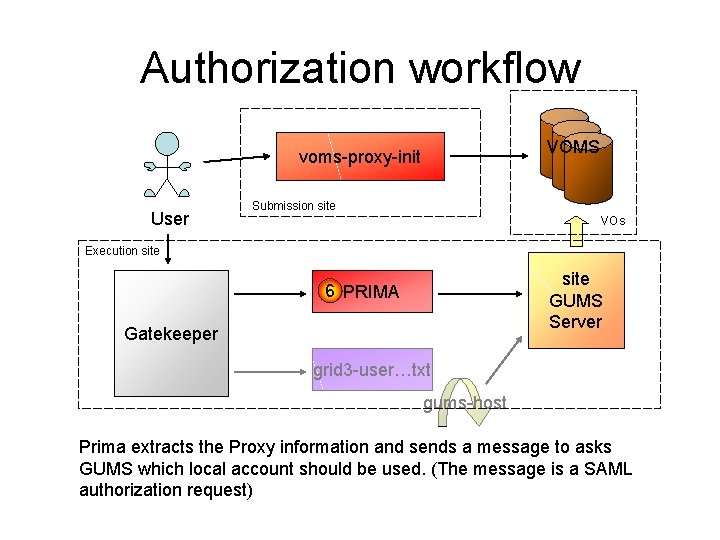
Authorization workflow VOMS voms-proxy-init User Submission site VOs Execution site GUMS Server 6 PRIMA Gatekeeper grid 3 -user…txt gums-host Prima extracts the Proxy information and sends a message to asks GUMS which local account should be used. (The message is a SAML authorization request)
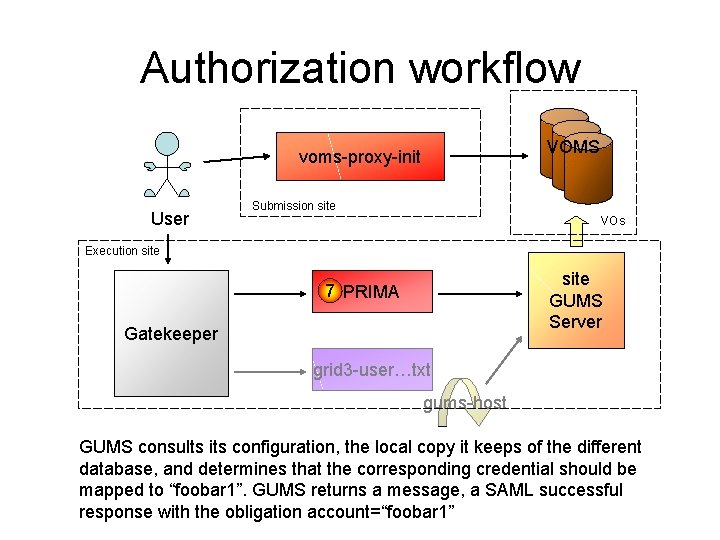
Authorization workflow VOMS voms-proxy-init User Submission site VOs Execution site GUMS Server 7 PRIMA Gatekeeper grid 3 -user…txt gums-host GUMS consults its configuration, the local copy it keeps of the different database, and determines that the corresponding credential should be mapped to “foobar 1”. GUMS returns a message, a SAML successful response with the obligation account=“foobar 1”
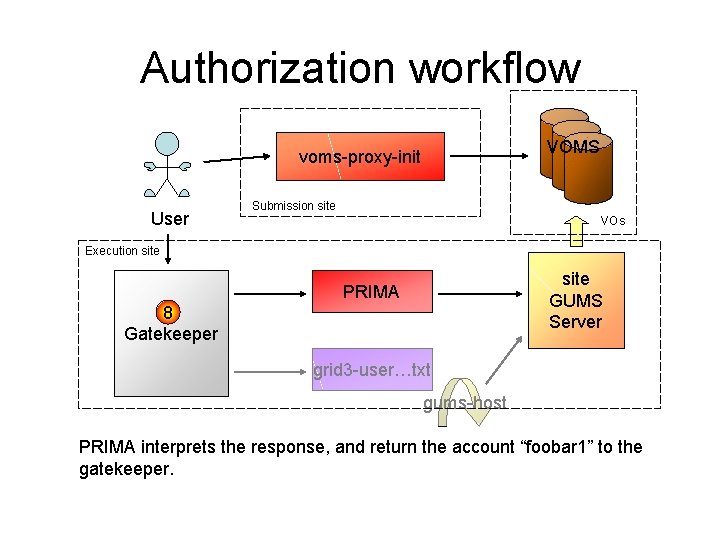
Authorization workflow VOMS voms-proxy-init User Submission site VOs Execution site GUMS Server PRIMA 8 Gatekeeper grid 3 -user…txt gums-host PRIMA interprets the response, and return the account “foobar 1” to the gatekeeper.
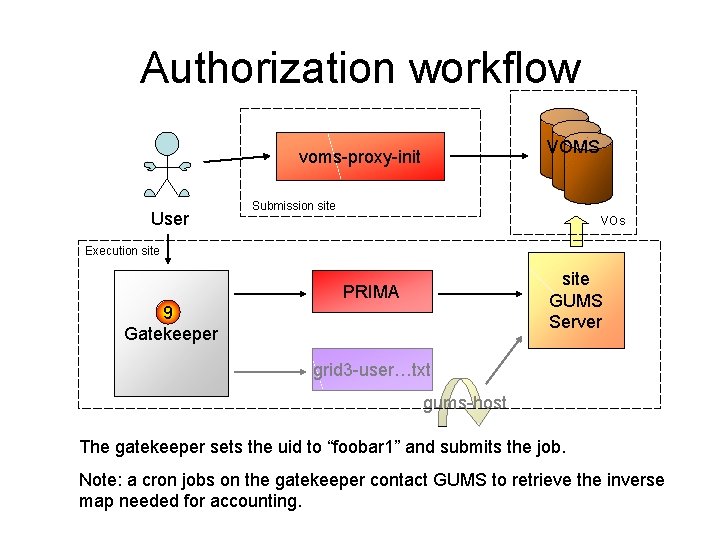
Authorization workflow VOMS voms-proxy-init User Submission site VOs Execution site GUMS Server PRIMA 9 Gatekeeper grid 3 -user…txt gums-host The gatekeeper sets the uid to “foobar 1” and submits the job. Note: a cron jobs on the gatekeeper contact GUMS to retrieve the inverse map needed for accounting.
- Slides: 10