
An update on Hashbased Signatures Andreas Hlsing Trapdoor
An update on Hash-based Signatures Andreas Hülsing
Trapdoor- / Identification Scheme -based (PQ-)Signatures Lattice, MQ, Coding Signature and/or key sizes Runtimes Secure parameters 13 -6 -2021 PAGE 2
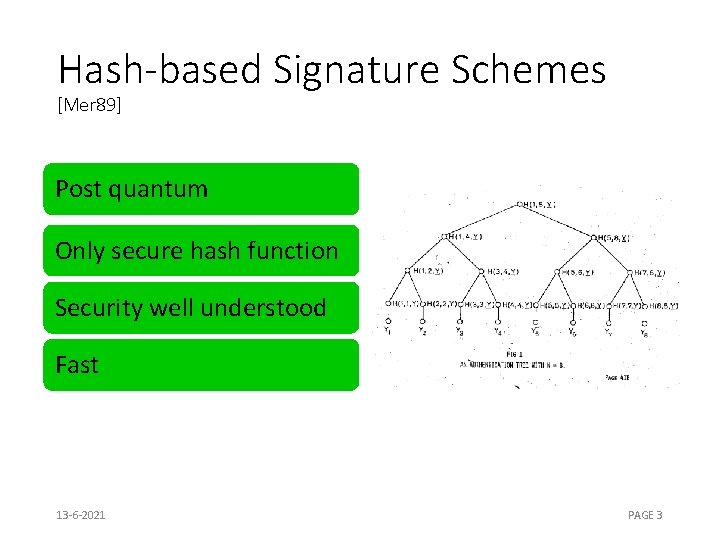
Hash-based Signature Schemes [Mer 89] Post quantum Only secure hash function Security well understood Fast 13 -6 -2021 PAGE 3
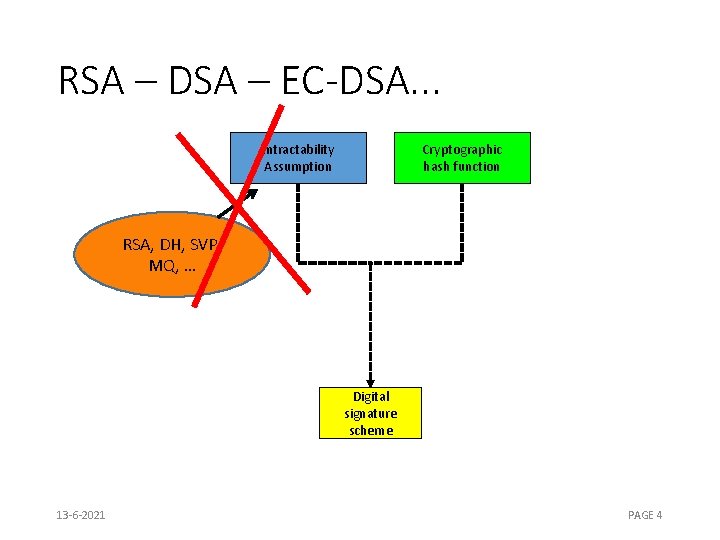
RSA – DSA – EC-DSA. . . Intractability Assumption Cryptographic hash function RSA, DH, SVP, MQ, … Digital signature scheme 13 -6 -2021 PAGE 4
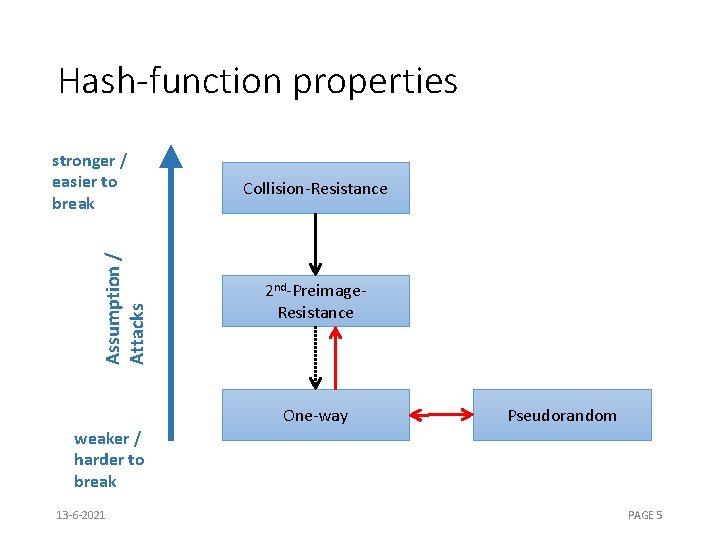
Hash-function properties Assumption / Attacks stronger / easier to break Collision-Resistance 2 nd-Preimage. Resistance One-way Pseudorandom weaker / harder to break 13 -6 -2021 PAGE 5
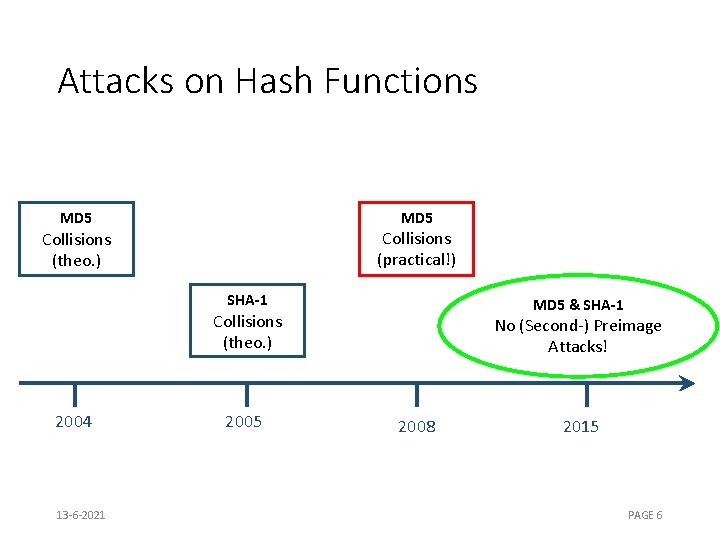
Attacks on Hash Functions MD 5 Collisions (practical!) Collisions (theo. ) SHA-1 MD 5 & SHA-1 Collisions (theo. ) 2004 13 -6 -2021 2005 No (Second-) Preimage Attacks! 2008 2015 PAGE 6
Basic Construction 13 -6 -2021 PAGE 7
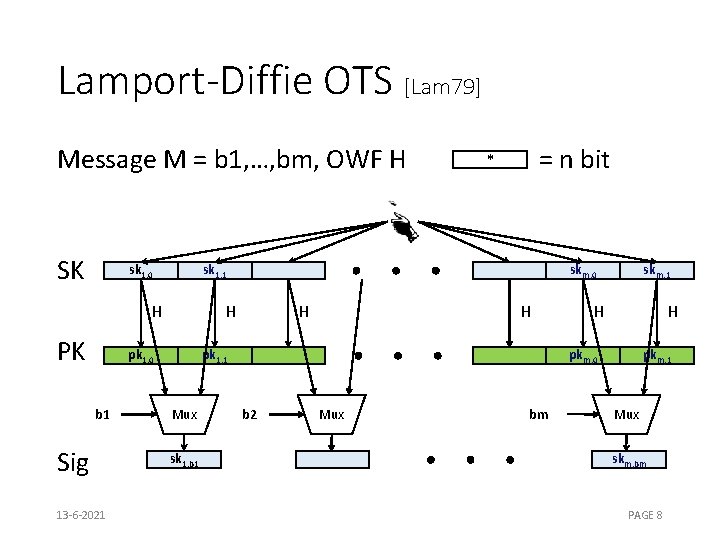
Lamport-Diffie OTS [Lam 79] Message M = b 1, …, bm, OWF H SK sk 1, 0 sk 1, 1 H PK Sig 13 -6 -2021 skm, 0 H pk 1, 0 b 1 = n bit * H H pk 1, 1 Mux sk 1, b 1 skm, 1 H H pkm, 0 b 2 Mux bm pkm, 1 Mux skm, bm PAGE 8
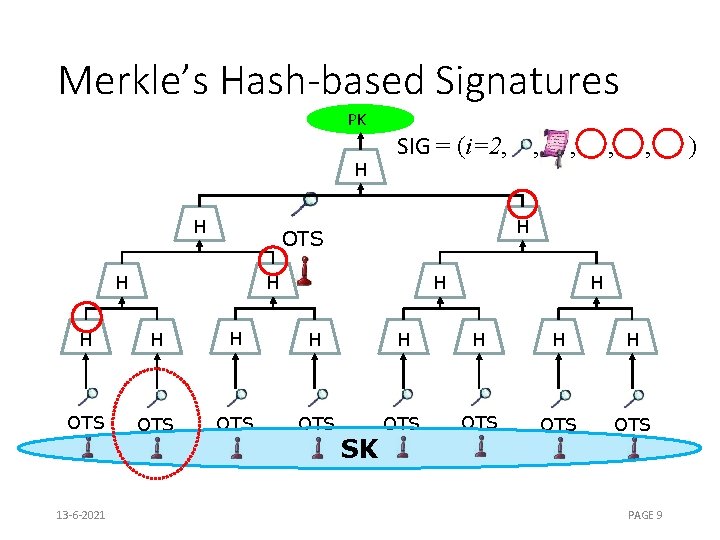
Merkle’s Hash-based Signatures PK H H SIG = (i=2, , H OTS H , H H H OTS OTS 13 -6 -2021 SK PAGE 9 )
Winternitz-OTS
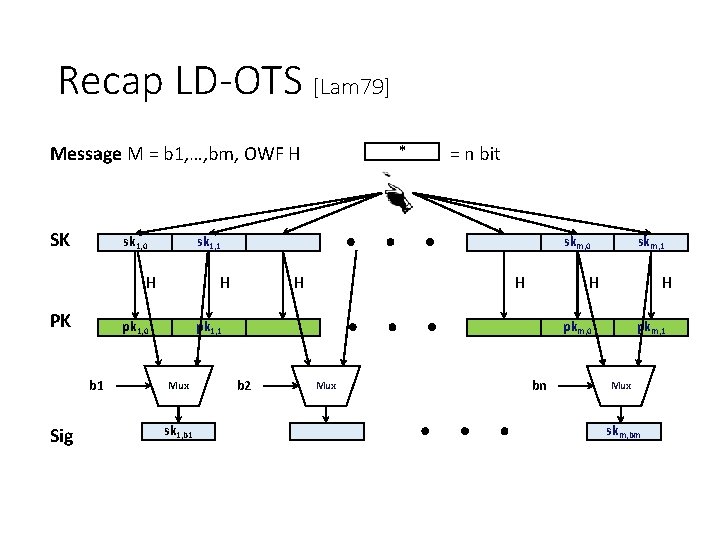
Recap LD-OTS [Lam 79] Message M = b 1, …, bm, OWF H SK sk 1, 0 Sig skm, 0 H pk 1, 0 b 1 = n bit sk 1, 1 H PK * H H H pk 1, 1 Mux sk 1, b 1 skm, 1 H pkm, 0 b 2 Mux bn pkm, 1 Mux skm, bm
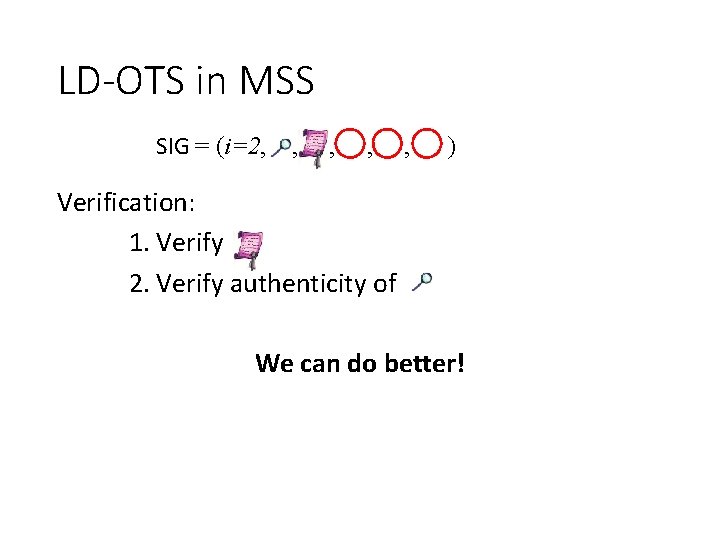
LD-OTS in MSS SIG = (i=2, , , ) Verification: 1. Verify 2. Verify authenticity of We can do better!
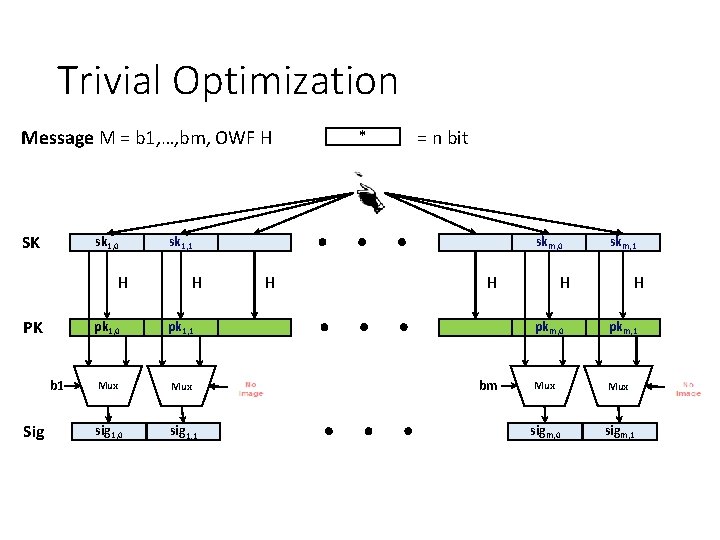
Trivial Optimization Message M = b 1, …, bm, OWF H SK sk 1, 0 H PK b 1 Sig * = n bit sk 1, 1 H pk 1, 0 pk 1, 1 Mux sig 1, 0 sig 1, 1 skm, 0 H H bm skm, 1 H H pkm, 0 pkm, 1 Mux sigm, 0 sigm, 1
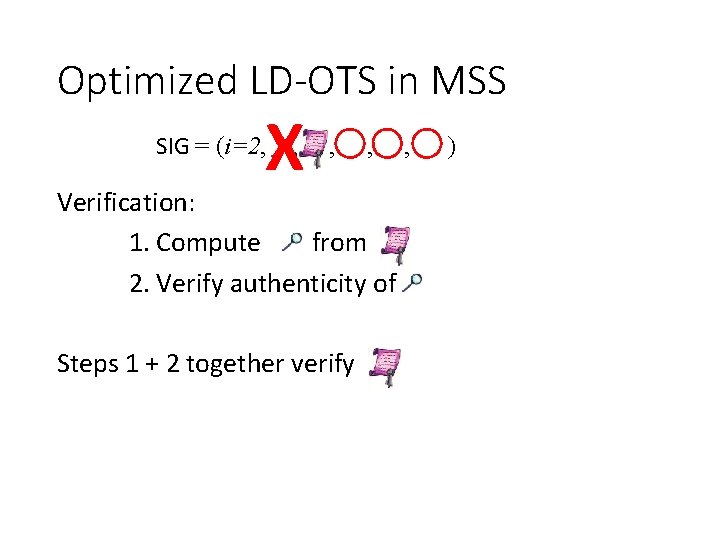
Optimized LD-OTS in MSS X SIG = (i=2, , , , Verification: 1. Compute from 2. Verify authenticity of Steps 1 + 2 together verify , )
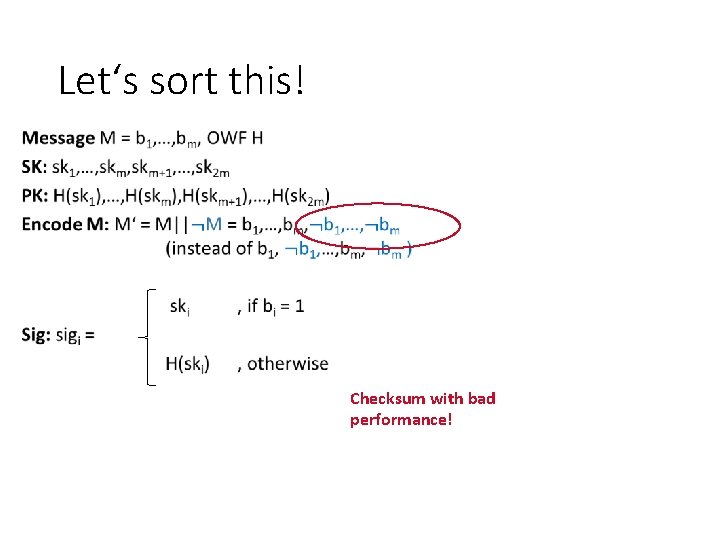
Let‘s sort this! Checksum with bad performance!
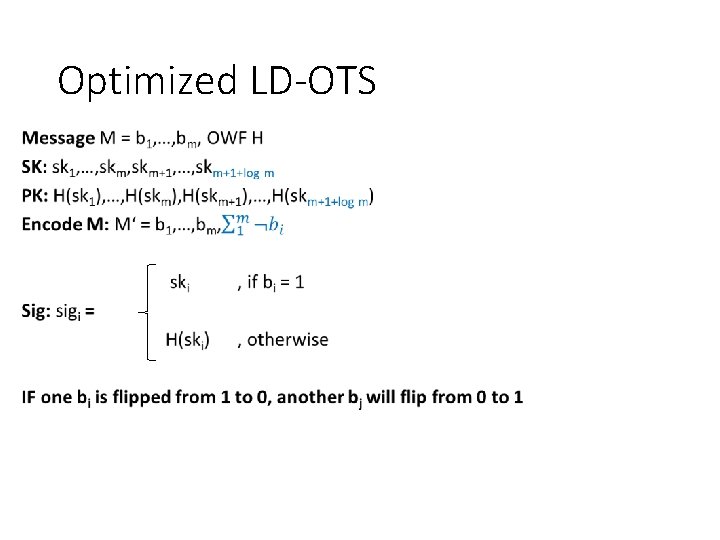
Optimized LD-OTS
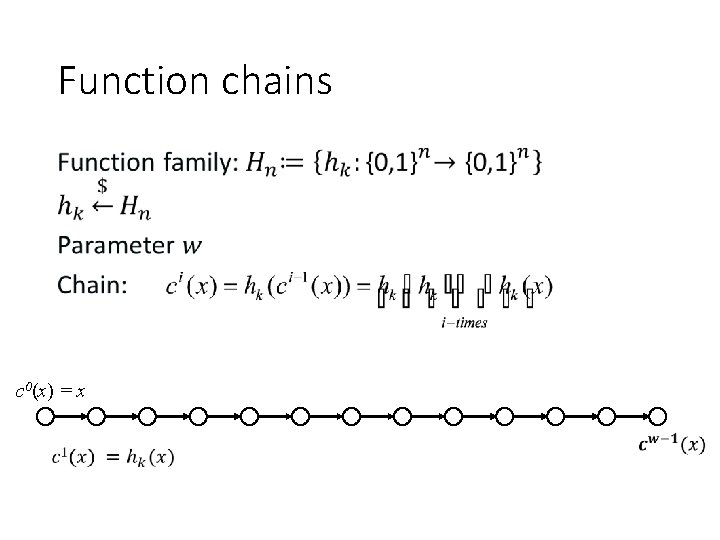
Function chains • c 0(x) = x
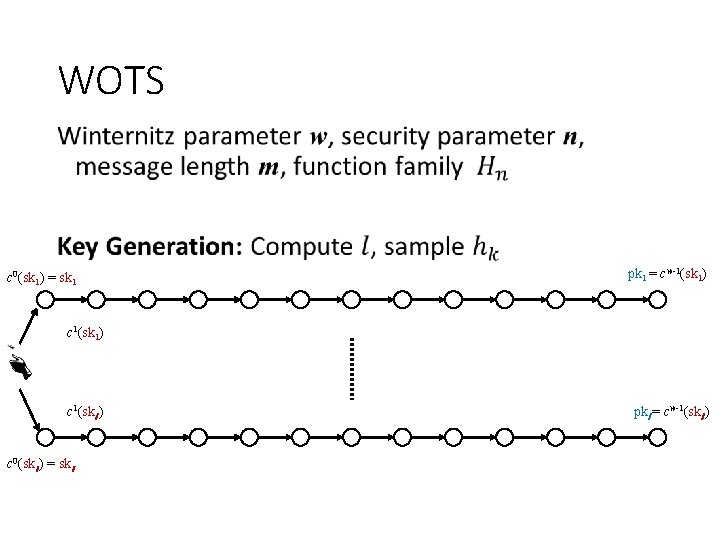
WOTS • c 0(sk 1) = sk 1 pk 1 = cw-1(sk 1) c 1(skl ) c 0(skl ) = skl pkl = cw-1(skl )
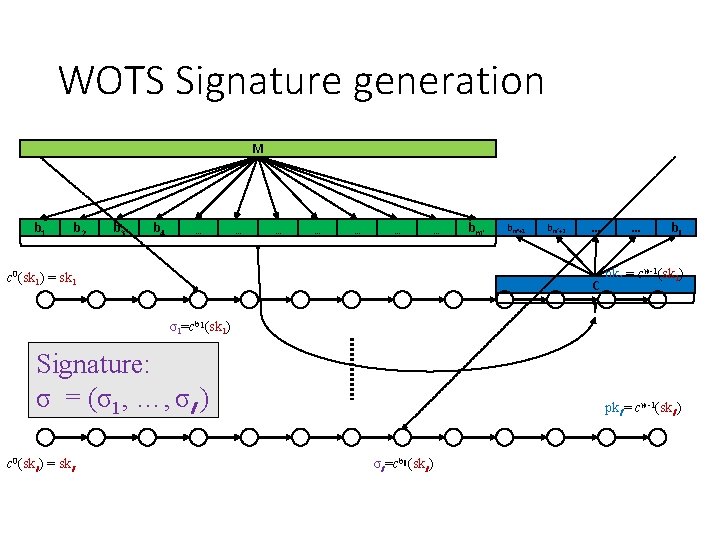
WOTS Signature generation M b 1 b 2 b 3 b 4 … … … … c 0(sk 1) = sk 1 bm‘+1 bm‘+2 … C … bl pk 1 = cw-1(sk 1) σ1=cb 1(sk 1) Signature: σ = (σ1, …, σl ) c 0(skl ) = skl pkl = cw-1(skl ) σl =cbl (skl )
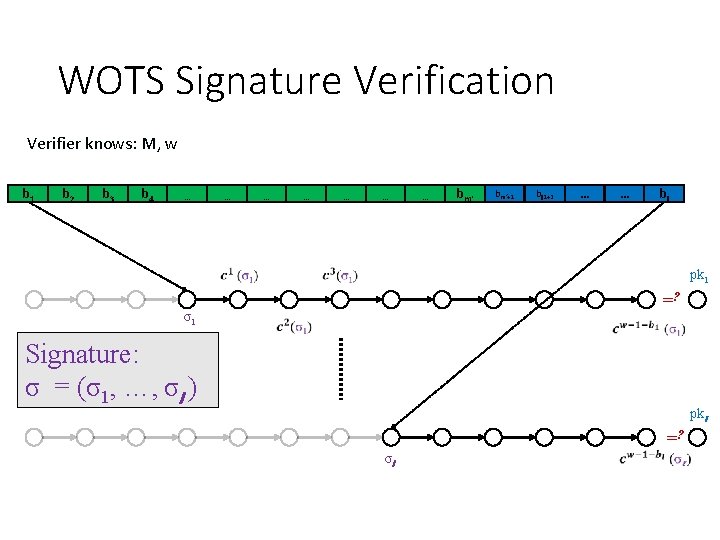
WOTS Signature Verification Verifier knows: M, w b 1 b 2 b 3 b 4 … … … … bm‘+1 bl 1+2 … … bl pk 1 =? σ1 Signature: σ = (σ1, …, σl ) pkl =? σl
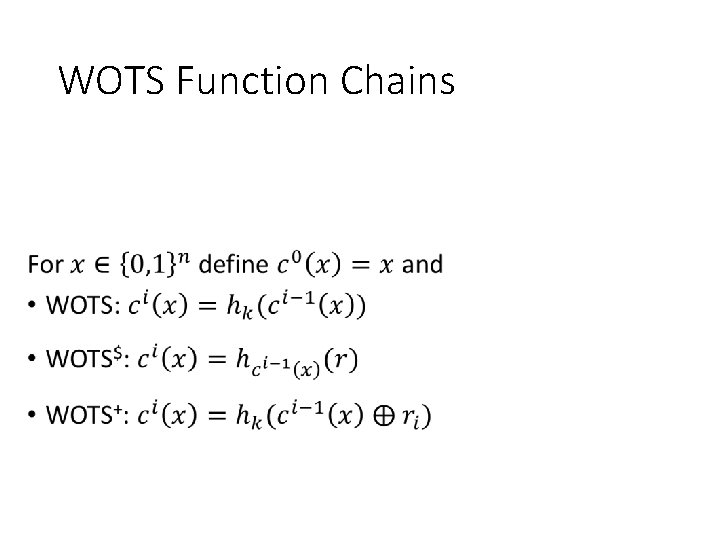
WOTS Function Chains •
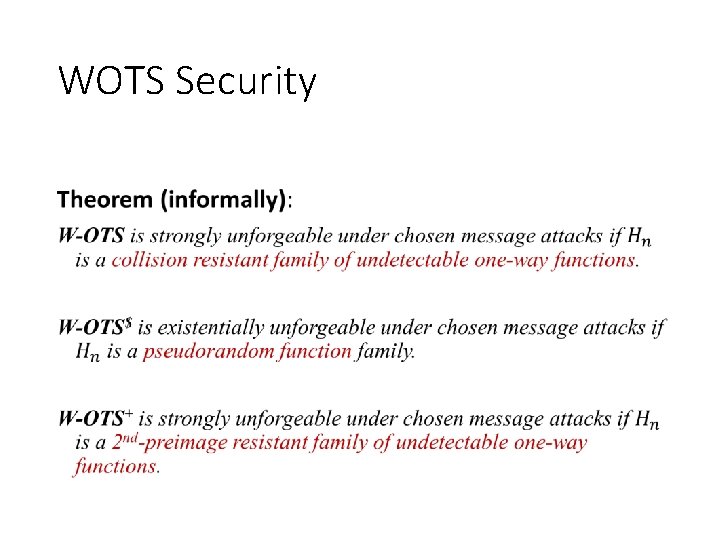
WOTS Security •
Standardizing hash-based signatures. The case of XMSS
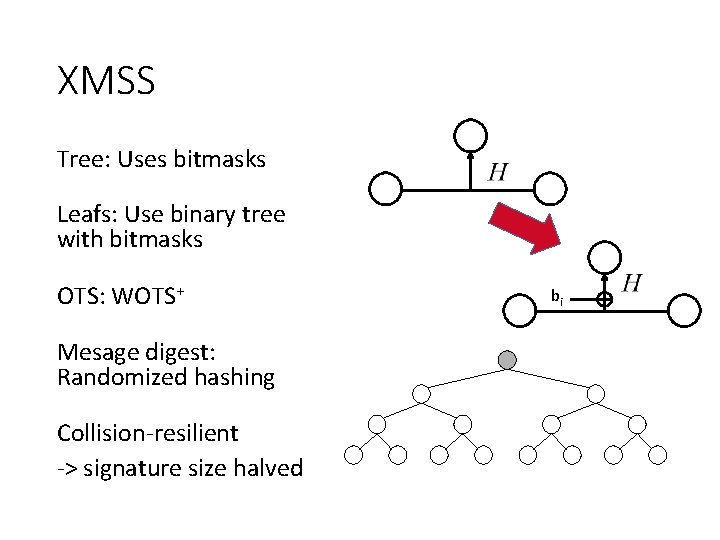
XMSS Tree: Uses bitmasks Leafs: Use binary tree with bitmasks OTS: WOTS+ Mesage digest: Randomized hashing Collision-resilient -> signature size halved bi
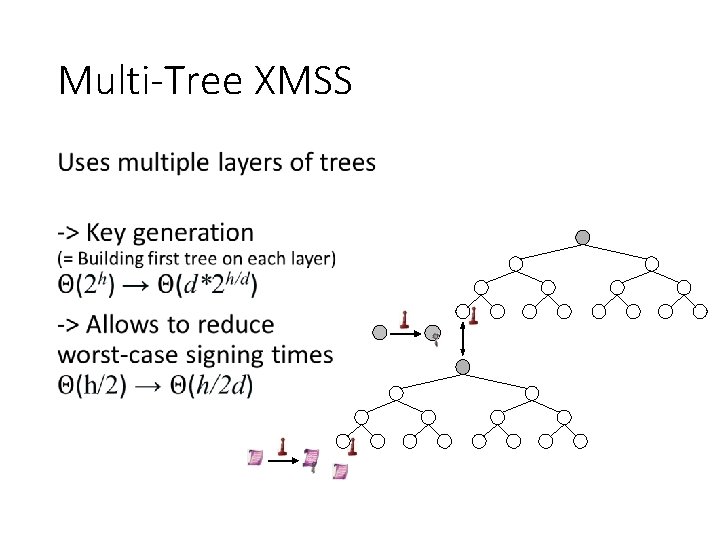
Multi-Tree XMSS •
Multi-target attacks What is the bit security of XMSS using a n = 256 bit hash function? 256 bit? No!
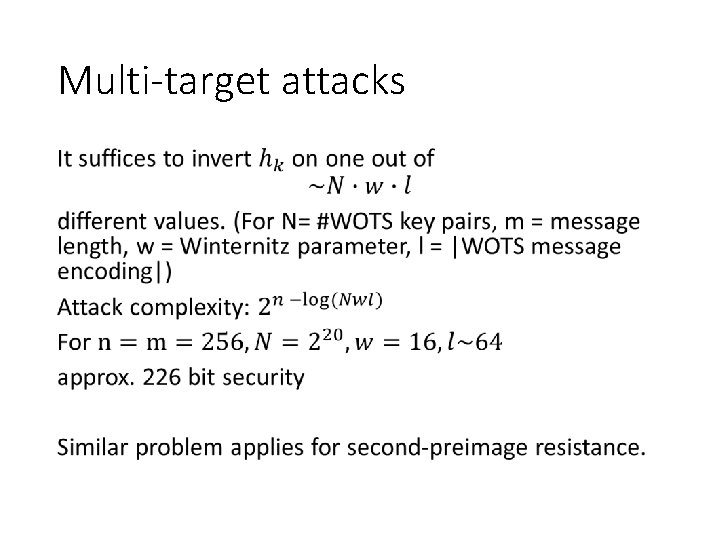
Multi-target attacks •
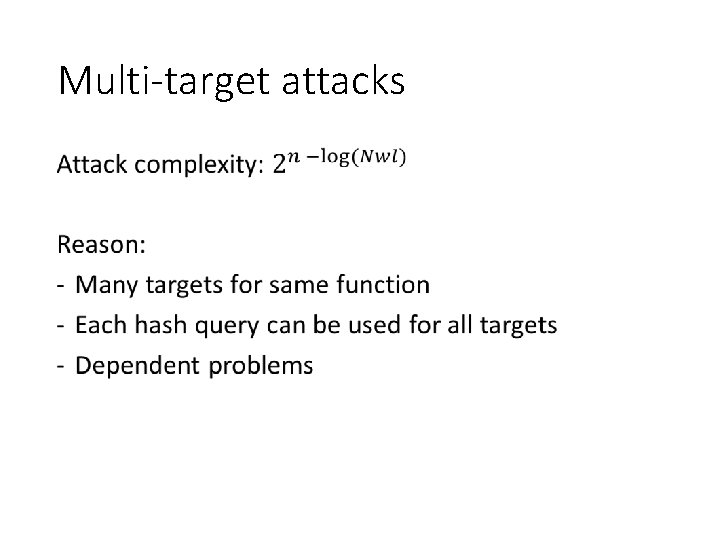
Multi-target attacks •
Solution? Use different elements from function family for each hash (and different bitmasks). - Makes problems independent - Each hash query can only be used for one target!
XMSS-Draft since -01 •
XMSS-Draft since -01 Solution: PRG + Seed in PK Security: - Not really standard model. - Natural but new assumption („Generating the public values using a PRG, the scheme does not get less secure if seed is published. “), - Or ROM
SPHINCS: practical stateless hashbased signatures joint work with Daniel J. Bernstein, Daira Hopwood, Tanja Lange, Ruben Niederhagen, Louiza Papachristodoulou, Michael Schneider, Peter Schwabe, Zooko Wilcox O’Hearn
How to Eliminate the State
Protest? PAGE 34 13 -6 -2021
Few-Time Signature Schemes 13 -6 -2021 PAGE 35
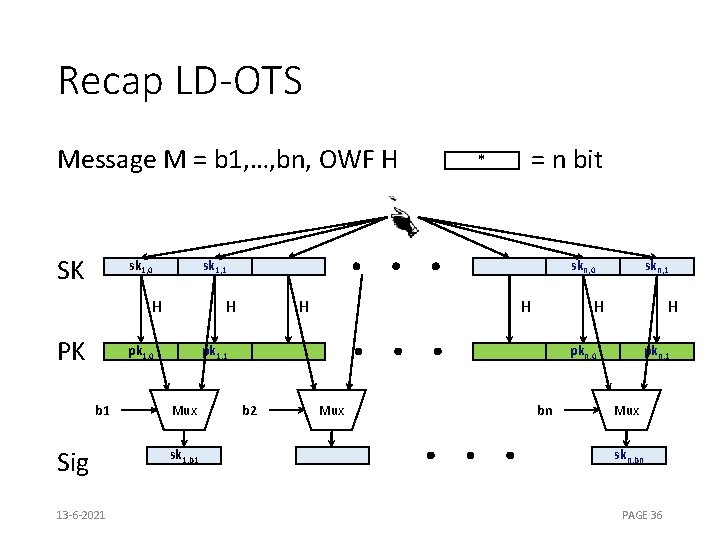
Recap LD-OTS Message M = b 1, …, bn, OWF H SK sk 1, 0 sk 1, 1 H PK Sig 13 -6 -2021 skn, 0 H pk 1, 0 b 1 = n bit * H H H pk 1, 1 Mux sk 1, b 1 skn, 1 H pkn, 0 b 2 Mux bn pkn, 1 Mux skn, bn PAGE 36
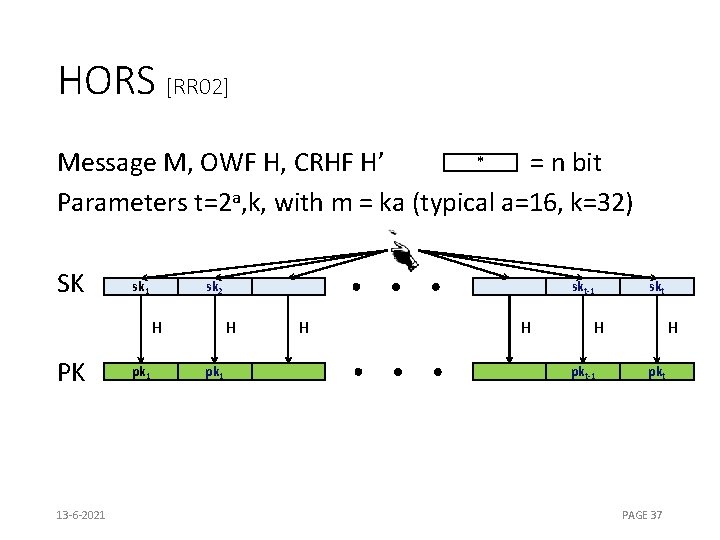
HORS [RR 02] * Message M, OWF H, CRHF H’ = n bit Parameters t=2 a, k, with m = ka (typical a=16, k=32) SK sk 1 sk 2 H PK 13 -6 -2021 pk 1 skt-1 H pk 1 H H skt H pkt-1 H pkt PAGE 37
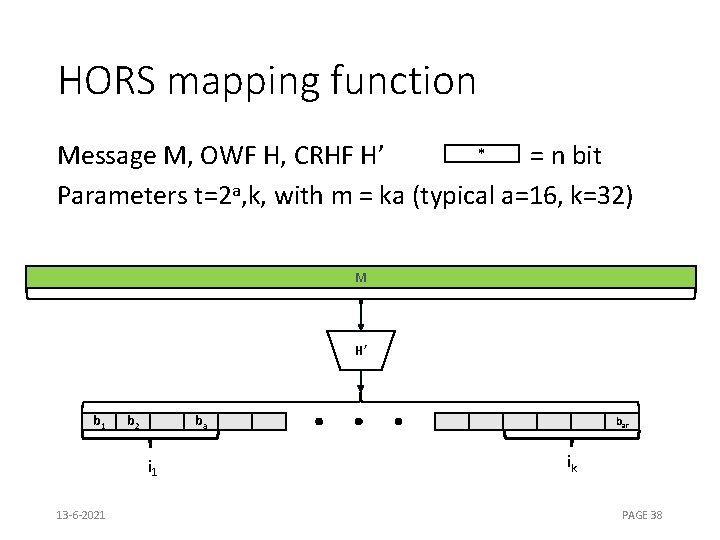
HORS mapping function * Message M, OWF H, CRHF H’ = n bit Parameters t=2 a, k, with m = ka (typical a=16, k=32) M H’ b 1 b 2 ba i 1 13 -6 -2021 bar ik PAGE 38
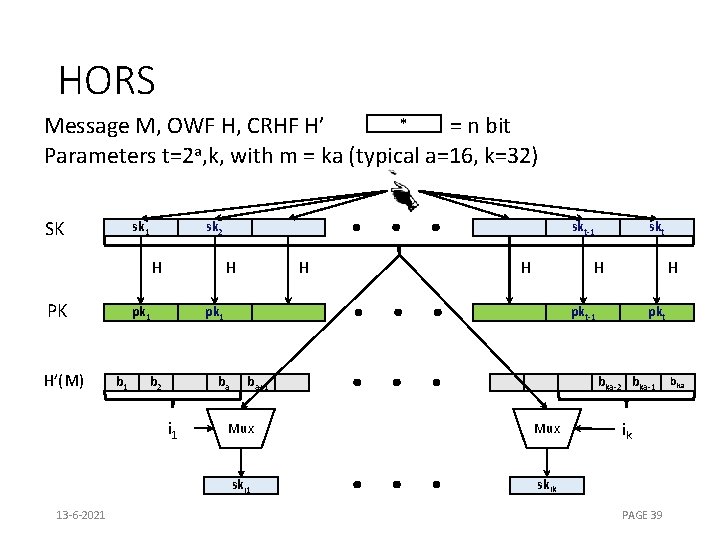
HORS * Message M, OWF H, CRHF H’ = n bit Parameters t=2 a, k, with m = ka (typical a=16, k=32) SK sk 1 sk 2 H PK H’(M) H pk 1 b 1 H H b 2 skt H pk 1 H pkt-1 ba i 1 13 -6 -2021 skt-1 ba+1 pkt bka-2 bka-1 Mux ski 1 skik ik PAGE 39 bka
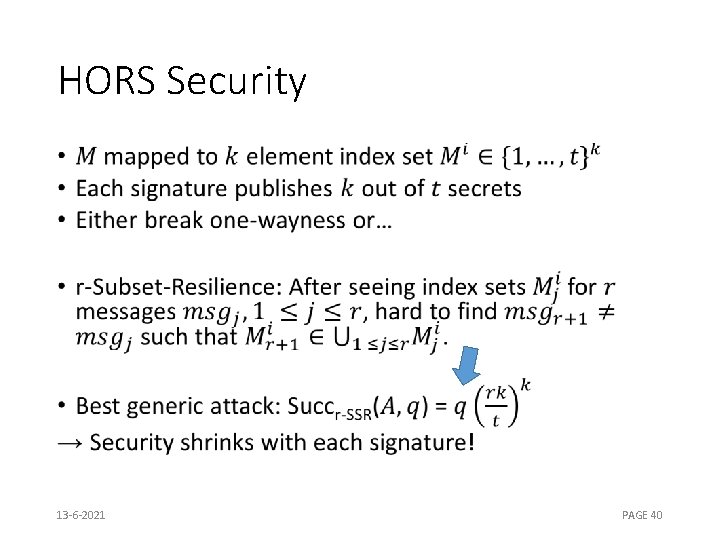
HORS Security • 13 -6 -2021 PAGE 40
HORST Using HORS with MSS requires adding PK (tn) to MSS signature. HORST: Merkle Tree on top of HORS-PK • New PK = Root • Publish Authentication Paths for HORS signature values • PK can be computed from Sig • With optimizations: tn → (k(log t − x + 1) + 2 x)n • E. g. SPHINCS-256: 2 MB → 16 KB • Use randomized message hash 13 -6 -2021 PAGE 41
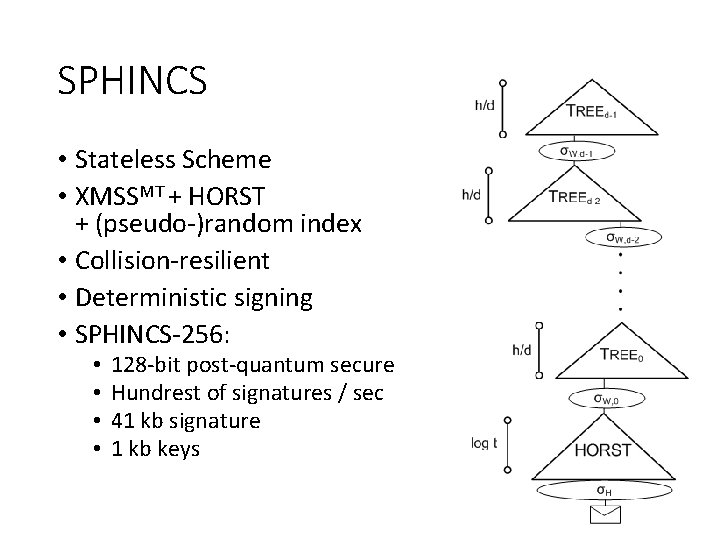
SPHINCS • Stateless Scheme • XMSSMT + HORST + (pseudo-)random index • Collision-resilient • Deterministic signing • SPHINCS-256: • • 128 -bit post-quantum secure Hundrest of signatures / sec 41 kb signature 1 kb keys
Thank you! Questions? For references & further literature see https: //huelsing. wordpress. com/hash-based-signature-schemes/literature/ 13 -6 -2021 PAGE 43
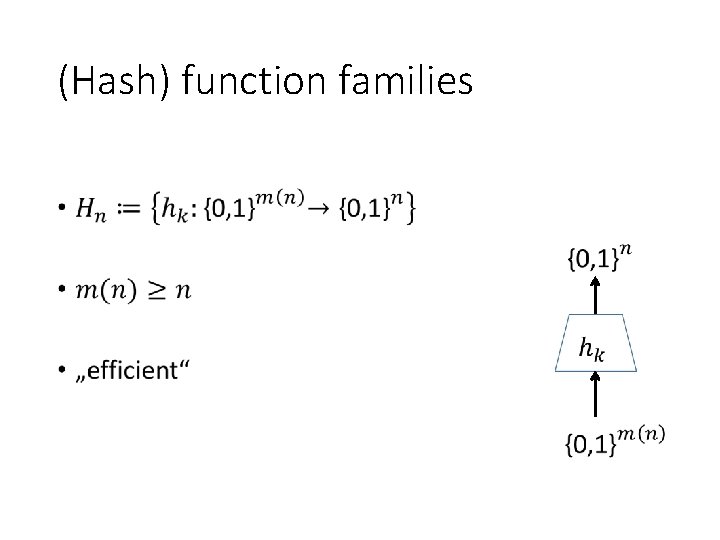
(Hash) function families •
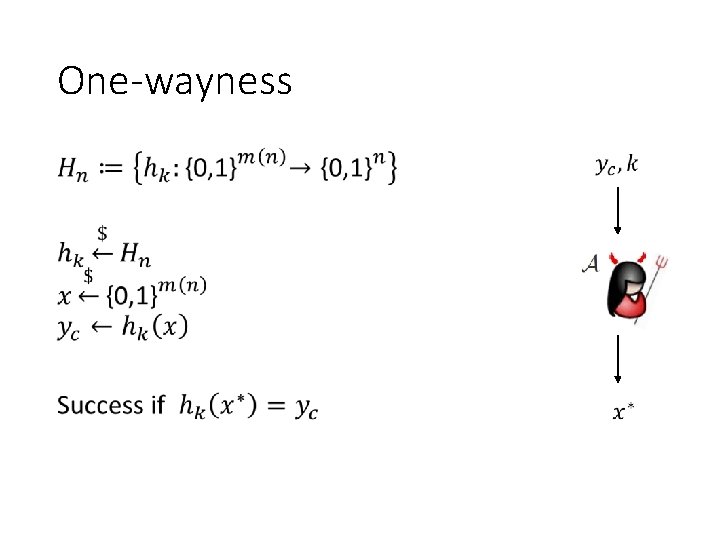
One-wayness •
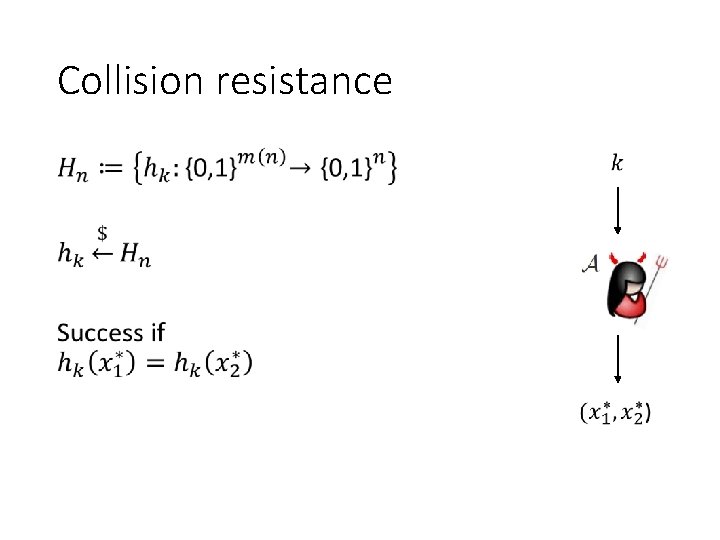
Collision resistance
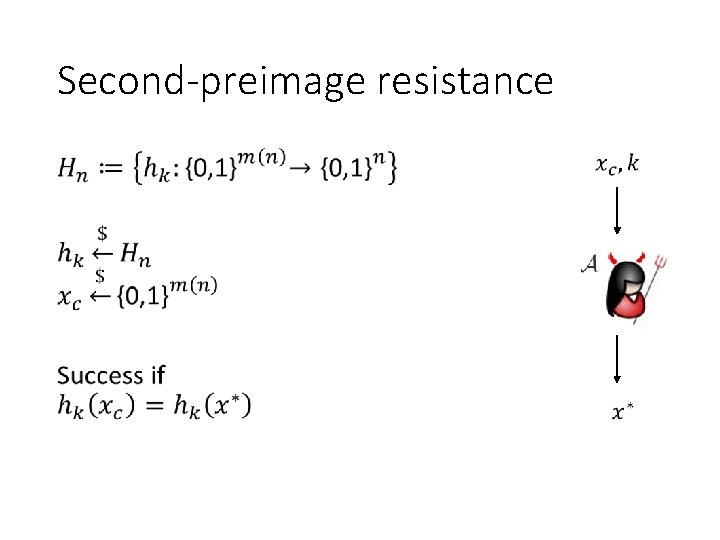
Second-preimage resistance •
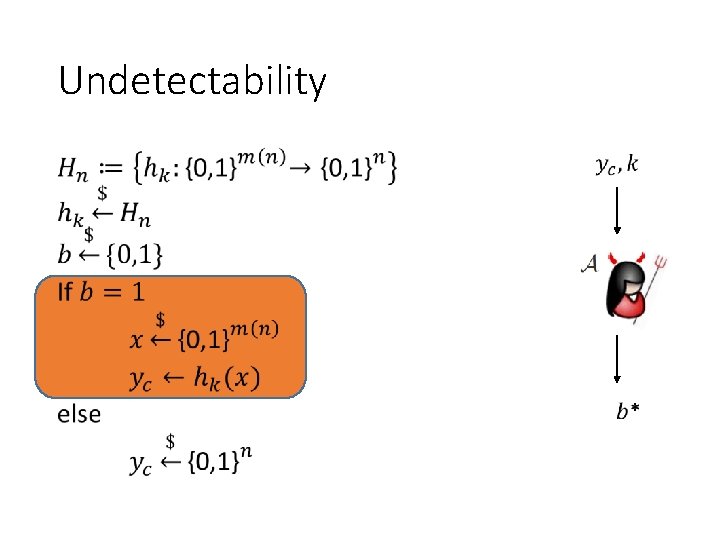
Undetectability •
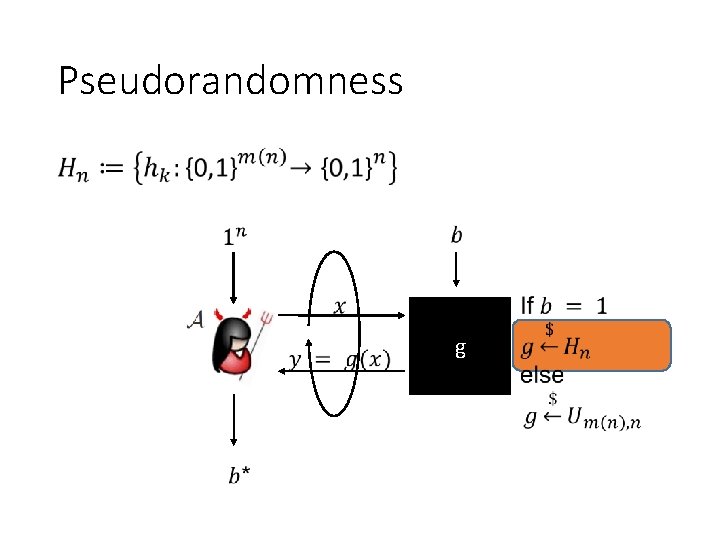
Pseudorandomness • g
- Slides: 49