
Adam Fowler Adelaide Windows User Group A comprehensive

- Slides: 63
Adam Fowler Adelaide Windows User Group
A comprehensive identity and access management cloud solution for your employees, partners, and customers. It combines directory services, advanced identity governance, application access management, and a rich standards-based platform for developers. B 2 E B 2 B B 2 C
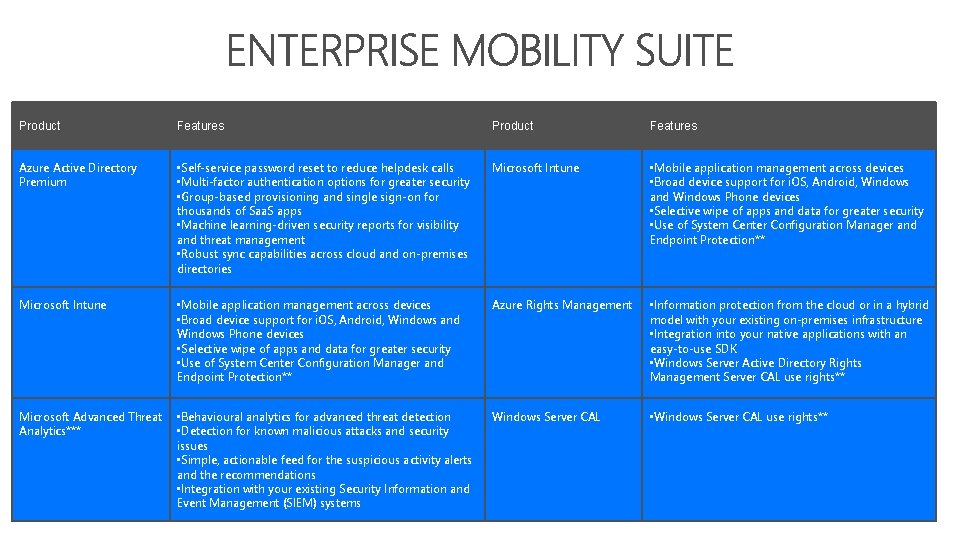
Product Features Azure Active Directory Premium • Self-service password reset to reduce helpdesk calls • Multi-factor authentication options for greater security • Group-based provisioning and single sign-on for thousands of Saa. S apps • Machine learning-driven security reports for visibility and threat management • Robust sync capabilities across cloud and on-premises directories Microsoft Intune • Mobile application management across devices • Broad device support for i. OS, Android, Windows and Windows Phone devices • Selective wipe of apps and data for greater security • Use of System Center Configuration Manager and Endpoint Protection** Azure Rights Management • Information protection from the cloud or in a hybrid model with your existing on-premises infrastructure • Integration into your native applications with an easy-to-use SDK • Windows Server Active Directory Rights Management Server CAL use rights** Microsoft Advanced Threat Analytics*** • Behavioural analytics for advanced threat detection • Detection for known malicious attacks and security issues • Simple, actionable feed for the suspicious activity alerts and the recommendations • Integration with your existing Security Information and Event Management (SIEM) systems Windows Server CAL • Windows Server CAL use rights**
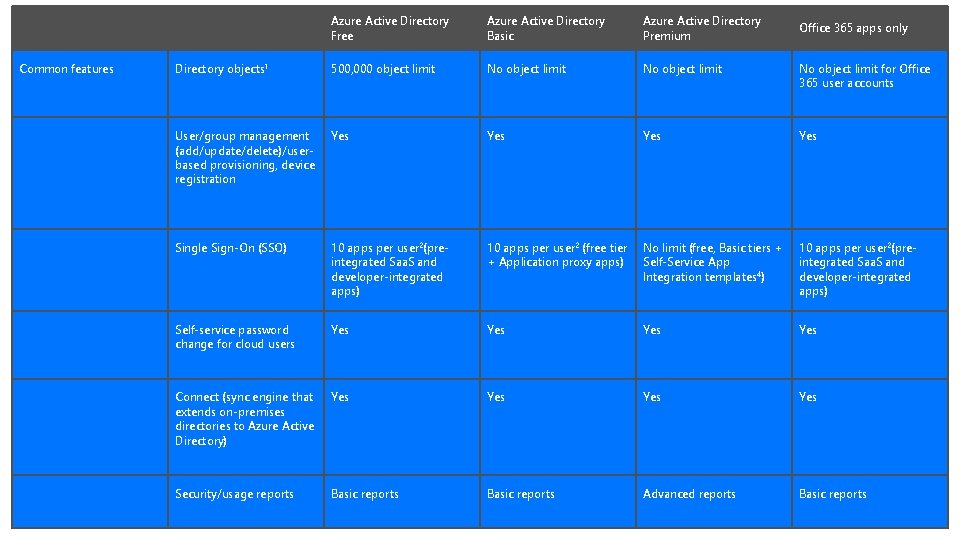
Common features Azure Active Directory Free Azure Active Directory Basic Azure Active Directory Premium Directory objects 1 500, 000 object limit No object limit for Office 365 user accounts User/group management (add/update/delete)/userbased provisioning, device registration Yes Yes Single Sign-On (SSO) 10 apps per user 2(preintegrated Saa. S and developer-integrated apps) 10 apps per user 2 (free tier + Application proxy apps) No limit (free, Basic tiers + Self-Service App Integration templates 4) 10 apps per user 2(preintegrated Saa. S and developer-integrated apps) Self-service password change for cloud users Yes Yes Connect (sync engine that extends on-premises directories to Azure Active Directory) Yes Yes Security/usage reports Basic reports Advanced reports Basic reports Office 365 apps only
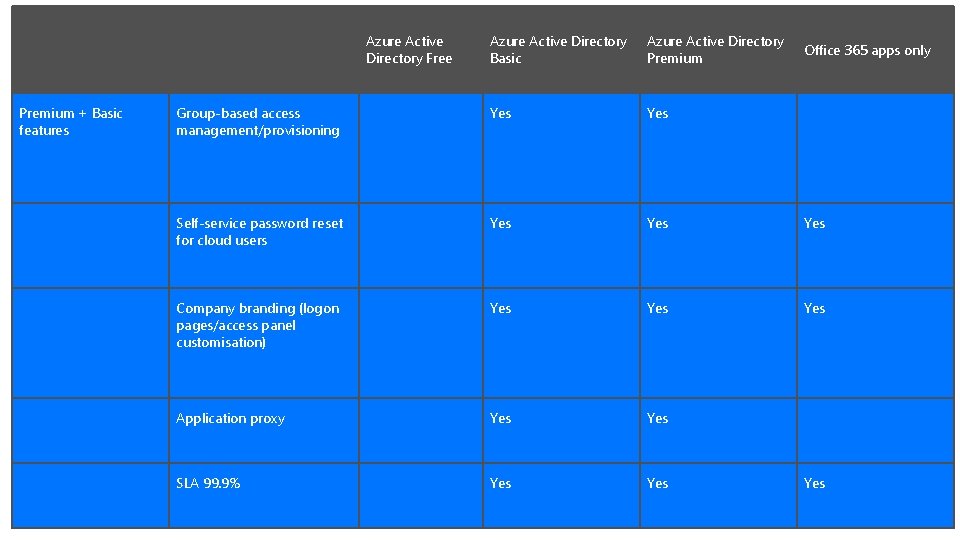
Azure Active Directory Free Premium + Basic features Azure Active Directory Basic Azure Active Directory Premium Group-based access management/provisioning Yes Self-service password reset for cloud users Yes Yes Company branding (logon pages/access panel customisation) Yes Yes Application proxy Yes SLA 99. 9% Yes Office 365 apps only Yes
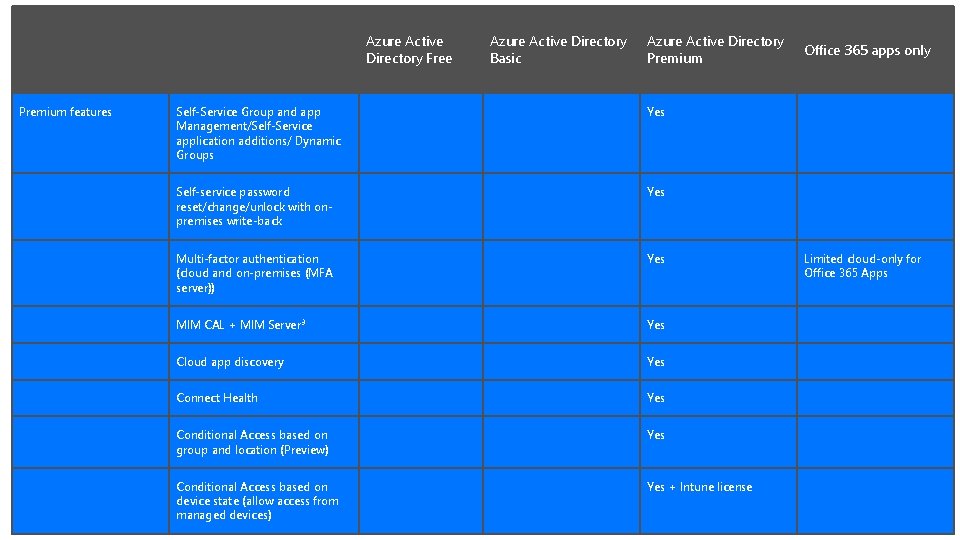
Azure Active Directory Free Premium features Azure Active Directory Basic Azure Active Directory Premium Self-Service Group and app Management/Self-Service application additions/ Dynamic Groups Yes Self-service password reset/change/unlock with onpremises write-back Yes Multi-factor authentication (cloud and on-premises (MFA server)) Yes MIM CAL + MIM Server 3 Yes Cloud app discovery Yes Connect Health Yes Conditional Access based on group and location (Preview) Yes Conditional Access based on device state (allow access from managed devices) Yes + Intune license Office 365 apps only Limited cloud-only for Office 365 Apps
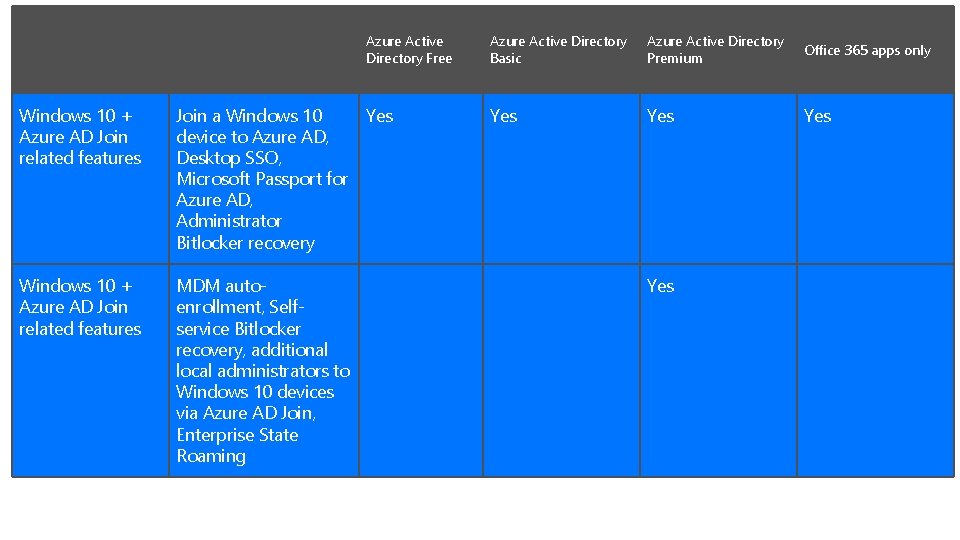
Windows 10 + Azure AD Join related features Join a Windows 10 device to Azure AD, Desktop SSO, Microsoft Passport for Azure AD, Administrator Bitlocker recovery Windows 10 + Azure AD Join related features MDM autoenrollment, Selfservice Bitlocker recovery, additional local administrators to Windows 10 devices via Azure AD Join, Enterprise State Roaming Azure Active Directory Free Azure Active Directory Basic Azure Active Directory Premium Office 365 apps only Yes Yes Yes
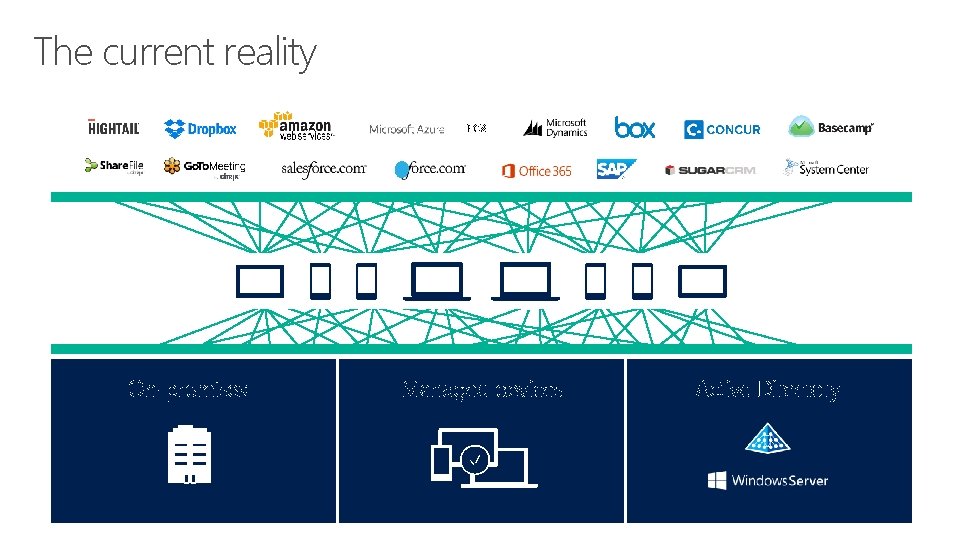
The current reality EC 2 On-premises Managed devices Active Directory
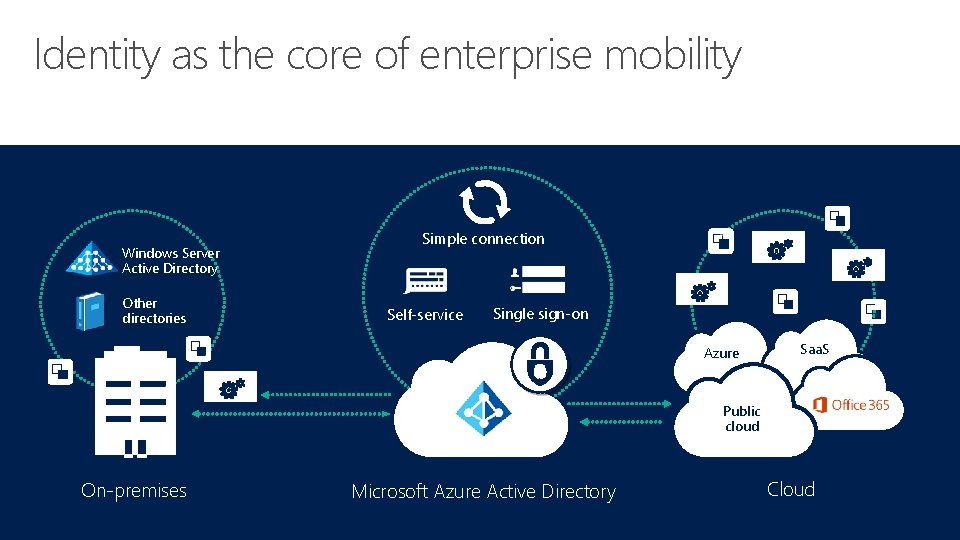
Identity as the core of enterprise mobility Windows Server Active Directory Other directories Simple connection Self-service Single sign-on Azure Saa. S Public cloud On-premises Microsoft Azure Active Directory Cloud
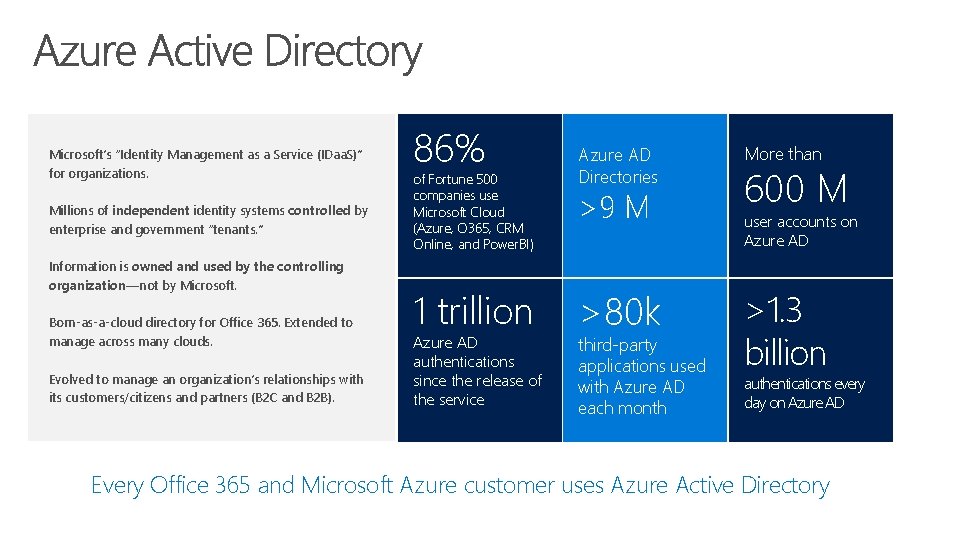
Microsoft’s “Identity Management as a Service (IDaa. S)” for organizations. Millions of independent identity systems controlled by enterprise and government “tenants. ” Information is owned and used by the controlling organization—not by Microsoft. Born-as-a-cloud directory for Office 365. Extended to manage across many clouds. Evolved to manage an organization’s relationships with its customers/citizens and partners (B 2 C and B 2 B). 86% of Fortune 500 companies use Microsoft Cloud (Azure, O 365, CRM Online, and Power. BI) 1 trillion Azure AD authentications since the release of the service Azure AD Directories >9 M >80 k third-party applications used with Azure AD each month More than 600 M user accounts on Azure AD >1. 3 billion authentications every day on Azure AD Every Office 365 and Microsoft Azure customer uses Azure Active Directory
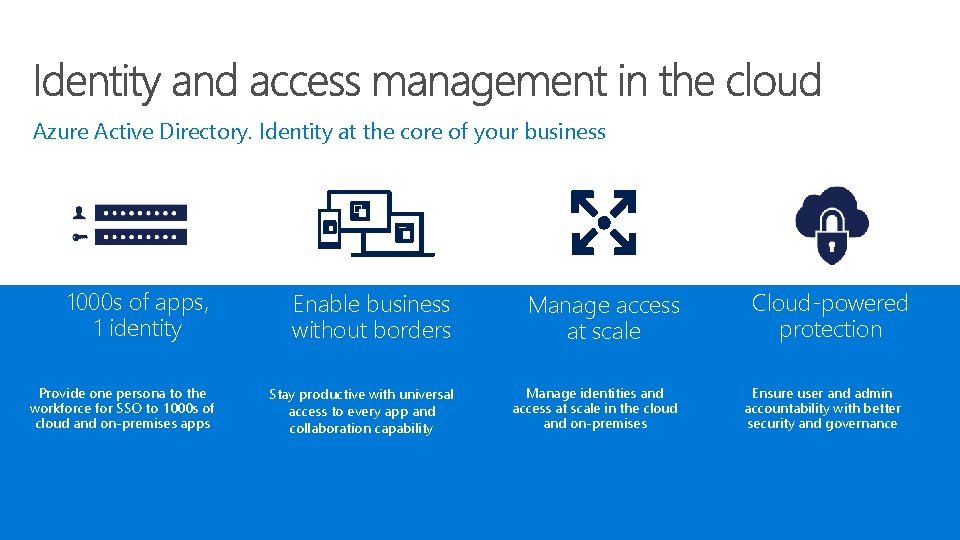
Azure Active Directory. Identity at the core of your business 1000 s of apps, 1 identity Provide one persona to the workforce for SSO to 1000 s of cloud and on-premises apps Enable business without borders Manage access at scale Stay productive with universal access to every app and collaboration capability Manage identities and access at scale in the cloud and on-premises Cloud-powered protection Ensure user and admin accountability with better security and governance
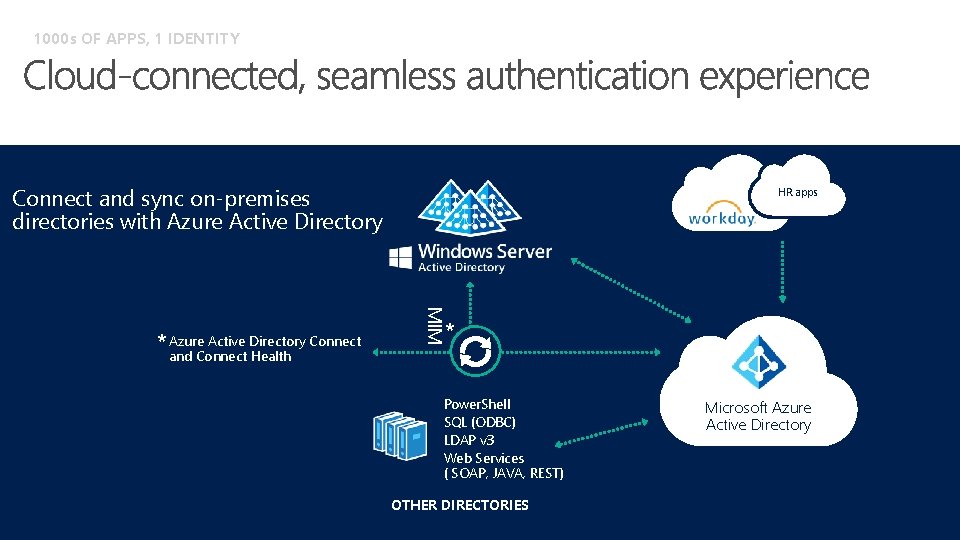
1000 s OF APPS, 1 IDENTITY Connect and sync on-premises directories with Azure Active Directory MIM * Azure Active Directory Connect HR apps * and Connect Health Power. Shell SQL (ODBC) LDAP v 3 Web Services ( SOAP, JAVA, REST) OTHER DIRECTORIES Microsoft Azure Active Directory
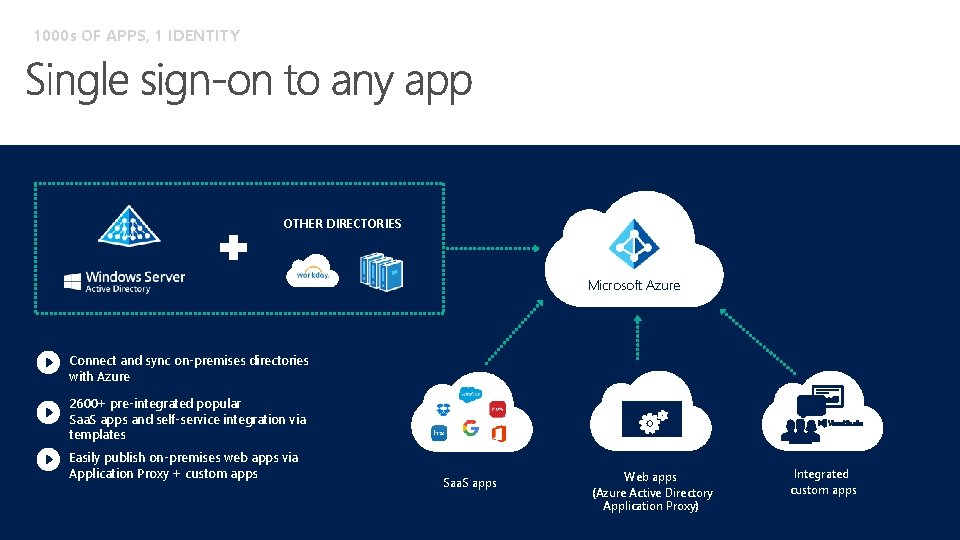
1000 s OF APPS, 1 IDENTITY OTHER DIRECTORIES Microsoft Azure Connect and sync on-premises directories with Azure 2600+ pre-integrated popular Saa. S apps and self-service integration via templates Easily publish on-premises web apps via Application Proxy + custom apps Saa. S apps Web apps (Azure Active Directory Application Proxy) Integrated custom apps
• Create a user on premises • Force Sync • Check logs – eventviewer + Azure AD Sync • Get-MSOLUser
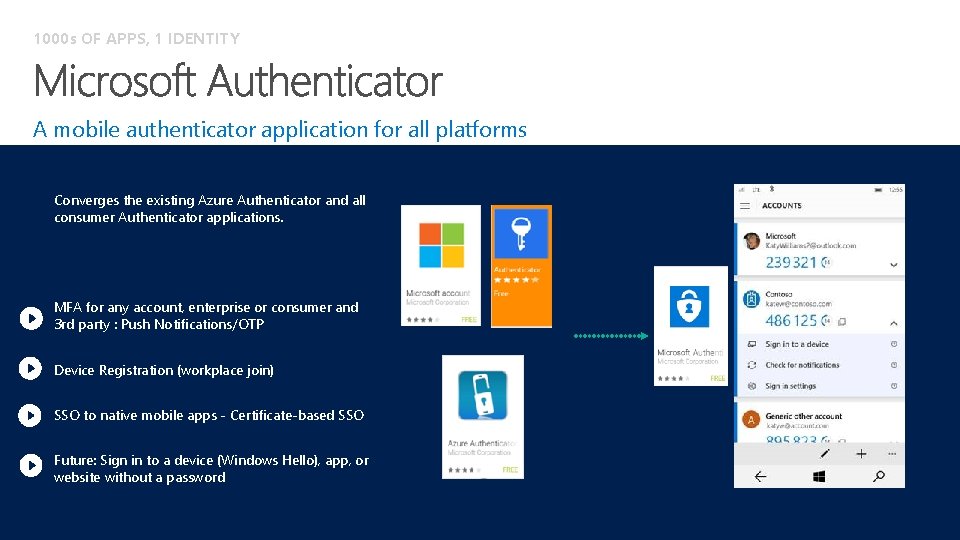
1000 s OF APPS, 1 IDENTITY A mobile authenticator application for all platforms Converges the existing Azure Authenticator and all consumer Authenticator applications. MFA for any account, enterprise or consumer and 3 rd party : Push Notifications/OTP Device Registration (workplace join) SSO to native mobile apps - Certificate-based SSO Future: Sign in to a device (Windows Hello), app, or website without a password
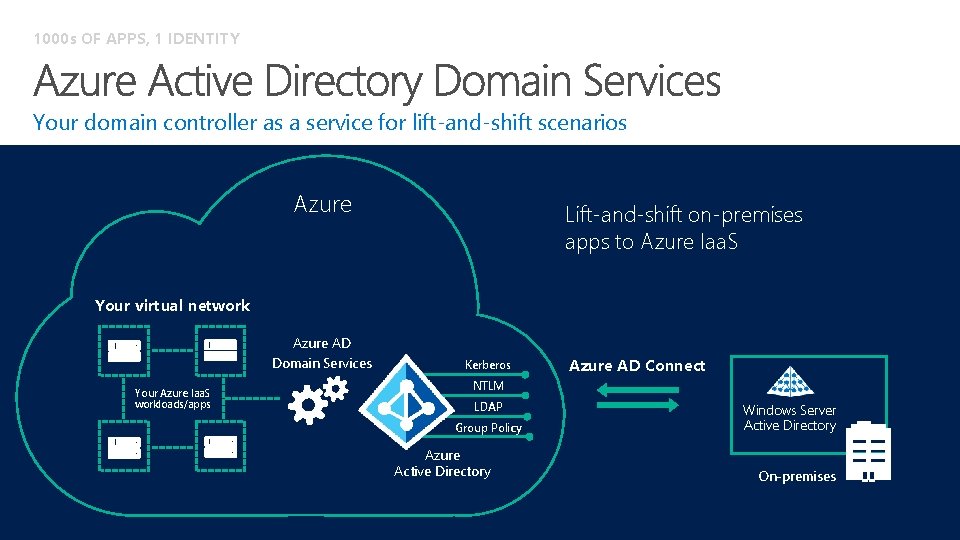
1000 s OF APPS, 1 IDENTITY Your domain controller as a service for lift-and-shift scenarios Azure Lift-and-shift on-premises apps to Azure Iaa. S Your virtual network Azure AD Domain Services Your Azure Iaa. S workloads/apps Kerberos Azure AD Connect NTLM LDAP Group Policy Azure Active Directory Windows Server Active Directory On-premises
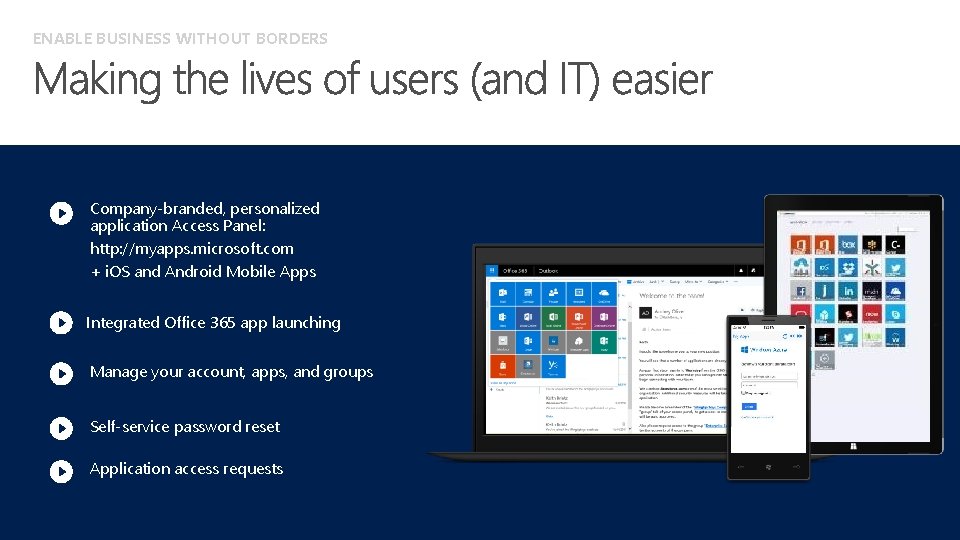
ENABLE BUSINESS WITHOUT BORDERS Company-branded, personalized application Access Panel: http: //myapps. microsoft. com + i. OS and Android Mobile Apps Integrated Office 365 app launching Manage your account, apps, and groups Self-service password reset Application access requests
• Users • Groups • Applications • Domains • Directory Integration • Configure • Reports • Licenses
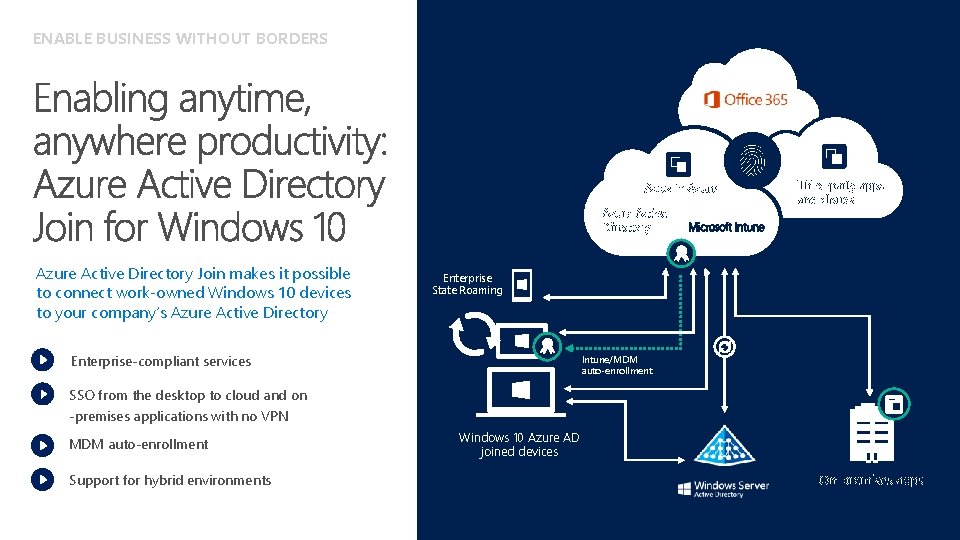
ENABLE BUSINESS WITHOUT BORDERS Apps in Azure Active Directory Join makes it possible to connect work-owned Windows 10 devices to your company’s Azure Active Directory Third-party apps and clouds Enterprise State Roaming Enterprise-compliant services Intune/MDM auto-enrollment SSO from the desktop to cloud and on -premises applications with no VPN MDM auto-enrollment Support for hybrid environments Windows 10 Azure AD joined devices On-premises apps
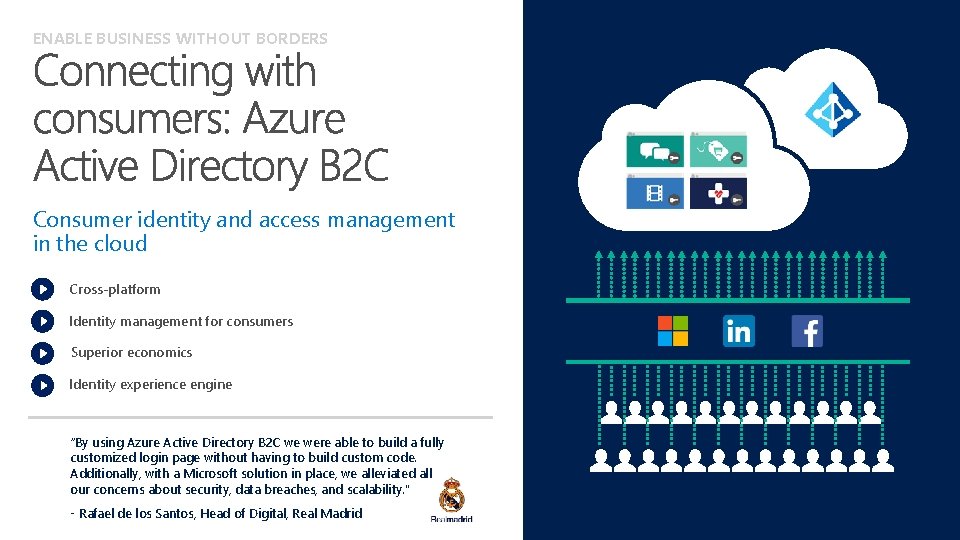
ENABLE BUSINESS WITHOUT BORDERS Consumer identity and access management in the cloud Cross-platform Identity management for consumers Superior economics Identity experience engine “By using Azure Active Directory B 2 C we were able to build a fully customized login page without having to build custom code. Additionally, with a Microsoft solution in place, we alleviated all our concerns about security, data breaches, and scalability. " - Rafael de los Santos, Head of Digital, Real Madrid
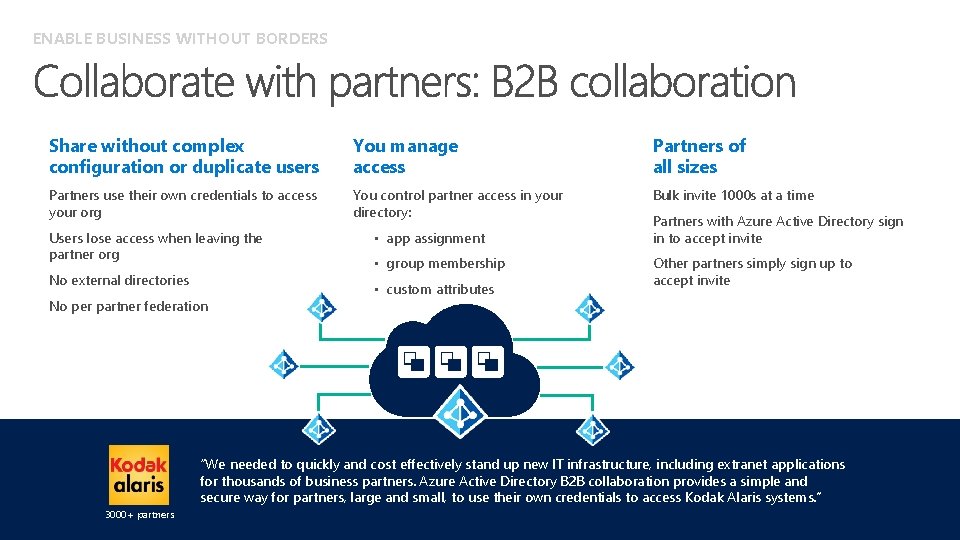
ENABLE BUSINESS WITHOUT BORDERS Share without complex configuration or duplicate users You manage access Partners of all sizes Partners use their own credentials to access your org You control partner access in your directory: Bulk invite 1000 s at a time Users lose access when leaving the partner org No external directories No per partner federation • app assignment • group membership • custom attributes Partners with Azure Active Directory sign in to accept invite Other partners simply sign up to accept invite “We needed to quickly and cost effectively stand up new IT infrastructure, including extranet applications for thousands of business partners. Azure Active Directory B 2 B collaboration provides a simple and secure way for partners, large and small, to use their own credentials to access Kodak Alaris systems. ” 3000+ partners
ENABLE BUSINESS WITHOUT BORDERS Partner
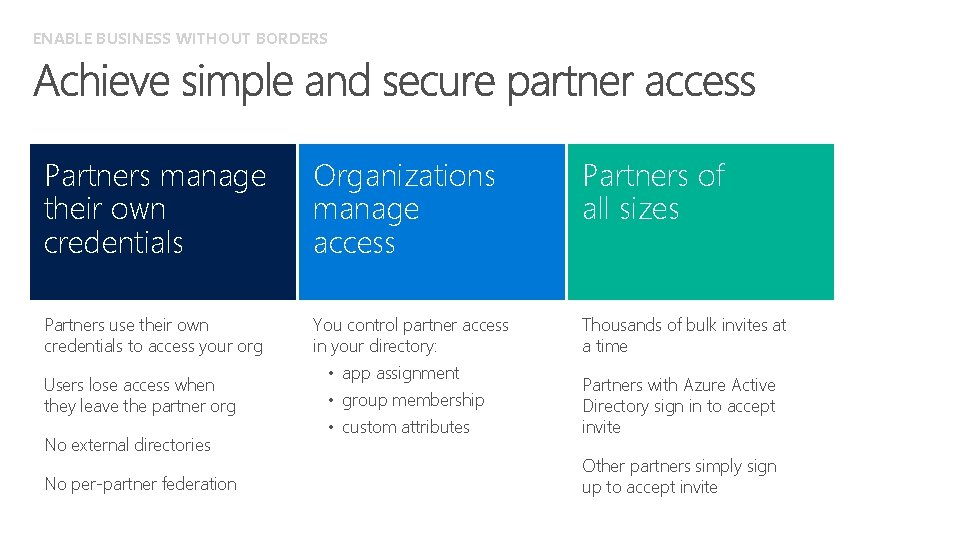
ENABLE BUSINESS WITHOUT BORDERS Partners manage their own credentials Organizations manage access Partners of all sizes Partners use their own credentials to access your org You control partner access in your directory: Thousands of bulk invites at a time Users lose access when they leave the partner org No external directories No per-partner federation • app assignment • group membership • custom attributes Partners with Azure Active Directory sign in to accept invite Other partners simply sign up to accept invite
• Creating an Application Link • Inviting External users • External user experience
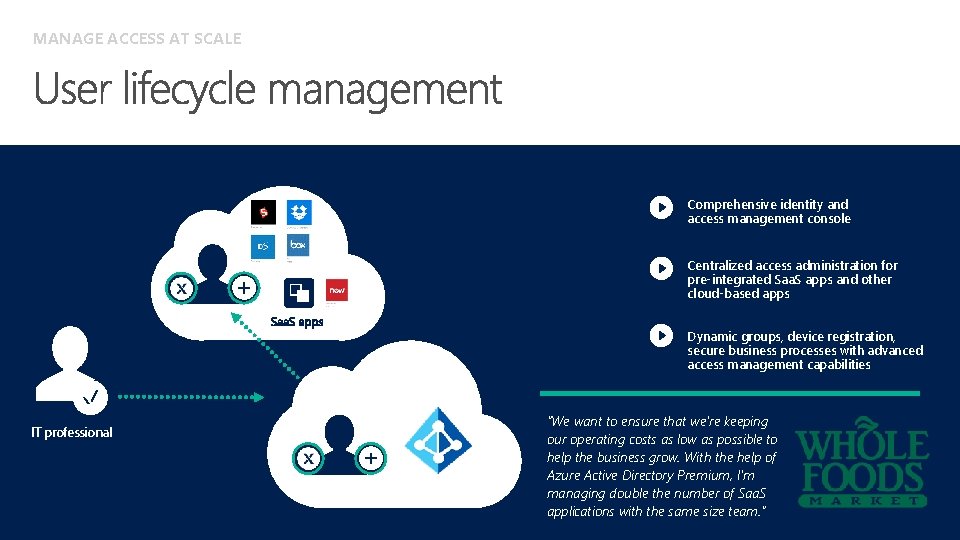
MANAGE ACCESS AT SCALE Comprehensive identity and access management console Centralized access administration for pre-integrated Saa. S apps and other cloud-based apps Dynamic groups, device registration, secure business processes with advanced access management capabilities IT professional “We want to ensure that we’re keeping our operating costs as low as possible to help the business grow. With the help of Azure Active Directory Premium, I’m managing double the number of Saa. S applications with the same size team. ”
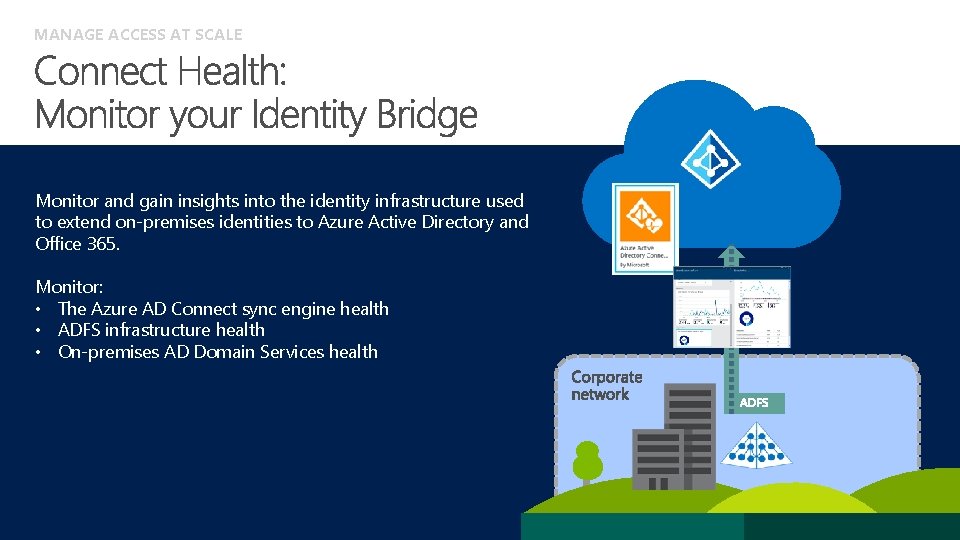
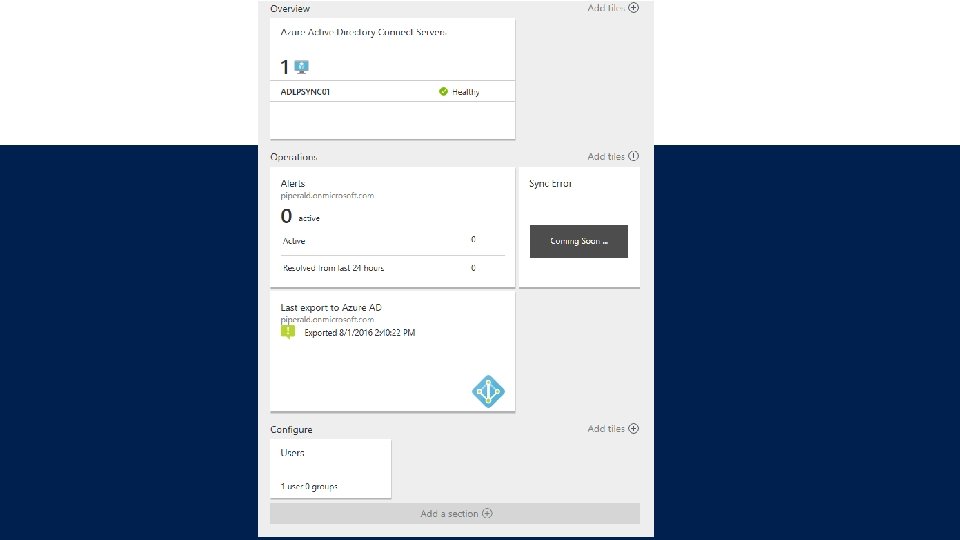
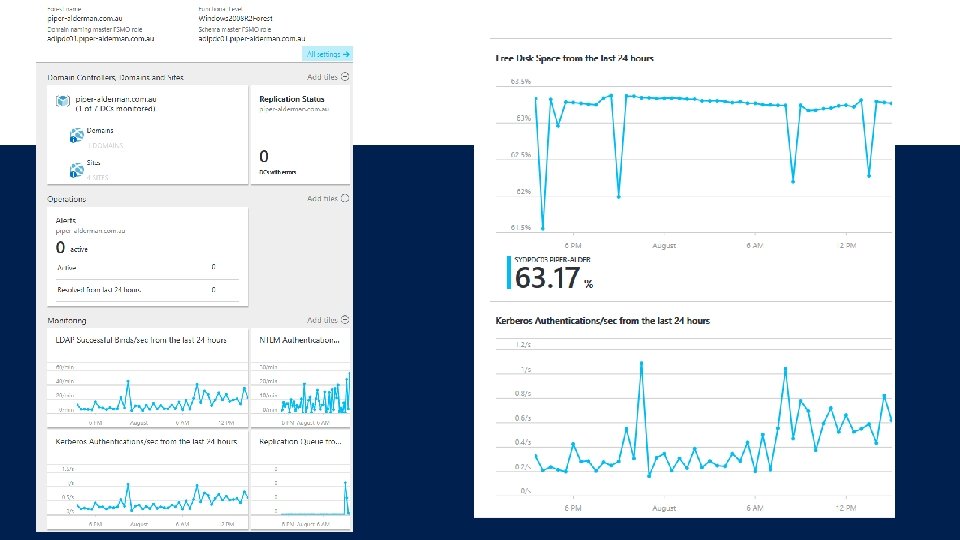
MANAGE ACCESS AT SCALE Monitor and gain insights into the identity infrastructure used to extend on-premises identities to Azure Active Directory and Office 365. Monitor: • The Azure AD Connect sync engine health • ADFS infrastructure health • On-premises AD Domain Services health
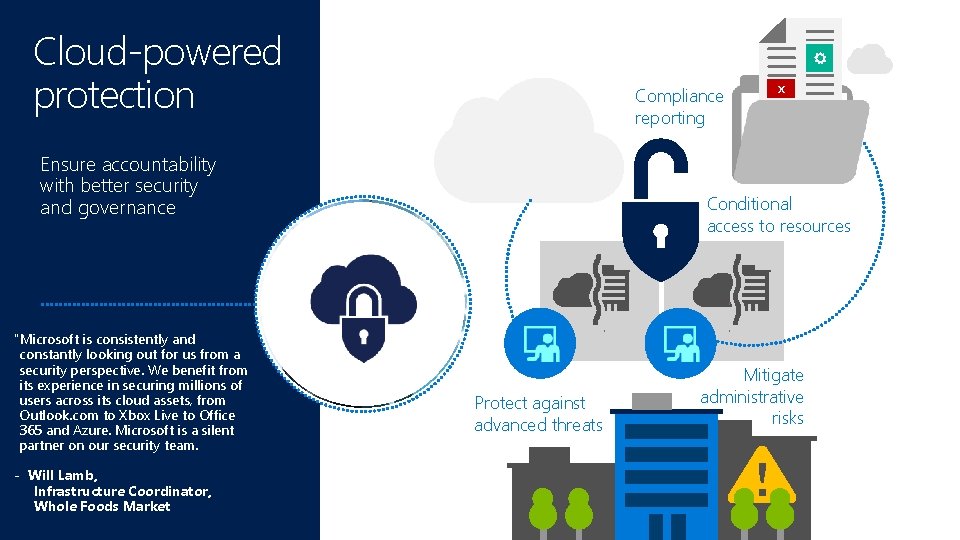
Cloud-powered protection R Compliance reporting Ensure accountability with better security and governance "Microsoft is consistently and constantly looking out for us from a security perspective. We benefit from its experience in securing millions of users across its cloud assets, from Outlook. com to Xbox Live to Office 365 and Azure. Microsoft is a silent partner on our security team. - Will Lamb, Infrastructure Coordinator, Whole Foods Market X Conditional access to resources Protect against advanced threats Mitigate administrative risks
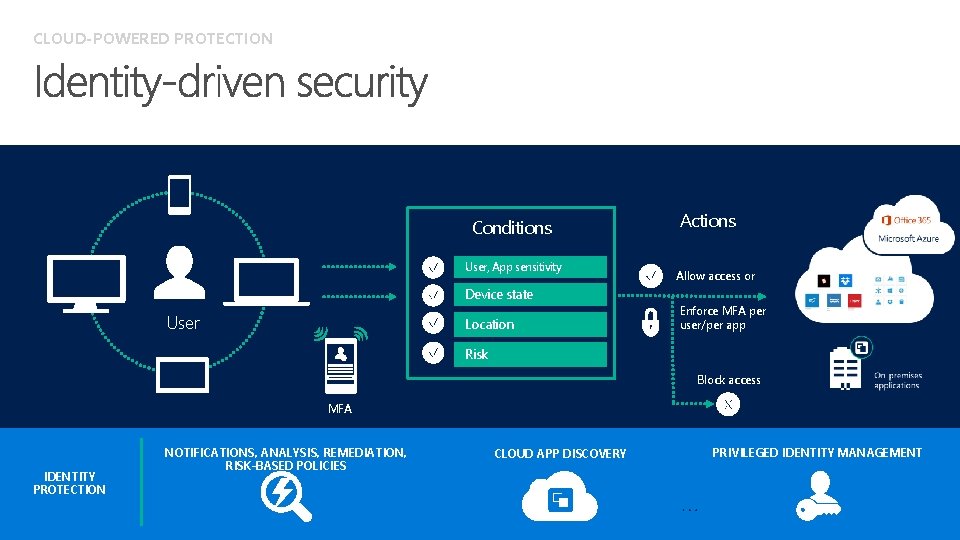
CLOUD-POWERED PROTECTION Conditions User, App sensitivity Actions Allow access or Device state User Location Enforce MFA per user/per app Risk Block access MFA IDENTITY PROTECTION NOTIFICATIONS, ANALYSIS, REMEDIATION, RISK-BASED POLICIES CLOUD APP DISCOVERY PRIVILEGED IDENTITY MANAGEMENT
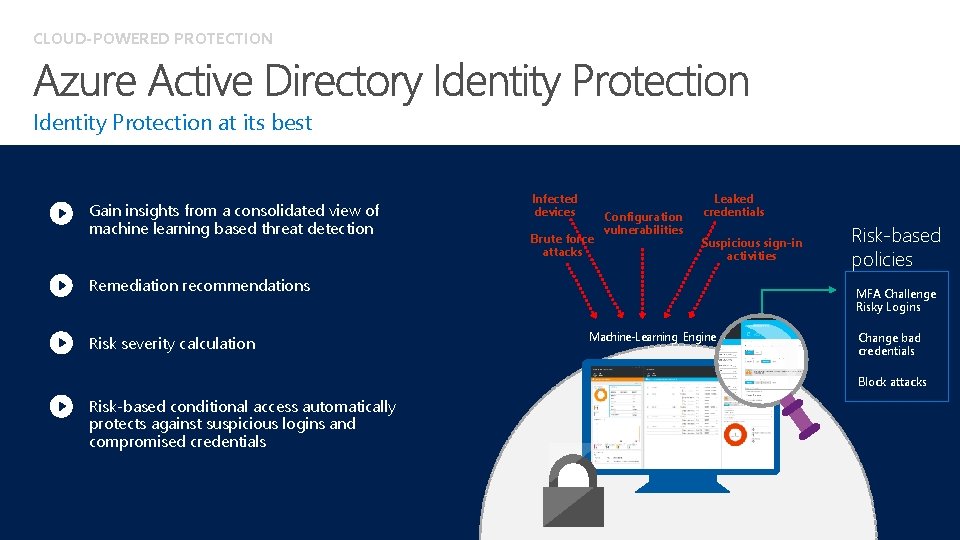
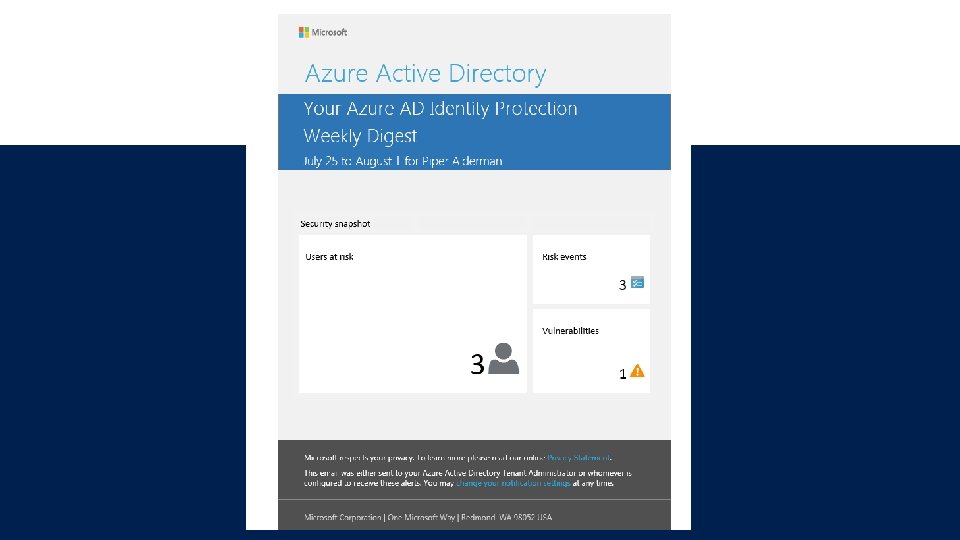
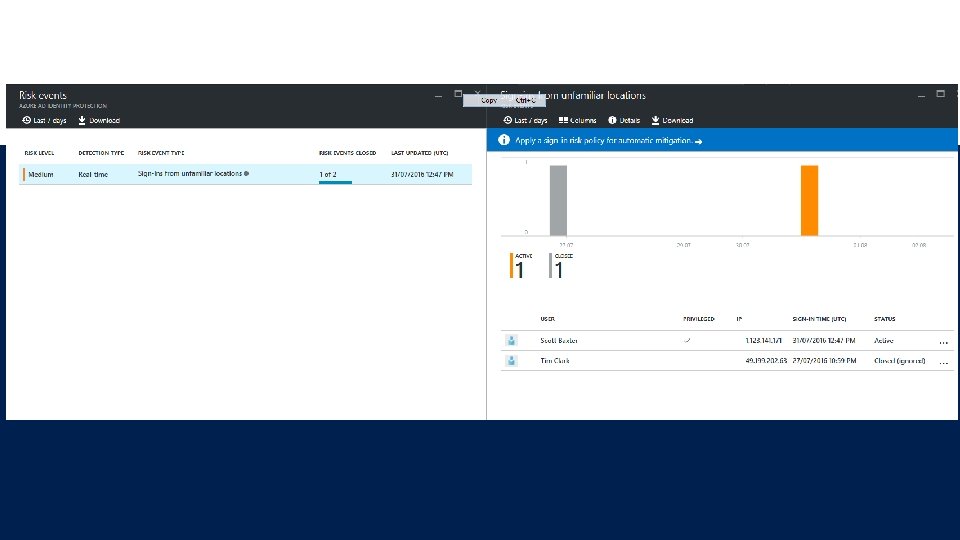
CLOUD-POWERED PROTECTION Identity Protection at its best Gain insights from a consolidated view of machine learning based threat detection Infected devices Brute force attacks Configuration vulnerabilities Leaked credentials Suspicious sign-in activities Remediation recommendations Risk severity calculation Risk-based policies MFA Challenge Risky Logins Machine-Learning Engine Change bad credentials Block attacks Risk-based conditional access automatically protects against suspicious logins and compromised credentials
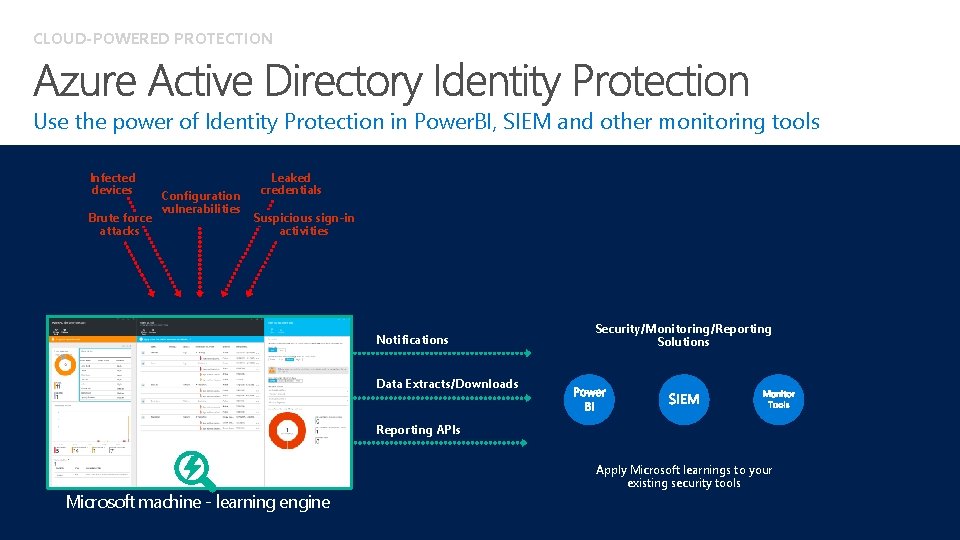
CLOUD-POWERED PROTECTION Use the power of Identity Protection in Power. BI, SIEM and other monitoring tools Infected devices Brute force attacks Configuration vulnerabilities Leaked credentials Suspicious sign-in activities Notifications Security/Monitoring/Reporting Solutions Data Extracts/Downloads Reporting APIs Microsoft machine - learning engine Apply Microsoft learnings to your existing security tools
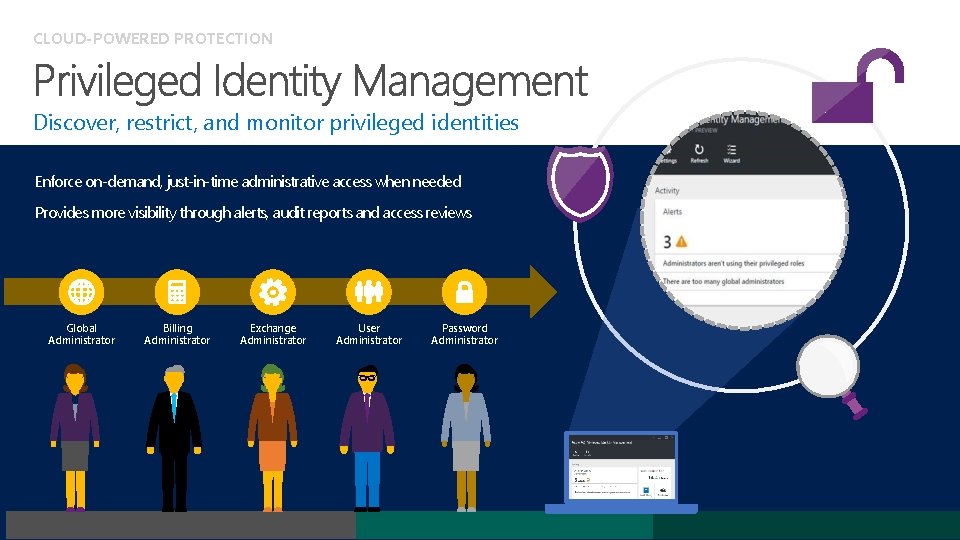
CLOUD-POWERED PROTECTION Discover, restrict, and monitor privileged identities Enforce on-demand, just-in-time administrative access when needed Provides more visibility through alerts, audit reports and access reviews Global Administrator Billing Administrator Exchange Administrator User Administrator Password Administrator
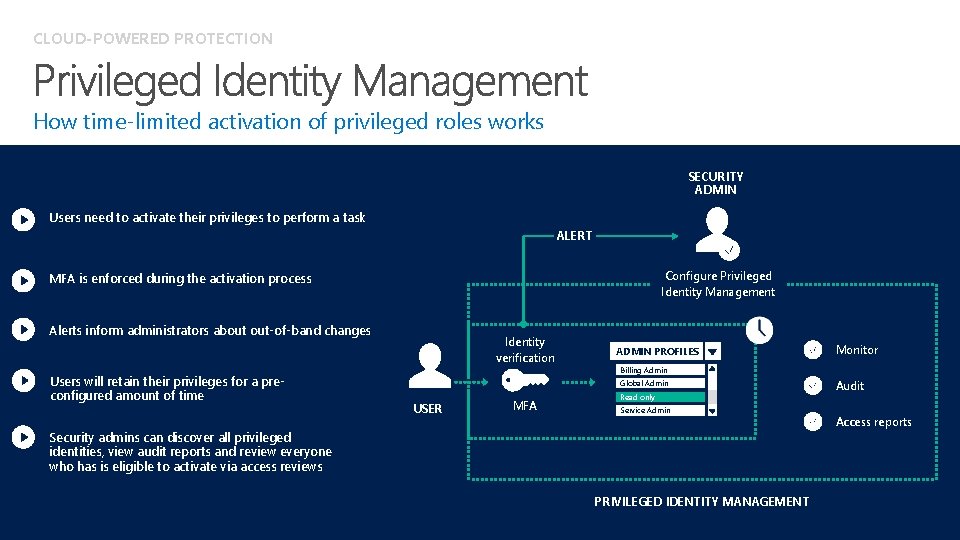
CLOUD-POWERED PROTECTION How time-limited activation of privileged roles works SECURITY ADMIN Users need to activate their privileges to perform a task ALERT Configure Privileged Identity Management MFA is enforced during the activation process Alerts inform administrators about out-of-band changes Users will retain their privileges for a preconfigured amount of time Identity verification ADMIN PROFILES Billing Admin Global Admin USER MFA Monitor Read only Service Admin Security admins can discover all privileged identities, view audit reports and review everyone who has is eligible to activate via access reviews PRIVILEGED IDENTITY MANAGEMENT Audit Access reports
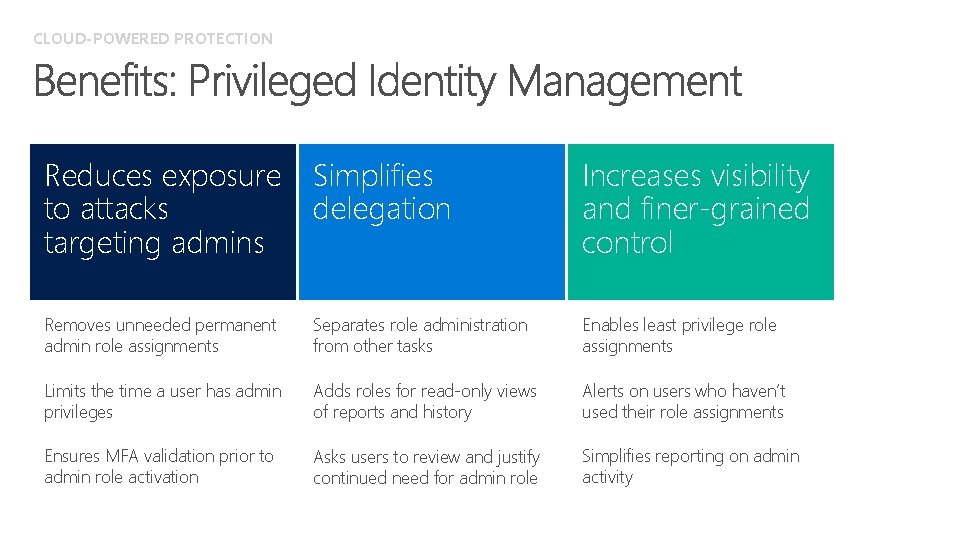
CLOUD-POWERED PROTECTION Reduces exposure to attacks targeting admins Simplifies delegation Increases visibility and finer-grained control Removes unneeded permanent admin role assignments Separates role administration from other tasks Enables least privilege role assignments Limits the time a user has admin privileges Adds roles for read-only views of reports and history Alerts on users who haven’t used their role assignments Ensures MFA validation prior to admin role activation Asks users to review and justify continued need for admin role Simplifies reporting on admin activity
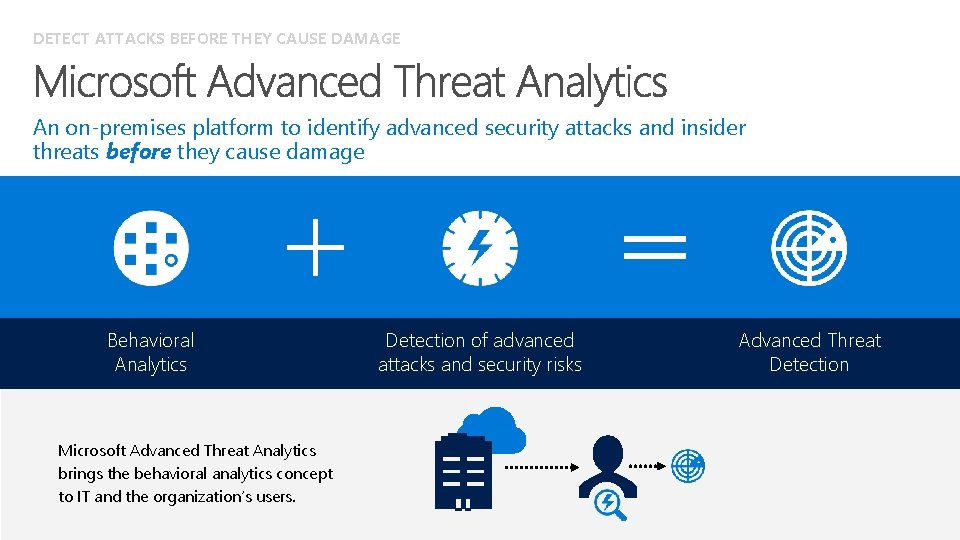
DETECT ATTACKS BEFORE THEY CAUSE DAMAGE An on-premises platform to identify advanced security attacks and insider threats before they cause damage Behavioral Analytics Microsoft Advanced Threat Analytics brings the behavioral analytics concept to IT and the organization’s users. Detection of advanced attacks and security risks Advanced Threat Detection
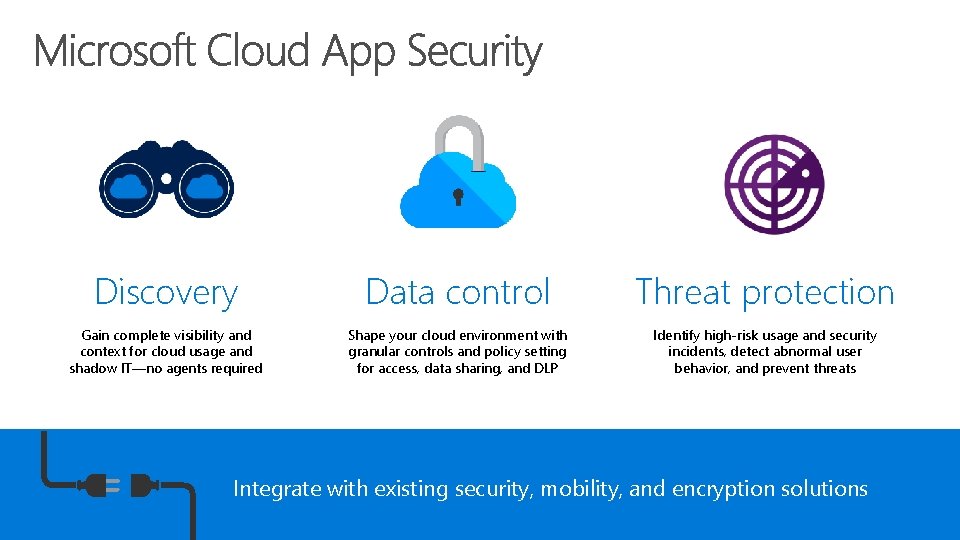
Discovery Data control Threat protection Gain complete visibility and context for cloud usage and shadow IT—no agents required Shape your cloud environment with granular controls and policy setting for access, data sharing, and DLP Identify high-risk usage and security incidents, detect abnormal user behavior, and prevent threats Integrate with existing security, mobility, and encryption solutions
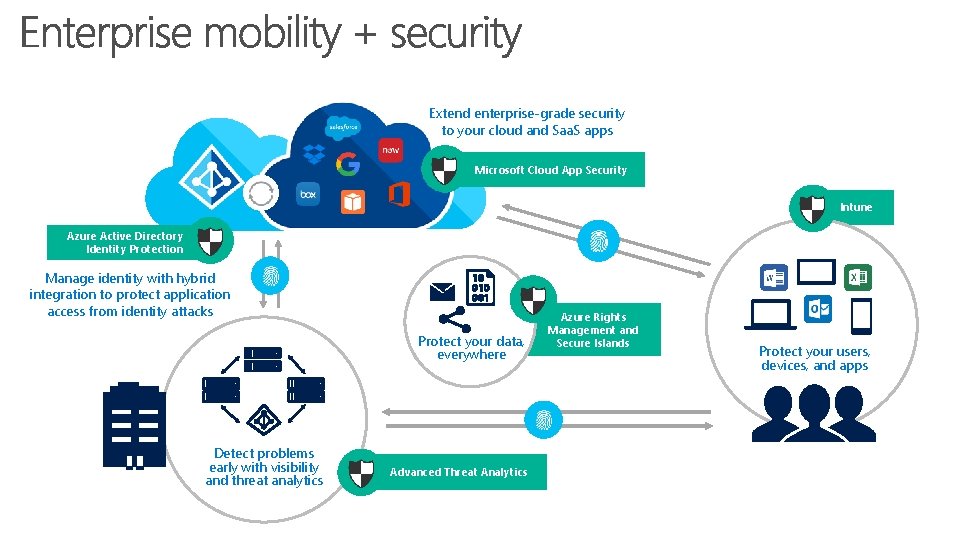
Extend enterprise-grade security to your cloud and Saa. S apps Microsoft Cloud App Security Intune Azure Active Directory Identity Protection Manage identity with hybrid integration to protect application access from identity attacks Protect your data, everywhere Detect problems early with visibility and threat analytics Advanced Threat Analytics Azure Rights Management and Secure Islands Protect your users, devices, and apps
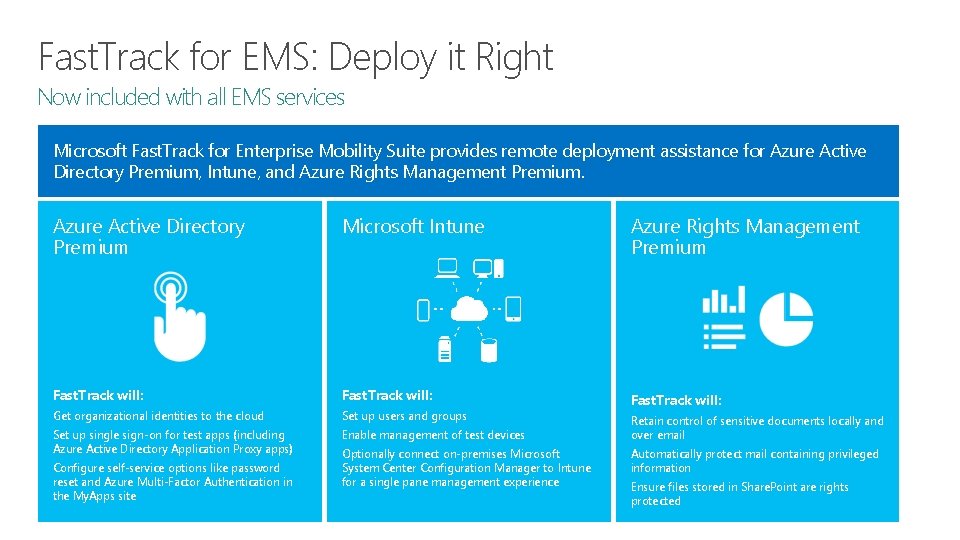
Fast. Track for EMS: Deploy it Right Now included with all EMS services Microsoft Fast. Track for Enterprise Mobility Suite provides remote deployment assistance for Azure Active Directory Premium, Intune, and Azure Rights Management Premium. Azure Active Directory Premium Microsoft Intune Azure Rights Management Premium Fast. Track will: Get organizational identities to the cloud Set up users and groups Fast. Track will: Set up single sign-on for test apps (including Azure Active Directory Application Proxy apps) Enable management of test devices Configure self-service options like password reset and Azure Multi-Factor Authentication in the My. Apps site Optionally connect on-premises Microsoft System Center Configuration Manager to Intune for a single pane management experience Retain control of sensitive documents locally and over email Automatically protect mail containing privileged information Ensure files stored in Share. Point are rights protected
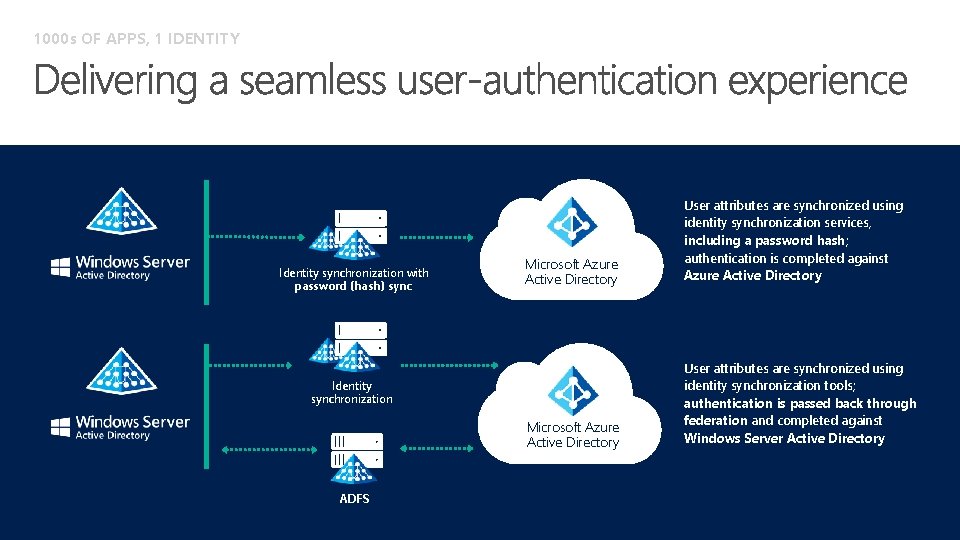
1000 s OF APPS, 1 IDENTITY Identity synchronization with password (hash) sync Microsoft Azure Active Directory User attributes are synchronized using identity synchronization services, including a password hash; authentication is completed against Azure Active Directory Microsoft Azure Active Directory User attributes are synchronized using identity synchronization tools; authentication is passed back through federation and completed against Windows Server Active Directory Identity synchronization ADFS
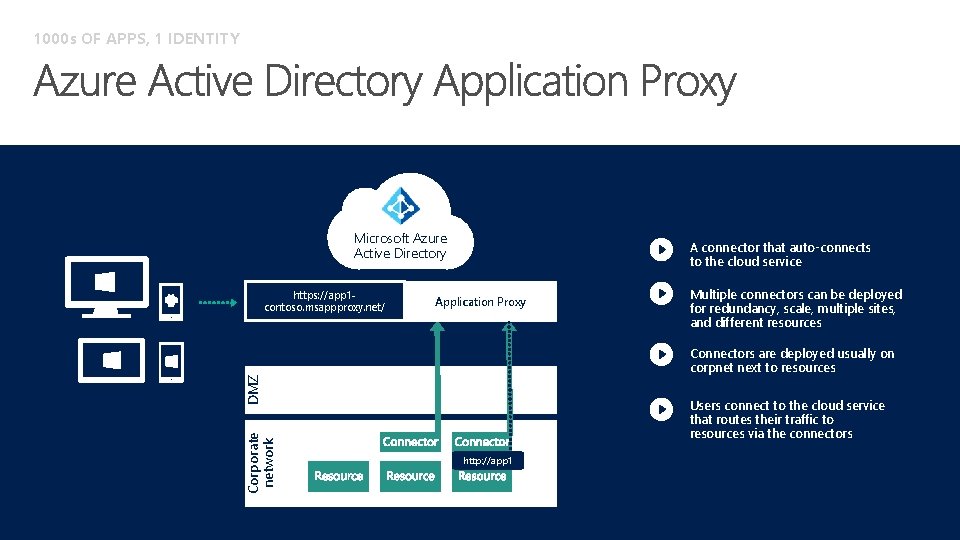
1000 s OF APPS, 1 IDENTITY Microsoft Azure Active Directory Application Proxy Corporate network Multiple connectors can be deployed for redundancy, scale, multiple sites, and different resources Connectors are deployed usually on corpnet next to resources DMZ https: //app 1 contoso. msappproxy. net/ A connector that auto-connects to the cloud service Users connect to the cloud service that routes their traffic to resources via the connectors http: //app 1
1000 s OF APPS, 1 IDENTITY
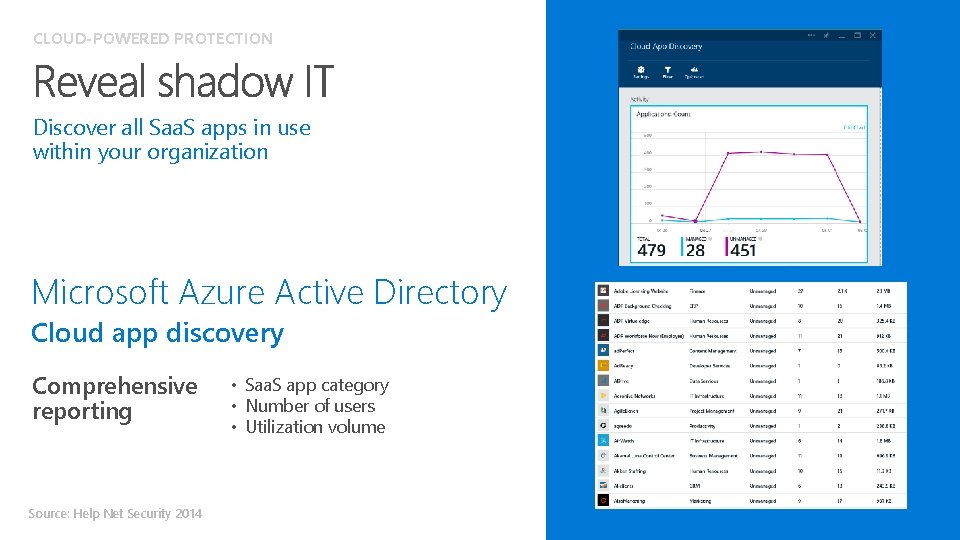
CLOUD-POWERED PROTECTION as many Cloud Discover all Saa. S apps in use apps within your organization than IT estimates are in use Microsoft Azure Active Directory Cloud app discovery Comprehensive reporting Source: Help Net Security 2014 • Saa. S app category • Number of users • Utilization volume
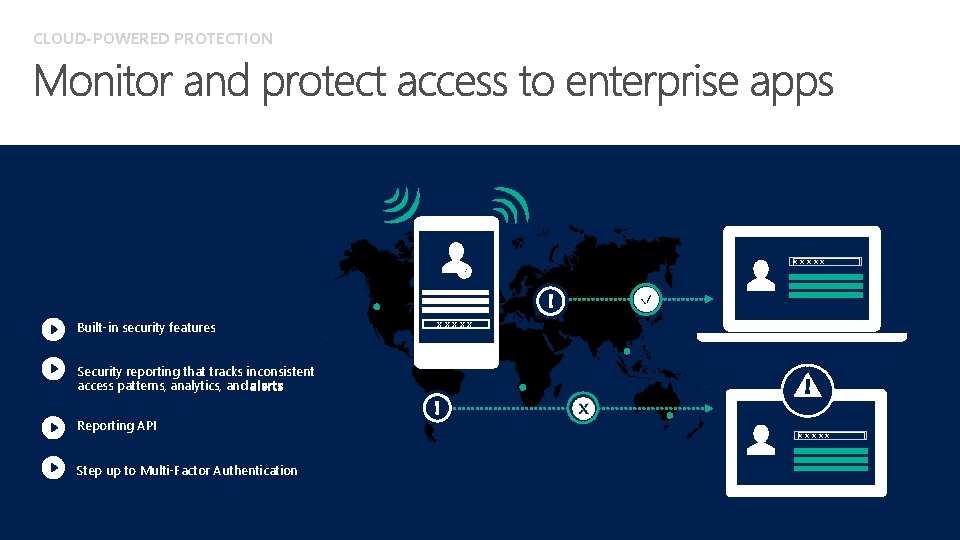
CLOUD-POWERED PROTECTION X X X Built-in security features X X X Security reporting that tracks inconsistent access patterns, analytics, and alerts Reporting API Step up to Multi-Factor Authentication X X X
CLOUD-POWERED PROTECTION A standalone Azure identity and access management service, also included in Azure Active Directory Premium Prevents unauthorized access to both on -premises and cloud applications by providing an additional level of authentication Trusted by thousands of enterprises to authenticate employee, customer, and partner access
CLOUD-POWERED PROTECTION Mobile apps Phone calls Text messages
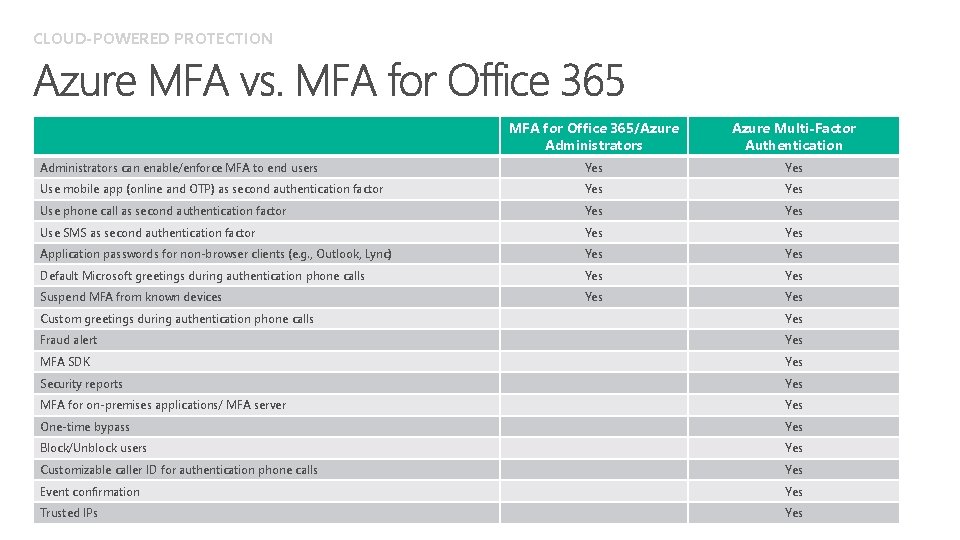
CLOUD-POWERED PROTECTION MFA for Office 365/Azure Administrators Azure Multi-Factor Authentication Administrators can enable/enforce MFA to end users Yes Use mobile app (online and OTP) as second authentication factor Yes Use phone call as second authentication factor Yes Use SMS as second authentication factor Yes Application passwords for non-browser clients (e. g. , Outlook, Lync) Yes Default Microsoft greetings during authentication phone calls Yes Suspend MFA from known devices Yes Custom greetings during authentication phone calls Yes Fraud alert Yes MFA SDK Yes Security reports Yes MFA for on-premises applications/ MFA server Yes One-time bypass Yes Block/Unblock users Yes Customizable caller ID for authentication phone calls Yes Event confirmation Yes Trusted IPs Yes
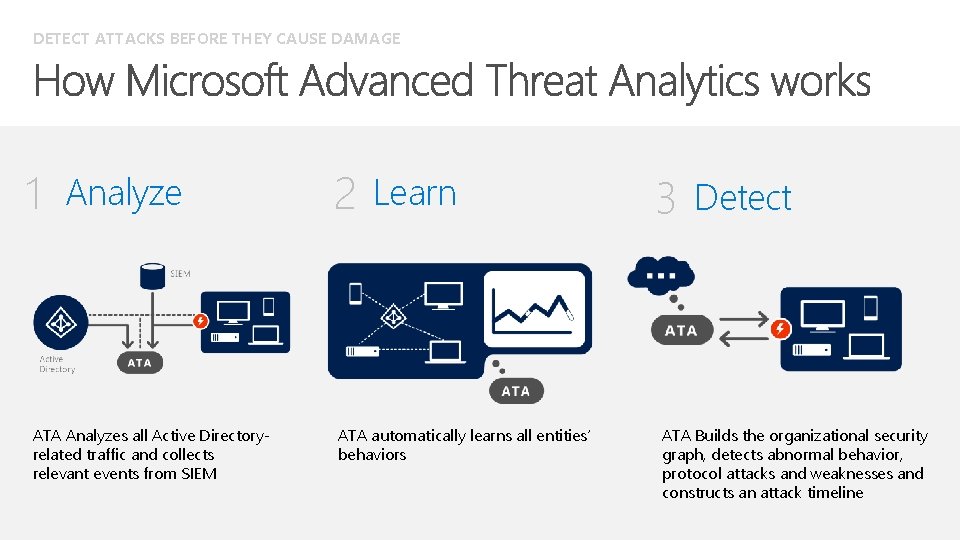
DETECT ATTACKS BEFORE THEY CAUSE DAMAGE 1 Analyze ATA Analyzes all Active Directoryrelated traffic and collects relevant events from SIEM 2 Learn ATA automatically learns all entities’ behaviors 3 Detect ATA Builds the organizational security graph, detects abnormal behavior, protocol attacks and weaknesses and constructs an attack timeline
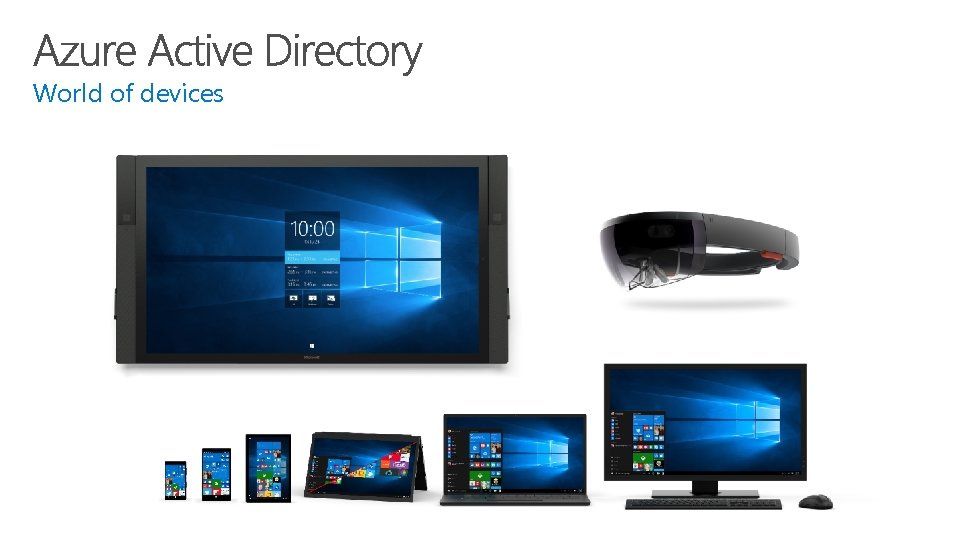
World of devices
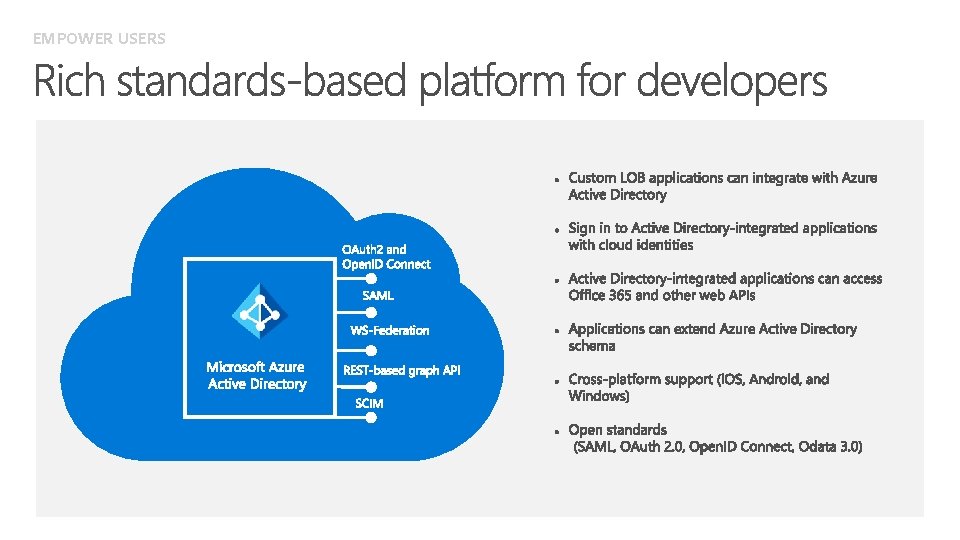
EMPOWER USERS
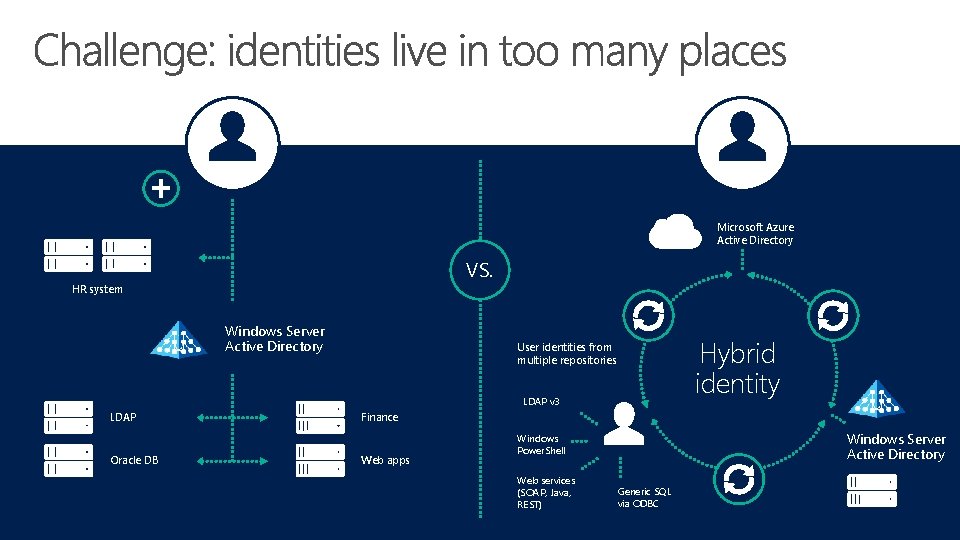
Microsoft Azure Active Directory VS. HR system Windows Server Active Directory Hybrid identity User identities from multiple repositories LDAP v 3 LDAP Oracle DB Finance Web apps Windows Server Active Directory Windows Power. Shell Web services (SOAP, Java, REST) Generic SQL via ODBC
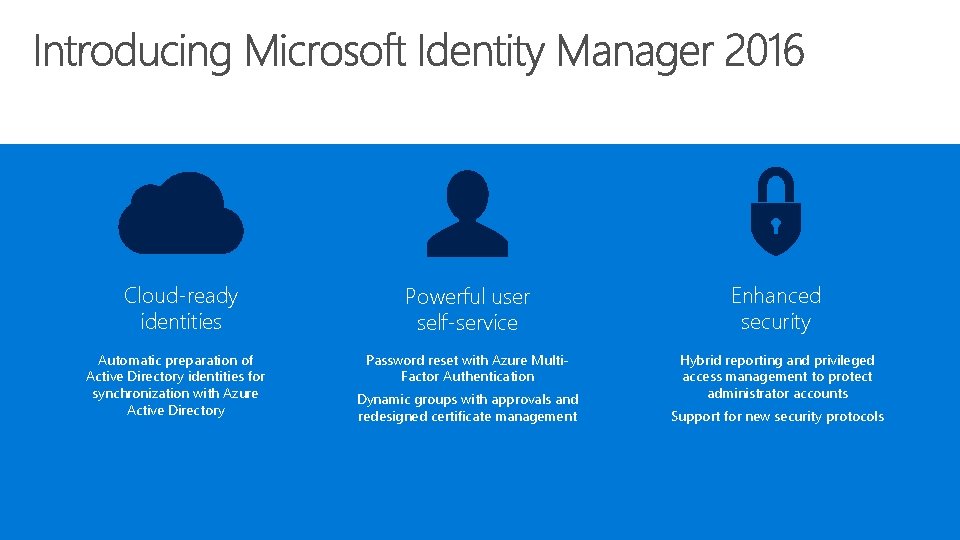
Cloud-ready identities Automatic preparation of Active Directory identities for synchronization with Azure Active Directory Powerful user self-service Enhanced security Password reset with Azure Multi. Factor Authentication Hybrid reporting and privileged access management to protect administrator accounts Dynamic groups with approvals and redesigned certificate management Support for new security protocols
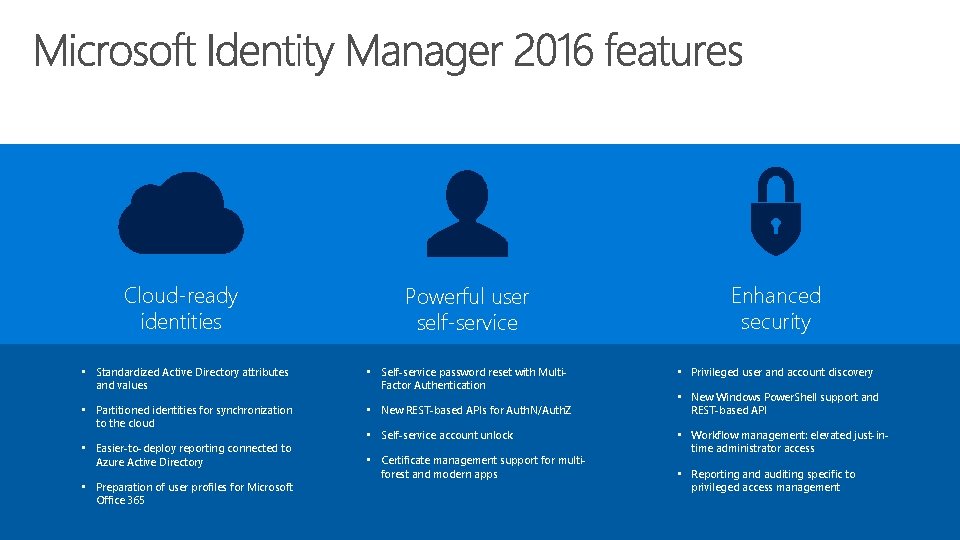
Powerful user self-service Enhanced security • Standardized Active Directory attributes and values • Self-service password reset with Multi. Factor Authentication • Privileged user and account discovery • Partitioned identities for synchronization to the cloud • New REST-based APIs for Auth. N/Auth. Z Cloud-ready identities • Easier-to-deploy reporting connected to Azure Active Directory • Preparation of user profiles for Microsoft Office 365 • Self-service account unlock • Certificate management support for multiforest and modern apps • New Windows Power. Shell support and REST-based API • Workflow management: elevated just-intime administrator access • Reporting and auditing specific to privileged access management
@Adam. Fowler_IT Adelaide Windows User Group