
Achieving A Trusted Cloud with VMware George Gerchow
- Slides: 52
Achieving A Trusted Cloud with VMware George Gerchow – VMware Director, Center for Policy & Compliance CISSP, ITIL, CCNA, MCPS, SCP Confidential © 2010 VMware Inc. All rights reserved
Physical, Virtual, Cloud cannot stop the Human Factor § Step 1 – Get great job at NG § Step 2 – New Laptop from IT § Step 3 – The Rebuild § Step 4 – Labs at CSU 2 Confidential
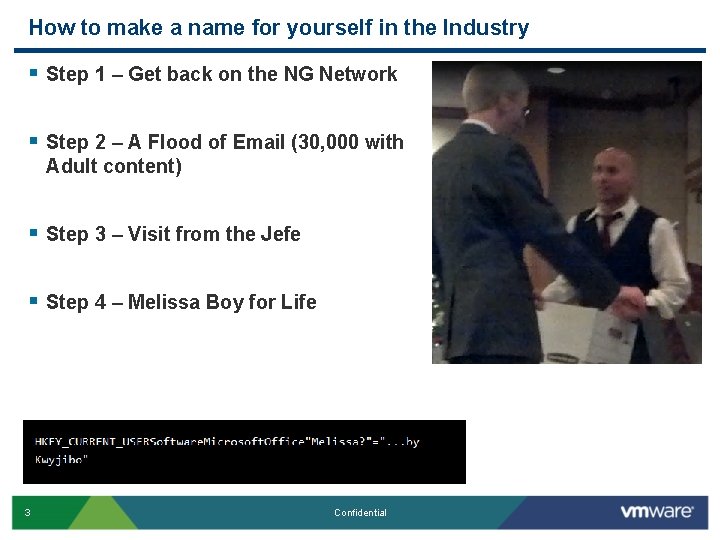
How to make a name for yourself in the Industry § Step 1 – Get back on the NG Network § Step 2 – A Flood of Email (30, 000 with Adult content) § Step 3 – Visit from the Jefe § Step 4 – Melissa Boy for Life 3 Confidential
Agenda § § § 4 Challenges in Cloud Adoption VMware Trusted Cloud Solutions VMware Trusted Cloud Ecosystem VMware Center for Policy & Compliance Key Takeaways Q&A Confidential
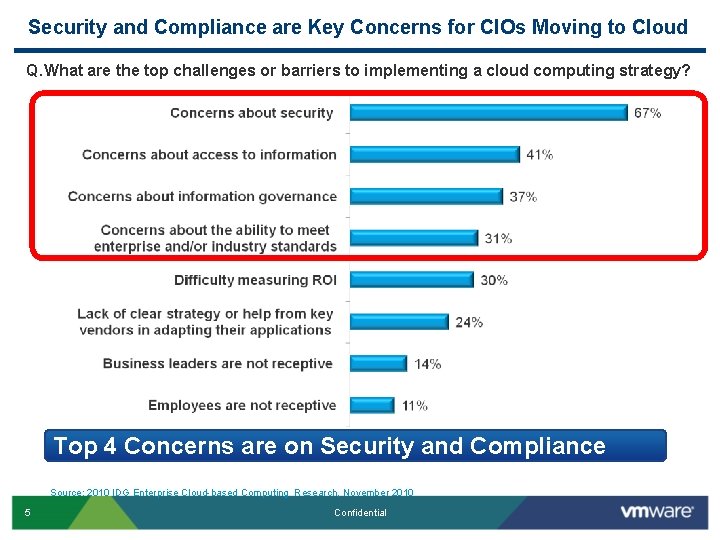
Security and Compliance are Key Concerns for CIOs Moving to Cloud Q. What are the top challenges or barriers to implementing a cloud computing strategy? Top 4 Concerns are on Security and Compliance Source: 2010 IDG Enterprise Cloud-based Computing Research, November 2010 5 Confidential
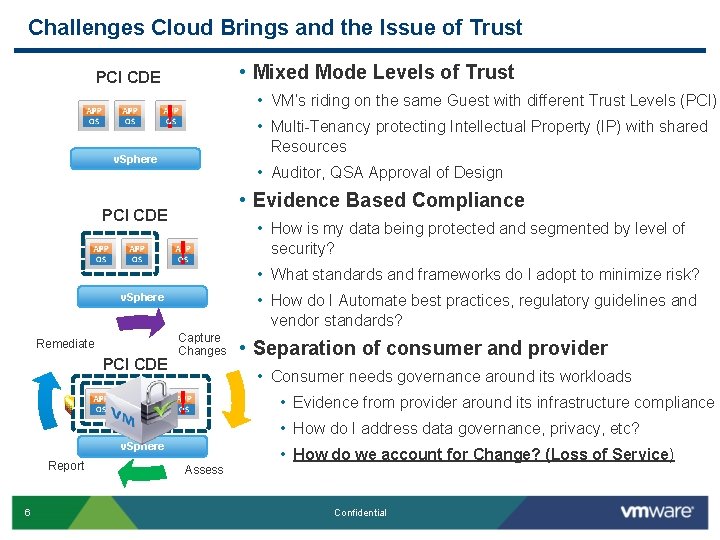
Challenges Cloud Brings and the Issue of Trust • Mixed Mode Levels of Trust PCI CDE • VM’s riding on the same Guest with different Trust Levels (PCI) • Multi-Tenancy protecting Intellectual Property (IP) with shared ! Resources v. Sphere • Auditor, QSA Approval of Design • Evidence Based Compliance PCI CDE ! v. Sphere • How is my data being protected and segmented by level of security? • What standards and frameworks do I adopt to minimize risk? • How do I Automate best practices, regulatory guidelines and vendor standards? Remediate PCI CDE Capture Changes ! v. Sphere Report 6 • Separation of consumer and provider • Consumer needs governance around its workloads • Evidence from provider around its infrastructure compliance • How do I address data governance, privacy, etc? • How do we account for Change? (Loss of Service) Assess Confidential
7 Confidential
What is the Industry saying about Cloud Security & Compliance “Survey finds most providers don't protect data, because they don't think it's their job” (Identity Week, IT security & news) “ 70% of Cloud Providers don’t believe that Security is a core responsibility (Ponemon 2010)” http: //gcn. com/articles/2011/05/06/cloud-security-vendors-donot-care. aspx “A Wall Street Journal article by Ben Rooney reported that the majority of cloud service providers do not consider security as one of their most important responsibilities” 8 Confidential
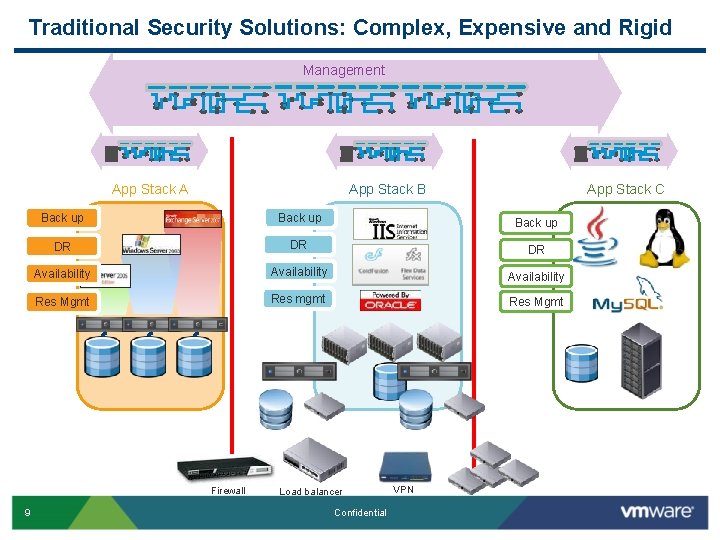
Traditional Security Solutions: Complex, Expensive and Rigid Management App Stack A Back up DR DR DR Availability Res Mgmt Res mgmt Res Mgmt Firewall 9 App Stack C App Stack B Load balancer Confidential VPN
Agenda § § § 10 Challenges in Cloud Adoption VMware Trusted Cloud Solutions VMware Trusted Cloud Ecosystem VMware Center for Policy & Compliance Key Takeaways Q&A Confidential
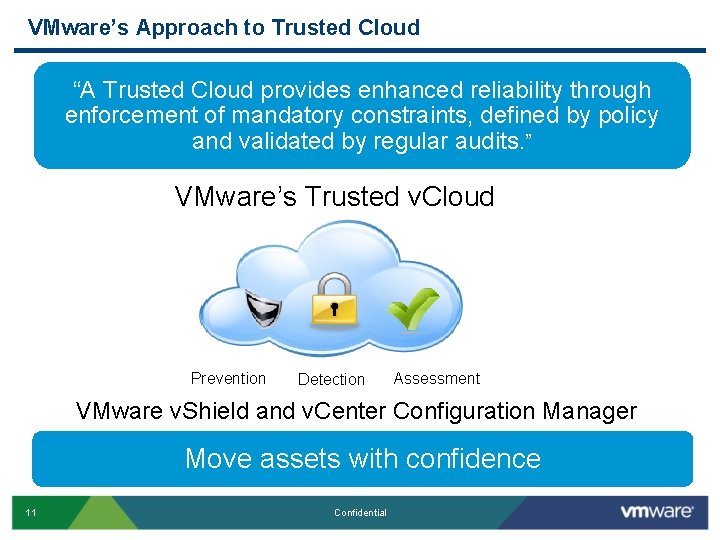
VMware’s Approach to Trusted Cloud “A Trusted Cloud provides enhanced reliability through enforcement of mandatory constraints, defined by policy and validated by regular audits. ” VMware’s Trusted v. Cloud Prevention Detection Assessment VMware v. Shield and v. Center Configuration Manager Move assets with confidence 11 Confidential
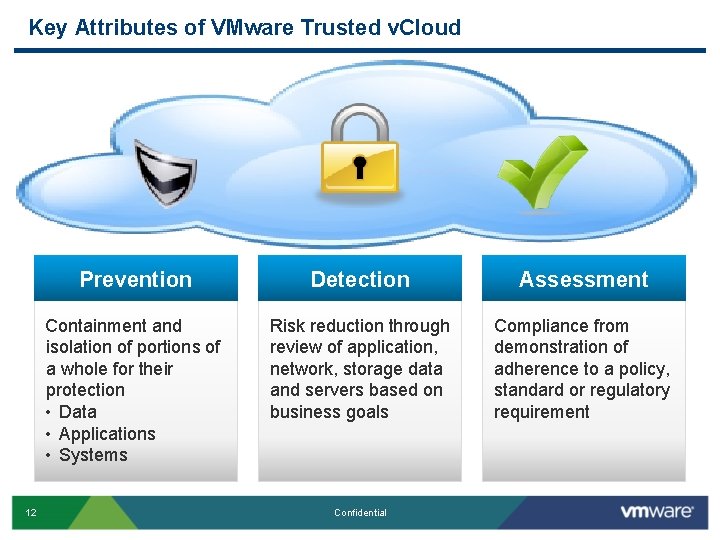
Key Attributes of VMware Trusted v. Cloud 12 Prevention Detection Assessment Containment and isolation of portions of a whole for their protection • Data • Applications • Systems Risk reduction through review of application, network, storage data and servers based on business goals Compliance from demonstration of adherence to a policy, standard or regulatory requirement Confidential
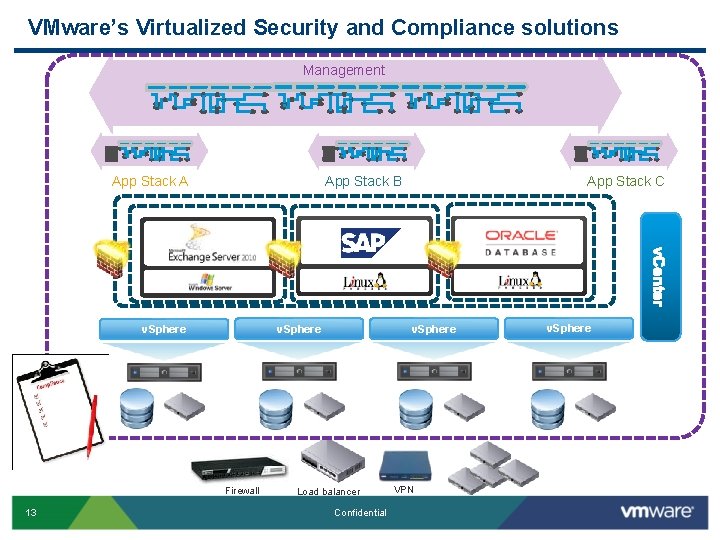
VMware’s Virtualized Security and Compliance solutions Management App Stack A Exchange SAP ERP File/Print Operating System v. Sphere Firewall 13 App Stack C App Stack B v. Sphere Load balancer Confidential VPN v. Sphere
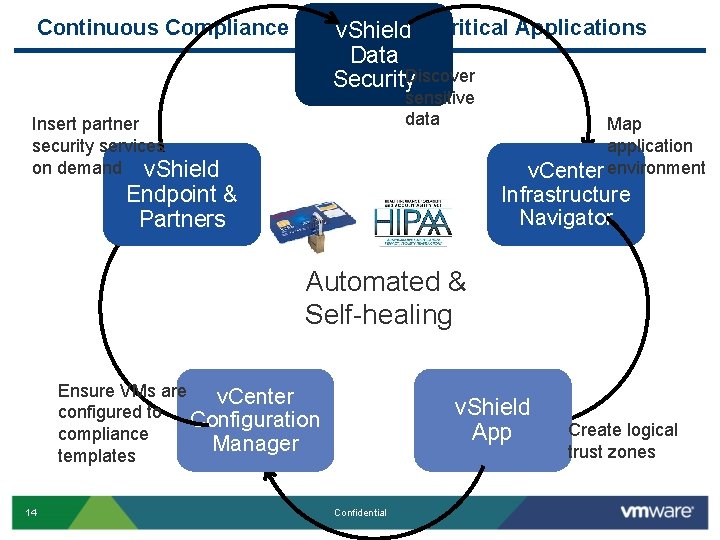
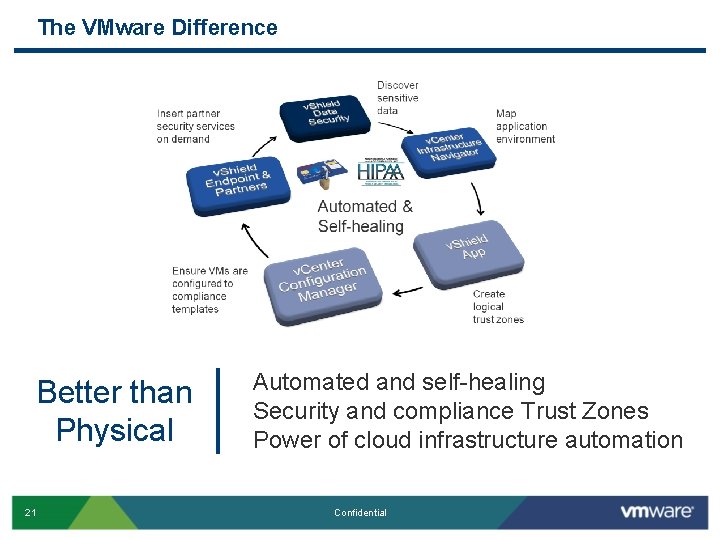
Continuous Compliance for Business v. Shield Critical Applications Data Security. Discover sensitive data Insert partner security services on demand v. Shield Endpoint & Partners Map application v. Center environment Infrastructure Navigator Automated & Self-healing Ensure VMs are v. Center configured to Configuration compliance Manager templates 14 v. Shield App Confidential Create logical trust zones
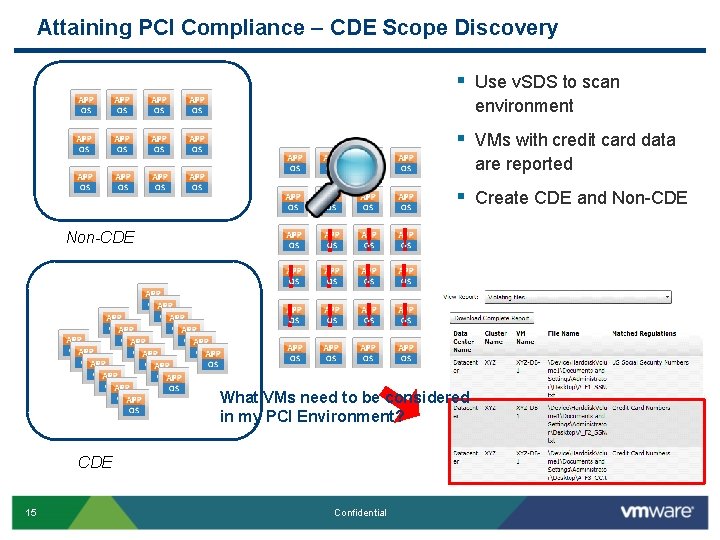
Attaining PCI Compliance – CDE Scope Discovery § Use v. SDS to scan environment § VMs with credit card data are reported § Create CDE and Non-CDE ! ! ! What VMs need to be considered in my PCI Environment? CDE 15 Confidential
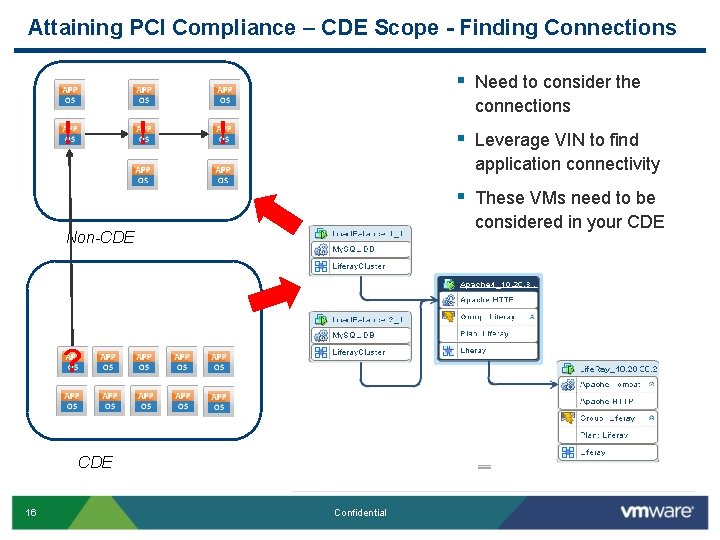
Attaining PCI Compliance – CDE Scope - Finding Connections § Need to consider the ! ! connections ! § Leverage VIN to find application connectivity § These VMs need to be considered in your CDE Non-CDE ? CDE 16 Confidential
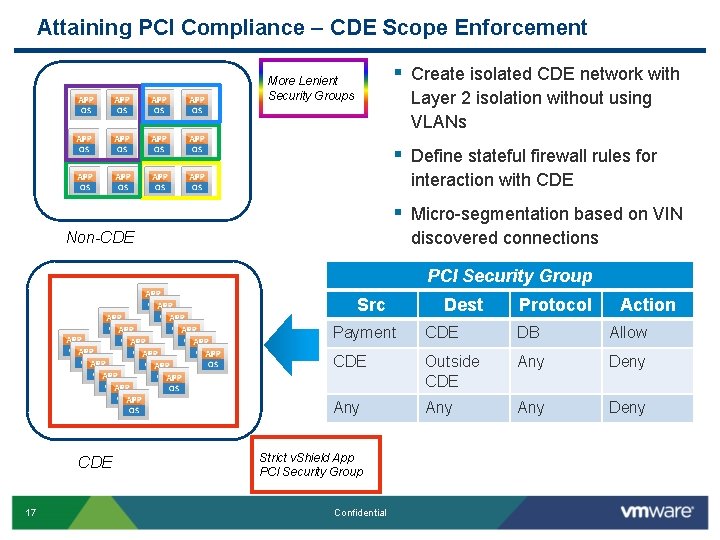
Attaining PCI Compliance – CDE Scope Enforcement § Create isolated CDE network with More Lenient Security Groups Layer 2 isolation without using VLANs § Define stateful firewall rules for interaction with CDE § Micro-segmentation based on VIN discovered connections Non-CDE PCI Security Group Src CDE 17 Dest Protocol Action Payment CDE DB Allow CDE Outside CDE Any Deny Any Any Deny Strict v. Shield App PCI Security Group Confidential
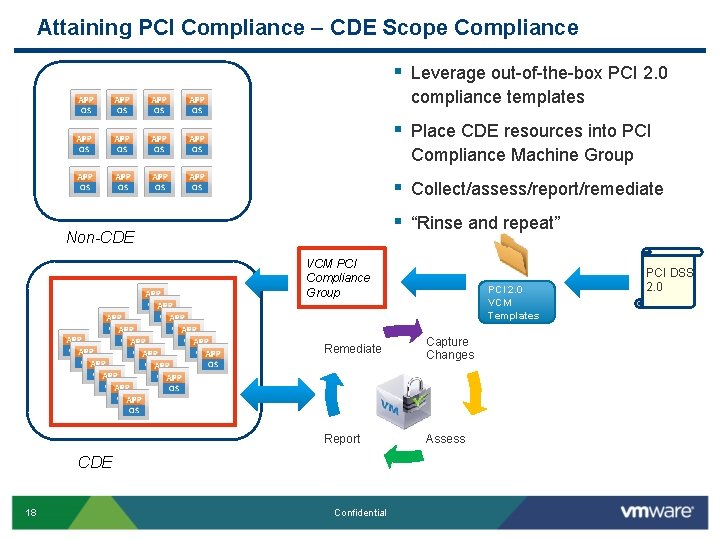
Attaining PCI Compliance – CDE Scope Compliance § Leverage out-of-the-box PCI 2. 0 compliance templates § Place CDE resources into PCI Compliance Machine Group § Collect/assess/report/remediate § “Rinse and repeat” Non-CDE VCM PCI Compliance Group Remediate Capture Changes Report Assess CDE 18 PCI 2. 0 VCM Templates Confidential PCI DSS 2. 0
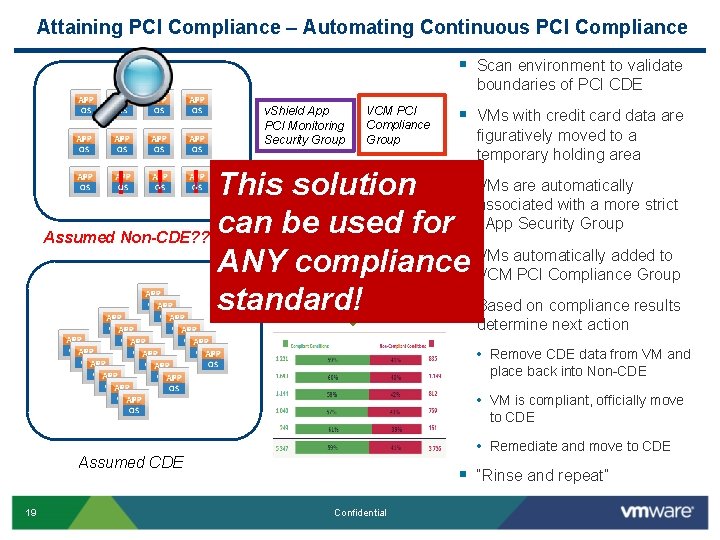
Attaining PCI Compliance – Automating Continuous PCI Compliance § Scan environment to validate boundaries of PCI CDE v. Shield App PCI Monitoring Security Group VCM PCI Compliance Group § VMs with credit card data are figuratively moved to a temporary holding area § VMs are automatically Holding Area ! ! ! This. CDEsolution associated with a more strict can be used for v. App Security Group Assumed Non-CDE? ? ? ! ! ! ANY compliance§ VMs automatically added to VCM PCI Compliance Group standard! § Based on compliance results determine next action • Remove CDE data from VM and place back into Non-CDE • VM is compliant, officially move to CDE • Remediate and move to CDE Assumed CDE 19 § “Rinse and repeat” Confidential
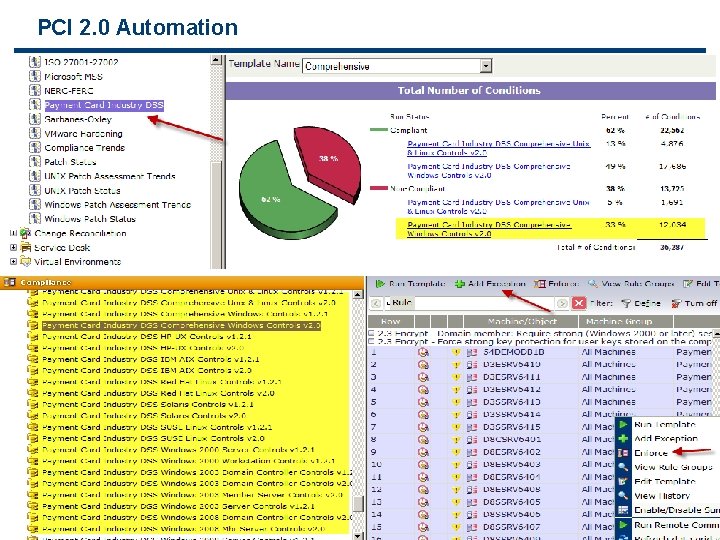
PCI 2. 0 Automation 20 Confidential
The VMware Difference Better than Physical 21 Automated and self-healing Security and compliance Trust Zones Power of cloud infrastructure automation Confidential
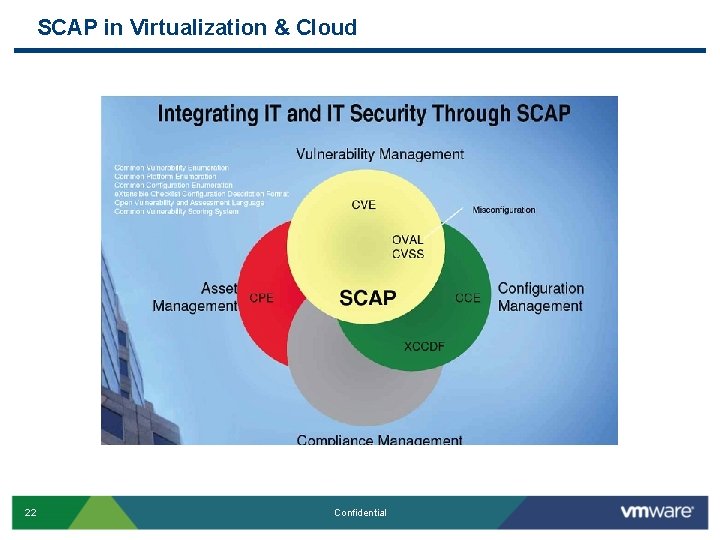
SCAP in Virtualization & Cloud 22 Confidential
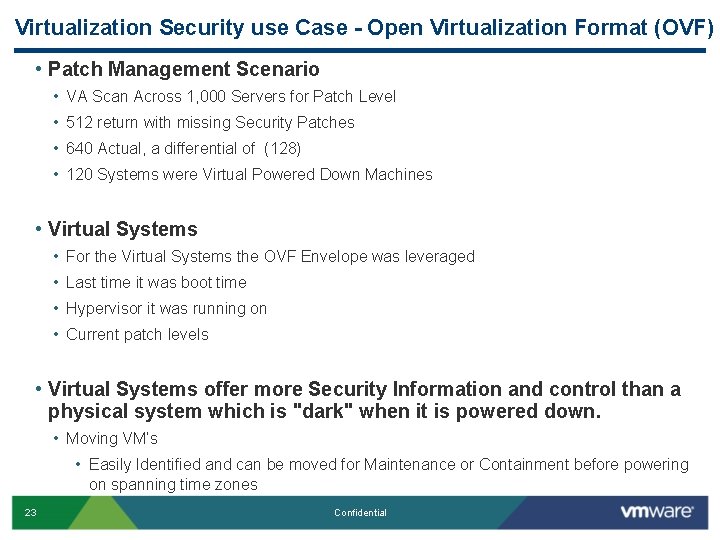
Virtualization Security use Case - Open Virtualization Format (OVF) • Patch Management Scenario • VA Scan Across 1, 000 Servers for Patch Level • 512 return with missing Security Patches • 640 Actual, a differential of (128) • 120 Systems were Virtual Powered Down Machines • Virtual Systems • For the Virtual Systems the OVF Envelope was leveraged • Last time it was boot time • Hypervisor it was running on • Current patch levels • Virtual Systems offer more Security Information and control than a physical system which is "dark" when it is powered down. • Moving VM’s • Easily Identified and can be moved for Maintenance or Containment before powering on spanning time zones 23 Confidential
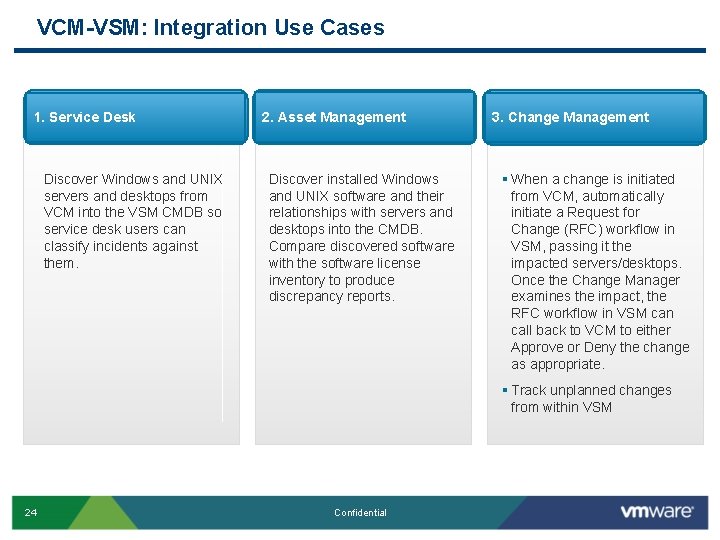
VCM-VSM: Integration Use Cases 1. Service Desk Discover Windows and UNIX servers and desktops from VCM into the VSM CMDB so service desk users can classify incidents against them. 2. Asset Management Discover installed Windows and UNIX software and their relationships with servers and desktops into the CMDB. Compare discovered software with the software license inventory to produce discrepancy reports. 3. Change Management § When a change is initiated from VCM, automatically initiate a Request for Change (RFC) workflow in VSM, passing it the impacted servers/desktops. Once the Change Manager examines the impact, the RFC workflow in VSM can call back to VCM to either Approve or Deny the change as appropriate. § Track unplanned changes from within VSM 24 Confidential
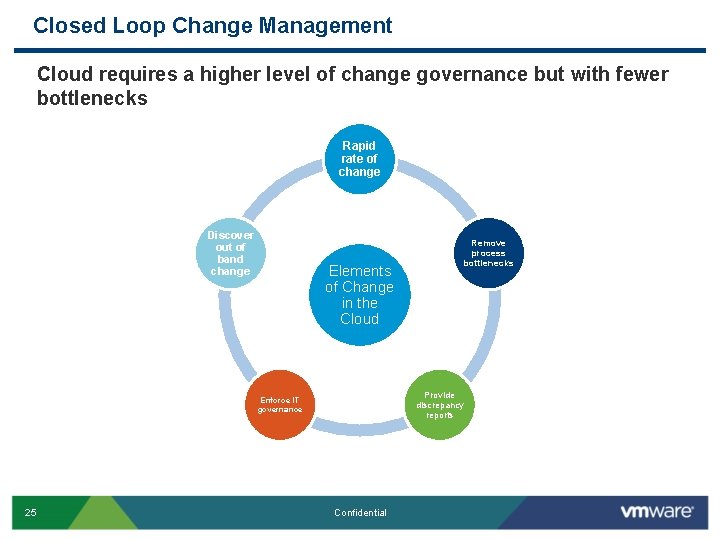
Closed Loop Change Management Cloud requires a higher level of change governance but with fewer bottlenecks Rapid rate of change Discover out of band change Elements of Change in the Cloud Provide discrepancy reports Enforce IT governance 25 Remove process bottlenecks Confidential
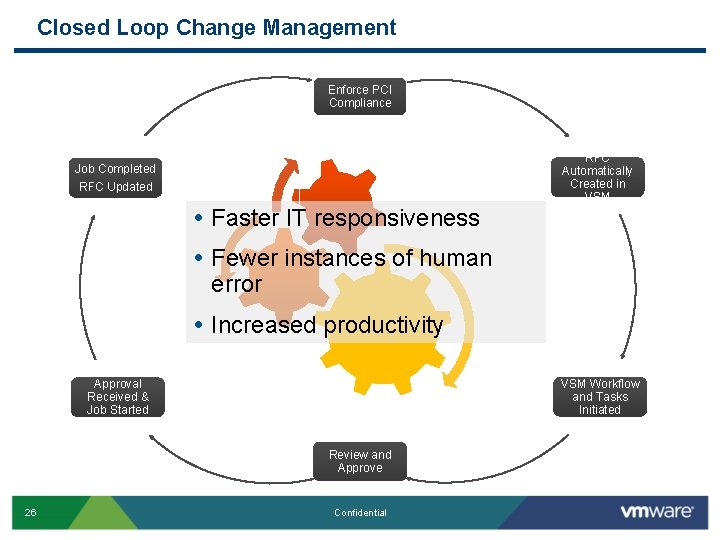
Closed Loop Change Management Enforce PCI Compliance Job Completed RFC Updated Faster IT responsiveness RFC Automatically Created in VSM Fewer instances of human error Increased productivity VSM Workflow and Tasks Initiated Approval Received & Job Started Review and Approve 26 Confidential
Agenda Challenges in Cloud Adoption VMware Trusted Cloud Solutions VMware Trusted Cloud Ecosystem VMware Center for Policy & Compliance Key Takeaways Q&A 27 Confidential
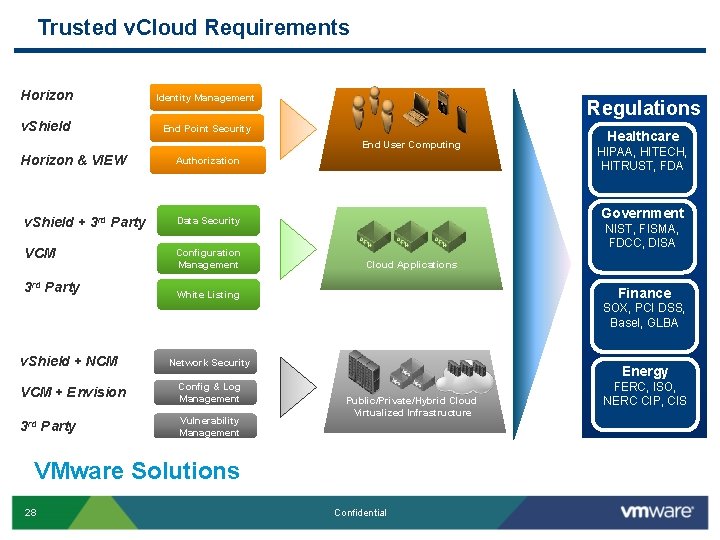
Trusted v. Cloud Requirements Horizon Identity Management v. Shield End Point Security Regulations End User Computing Horizon & VIEW Authorization v. Shield + 3 rd Party Data Security VCM Configuration Management 3 rd Party Healthcare HIPAA, HITECH, HITRUST, FDA Government NIST, FISMA, FDCC, DISA Cloud Applications Finance White Listing SOX, PCI DSS, Basel, GLBA v. Shield + NCM Network Security VCM + Envision Config & Log Management 3 rd Party Vulnerability Management Energy Public/Private/Hybrid Cloud Virtualized Infrastructure VMware Solutions 28 Confidential FERC, ISO, NERC CIP, CIS
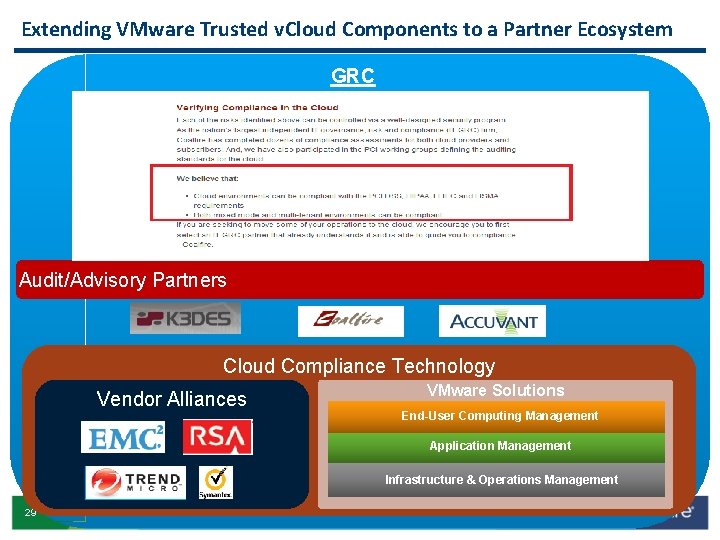
Extending VMware Trusted v. Cloud Components to a Partner Ecosystem GRC Audit/Advisory Partners Cloud Compliance Technology VMware Solutions Vendor Alliances End-User Computing Management Application Management Infrastructure & Operations Management 29 Confidential
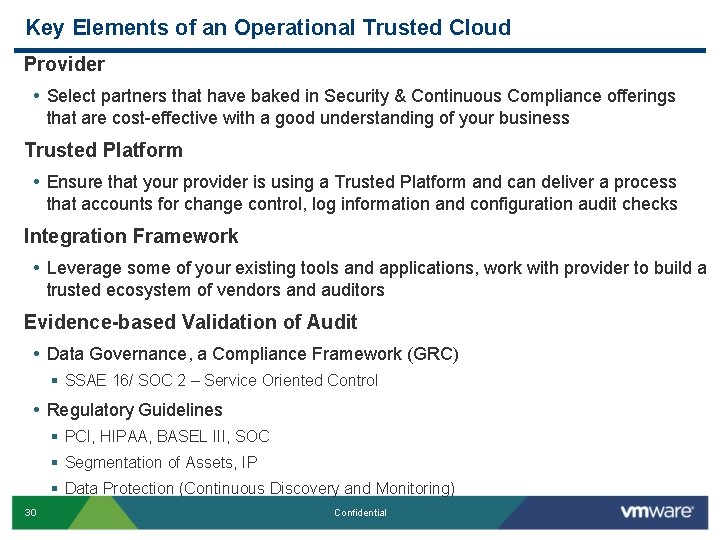
Key Elements of an Operational Trusted Cloud Provider • Select partners that have baked in Security & Continuous Compliance offerings that are cost-effective with a good understanding of your business Trusted Platform • Ensure that your provider is using a Trusted Platform and can deliver a process that accounts for change control, log information and configuration audit checks Integration Framework • Leverage some of your existing tools and applications, work with provider to build a trusted ecosystem of vendors and auditors Evidence-based Validation of Audit • Data Governance, a Compliance Framework (GRC) § SSAE 16/ SOC 2 – Service Oriented Control • Regulatory Guidelines § PCI, HIPAA, BASEL III, SOC § Segmentation of Assets, IP § Data Protection (Continuous Discovery and Monitoring) 30 Confidential
Sample - Locking down Virtualized Enviroments Authentication • Restricting Admin Root Access Communication Networking • Making sure network is segmented properly • Leak Prevention § Guest from Host § Guest to Guest § Configuration Patching • Changing Root Password (90 days) • Patching Host 31 Confidential
Sample - Questions to ask your QSA Industry Knowledge • Have you successfully taken a virtual environment through a PCI Certification § Submitted an ROC to the Council (Report On Compliance) Scope • Does your virtual environment require for you to put everything in scope? § What would they (QSA) do to reduce scope Segmentation • What does it mean to segment in a Virtual Environment? § Firewall, IDS, IPS (Statefull or Stateless) 32 Confidential
Authorative Sources in the Compliance Industry NIST - The National Institute of Standards and Technology • Free Guidance, have been researching Cloud Computing since early 2000’s • Definition of Cloud Computing (SP 800 -145) • Cloud Computing Reference Architecture (SP 500 -292) • Guidelines on Security and Privacy in Public Cloud Computing (SP 800 -144) CSA – Cloud Security Alliance • Membership Based (CCSK - Certificate of Cloud Security Knowledge) • Security Guidance for Critical Areas of Focus in Cloud Computing • 14 Domains, #13 covers Virtualization • Cloud Control Matrix (CCM v 1. 2) • Consensus Assessments Initiative Questionnaire (CSA – CAI) • CTP – Cloud Trust Protocol (24 Elements of Trust, 4 th Pillar of GRC) DISA – Defense Information System Agency • Not much in Cloud Computing • v. Sphere STIG 33 Confidential
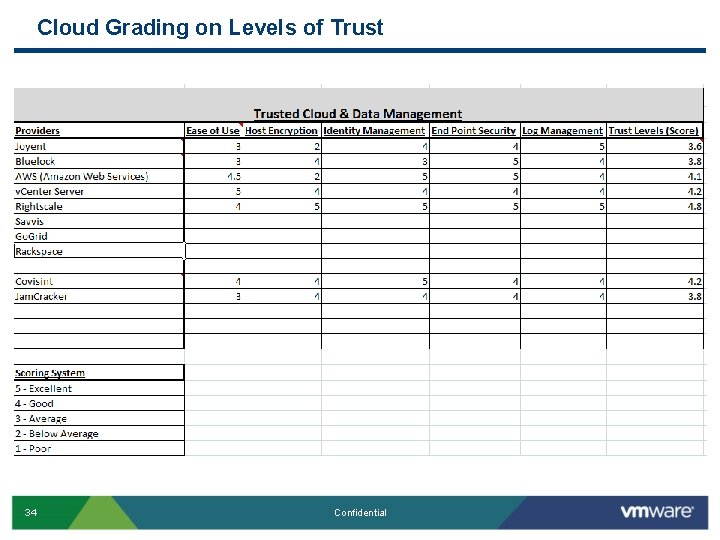
Cloud Grading on Levels of Trust 34 Confidential
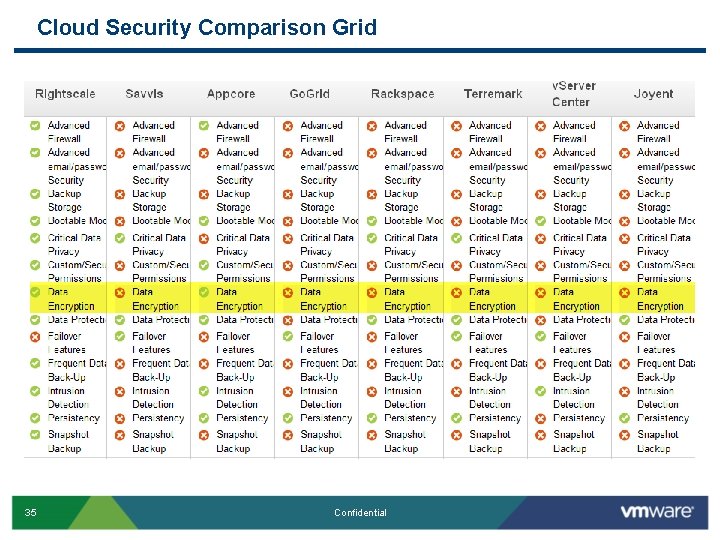
Cloud Security Comparison Grid 35 Confidential
Agenda Challenges in Cloud Adoption VMware Trusted Cloud Solutions VMware Trusted Cloud Ecosystem VMware Center for Policy & Compliance Key Takeaways Q&A 36 Confidential
VMware Center for Policy & Compliance § The Center for Policy & Compliance (CP&C) is a dedicated group comprised of security and compliance policy experts, analysts and technical specialists chartered to research and develop compliance solutions for cloud computing environments § Current staff of includes team members that average over 18 years experience and hold numerous certifications such as CISSP, CCNA, ITIL, MCSE, MCDBA, and of course v. CP. § CP&C has a Global presence and frequently meets with Customers, Auditors and Analyst to provide guidance & thought leadership in PCI, Healthcare and Trusted Cloud environments. 37 Confidential
CP&C Business Objectives Support migration of highly regulated workloads to v. Cloud Infrastructure Family • Create and support content and hardening guidelines for v. Sphere, v. Center, v. Shield, v. CD, VIEW • Compile Deployment Information Guides (DIGs) on how to deploy the v. Sphere stack to support highly regulated workloads, e. g. PCI • Set foundation and high level reference architecture for Trusted Cloud Provide coverage of common regulatory, industry and vendor policies • Address the Healthcare vertical first as it’s highly regulated • Will naturally provide coverage for other verticals (Finance, Federal) • Build a partner ecosystem for Trusted Cloud (RSA, EMC…) Drive industry thought leadership • Evangelize VMware’s compliance strategy • Align and influence compliance industry initiative and bodies like CSA, CTP • Continued market education – QSAs, analysts, customers and partners 38 Confidential
Real World Examples - Healthcare Related Breaches “The computer vanished from an NHS building in the biggest-ever security breach of its kind. […] A LAPTOP holding the medical records of eight MILLION patients has gone missing. […] The unencrypted laptop contains sensitive details of 8. 63 million people plus records of 18 million hospital visits, operations and procedures. ” (1) NHS (1) http: //www. thesun. co. uk/sol/homepage/news/3637704/Missing-Laptop-with-86 million-medical-records. html 39 Confidential
HIPAA BARES IT’S TEETH!!!!! § Feb 2 k 11 - Maryland health care provider was fined $4. 3 m fine for violations of the HIPAA Privacy Rule. • First monetary fine issued since the Act was passed in 1996. • Also in February, Massachusetts General Hospital fined to pay $1 million to settle HIPAA violations following the loss of customers' medical data. § July 2 k 11 - University of California at Los Angeles Health Services (UCLAHS) has agreed to pay a $865, 000 breaking the Health Insurance Portability and Accountability Act (HIPAA). • According to a press release on the HHS site, the settlement stems from two claims that unauthorized employees accessed records of celebrities that received care at UCLAHS. 40 Confidential
Agenda § § § 41 Challenges in Cloud Adoption VMware Trusted Cloud Solutions VMware Trusted Cloud Ecosystem VMware Center for Policy & Compliance Key Takeaways Q&A Confidential
Where Does VMware Fit? §Cloud Infrastructure Suite Trusted Platform § v. Sphere, v. Cloud Director, v. Center §v. Shield – Enable Security Controls • Securing Perimeter, • Segmenting Applications • Data Discovery and Protection §v. CM – Continuous Compliance • Adherence to regulatory Guidelines • Out of the Box Benchmarks • Auto Remediate Non Compliant Results §VIN & VCO • Cloud Framework, Application Relationships 42 Confidential
Call to Action and key Takeaways § Further Education and TCO • Solutions Demo • http: //info. vmware. com/content/VCMSolutions. Demo § *NEW* VMware/Forrester v. CM ROI • https: //www. gosavo. com/vmware/Document. aspx? id=2222106&view=Preview § Leverage CP&C with Auditors (QSA) • Mixed Mode Environments, Trusted Cloud Architecture & Partner Ecosystem § More Security & Compliance Information • Mastermind Series • http: //info. vmware. com/content/13090_Virt. Mng_NA_Security_ITCompliance? src=SALE S-NPD&elq=&xyz • VMware Security Blog • http: //blogs. vmware. com/security/ • Free Compliance Checkers • http: //communities. vmware. com/community/vmtn/vsphere/compliance-checker 43 Confidential
Enterprise Hybrid cloud requirements – best of both worlds Agility with Reliable Performance • On-demand provisioning of virtual servers • Fast scale up at reasonable cost • Predictable, consistent SLAs Security & Compliance • Secure & auditable cloud infrastructure • Secure apps and user access Application Portability • Compatible with existing workloads • Globally consistent service across providers 44 Confidential
What To Expect From ITBM…. . ü Transition from managing technology to managing services ü Expose the cost and value of IT & Compliance to your entire organization ü Understand impact of business demand change ü Identify where money saving opportunities exist ü Communicate and improve quality of service ü Manage the relationships with your customers and external vendors Find Opportunities Identify cost savings opportunities Analyze Costs Analyze existing IT costs Make Changes Track Savings Track cost savings 45 Confidential Implement cost Optimization strategies
Agenda § § § 46 Challenges in Cloud Adoption VMware Trusted Cloud Solutions VMware Trusted Cloud Ecosystem VMware Center for Policy & Compliance Key Takeaways Q&A Confidential
Questions Confidential © 2010 VMware Inc. All rights reserved
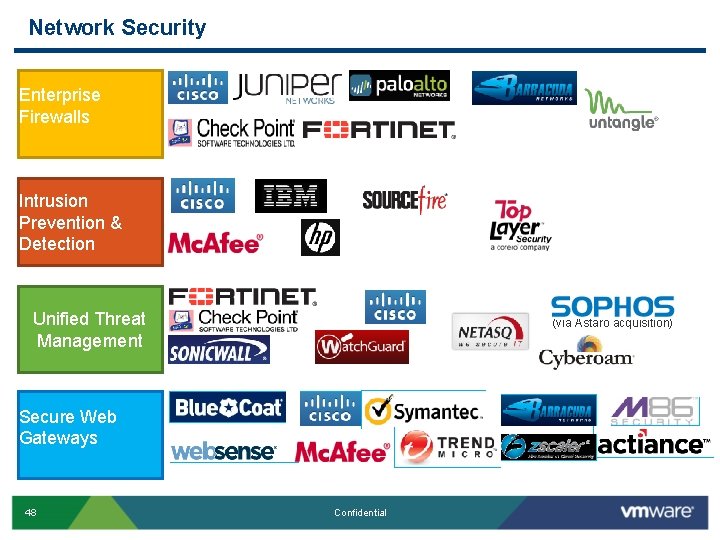
Network Security Enterprise Firewalls Intrusion Prevention & Detection Unified Threat Management (via Astaro acquisition) Secure Web Gateways 48 Confidential
Network Security cont. Web Application Firewalls Firewall Rule Analysis & Management Database Activity Monitoring Application Control (Whitelisting) 49 Confidential
Configuration and Change Mgmt. , Identity Mgmt. , Data Security, Compliance Configuration & Change Management Identity & Access Management Data Security: Encryption & Key Mgmt. $45 M funding, $30 M revenue $41 M funding, $10 M revenue Data Loss Prevention 50 Confidential
Configuration and Change Mgmt. , Identity Mgmt. , Data Security, Compliance Vulnerability Assessment & Management Governance, Risk Management Compliance Enterprise Security Information Management (Gartner taxonomy: ESIM = SIEM + OLM) Security Information & Event Monitoring Operational Log Management 51 Confidential
Network Management Network Configuration Management DDI $150 M runrate (DNS, DHCP, IPAM) Network Access Controller Endpoint Security 52 Confidential