
A Framework for Diversifying Windows Native APIs to
- Slides: 9
A Framework for Diversifying Windows Native APIs to Tolerate Code Injection Attacks Lynette Qu Nguyen, Tufan Demir, Jeff Rowe, Francis Hsu and Karl Levitt Monday, February 09, 2009 Cho, Ho-Gi
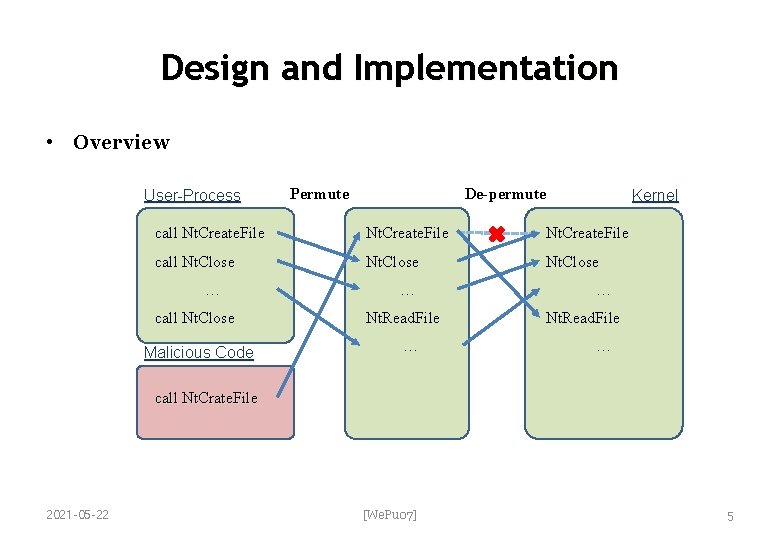
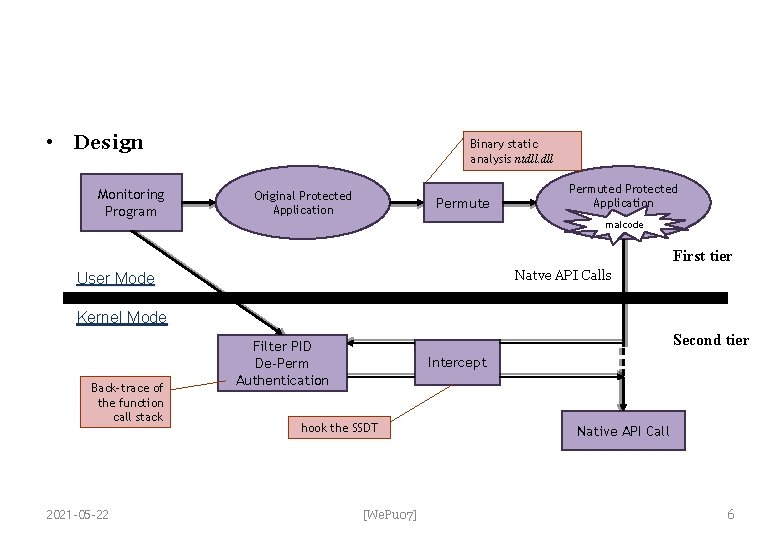
Abstract • Code injection attacks – take advantage of software memory errors to gain complete control of a victim machine by injecting malicious instructions into the victim’s process memory • Problem – The kernel serves both from malicious injected instructions and from the legitimate user processes without distinctions • Solution – First-tier • permute the Native API dispatch ID number for diversifying Windows Native APIs – Second-tier • provide an authentication process in case an attacker guesses the first-tier permutation order 2021 -05 -22 [We. Pu 07] 2
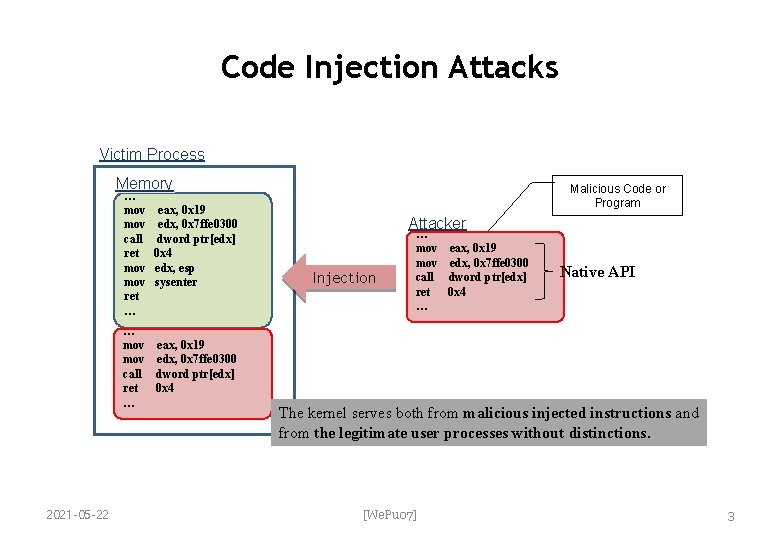
Code Injection Attacks Victim Process Memory … mov call ret mov ret … … mov call ret … 2021 -05 -22 eax, 0 x 19 edx, 0 x 7 ffe 0300 dword ptr[edx] 0 x 4 edx, esp sysenter Malicious Code or Program Attacker Injection … mov eax, 0 x 19 mov edx, 0 x 7 ffe 0300 call dword ptr[edx] ret 0 x 4 … Native API eax, 0 x 19 edx, 0 x 7 ffe 0300 dword ptr[edx] 0 x 4 The kernel serves both from malicious injected instructions and from the legitimate user processes without distinctions. [We. Pu 07] 3
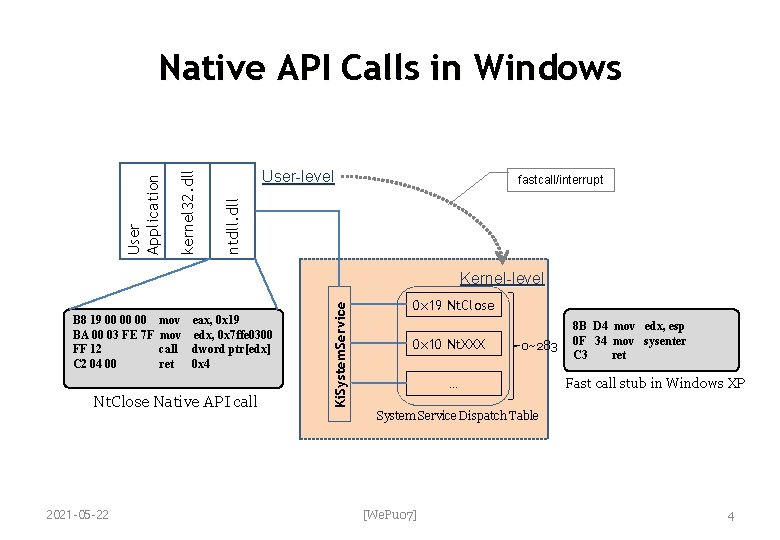
User-level fastcall/interrupt ntdll. dll kernel 32. dll User Application Native API Calls in Windows B 8 19 00 00 00 BA 00 03 FE 7 F FF 12 C 2 04 00 mov eax, 0 x 19 mov edx, 0 x 7 ffe 0300 call dword ptr[edx] ret 0 x 4 Nt. Close Native API call 2021 -05 -22 Ki. System. Service Kernel-level 0 x 19 Nt. Close 0 x 10 Nt. XXX 0~283 … 8 B D 4 mov edx, esp 0 F 34 mov sysenter C 3 ret Fast call stub in Windows XP System Service Dispatch Table [We. Pu 07] 4
Design and Implementation • Overview User-Process Permute De-permute Kernel call Nt. Create. File call Nt. Close … call Nt. Close Malicious Code … Nt. Read. File … call Nt. Crate. File 2021 -05 -22 [We. Pu 07] 5
• Design Monitoring Program Binary static analysis ntdll. dll Original Protected Application Permuted Protected Application malcode First tier Natve API Calls User Mode Kernel Mode Back-trace of the function call stack 2021 -05 -22 Second tier Filter PID De-Perm Authentication Intercept hook the SSDT [We. Pu 07] Native API Call 6
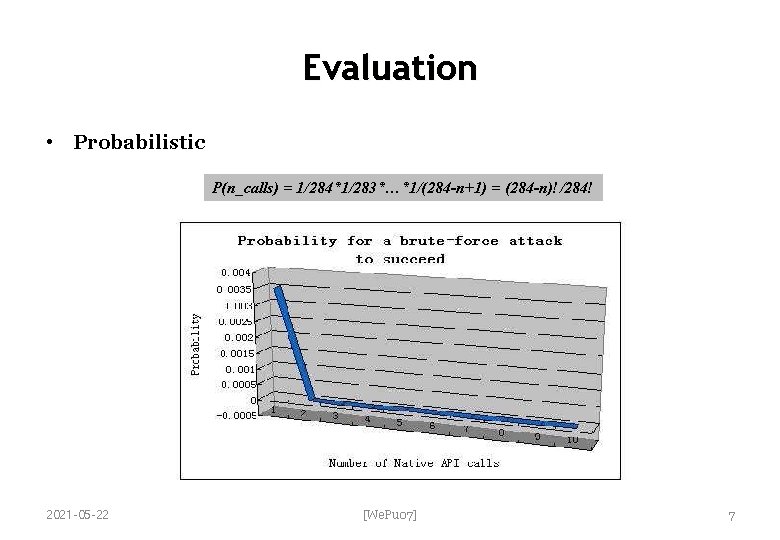
Evaluation • Probabilistic P(n_calls) = 1/284*1/283*…*1/(284 -n+1) = (284 -n)!/284! 2021 -05 -22 [We. Pu 07] 7
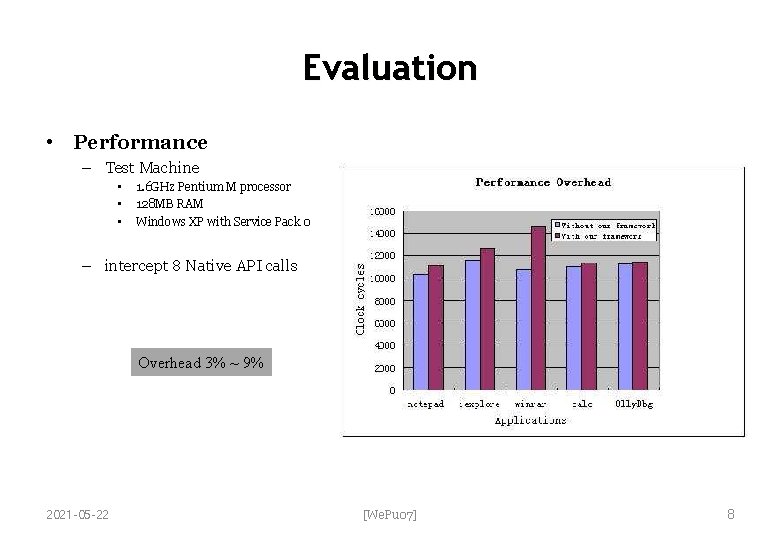
Evaluation • Performance – Test Machine • • • 1. 6 GHz Pentium M processor 128 MB RAM Windows XP with Service Pack 0 – intercept 8 Native API calls Overhead 3% ~ 9% 2021 -05 -22 [We. Pu 07] 8
Conclusions • • can not easily bypass this monitor by guessing does not require access to source code can be easily deployed without major changes to the system indicate minor run-time overhead 2021 -05 -22 [We. Pu 07] 9